

qiling
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
binary-analysisdebuggersdynamic-analysis-sandboxing+7
6.1k
qilingframework/qilingA True Instrumentable Binary Emulation Framework
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
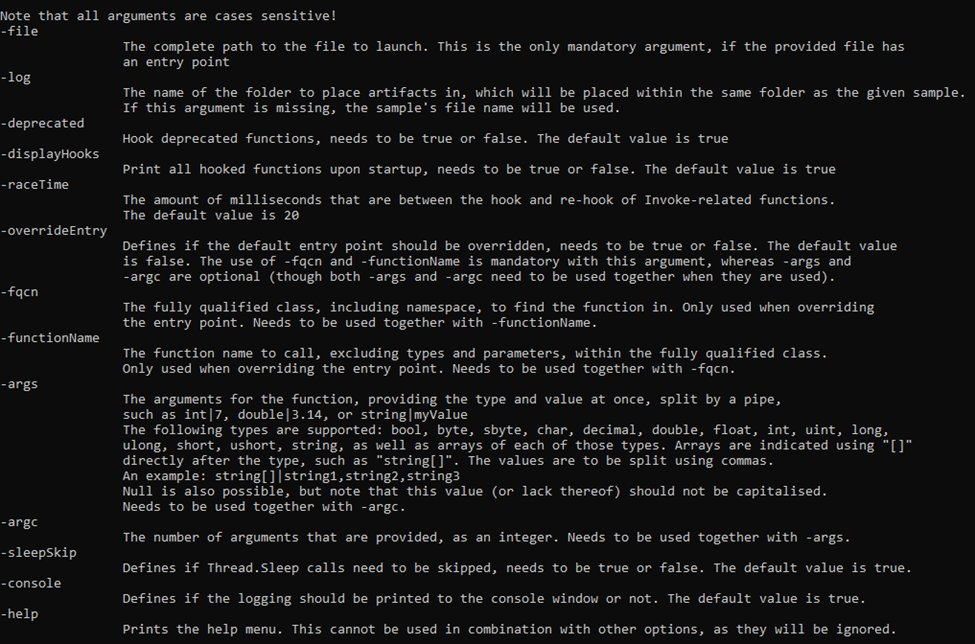 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 gallopsled/pwntools
CTF framework and exploit development library
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 cea-sec/miasm
Reverse engineering framework in Python
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 openrce/paimei
A reverse engineering framework written in Python.
 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
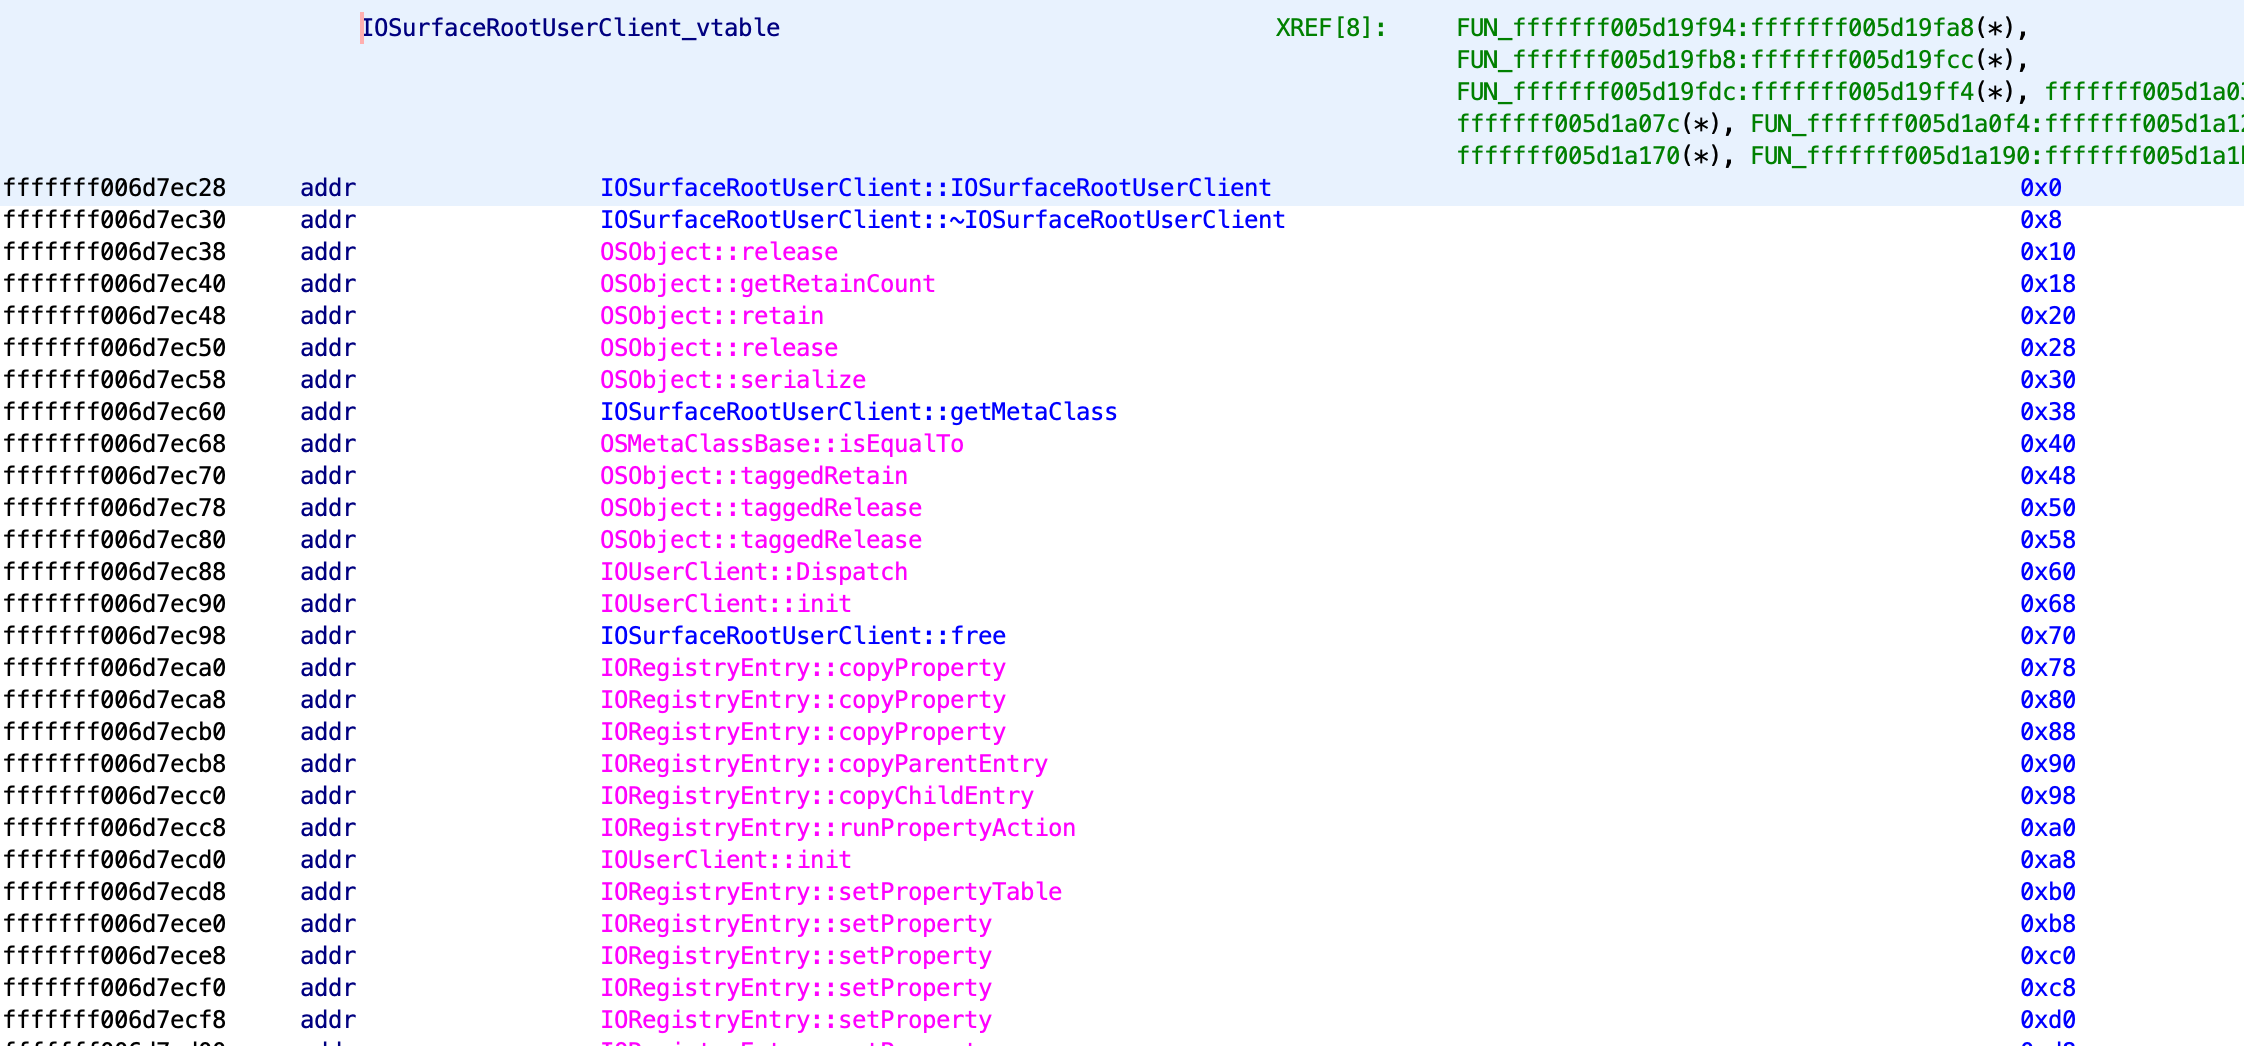 0x36/ghidra_kernelcache
a Ghidra framework for iOS kernelcache reverse engineering
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 nirizr/rematch
REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
 ropfuscator/ropfuscator
ROPfuscator is a fine-grained code obfuscation framework for C/C++ programs using ROP (return-oriented programming).
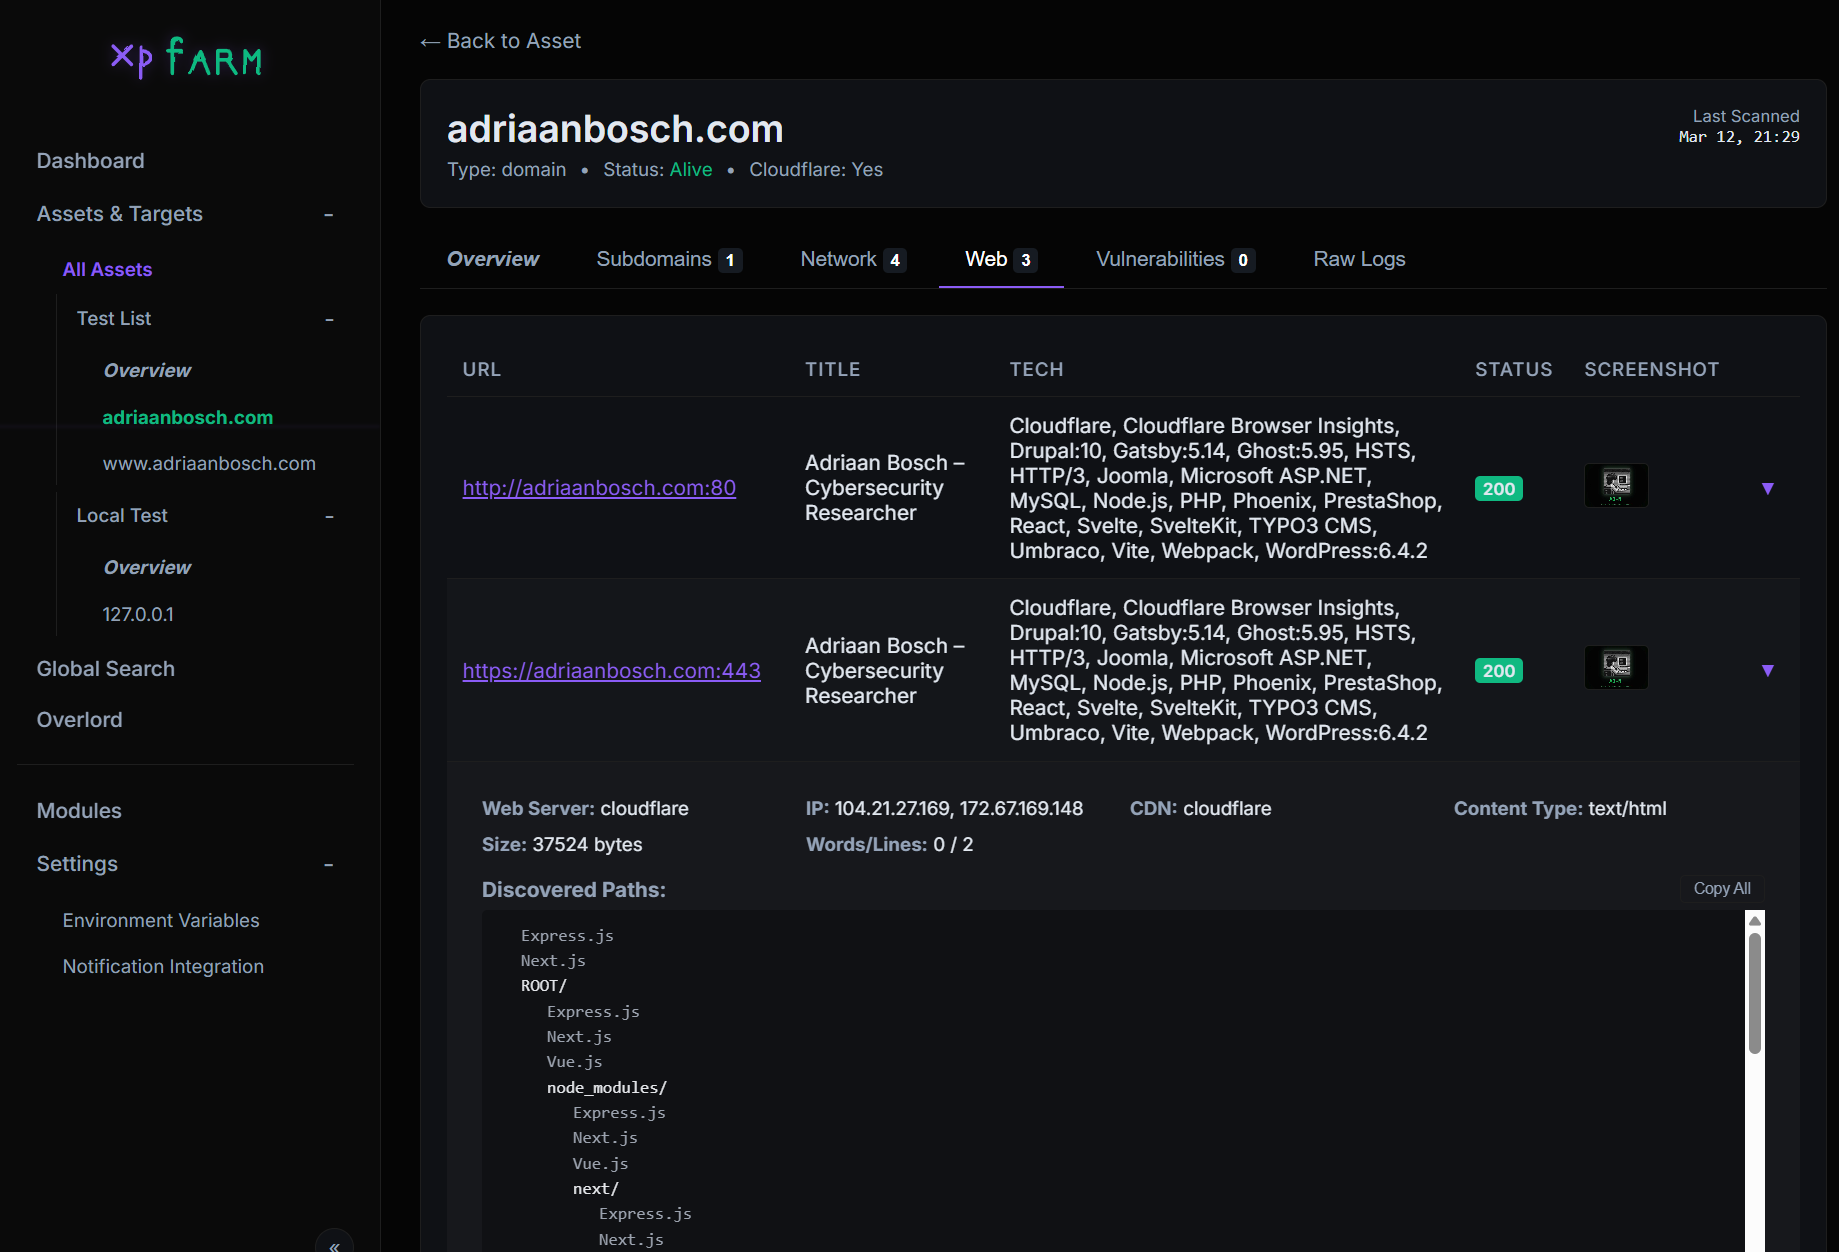 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment