
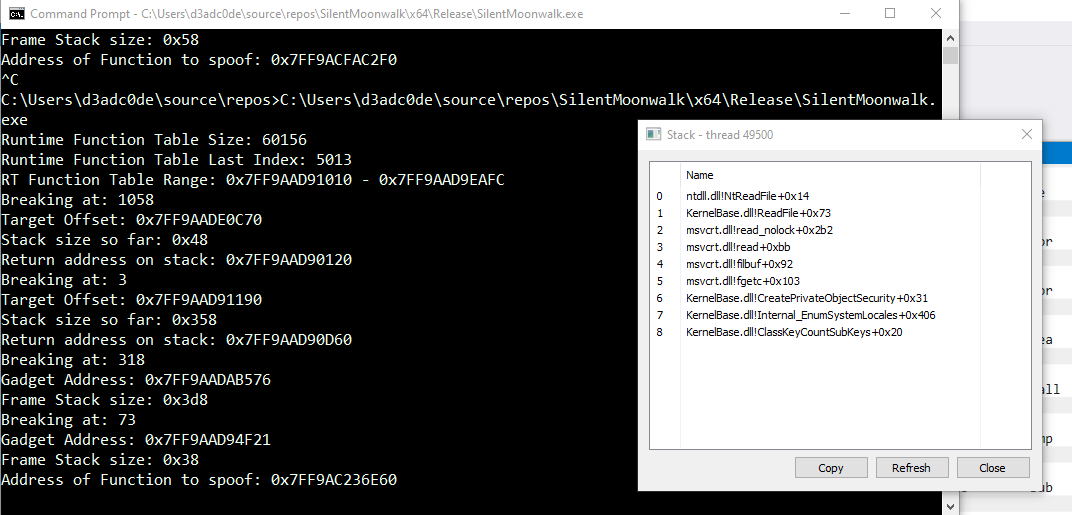
SilentMoonwalk
 klezvirus/silentmoonwalk
PoC Implementation of a fully dynamic call stack spoofer
binary-analysisexploitationpayload-development+2
996
klezvirus/silentmoonwalkPoC Implementation of a fully dynamic call stack spoofer
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 phith0n/zkar
Go-based Java serialization protocol analyzer that parses, dumps, and generates deserialization payloads with ysoserial gadget support and a library…
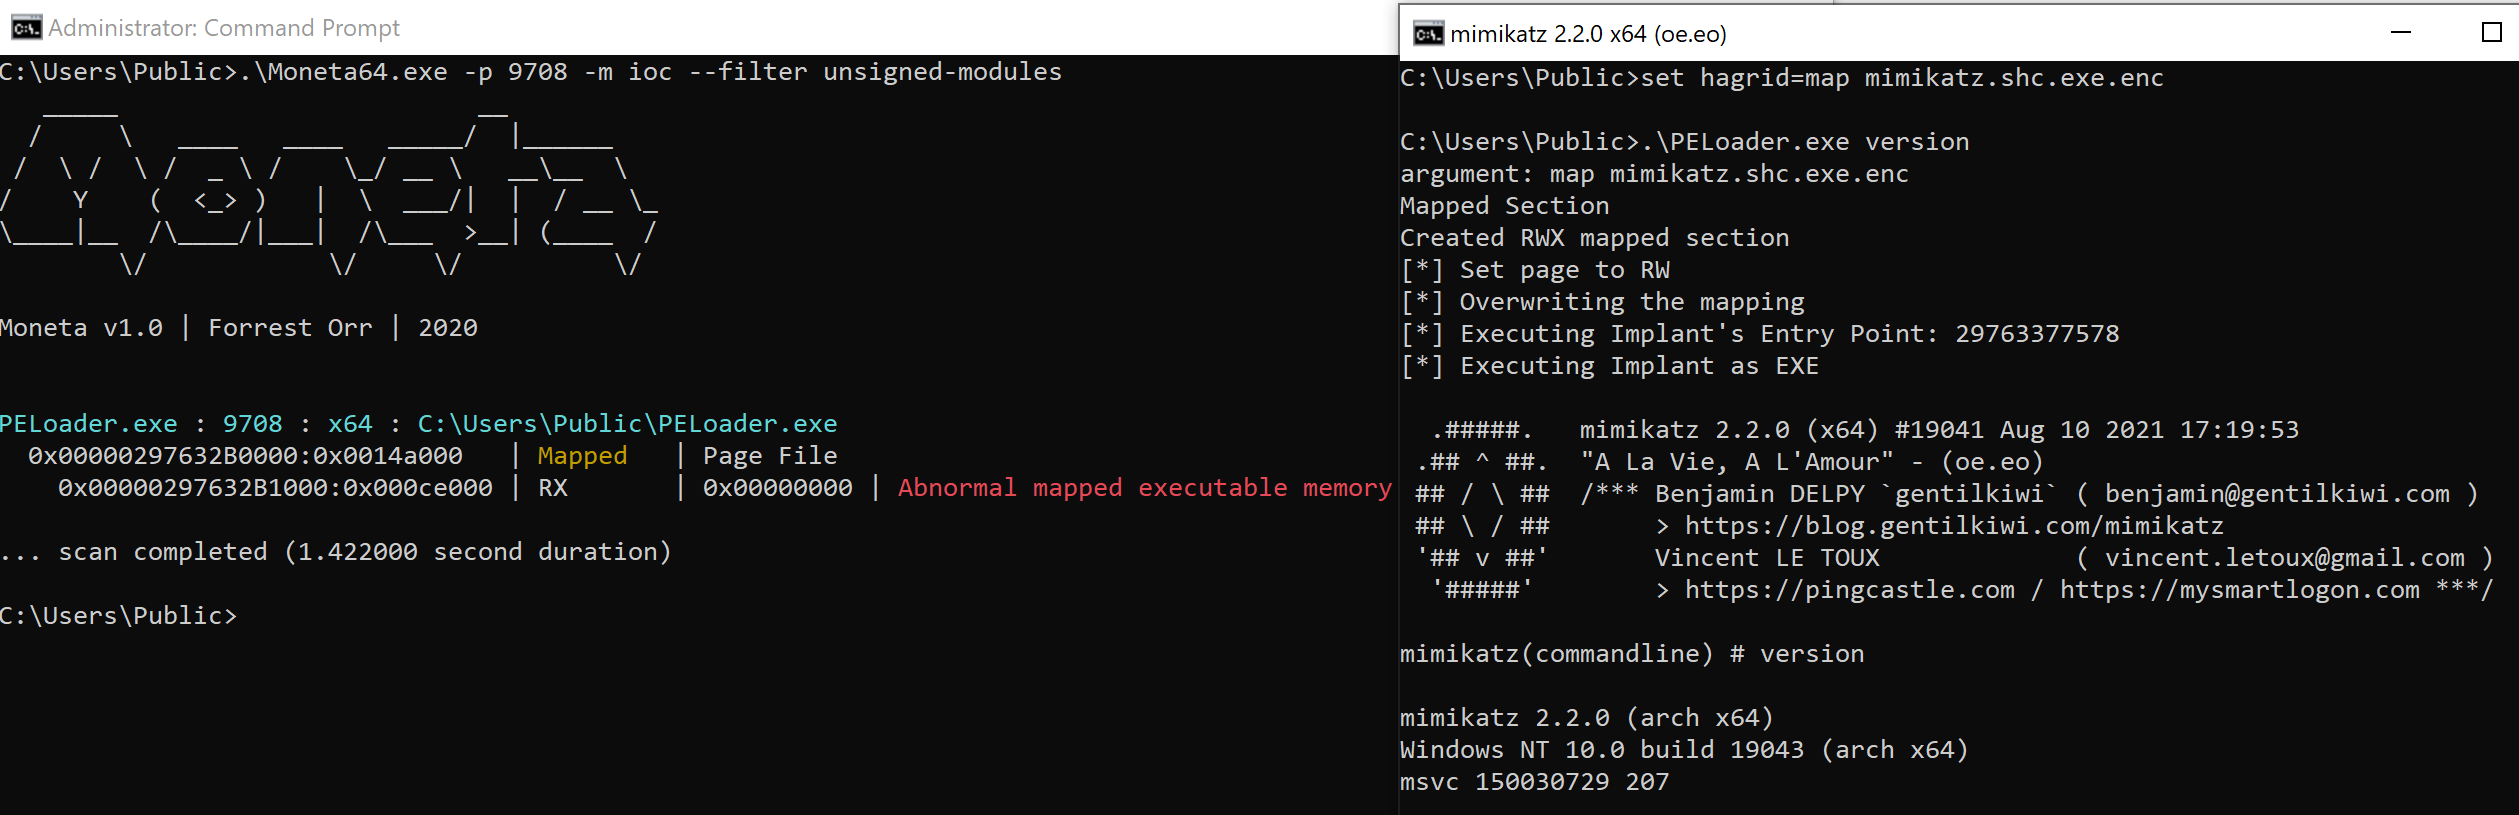 hagrid29/peloader
PE loader with various shellcode injection techniques
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
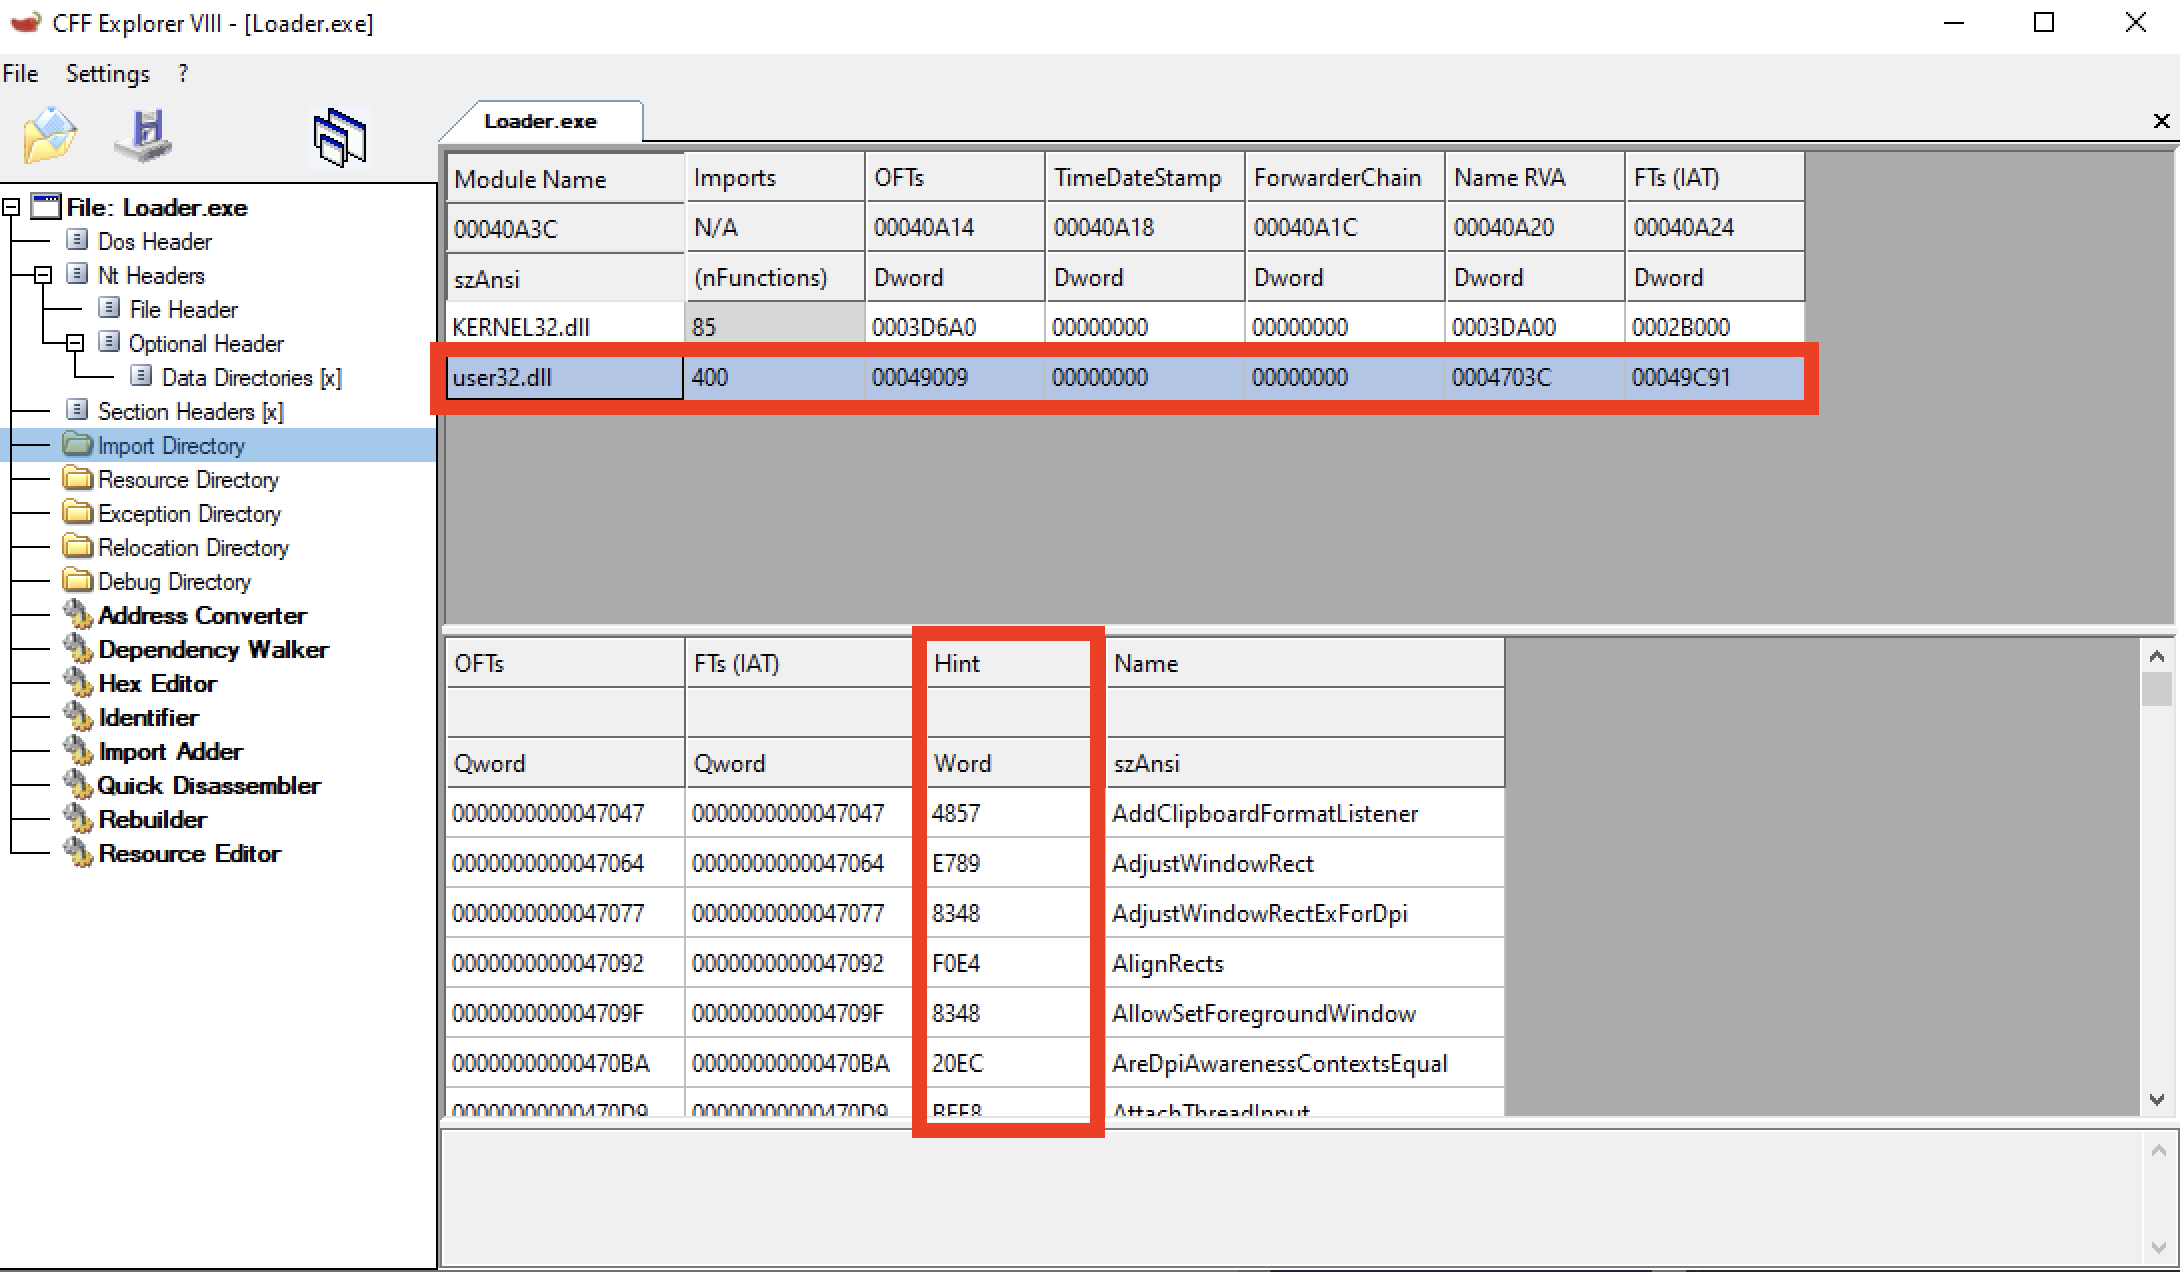 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 blacknbunny/shellcode2assembly
💻 ARCH : ARM, ARM64, MIPS, PPC, X86
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
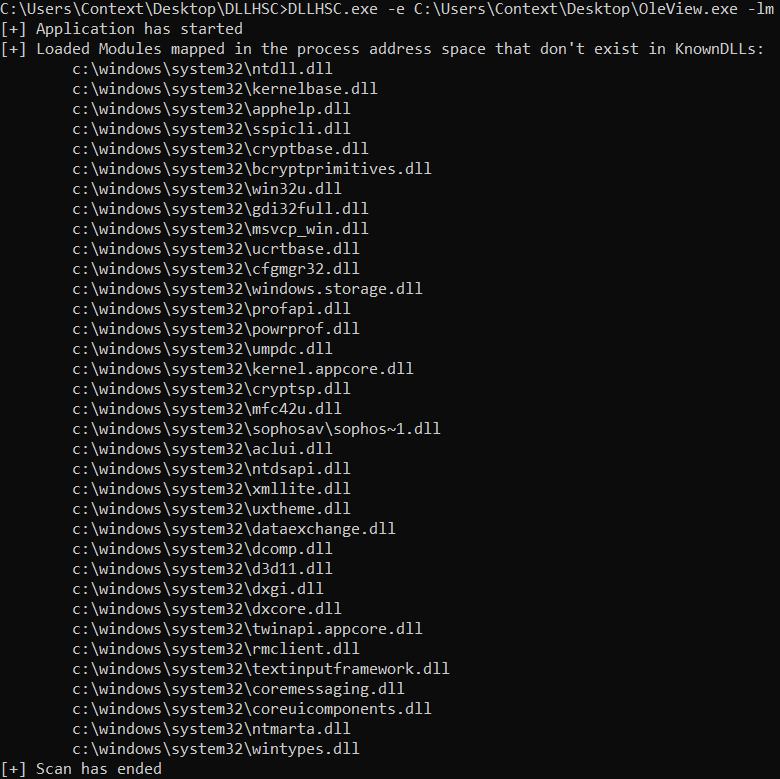 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
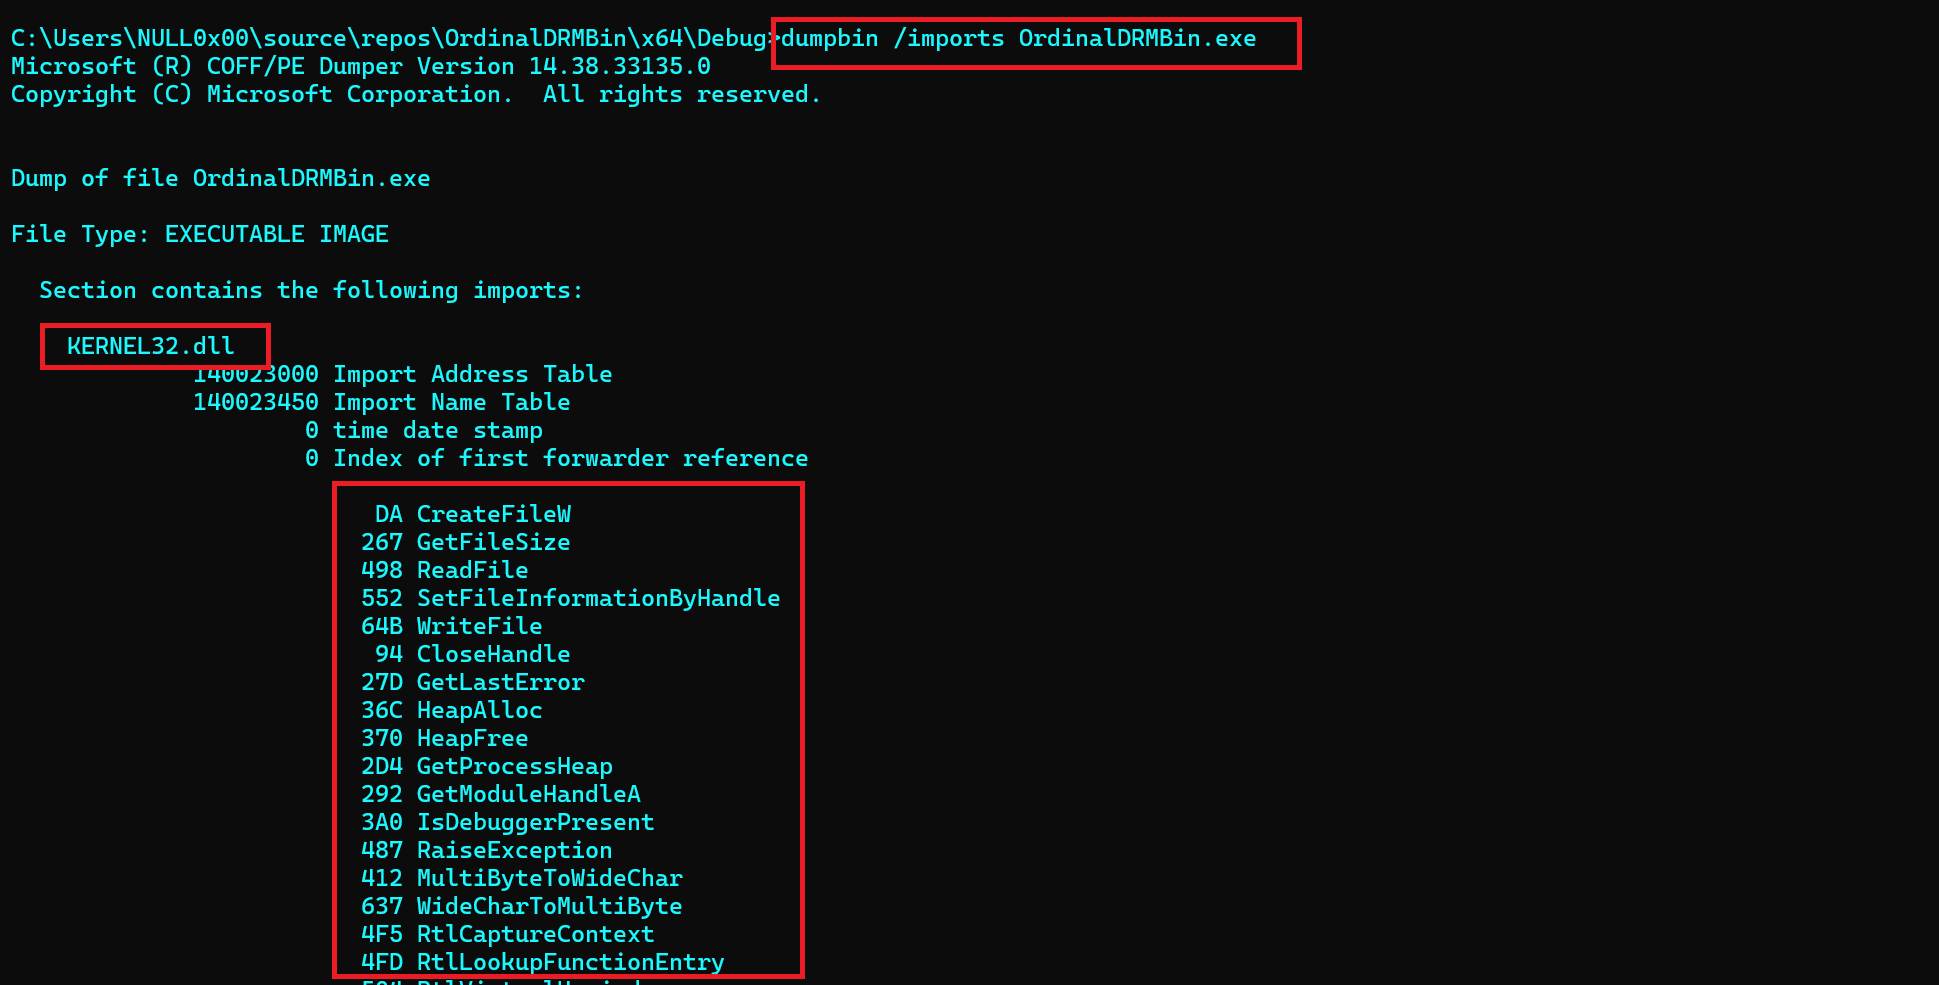 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis