
Posh-SSH
 darkoperator/posh-ssh
PowerShell Module for automating tasks on remote systems using SSH
network-securityscripting-automationutilities-frameworks
darkoperator/posh-sshPowerShell Module for automating tasks on remote systems using SSH
 likekabin/cve-2018-10933-libssh-authentication-bypass
Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…
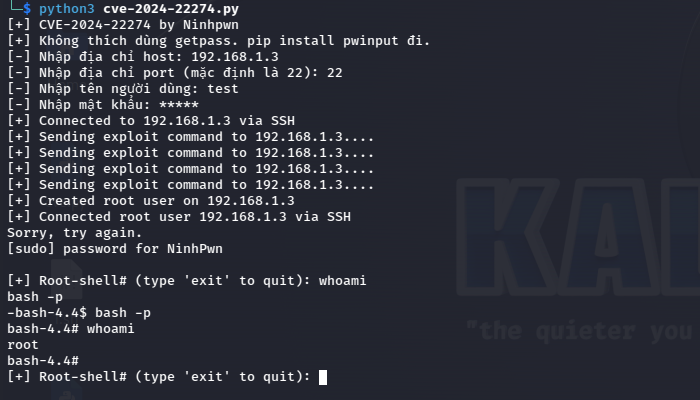 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 qingsiweisan/cve-2022-40684
Python exploit for CVE-2022-40684 targeting FortiGate devices. Supports single and batch execution with custom SSH public key injection for…
 abrewer251/cve-2025-32433_erlang-otp_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 odst-forge/cve-2025-32433_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
 4lxprime/regresshive
rewrited SSH Exploit for CVE-2024-6387 (regreSSHion)
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 sleepthegod/ssh-remote-code-execution
SSH Zero-Day Made By ClumsyLulz
 p4x1s/cve-2024-6387
SSH RCE PoC CVE-2024-6387
 adhikara13/cve-2022-4510-walkingpath
A Python script for generating exploits targeting CVE-2022-4510 RCE Binwalk. It supports SSH, command execution, and reverse shell options. Exploits…
 tenebrae93/cve-2025-3243
A proof-of-concept exploit for CVE-2025-32433, a critical vulnerability in Erlang's SSH library that allows pre-authenticated code execution via…
 symbolexe/cve-2024-6387
SSH Exploit for CVE-2024-6387 : RCE in OpenSSH's server, on glibc-based Linux systems
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 0xpthree/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang OTP SSH server. Sends crafted SSH packets to open a reverse shell and gain root access.
 robidev/cve-2020-14871-exploit
This is a basic ROP based exploit for CVE 2020-14871. CVE 2020-14871 is a vulnerability in Sun Solaris systems libpam library, and exploitable over…