
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
103 results
EDIDFuzzer preview

EDIDFuzzer

GitHubnccgroup/edidfuzzer

EDID (Enhanced Display Identification Data) Fuzzer

binary-analysisembedded-systems-securityfuzzing+2
1912 years ago
LazZzy_Dump preview

LazZzy_Dump

GitHubtrustedsec/lazzzy_dump

Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
binary-analysiscode-analysisdigital-forensics+6
129 days ago
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k4 months ago
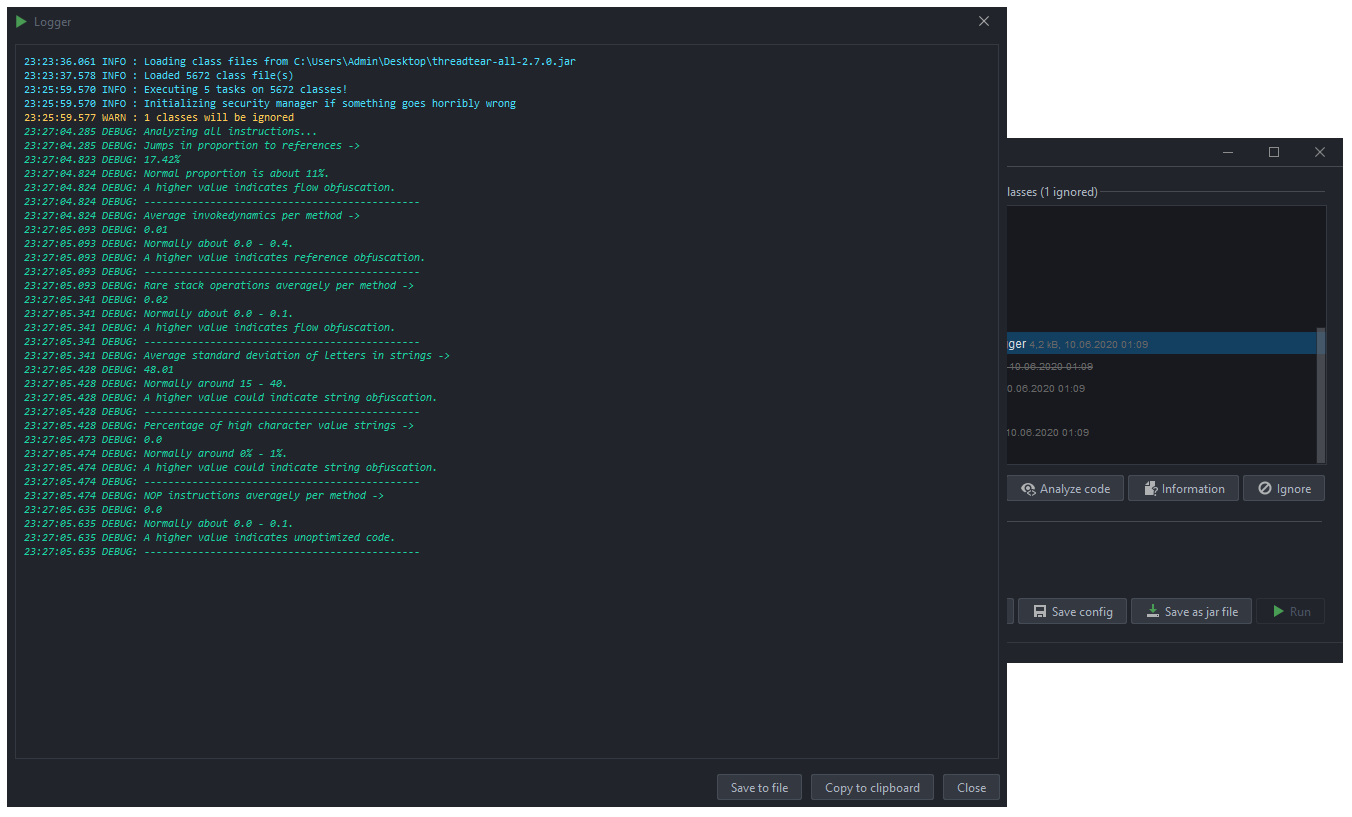
threadtear preview

threadtear

GitHubloerting/threadtear

Multifunctional java deobfuscation tool suite

binary-analysiscode-analysisdebuggers+3
9825 years ago
Introspy-iOS preview

Introspy-iOS

GitHubisecpartners/introspy-ios

Security profiling for blackbox iOS
binary-analysisdebuggersdynamic-analysis-sandboxing+5
7409 years ago
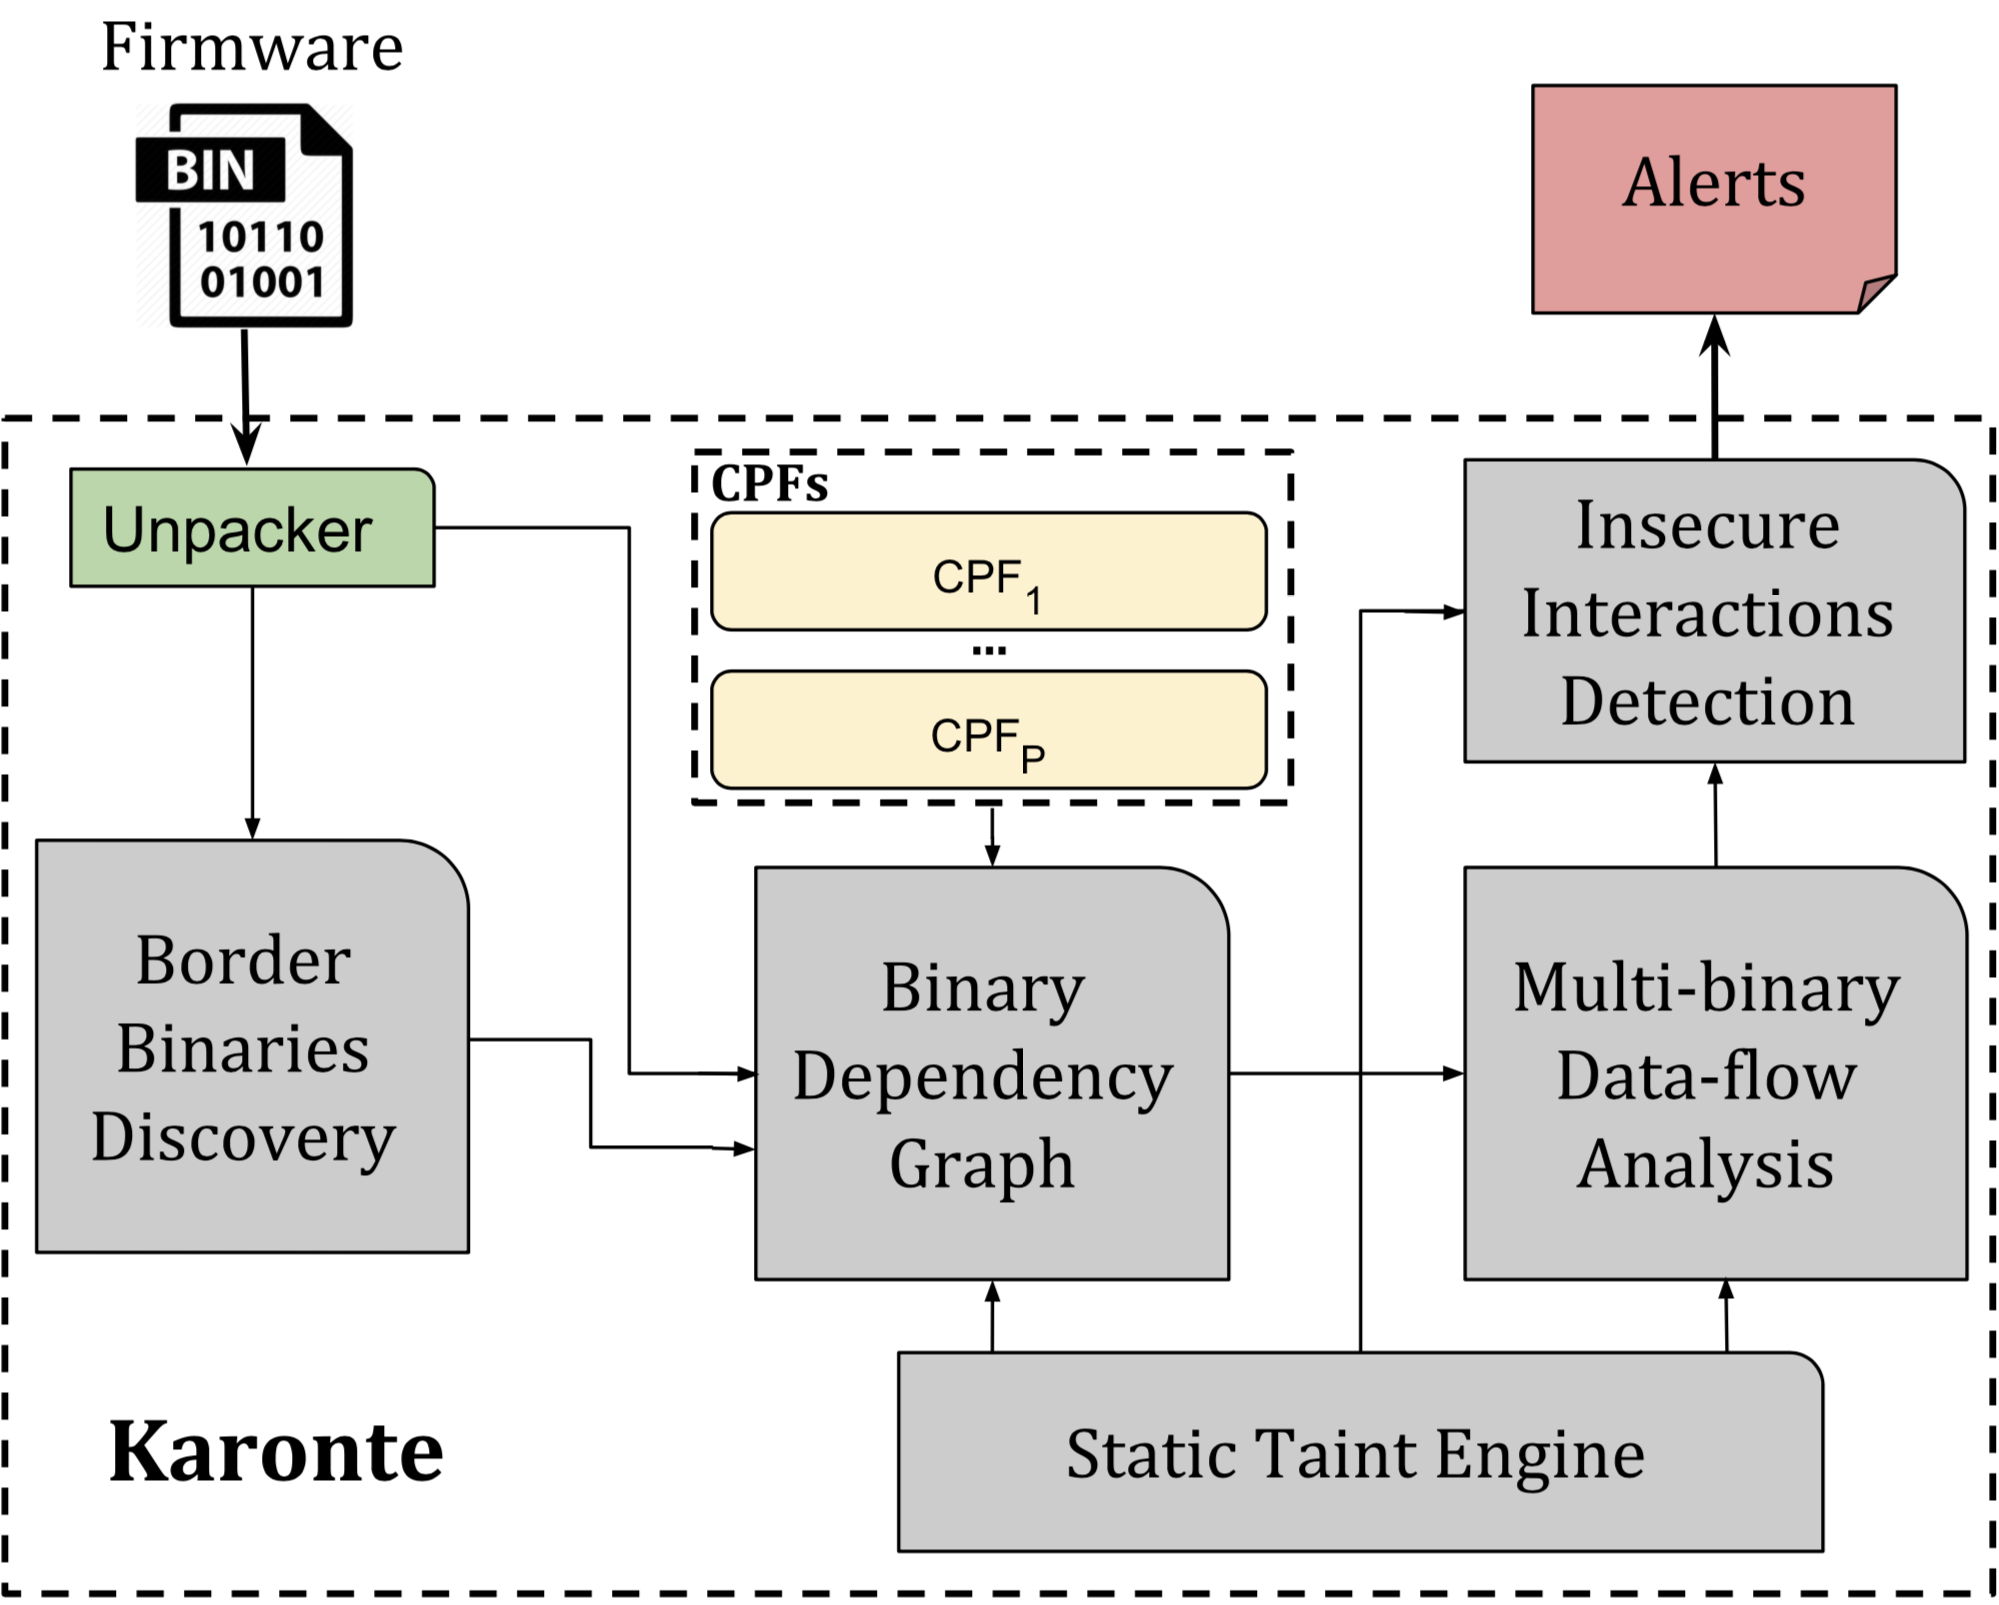
karonte preview

karonte

GitHubucsb-seclab/karonte

Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
binary-analysisembedded-systems-securityfirmware-analysis+2
4345 years ago
rop-tool preview

rop-tool

GitHubt00sh/rop-tool

A tool to help you write binary exploits
binary-analysisbinary-exploitationdebuggers+3
6107 years ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
DLLirant preview

DLLirant

GitHubredteamsocietegenerale/dllirant

DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.

binary-analysisdynamic-code-analysisexploitation+3
5023 years ago
asatools preview

asatools

GitHubnccgroup/asatools

Main repository to pull all NCC Group Cisco ASA-related tool projects.
binary-analysisdebuggersembedded-systems-security+3
2398 years ago
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel
binary-analysisdebuggerseducation+2
1578 years ago
MemITM preview

MemITM

GitHubamossys/memitm

Tool to make in memory man in the middle
binary-analysisdebuggersdynamic-analysis-sandboxing+4
1268 years ago
IDA2Obj preview

IDA2Obj

GitHubjhftss/ida2obj

Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…

binary-analysisdebuggersfuzzing+2
1225 years ago
Squalr preview

Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.
binary-analysisdebuggersdynamic-analysis-sandboxing+5
1873 months ago
Pishi preview

Pishi

GitHubr00tkitsmm/pishi

Pishi is a code coverage tool like kcov for macOS.
binary-analysiscode-analysisdynamic-code-analysis+3
771 month ago
cachegrab preview

cachegrab

GitHubnccgroup/cachegrab

a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores
binary-analysisembedded-systems-securityexploitation+3
877 years ago
draytek-arsenal preview

draytek-arsenal

GitHubinfobyte/draytek-arsenal

Reverse Engineering and Observability toolkit for Draytek firewalls
binary-analysisembedded-systems-securityfirmware-analysis+5
541 year ago
intel-me-research preview

intel-me-research

GitHubjatinkapilaq1/intel-me-research

Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…

binary-analysisembedded-systems-securityfirmware-analysis+4
172 months ago
Previous123456Next