
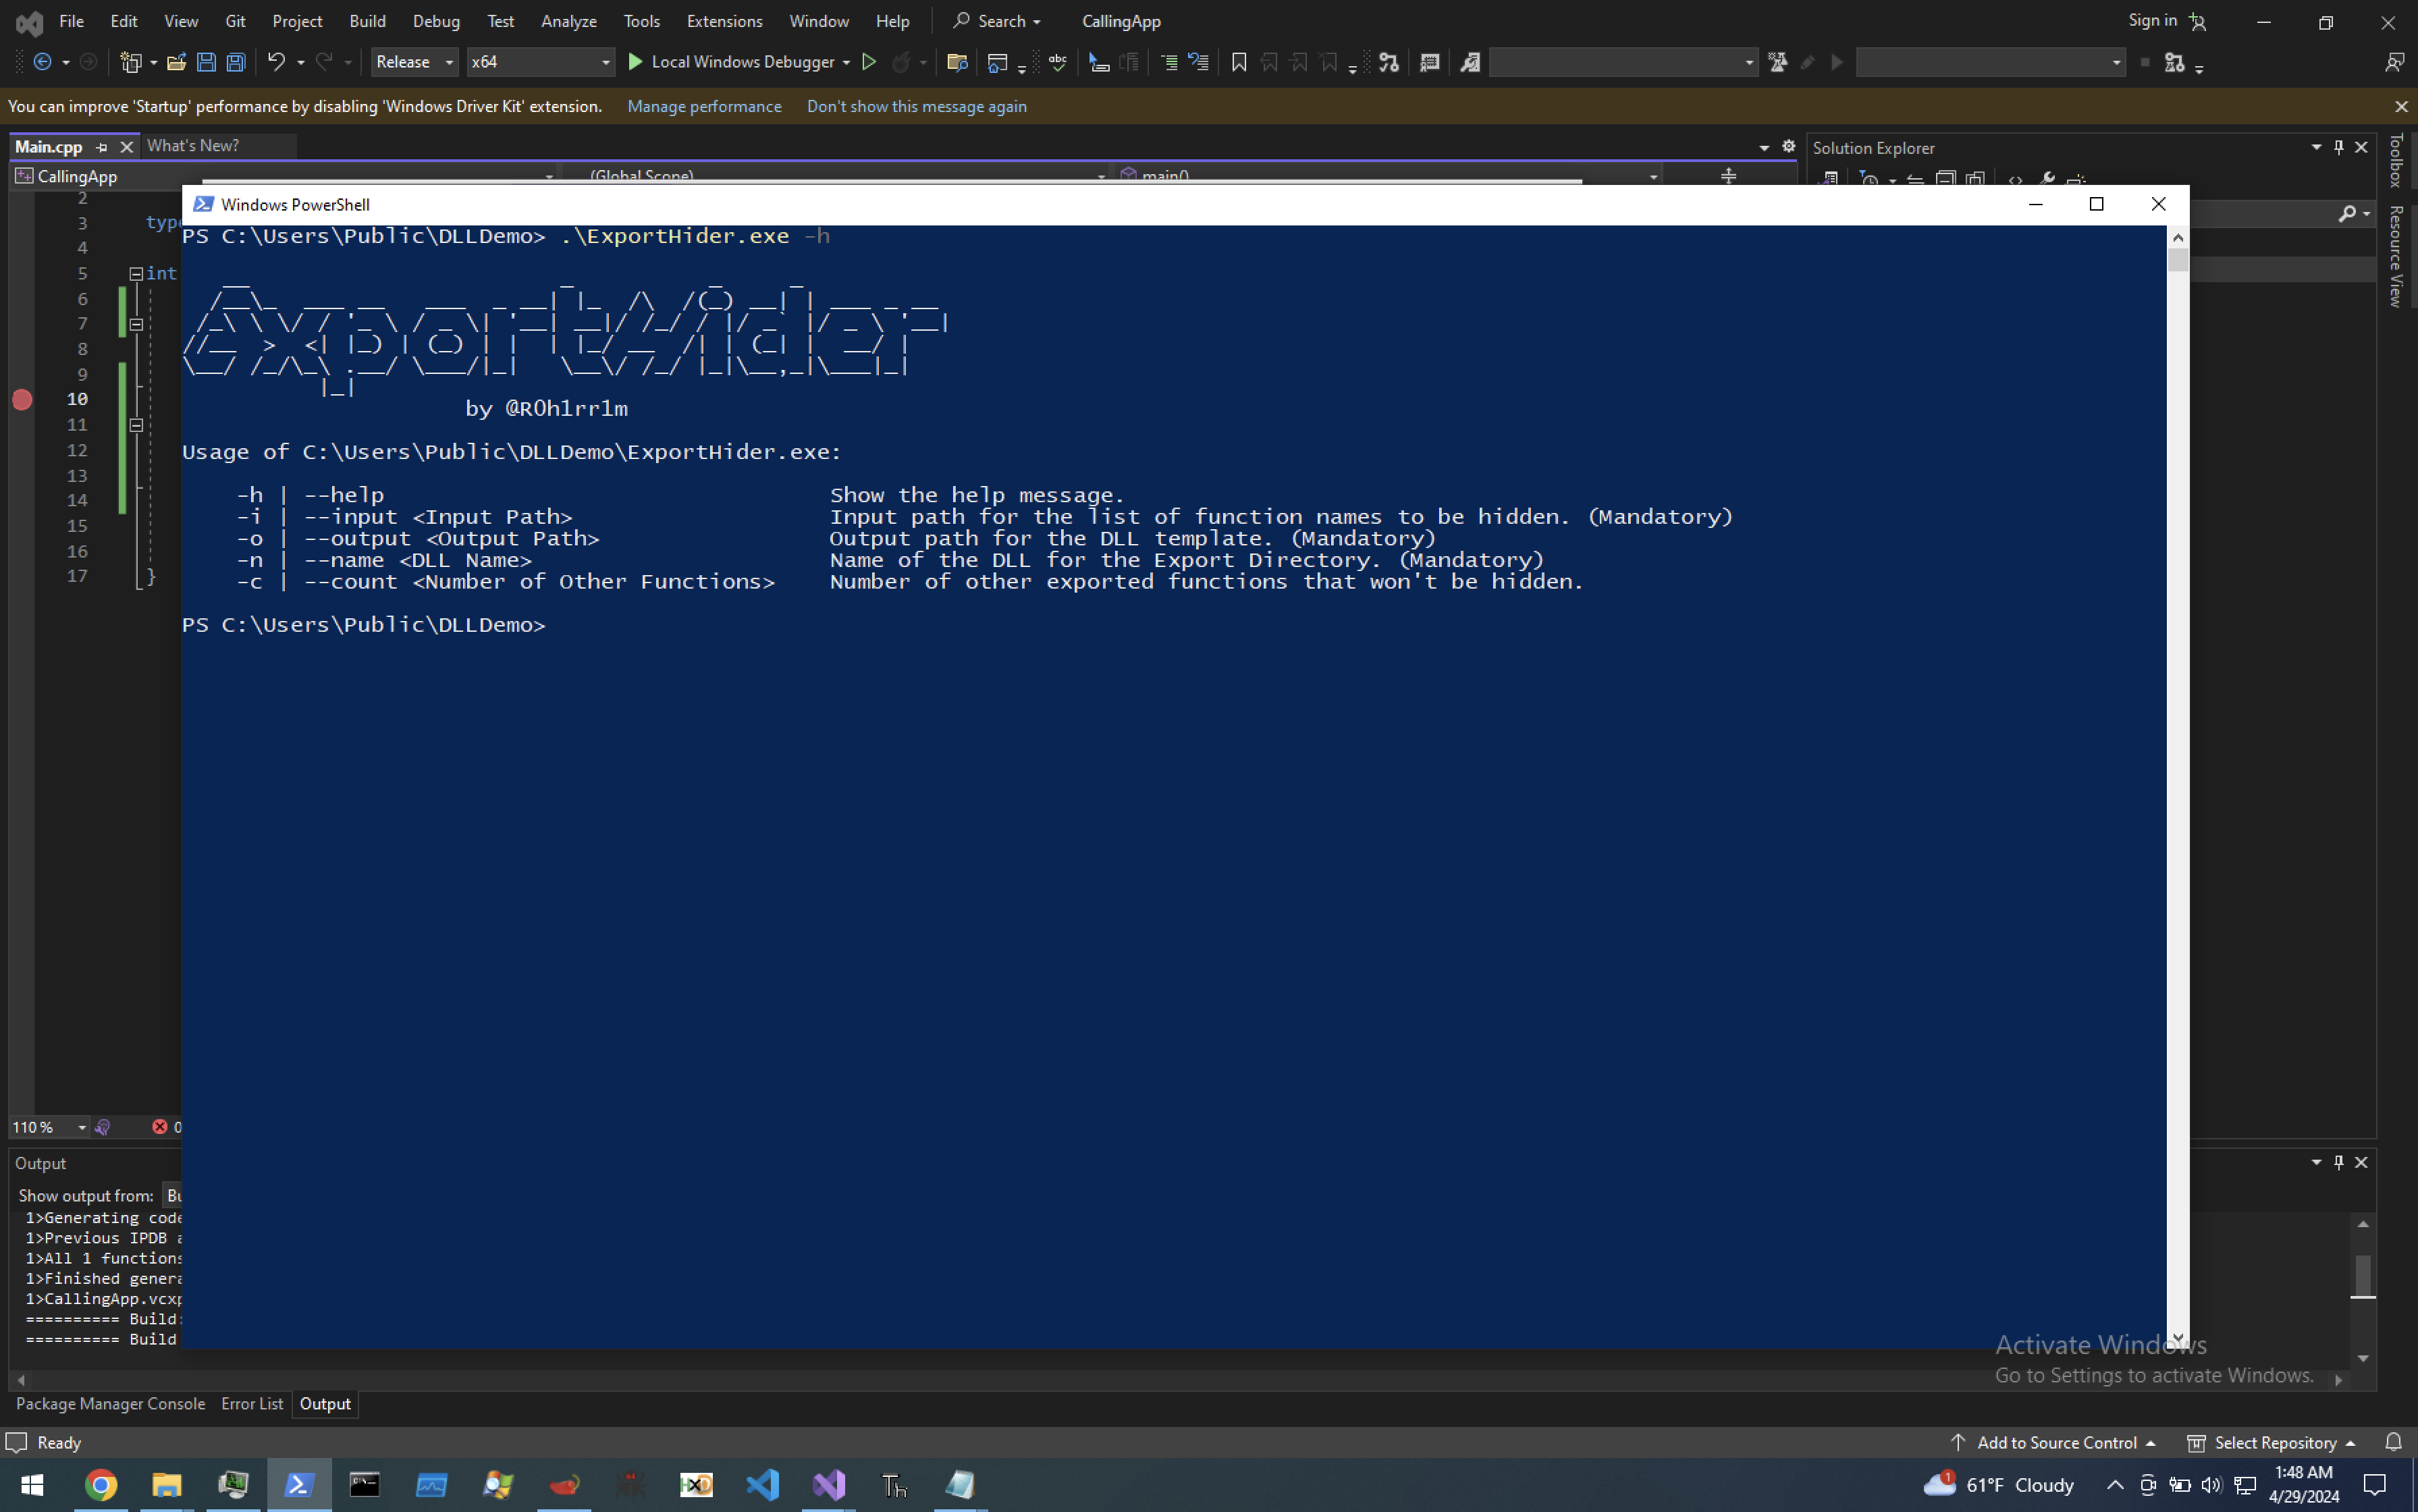
ExportHider
 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
binary-analysisdynamic-code-analysisexploitation+4
frkngksl/exporthiderExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
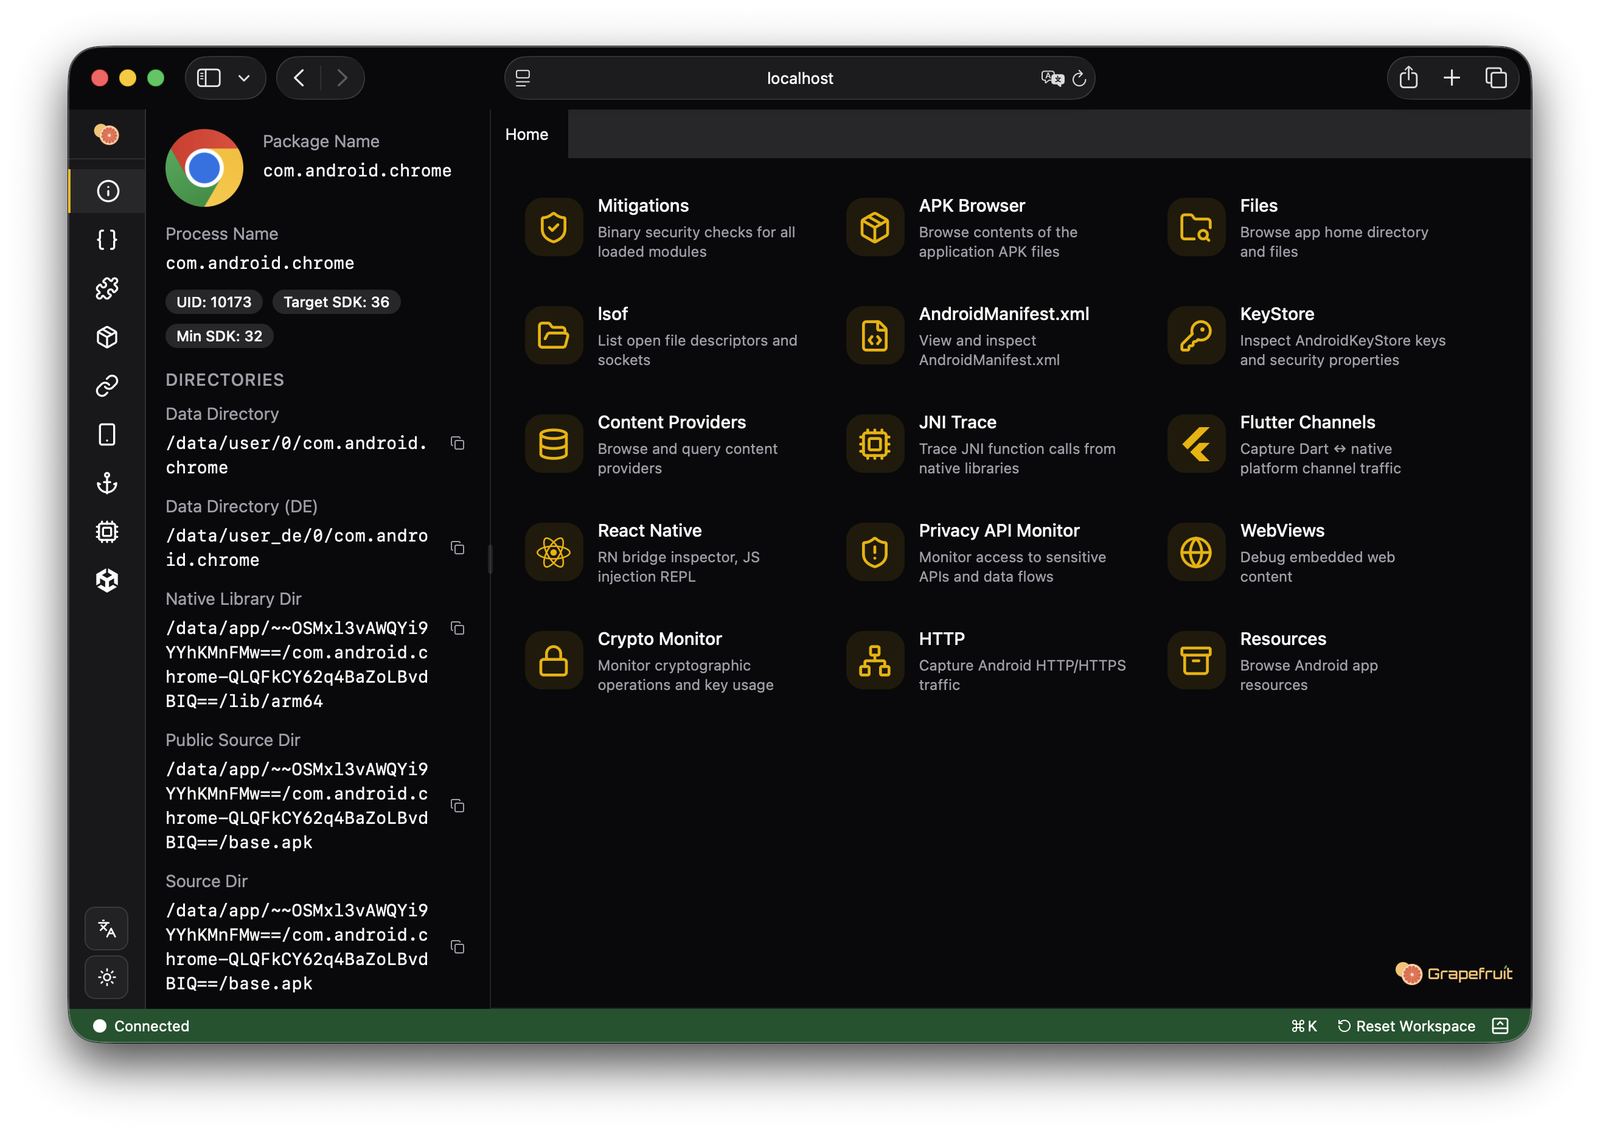 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 chichou/vscode-frida
Unofficial frida extension for VSCode
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
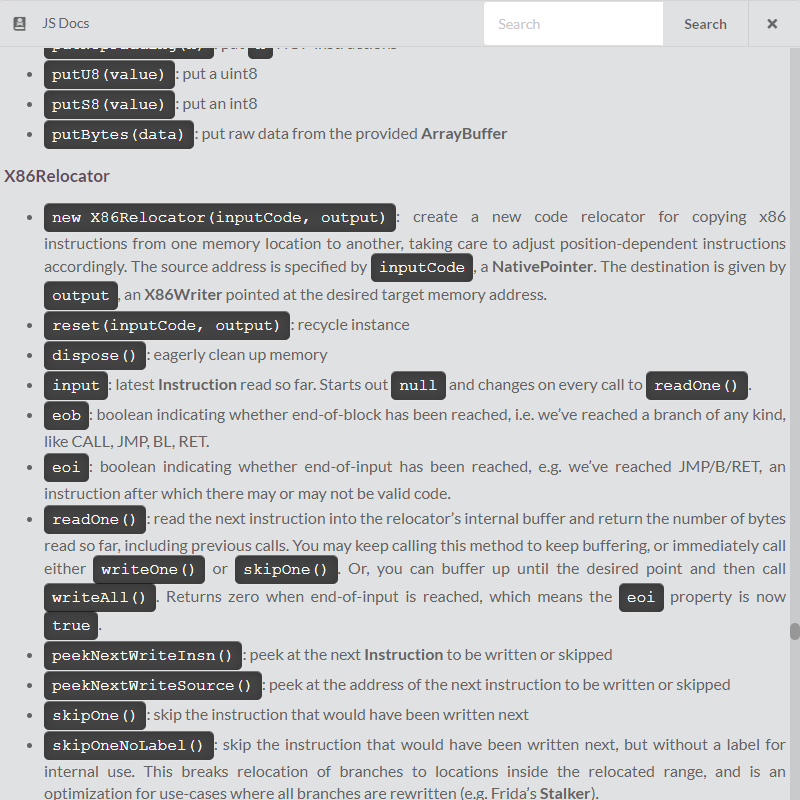 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 hacefresko/cve-2021-4045
Exploit for command injection vulnerability found in uhttpd binary from TP-Link Tapo c200 IP camera
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 oscarsantanaarias/ida-ghidra-bridge
TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…
 vichhka-git/universal-flutter-ssl-pinning
Automated SSL pinning bypass for any Flutter & Shorebird version — PyGhidra static analysis auto-discovers BoringSSL and generates ready-to-run Frida…