
zkar
 phith0n/zkar
Go-based Java serialization protocol analyzer that parses, dumps, and generates deserialization payloads with ysoserial gadget support and a library…
binary-analysisexploitationpayload-generation+1
653
phith0n/zkarGo-based Java serialization protocol analyzer that parses, dumps, and generates deserialization payloads with ysoserial gadget support and a library…
 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
 gamozolabs/applepie
A hypervisor for fuzzing built with WHVP and Bochs
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
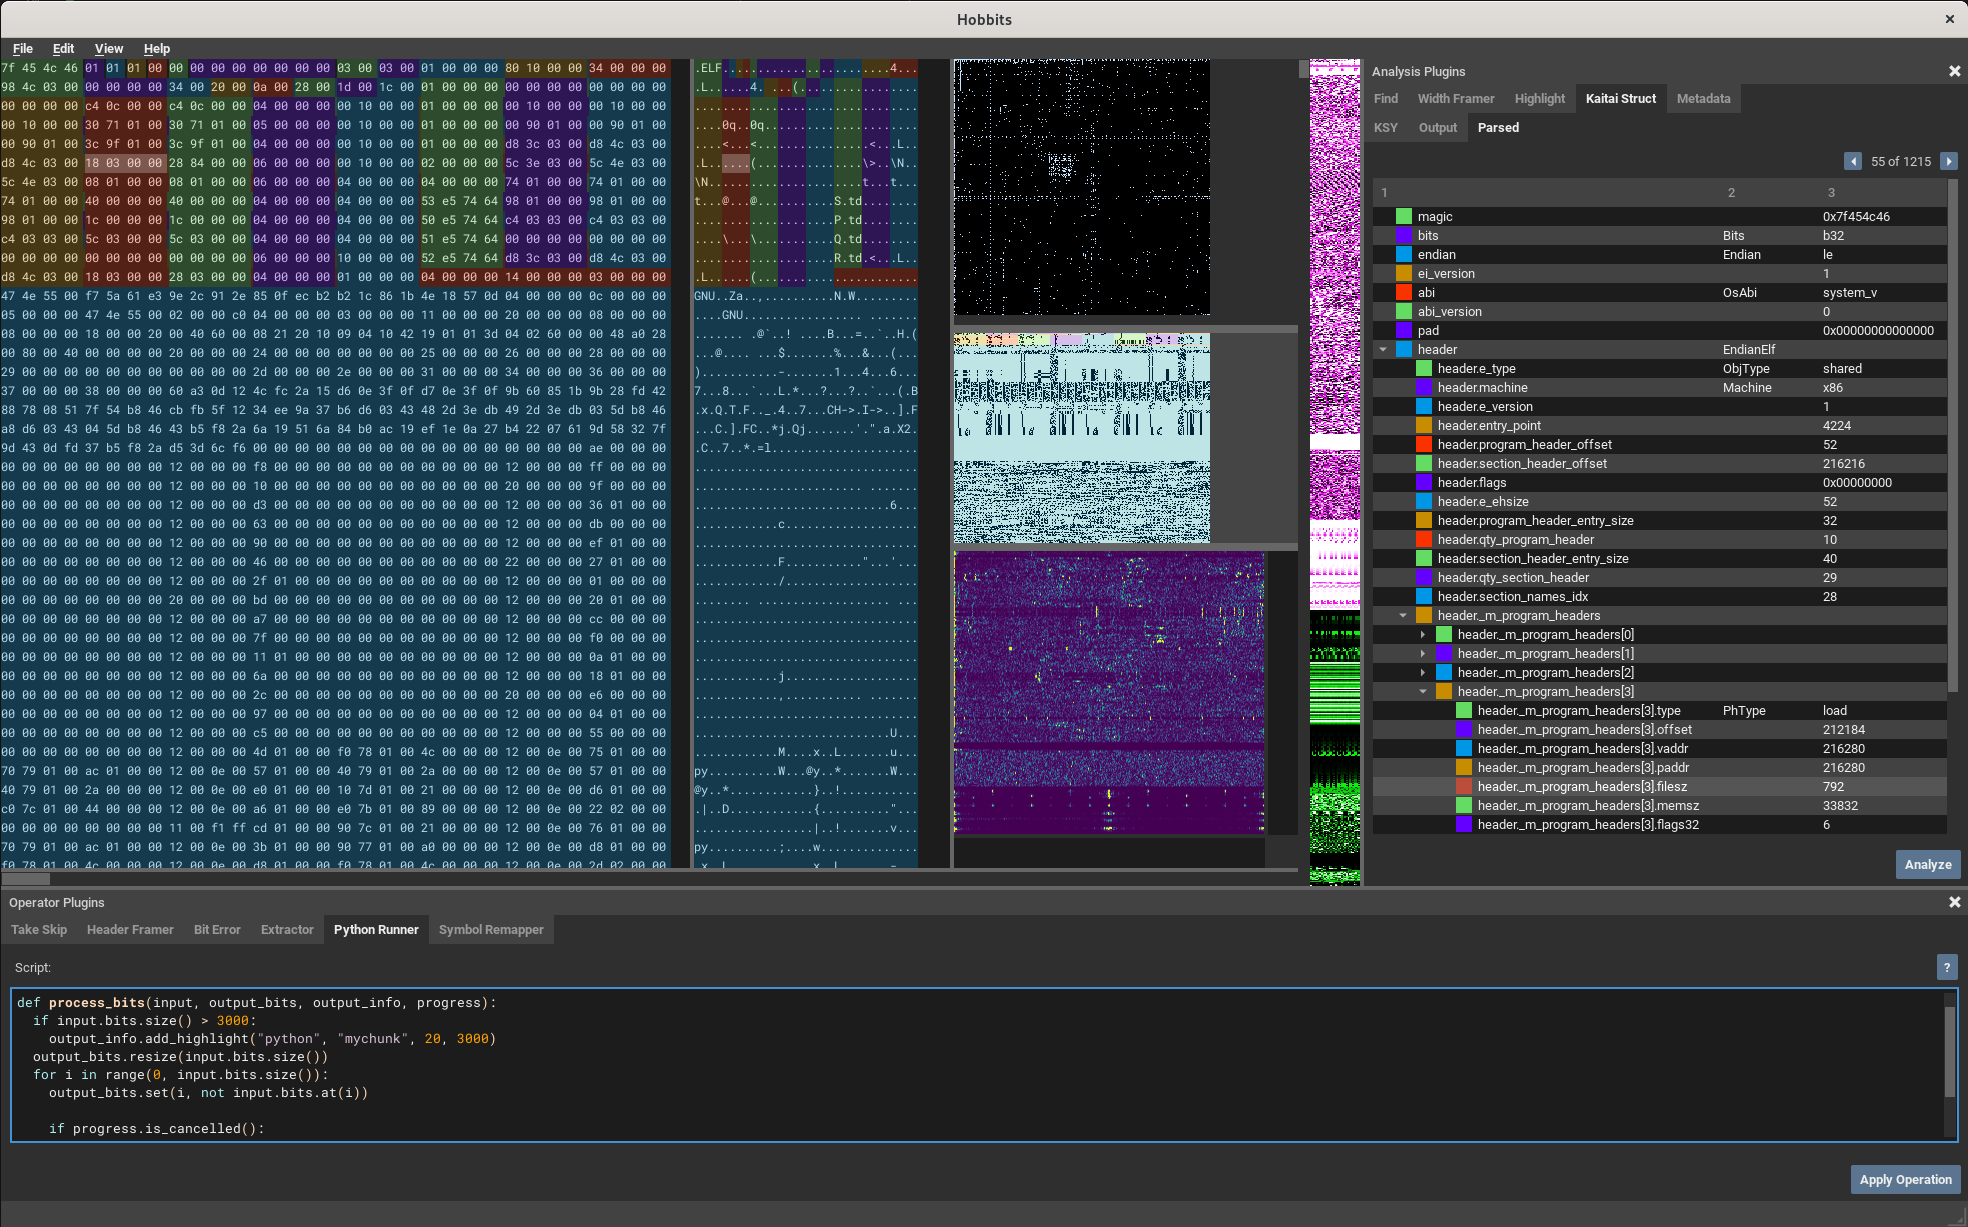 mahlet-inc/hobbits
A multi-platform GUI for bit-based analysis, processing, and visualization
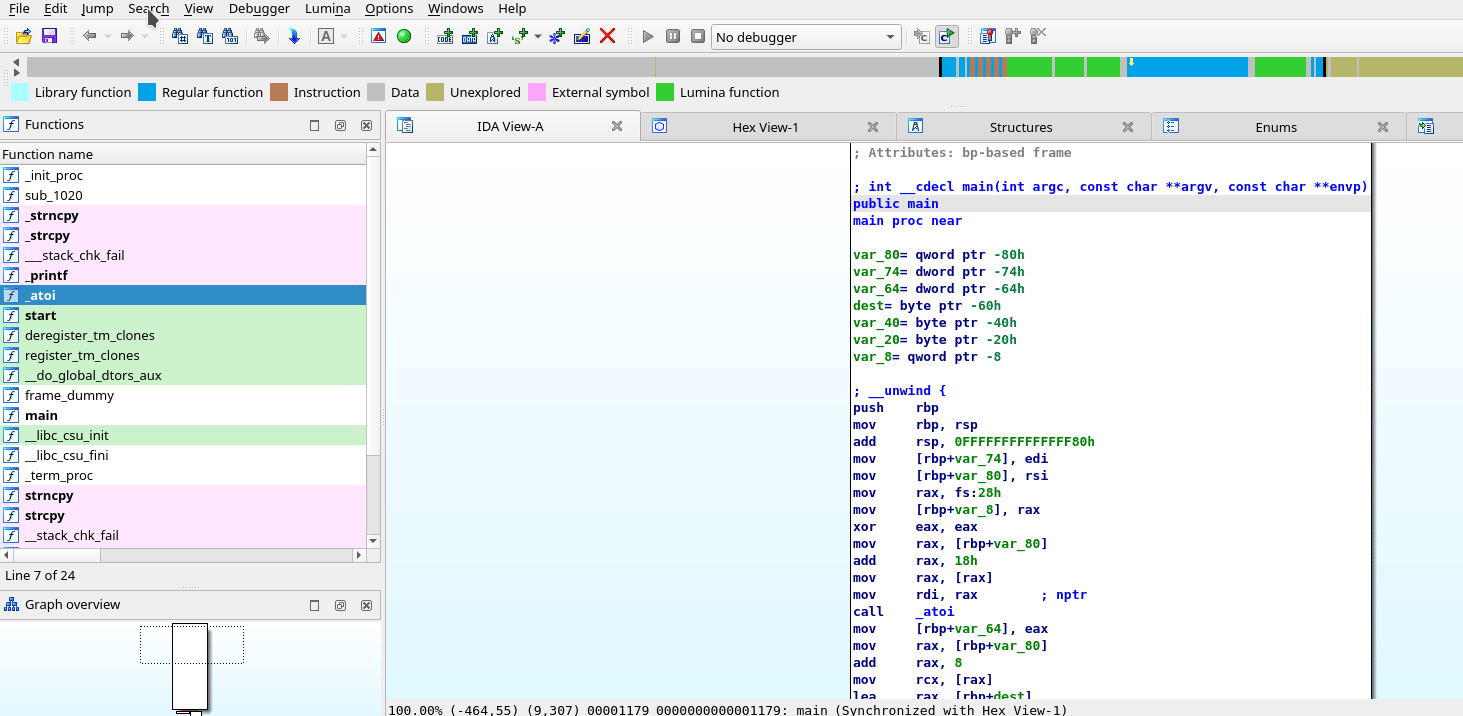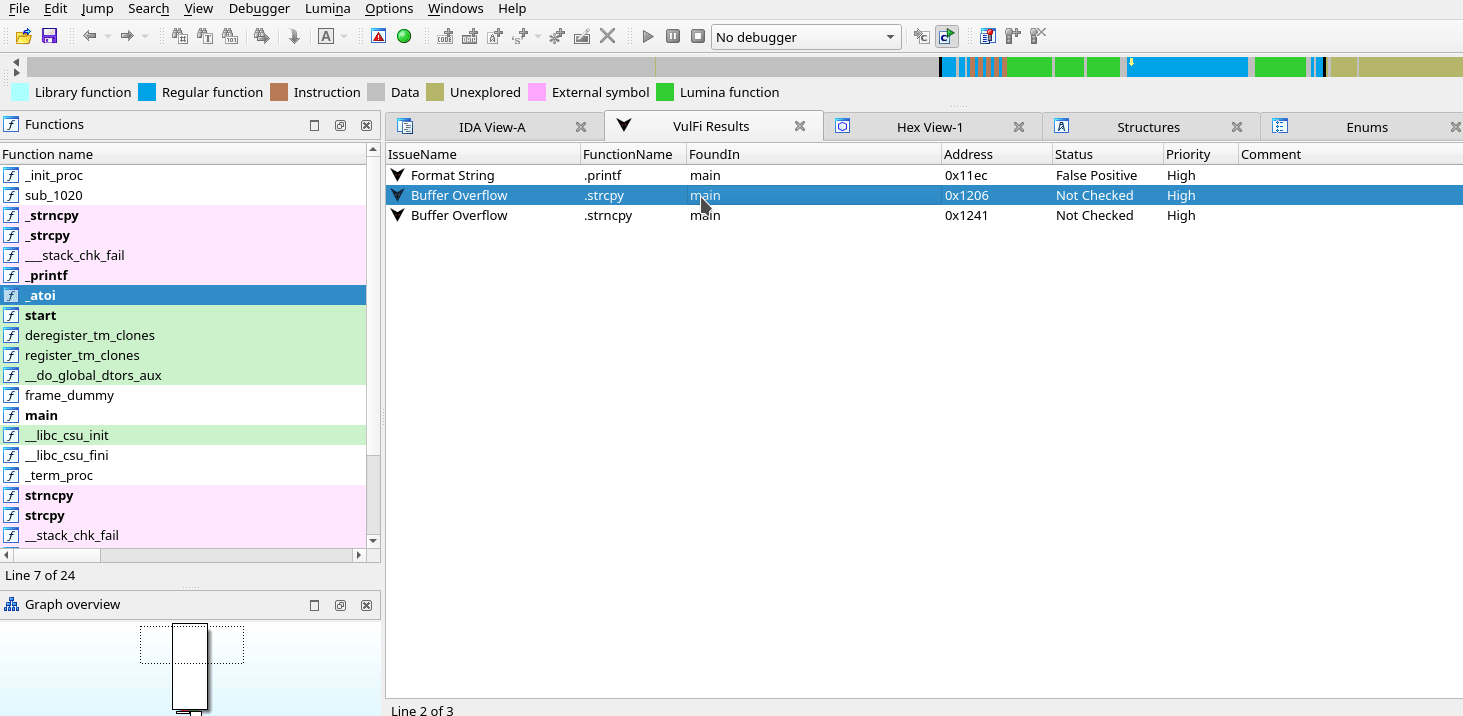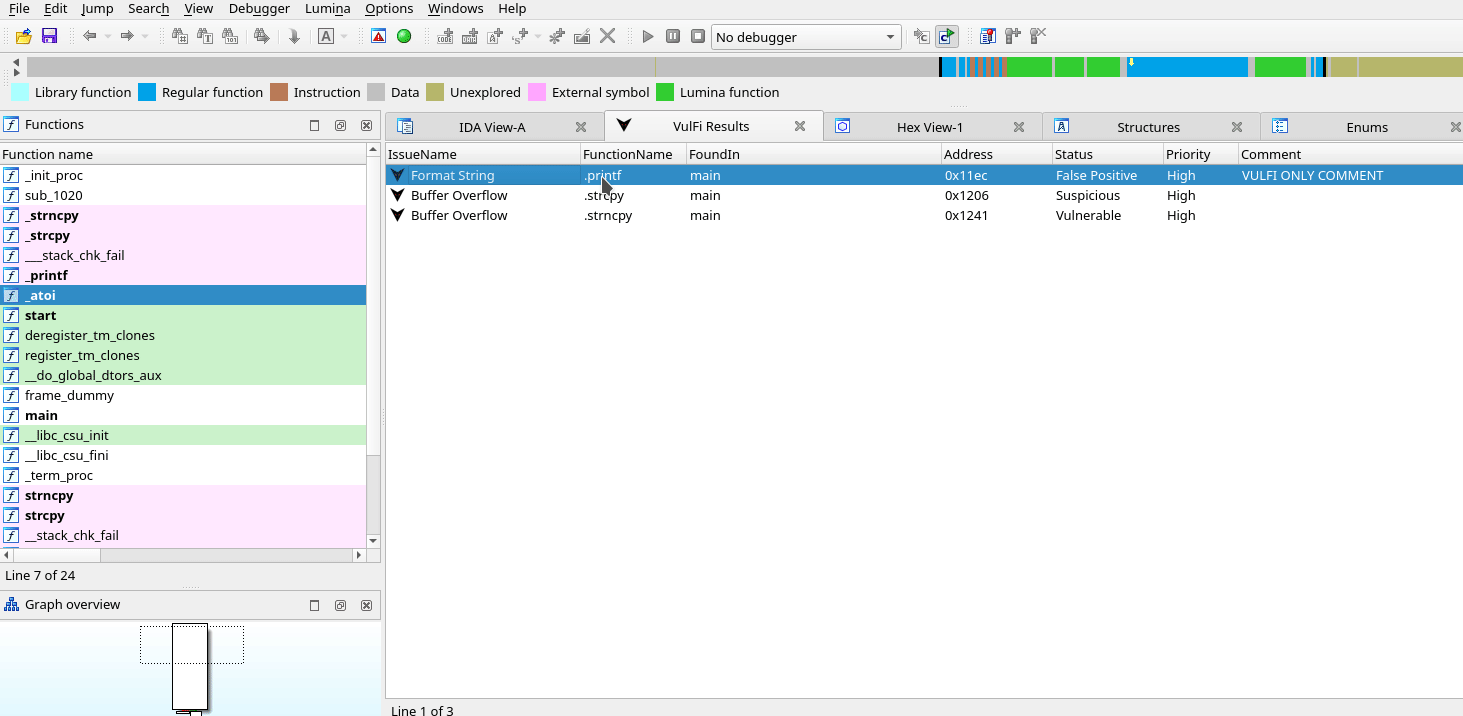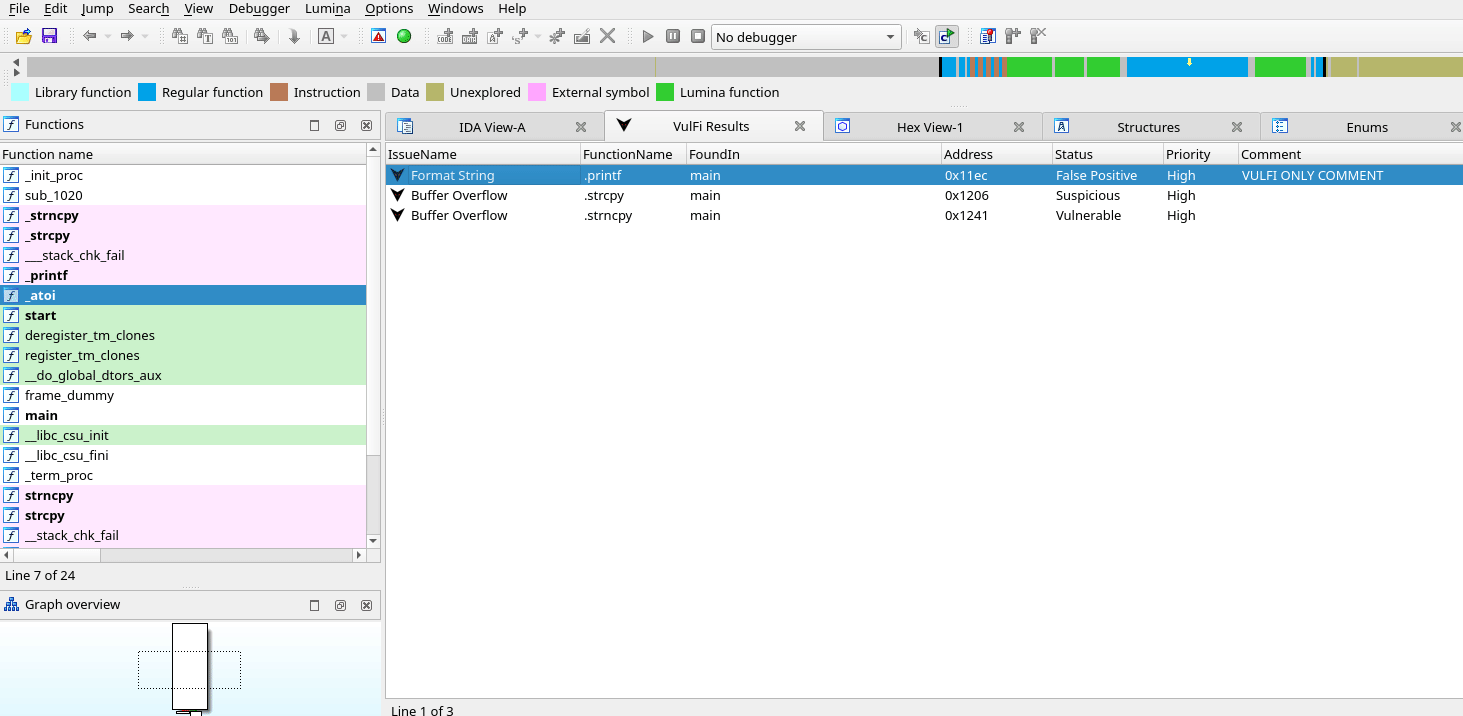 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
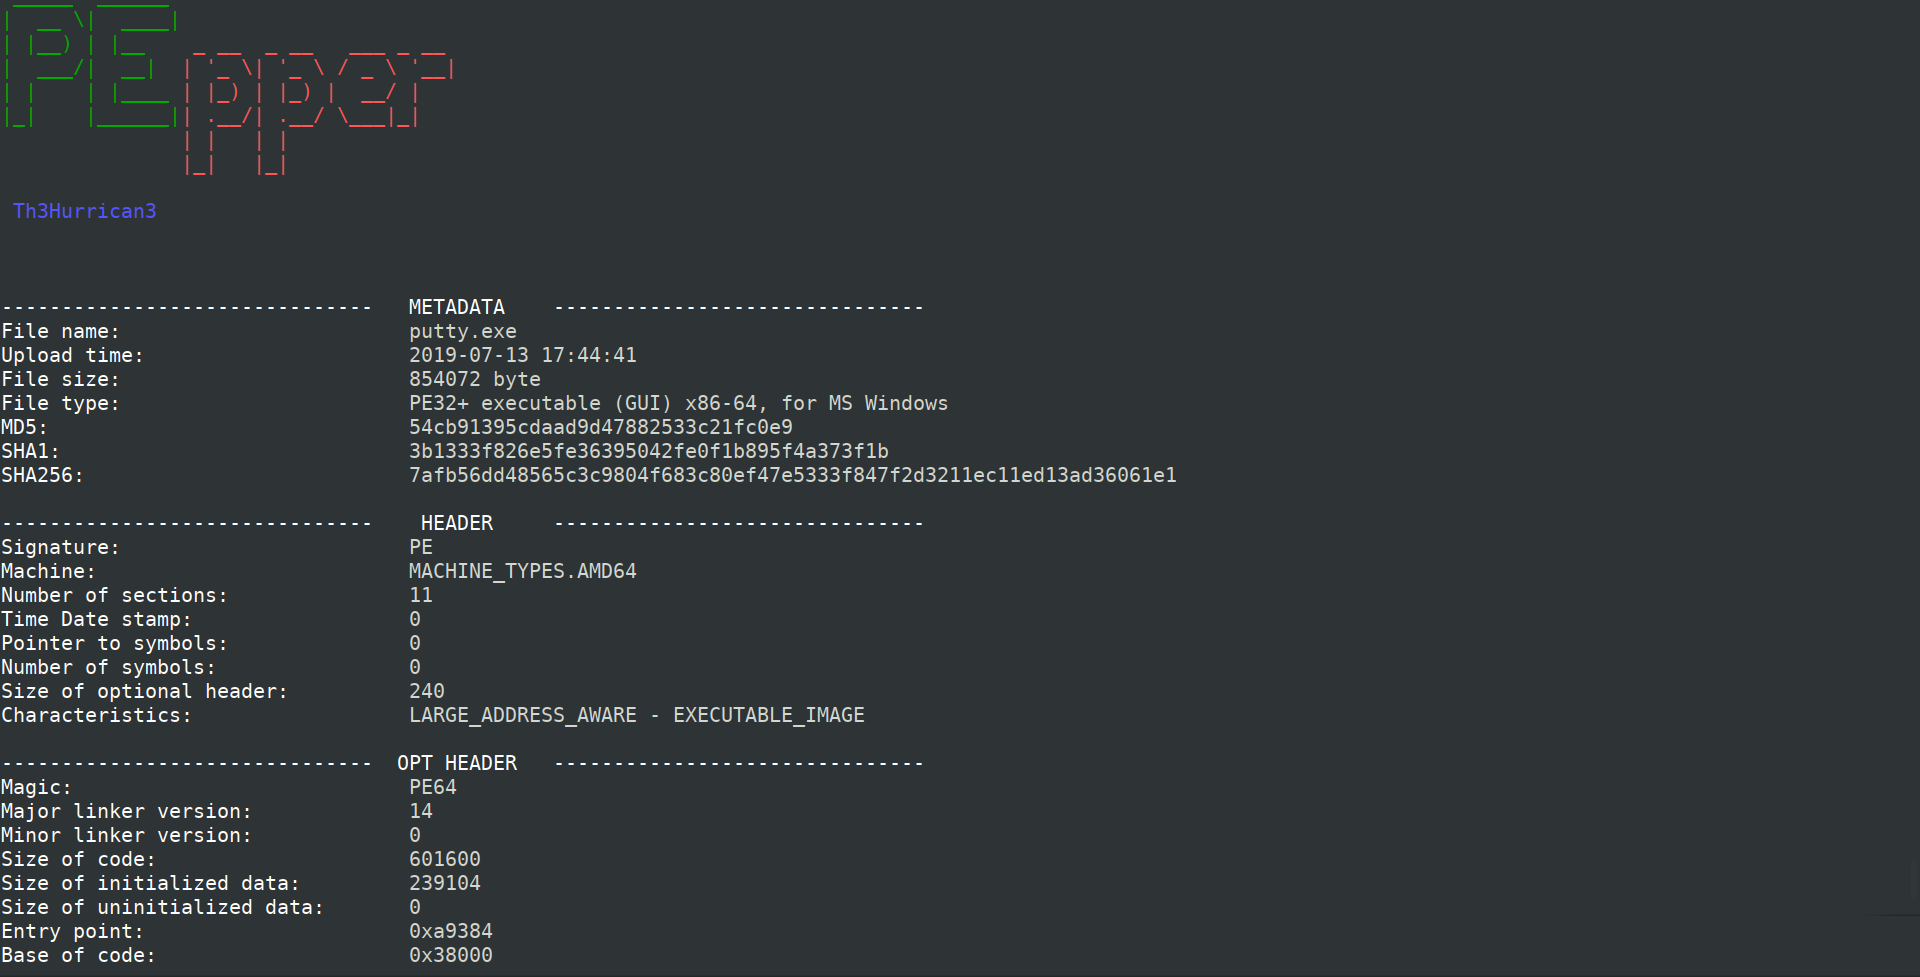 0x0be/pepper
An open source script to perform malware static analysis on Portable Executable
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
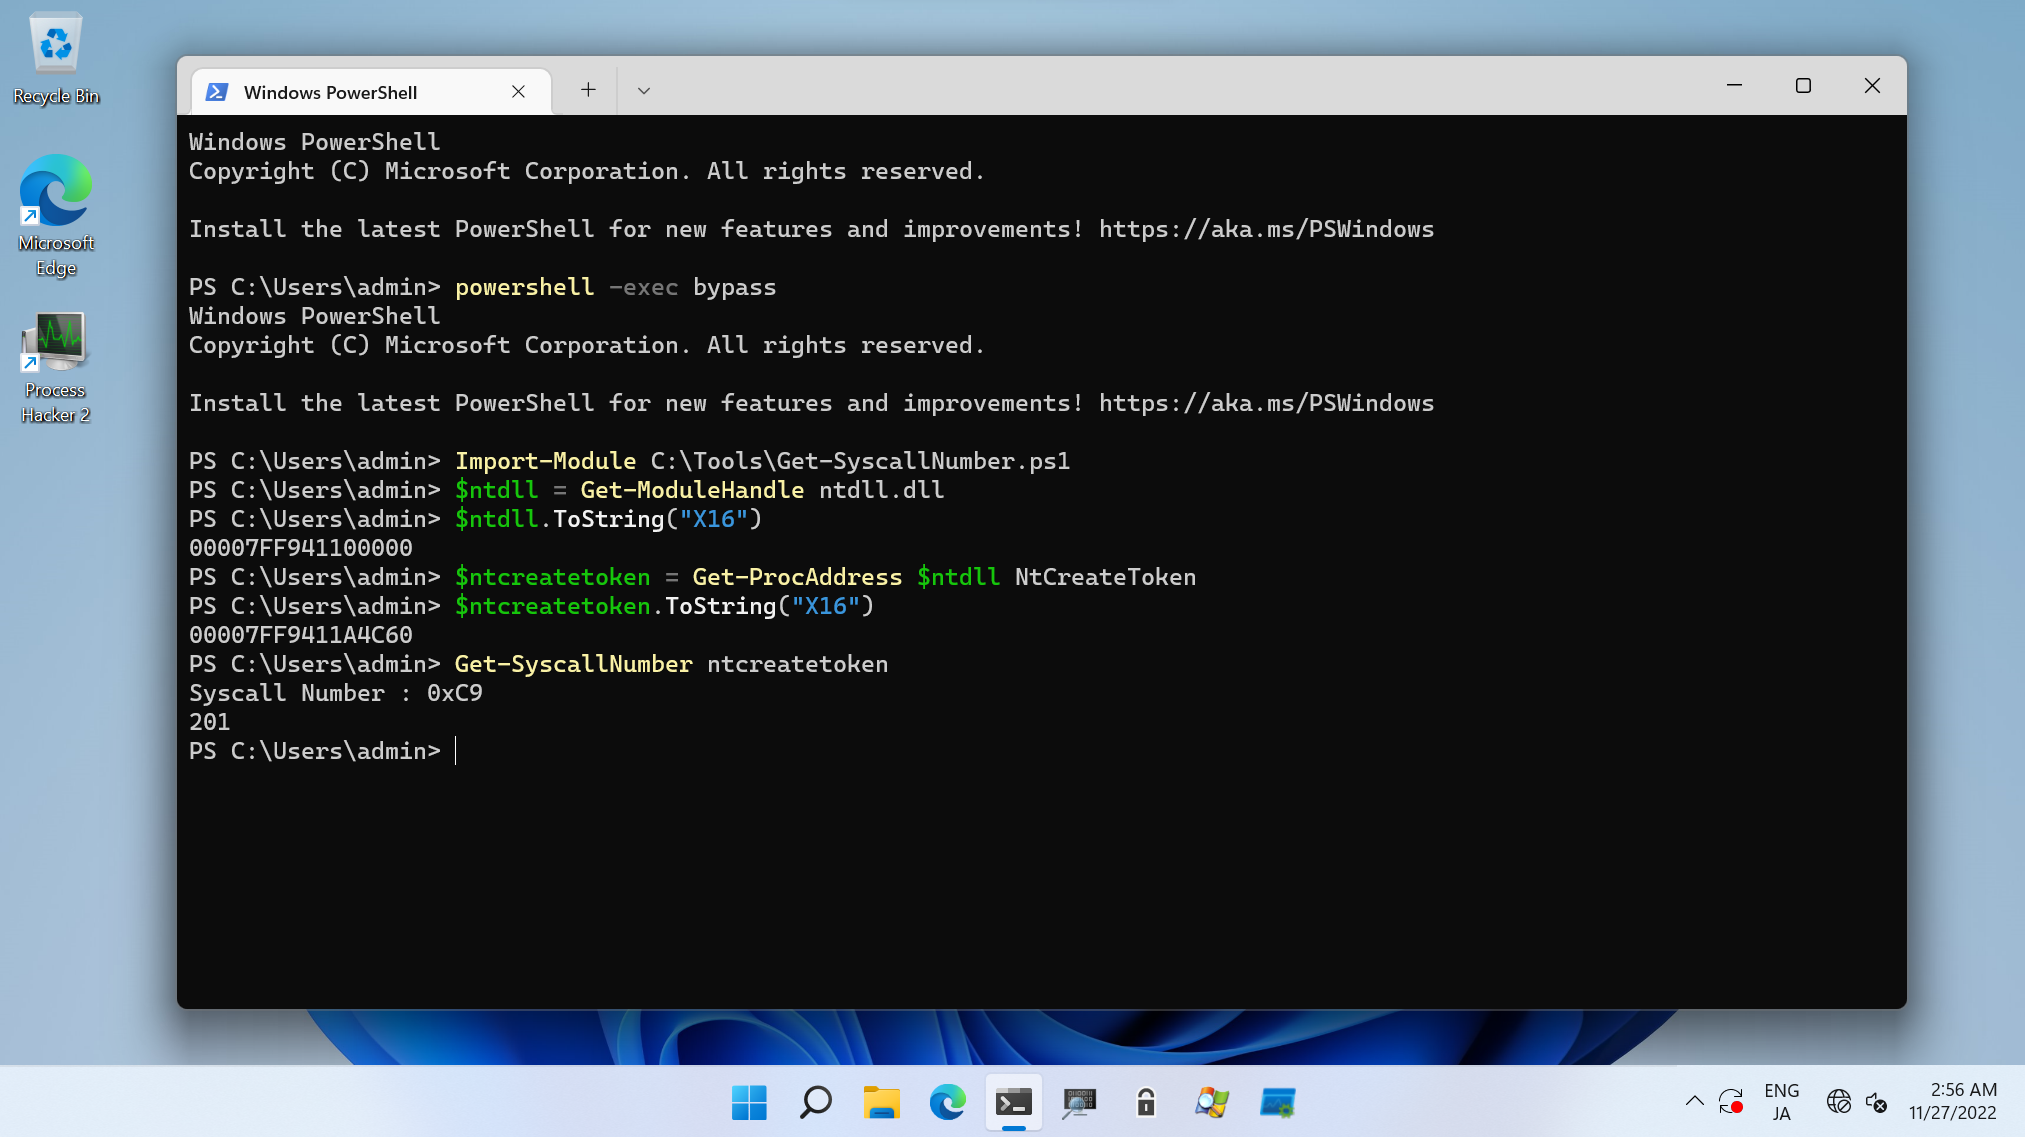 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 helixo32/crimsonedr
Simulate the behavior of AV/EDR for malware development training.
 secrary/infectpe
InfectPE - Inject custom code into PE file [This project is not maintained anymore]
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
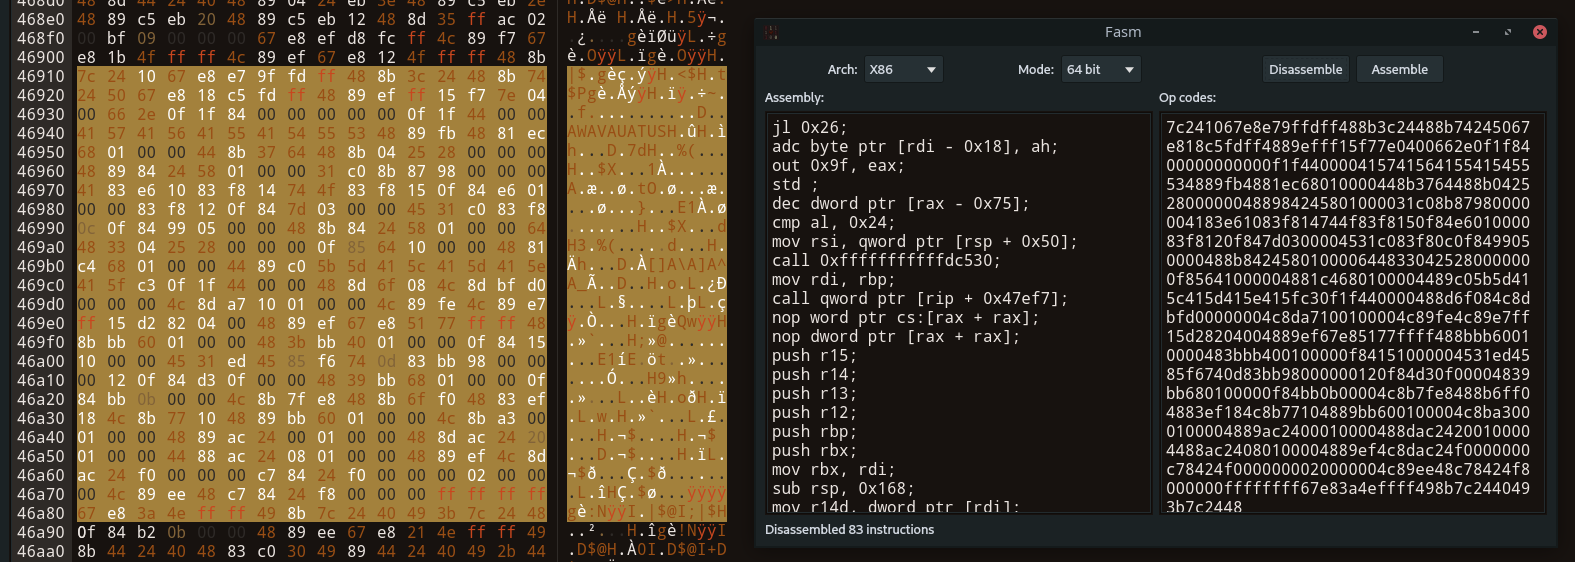 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs