

jscd
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
binary-analysiscode-analysisdynamic-code-analysis+4
ejfkdev/jscdReverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 binsec/xyntia
Xyntia, the black-box deobfuscator
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
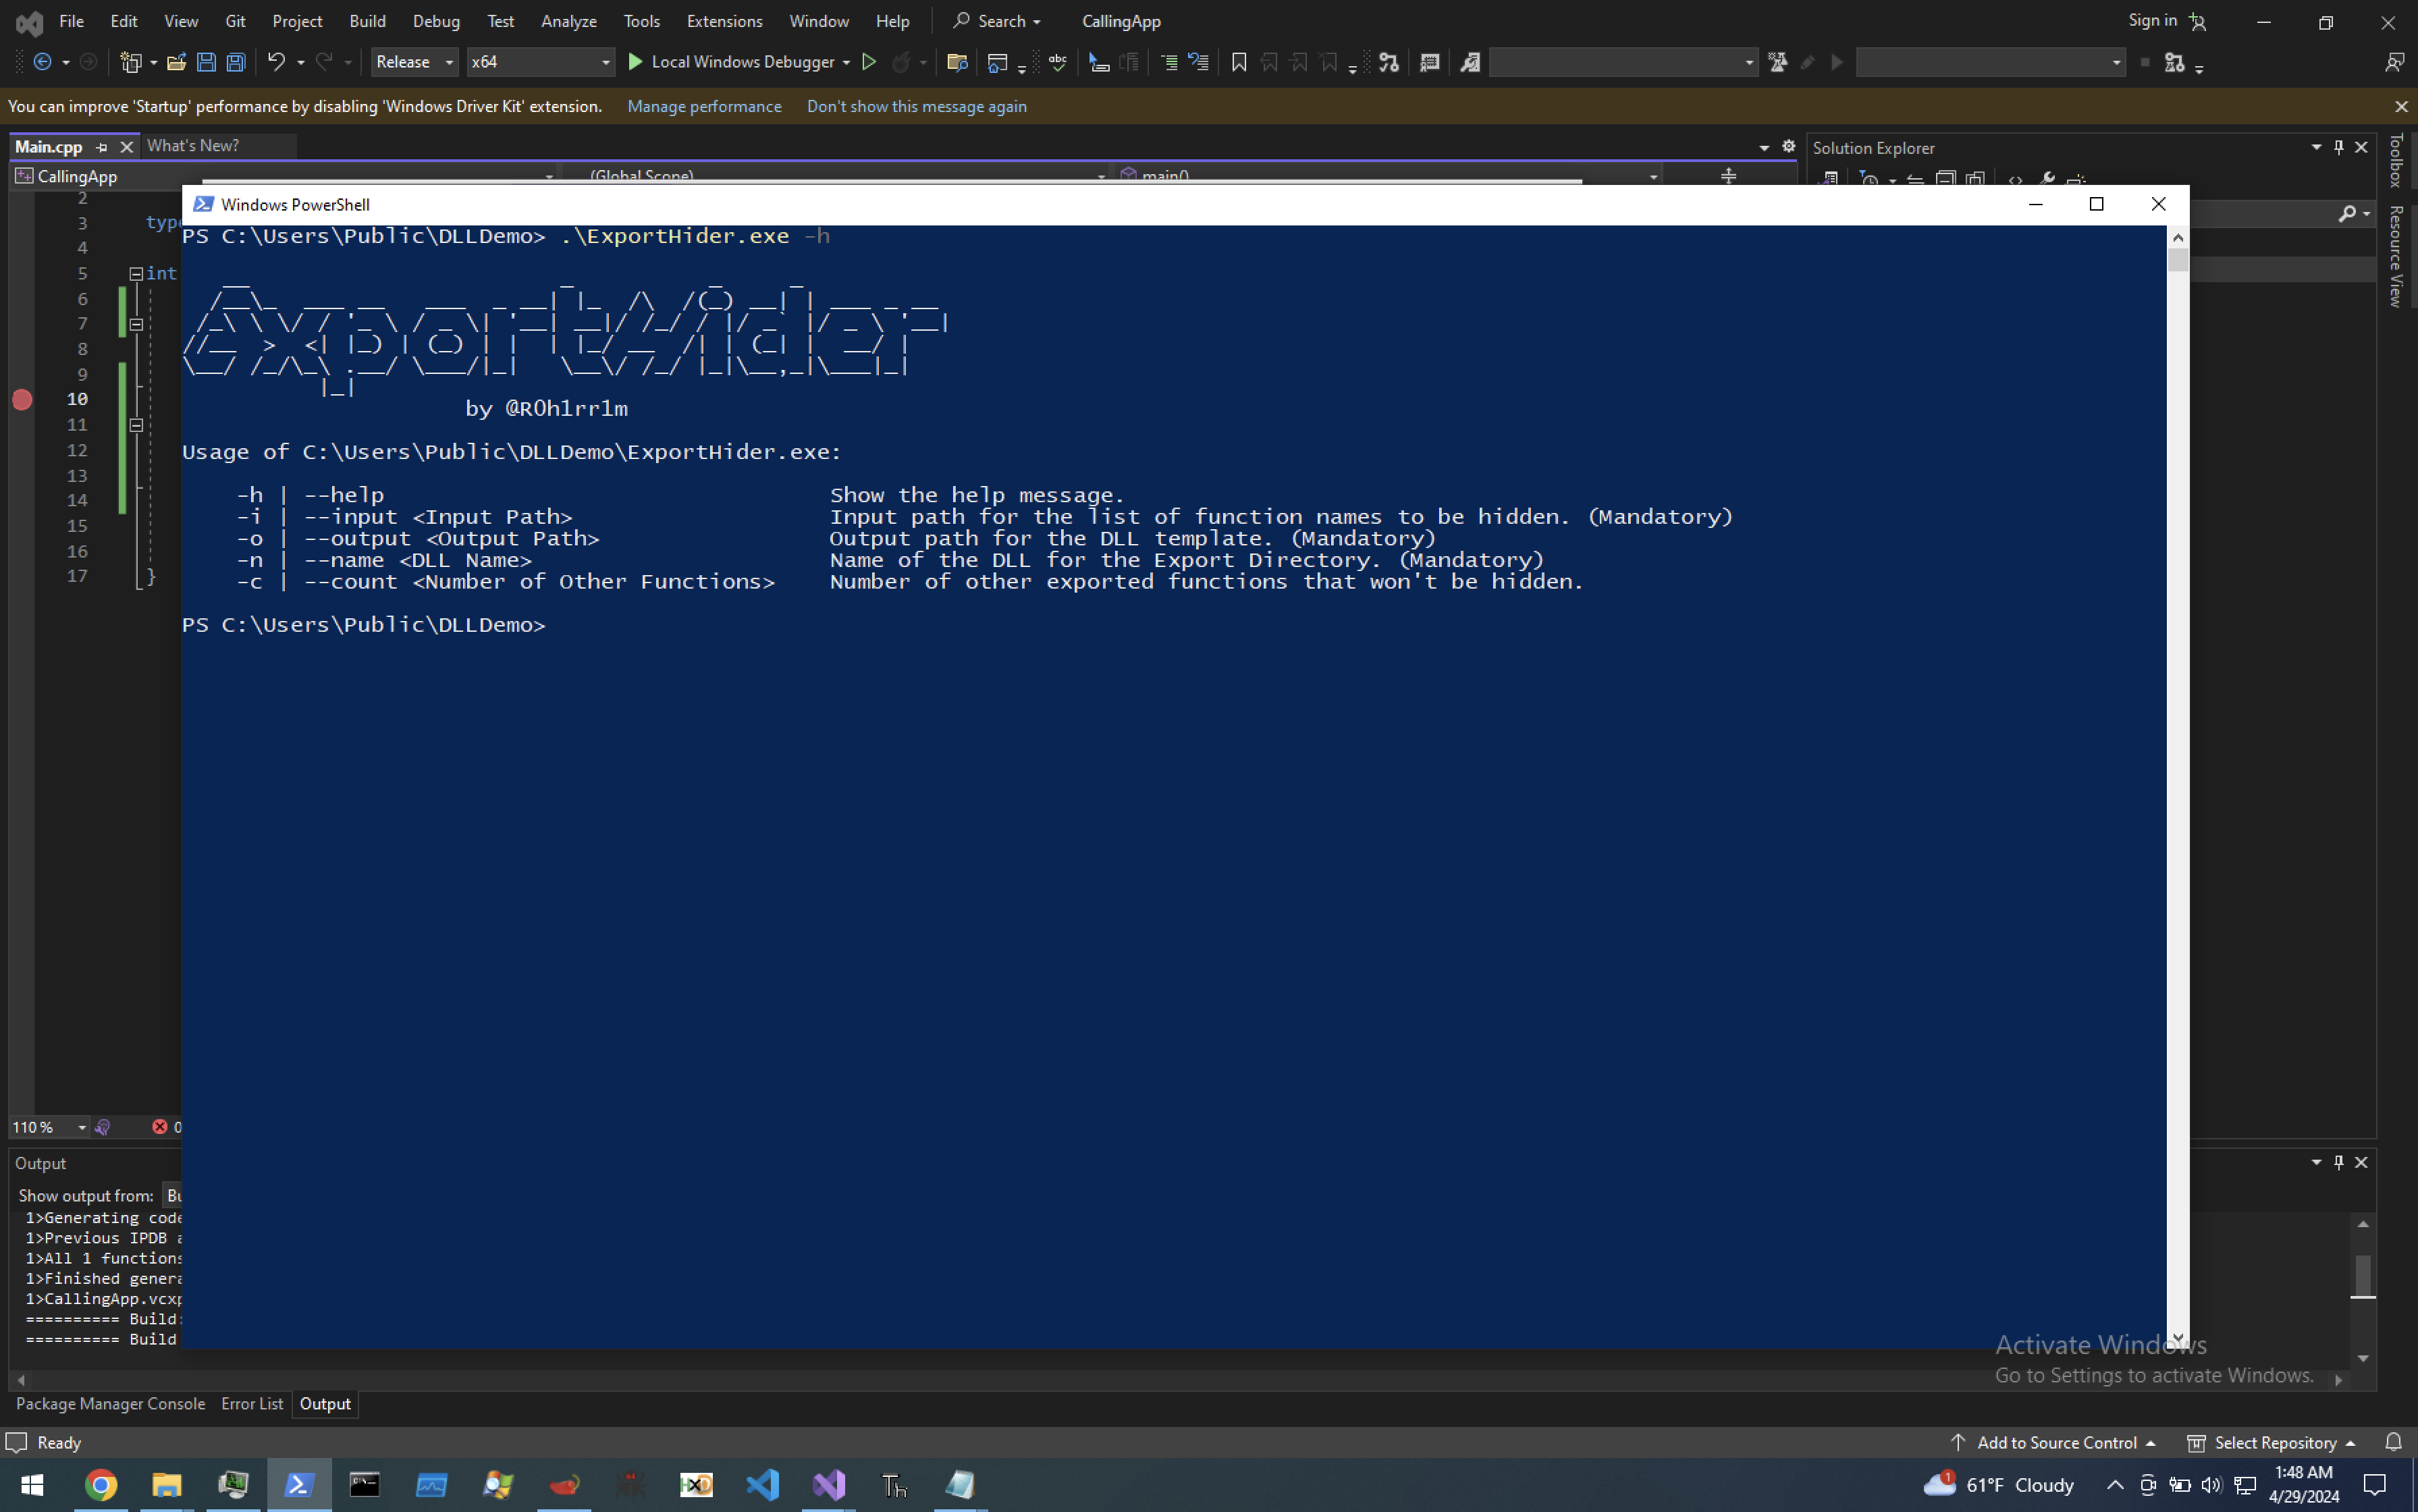 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
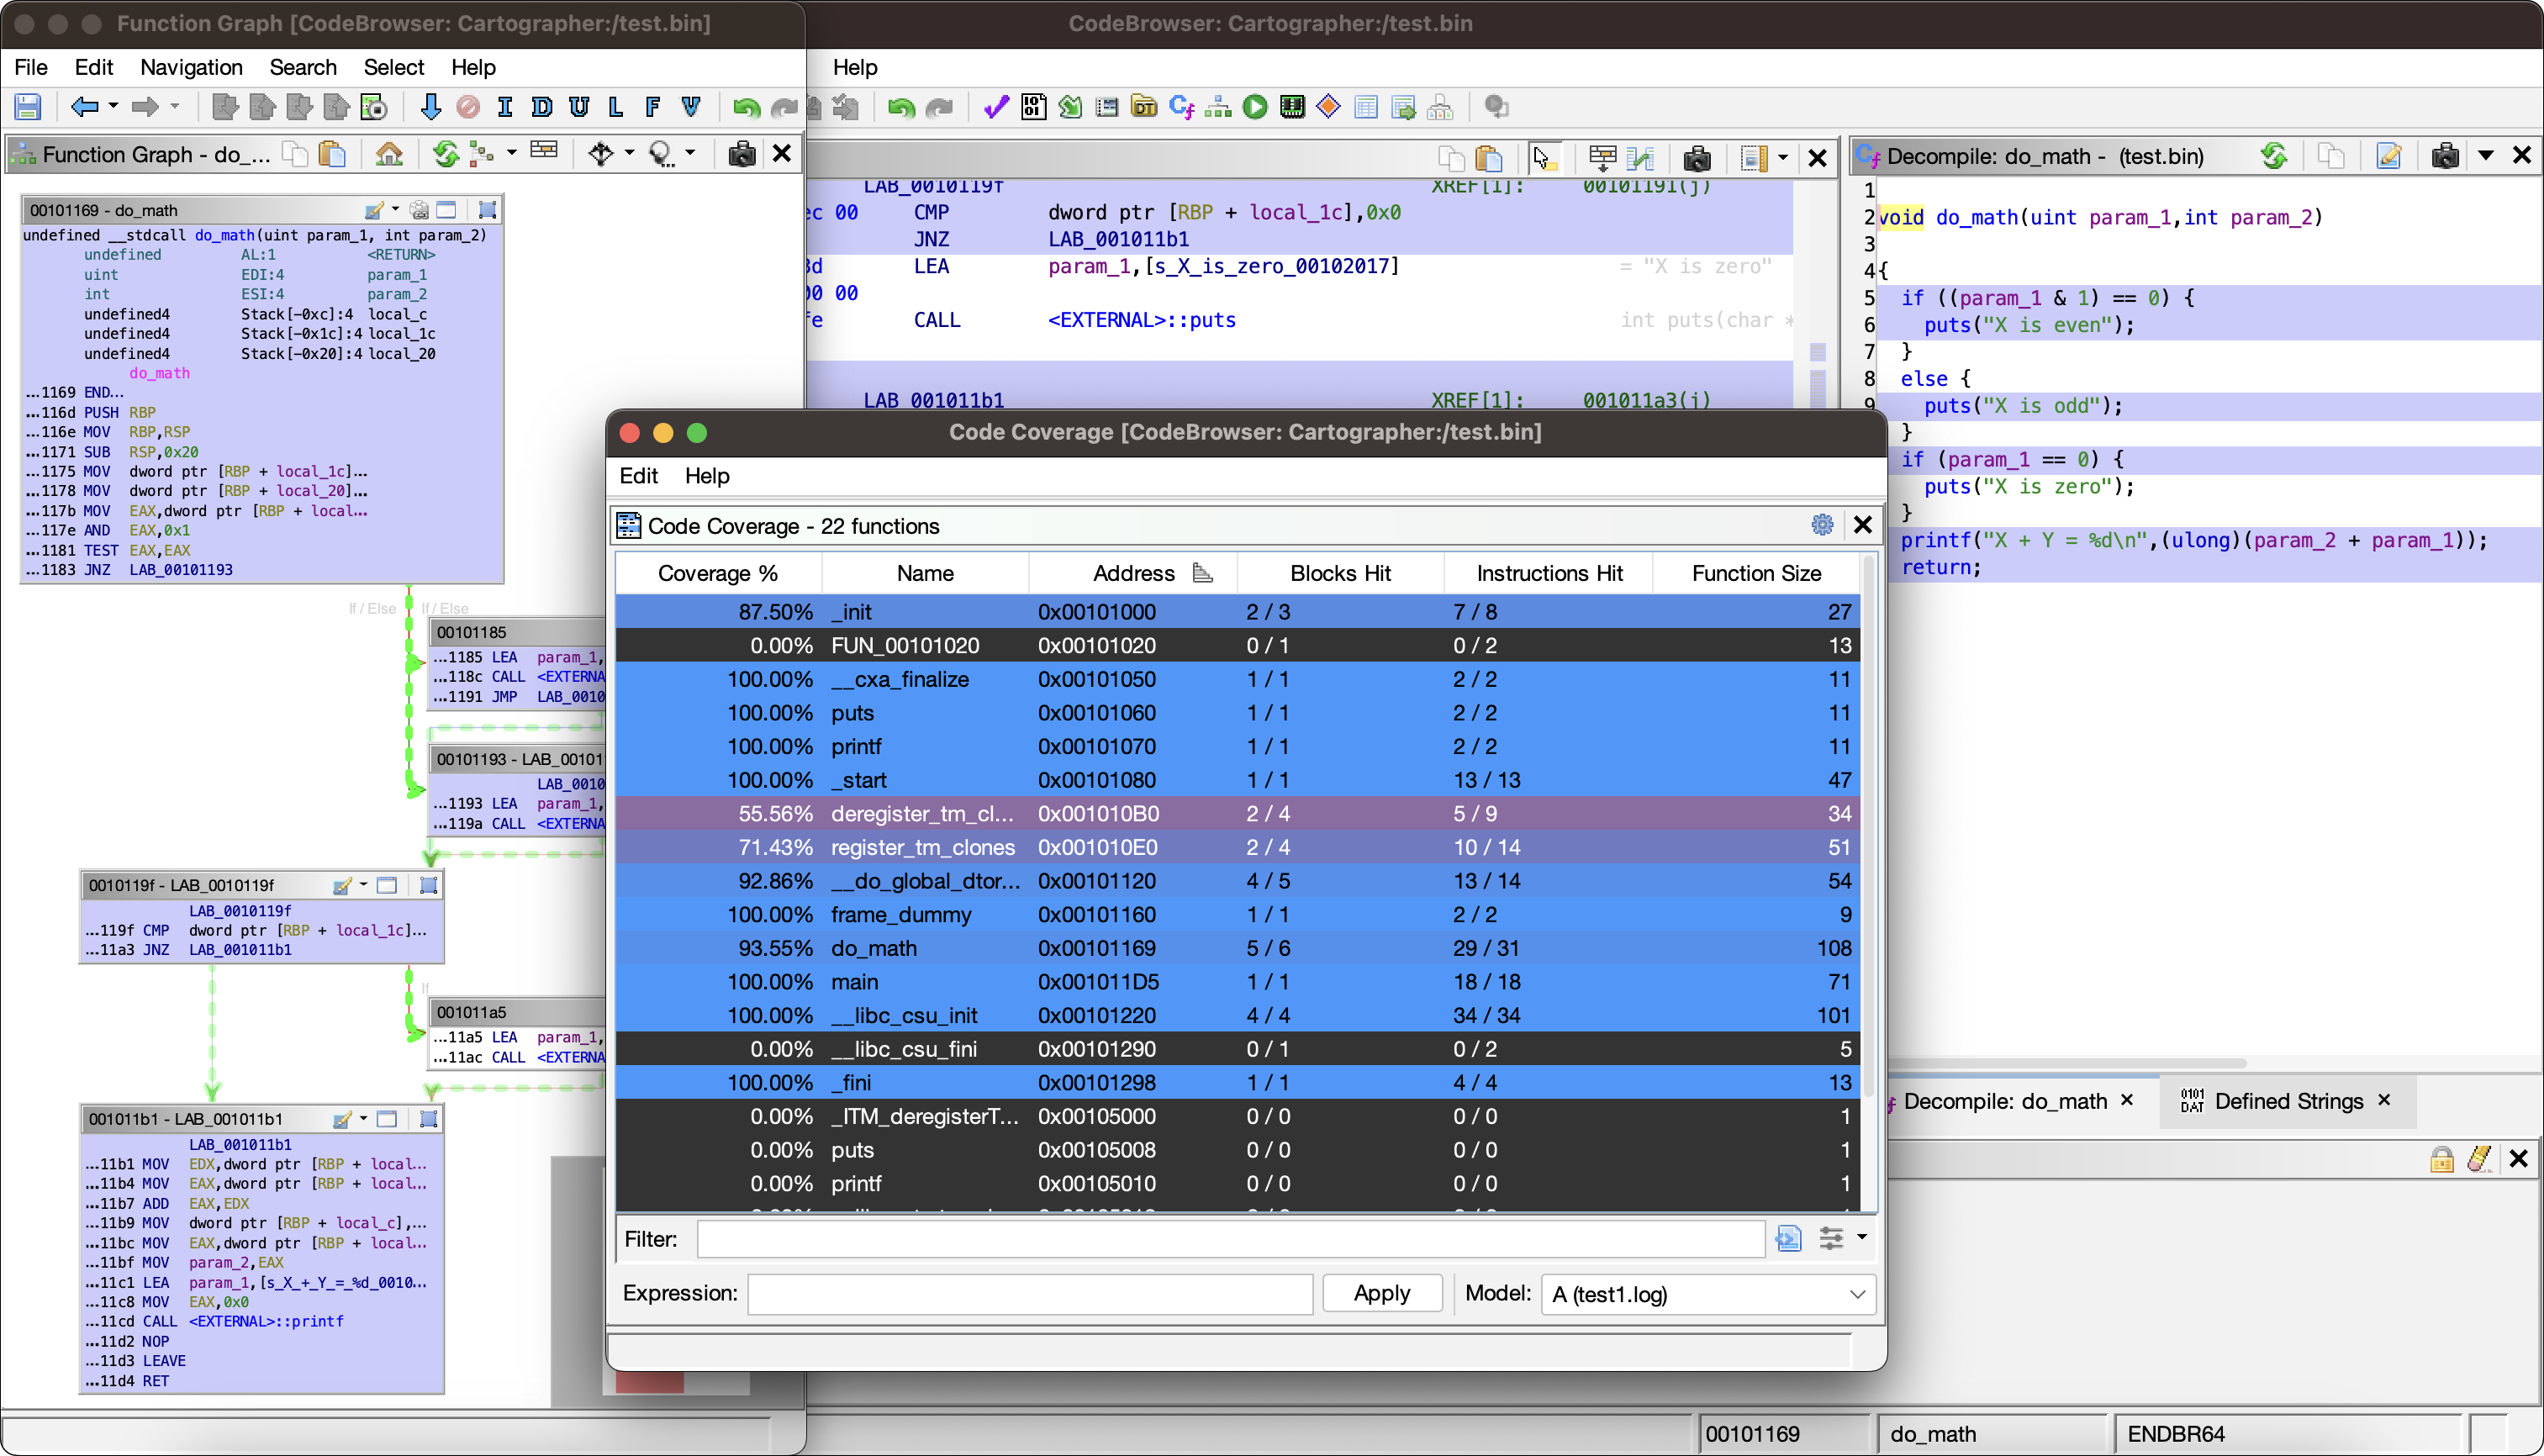 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 hasherezade/pesieve-go
Golang bindings for PE-sieve