

frida
 frida/frida
Main repo for hosting release binaries
android-securitybinary-analysiscode-analysis+9
frida/fridaMain repo for hosting release binaries
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
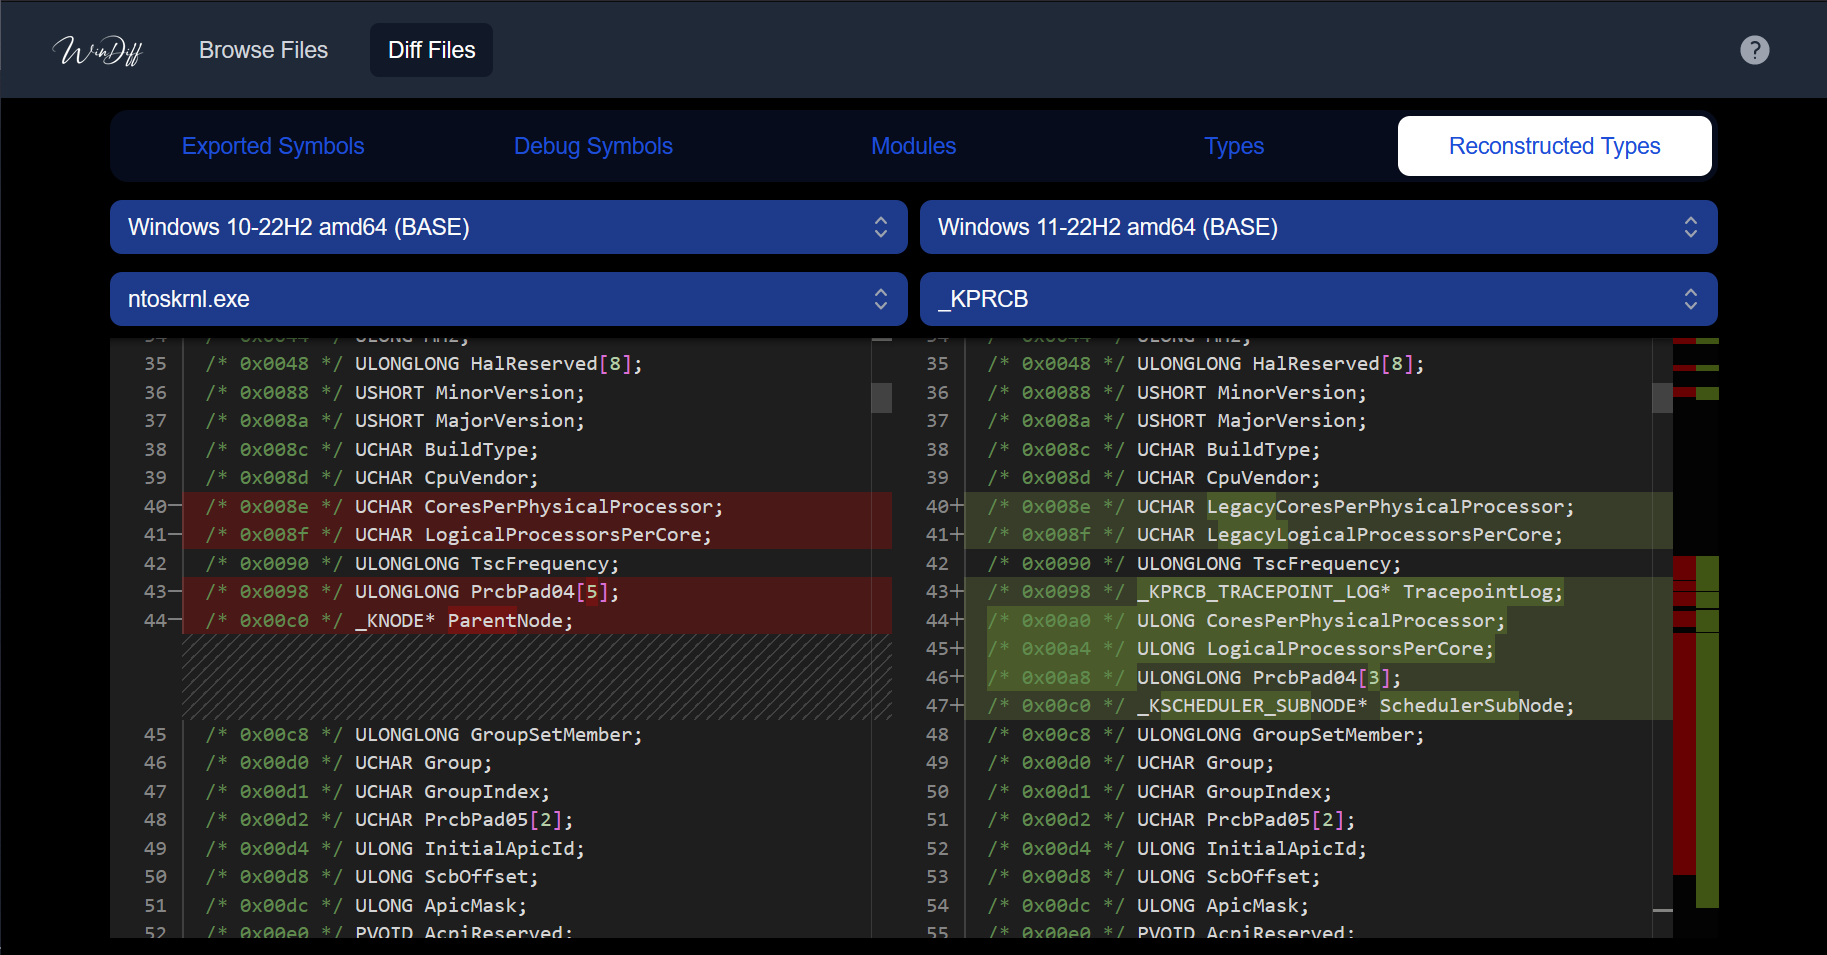 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 kikiuuw/cve-2025-68921
Analyze and demonstrate the local privilege escalation vulnerability (CVE-2025-68921) in Nahimic audio software on gaming laptops, with automated…
 nmatt0/moria
IoT firmware identification and extraction
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
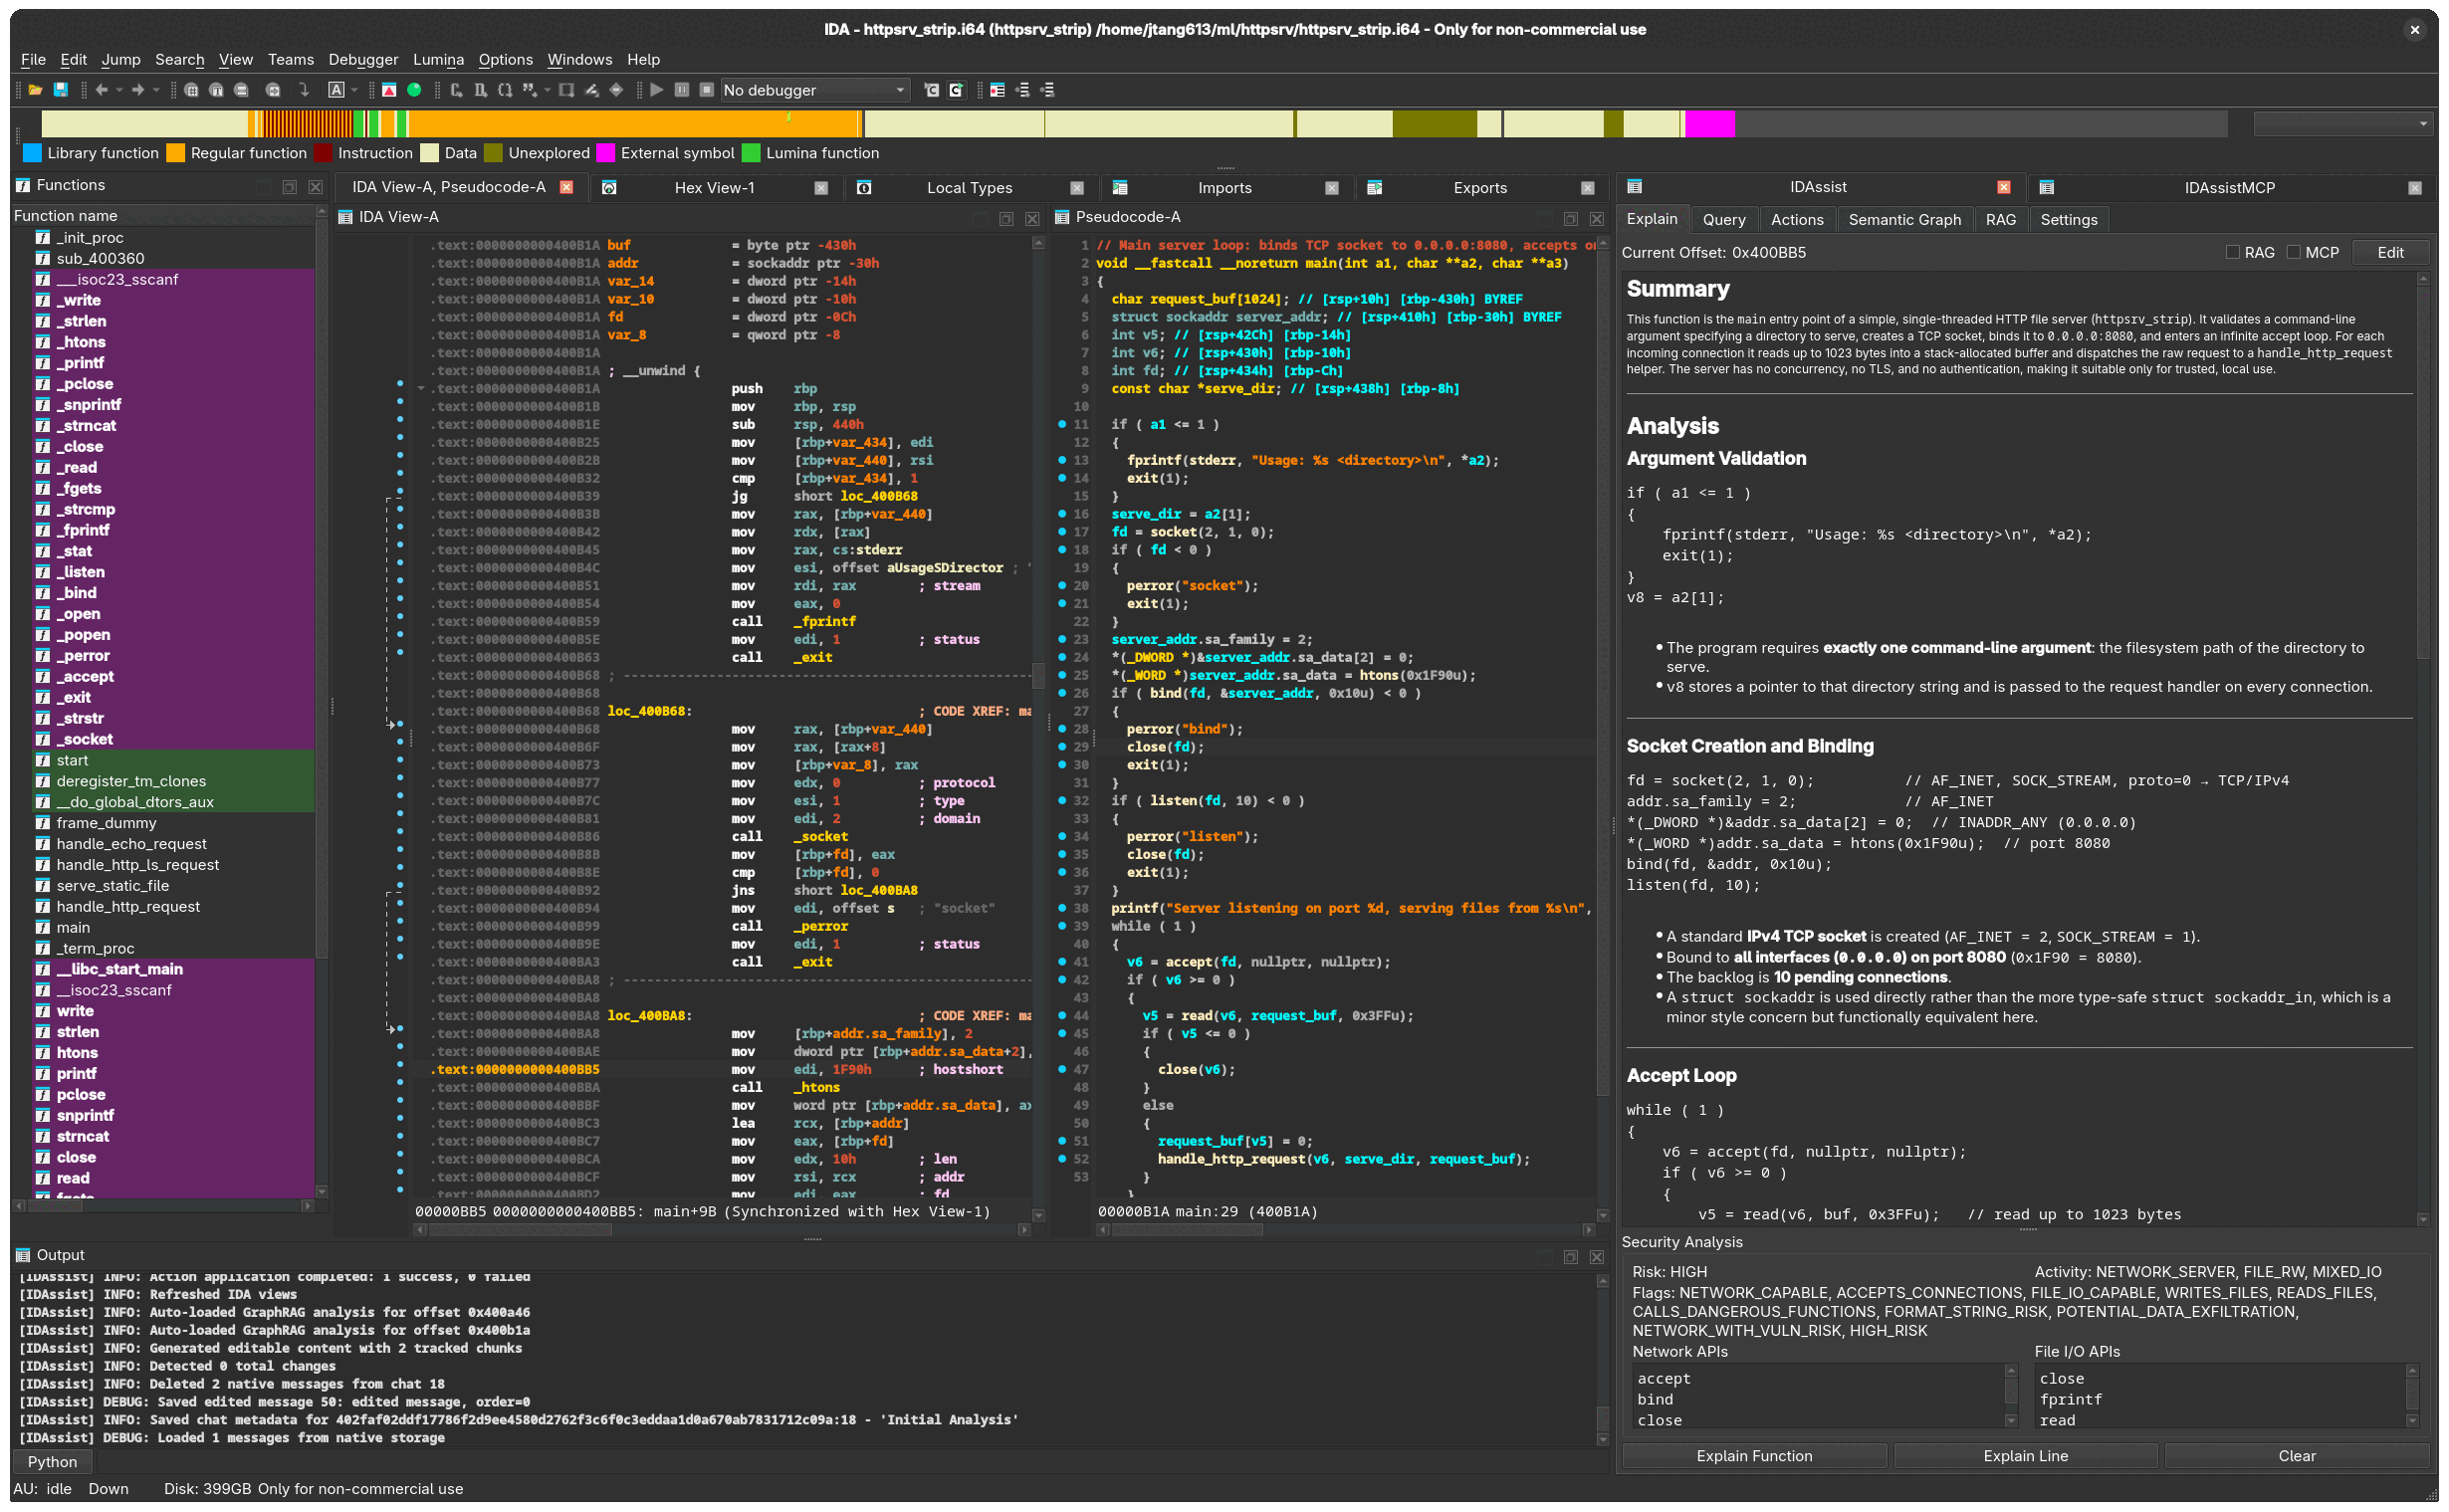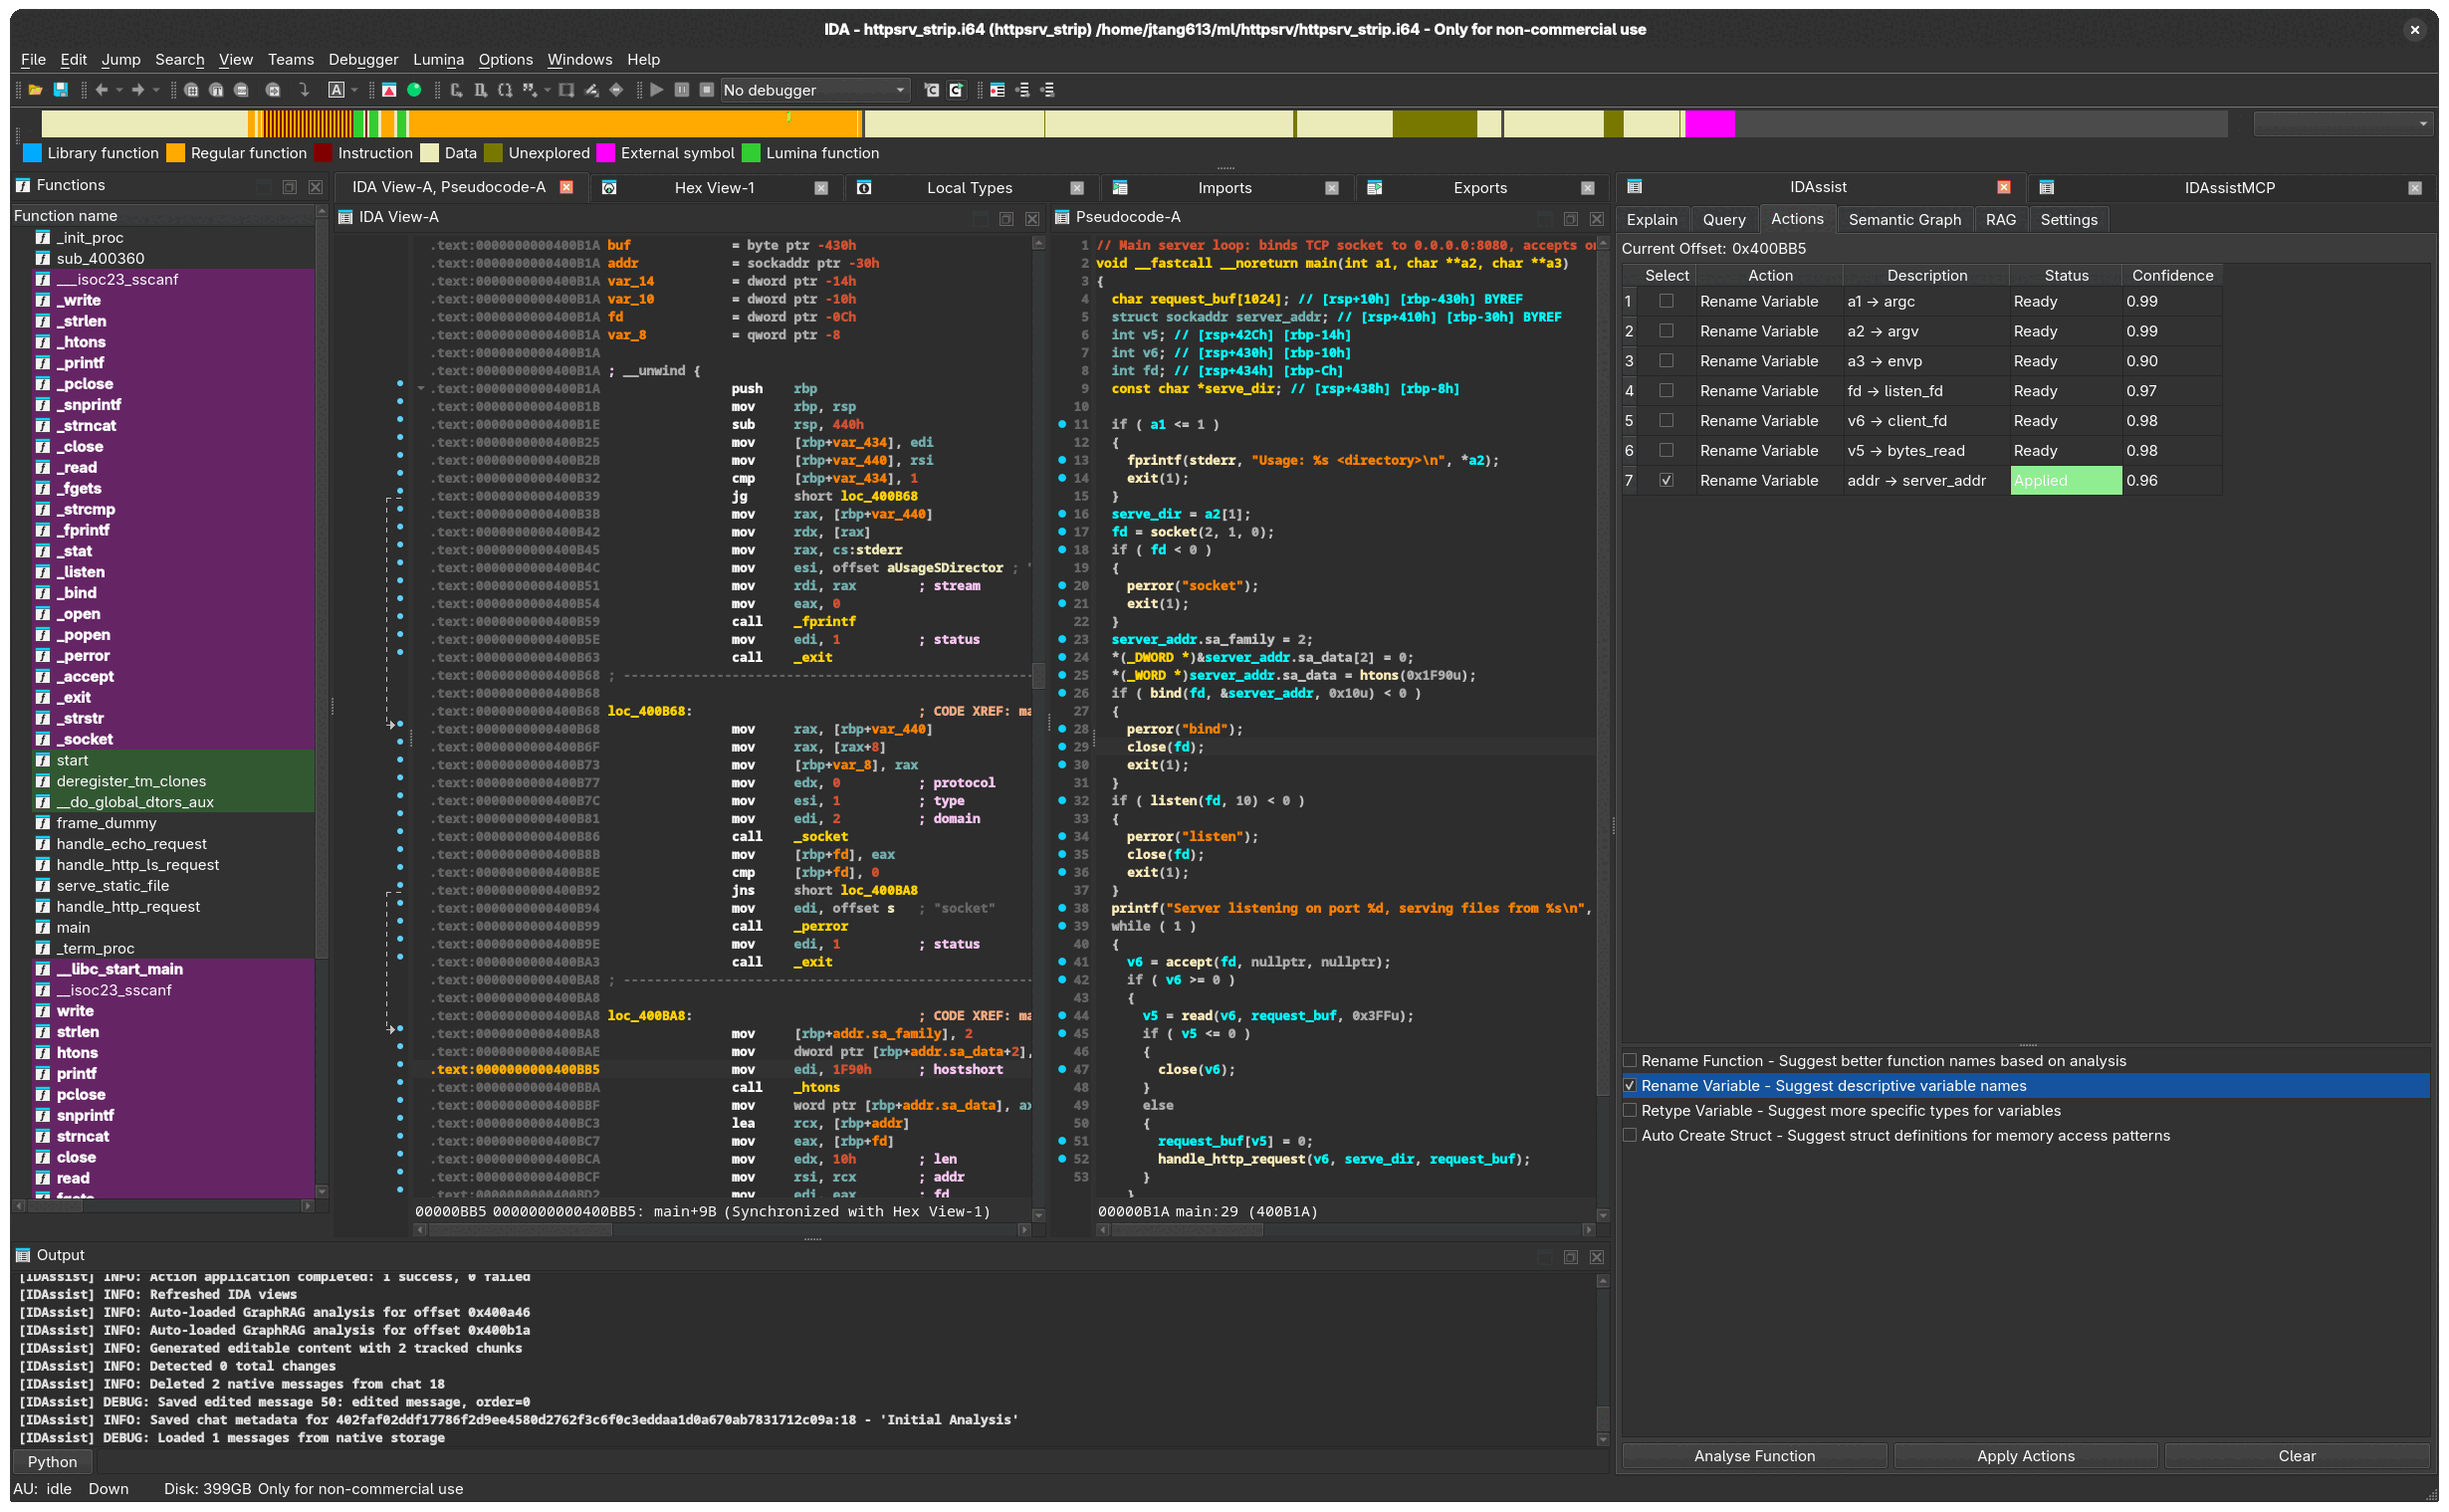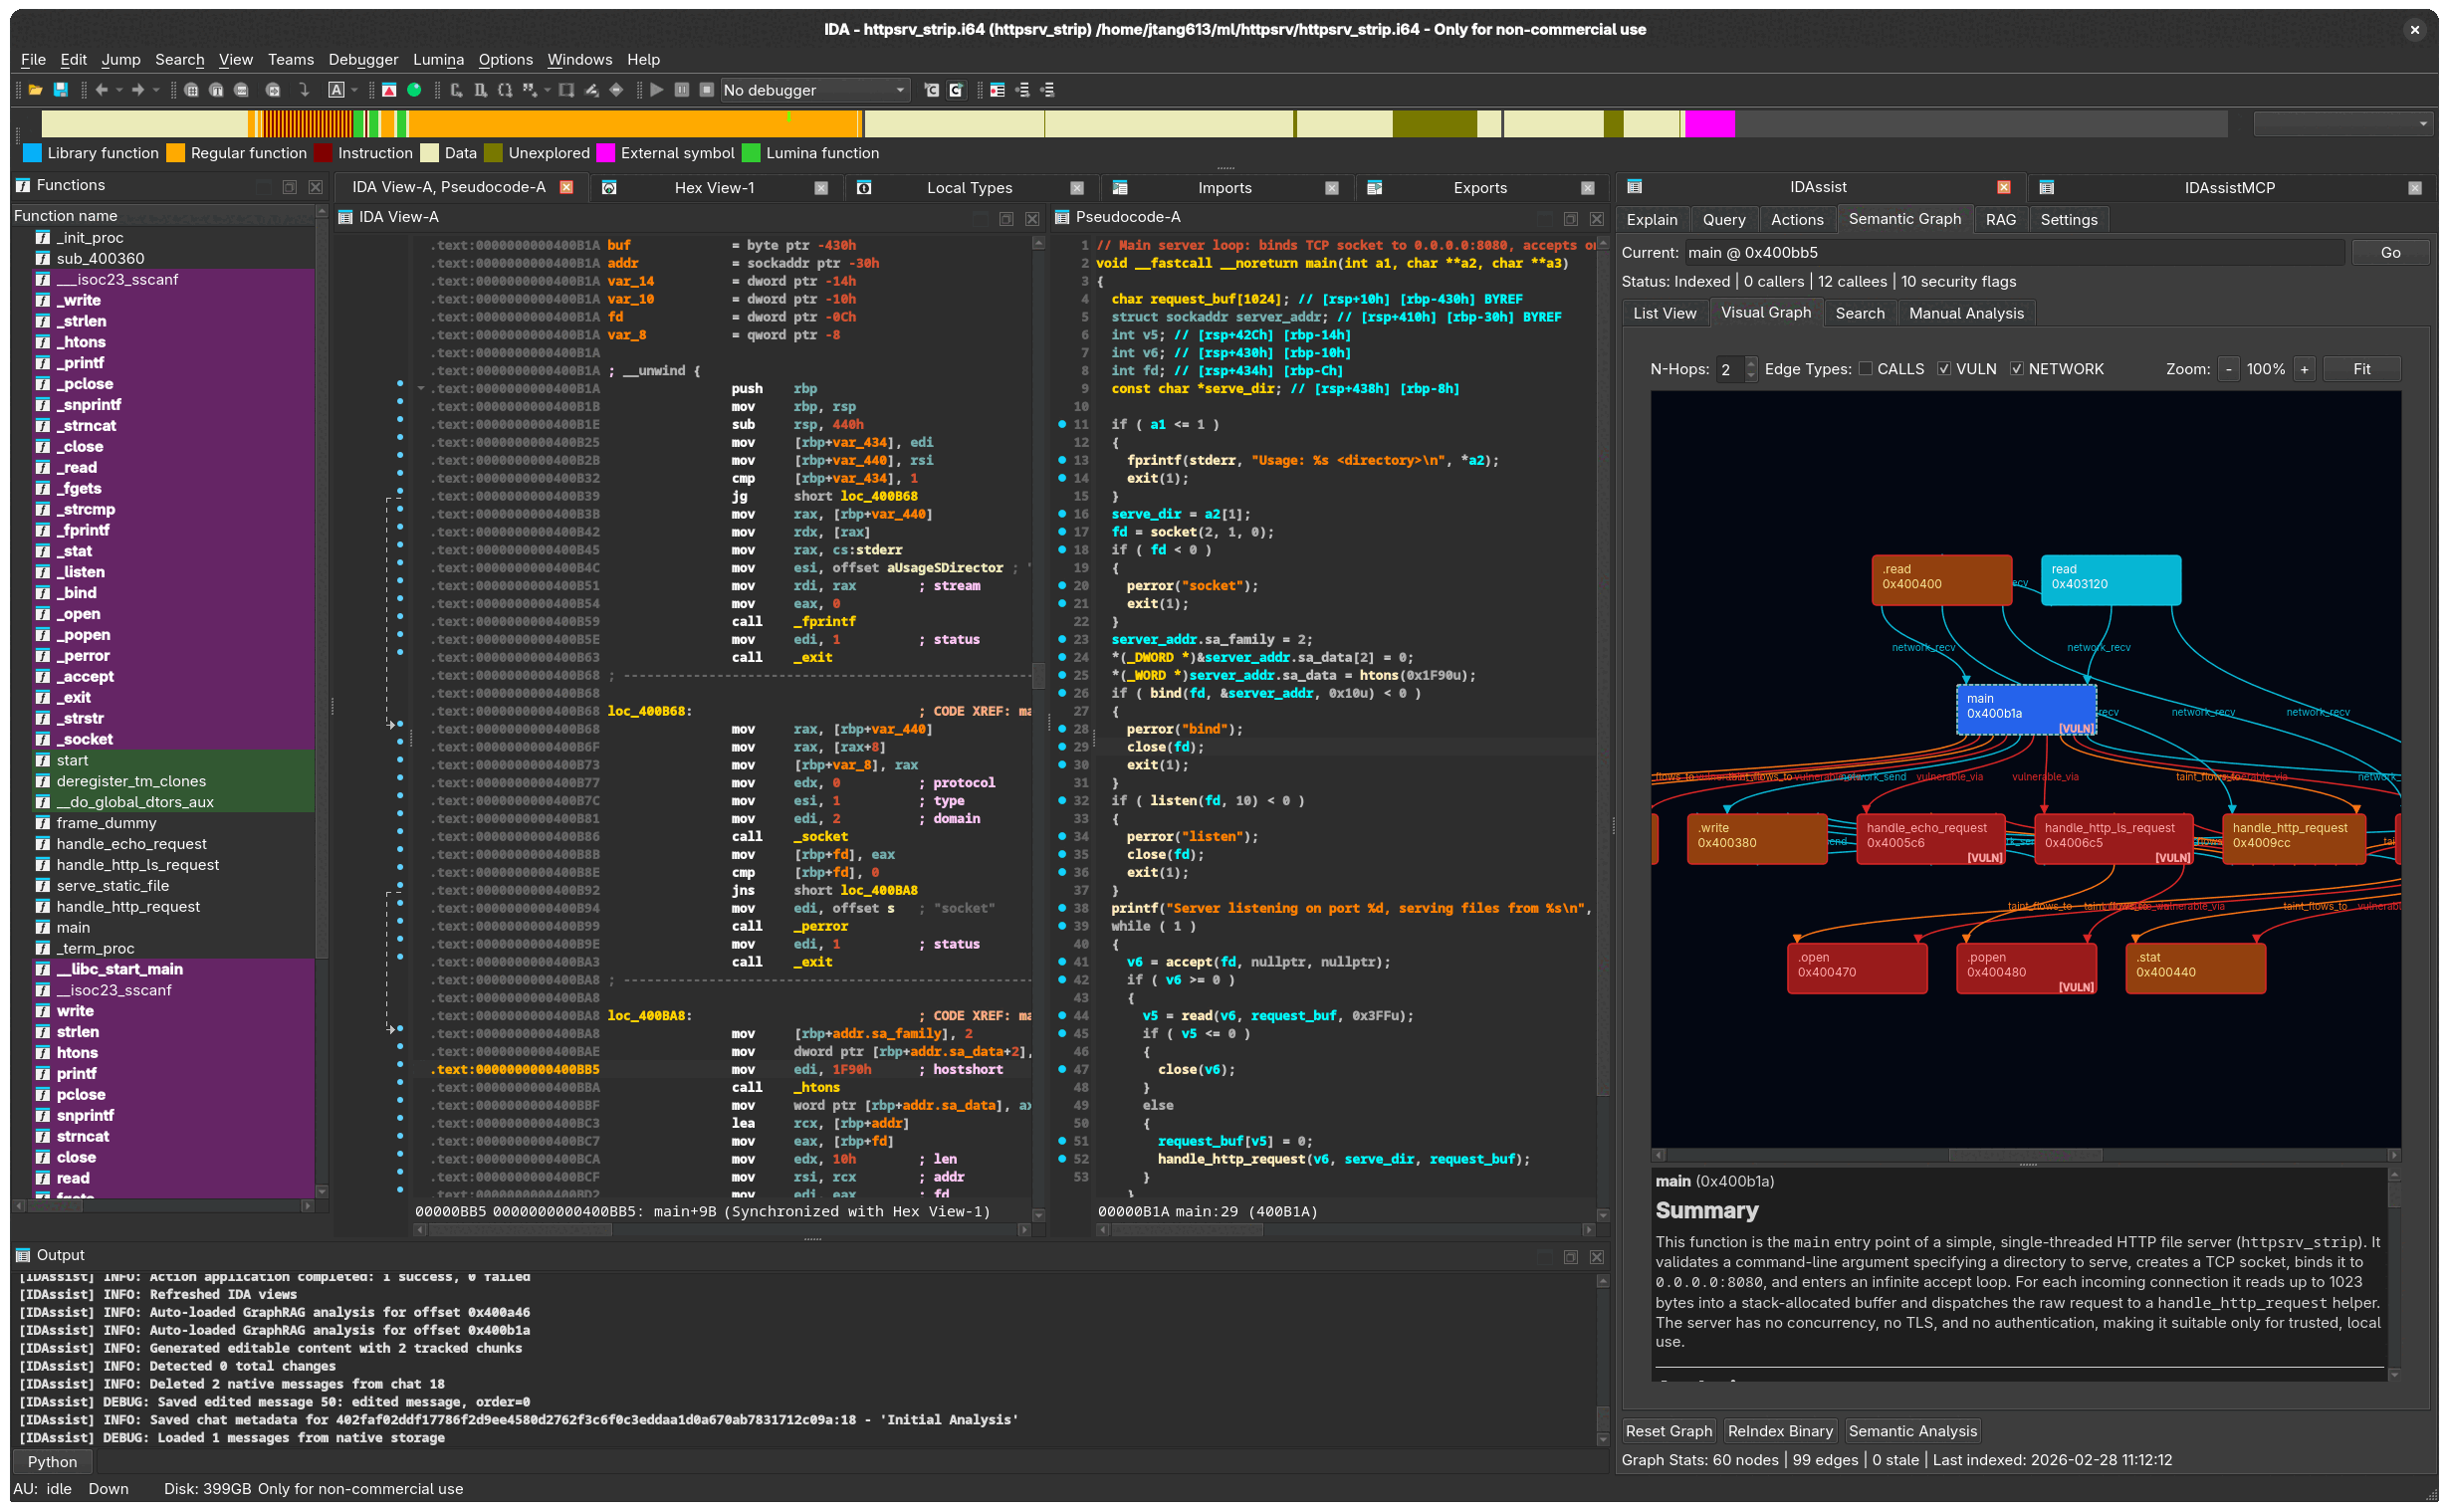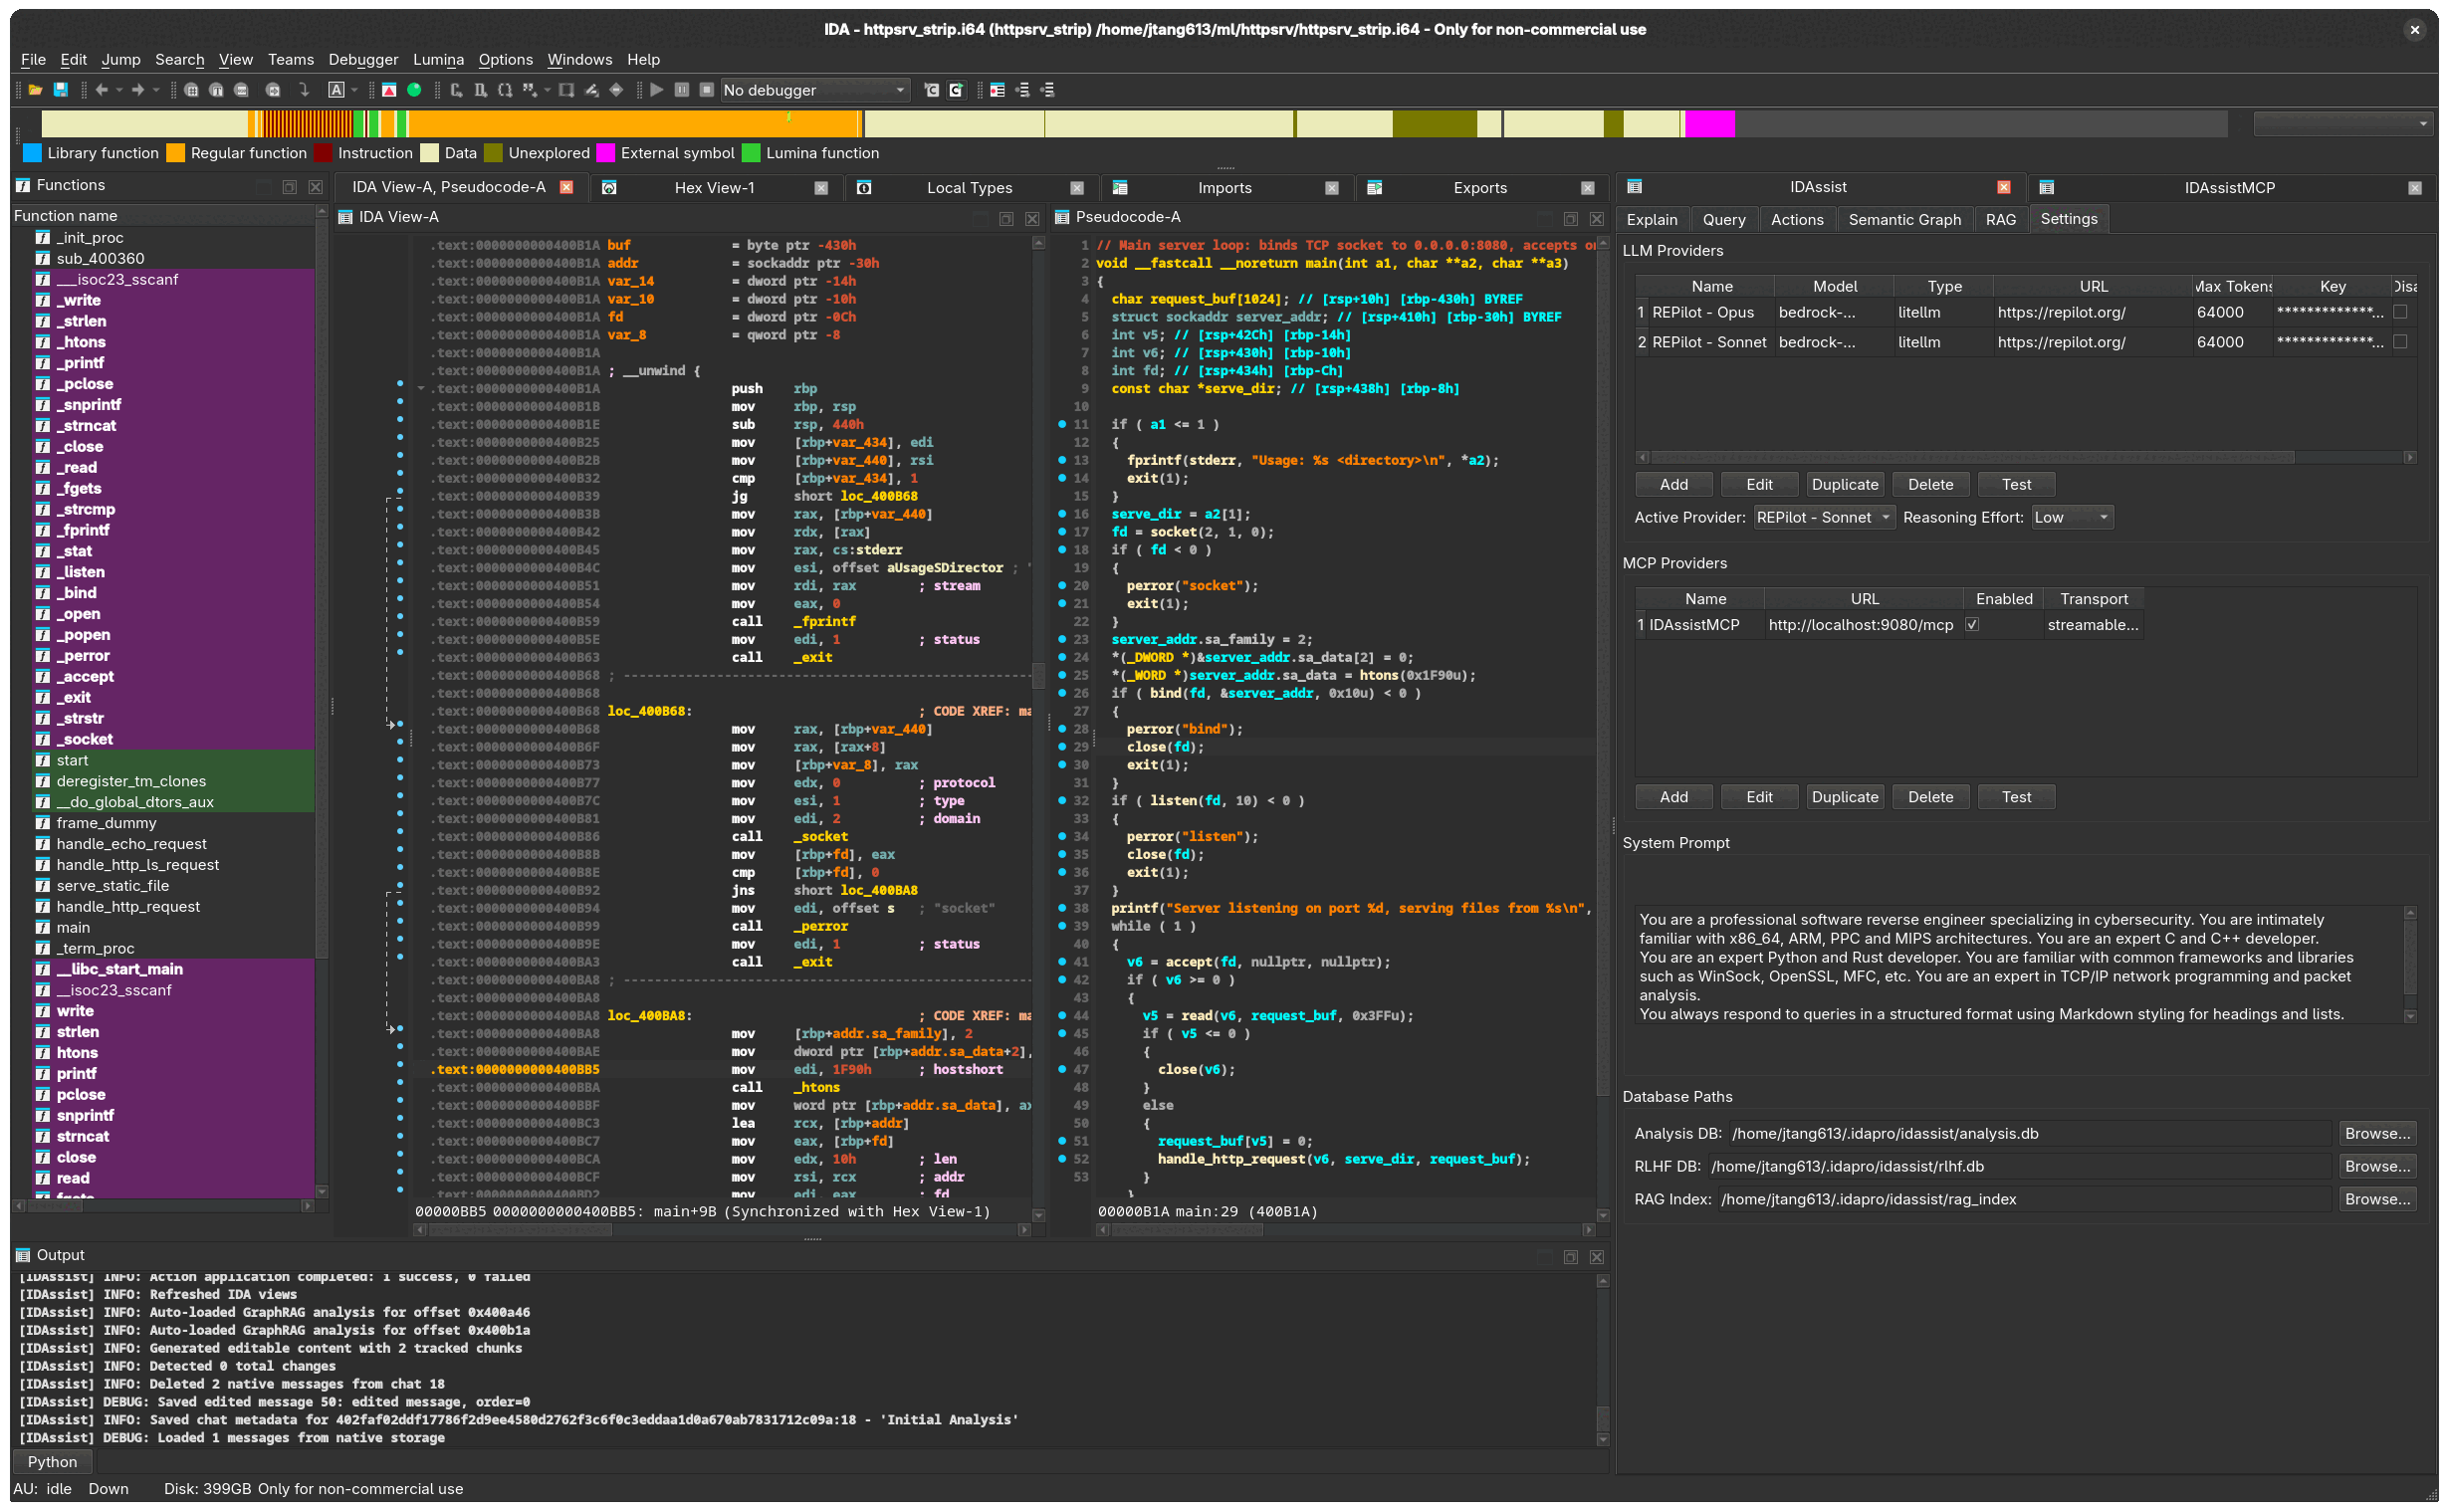 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
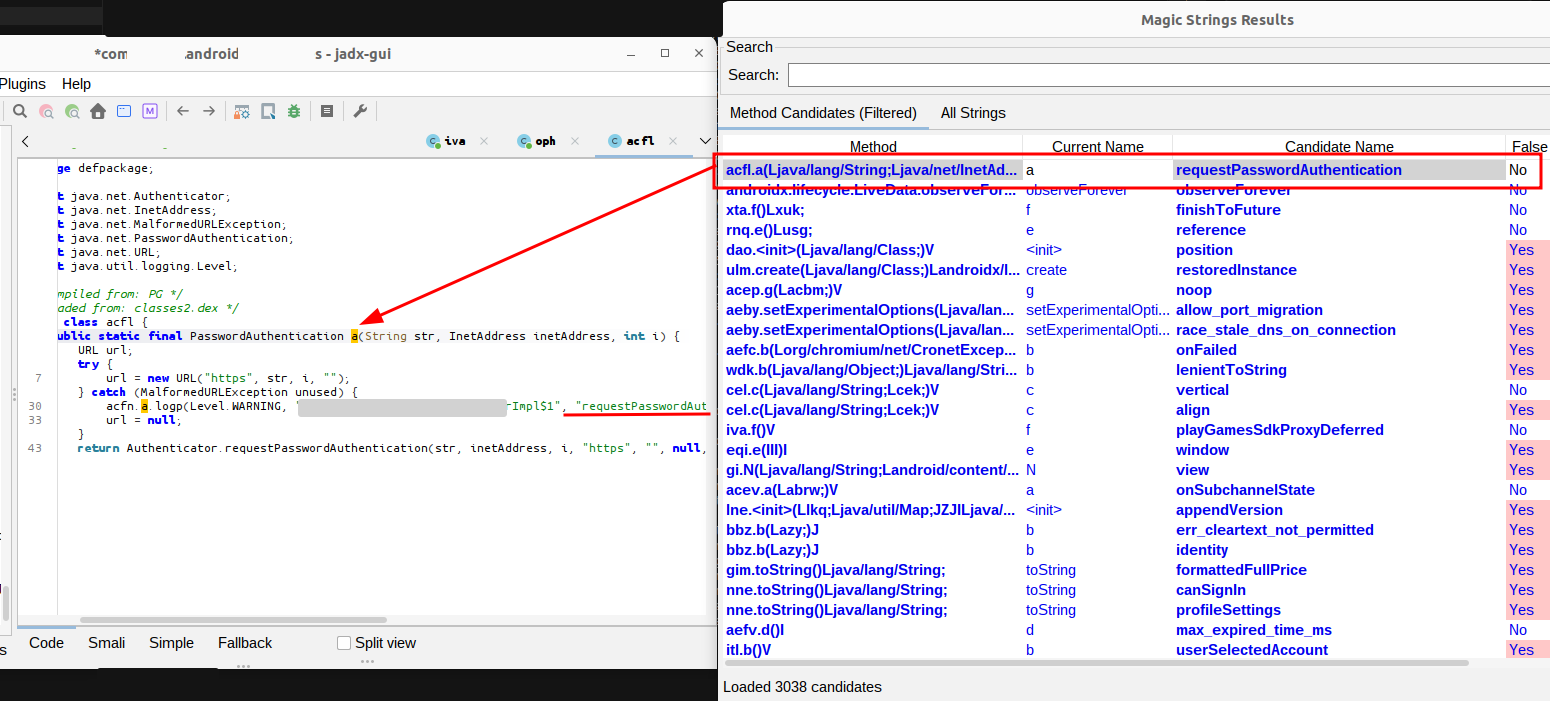 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 m10ust/machscope
macOS IPC, launchd, Mach-O, and trust relationship explorer — zero-dependency terminal-native forensic tool
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass