

frida
 frida/frida
Main repo for hosting release binaries
android-securitybinary-analysiscode-analysis+9
frida/fridaMain repo for hosting release binaries
 angr/angr
A powerful and user-friendly binary analysis platform!
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 upx/upx
UPX - the Ultimate Packer for eXecutables
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

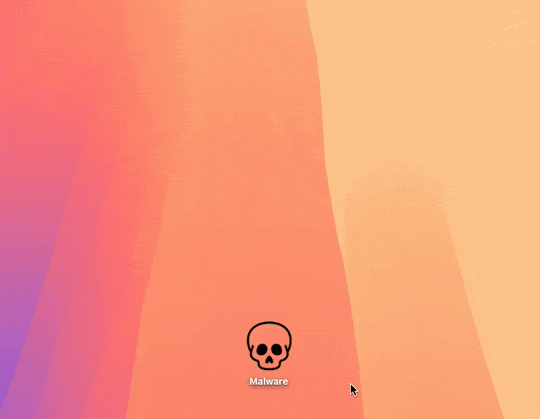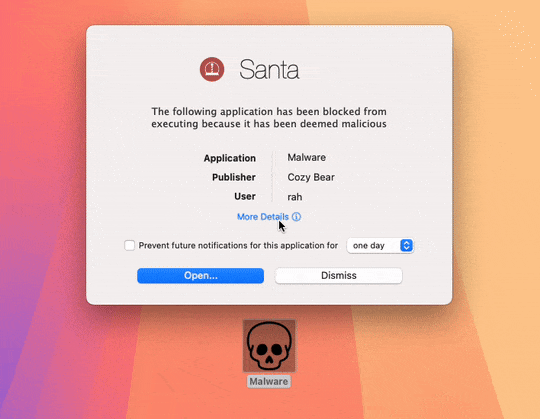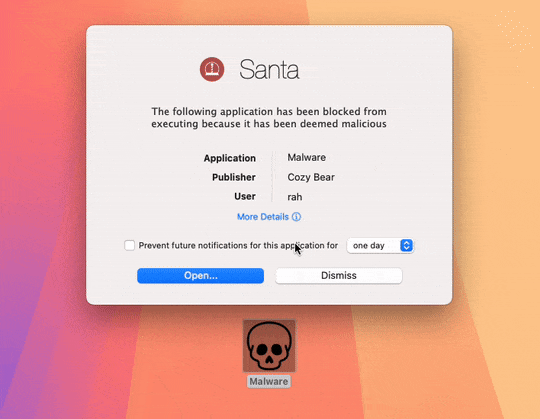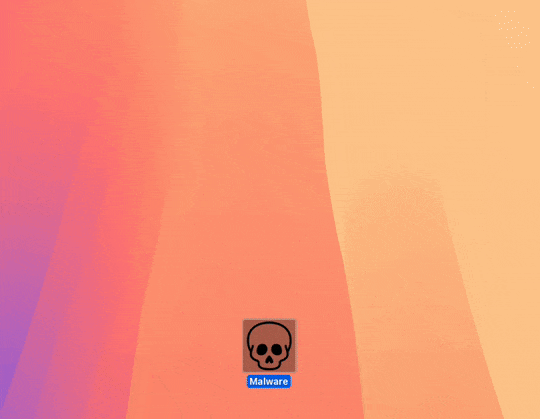 northpolesec/santa
A binary and file access authorization system for macOS.
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
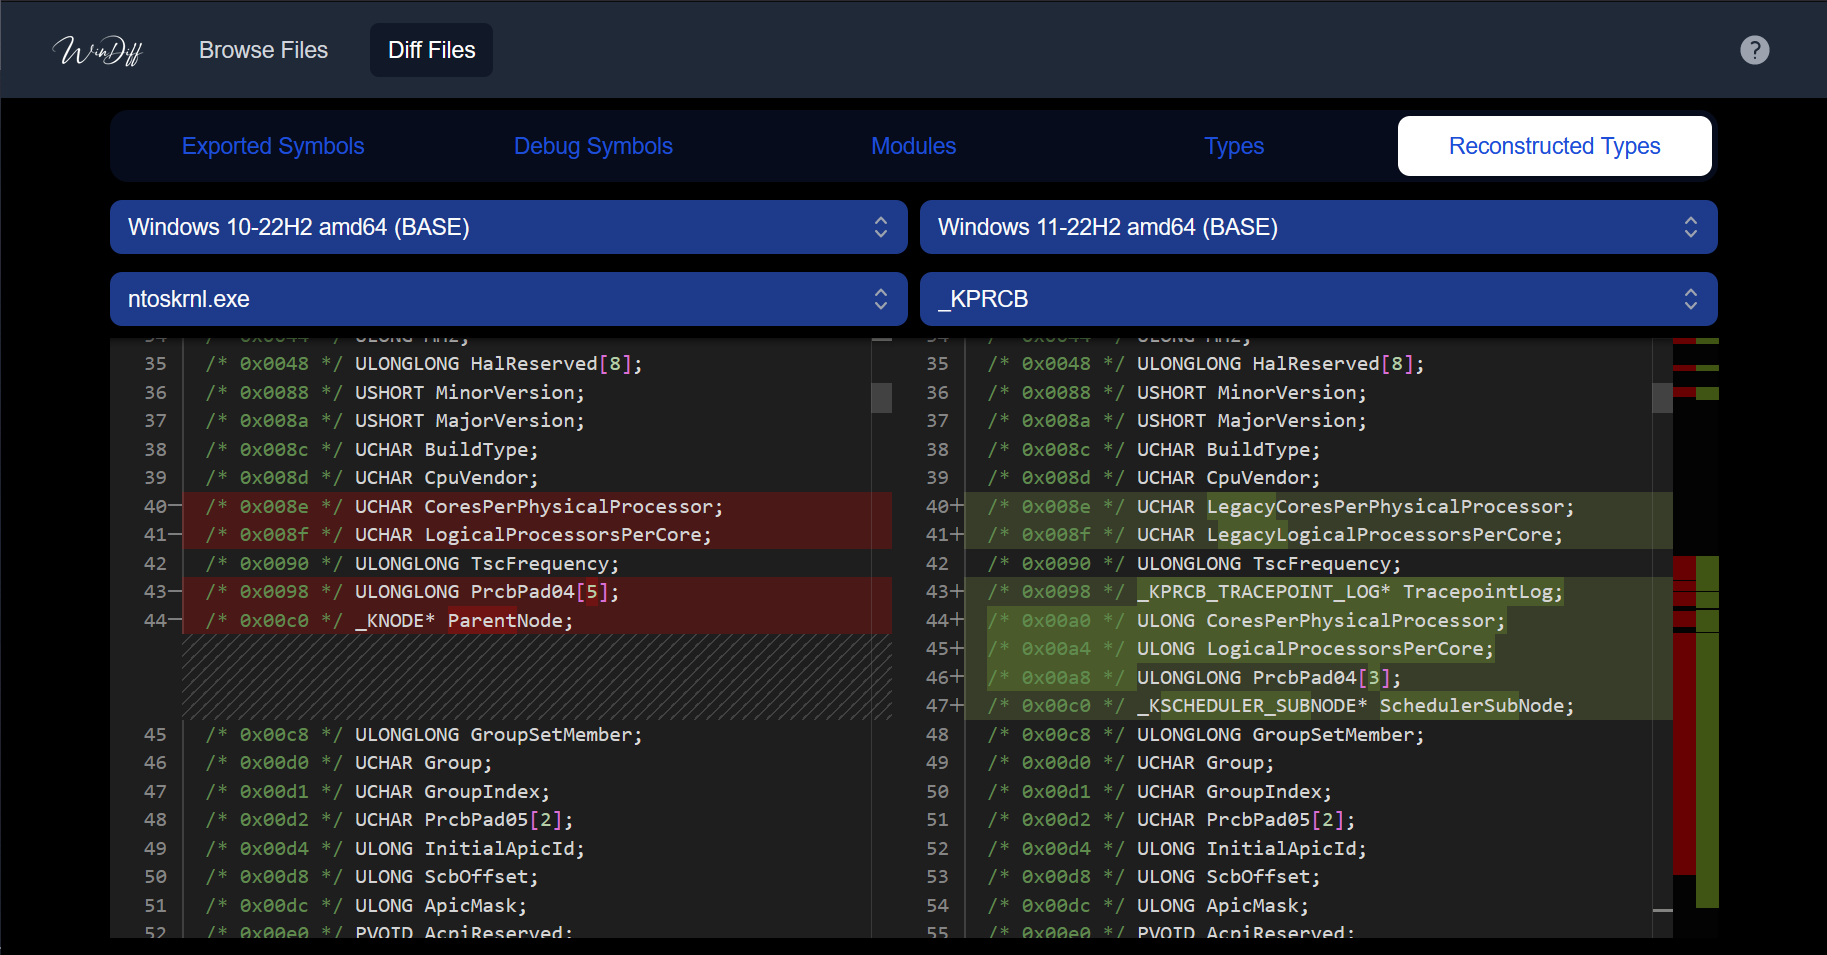 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 nmatt0/moria
IoT firmware identification and extraction