

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
75.8k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 frida/frida
Main repo for hosting release binaries
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
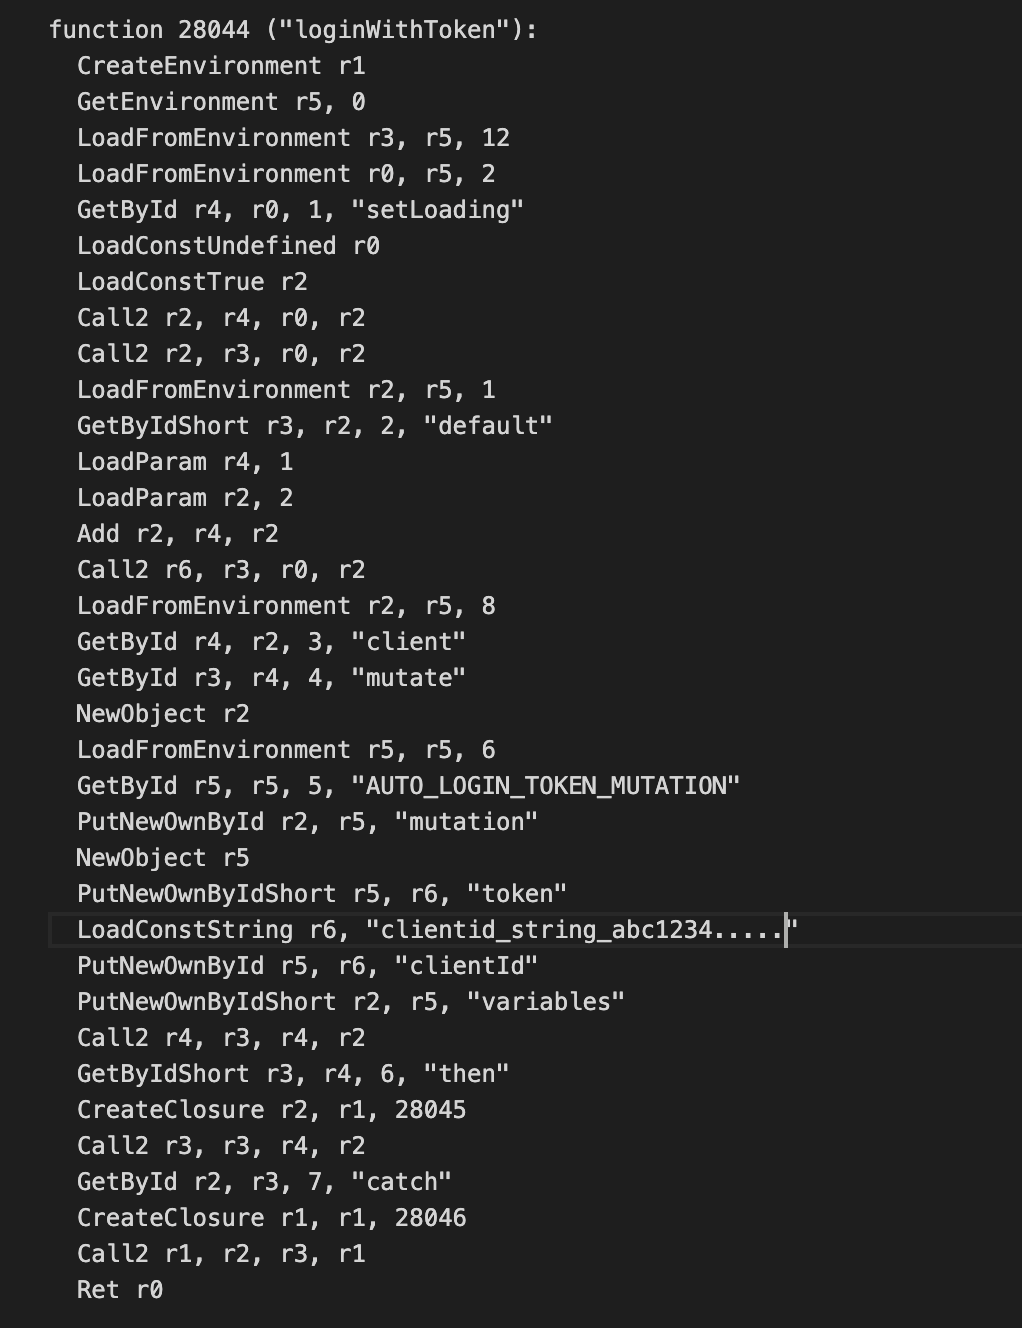 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
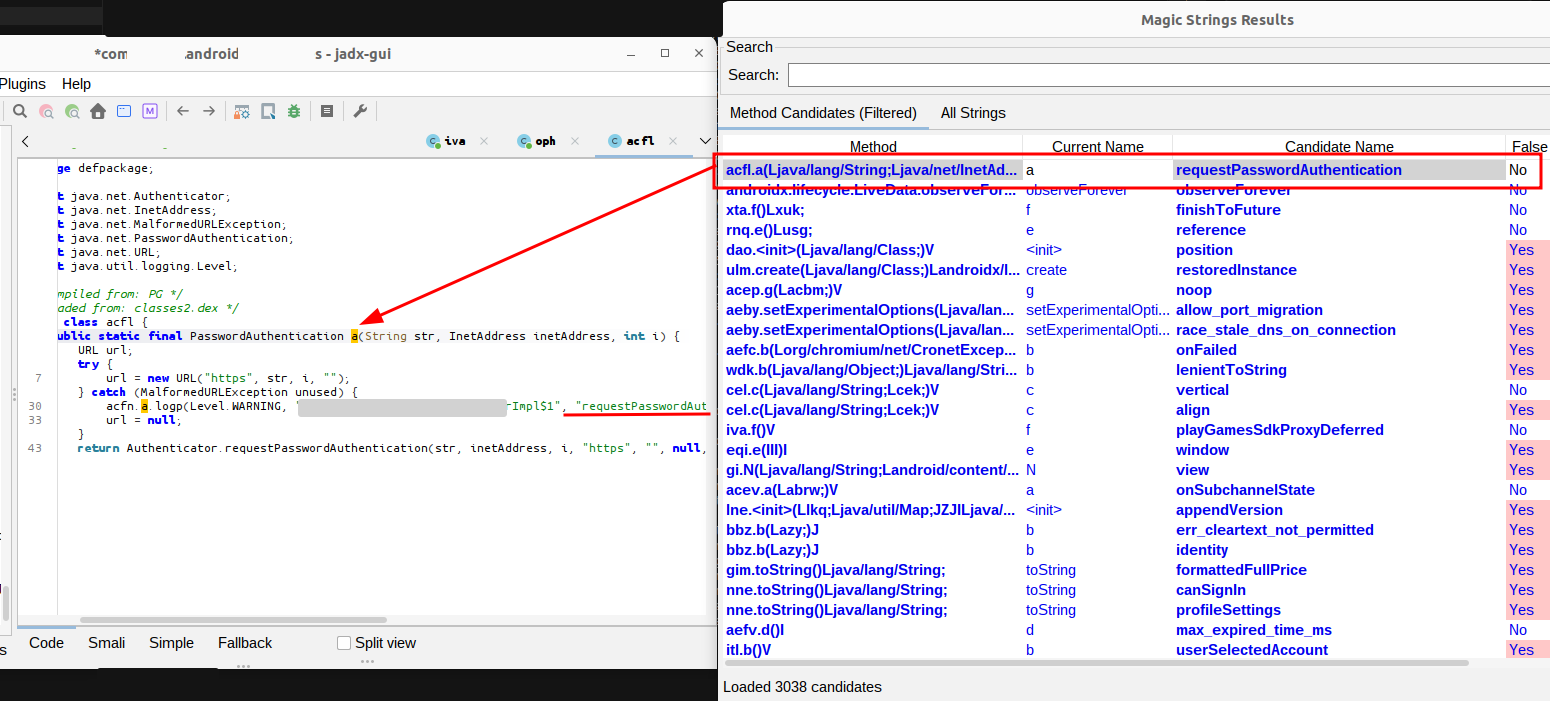 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
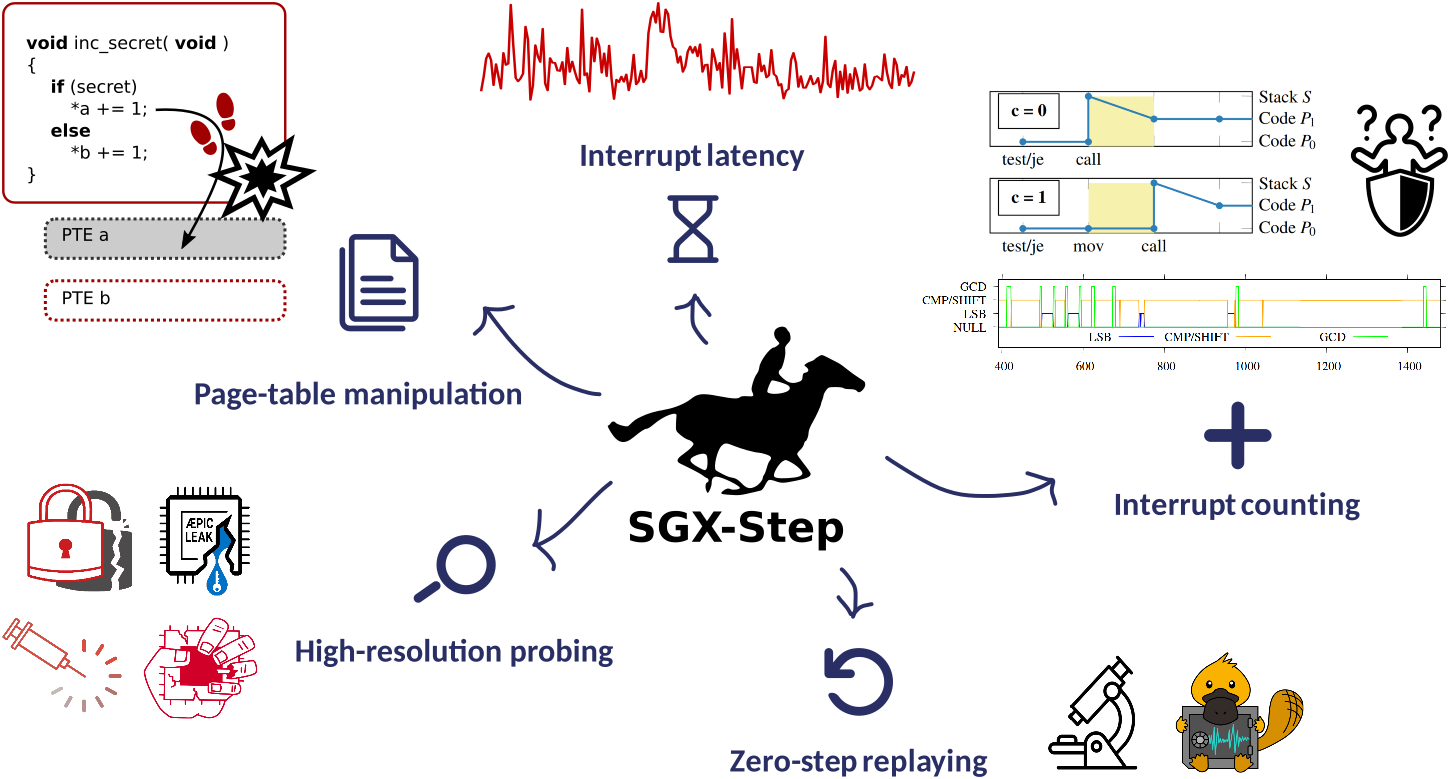 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
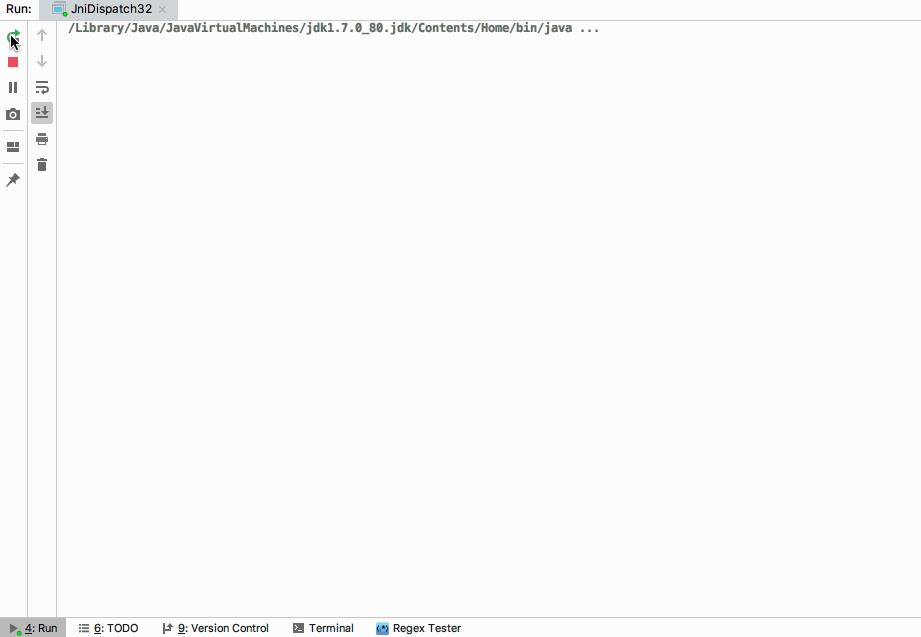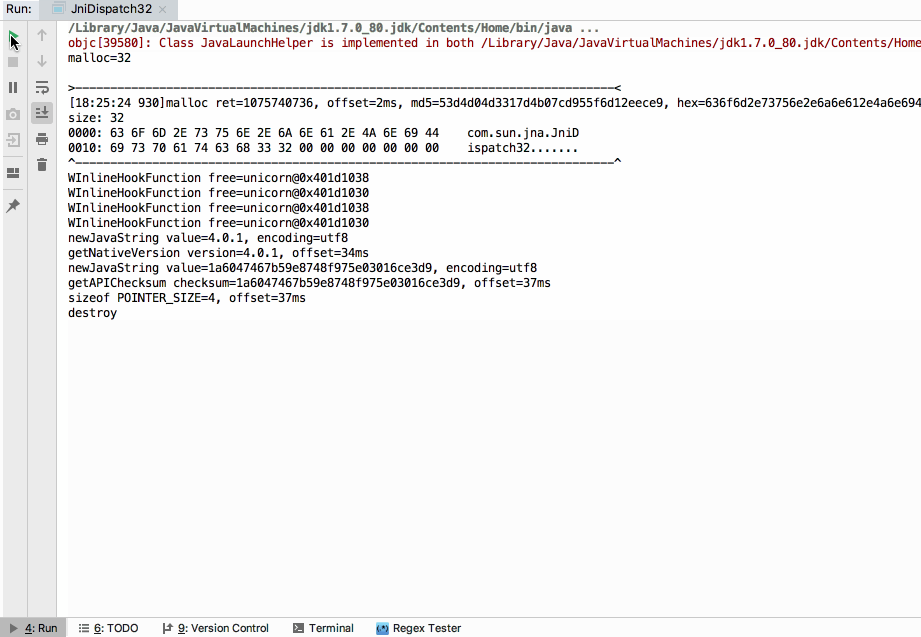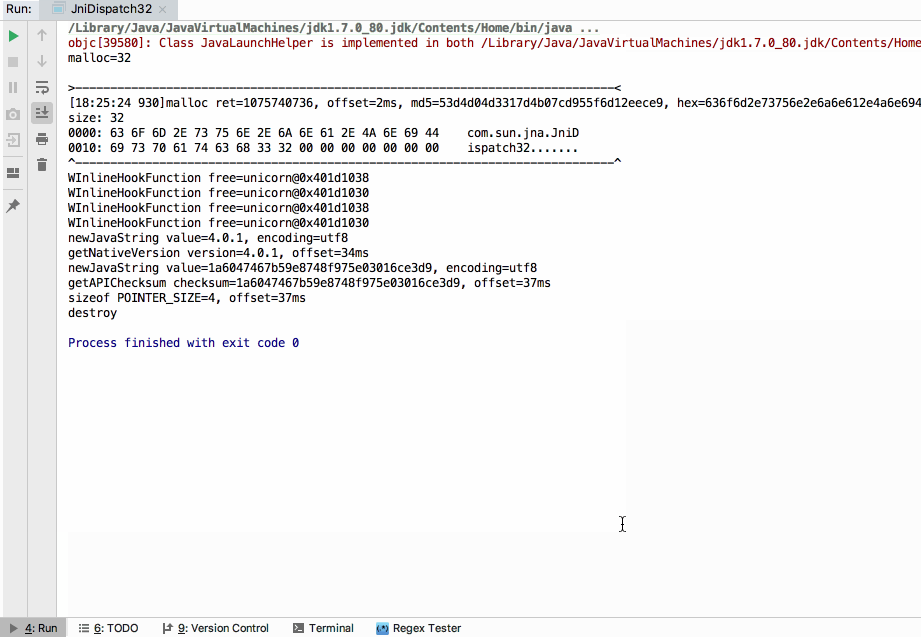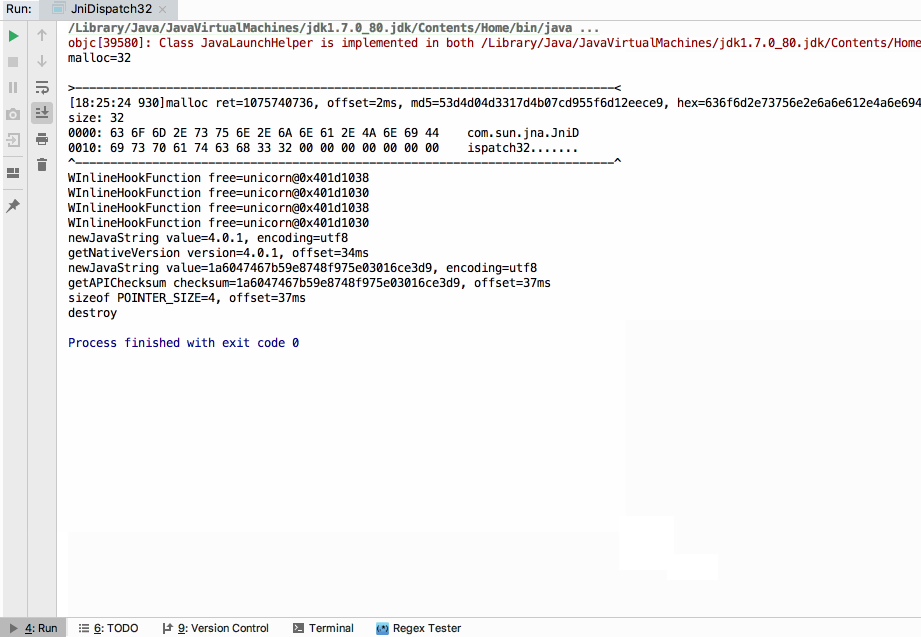 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…