
 0xor0ne/awesome-list
Cybersecurity oriented awesome list
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 mr-wolf-is-me/ida-processor-modules
IDA Pro processor modules adding disassembly support for uncommon CPU, DSP, and GPU architectures including XMOS xCORE, TI C7x/PRU, MicroBlaze, and…
 zardus/ctf-tools
Some setup scripts for security research tools.
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 0xdea/ghidra-scripts
Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…
 0xdea/semgrep-rules
A collection of my Semgrep rules to facilitate vulnerability research.
 kraxel/virt-firmware
Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
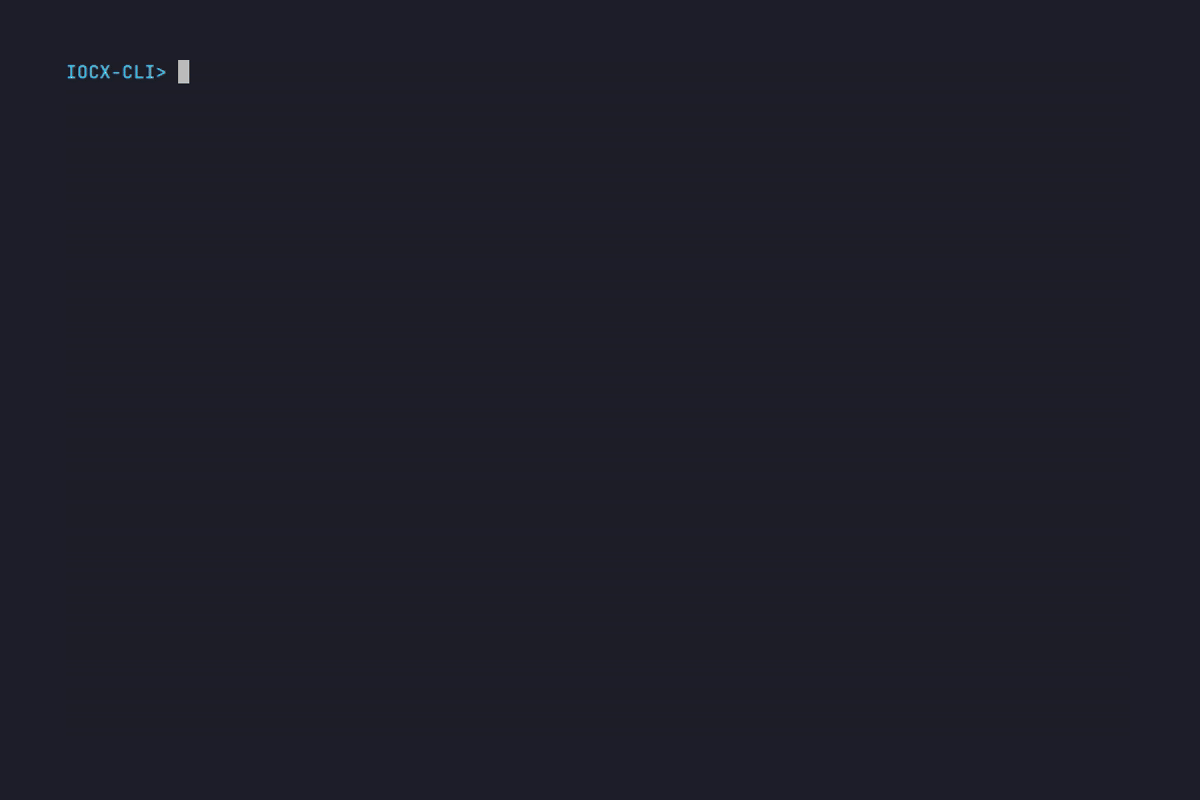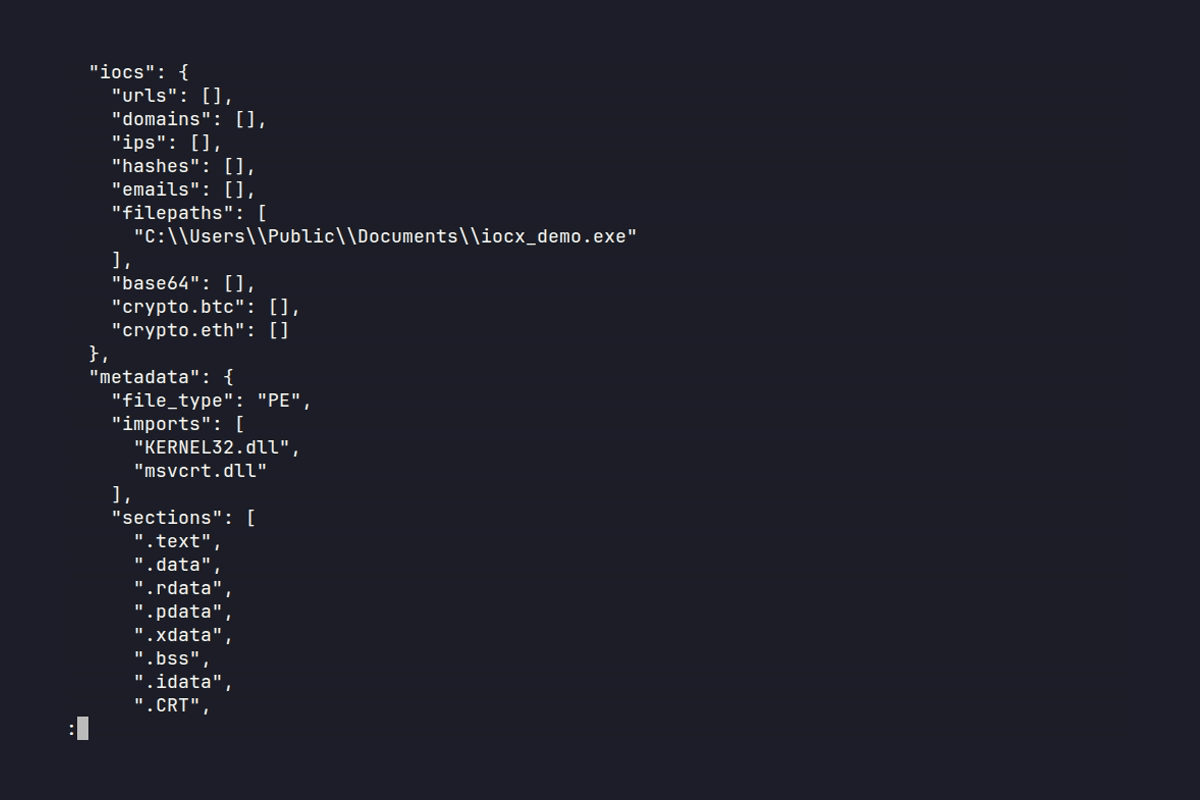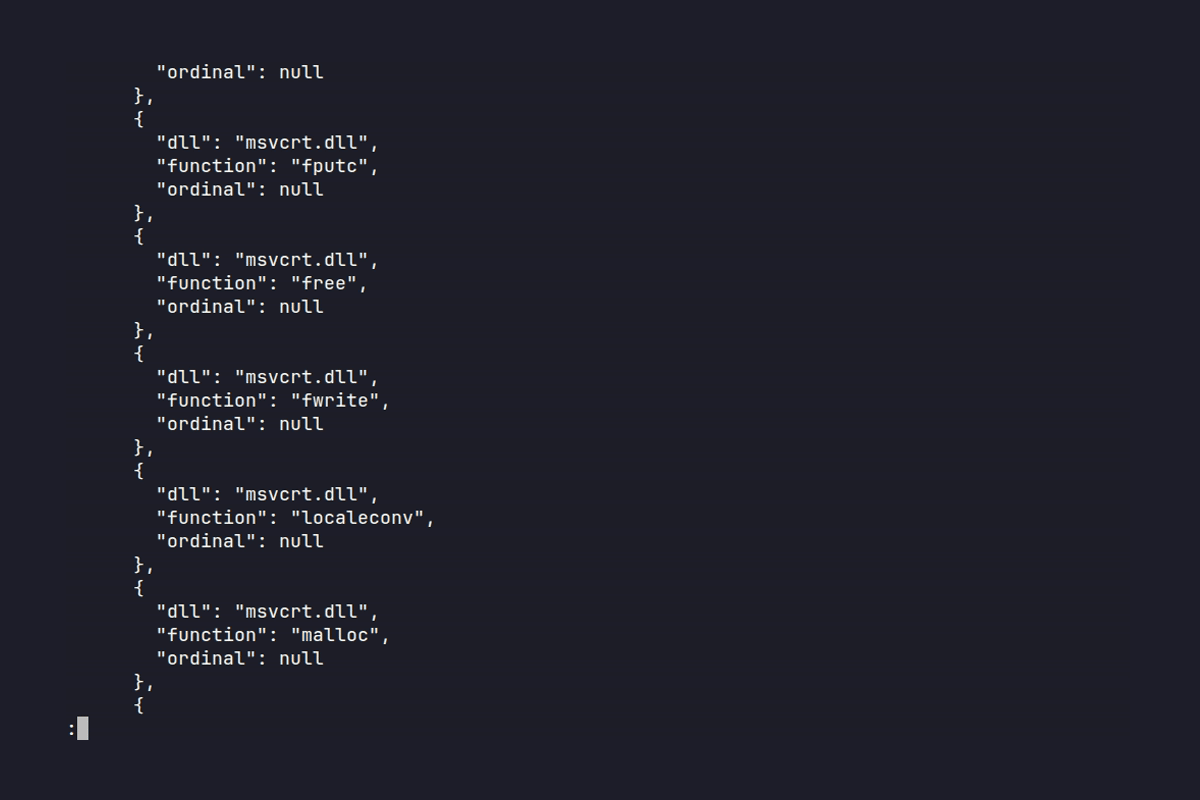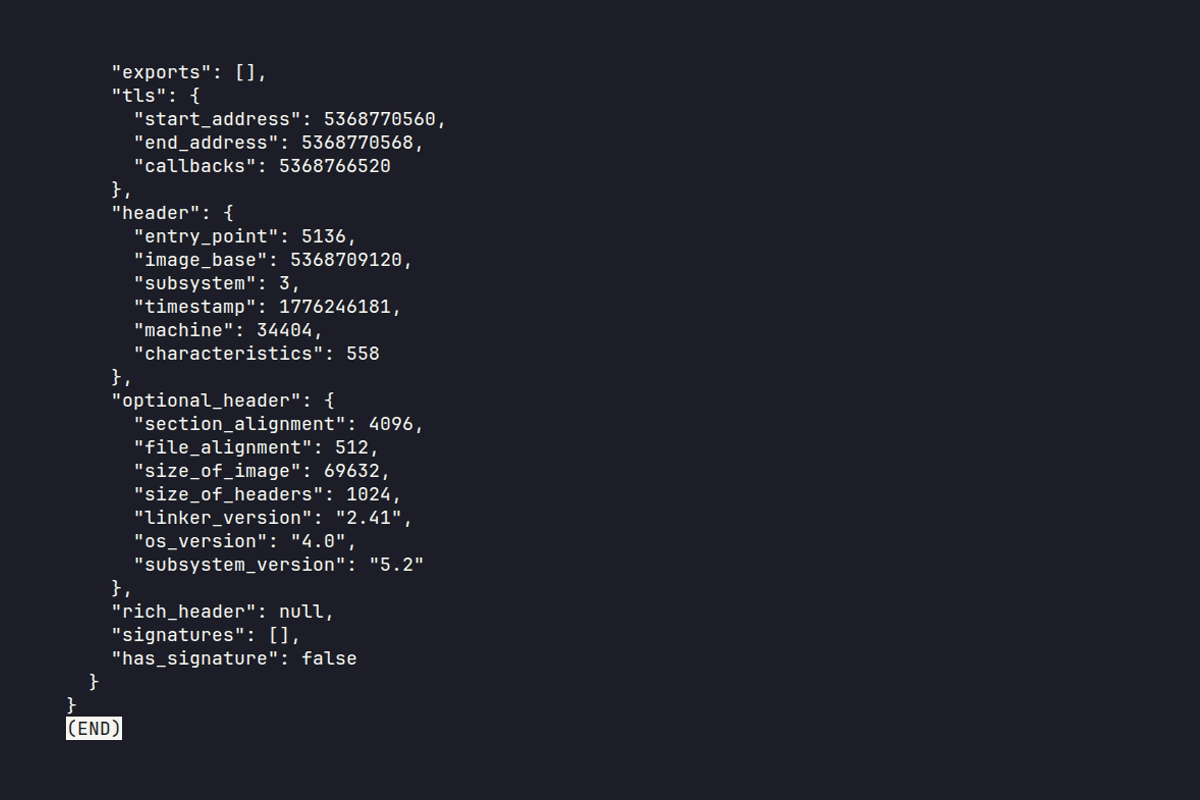 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 cristianzsh/forensictools
Collection of forensic tools
 struppigel/hedgehog-tools
Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 xkiian/datadome-vm
Reverse engineering the new Datadome VM 🔥