
certgraveyard_yara
 tjnel/certgraveyard_yara
Automated YARA rule generation from the Cert Central compromised certificate database.
defensive-toolsforensicsmalware-analysis+2
15
tjnel/certgraveyard_yaraAutomated YARA rule generation from the Cert Central compromised certificate database.
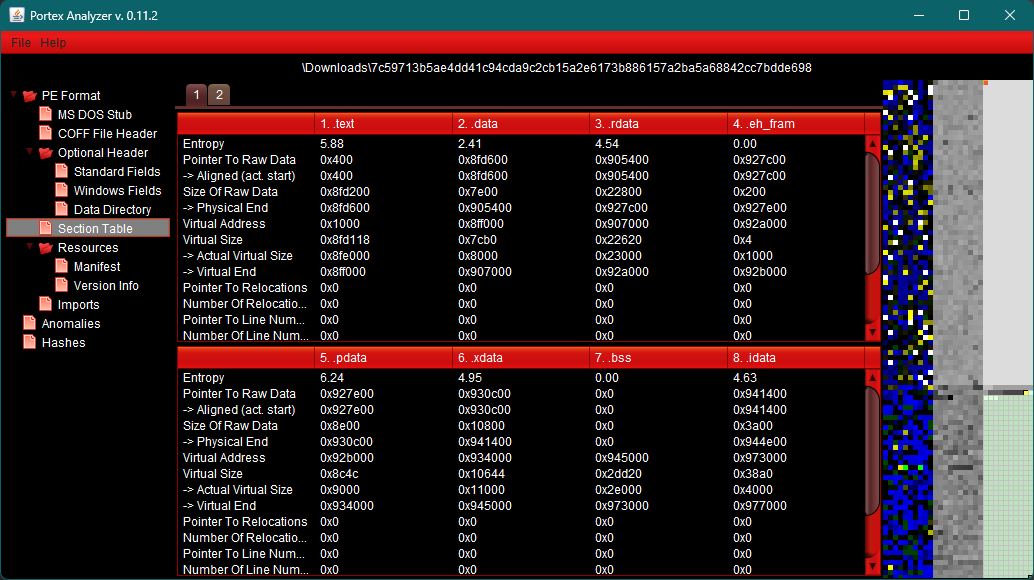 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 happytotoro116/ghidra-llm-pipeline
Deterministic PyGhidra extraction, triage, and local LLM compiler-backend pipeline for C reimplementation.
 cristianzsh/freki
Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
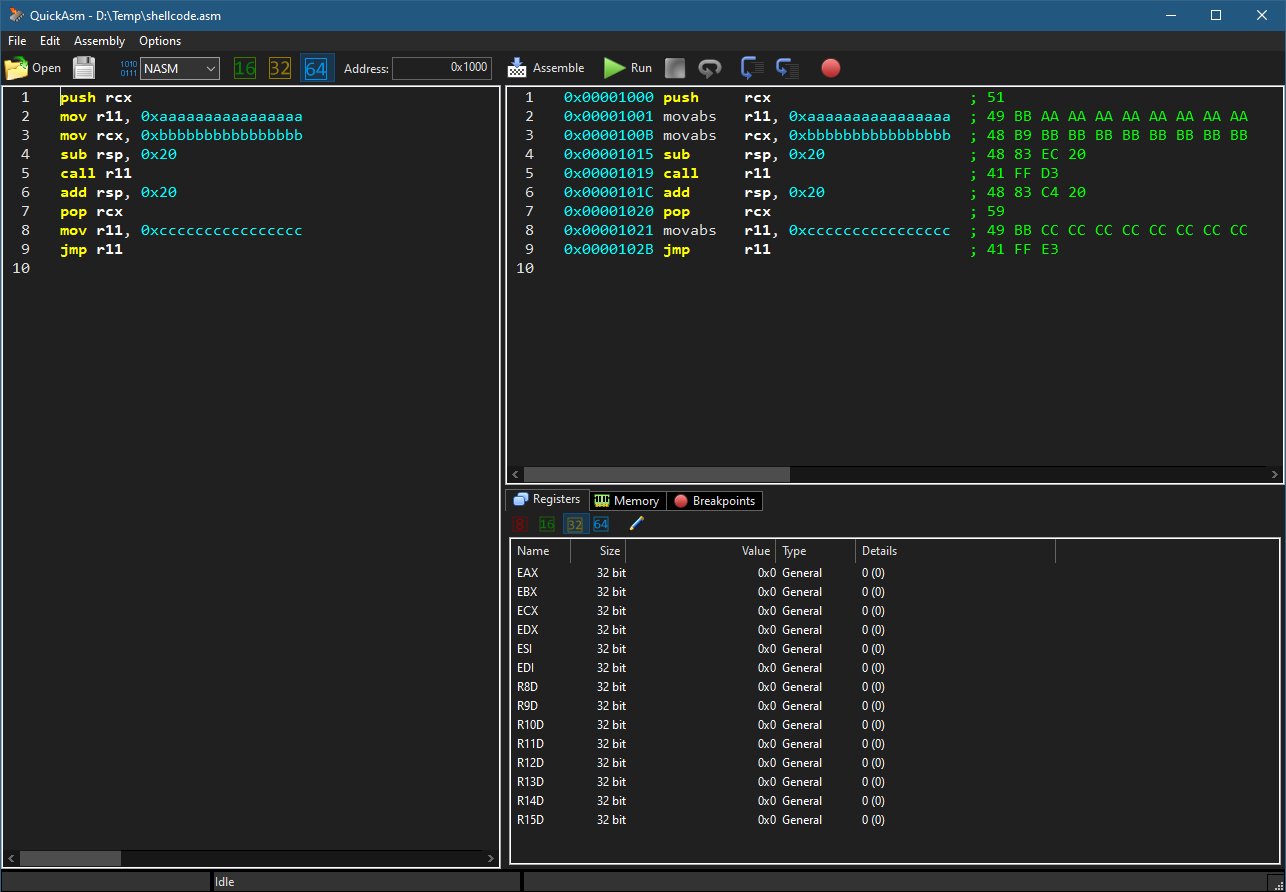 zodiacon/quickasm
Simple x86/x64 Assembler/Disassembler/Emulator
 nmatt0/moria
IoT firmware identification and extraction
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 epasveer/seer
Seer - a gui frontend to gdb
 gallopsled/pwntools
CTF framework and exploit development library
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 nowsecure/r2frida
Radare2 and Frida better together.
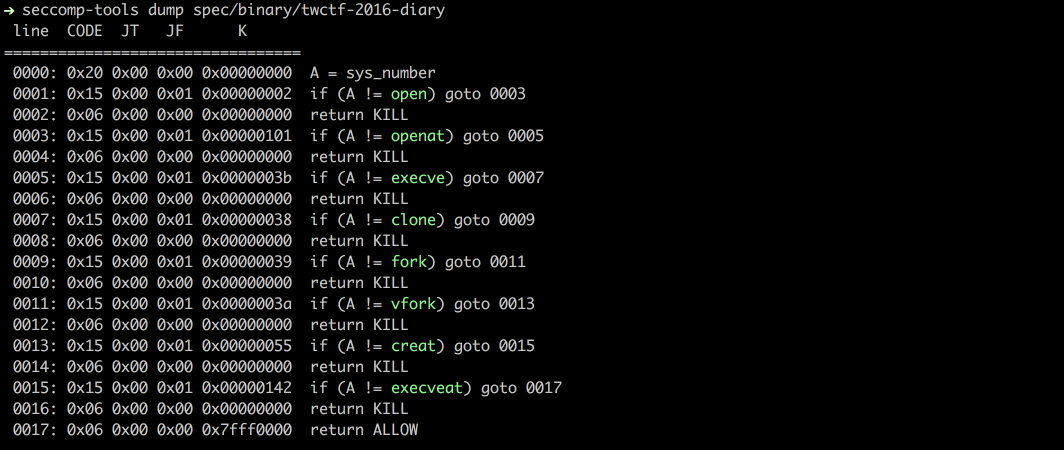 david942j/seccomp-tools
Provide powerful tools for seccomp analysis
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.