

lazy_importer
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
anti-botbinary-analysisexploitation+6
1.9k
justasmasiulis/lazy_importerlibrary for importing functions from dlls in a hidden, reverse engineer unfriendly way
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 sizeable-bingus/massdriver
Proxies sensitive API calls from shellcode to artifacts for CET-compatible clean call stacks, enabling stealthy payload execution and call stack…
 gmh5225/awesome-mba
List of mixed boolean-arithmetic resources
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
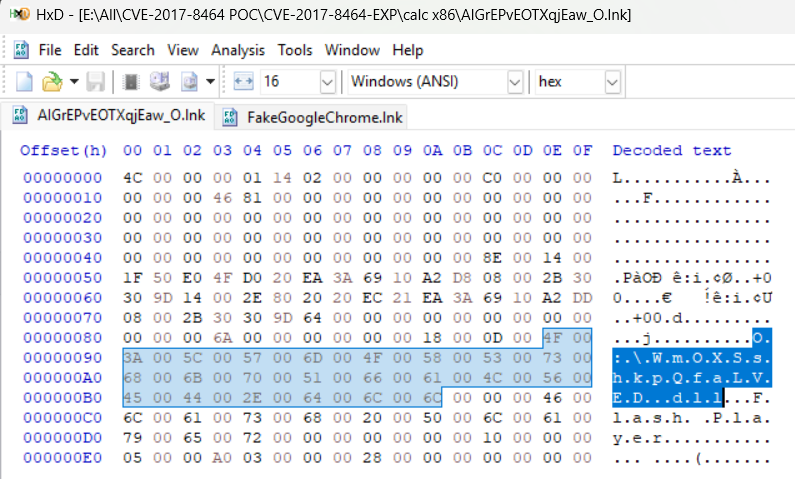 playboisk8/poc-cve-2017-8464-opencalculator
Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
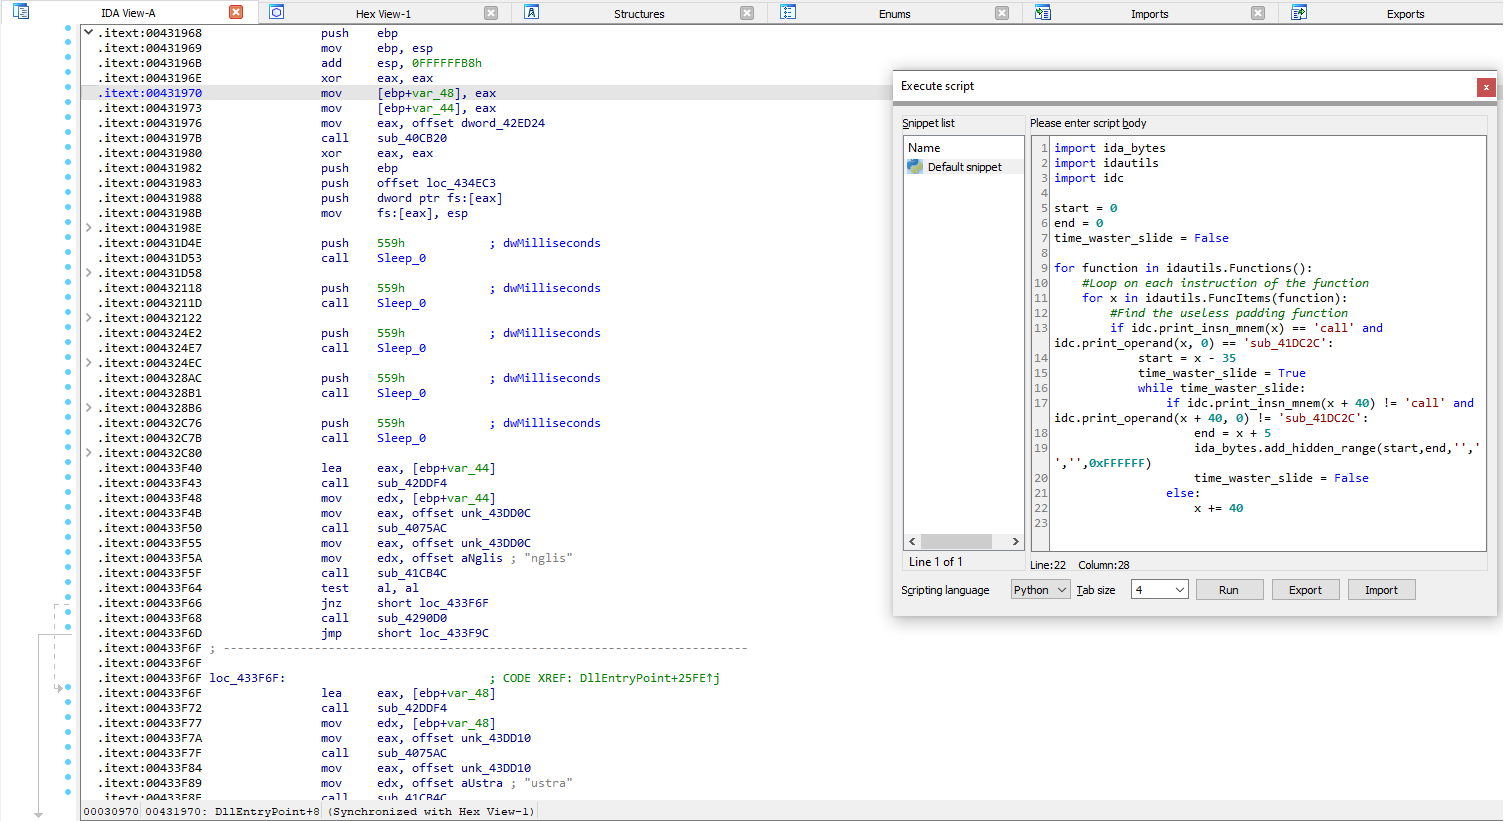 dodo-sec/astaroth-deobfuscator
IDA python script for deobfuscating Astaroth/Guildma injector DLL
 ropfuscator/ropfuscator
ROPfuscator is a fine-grained code obfuscation framework for C/C++ programs using ROP (return-oriented programming).
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
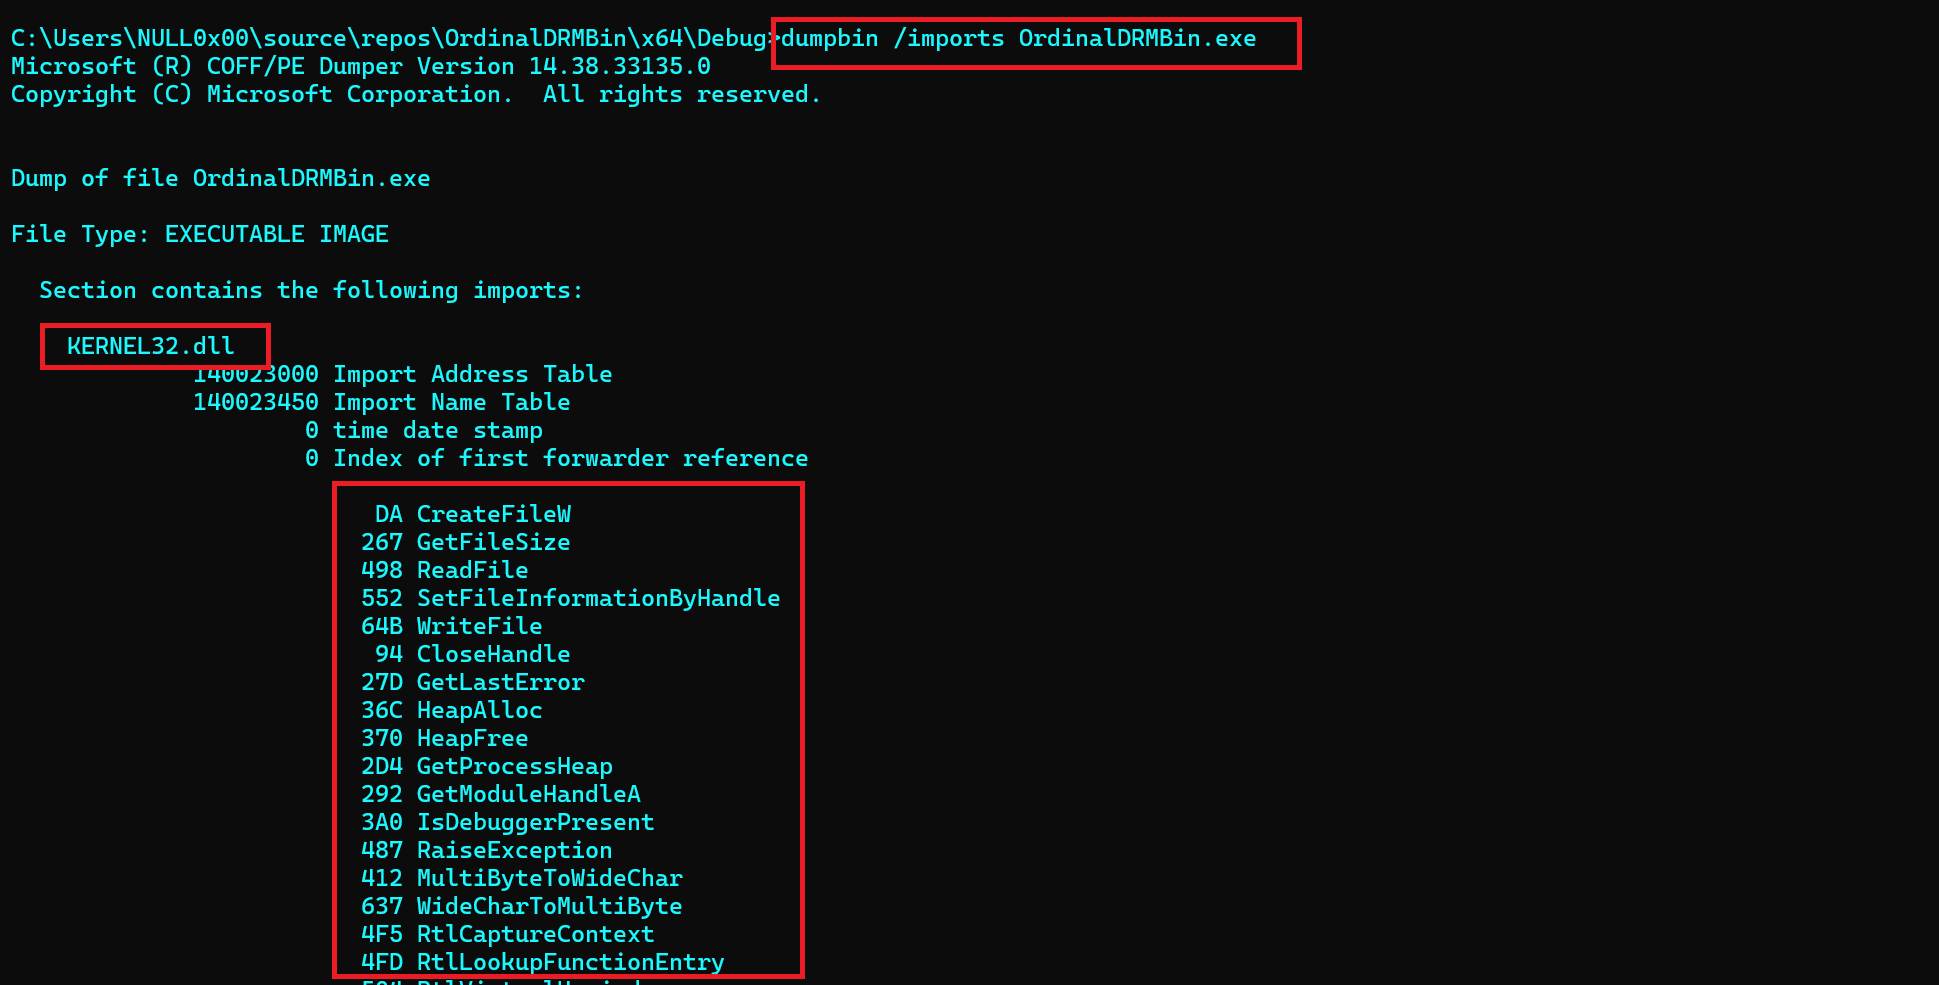 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 synacktiv/mojarragadget
Proof-of-concept exploit for a Java gadget chain in the Mojarra library, demonstrating deserialization vulnerability exploitation for versions 2.3…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development