
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
624 results
KernelFlirt preview

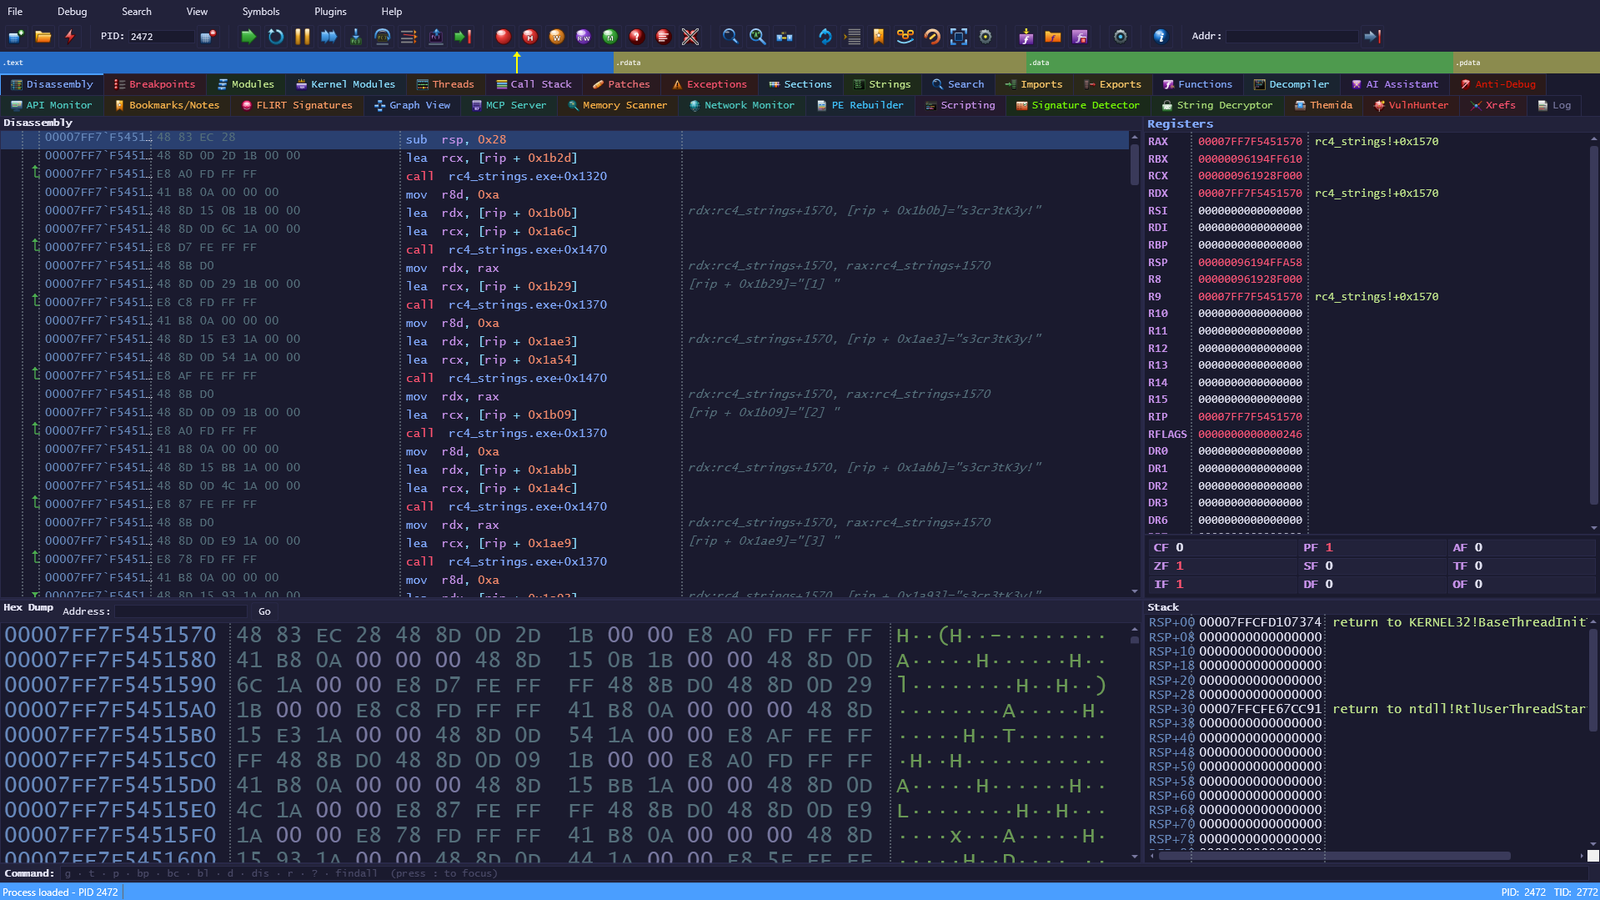
KernelFlirt

GitHubakatorich/kernelflirt

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…

ai-assisted-reversingai-securityanti-bot+9
324 months ago
Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis preview

Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis

GitHubkaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
binary-analysisdebuggersdigital-forensics+6
63 days ago
HookTools preview

HookTools

GitHubgmh5225/hooktools

Basic injectable for analyzing the behavior of evasive malware
binary-analysisdebuggersdefensive-tools+3
2 years ago
HWID-SteamSpywareTerminator preview

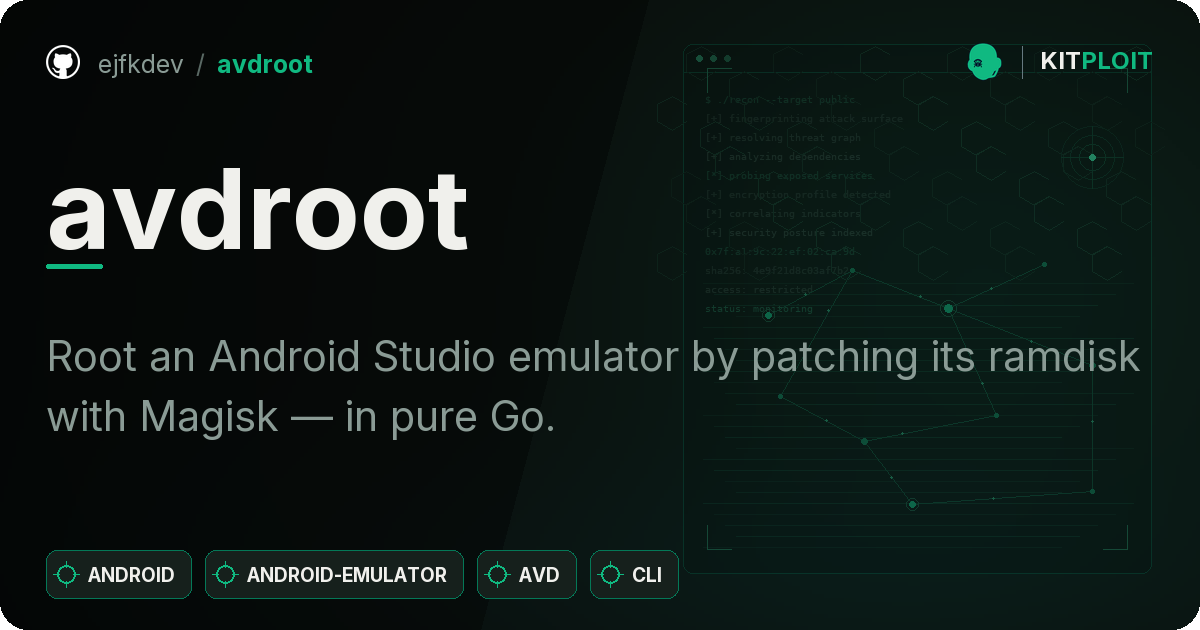
HWID-SteamSpywareTerminator

GitHubgmh5225/hwid-steamspywareterminator

Work-in-progress library injected into Steam to block the hidden CFillMachineInfoThread that collects HWID, disk, network adapter, and registry…
anti-botbinary-analysisdefensive-tools+3
14 years ago
avdroot preview

avdroot

GitHubejfkdev/avdroot

Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.

android-securitybinary-analysismobile-app-pentesting+6
316 days ago
ddc preview

ddc

GitHubejfkdev/ddc

DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI

android-securitybinary-analysiscode-analysis+6
3253 days ago
0 preview

0

GitHub0sec-labs/0

A cybersecurity harness for full-stack LLM-driven penetration testing. Find and fix vulnerabilities autonomously, 24/7. [RESEARCH PREVIEW]

ai-securitybinary-analysisdevsecops+6
1623 days ago
CVE-2026-46595-proof preview

CVE-2026-46595-proof

GitHubsdodson/cve-2026-46595-proof

Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…

binary-analysiscode-analysiscontainer-security+4
6 days ago
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

binary-analysiscryptographydefensive-tools+6
359 days ago
ceasta preview

ceasta

GitHubngwg/ceasta

disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…

ai-assisted-reversingbinary-analysisbinary-exploitation+6
1385 days ago
rdx preview

rdx

GitHubch0pin/rdx

A native APK and DEX decompiler written in Rust
android-securitybinary-analysiscode-analysis+6
13611h 22m ago
REx-skill preview

REx-skill

GitHubtihanyin/rex-skill

REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
ai-assisted-reversingbinary-analysisbinary-exploitation+8
998 days ago
CVE-2026-96515 preview

CVE-2026-96515

GitHubwhoami-012/cve-2026-96515

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…

binary-analysisembedded-systems-securityexploitation+7
7 days ago
recurse preview

recurse

GitHubrecurse-labs/recurse

Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
ai-assisted-reversingai-securitybinary-analysis+7
2841 day ago
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering

anti-botbinary-analysisdefensive-tools+4
33310 days ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
1610 days ago
discord-crasher preview

discord-crasher

GitHubaftermathlabs/discord-crasher

Some bugs found via binary instrumentation and fuzzing

binary-analysisdynamic-analysis-sandboxingexploitation+5
2316 days ago
Veridiff preview

Veridiff

GitHubveridiff/veridiff

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.

binary-analysisbinary-exploitationcode-analysis+7
616h 13m ago
Previous12…35Next