
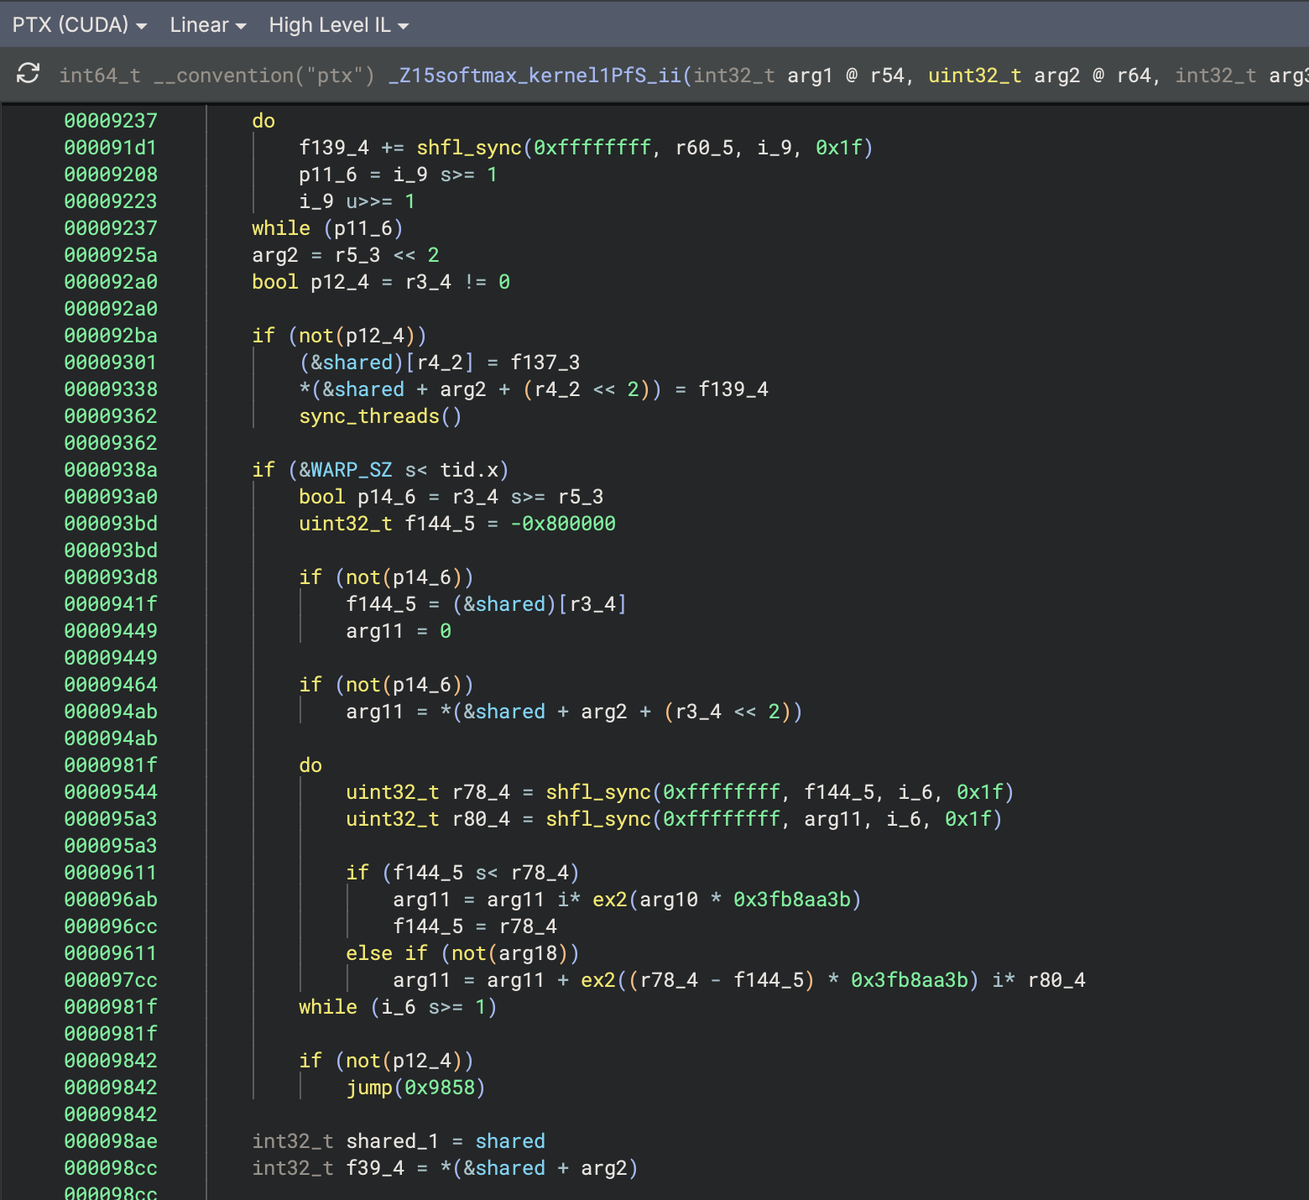
ptxNinja
 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
binary-analysiscode-analysishardware-iot-security+3
65
seekbytes/ptxninjaBinary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 george0papasotiriou/cve-2026-20404-mediatek-modem-remote-dos-rogue-base-station-scenario-
A MediaTek modem input validation issue can cause a system crash (remote DoS) when a UE connects to a rogue base station controlled by an attacker…
 xingchenrs/cybermeowfians
The next stage of CyberMeowfil (CVE-2026-43499 and 43074),Possibly biased toward vivo devices?
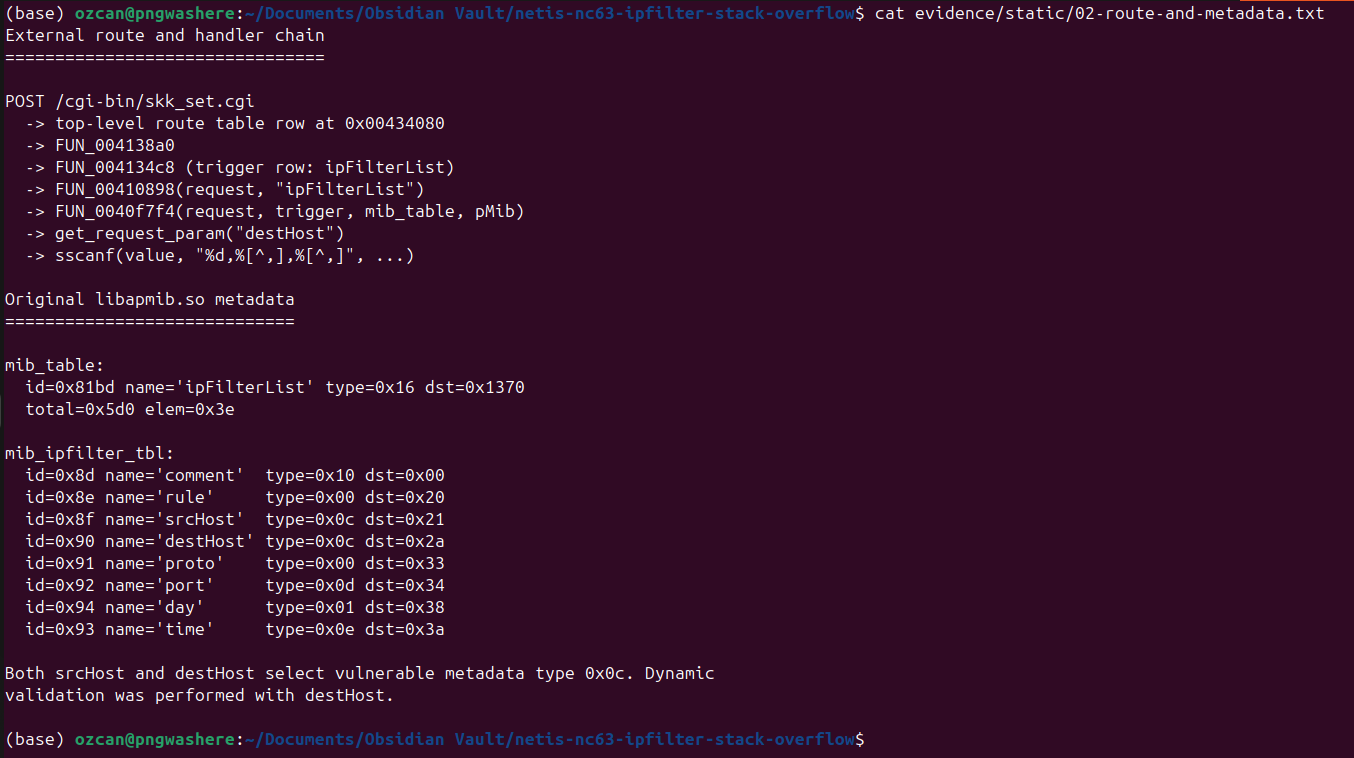 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 chichou/vscode-frida
Unofficial frida extension for VSCode
 cq674350529/pocs_slides
my advisory, poc, slides and scripts related to IoT/protocol security
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
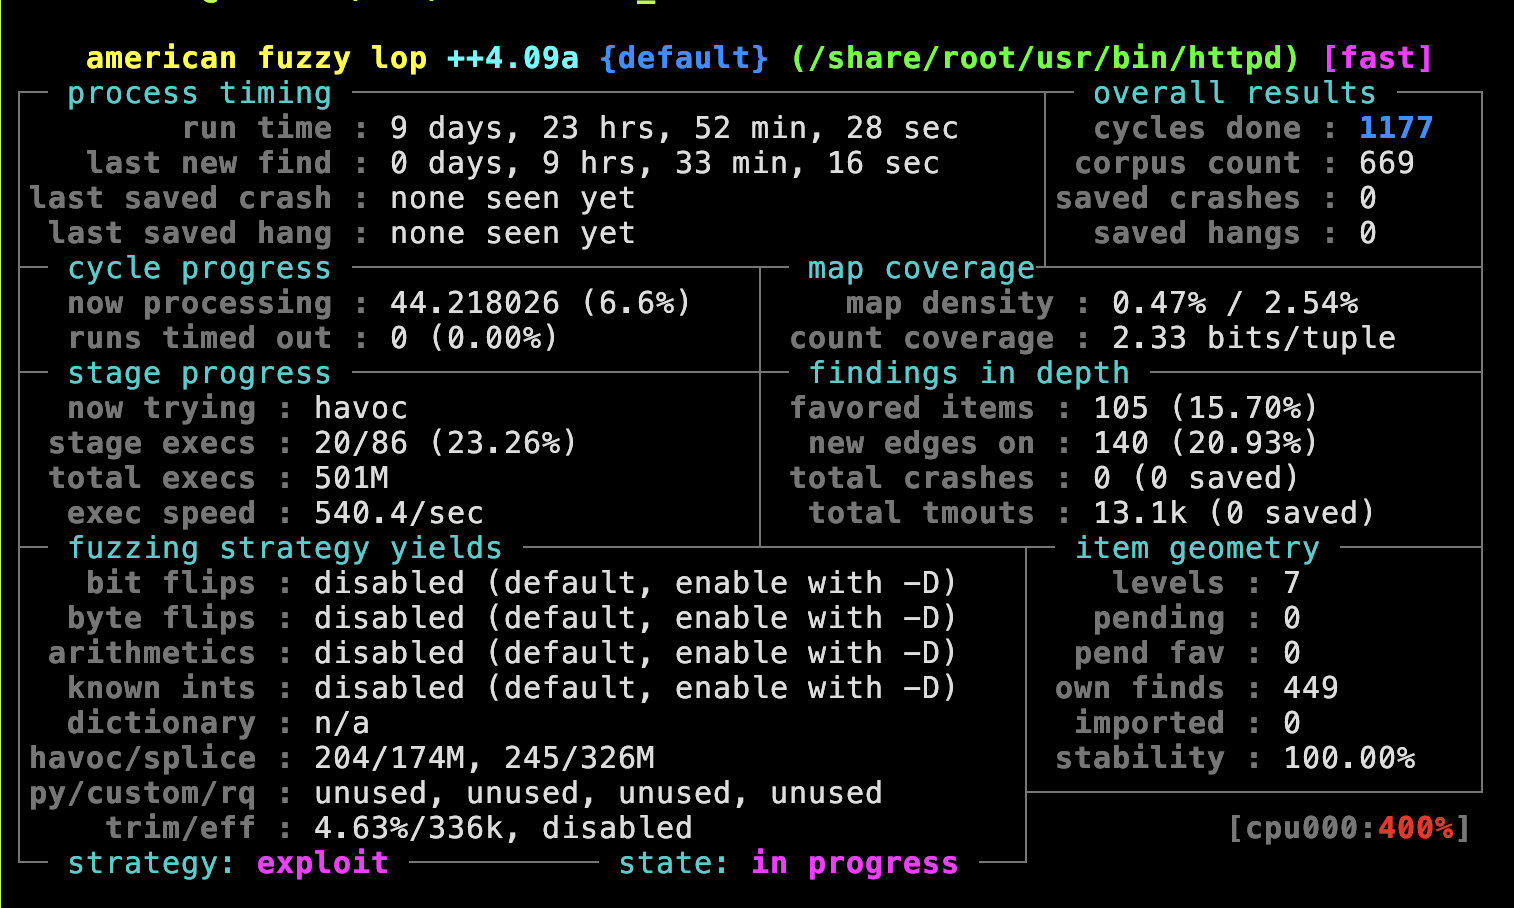 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
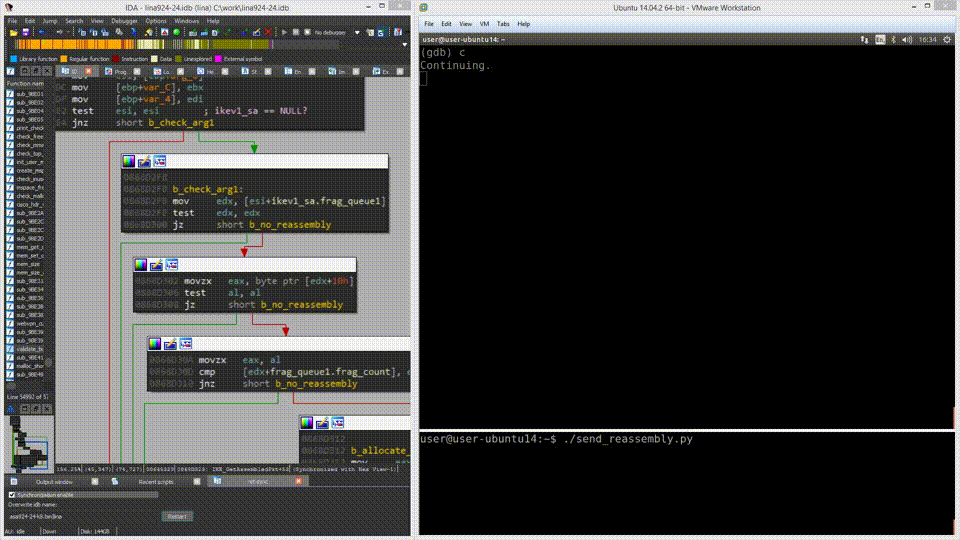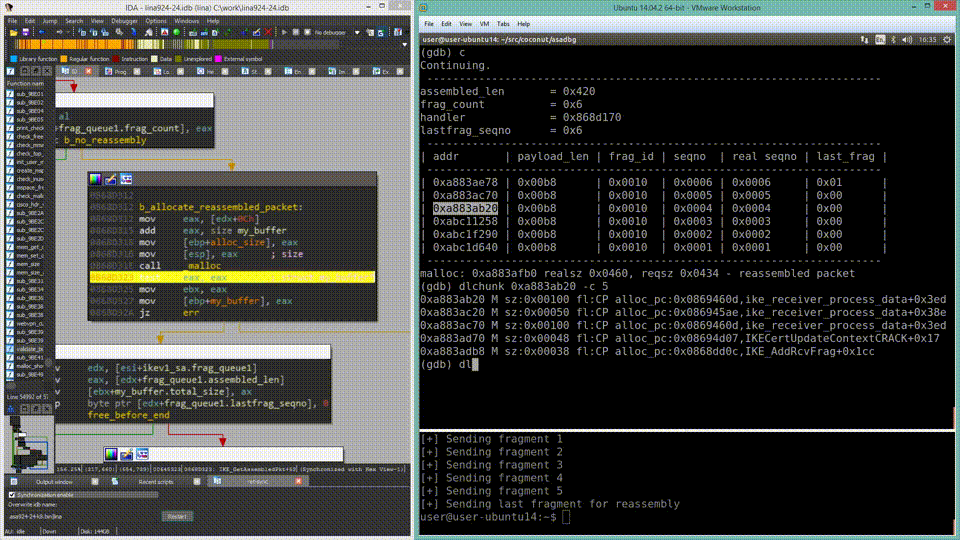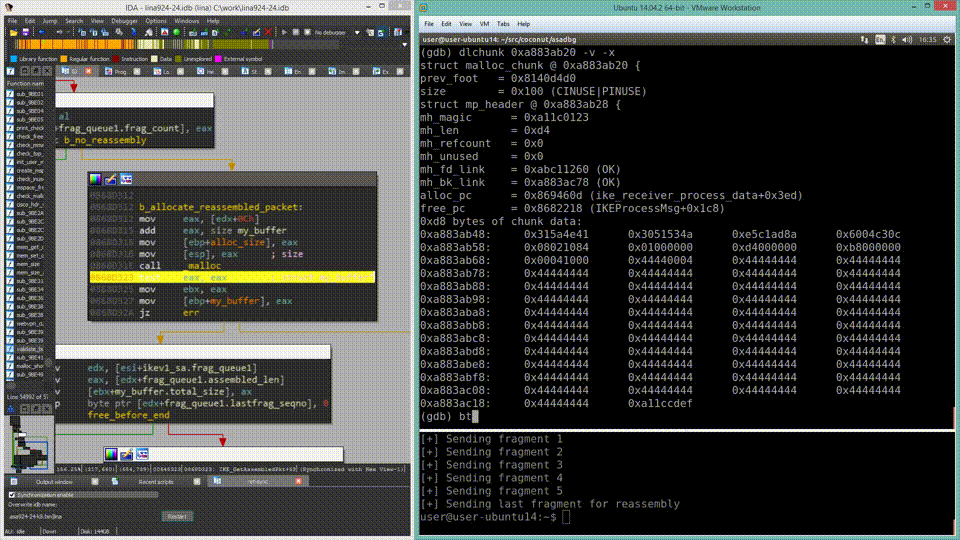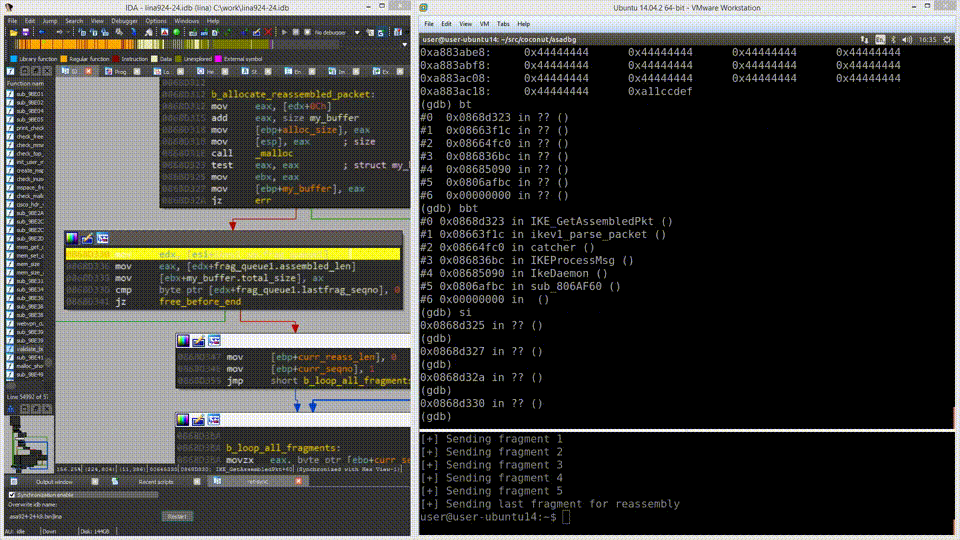 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 0xjohnnydev/webkit-navigationapi-sop-bypass
WebKit NavigateEvent.canIntercept SOP bypass via cross-port interception — iOS 26.3.1 BSI (CVE-2026-20643)
 olafdaf/cve-2022-40363
A buffer overflow in the component nfc_device_load_mifare_ul_data of Flipper Devices Inc., Flipper Zero before v0.65.2 allows attackers to cause a…
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 bootleg/ret-sync
ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…
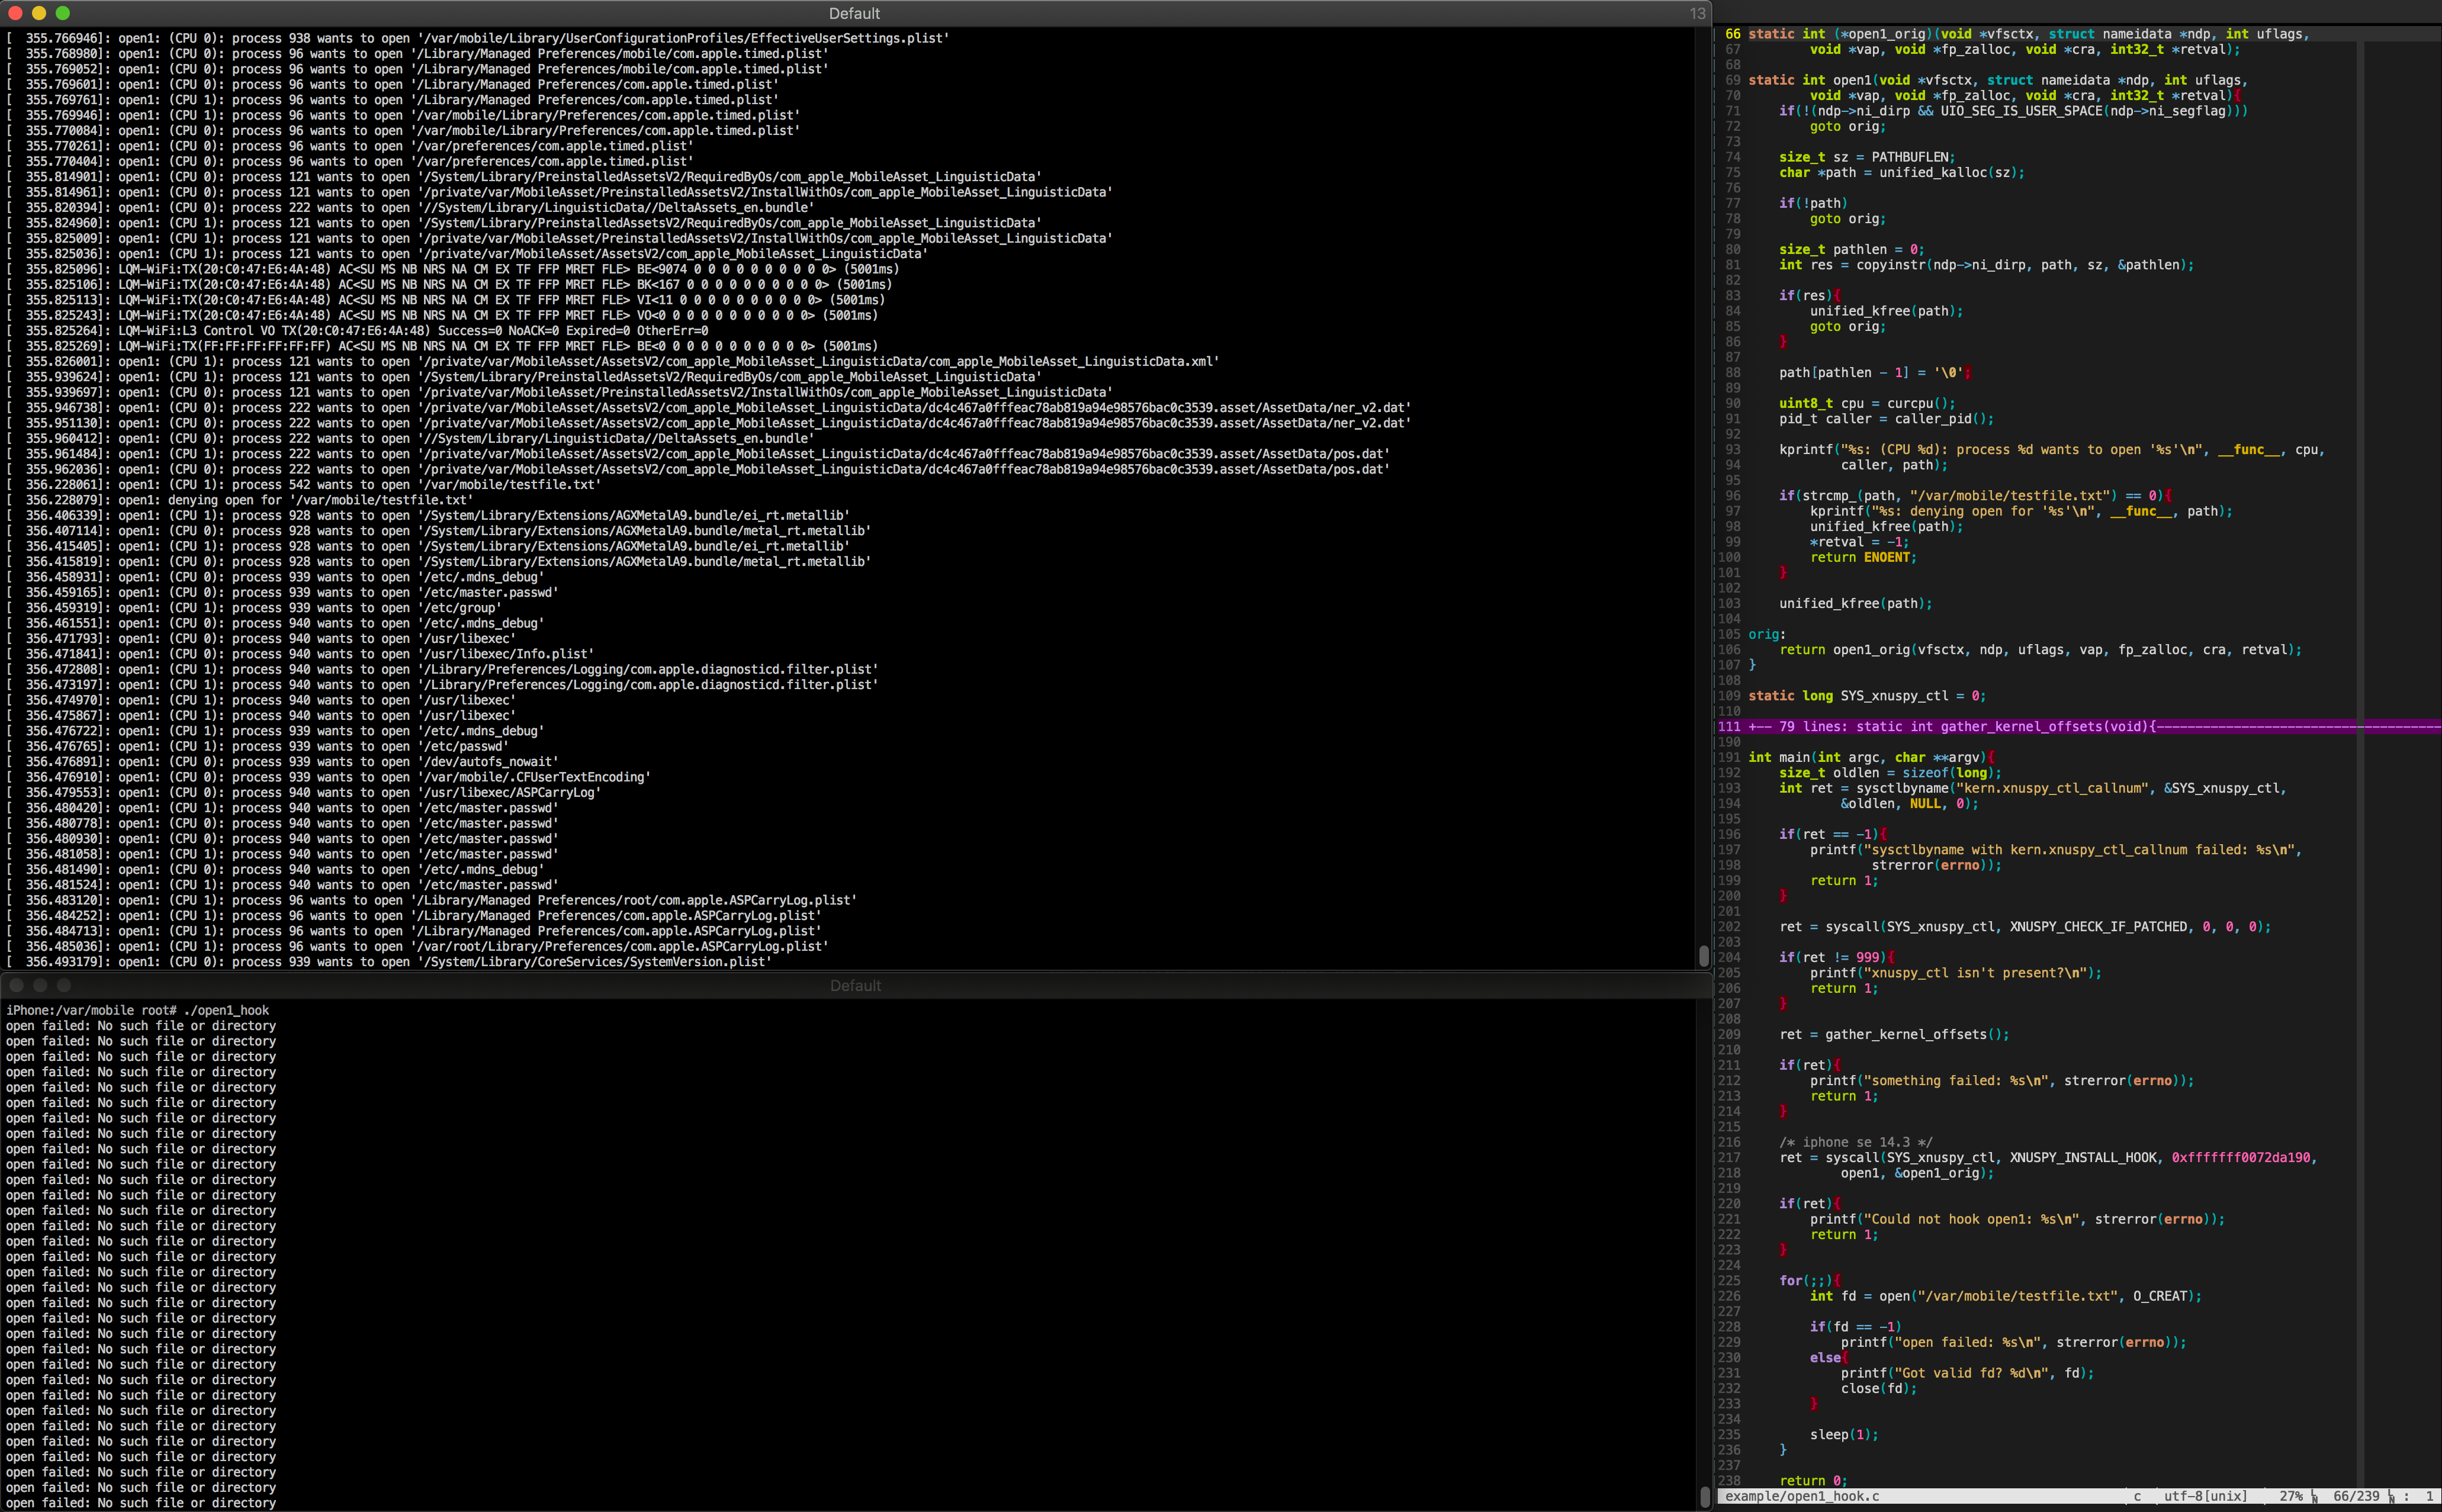 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices