

entropystrip
 dwexi/entropystrip
Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine
binary-analysisdefensive-toolsdigital-forensics+6
85 days ago
dwexi/entropystripAlgorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine
 67-6f-64/antioreans-codedevirtualizer
IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 misterdengi/cve-2026-1801c
Static reverse-engineering analysis of movement input heuristics in Source 2 engine, identifying structural edge cases in input automation and jump…
 sneakynachos/cve-2026-74936-gc-potato
Reproduction of a WebAssembly use-after-free vulnerability in Mozilla's JavaScript engine, demonstrating a deterministic race condition and providing…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
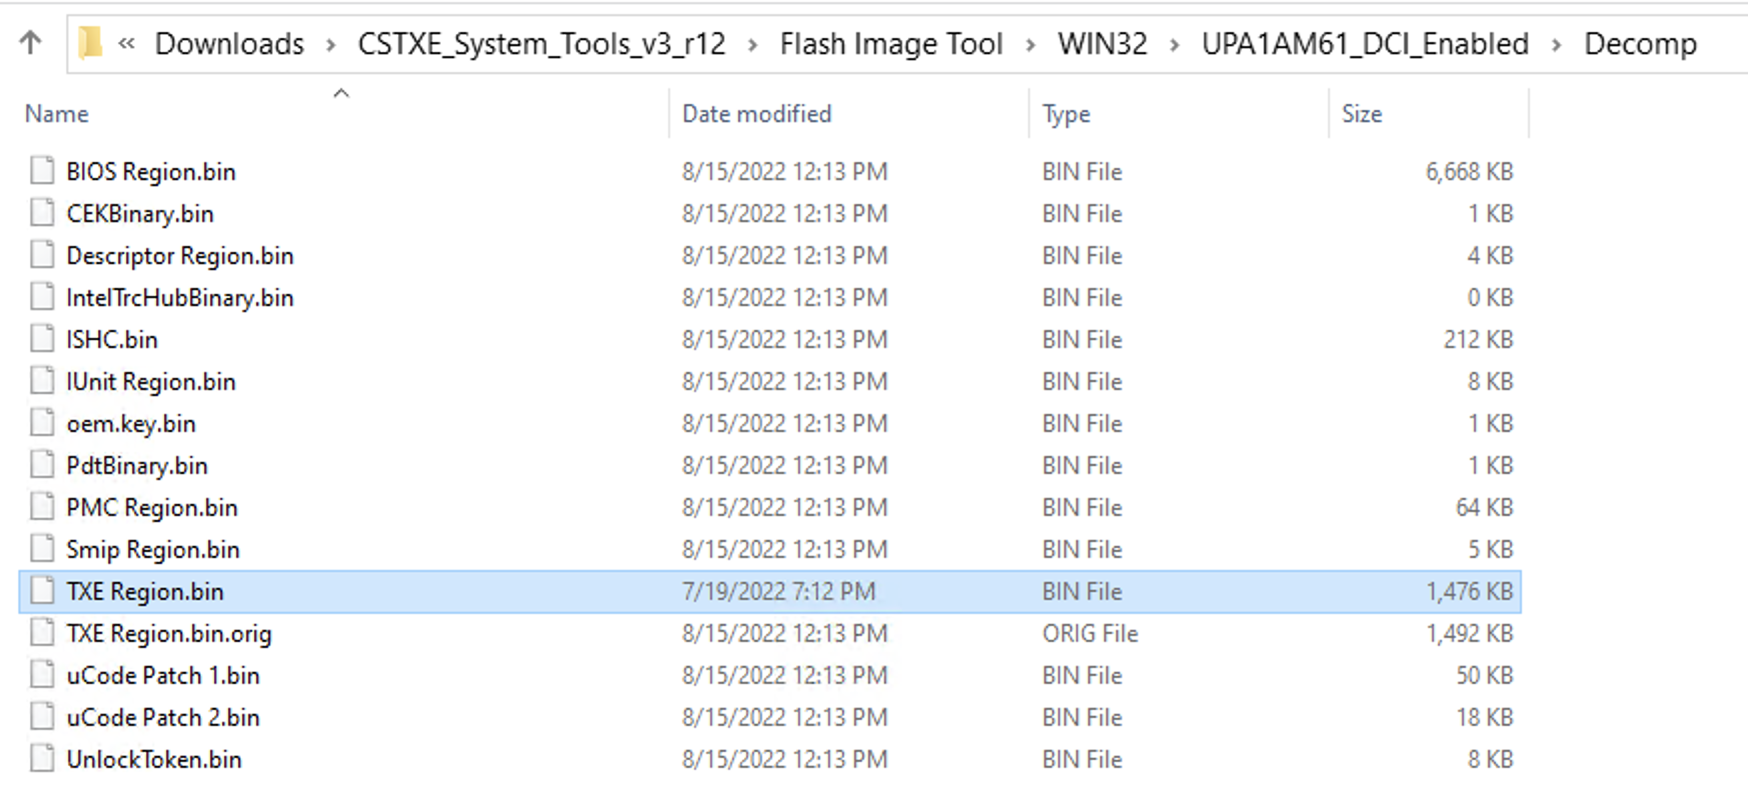 xenokovah/inteltxe-poc
Intel Management Engine JTAG Proof of Concept - 2022 Instructions
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)