ceasta
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
138
ngwg/ceastadisassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 0sec-labs/0
A cybersecurity harness for full-stack LLM-driven penetration testing. Find and fix vulnerabilities autonomously, 24/7. [RESEARCH PREVIEW]
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 tomer8007/widevine-l3-decryptor
A Chrome extension that demonstrates bypassing Widevine L3 DRM
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
 0xax/linux-insides
A book-in-progress about the Linux kernel and its insides.
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 grizzzer/cve-2026-42978-poc-research
CVE-2026-42978 — Use-After-Free race condition in Windows Push Notifications (WpnService). Patch diff, root cause analysis, TOCTOU lab, Sysmon/ETW…
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
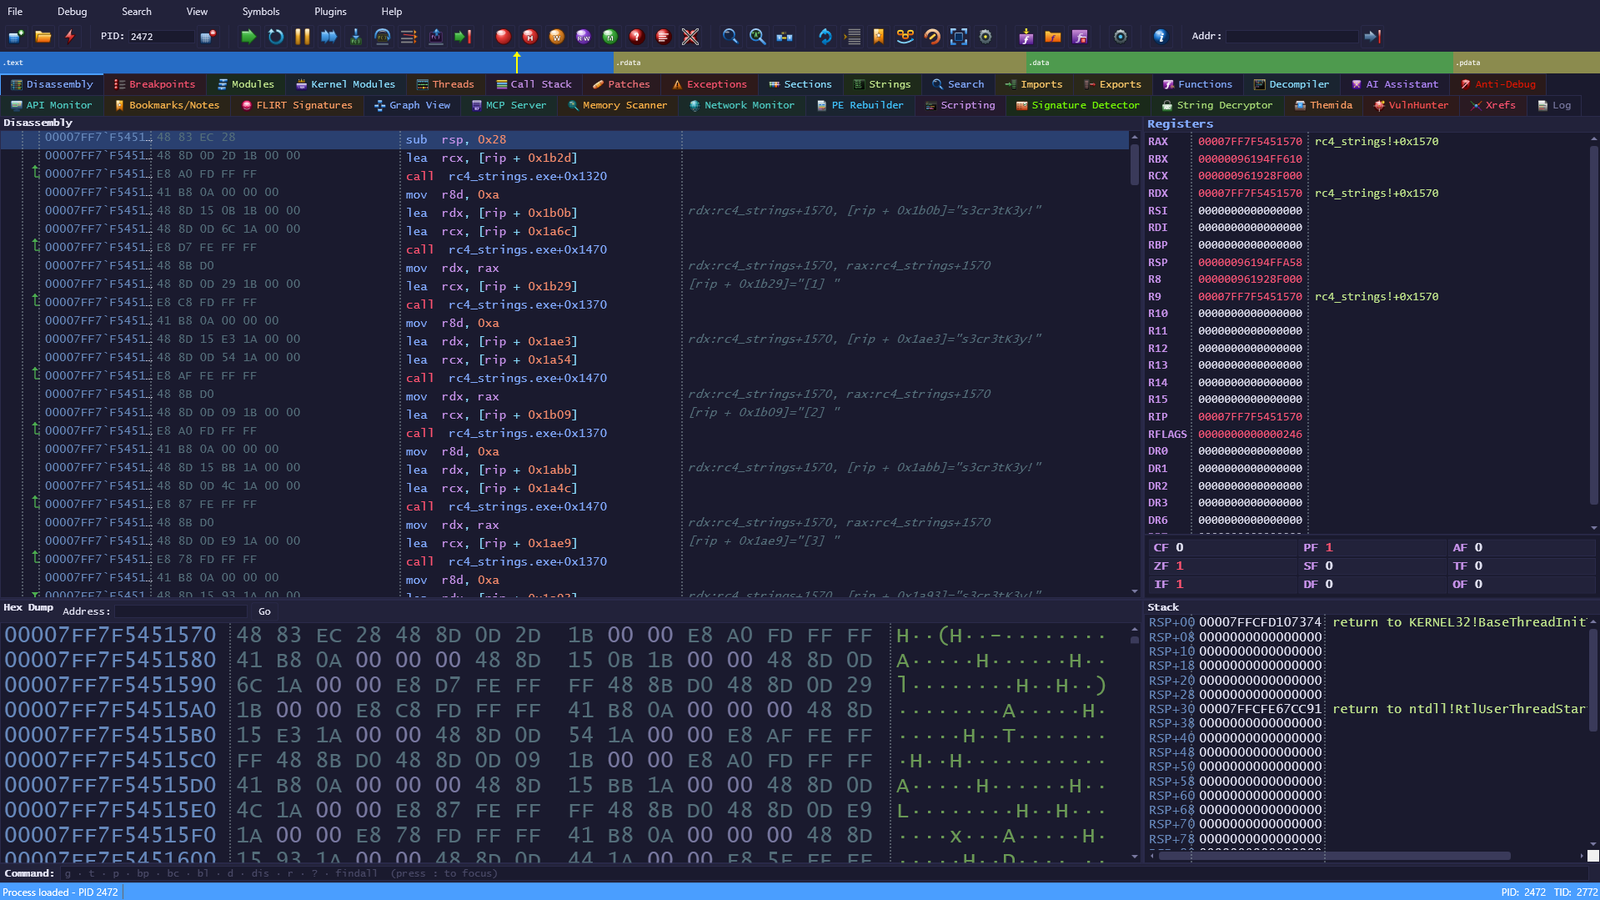 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 zznop/sploit
Go package that aids in binary analysis and exploitation