ablation
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
ai-assisted-reversingandroid-securitybinary-analysis+7
66
ablation-tool/ablationReverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
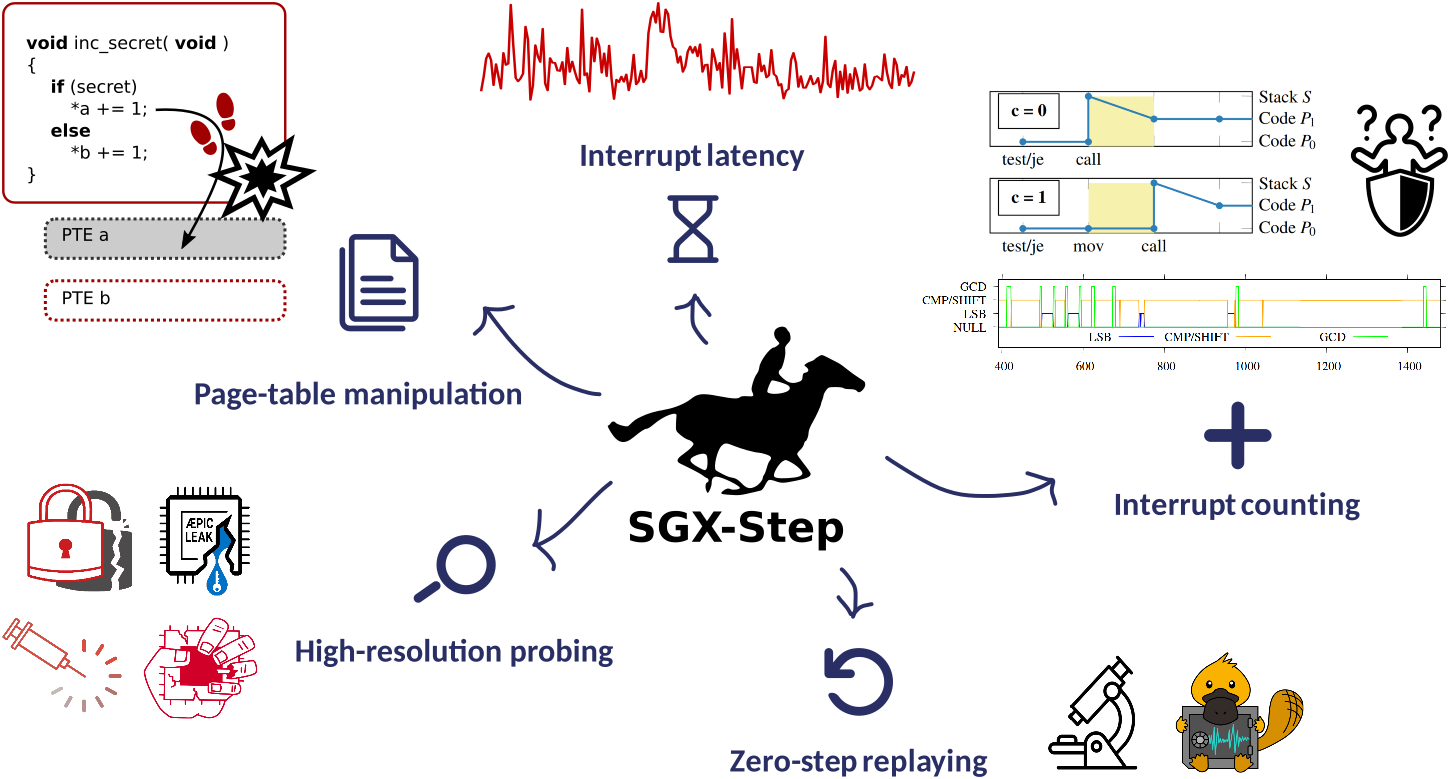 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
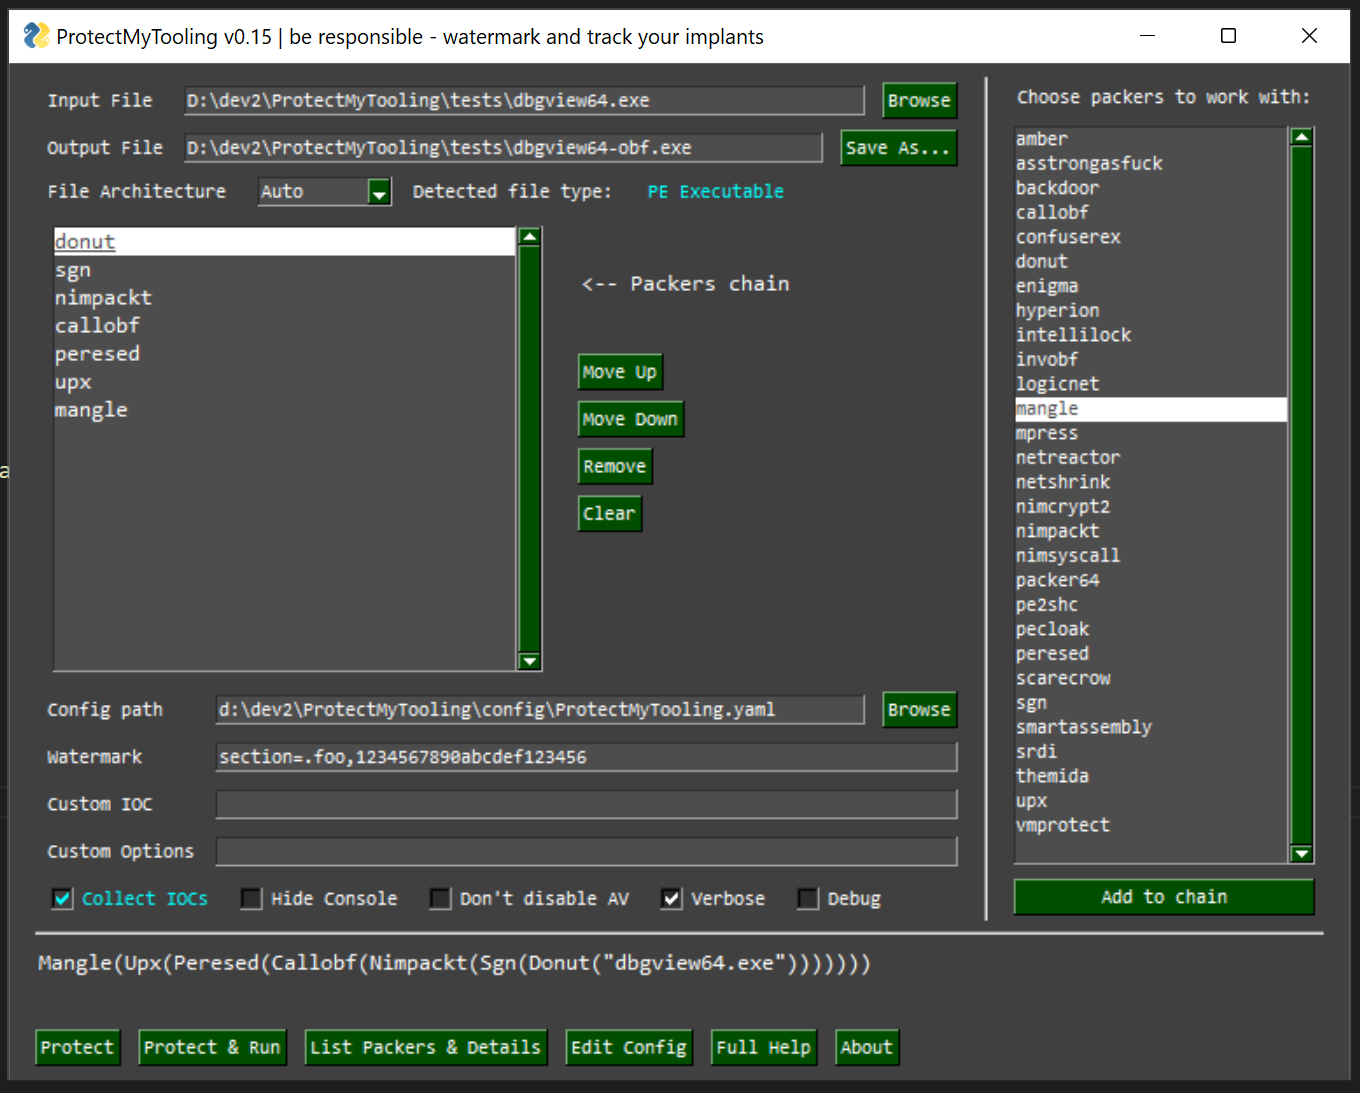 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 ptswarm/reflutter
Flutter Reverse Engineering Framework
 reverseclabs/needle
The iOS Security Testing Framework
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
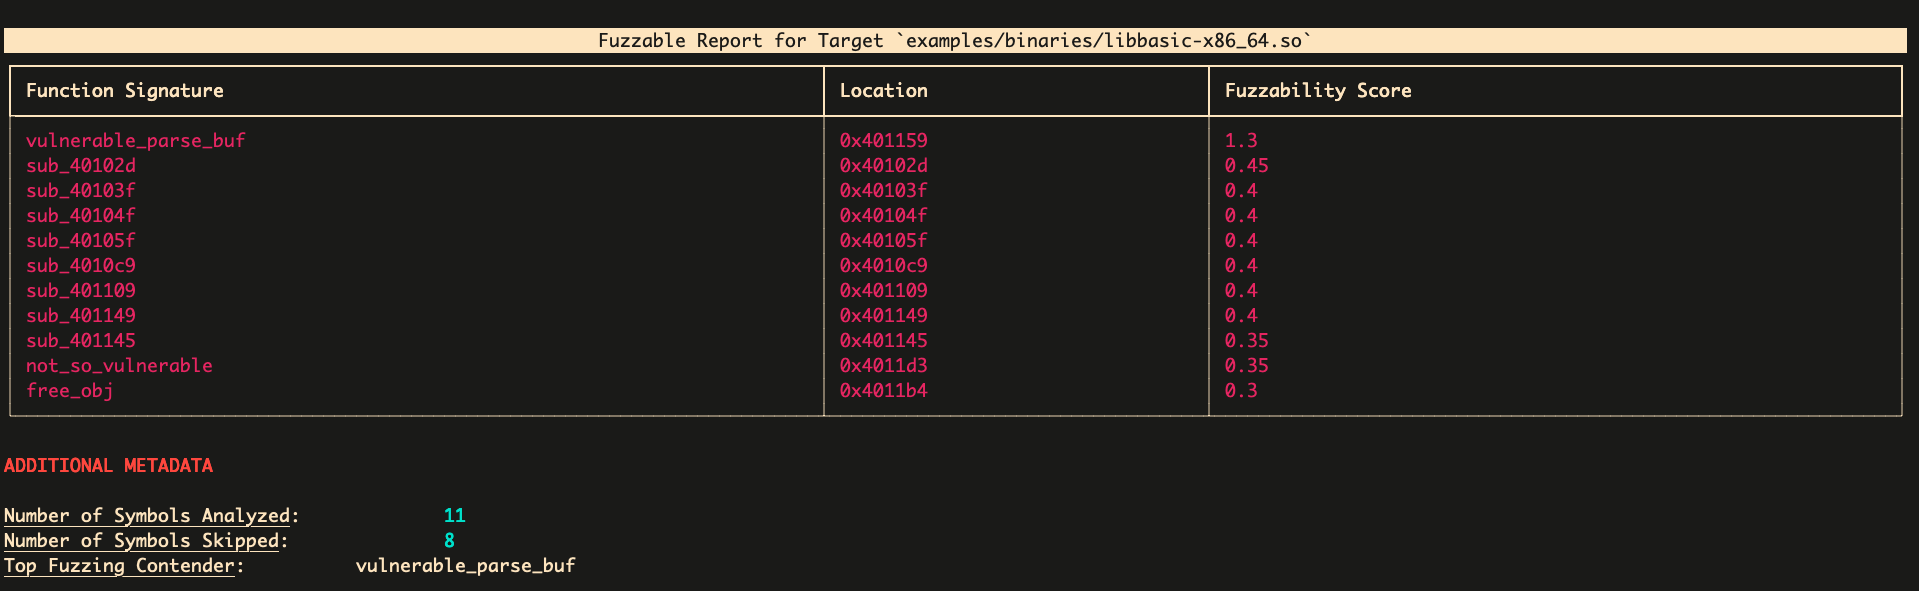 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!