ghidra-firmware-utils

Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…

Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

IoT firmware identification and extraction

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

Windows memory hacking library

EMBA - The firmware security analyzer

A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

A byte code analyzer for finding deserialization gadget chains in Java applications

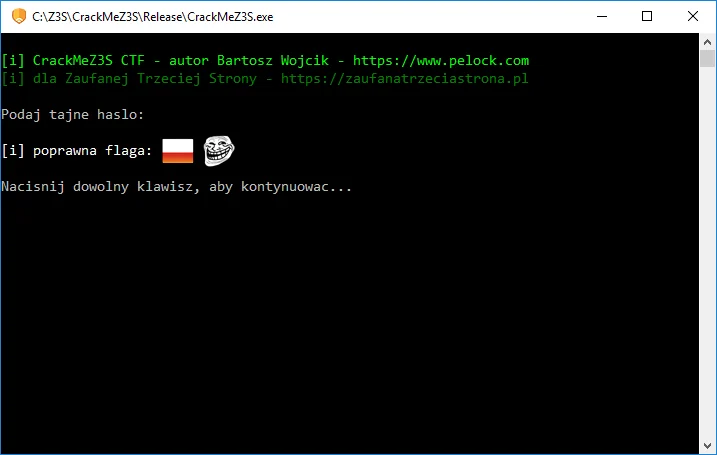
How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

Analysis for stage1 shellcode loader from hacking

idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro

Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…

Firmware Analysis Tool

A tool for UEFI firmware reverse engineering

Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…