
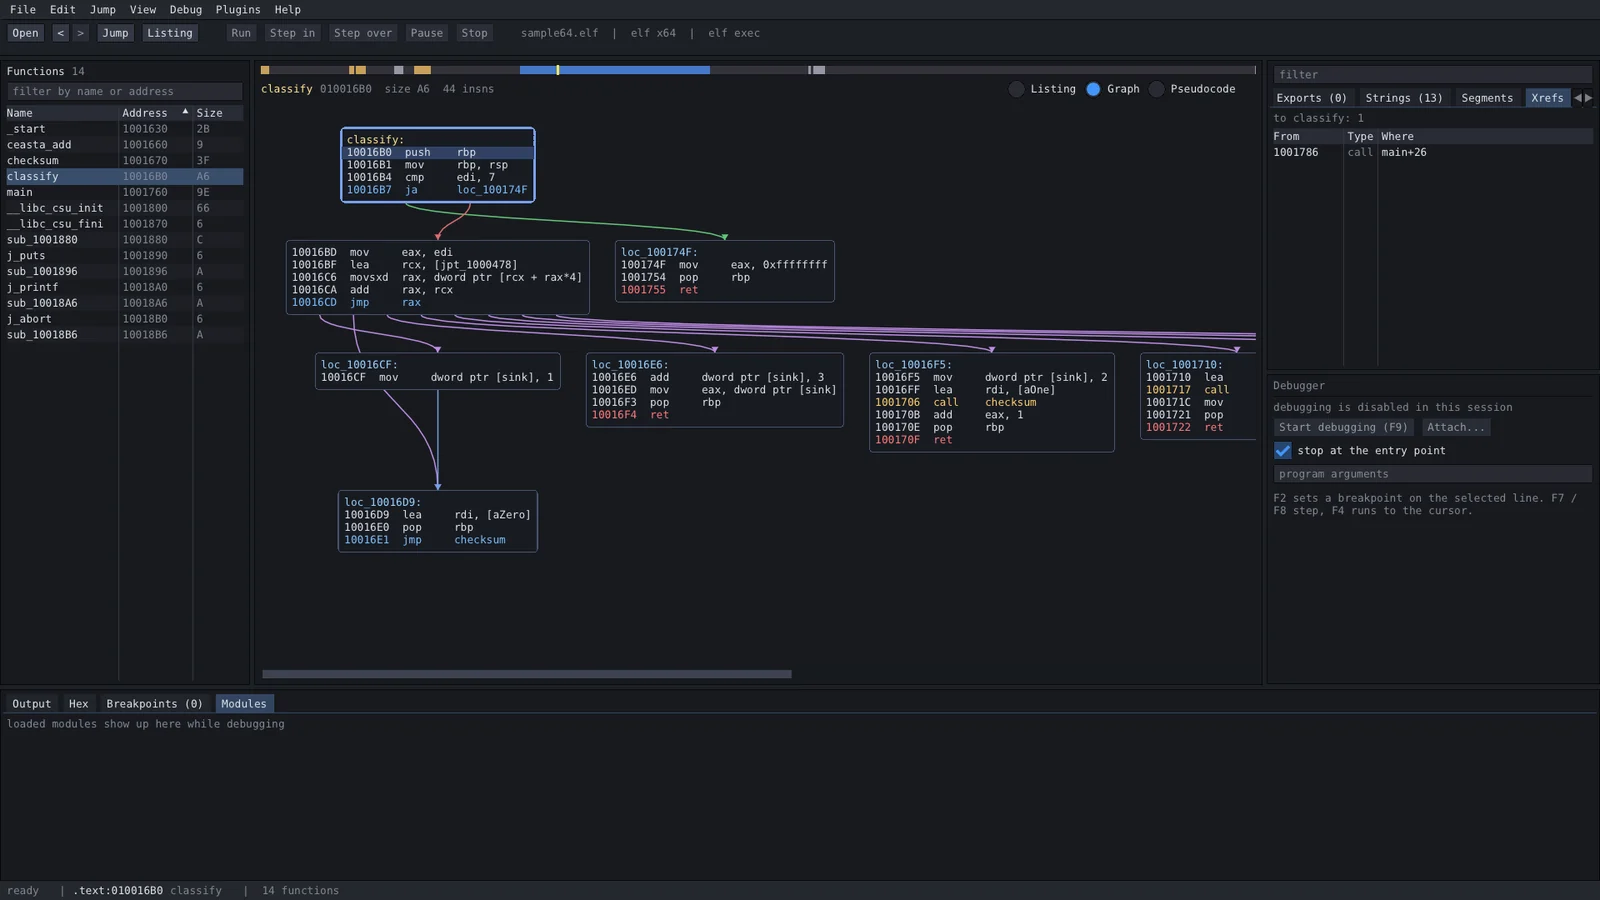
ceasta
 ngwg/ceasta
reverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
25
ngwg/ceastareverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
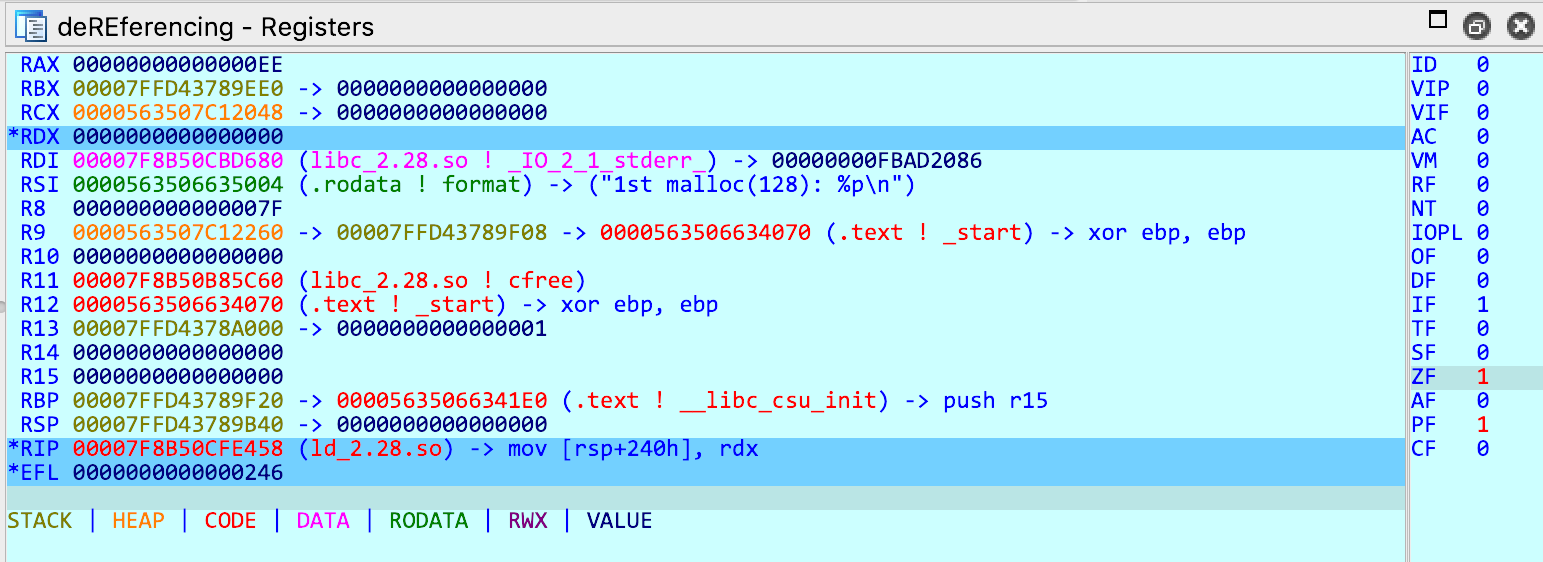 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views
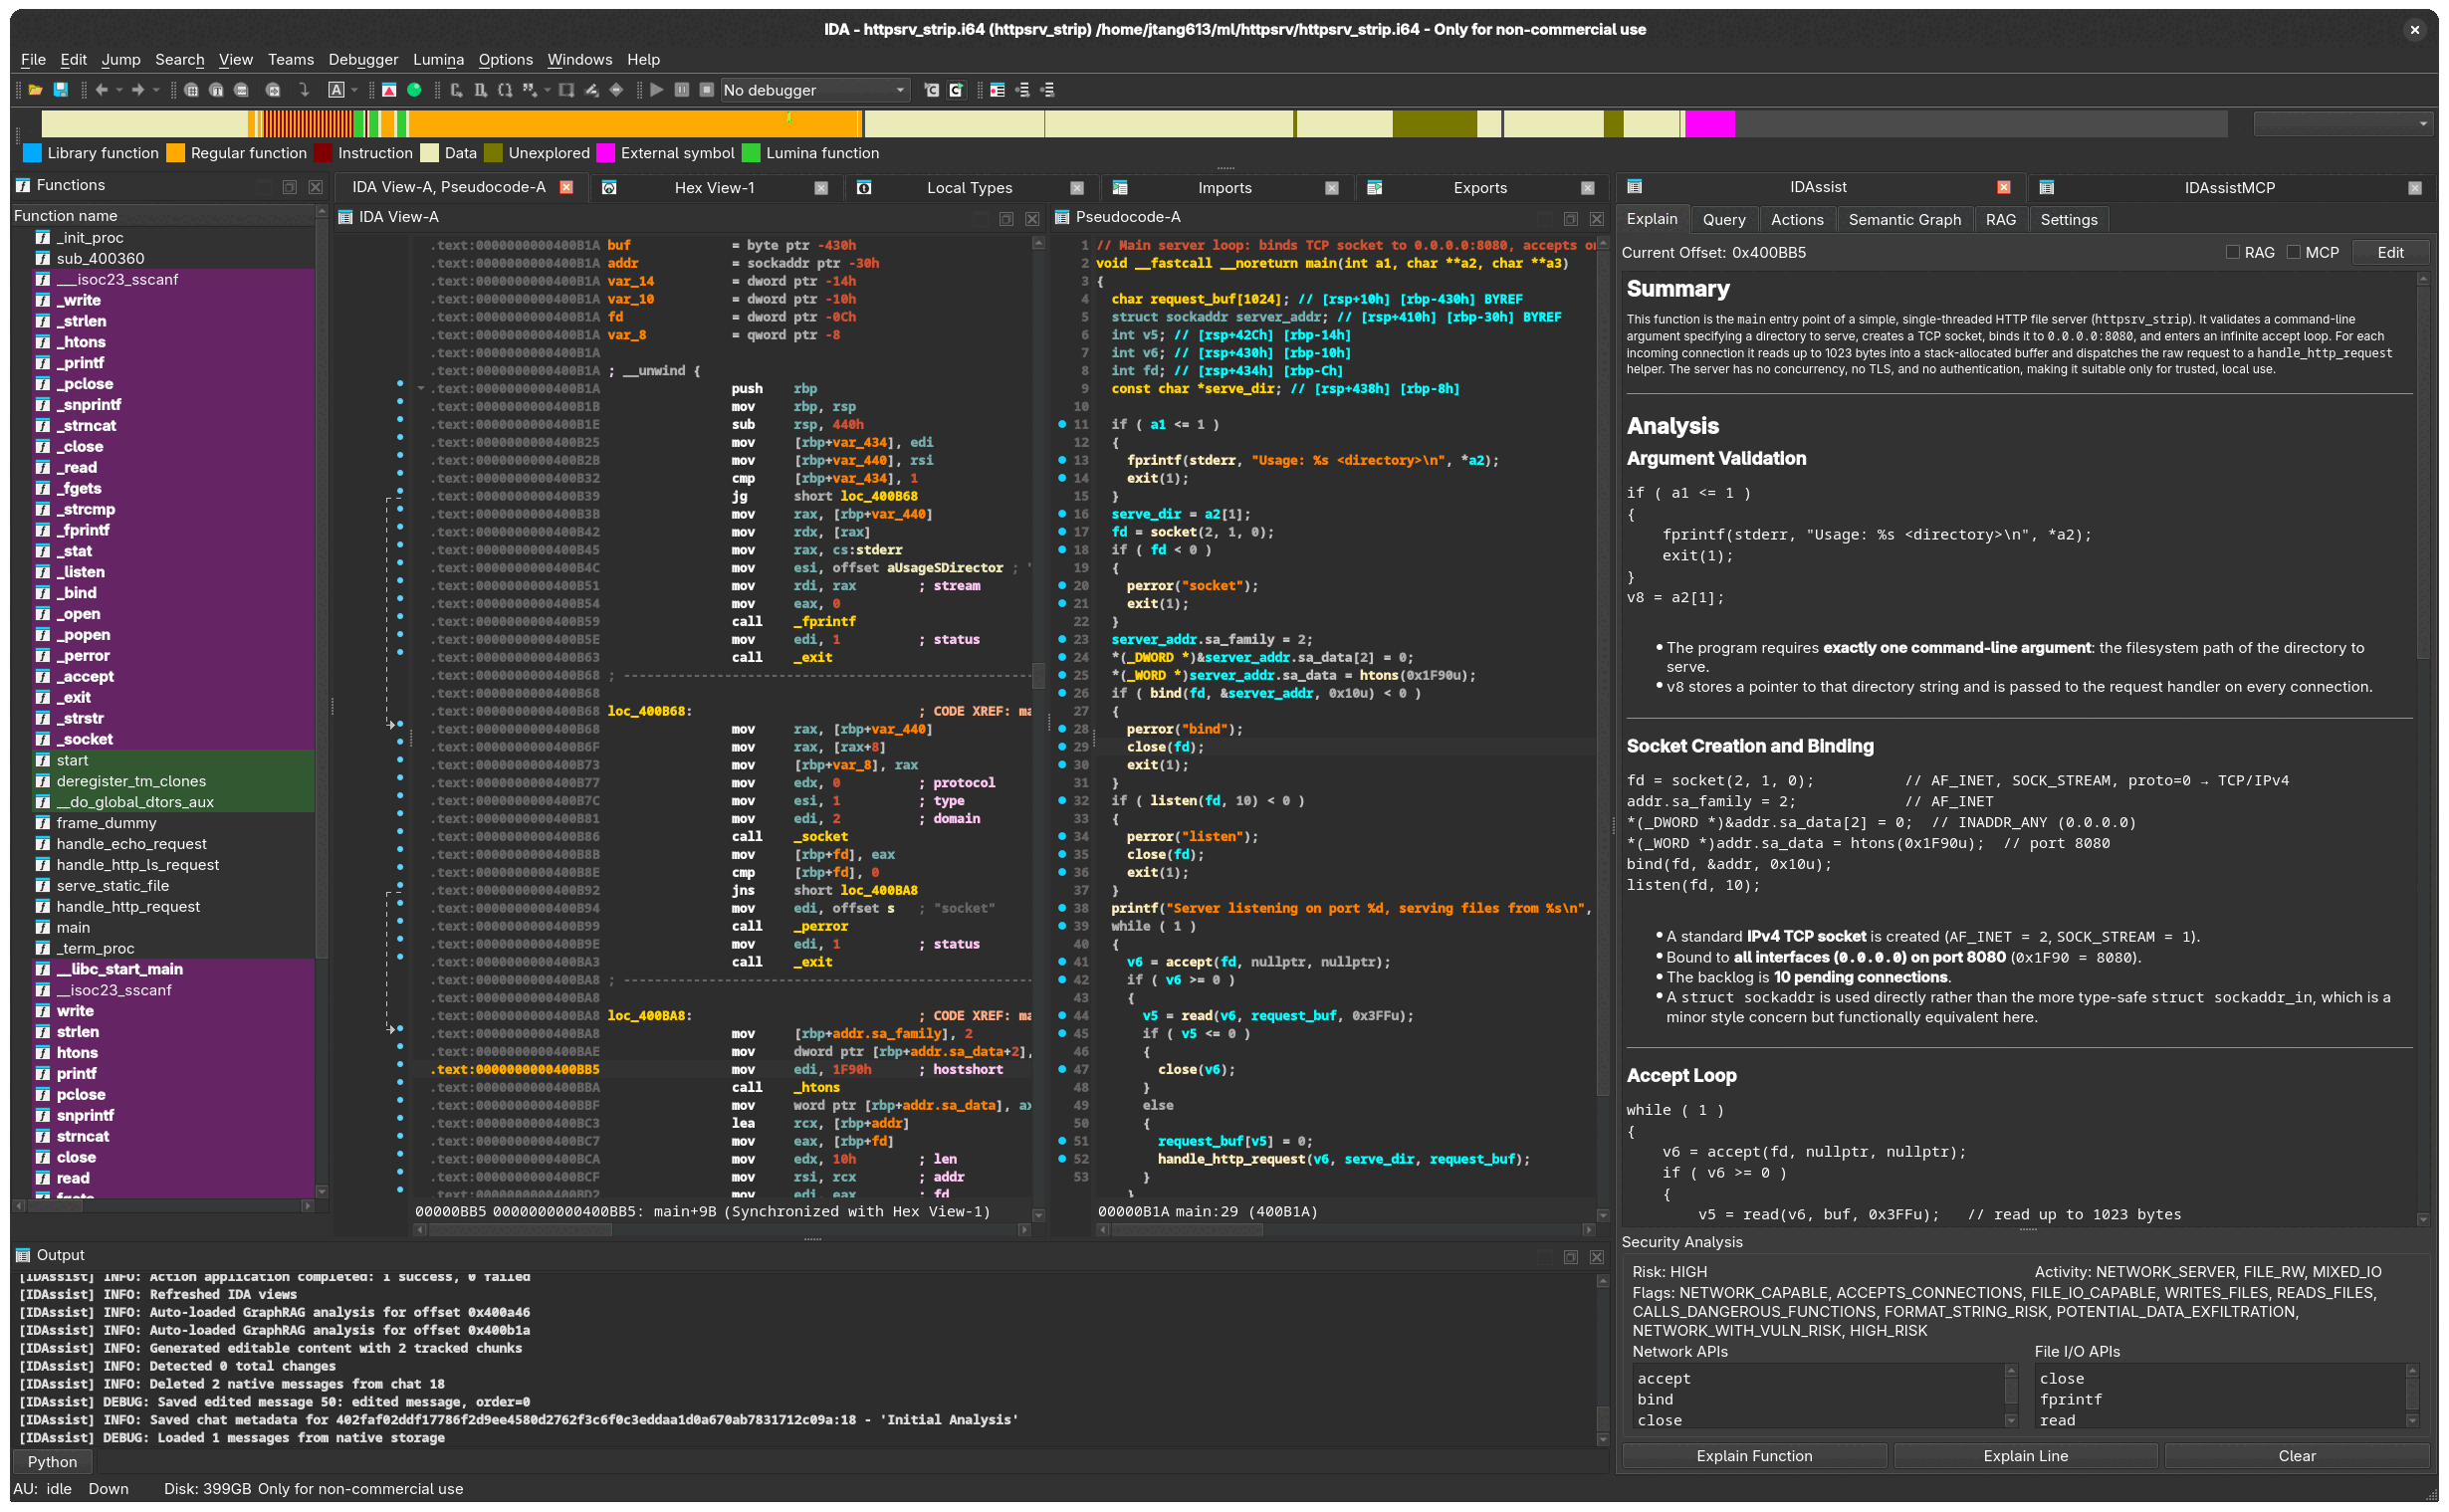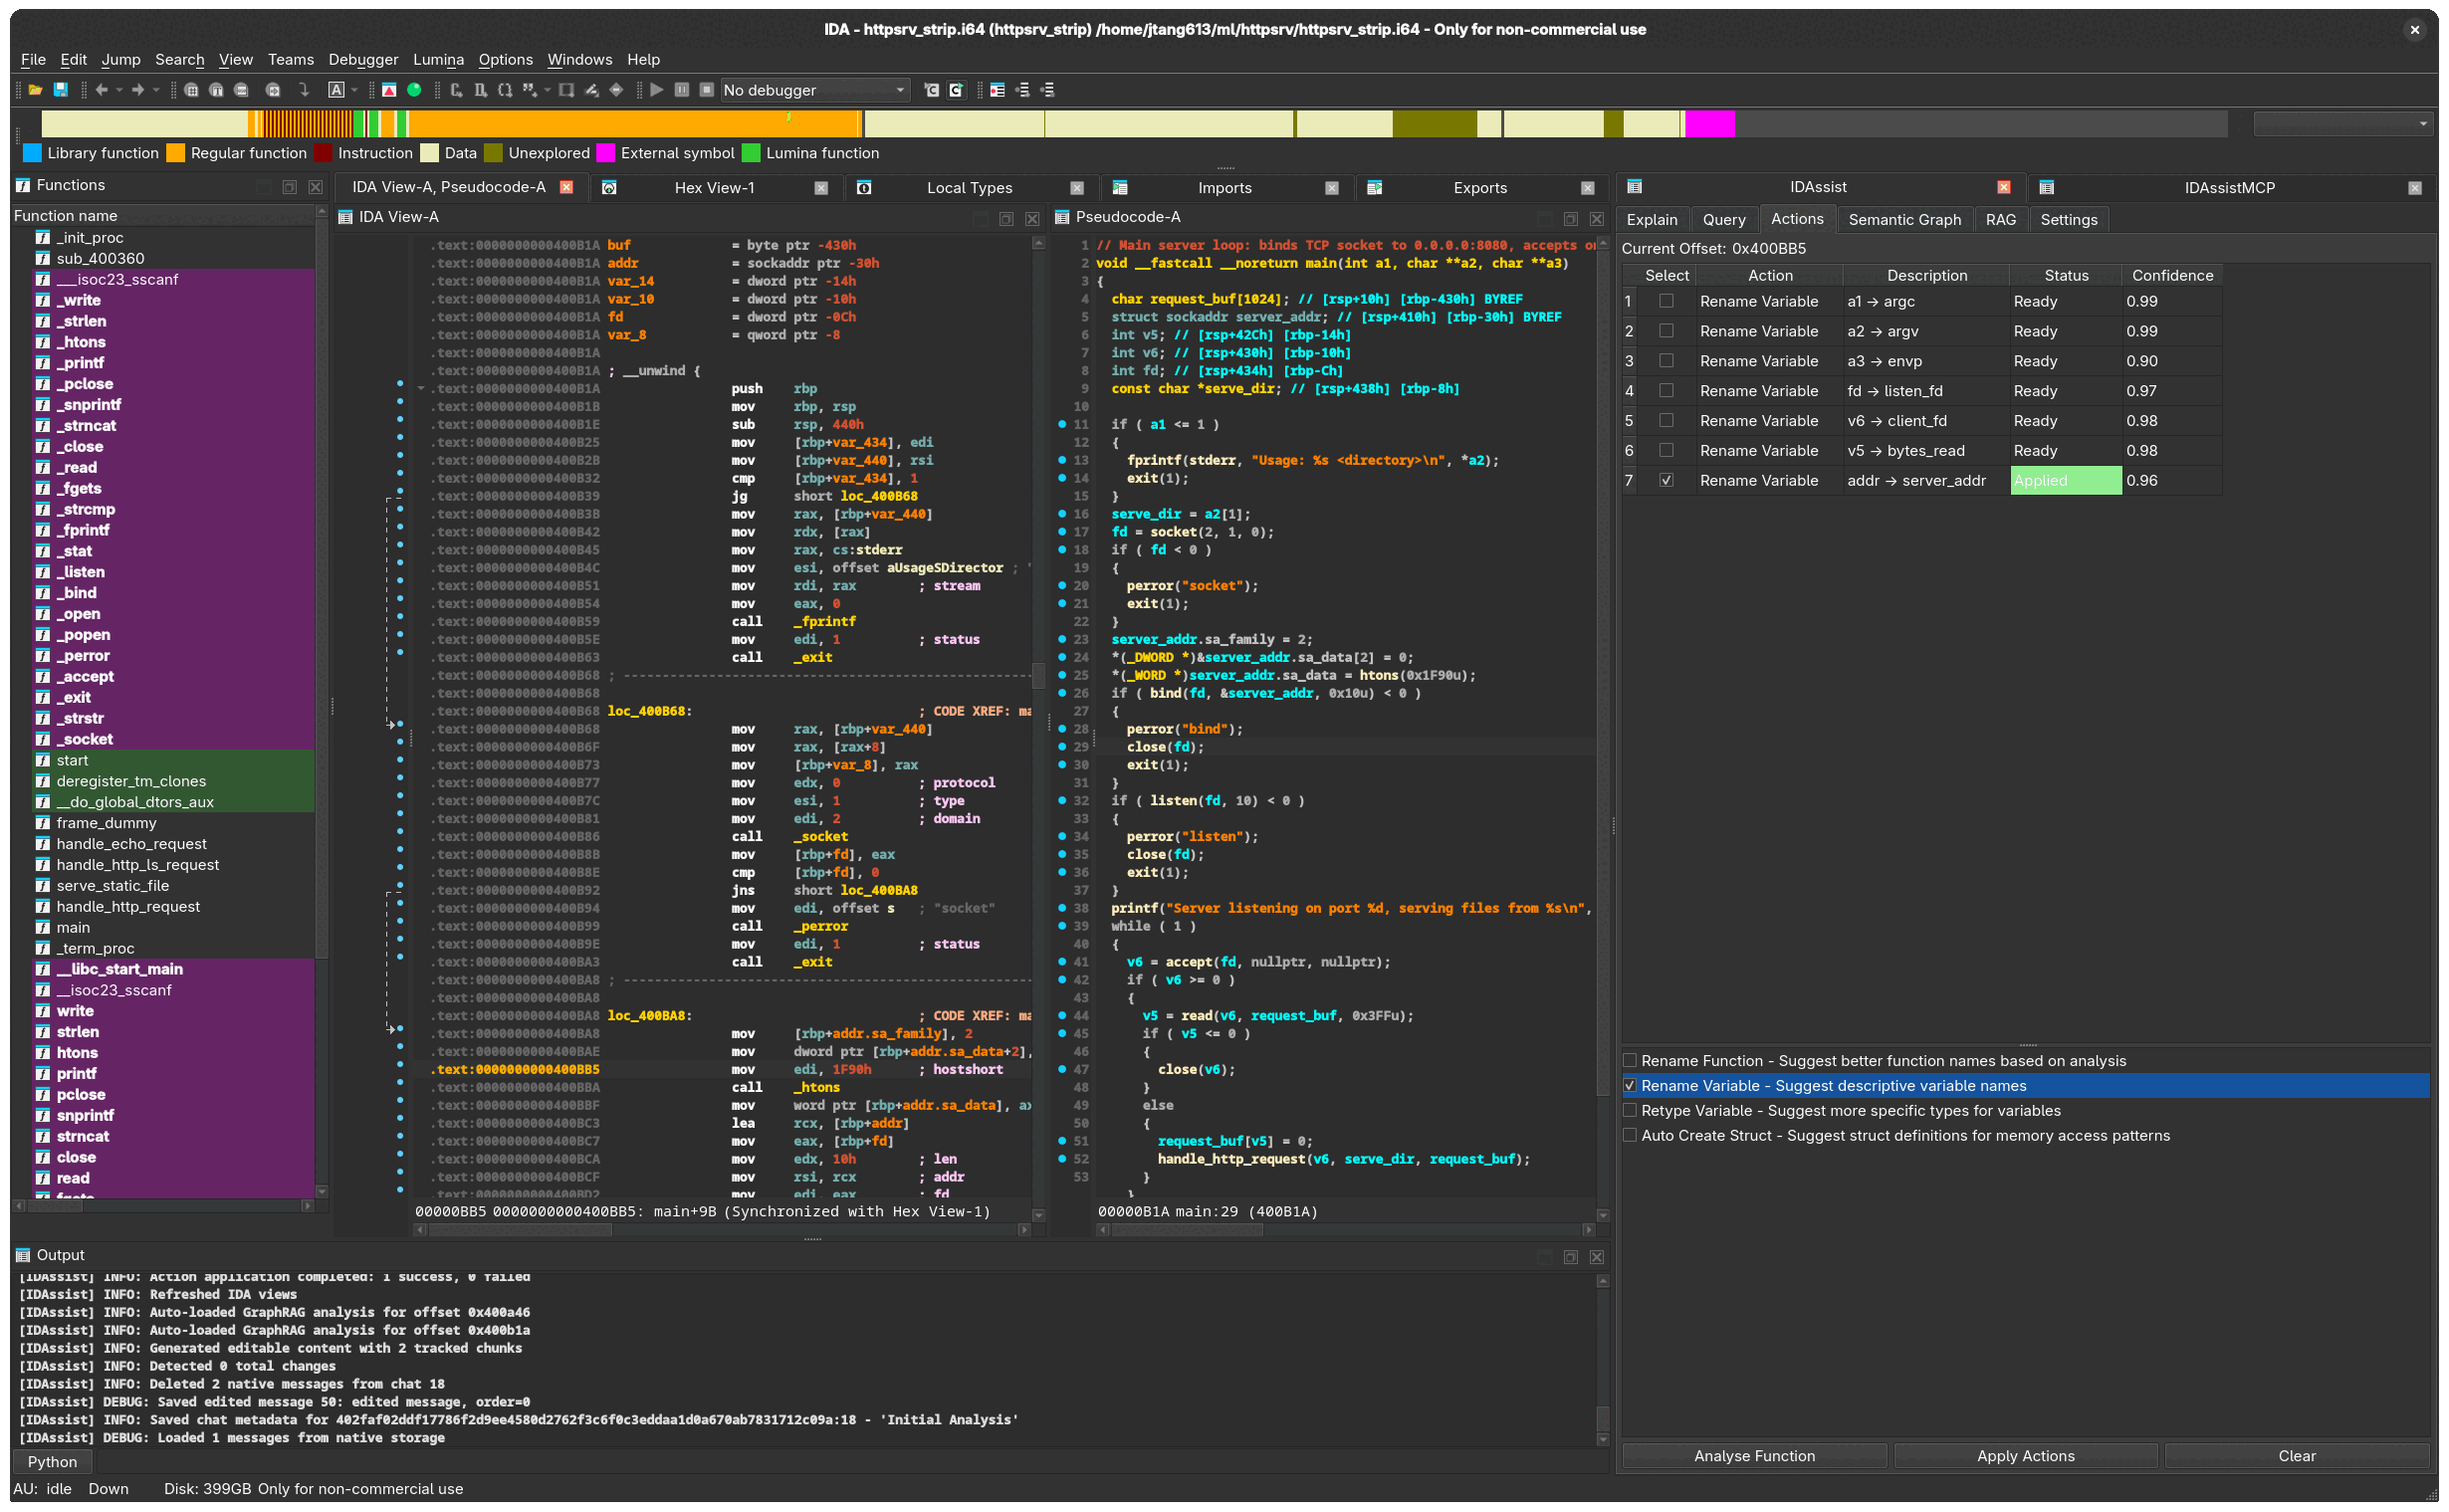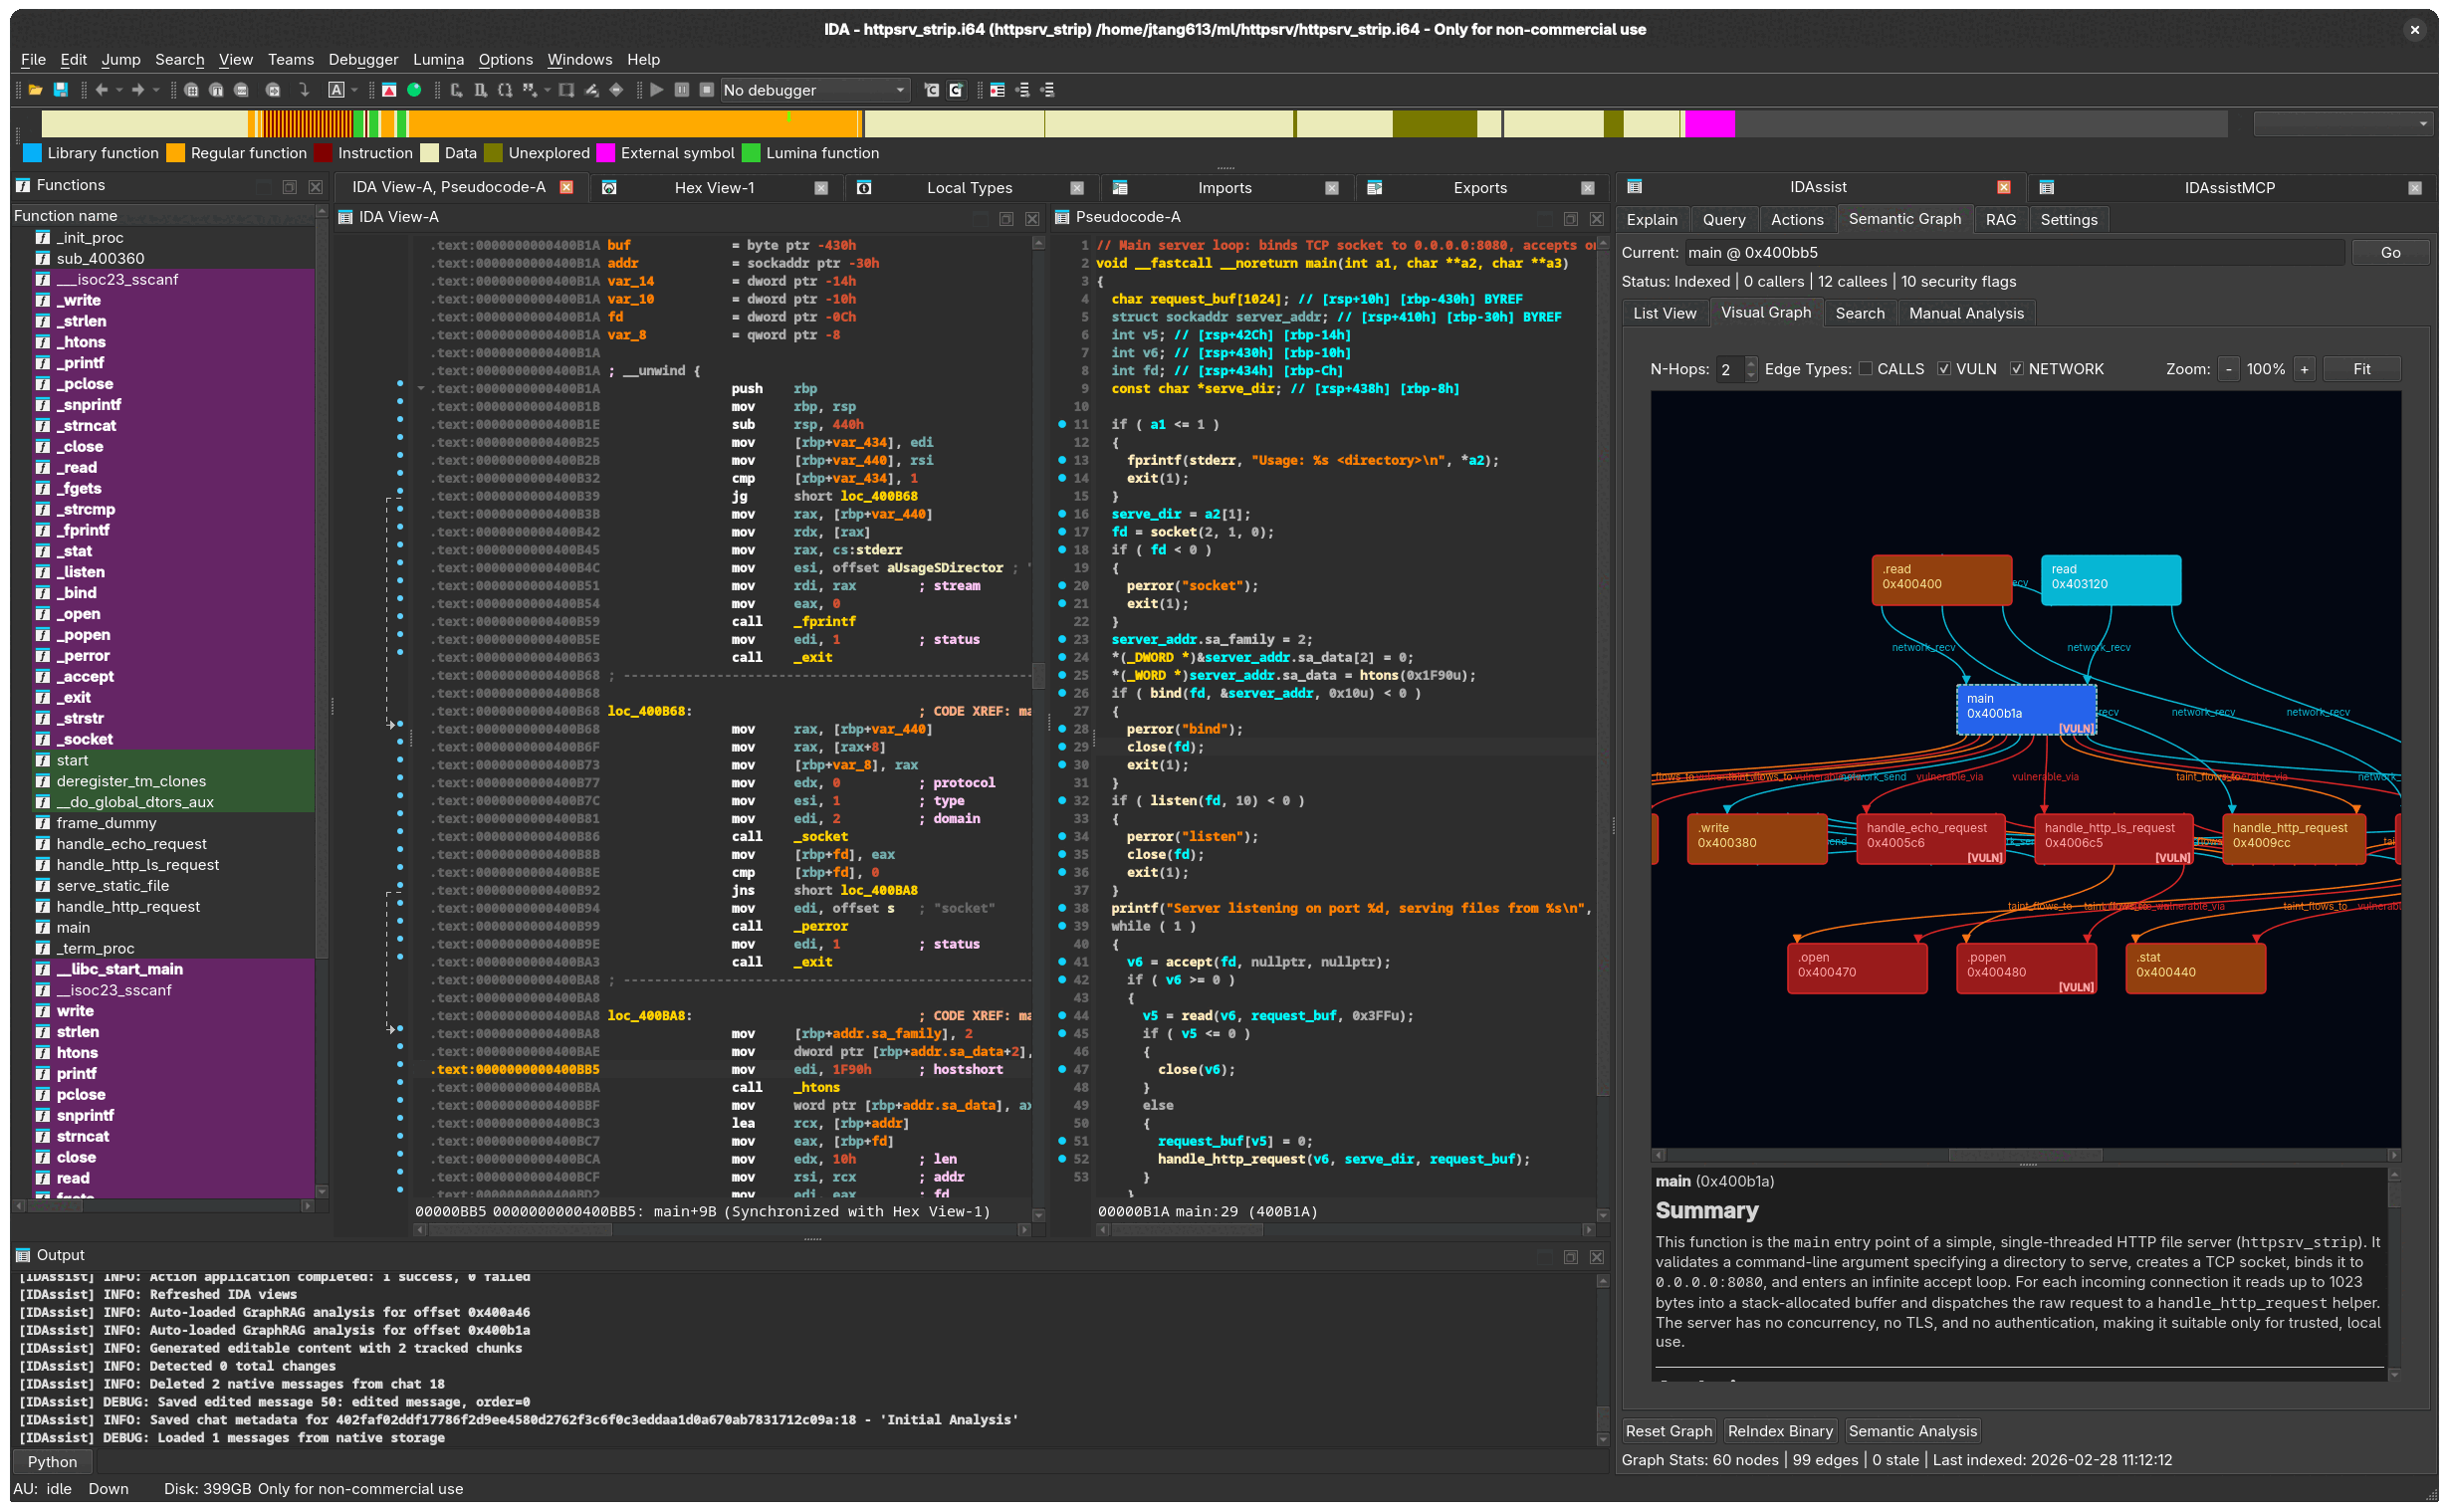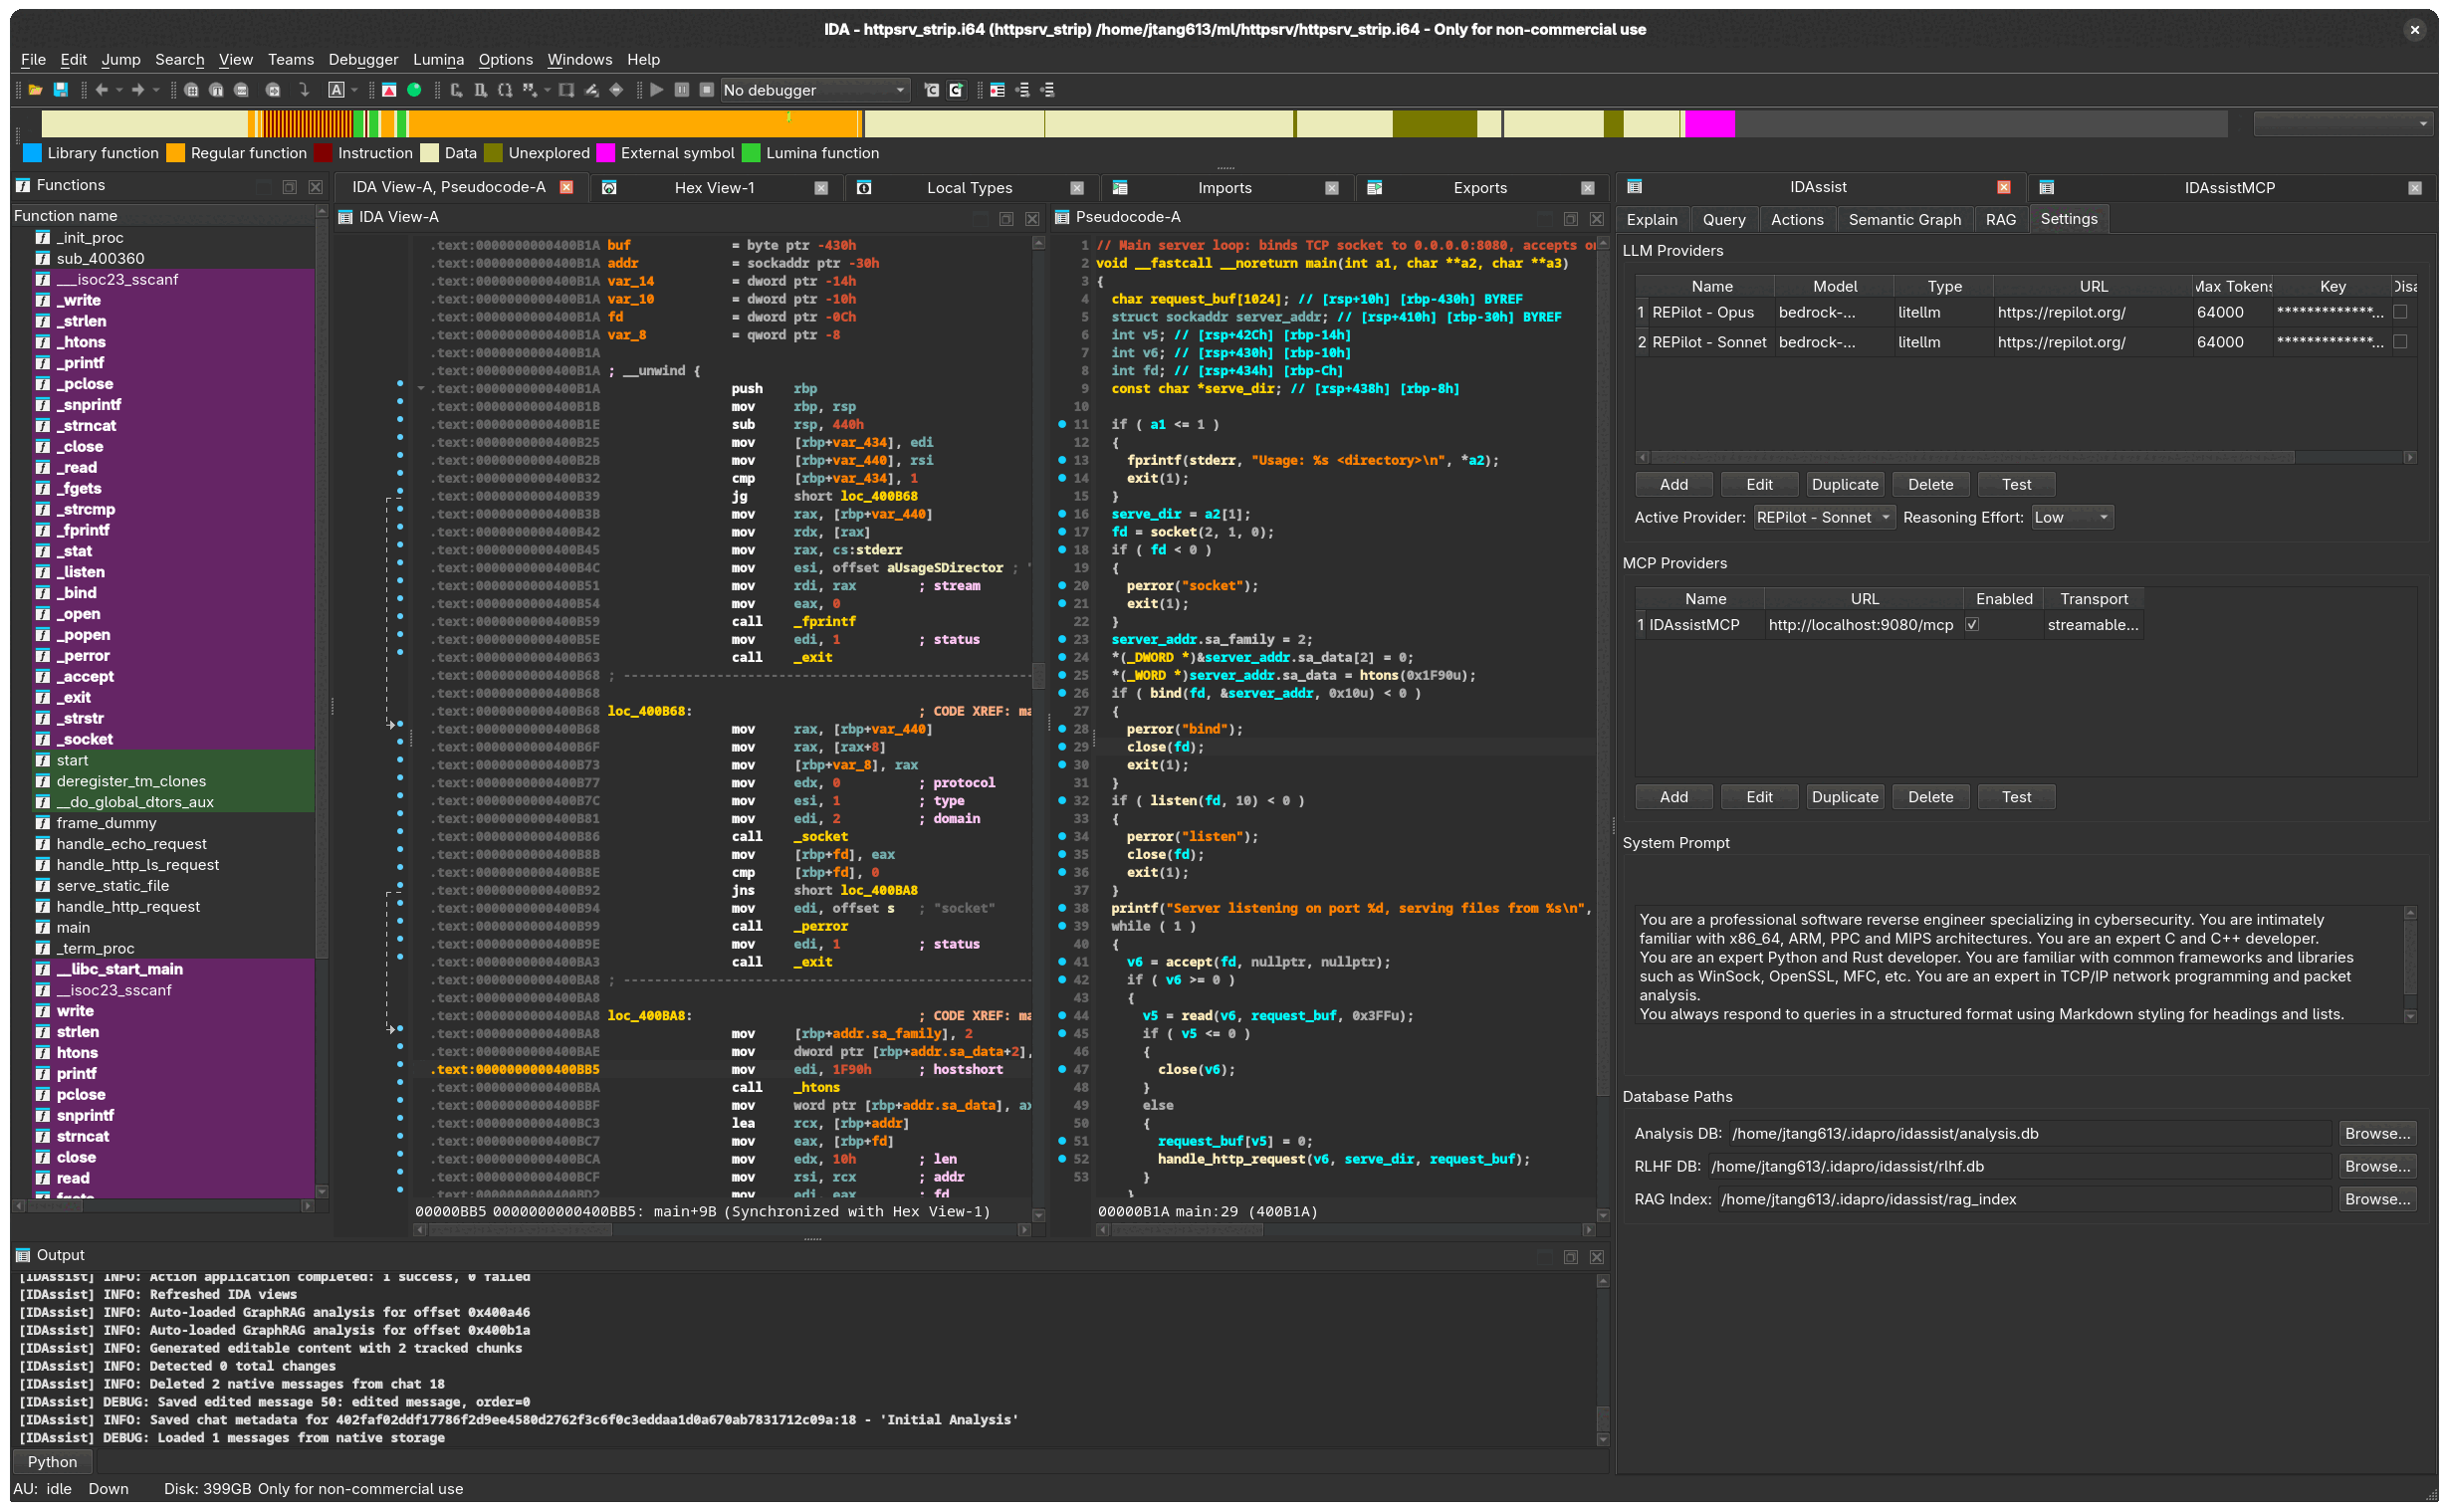 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 zznop/sploit
Go package that aids in binary analysis and exploitation
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 zardus/ctf-tools
Some setup scripts for security research tools.
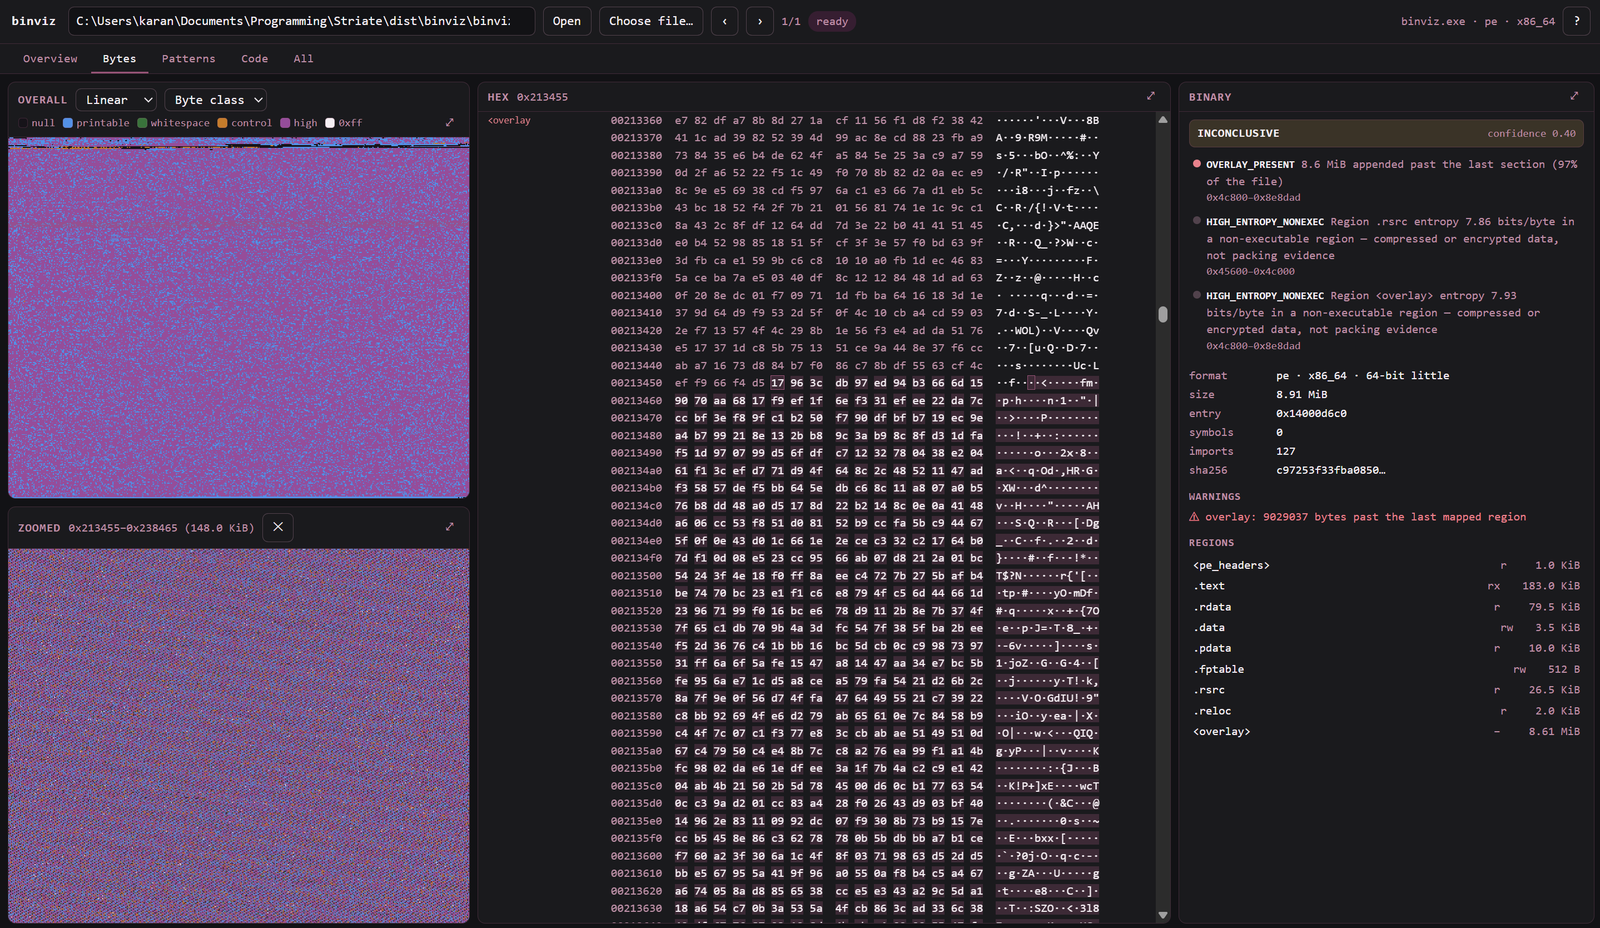 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 trailofbits/fickling
A Python pickling decompiler and static analyzer
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
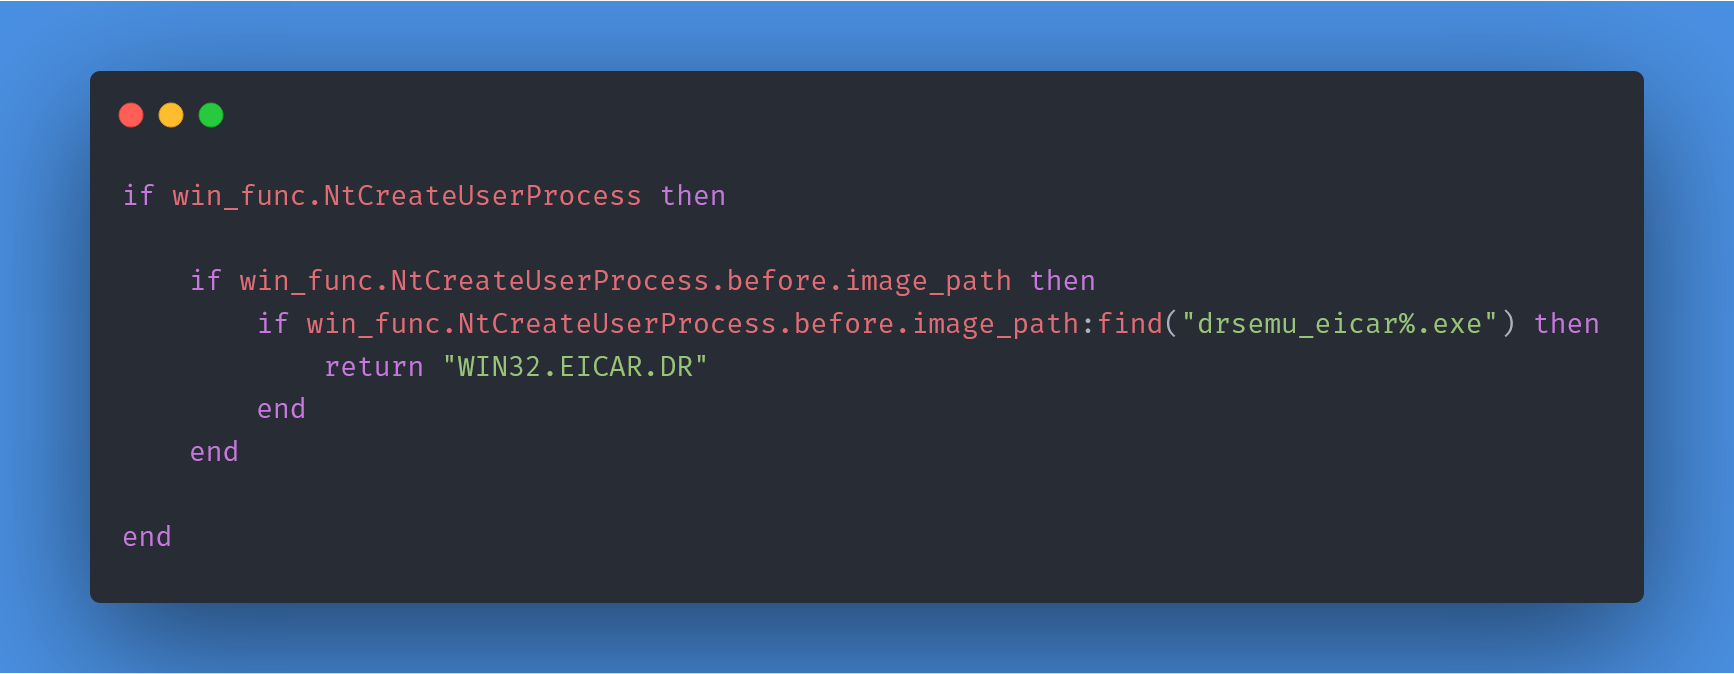 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 frida/frida
Main repo for hosting release binaries
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.