CVE-2025-0316-Exploit

Automated auth bypass exploit for CVE-2025-0316 targeting WordPress WP Directorybox Manager. Features user enumeration, proxy support,…

Automated auth bypass exploit for CVE-2025-0316 targeting WordPress WP Directorybox Manager. Features user enumeration, proxy support,…

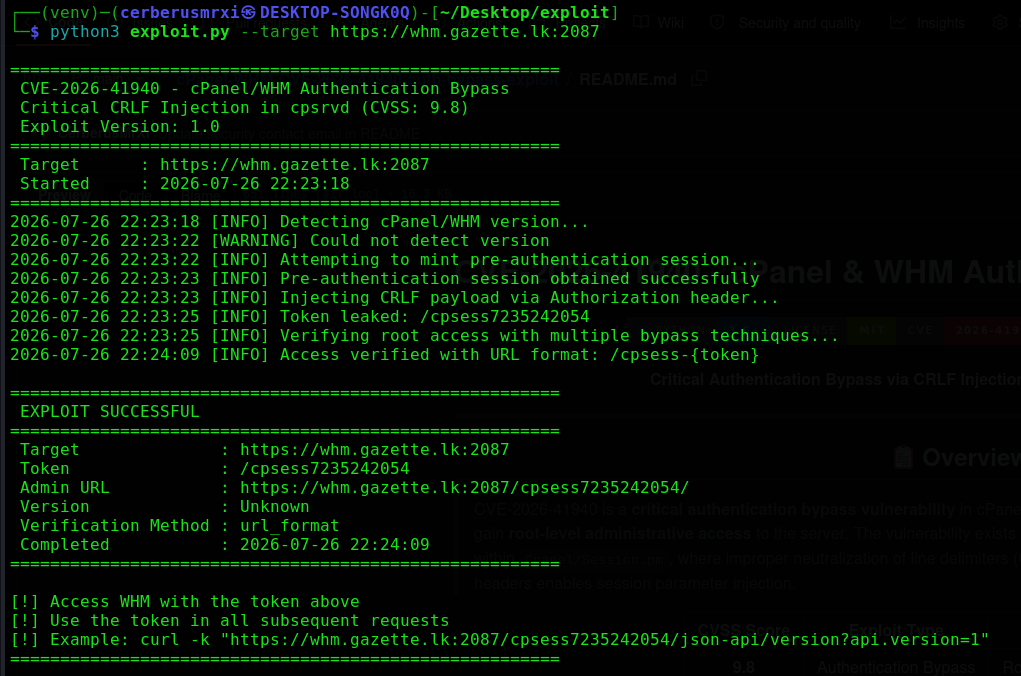
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…

The code for personally reproducing the corresponding vulnerability

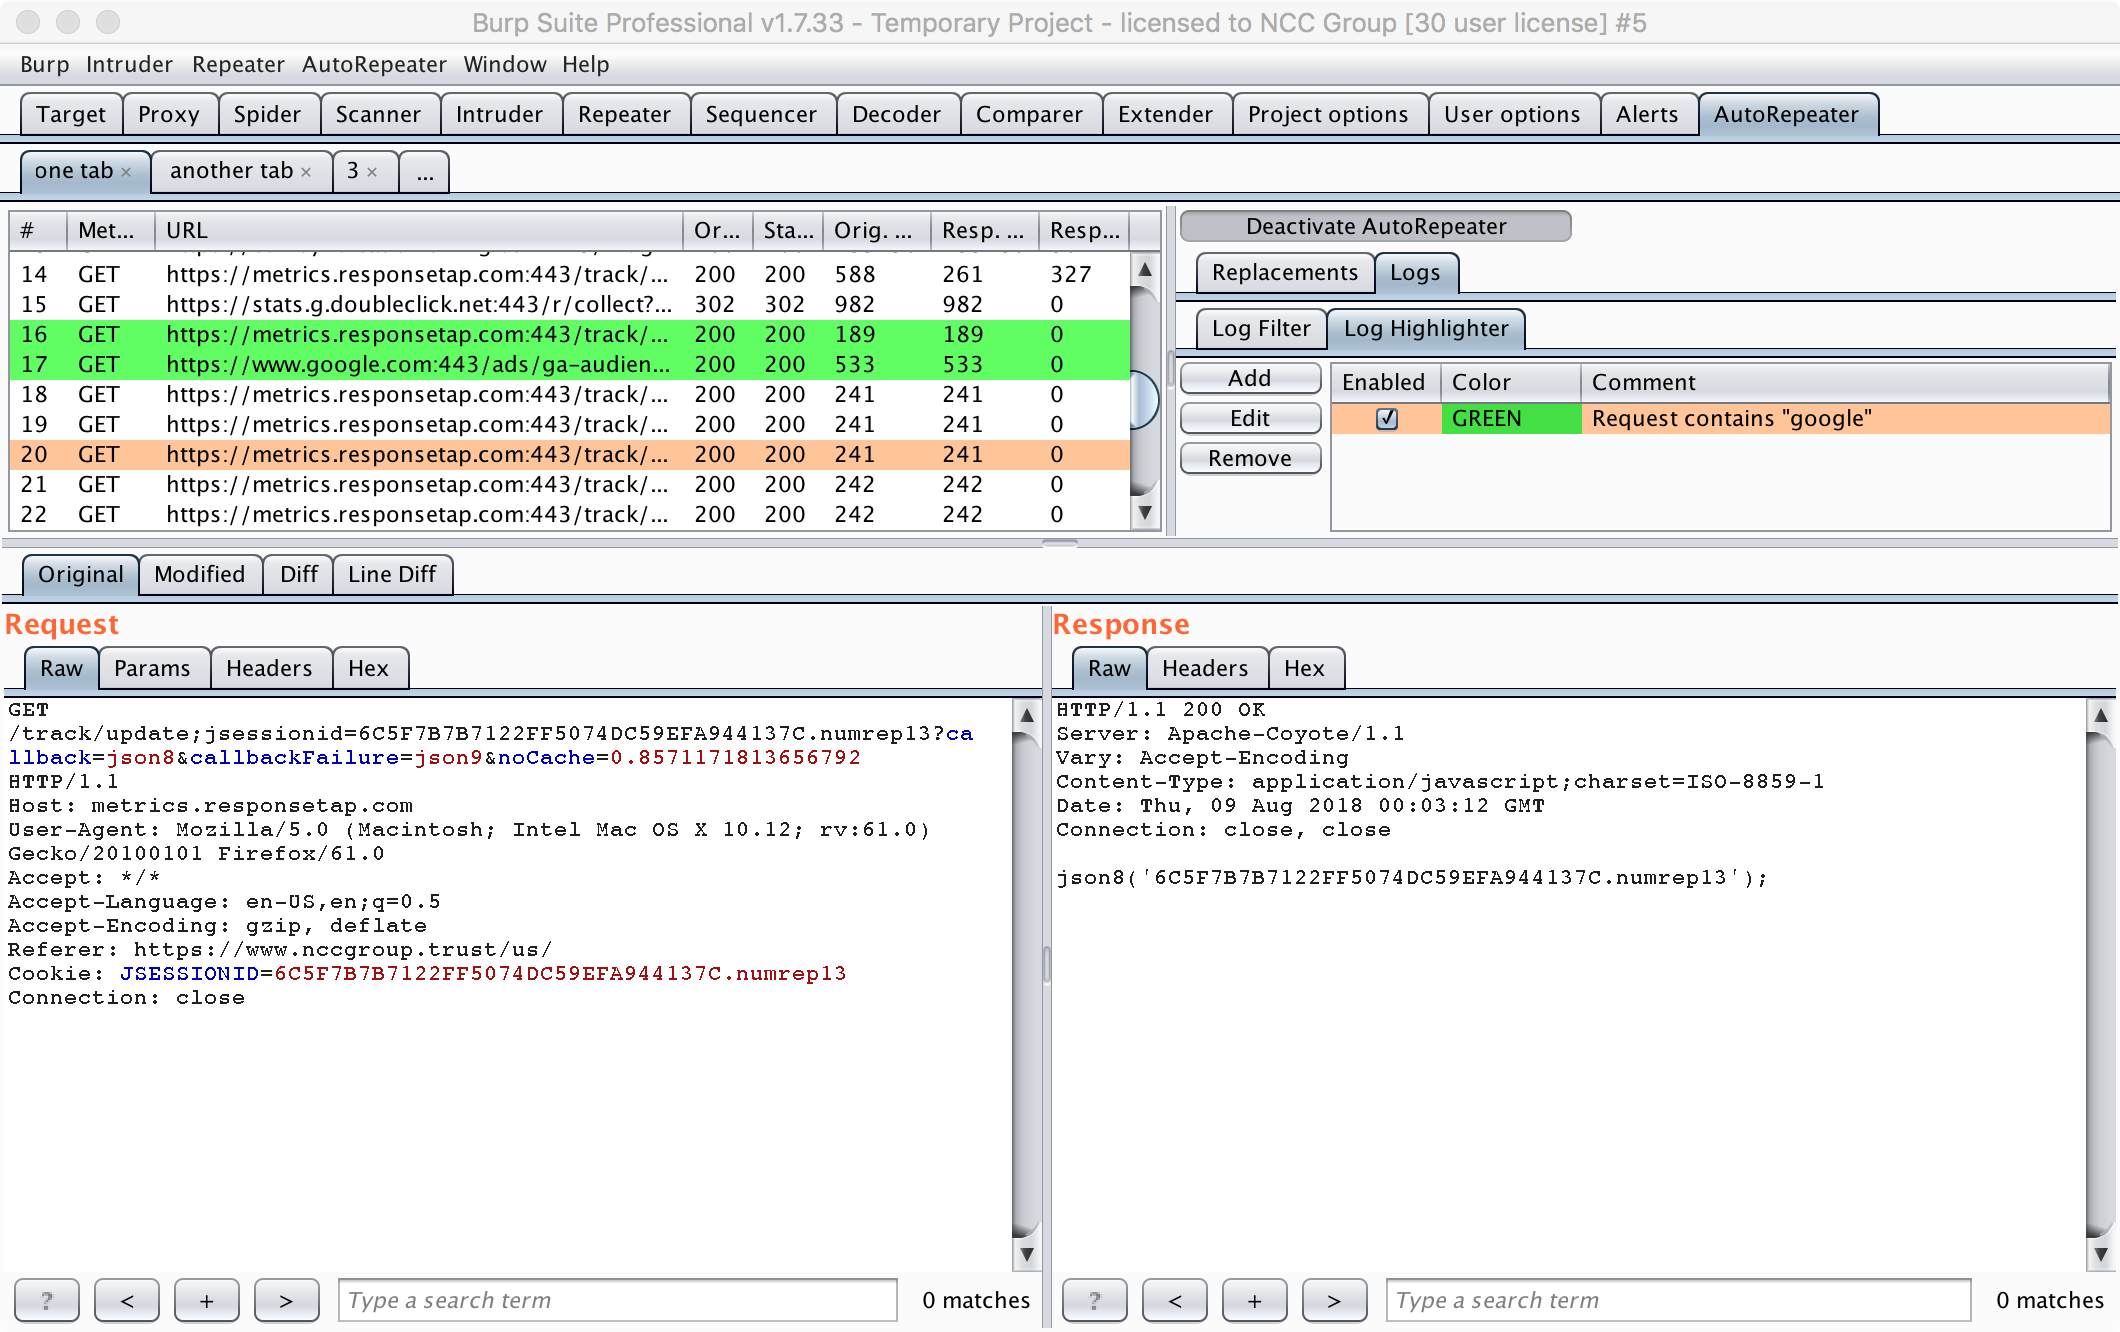
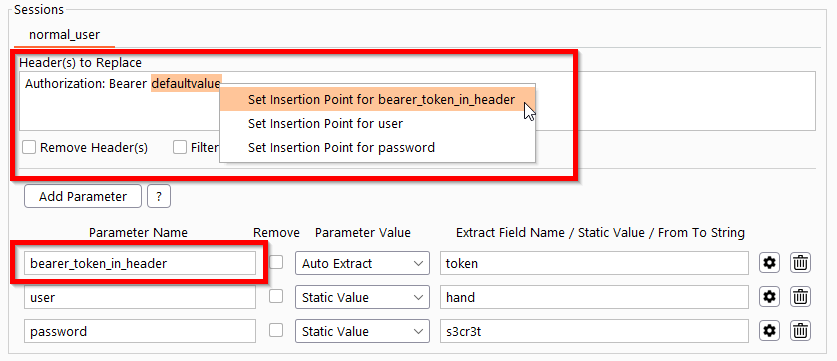
Automated HTTP Request Repeating With Burp Suite

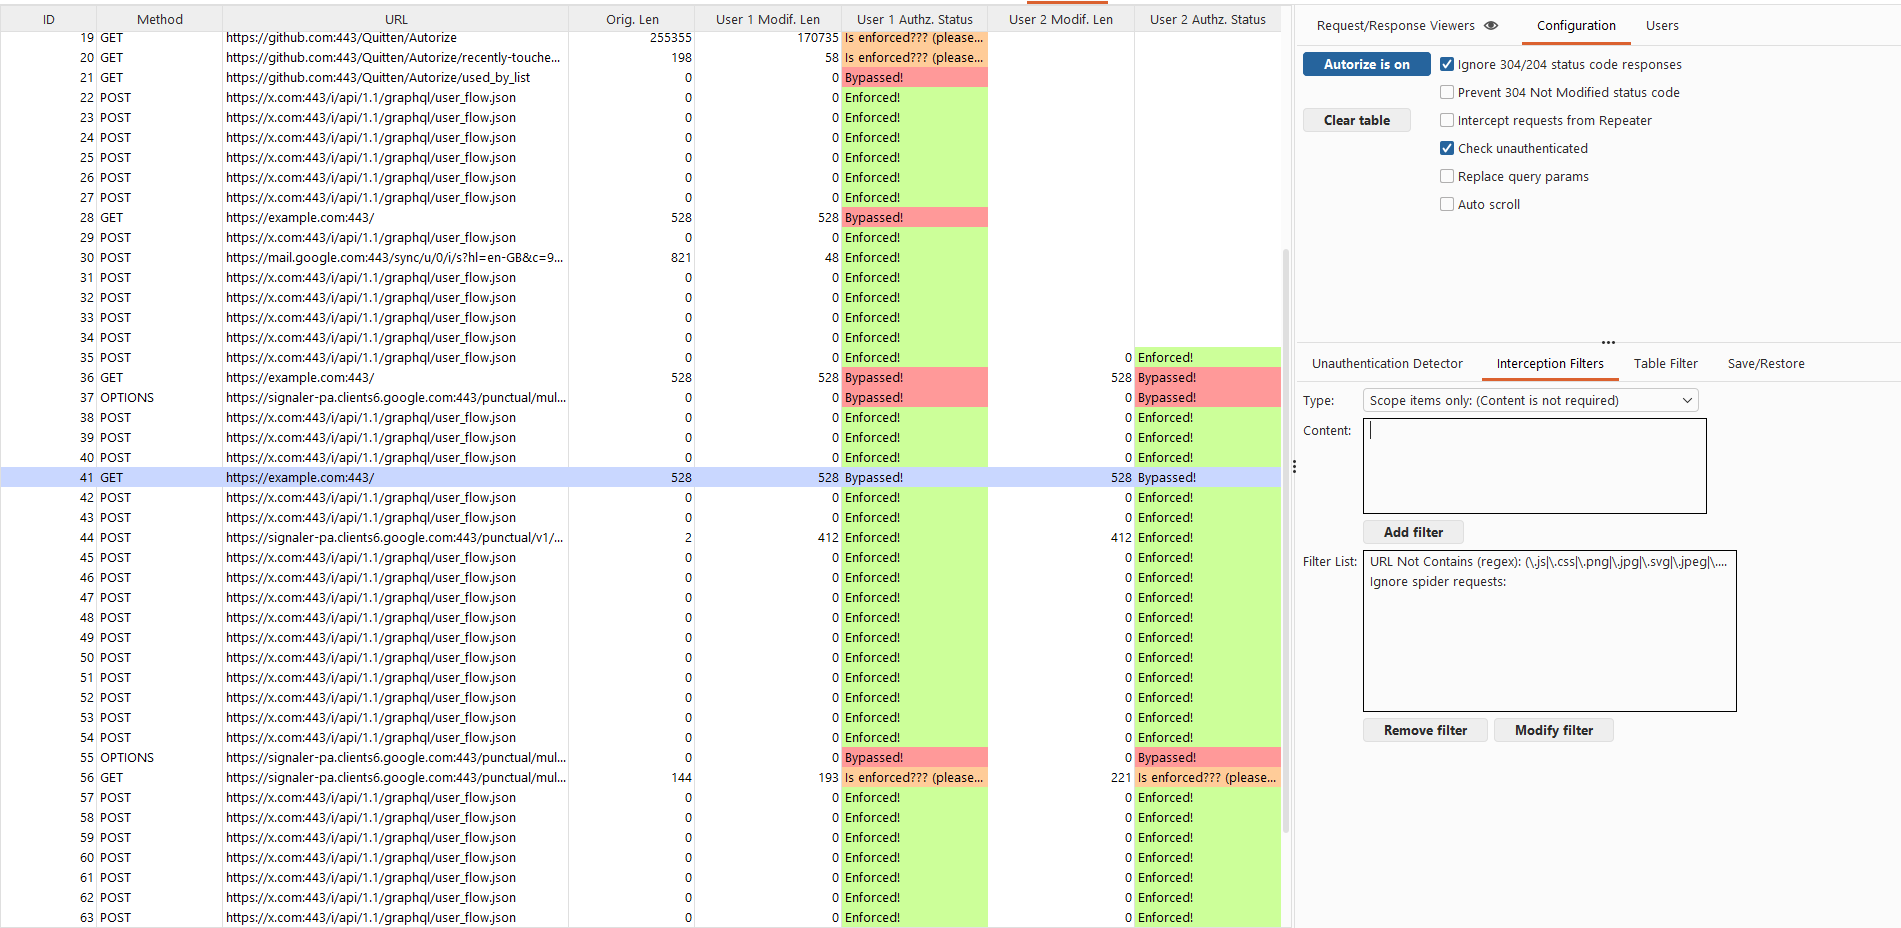
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…

Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.

Burp Suite Extension useful to verify OAUTHv2 and OpenID security

FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

OAuth Request Crafter

GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…

Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…

Ultimate Gift Cards for WooCommerce <= 3.0.6 - Missing Authorization to Infinite Money Glitch

Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.

演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。