
lgosp-poc
 irsl/lgosp-poc
LG On Screen Phone authentication bypass PoC (CVE-2014-8757)
android-securityauthentication-authorizationbluetooth-security+5
1611 years ago
irsl/lgosp-pocLG On Screen Phone authentication bypass PoC (CVE-2014-8757)
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
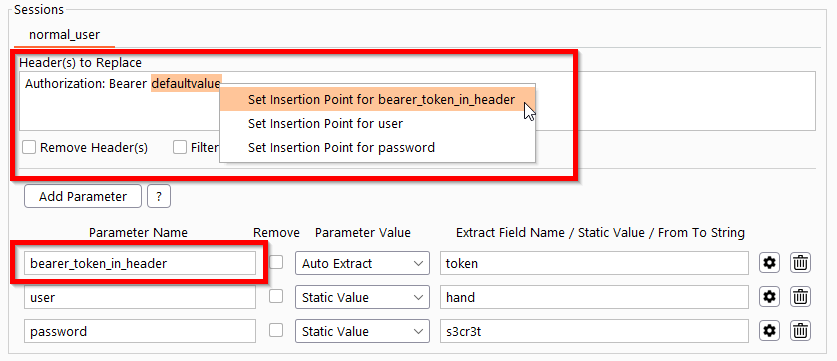 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 dsccommunity/certificatedsc
DSC resources to simplify administration of certificates on a Windows Server.
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
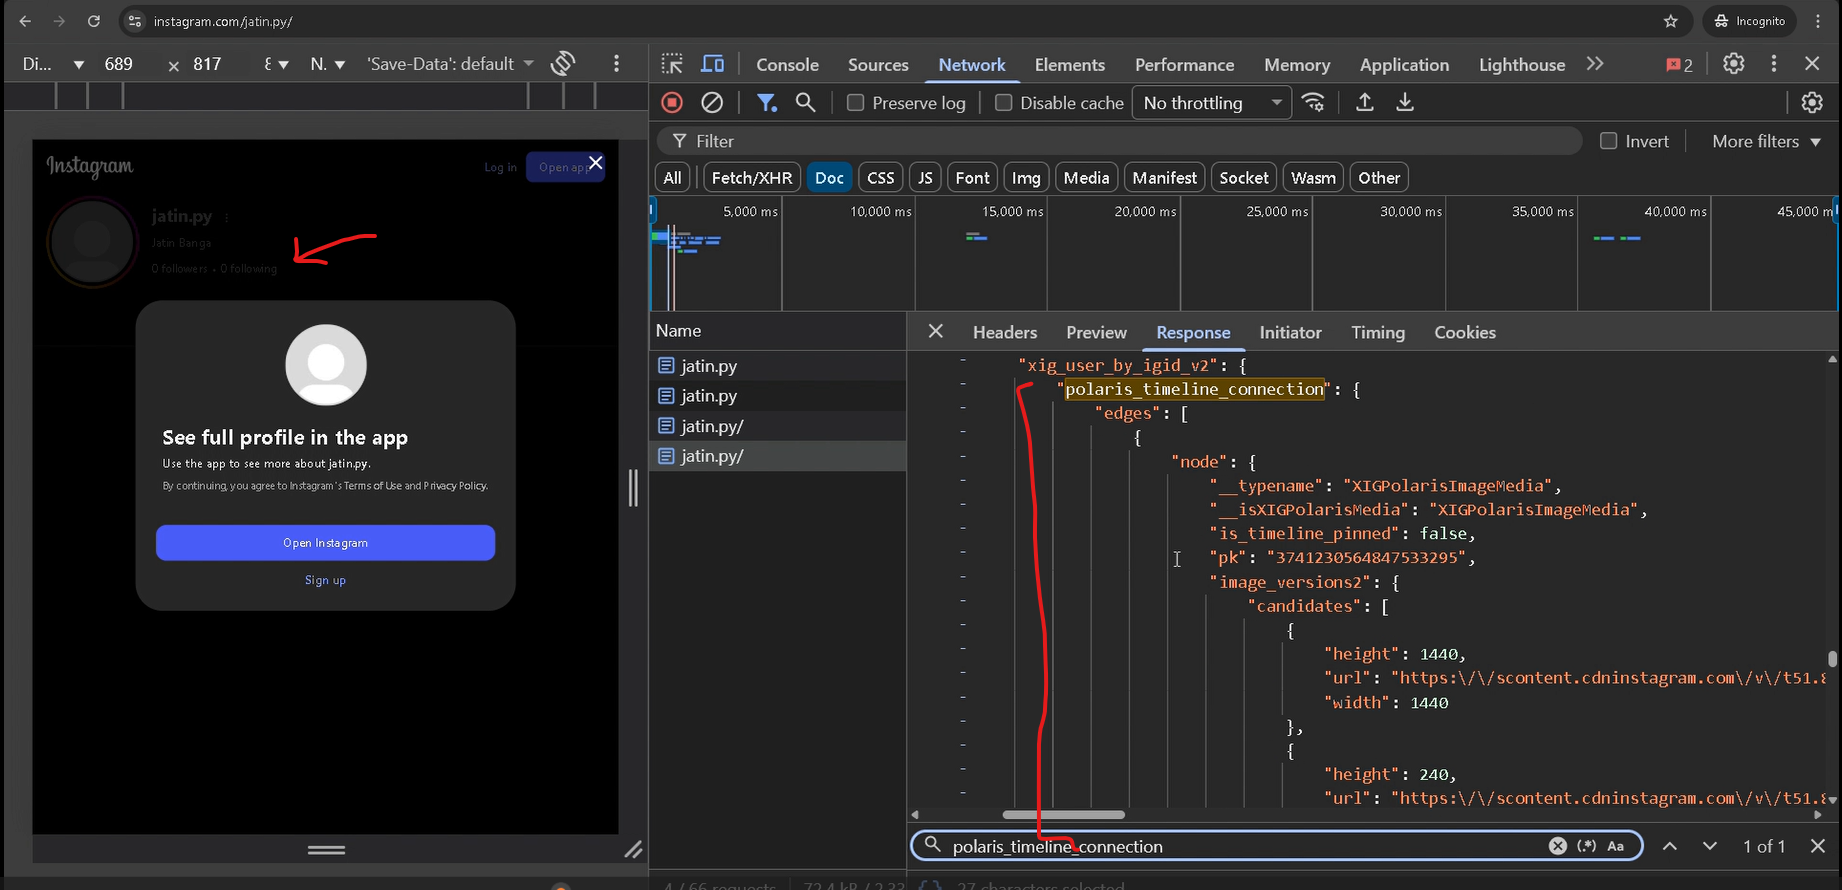 jatin-dot-py/instagram-private-bypass
This repository discloses a server-side authorization bypass in Instagram, which allowed unauthenticated access to private timelines; it seems likely…
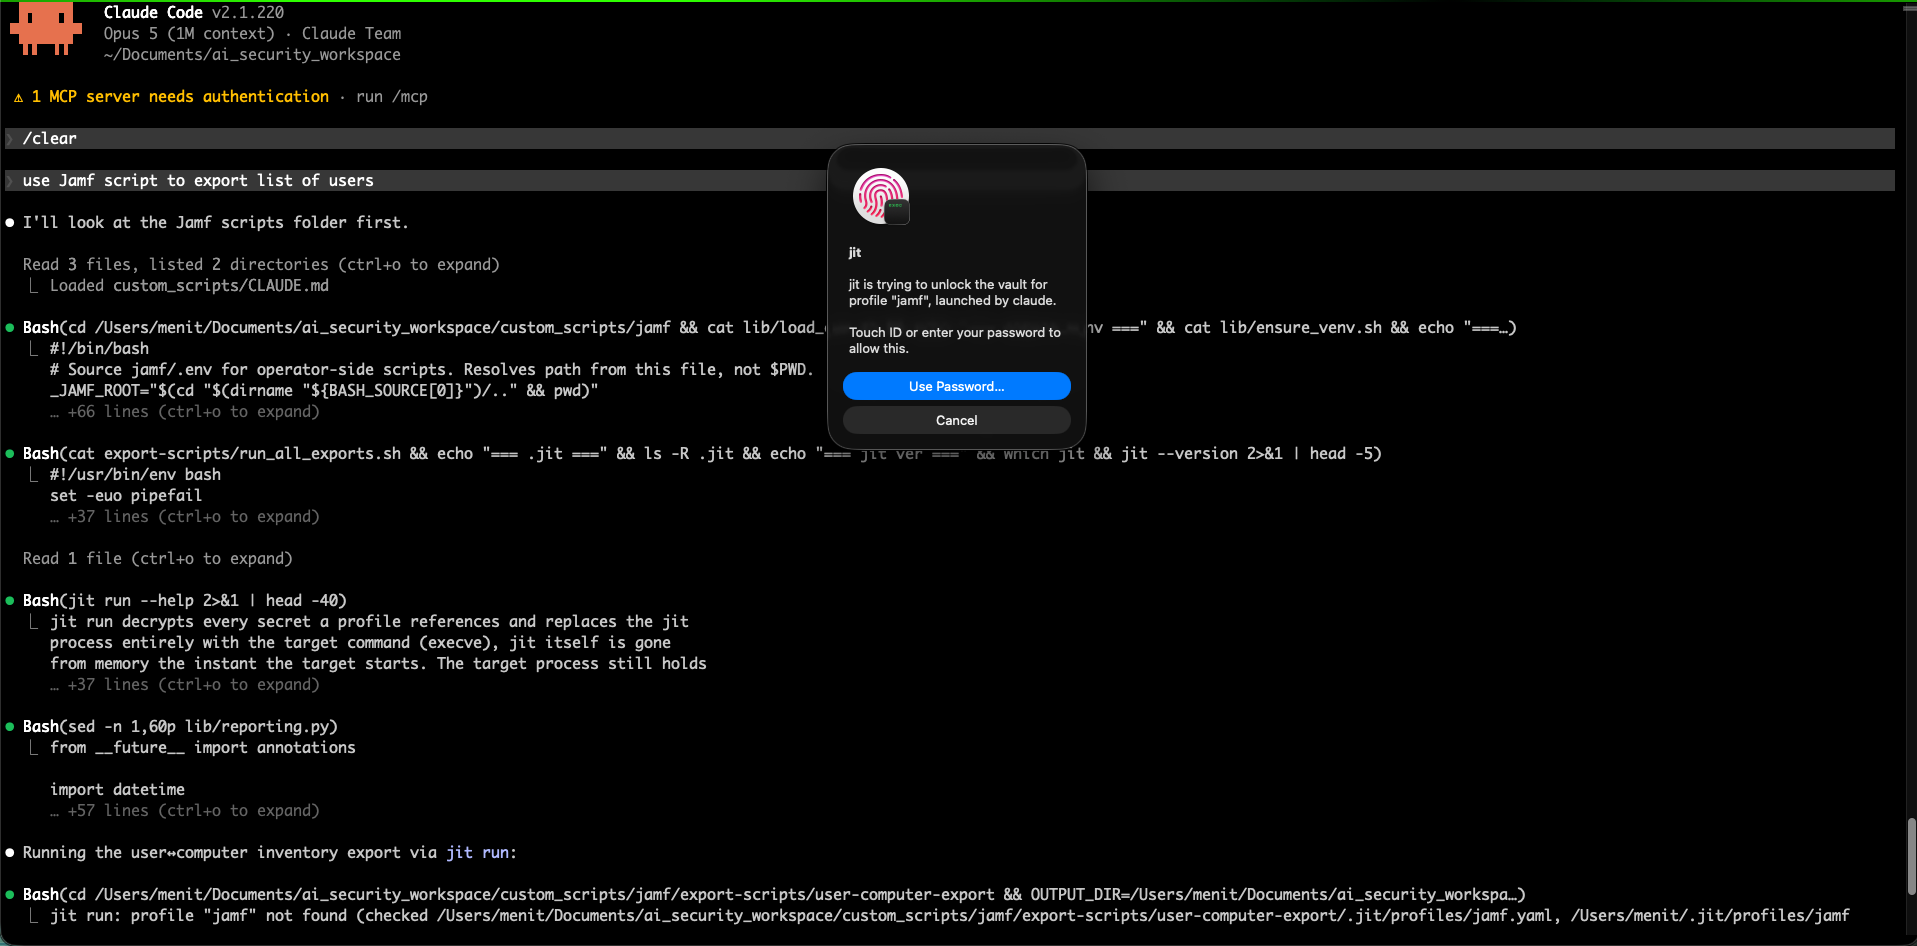 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
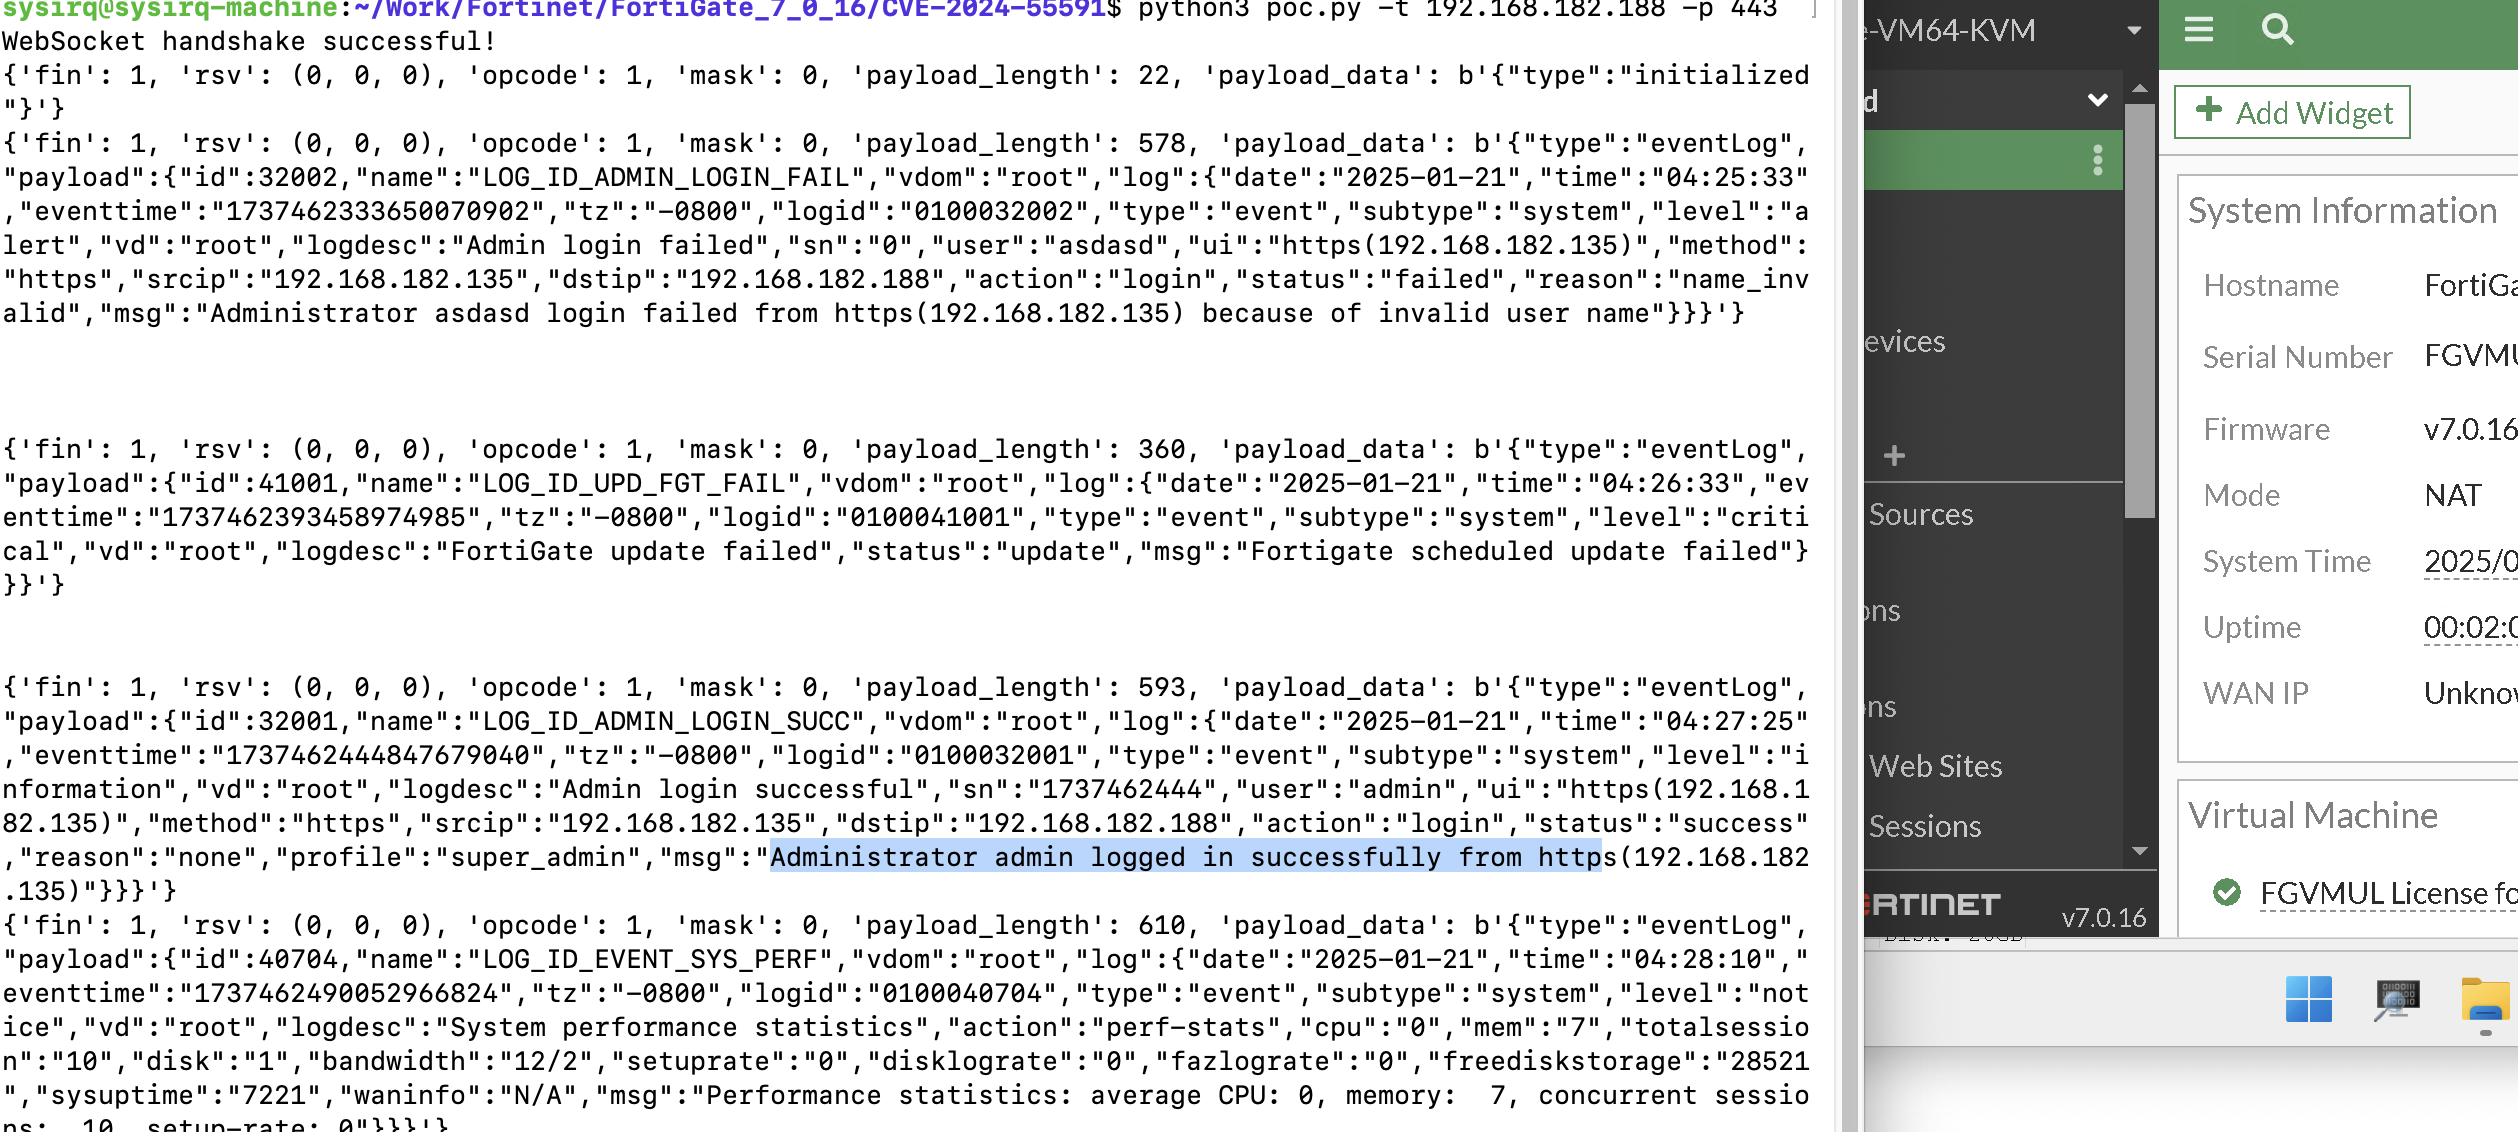 sysirq/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for FortiOS authentication bypass (CVE-2024-55591) that allows unauthenticated access to system logs via WebSocket on…
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
 0xreadingsteiner/silent-call
Silent;Call — Pre-authentication remote root on Cisco CUCM 15.x (CVSS 10.0)
 golioth/signy
Asymmetric cryptography library for generating signed URLs on embedded devices, enabling time-limited resource access using PSA Crypto API with…
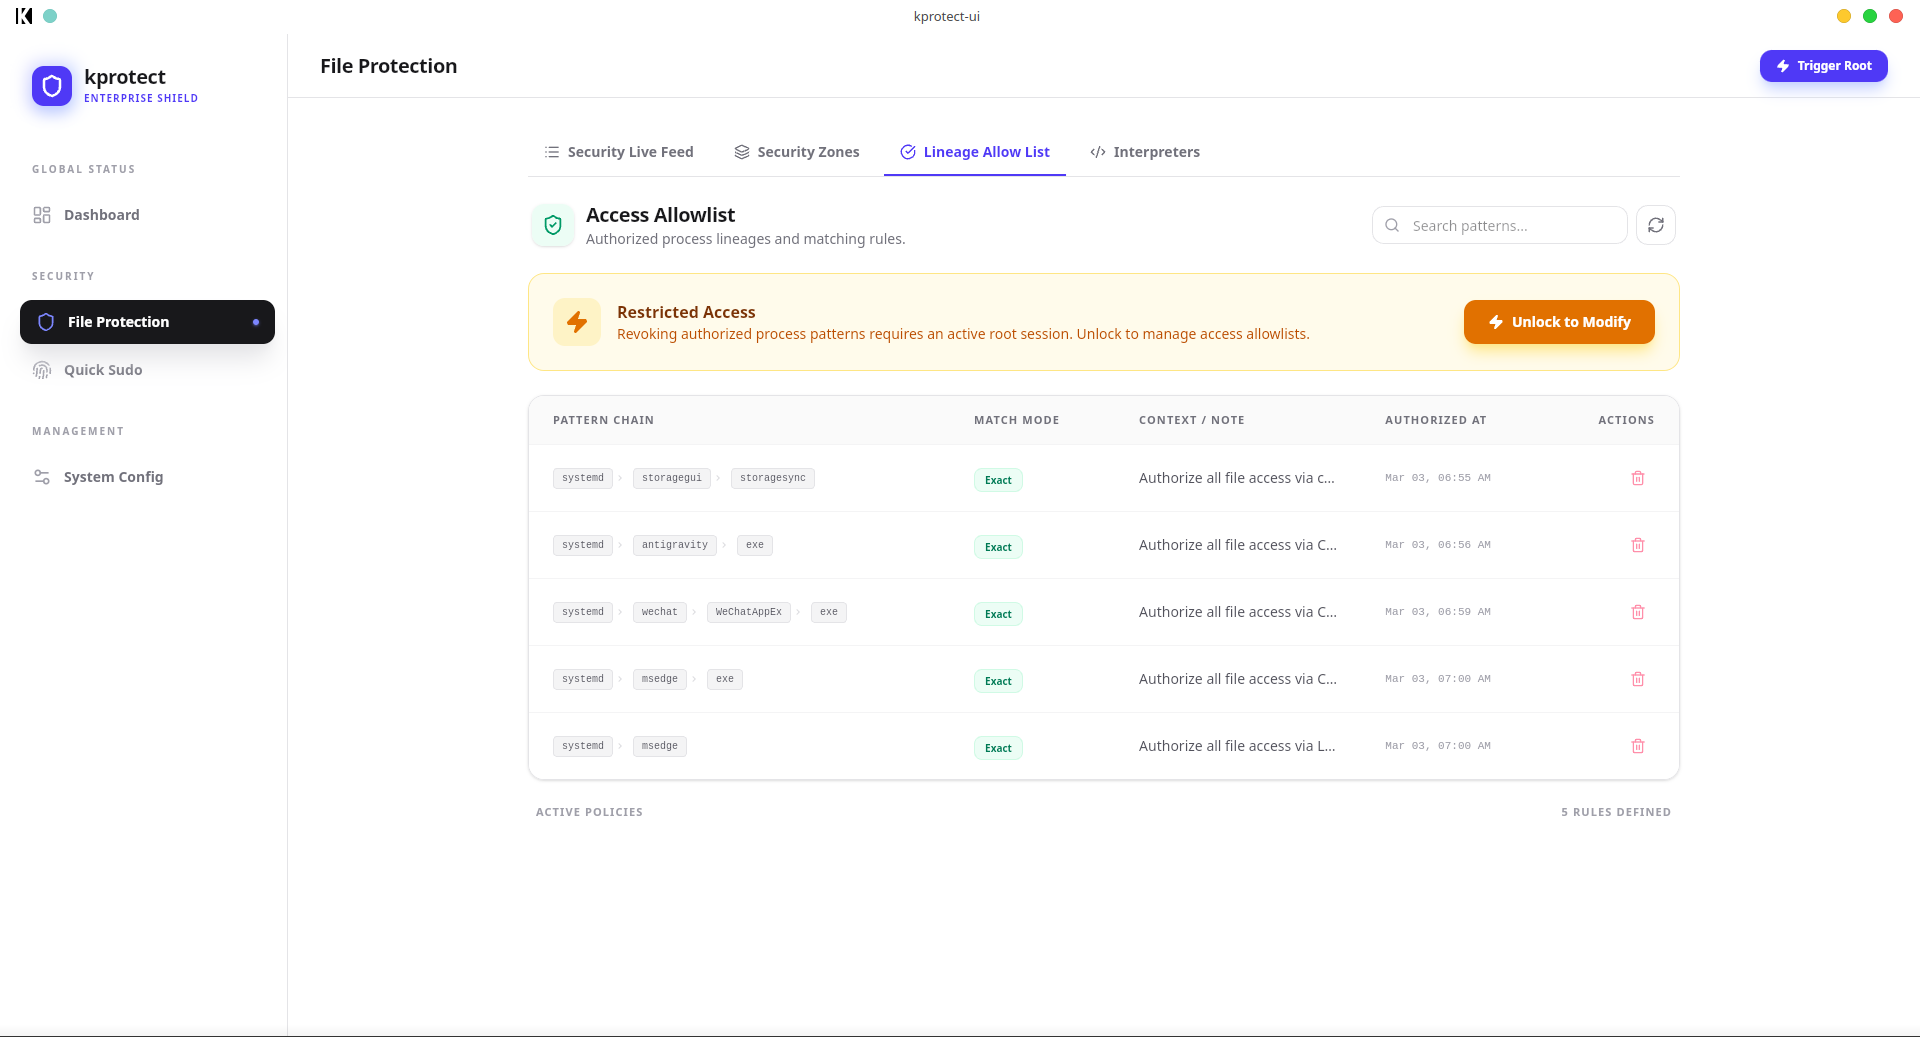 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 fengchenzxc/cve-2020-28148
Wi-Fi portal authentication bypass exploit using MAC address spoofing to gain unauthorized network access, demonstrated on enterprise AC and AP…