
CVE-2025-69985
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
authentication-authorizationexploitationpayload-development+5
kaleth4/cve-2025-69985PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 iteride/cve-2025-2825
Detailed analysis and PoC exploit for CVE-2025-2825, an authentication bypass in CrushFTP. Includes nuclei templates, multi-threaded scanner, and…
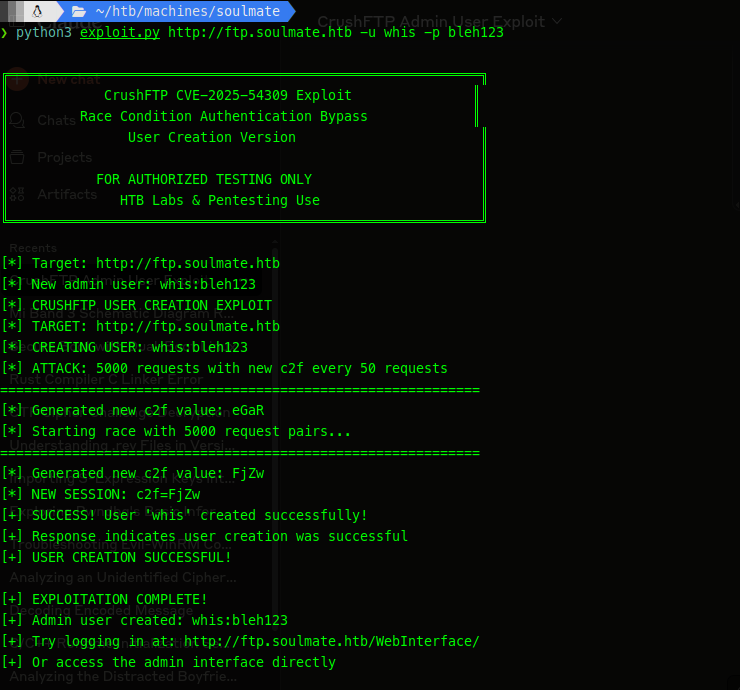 whisperer1290/cve-2025-54309__enhanced_exploit
Multi-threaded exploit for CrushFTP authentication bypass (CVE-2025-54309) with race condition implementation, XML payload generation, and admin user…
 r0otk3r/cve-2025-41646
Python exploit script for CVE-2025-41646, an authentication bypass in RevPi Webstatus <= 2.4.5. Supports single/mass exploitation, proxy, silent…
 shoucheng3/apache__jspwiki_cve-2019-10077_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…
 dezso-dfield/cve-2023-27350
PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 0xyur1/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 kill1234545/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
 horkimhab/cve-2026-0257
CVE-2026-0257 - PAN-OS
 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…