

Kangaroo
 monkeysec-sys/kangaroo
Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
authentication-authorizationeducationexploitation+3
2
monkeysec-sys/kangarooAuthentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
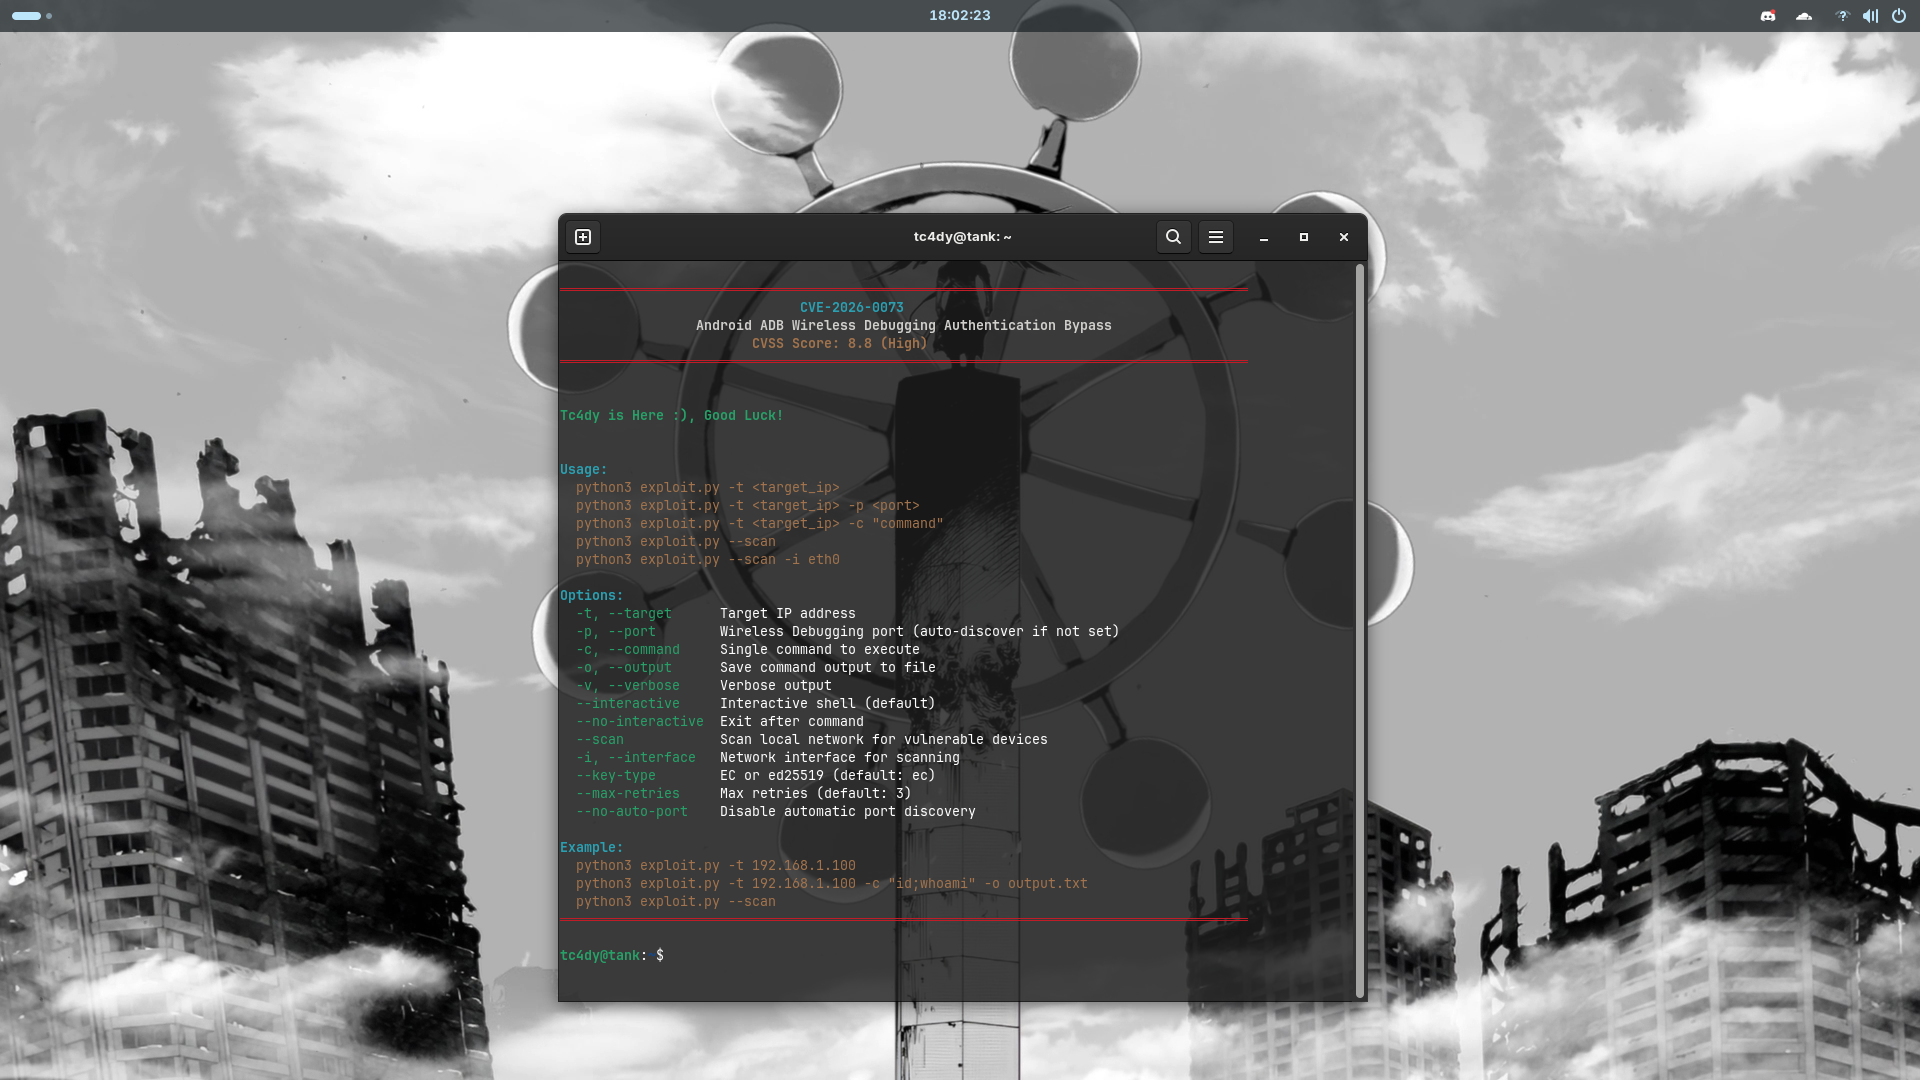 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 immersive-labs-sec/cve-2021-32648
Proof-of-concept exploit for OctoberCMS authentication bypass (CVE-2021-32648), demonstrating unauthorized access and providing a working PoC for…
 hackspeak/cve-2026-16232
CVE-2026-16232 (Check Point SmartConsole authentication bypass) PoC - unauth to admin; for authorized security testing
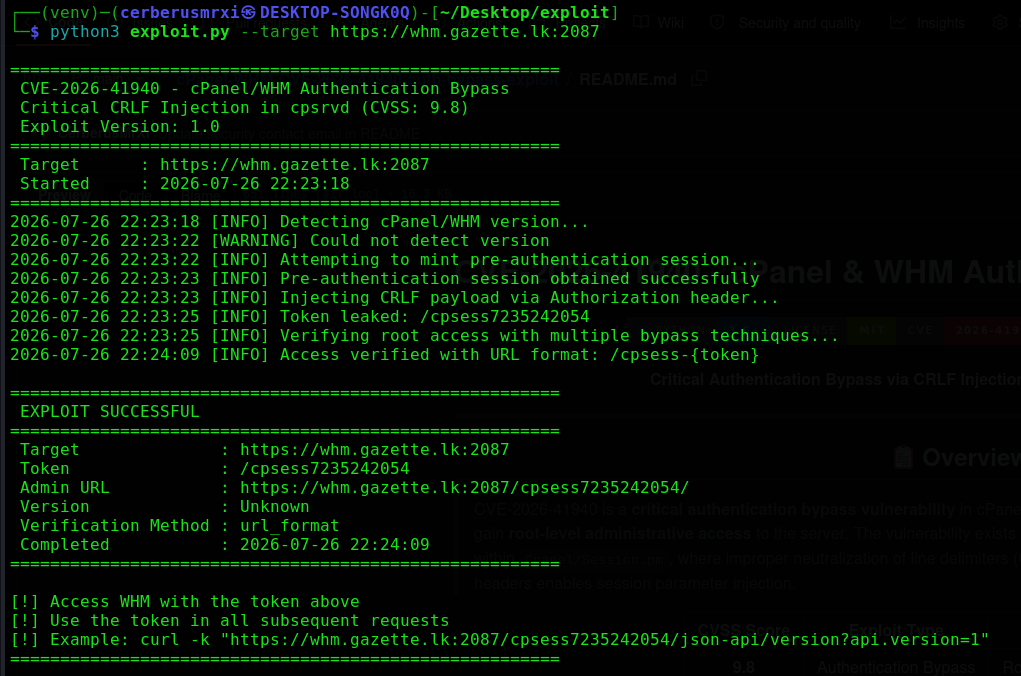 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
 xrzmodz444/cve-2026-41940-poc-linux
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports custom payloads and verbose logging, compatible with…
 ha5ant/silverpeas-authbypass-cve-2024-36042
Python PoC for CVE-2024-36042 authentication bypass in Silverpeas < 6.3.5. Features version detection, multi-threaded user enumeration, message…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
 izxci/cve-2026-8206
Exploit for CVE-2026-8206 targeting unauthenticated account takeover in the Kirki WordPress plugin. Provides a proof-of-concept for security testing…
 eagle-nett/fortiweb_cve-2025-64446-58034
PoC exploit for FortiWeb CVEs: authentication bypass via path traversal and authenticated OS command injection. Includes detailed analysis, payloads,…
 okkotsu1/cve-2024-47533
Exploit for CVE-2024-47533, a critical authentication bypass in Cobbler XML-RPC API, granting unauthenticated admin access for educational security…
 sumaiyafathima-code/cve-2023-27524
Exploit tool for CVE-2023-27524, an authentication bypass vulnerability in Apache Superset. Enables unauthorized access to vulnerable instances for…
 shoucheng3/apache__jspwiki_cve-2019-10089_2-11-0-m4
Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…
 tamatahyt/cve-2026-53576
Kestra Unauthenticated RCE Exploit (CVE-2026-53576)
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
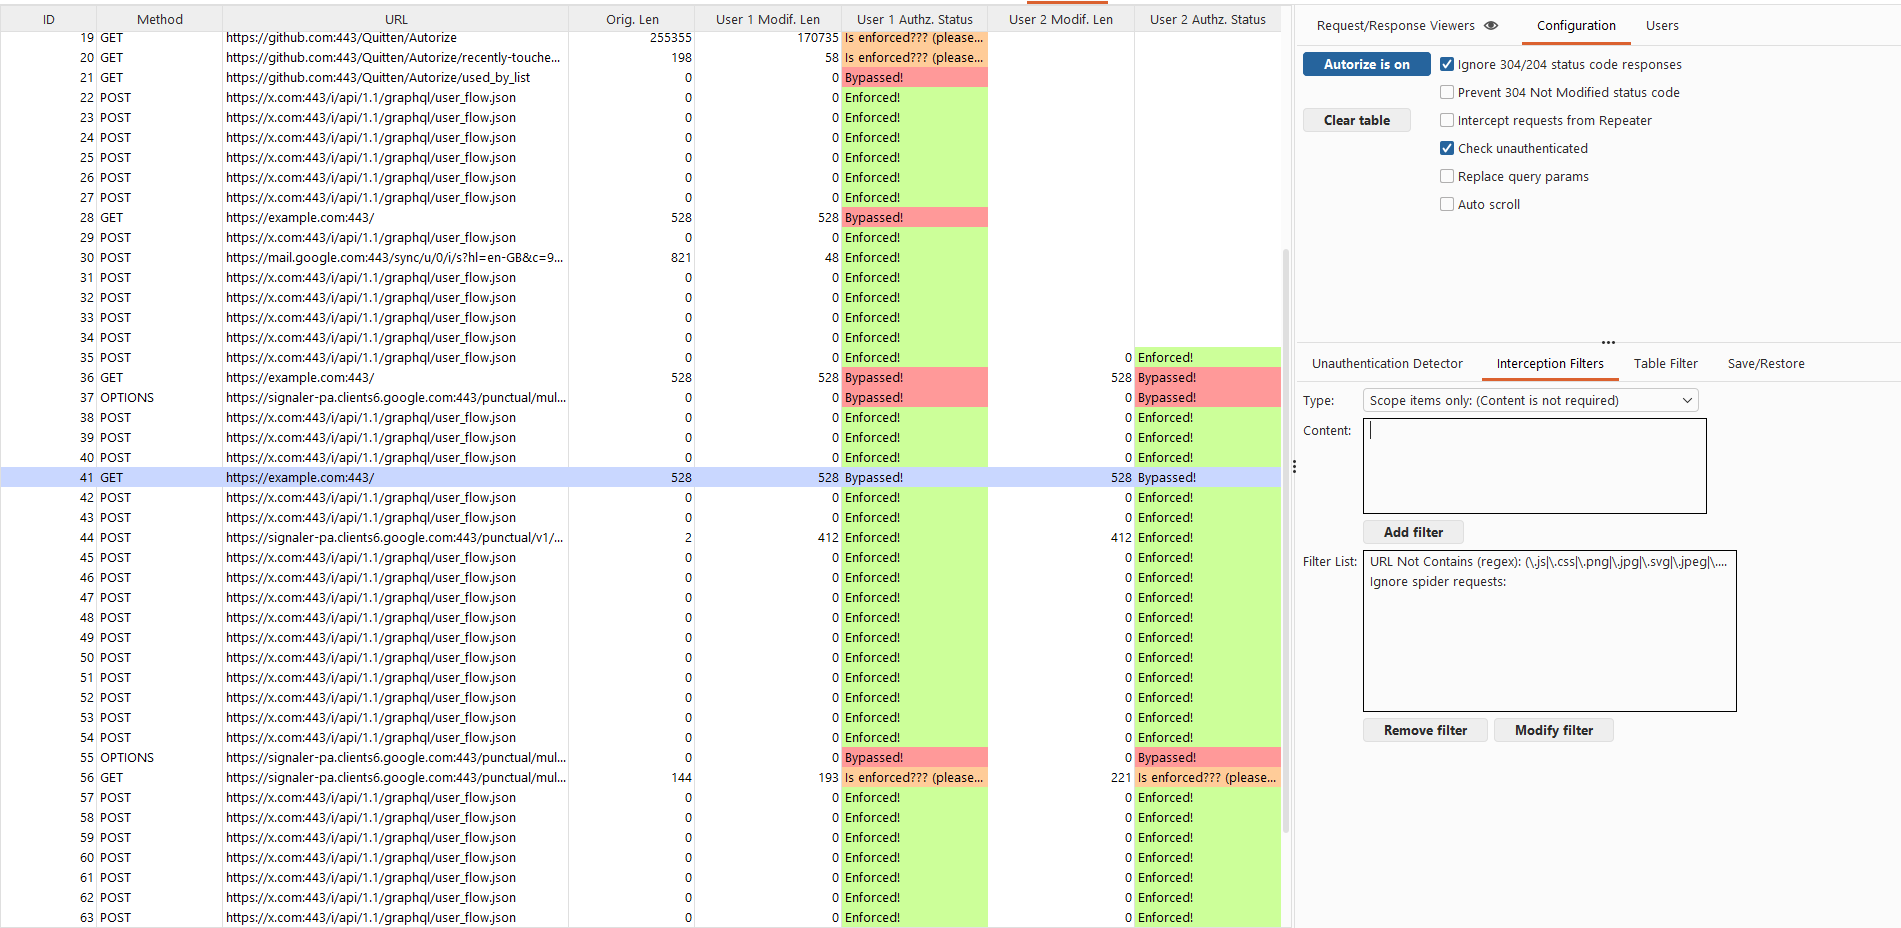 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
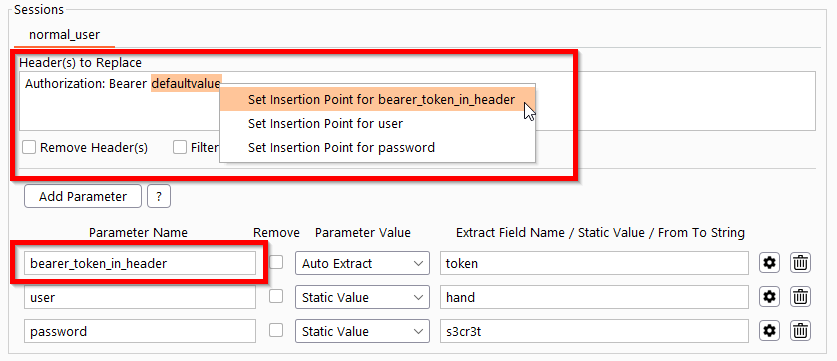 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.