

OAUTHScan
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
api-securityapi-security-testingauthentication-authorization+6
180
akabe1/oauthscanBurp Suite Extension useful to verify OAUTHv2 and OpenID security
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 k3ystr0k3r/cve-2026-31816
CVE-2026-31816 - Budibase Authentication Bypass to RCE
 apache/casbin
Authorization library enforcing ACL, RBAC, ABAC, and custom access-control models with RESTful matching and policy management APIs for applications…
 w01fh4cker/cve-2024-27198-rce
CVE-2024-27198 & CVE-2024-27199 Authentication Bypass --> RCE in JetBrains TeamCity Pre-2023.11.4
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
 synacktiv/cve-2024-45409
Ruby-SAML / GitLab Authentication Bypass (CVE-2024-45409) exploit
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 thatonesecguy/zerologon-cve-2020-1472
PoC for Zerologon (CVE-2020-1472) - Exploit
 projectdiscovery/ldapserver
Package ldapserver implements LDAP Server
 artemy-ccrsky/cve-2024-41276
PIN-based Authentication Bypass vulnerability in Kaiten
 george0papasotiriou/cve-2026-22005-oauth-2.0-device-code-phishing-short-interval-
Proof-of-concept for CVE-2026-22005 showing OAuth 2.0 device code phishing via too-short polling interval, with vulnerable Flask server and exploit…
 george0papasotiriou/cve-2026-4444-jwt-algorithm-confusion-via-kid-injection
POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…
 0xn7y/cve-2022-46169
Exploit for CVE-2022-46169
 tanarchytan/cve-2021-1675
Fix without disabling Print Spooler
 s1lkys/cve-2020-29669
Macally WIFISD2
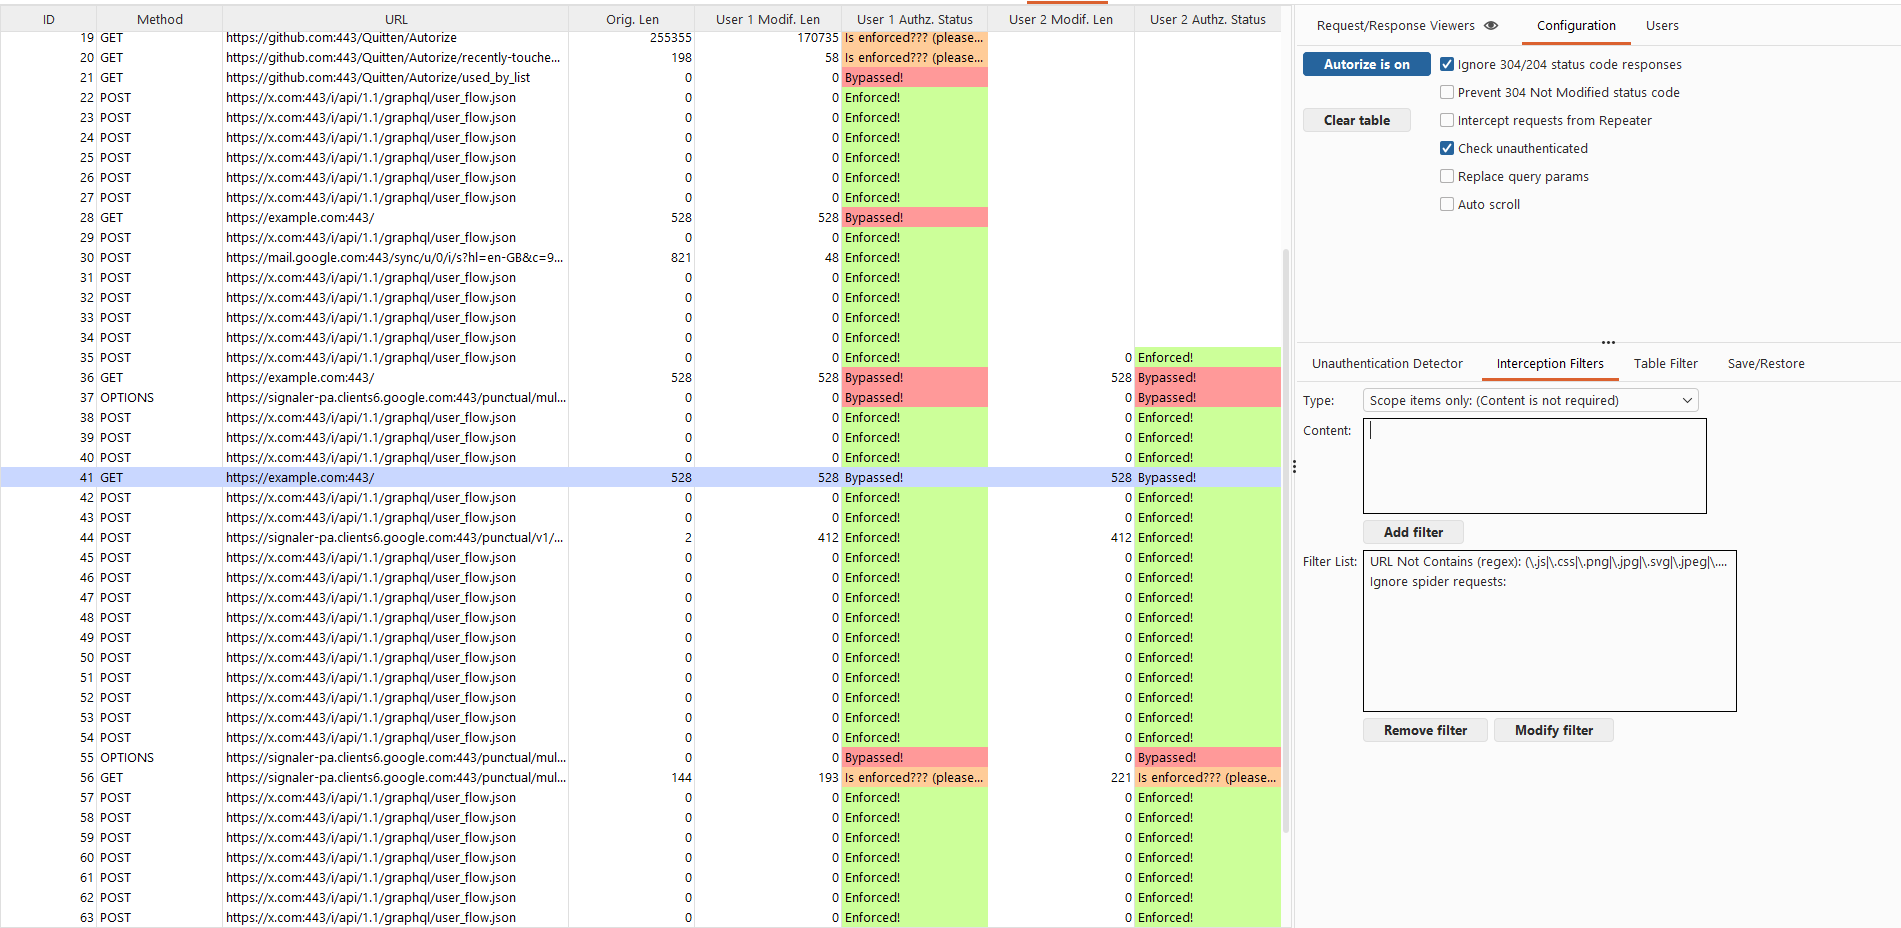 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
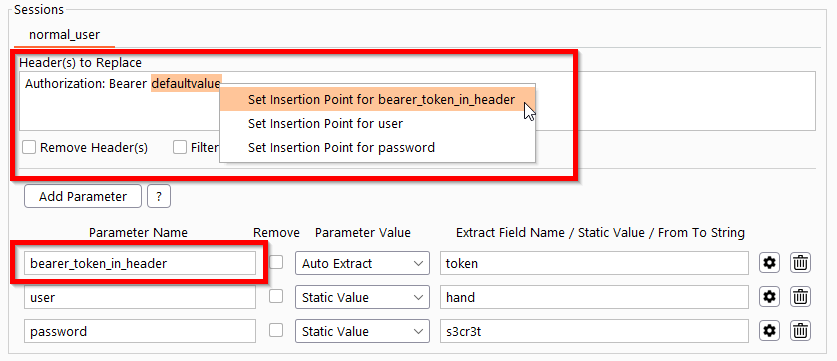 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.