
oauth-scan
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
authentication-authorizationconfiguration-auditinginformation-gathering+3
192
portswigger/oauth-scanBurp Suite Extension useful to verify OAUTHv2 and OpenID security
 zakipedio/bridgehead
Native C++ access to Active Directory over ADWS, no .NET, no WCF, no HTTP stack.
 h4x0r-dz/cve-2024-3656
Keycloak admin API allows low privilege users to use administrative functions
 h454nsec/cve-2023-42793
JetBrains TeamCity Authentication Bypass CVE-2023-42793 Exploit
 malwareman007/cve-2022-36537
POC of CVE-2022-36537
 qarait/ephemera
Zero-Trust SSH CA
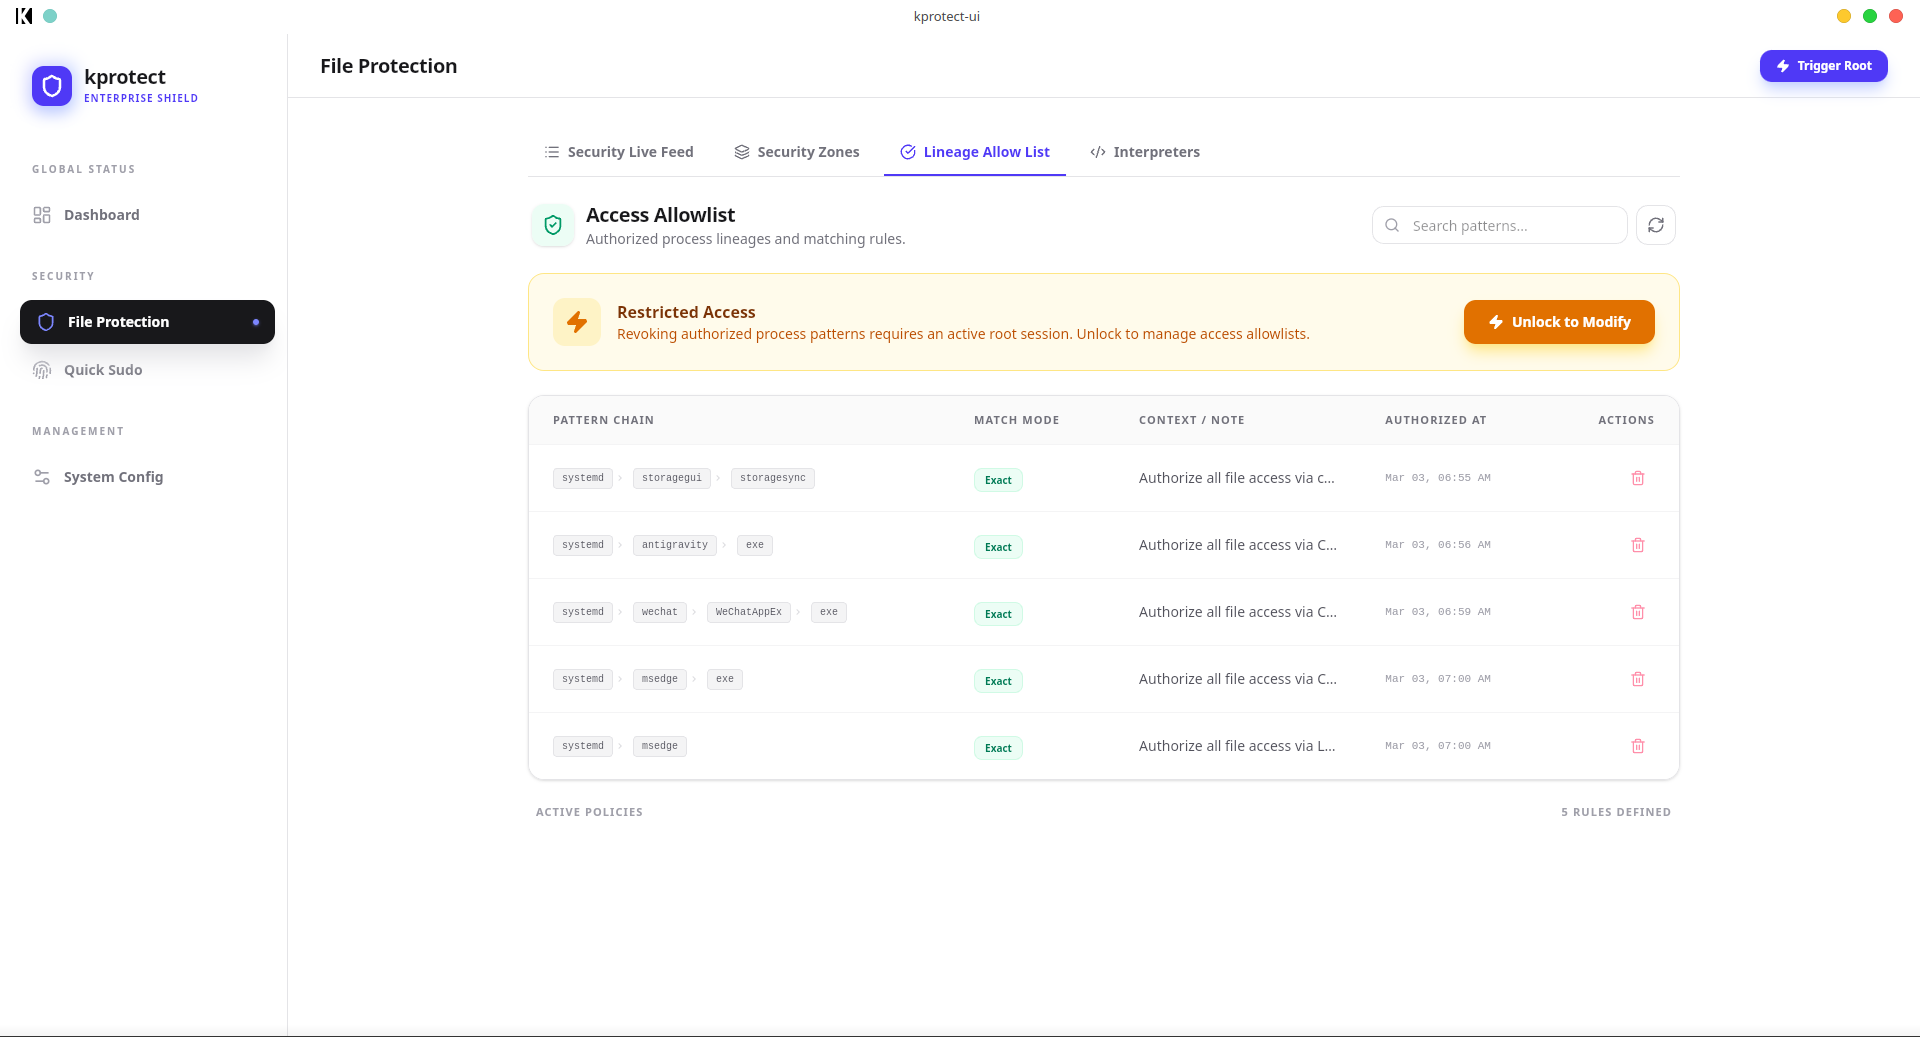 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 portbuster1337/cve-2026-27771
CVE-2026-27771 - Gitea/Forgejo Container Registry Auth Bypass Exploit PoC - Pull private container images without authentication
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
 okaytc/superset_auth_bypass_check
Apahce-Superset身份认证绕过漏洞(CVE-2023-27524)检测工具
 agnihackers/cve-2022-36537-exploit
CVE-2022-36537
 trya9ain/nopac
CVE-2021-42287/CVE-2021-42278 Exploiter
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 spy0x7/cve-2021-33044
Dahua IPC/VTH/VTO devices auth bypass exploit
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.