

CVE-2026-130347
 googlesky/cve-2026-130347
PoC and differential lab for CVE-2026-130347: phpMyFAQ password-reset flow issues tokens for OIDC/LDAP accounts, enabling local password set and…
authenticationexploitationlabs-practice+5
googlesky/cve-2026-130347PoC and differential lab for CVE-2026-130347: phpMyFAQ password-reset flow issues tokens for OIDC/LDAP accounts, enabling local password set and…
 aduli198/cve-2026-21589
Proof-of-concept for CVE-2026-21589: unauthenticated path traversal file read in Atlassian Data Center products, chained via Crowd credentials into…
 lheiakim/cve-2026-75045-poc
CVE-2026-75045 - JetBrains YouTrack unauthenticated database backup download via shared draft signature (CVSS 9.1)
 murrez/cve-2026-85984
Python PoC for CVE-2026-85984: checks and exploits the miniOrange OTP plugin (≤5.5.5) unauthenticated WordPress admin auth bypass, with version scan…
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 abraxas/pfsense-api-unix-sock-noauth
pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 affolter-engineering/ldapin
CLI tool to perform basic LDAP task for security assessments
 abraxas/nextcloud-federated-ocm-token
Nextcloud 35.0.0 — federated share secret is an unscoped app password for the sharer's whole Files tree
 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 muhammedhussein17/keycloak
Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
 alt3kx/cve-2026-18963
Detection and verification tool for CVE-2026-18963, a Keycloak reset-credentials state bypass. Performs version fingerprinting, realm/client/user…
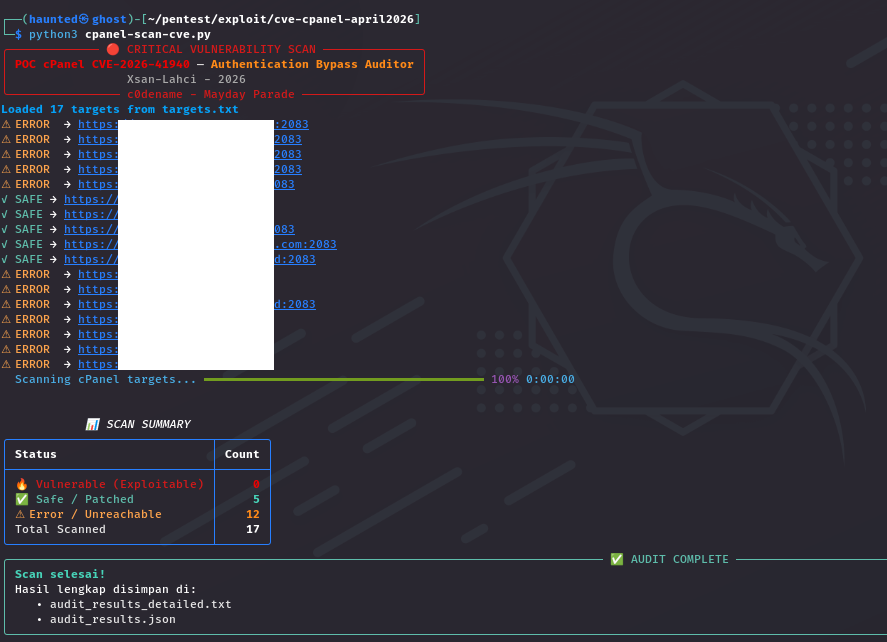 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…