

Tiredful-API
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
api-security-testingeducationlabs-practice+2
payatu/tiredful-apiAn intentionally designed broken web application based on REST API.
 fopje/cve-2022-36539
Insecure Permissions WeDayCare
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 alt3kx/cve-2018-7690
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 alt3kx/cve-2018-7691
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 filipegaudard/cve-2026-30944-poc
Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
 secsys-fdu/cve-2025-51862
Demonstrates an IDOR vulnerability in TelegAI's chat API allowing unauthorized conversation tampering, leading to phishing and XSS-based account…
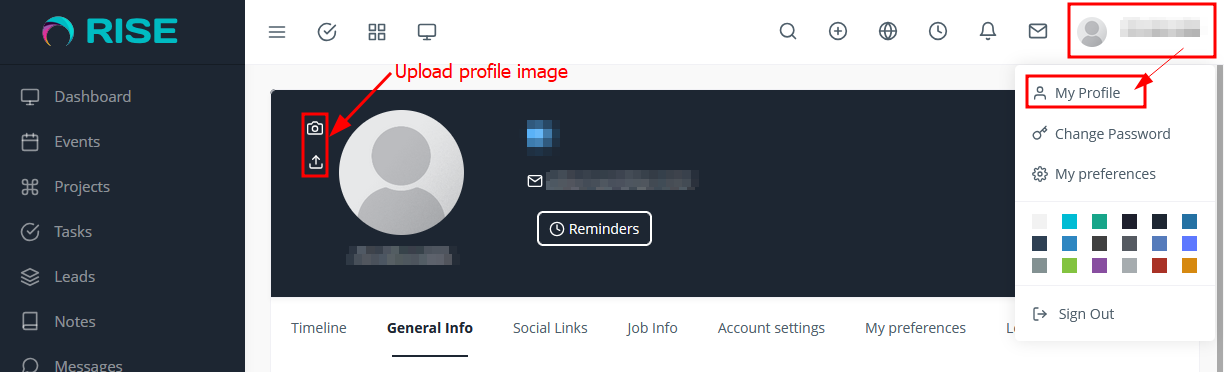 l4zyfox/rise-ultimate_project_manager_e_crm
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
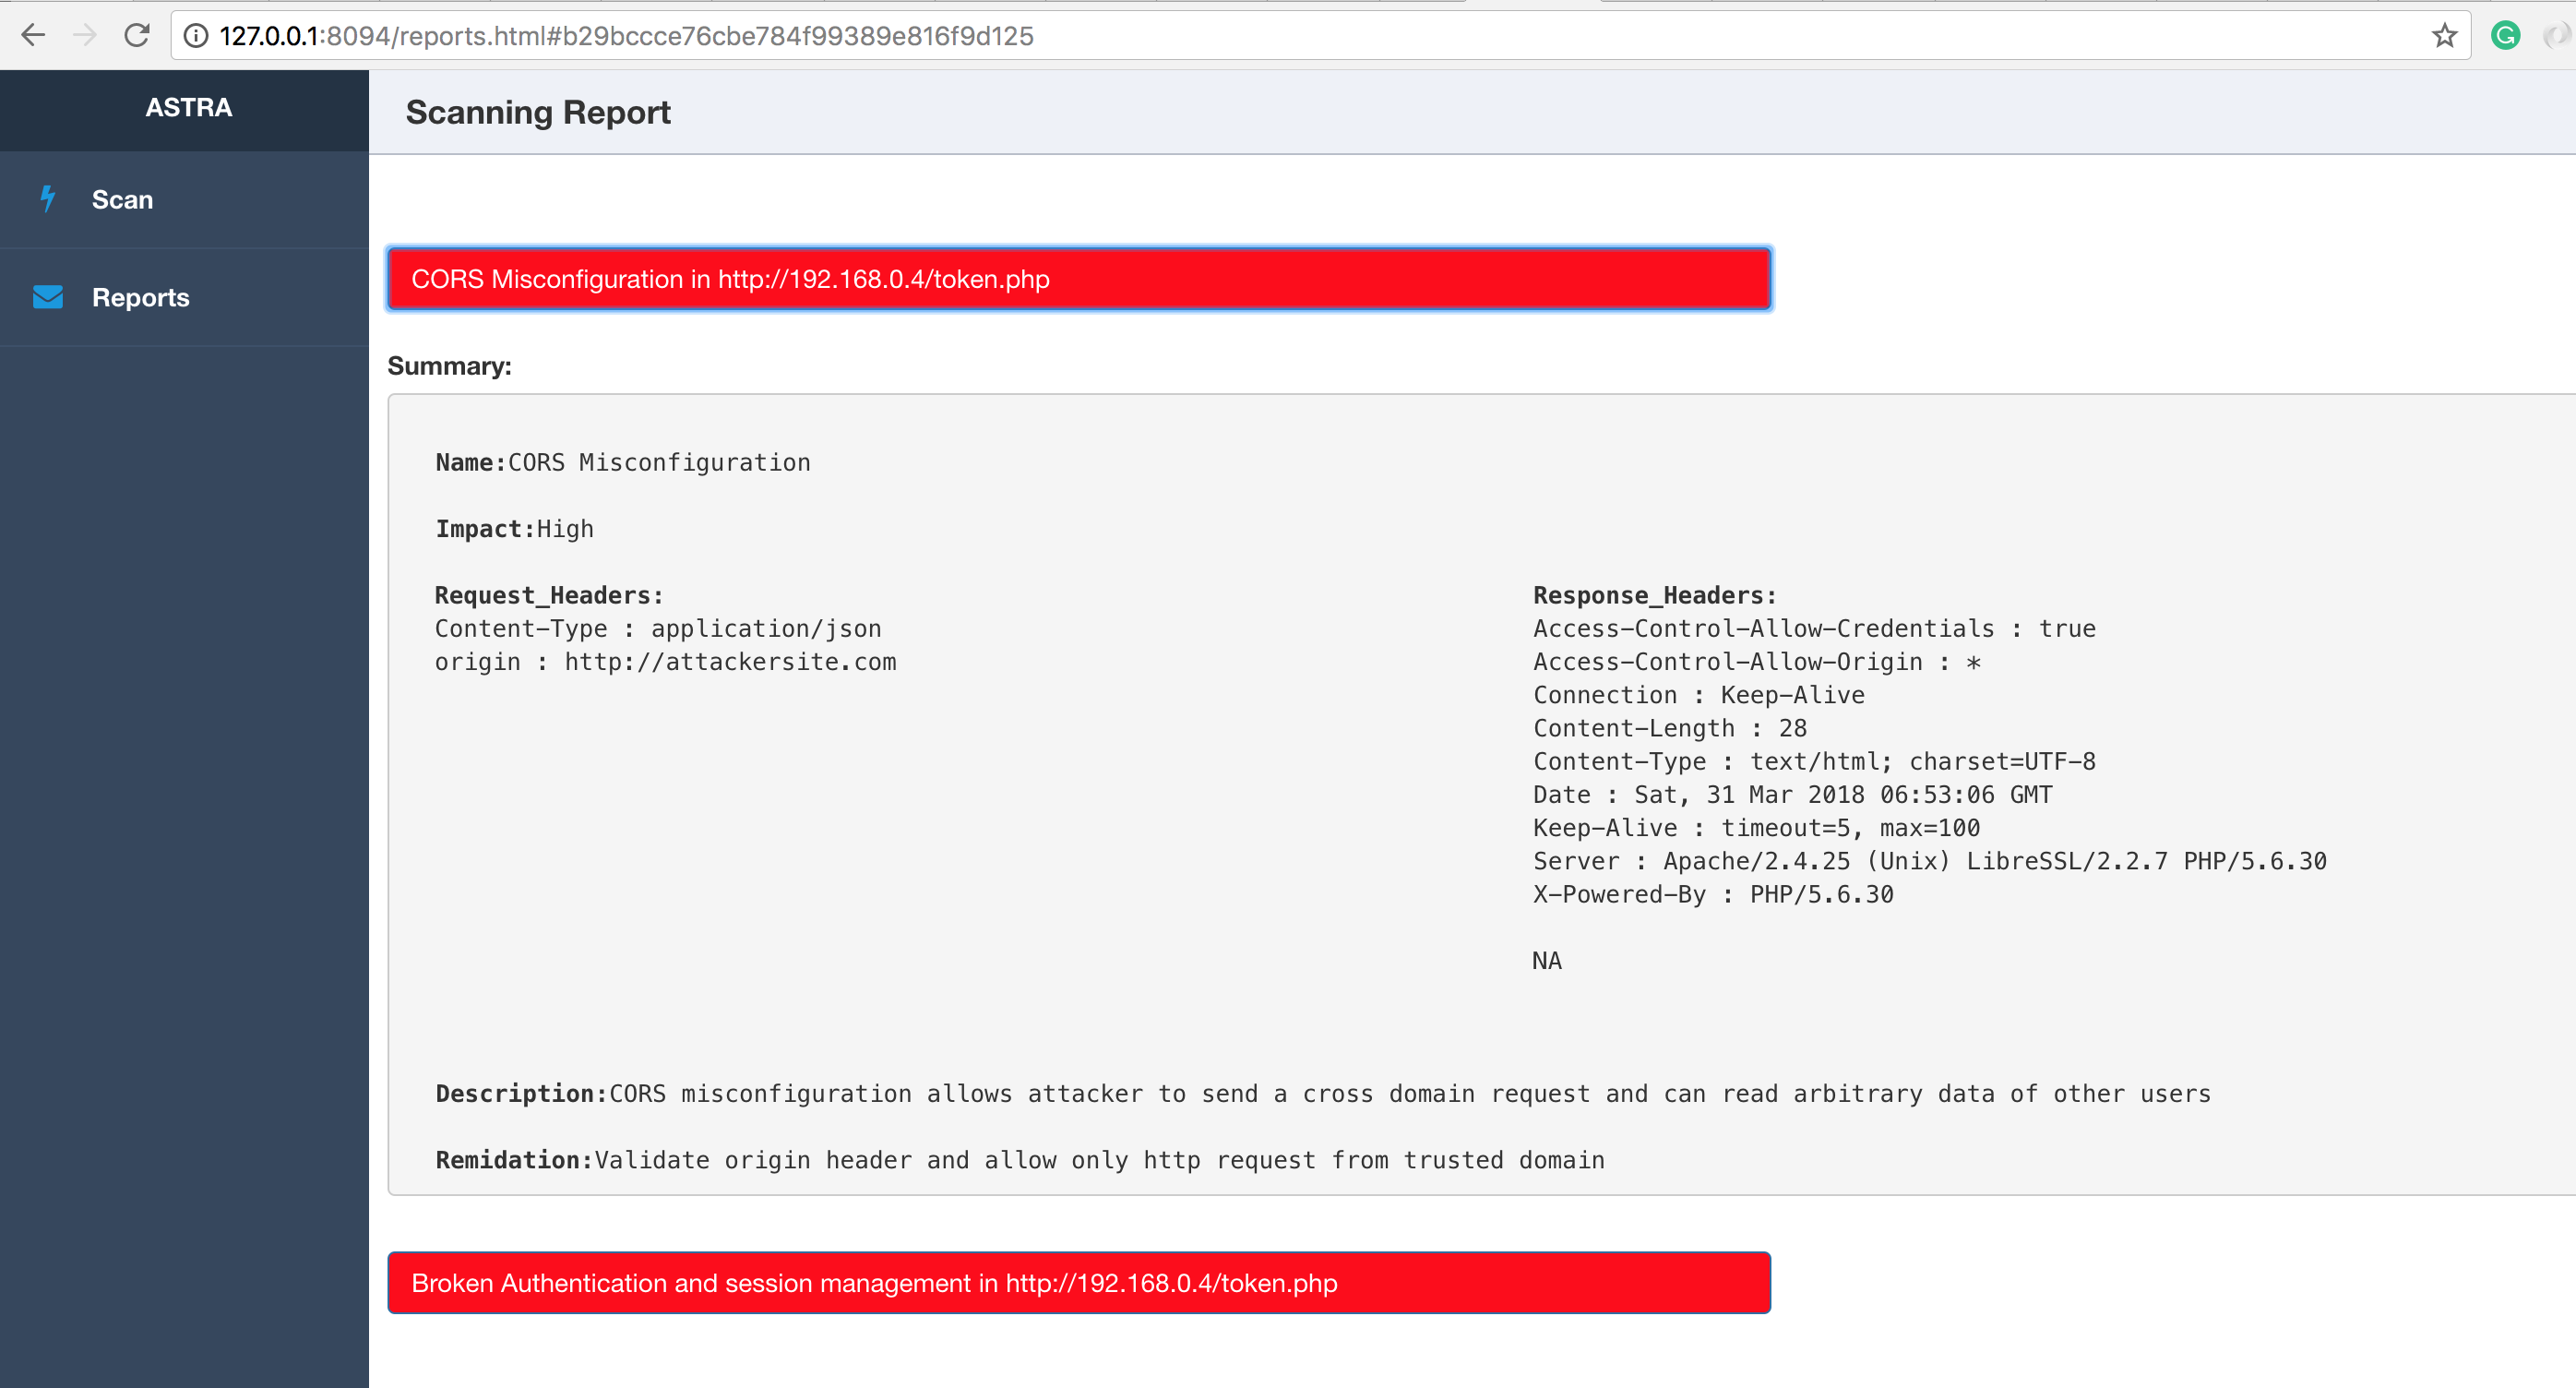 flipkart-incubator/astra
Automated Security Testing For REST API's
 keyvaluesoftwaresystems/agent-opfor
Open-source adversary emulation for AI agents and MCP servers.
 bbva/apicheck
The DevSecOps toolset for REST APIs
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…