
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
RISE-Ultimate_Project_Manager_e_CRM — CVE-2025-3855 - RISE Ultimate Project Manager - IDOR | Kitploit

Tools/GitHubGitHub/l4zyfox/rise-ultimate_project_manager_e_crm
ReconnaissanceVulnerability AnalysisWeb Application ExploitationAPI Security TestingInformation GatheringPenetration Testing
GitHubl4zyfox/rise-ultimate_project_manager_e_crm

RISE-Ultimate_Project_Manager_e_CRM

Share

CVE-2025-3855 - RISE Ultimate Project Manager - IDOR

View Repository
321 year agoNot yet reviewed

CVE-2025-3855 - RISE Ultimate Project Manager - IDOR

Security vulnerability: IDOR (Insecure Direct Object Reference)
Affected Component: profile image upload endpoint, team_members controller
Software: RISE - Ultimate Project Manager & CRM
Vendor: codecanyon
Version: 3.8.2

CVE ORG : https://www.cve.org/CVERecord?id=CVE-2025-3855
NIST: https://nvd.nist.gov/vuln/detail/CVE-2025-3855
CVE DETAILS: https://www.cvedetails.com/cve/CVE-2025-3855

Describe the bug/issue:

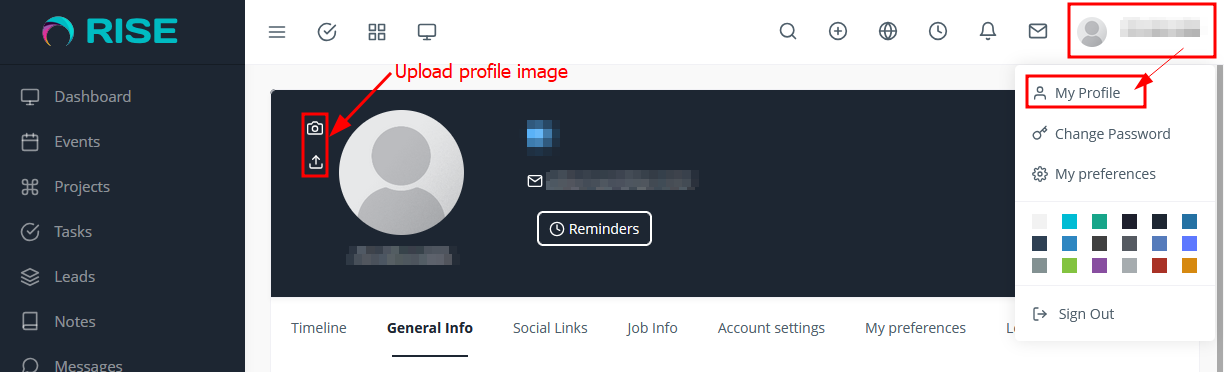
A vulnerability was discovered in RISE - Ultimate Project Manager & CRM that allows an authenticated user to change the profile picture of any other user by exploiting an Insecure Direct Object Reference (IDOR) in the /index.php/team_members/save_profile_image/[user_id] endpoint. The application does not properly validate whether the authenticated user is authorized to update the specified user ID’s profile image, allowing unauthorized modification of user data. This flaw impacts data integrity and may lead to impersonation or disruption of user experience.

To Reproduce:

🧑‍💼 1. Authenticated Access to Profile Settings

An authenticated user navigates to the "My Profile" section of the application, where they are provided with an option to upload or update their profile image.

📤 2. Interception of the Upload Request

Upon uploading a profile image, the request can be intercepted using a proxy tool such as Burp Suite. The request is a POST to the following endpoint:

POST /index.php/team_members/save_profile_image/36

Here, 36 corresponds to the authenticated user's numeric ID.

🔁 3. Exploiting the IDOR via User ID Manipulation

By changing the ID in the URL path to that of another valid user, for example:

POST /index.php/team_members/save_profile_image/44

The application processes the request and updates the profile picture of user ID 44, without performing any access control checks.

🔐 4. Lack of Authorization Validation

The server-side implementation fails to validate whether the authenticated user is authorized to perform the action on the targeted user ID. As a result, any authenticated user can change the profile images of other users, impacting the integrity of user data and potentially leading to impersonation or user confusion.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →




