

pwnproxy
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
ai-securityapi-security-testingcrawler+6
822 days ago
ericmtzmtz/pwnproxyAn open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 spectolabs/hoverfly
Lightweight service virtualization/ API simulation / API mocking tool for developers and testers
 0xsteph/pentest-ai
Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
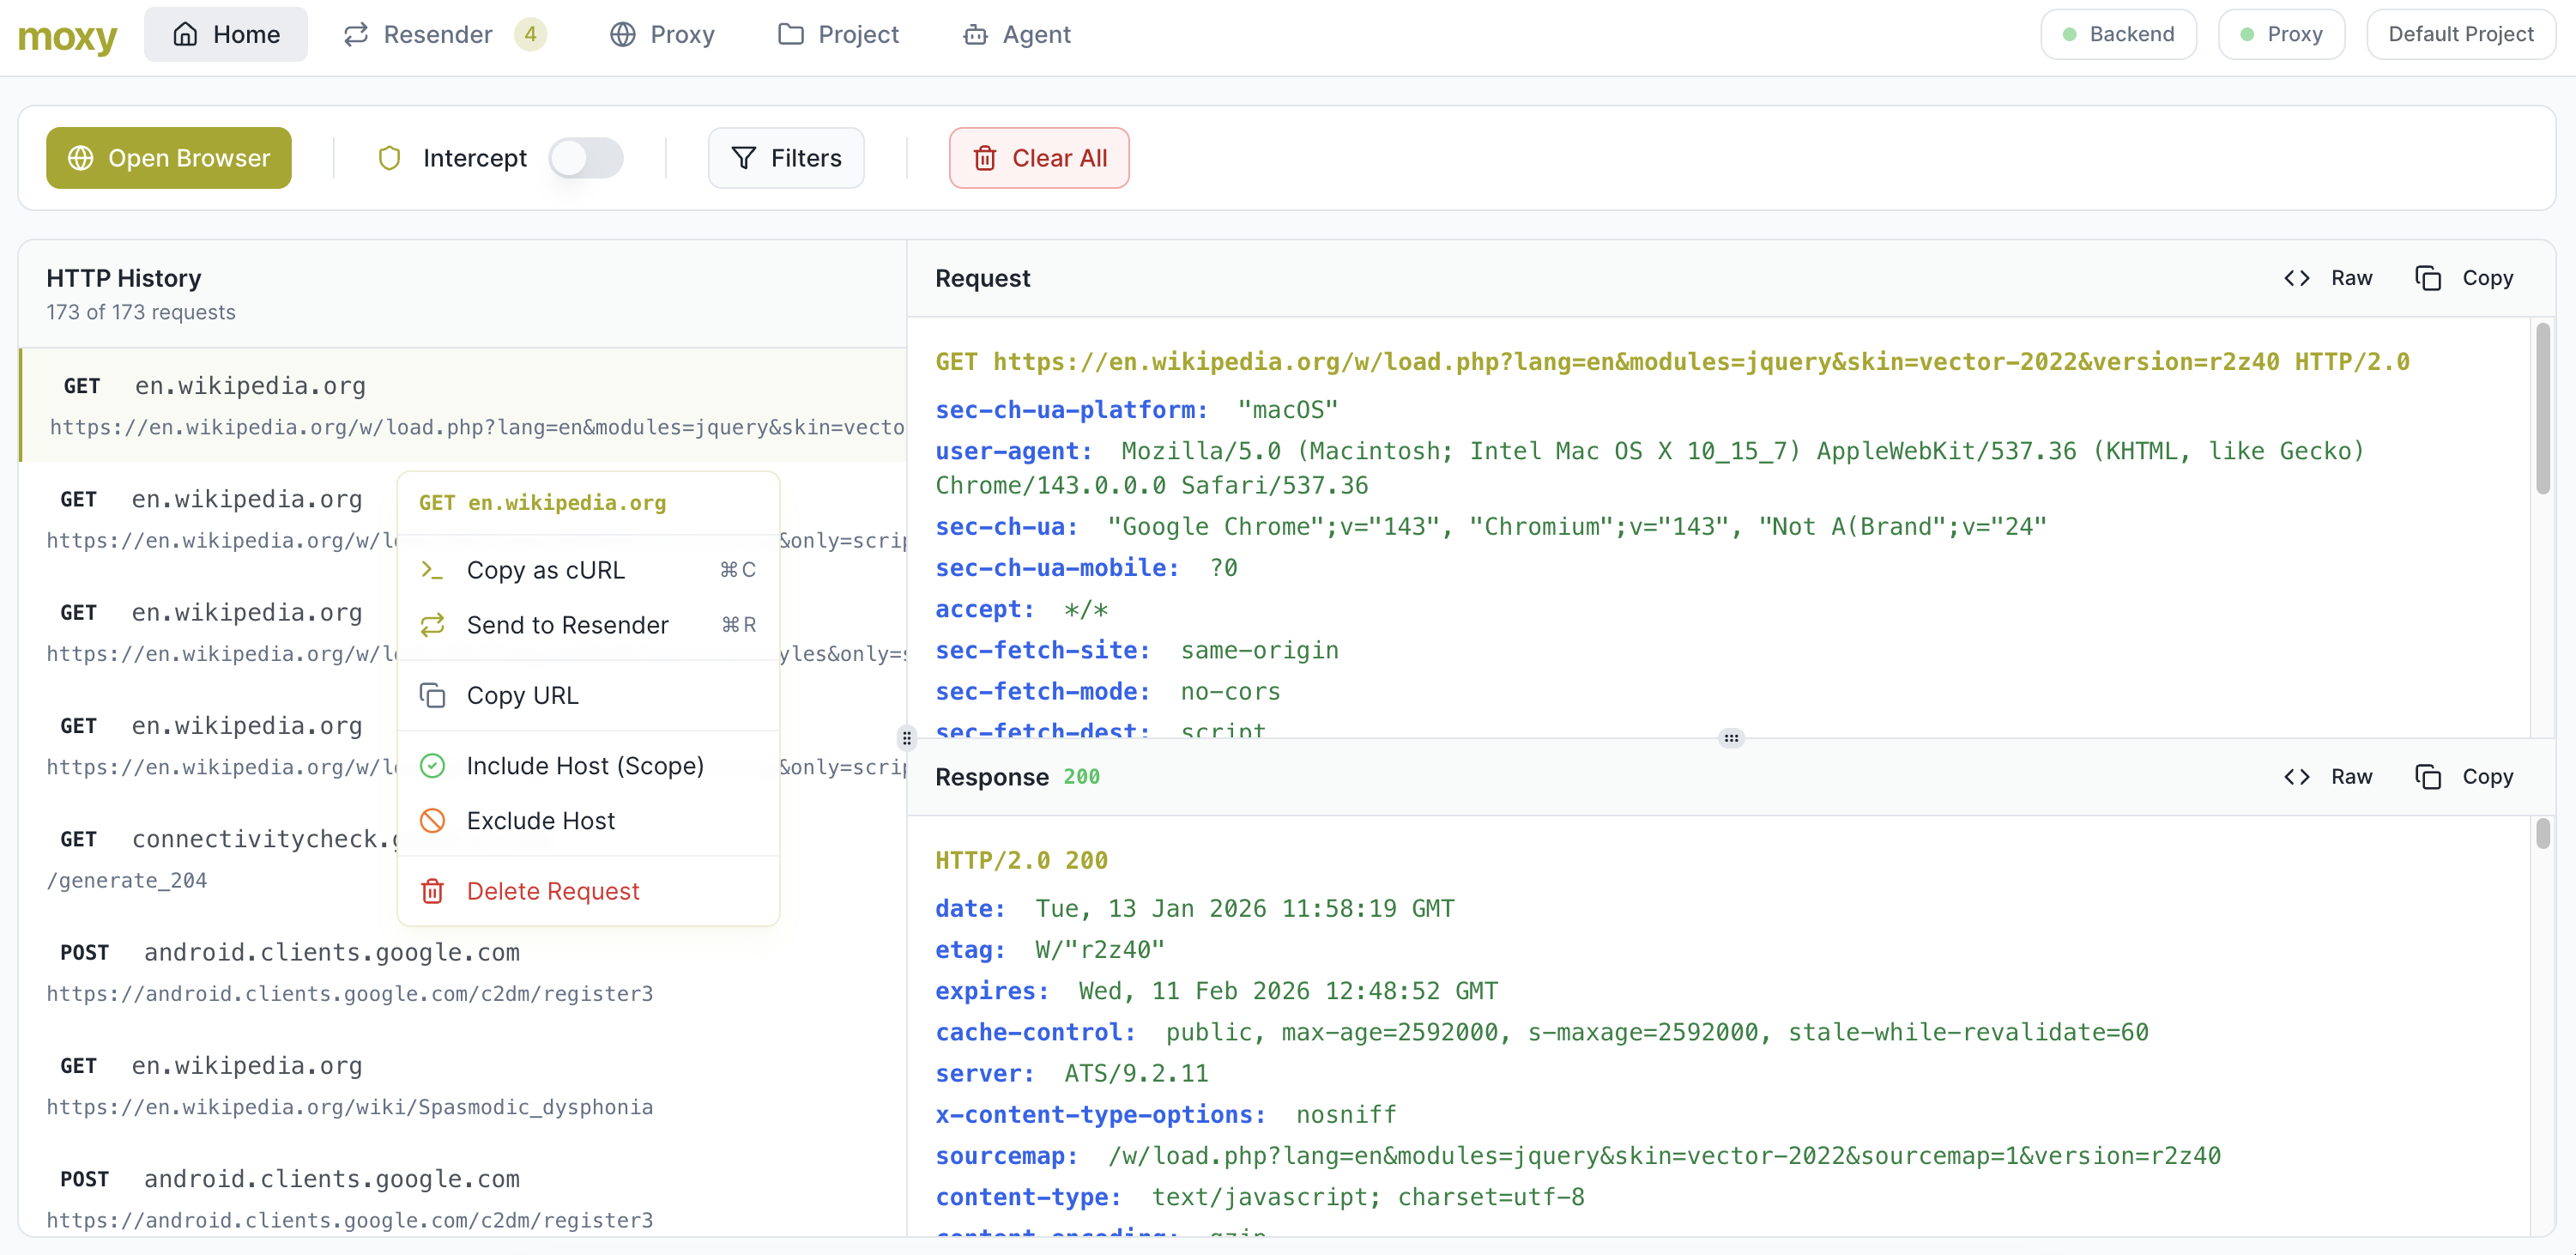 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
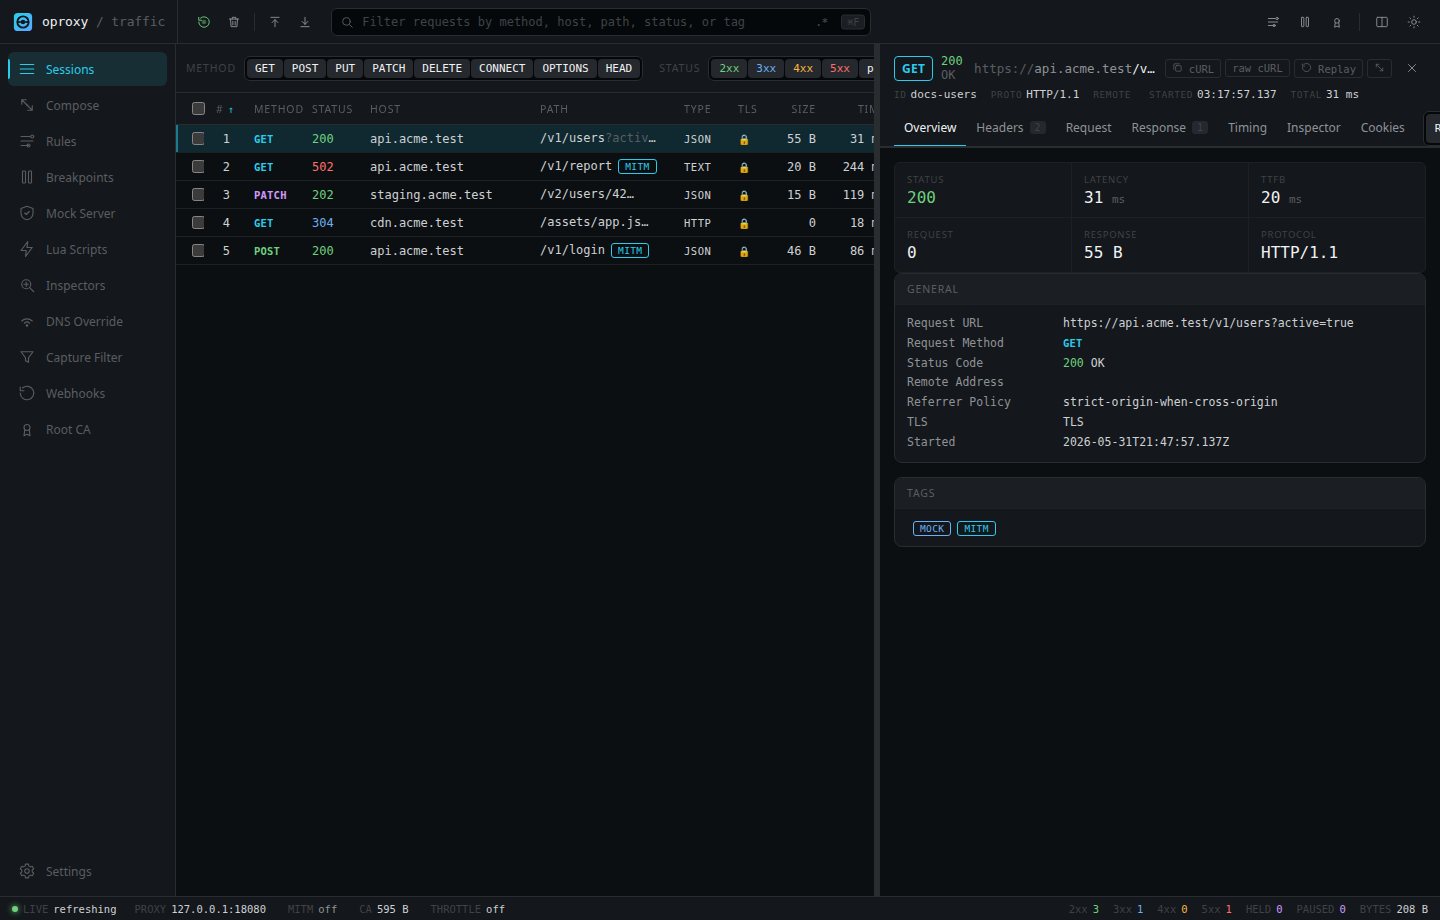 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
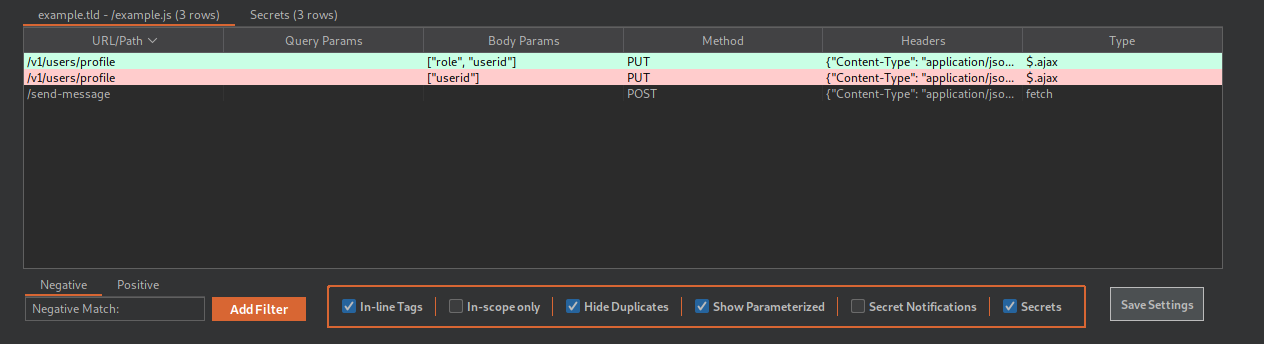 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…