

strix
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
ai-securityapi-security-testingcode-analysis+9
64.2k
usestrix/strixOpen-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
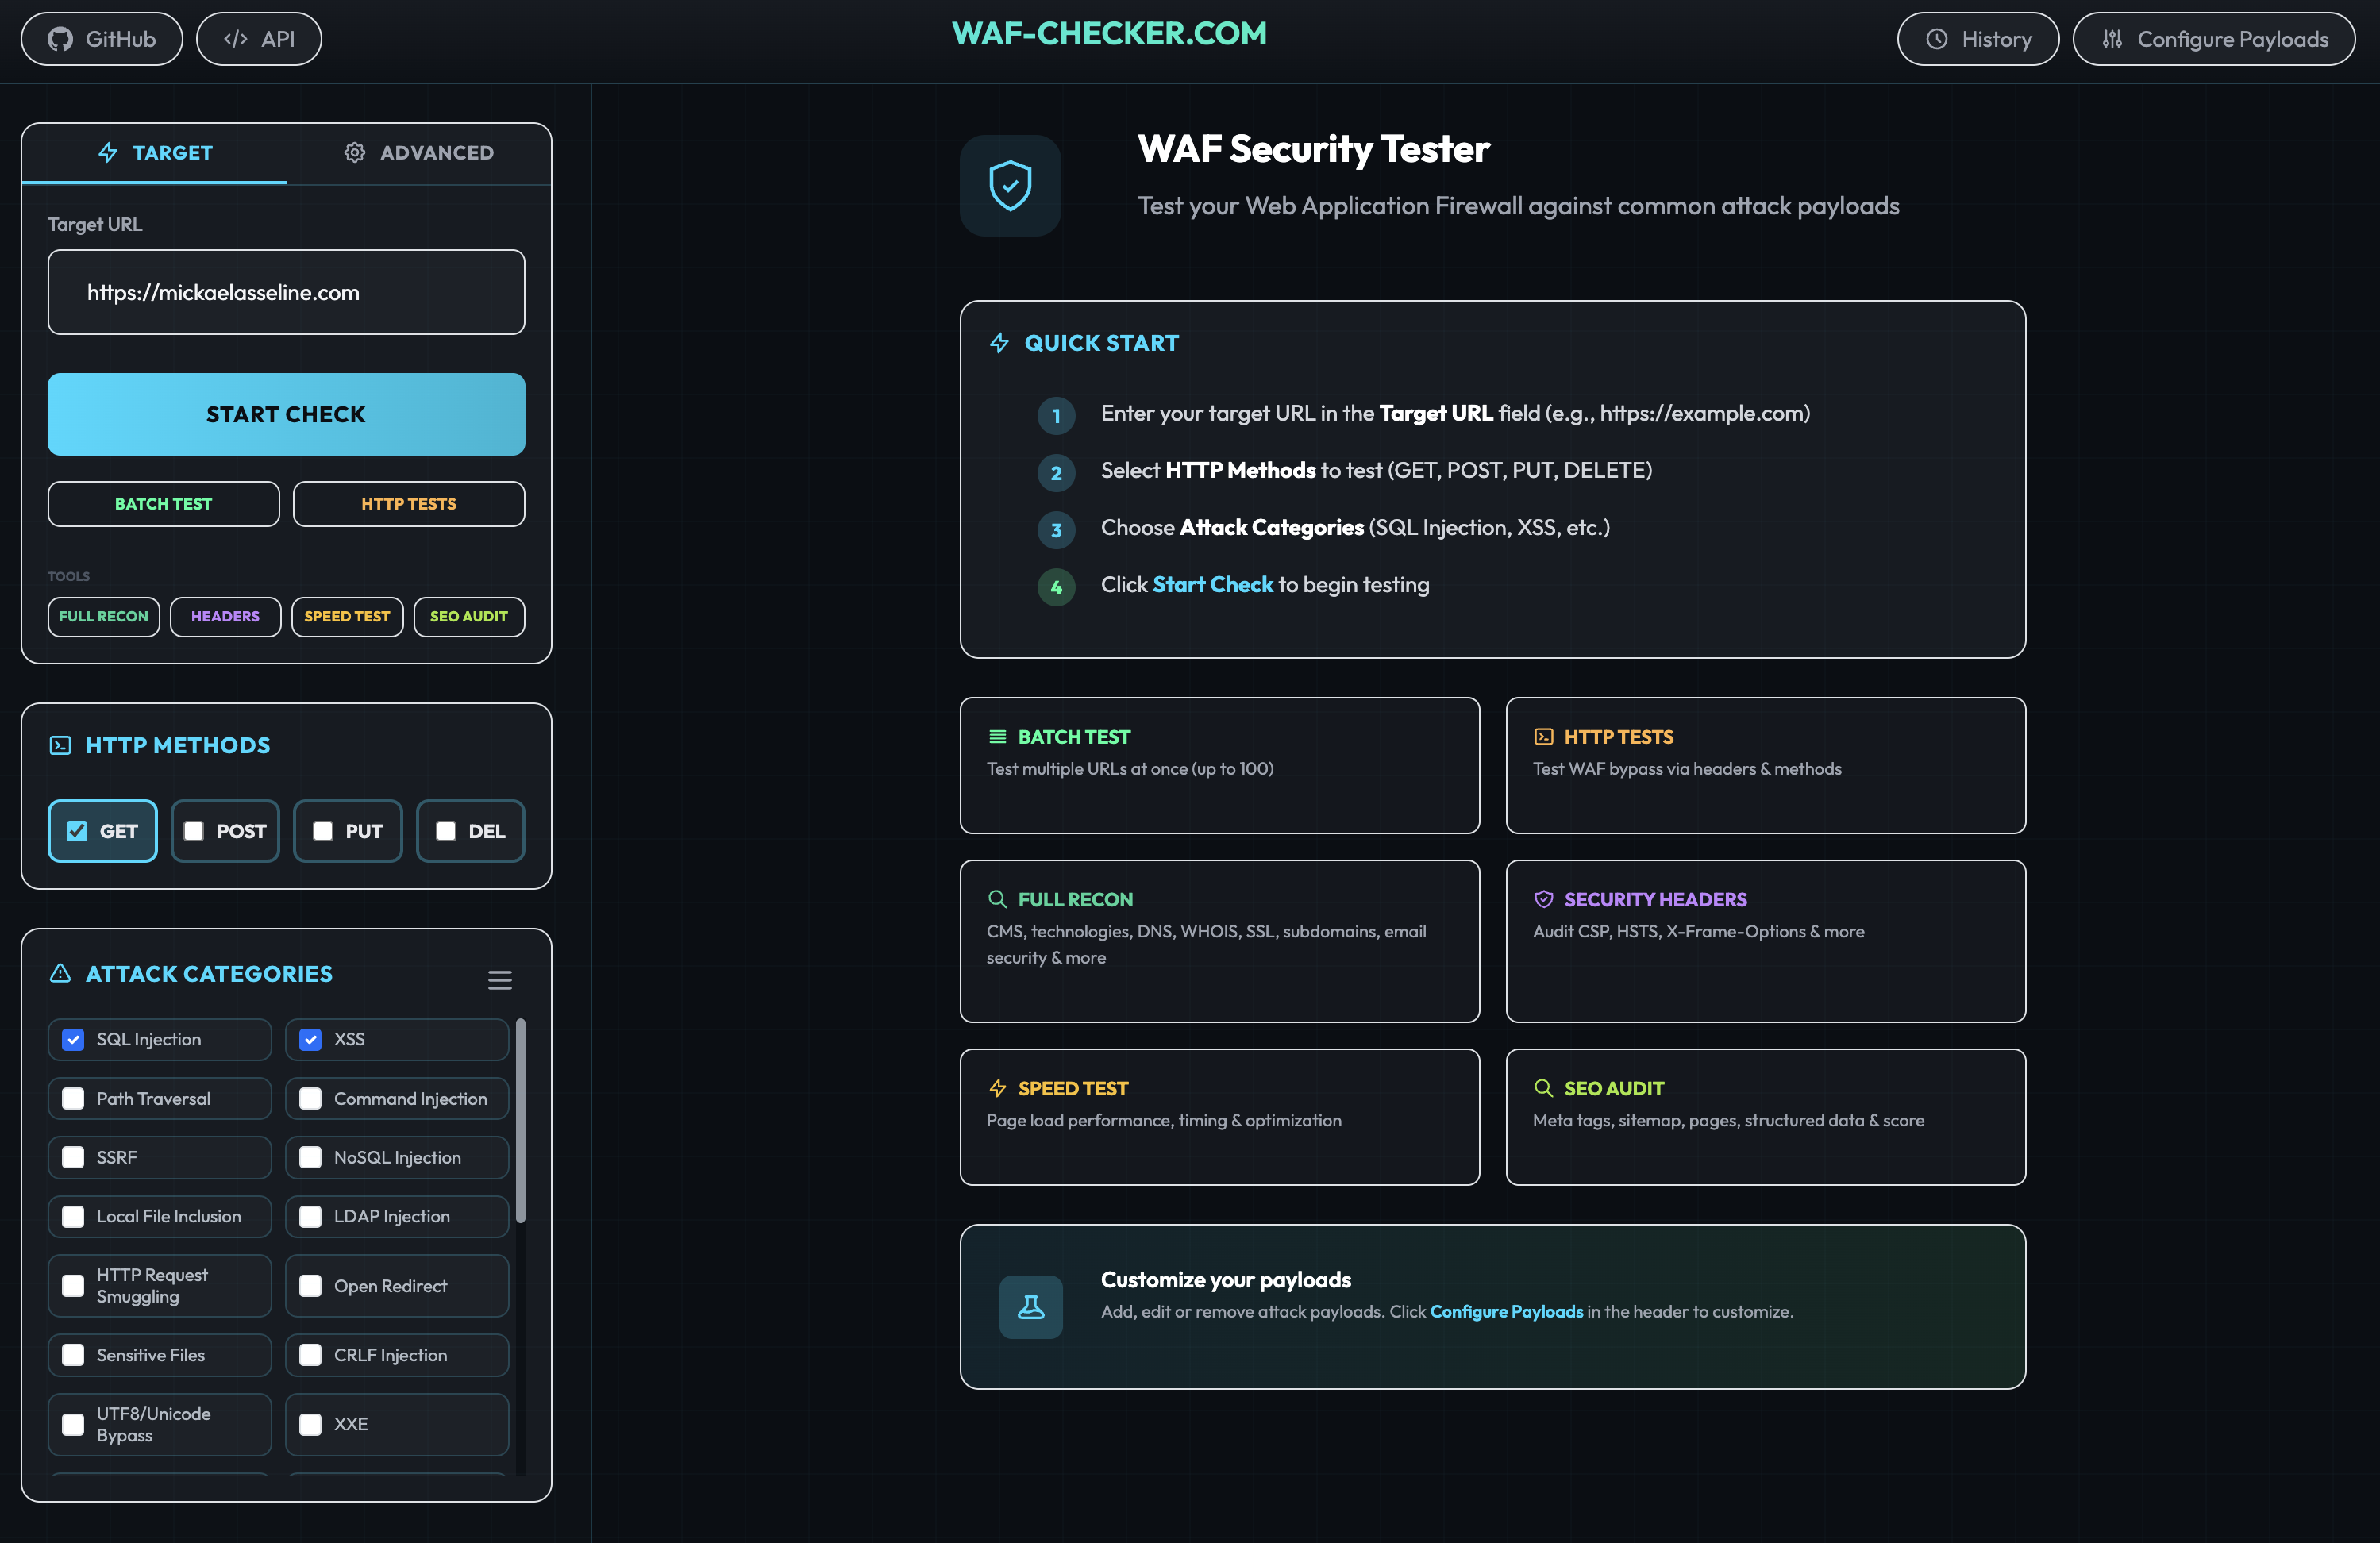 papamica/waf-checker
Tests your WAF with +160 payloads
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
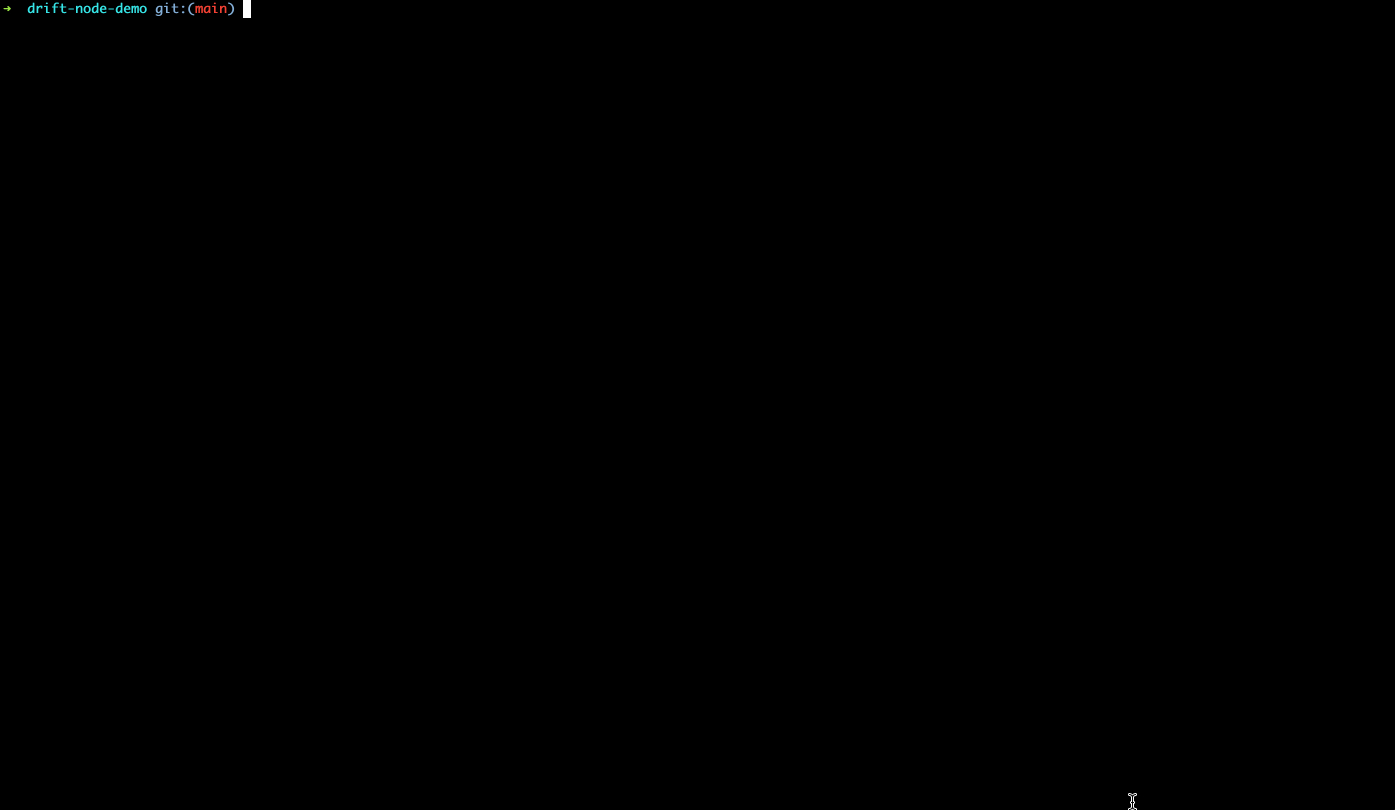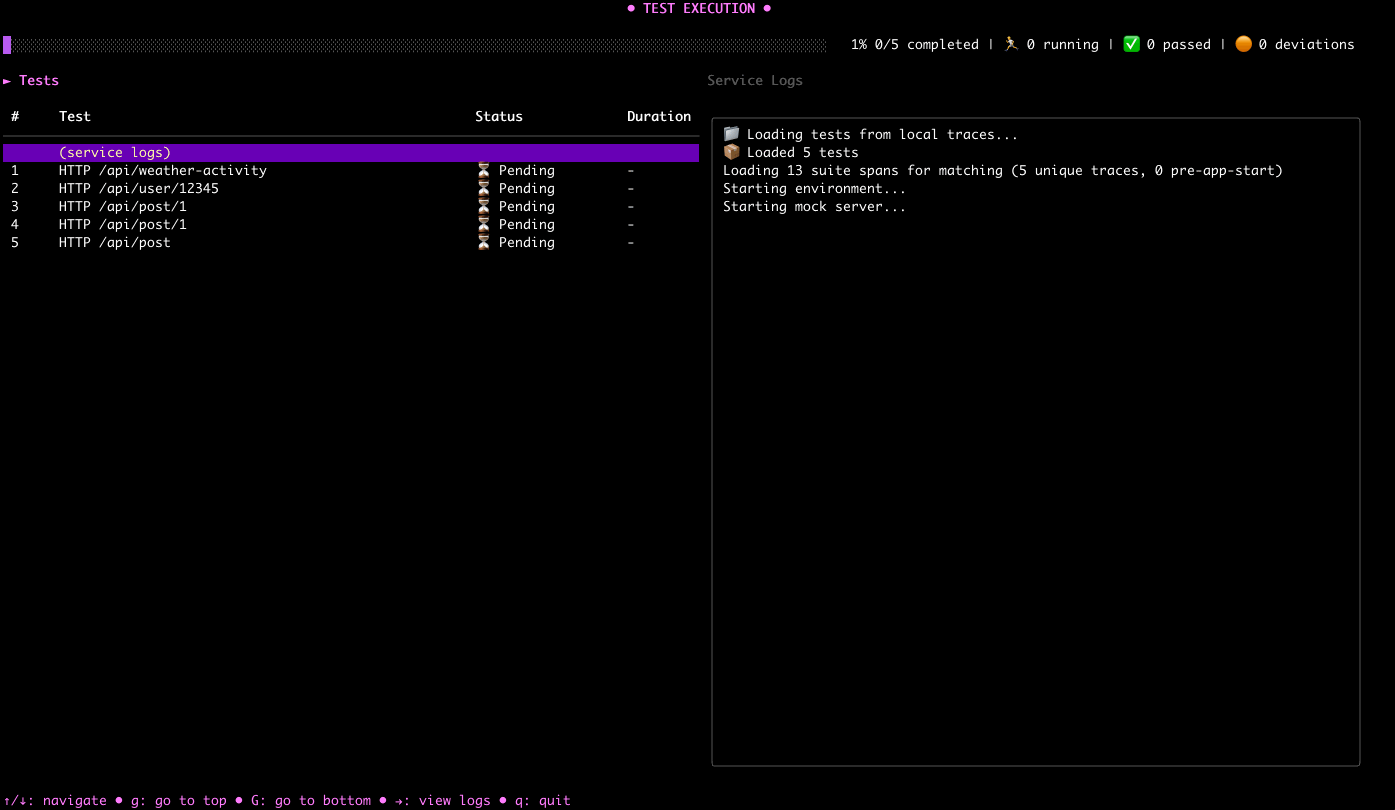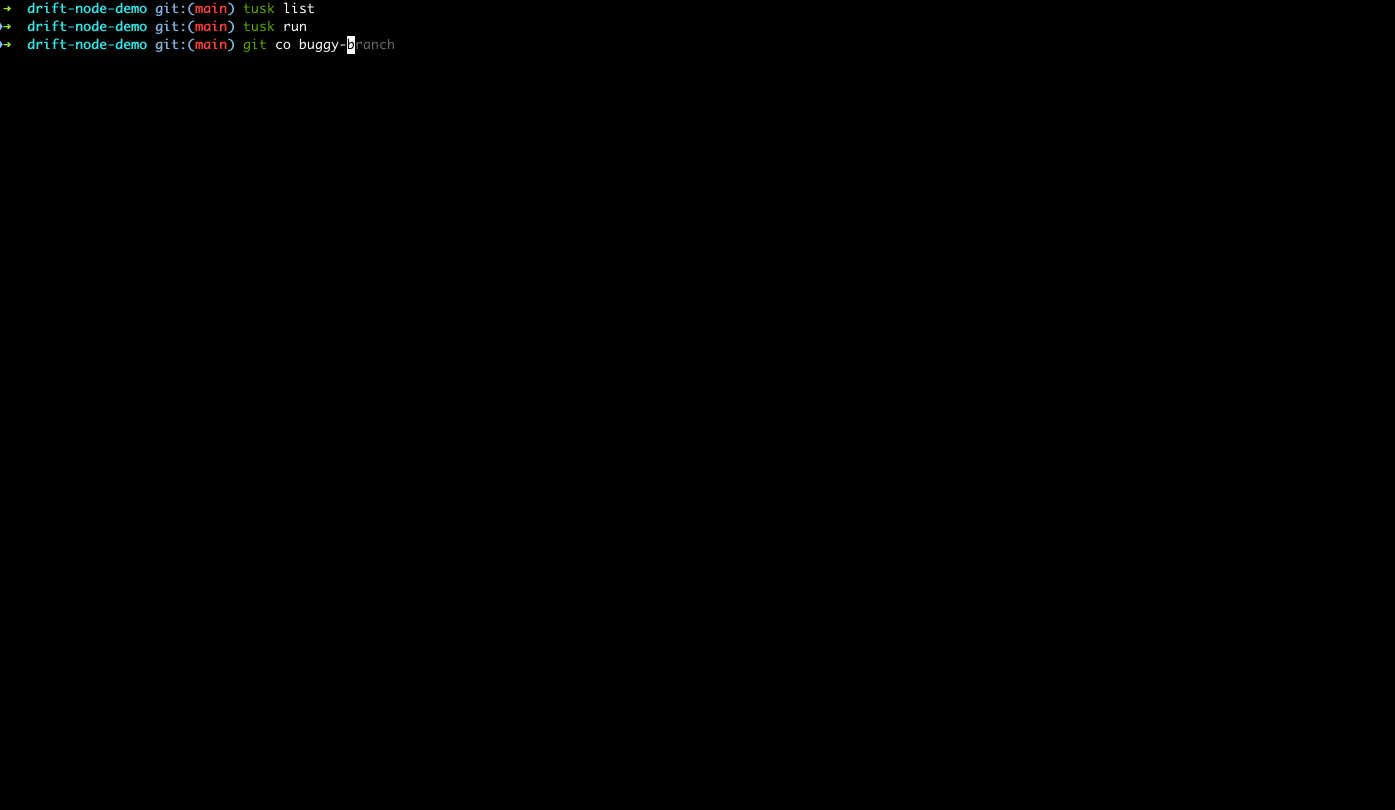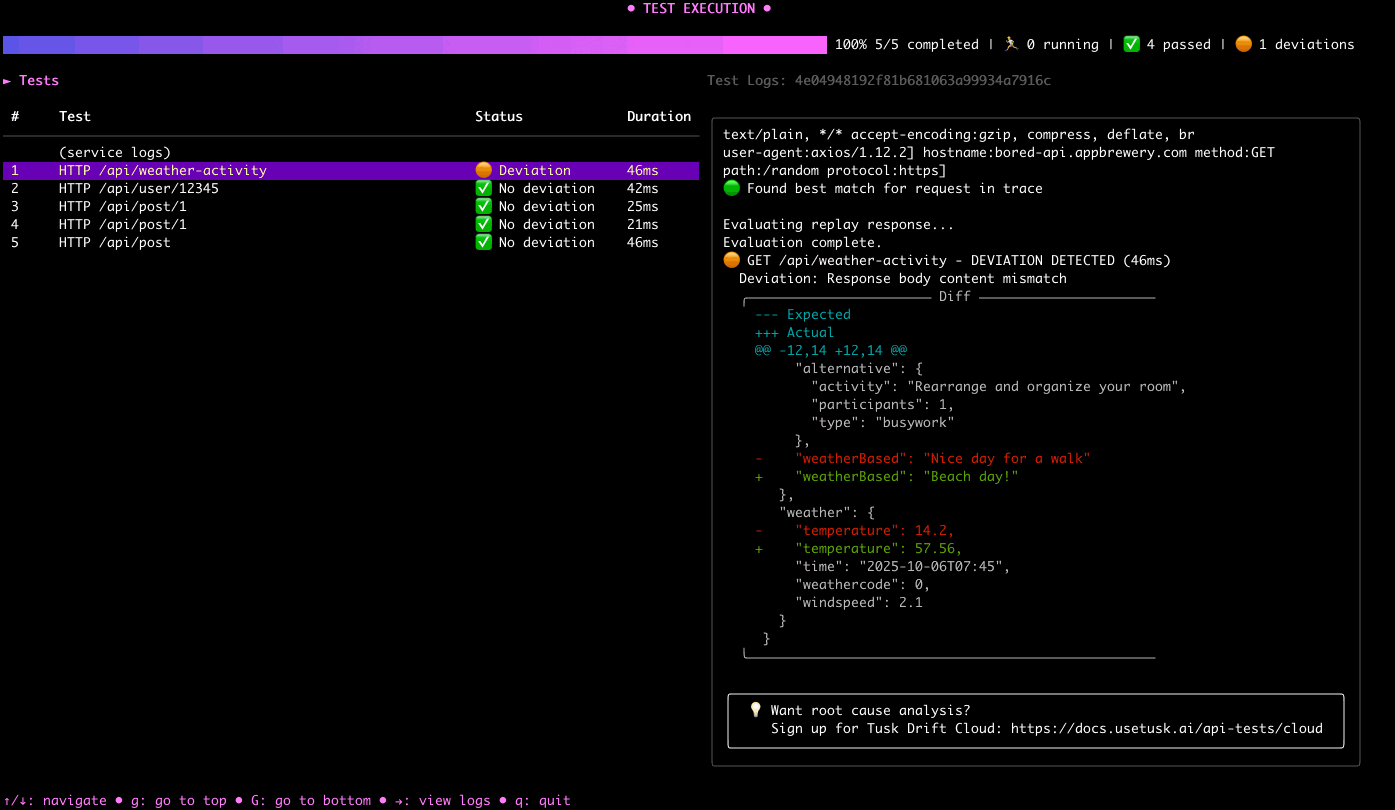 use-tusk/drift-node-sdk
Node.js SDK for capturing and replaying API calls made to/from your service
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
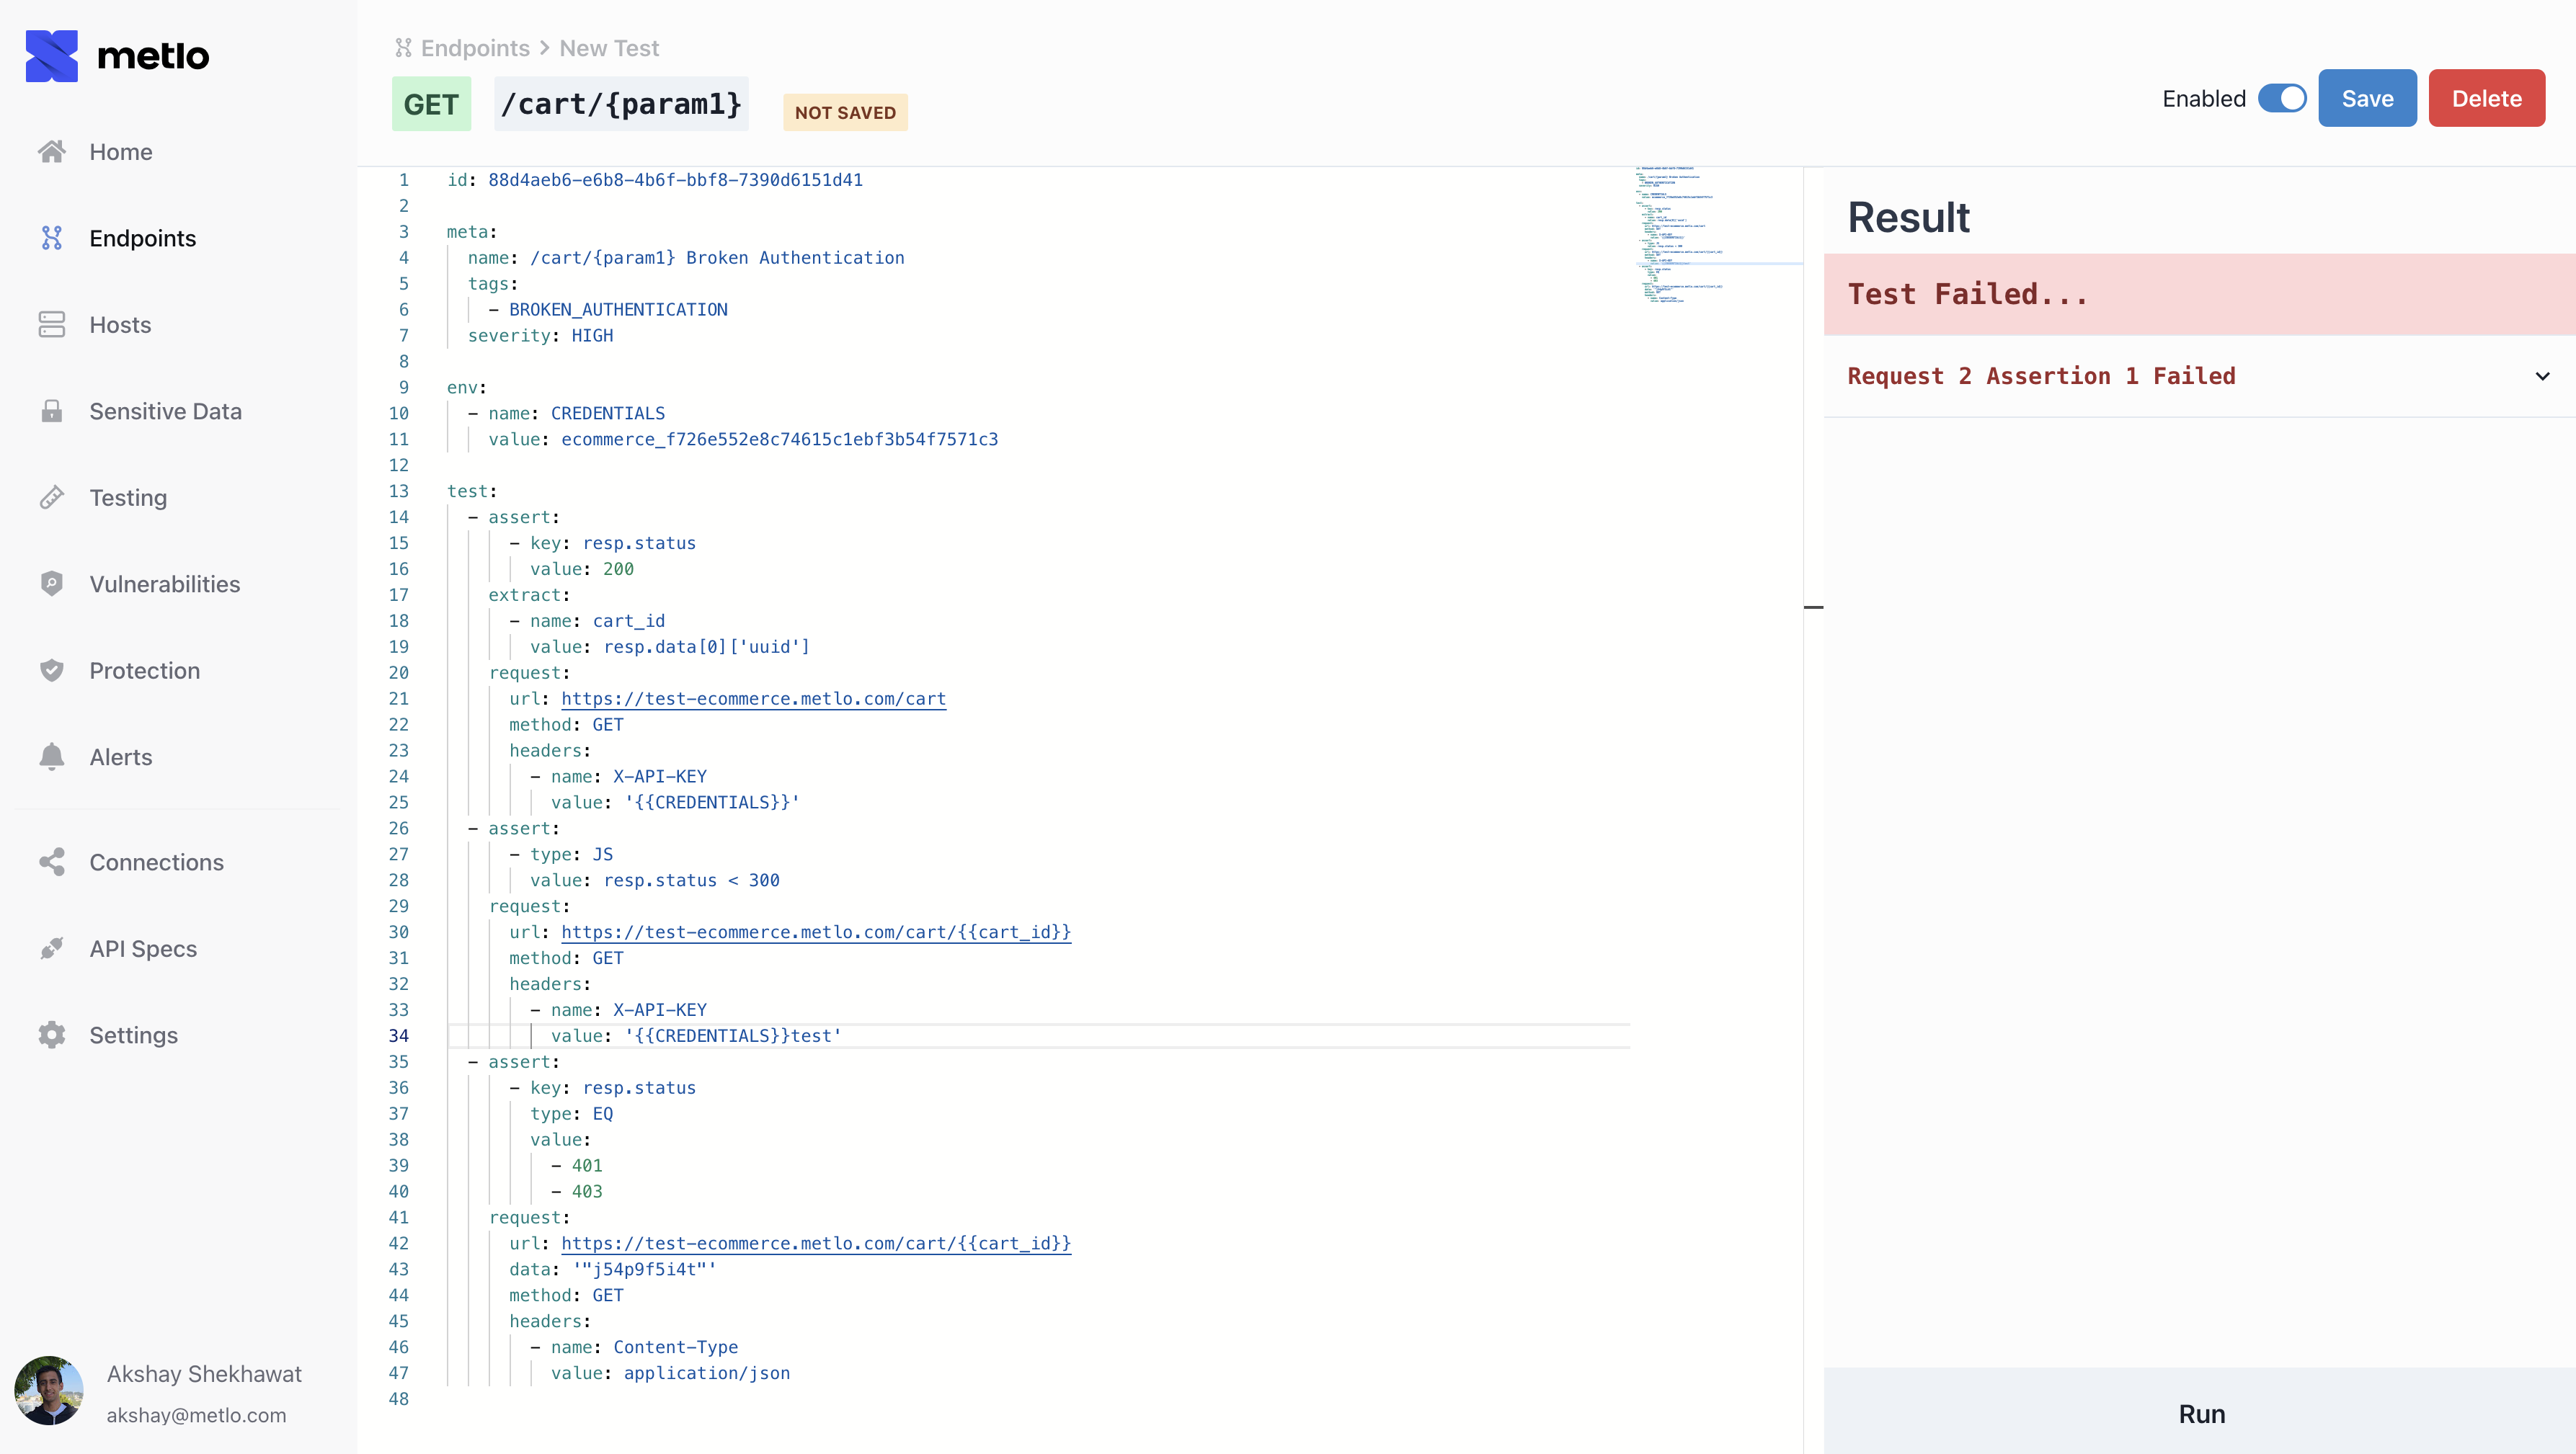 metlo-labs/metlo
Metlo is an open-source API security platform.
 elastic/agent-skills
Official Elastic Skills
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
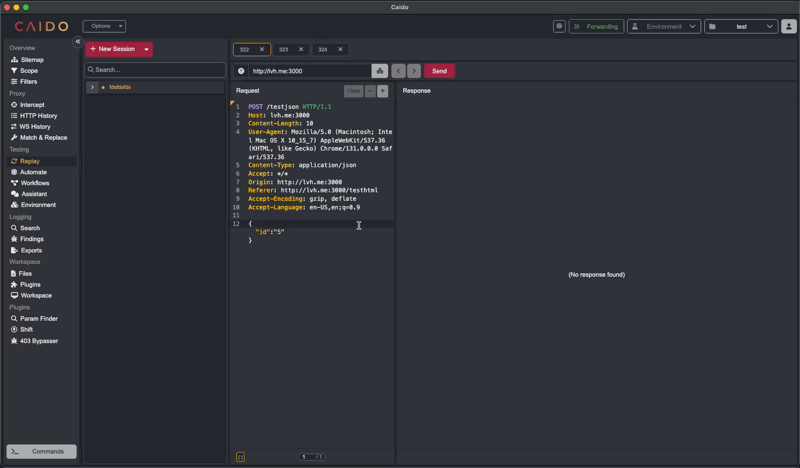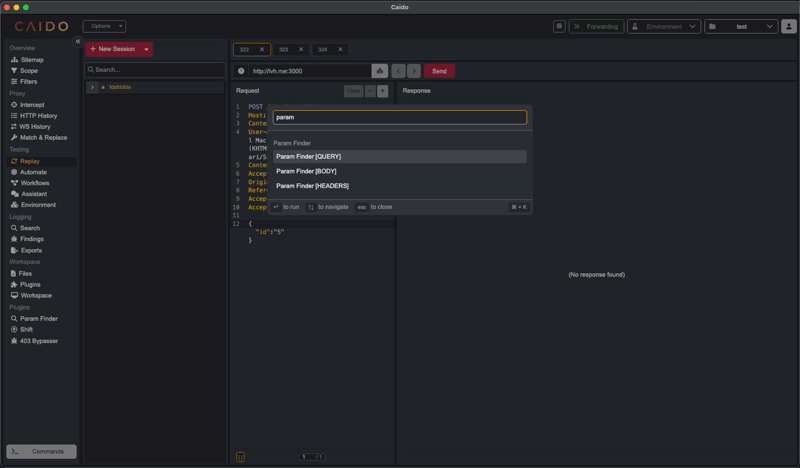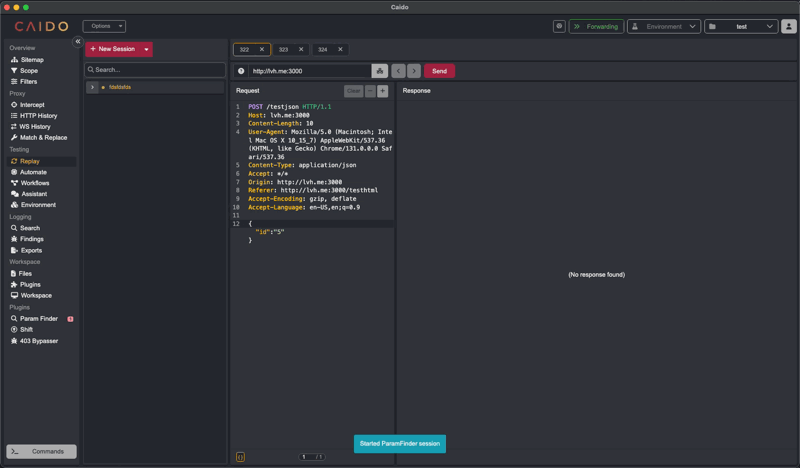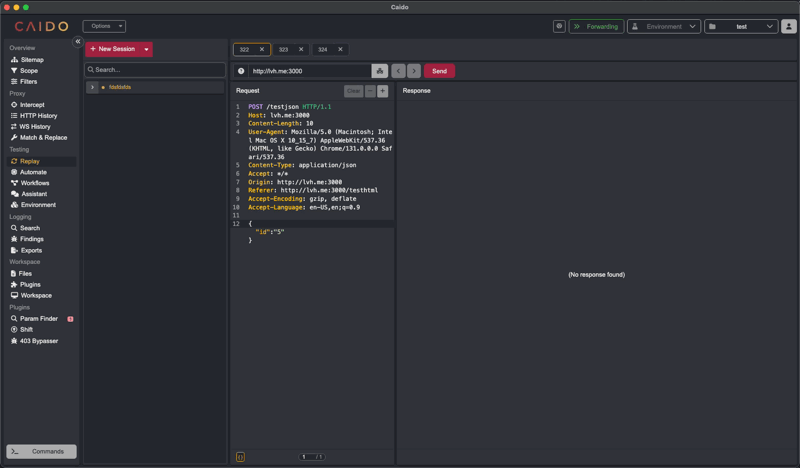 caido-community/paramfinder
Discover hidden parameters in Caido