
Archived
syntribos
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
api-security-testingfuzzingpenetration-testing+2
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 flipkart-incubator/astra
Automated Security Testing For REST API's
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
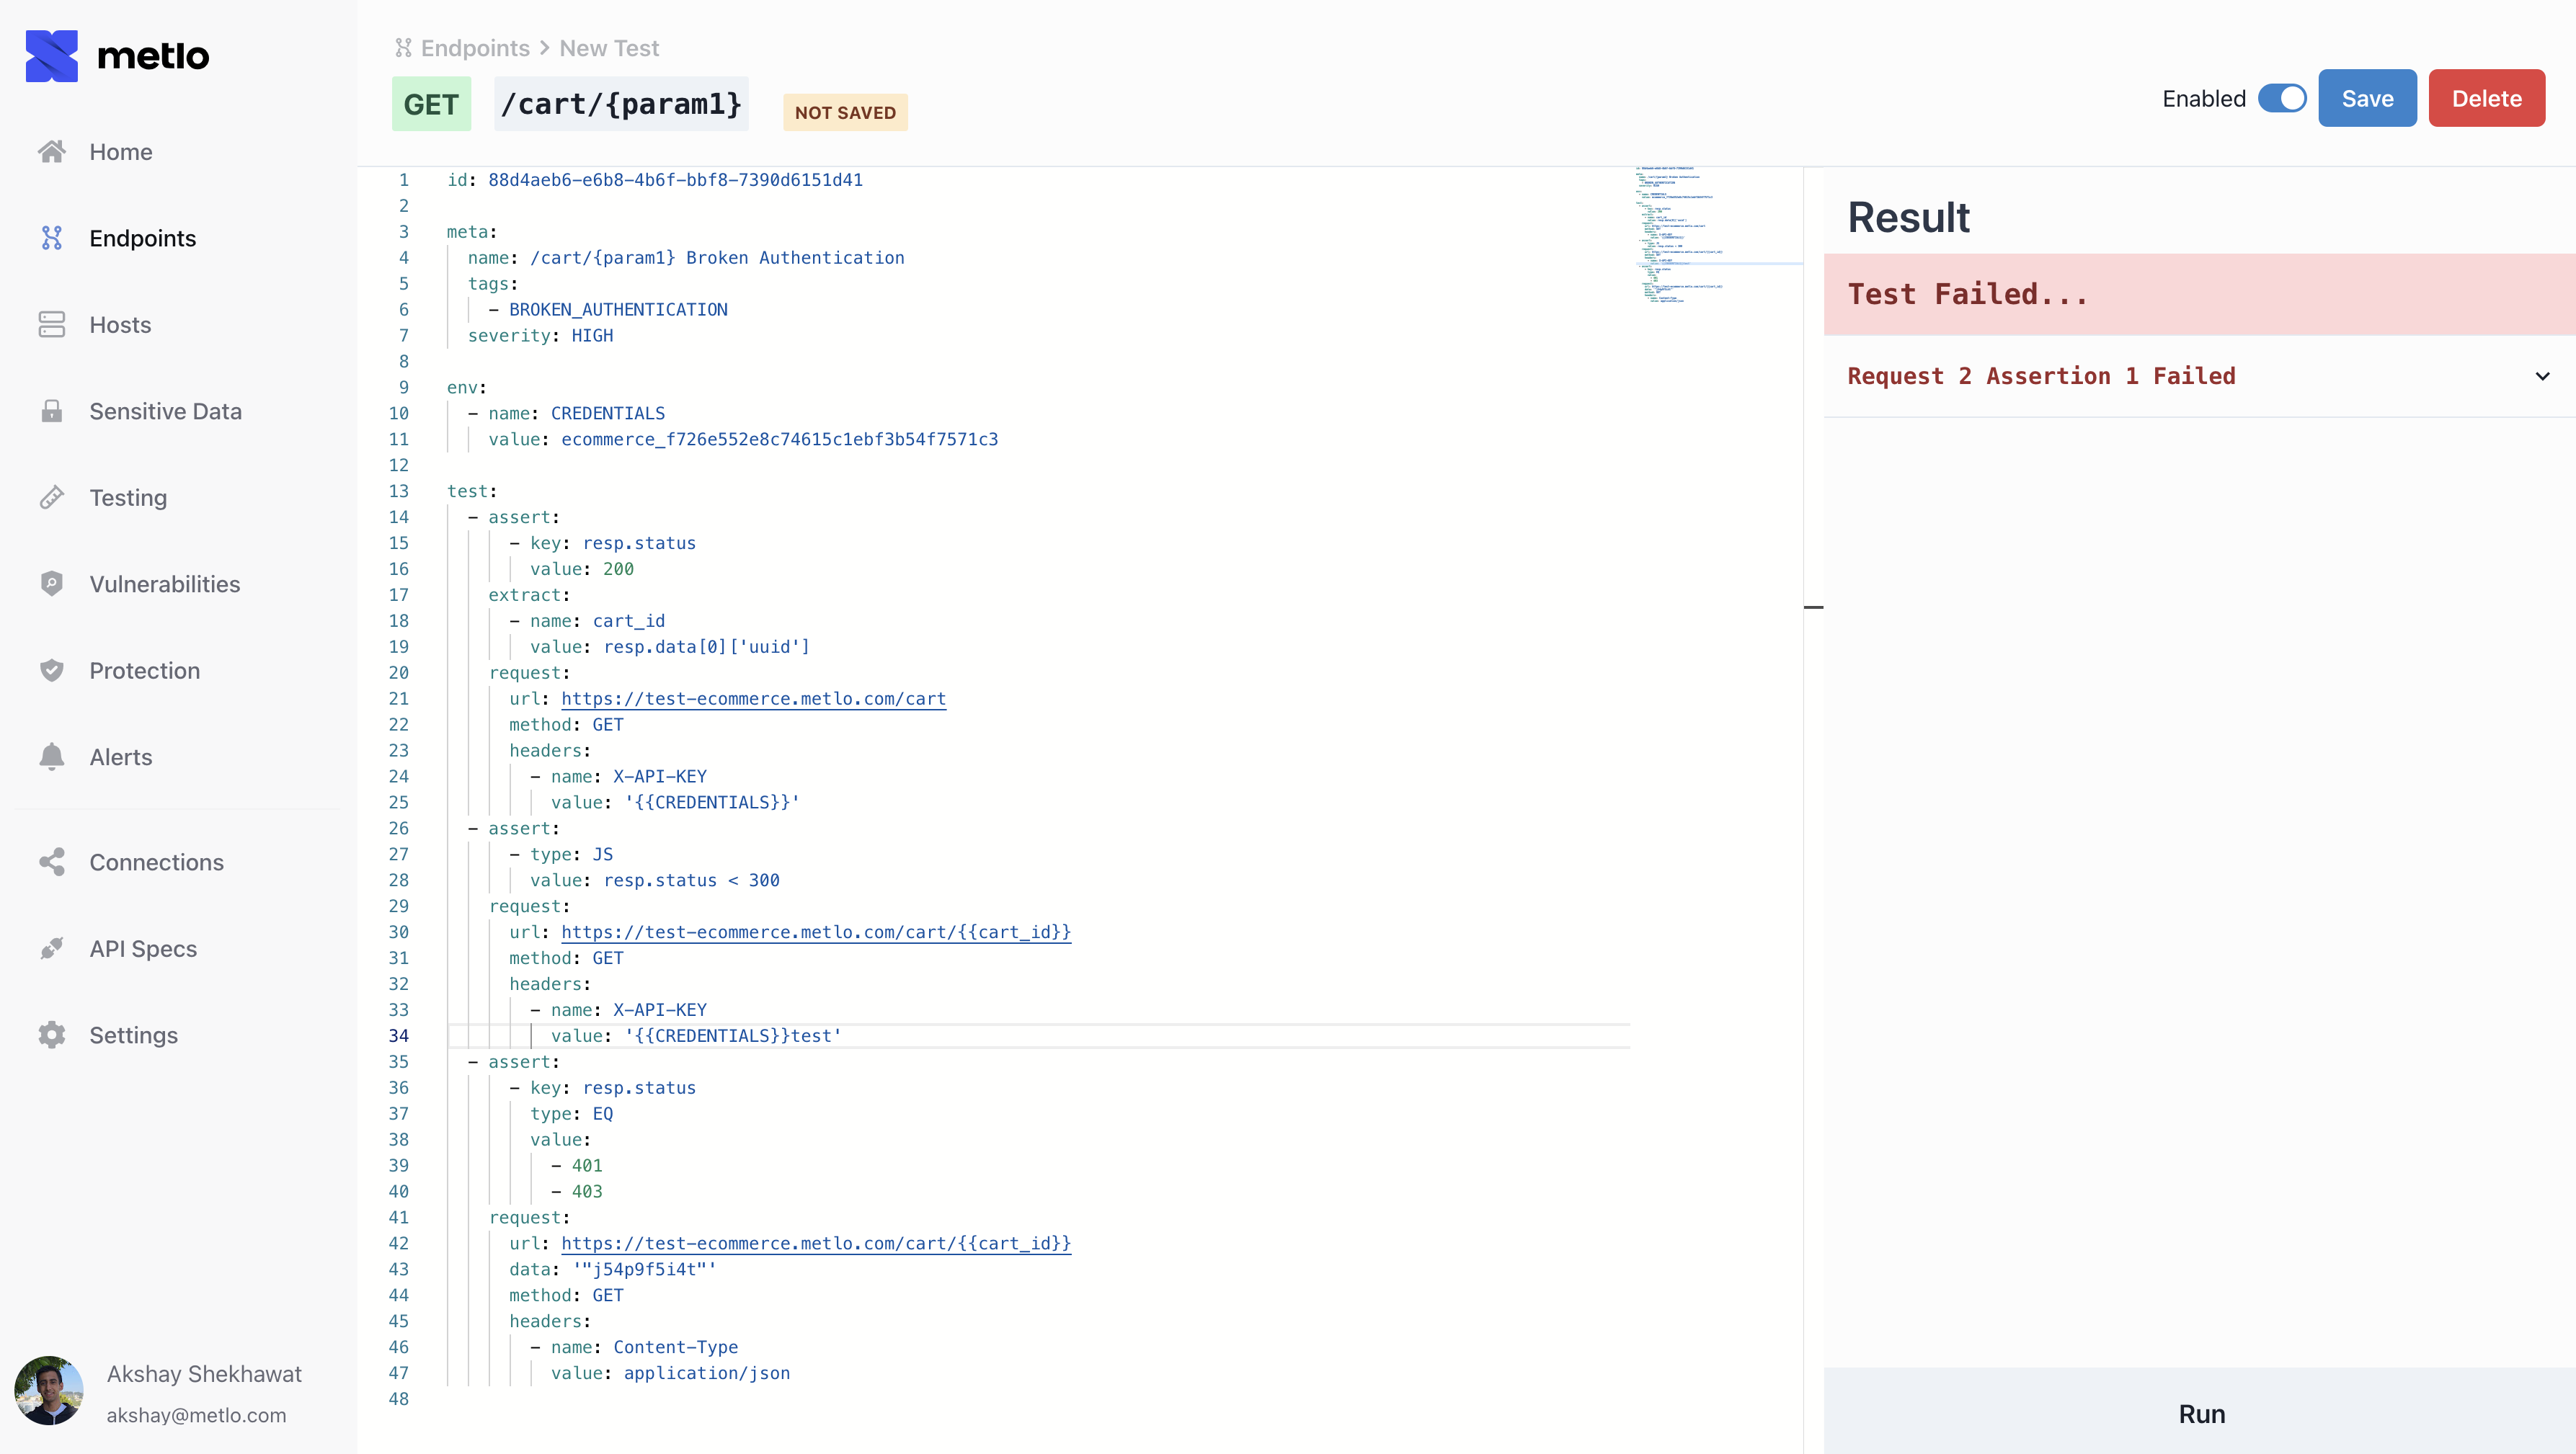 metlo-labs/metlo
Metlo is an open-source API security platform.
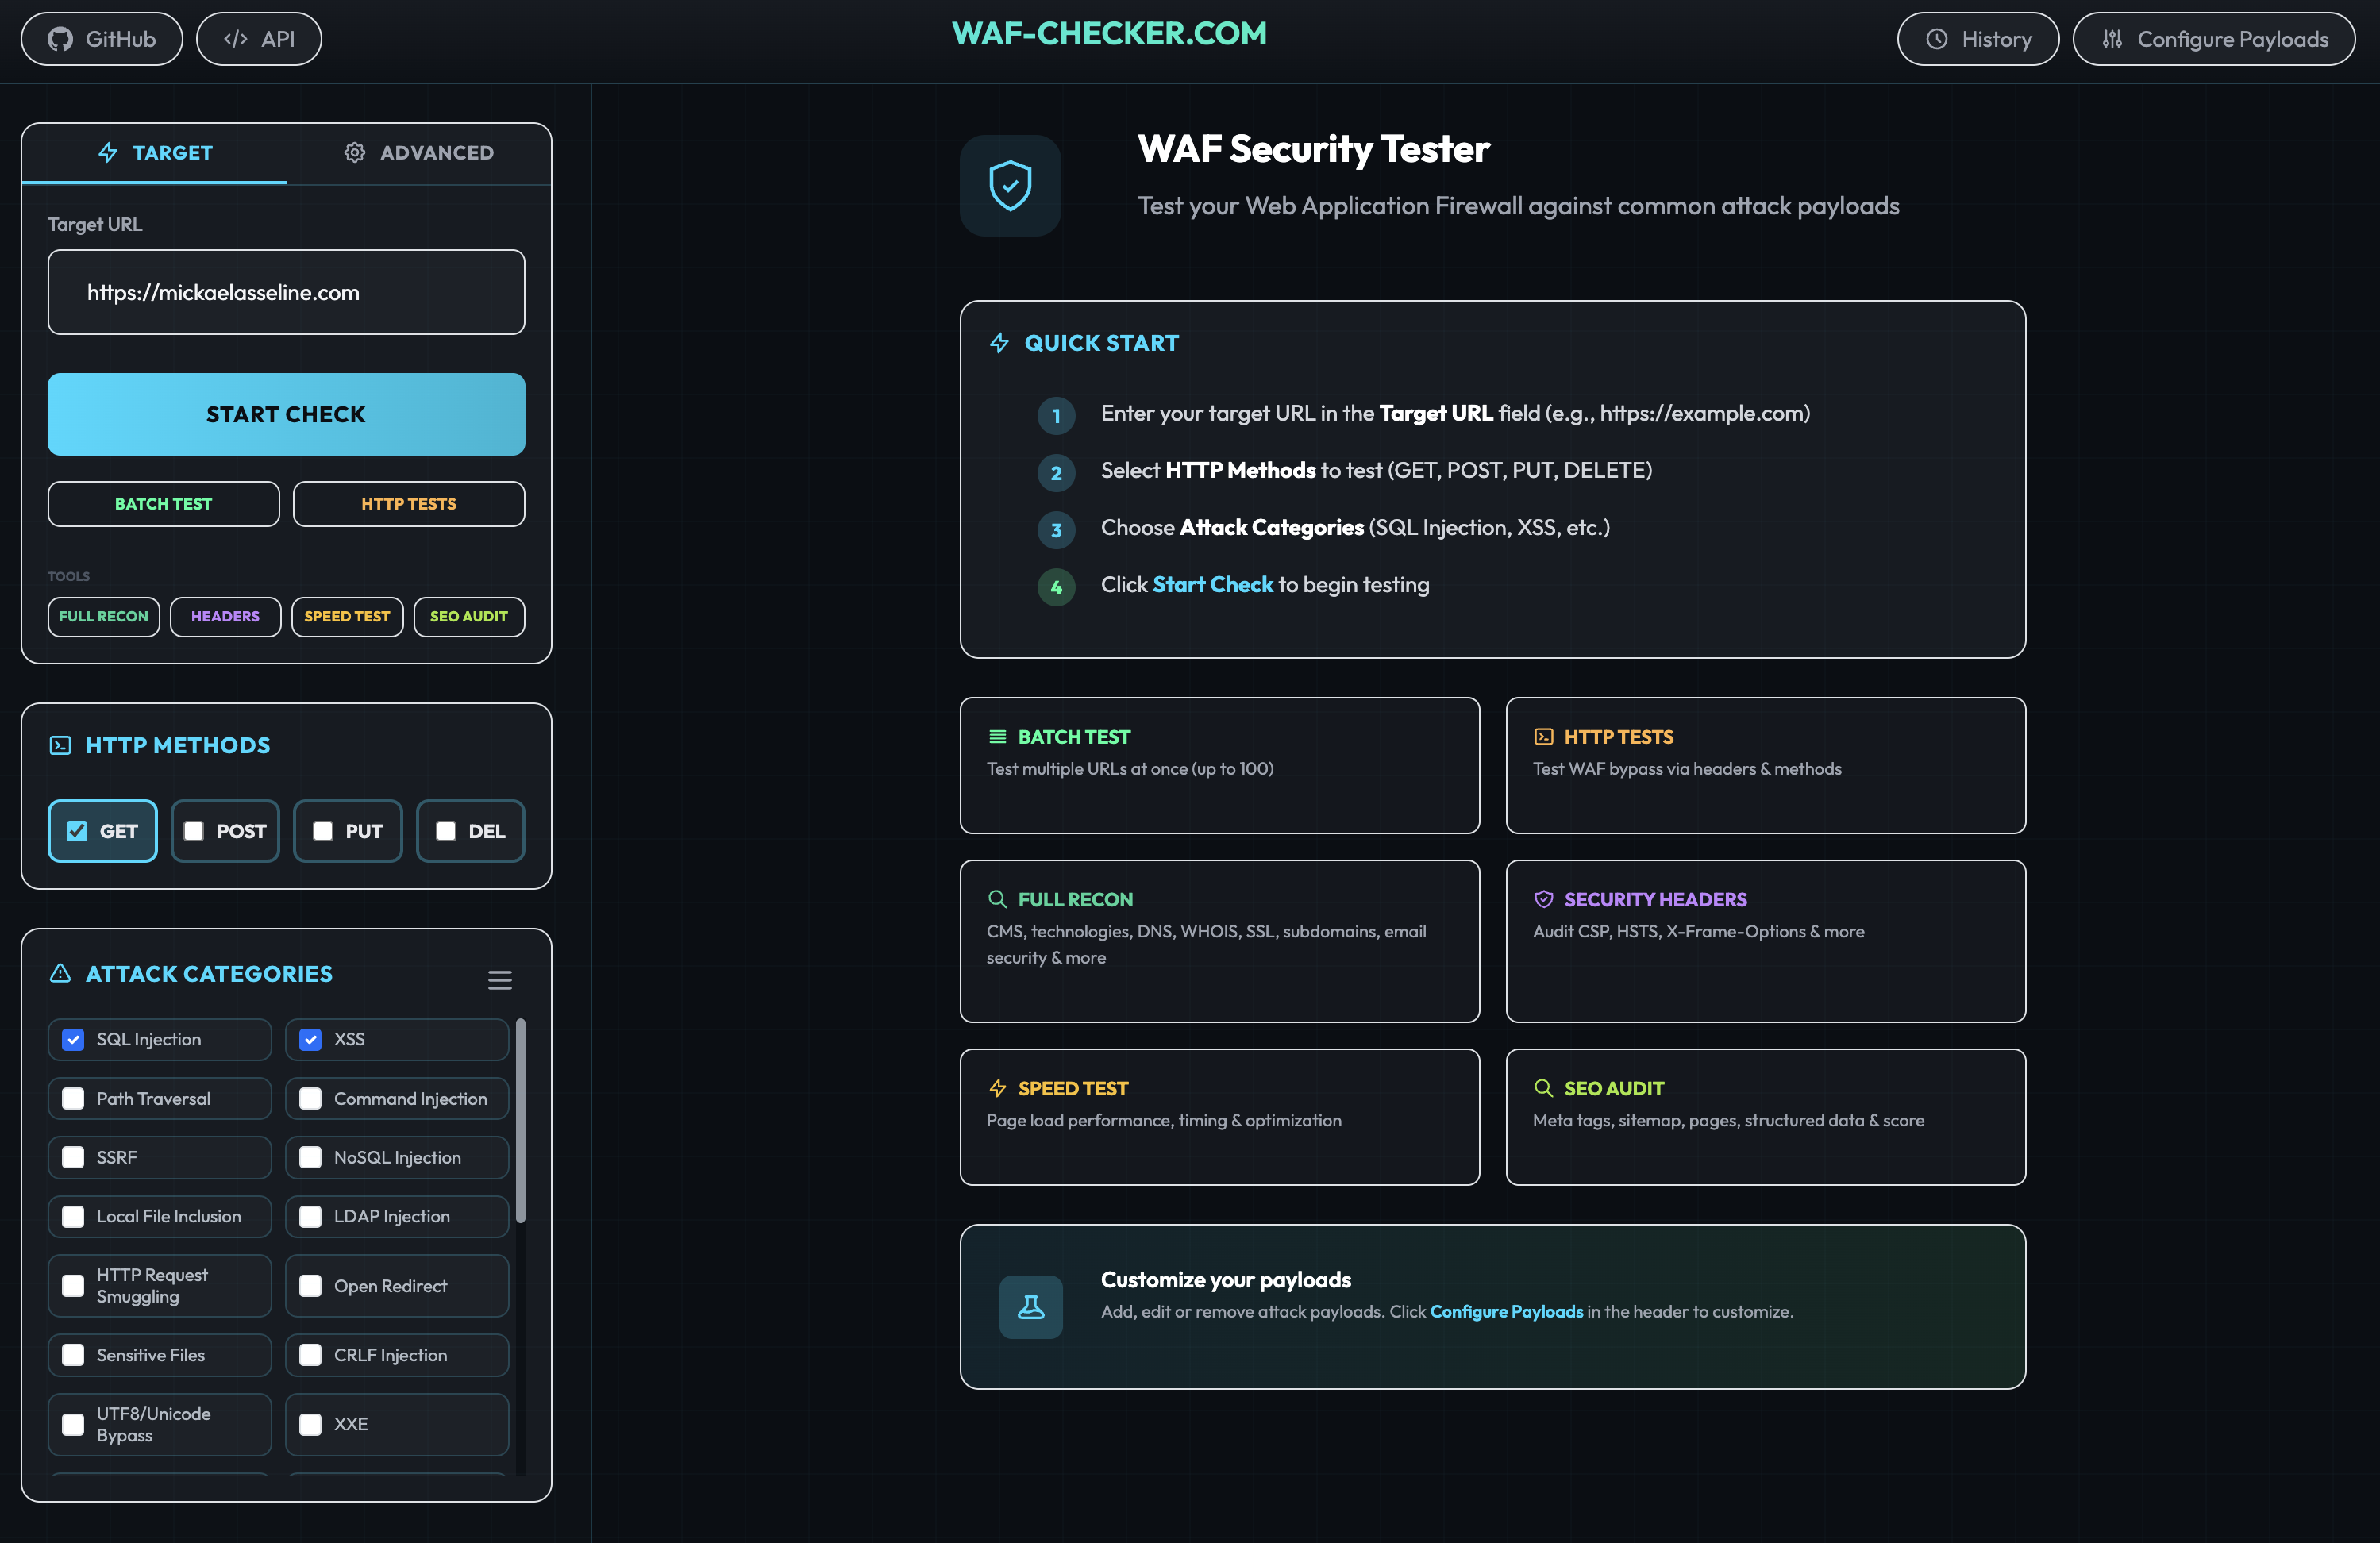 papamica/waf-checker
Tests your WAF with +160 payloads
 elastic/agent-skills
Official Elastic Skills
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
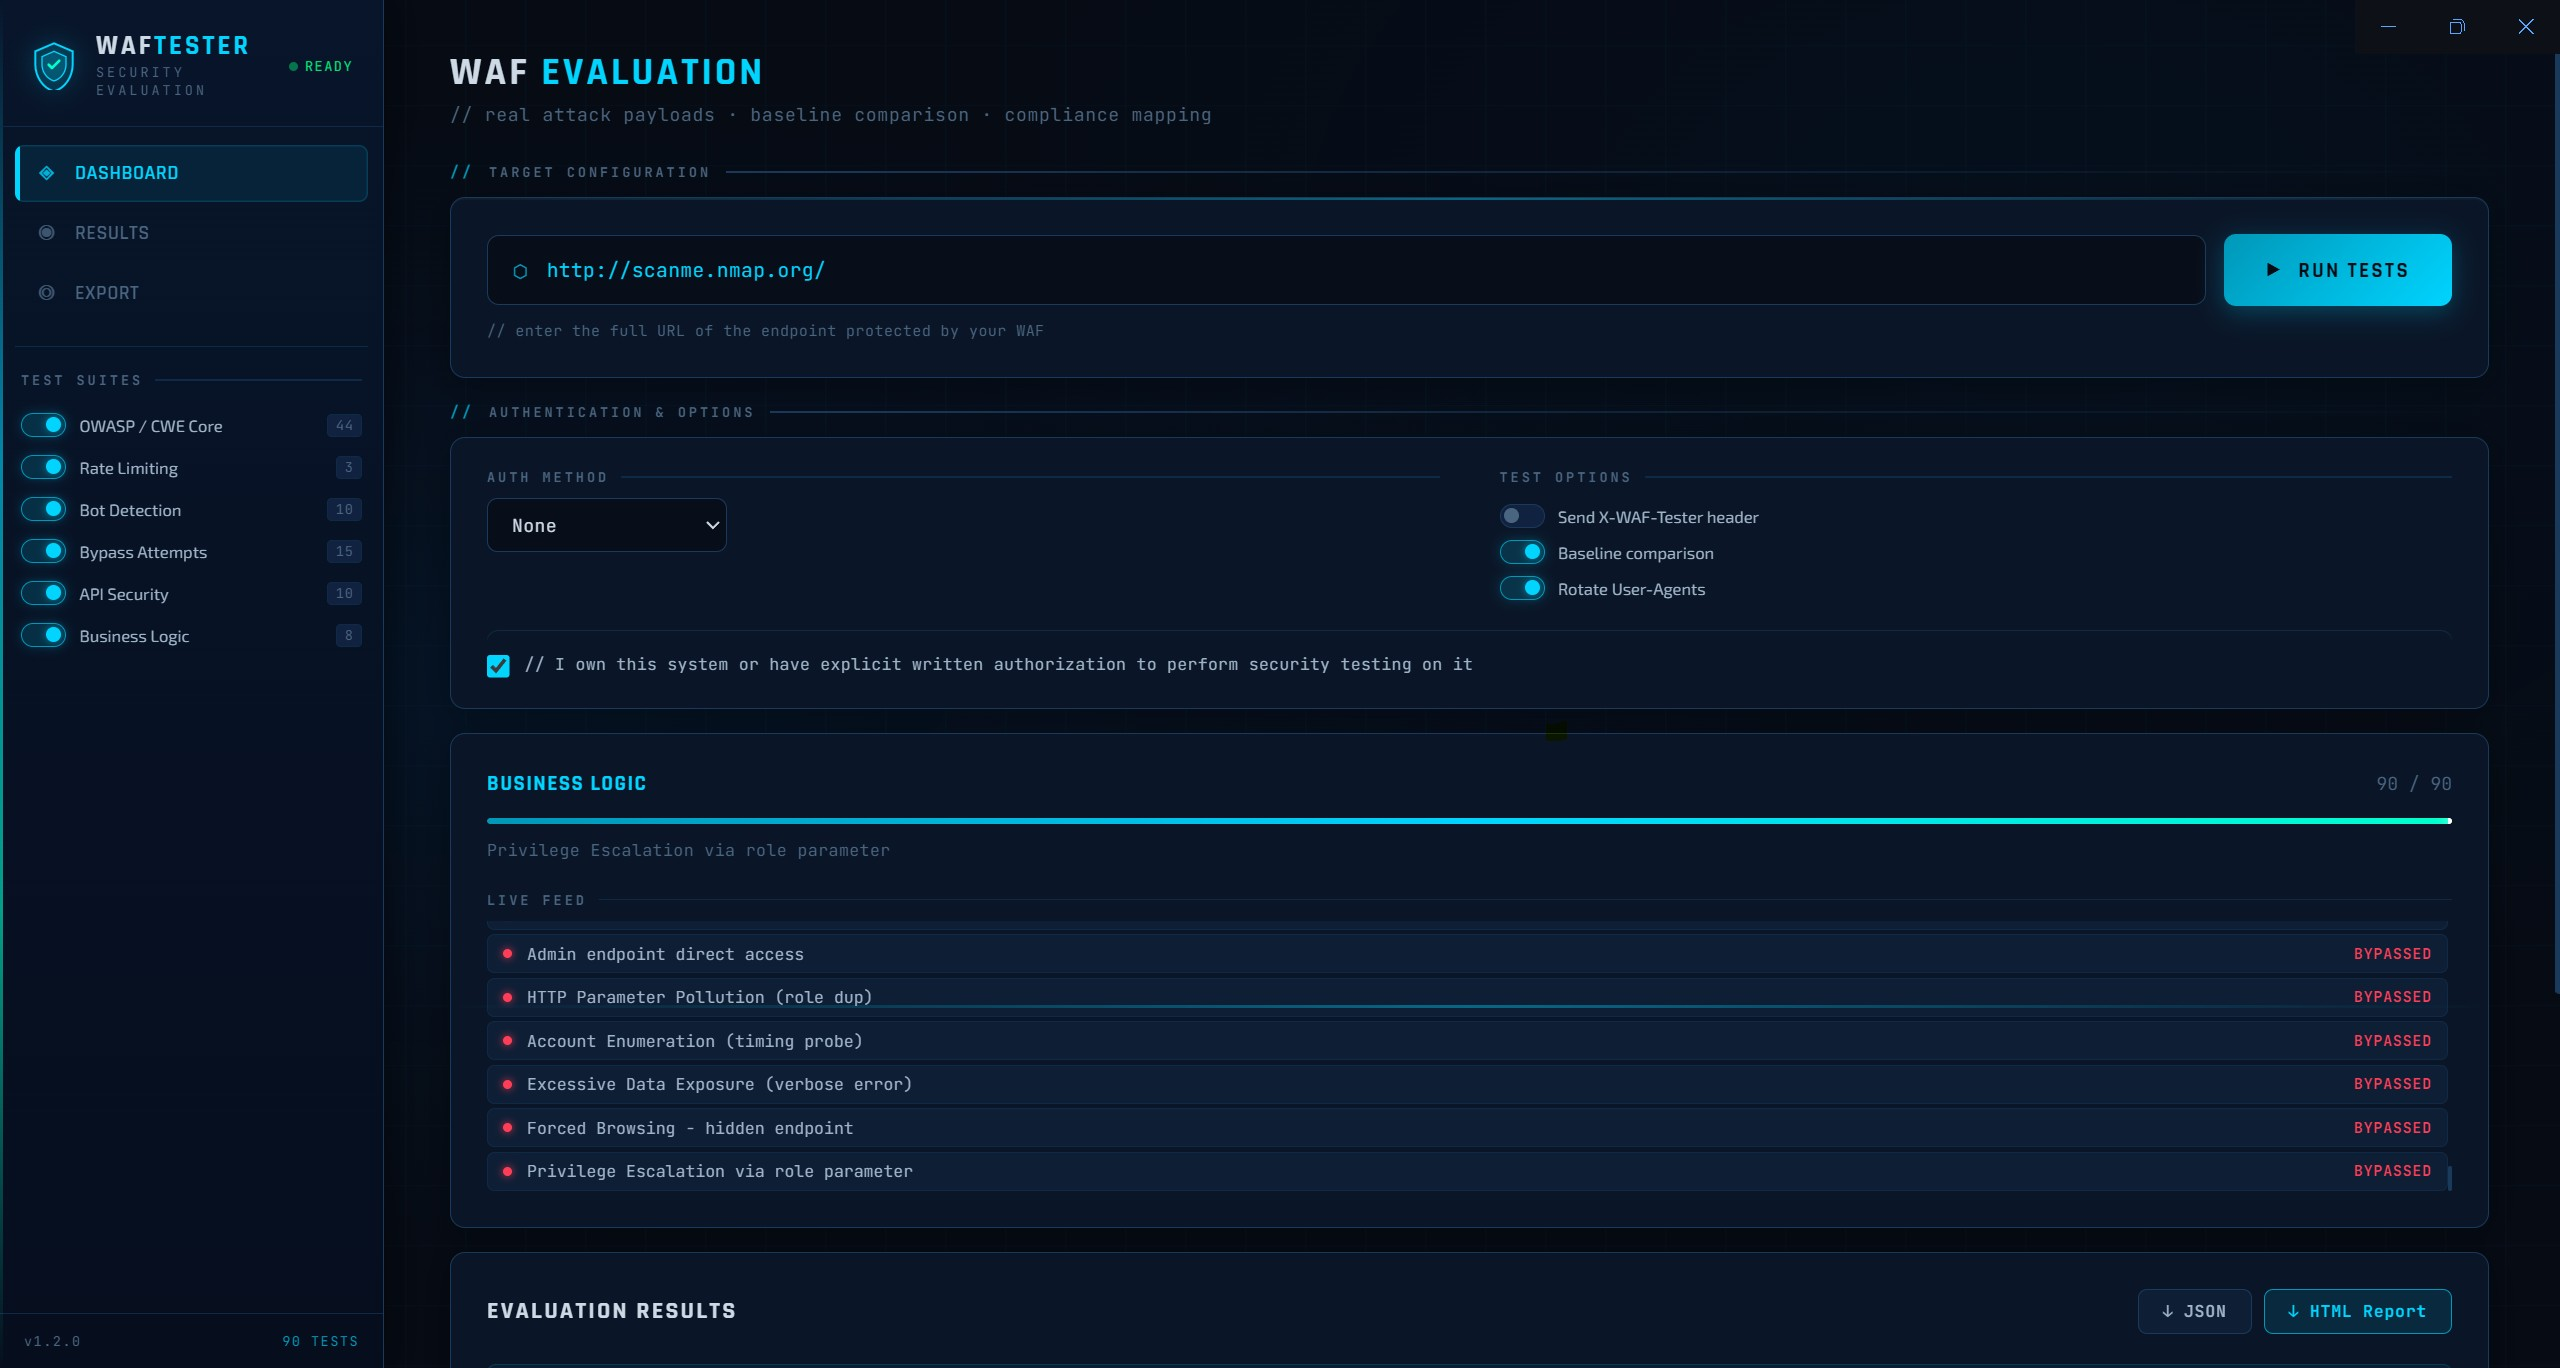 kpomin57/waf-tester
A program for testing WAF functionality
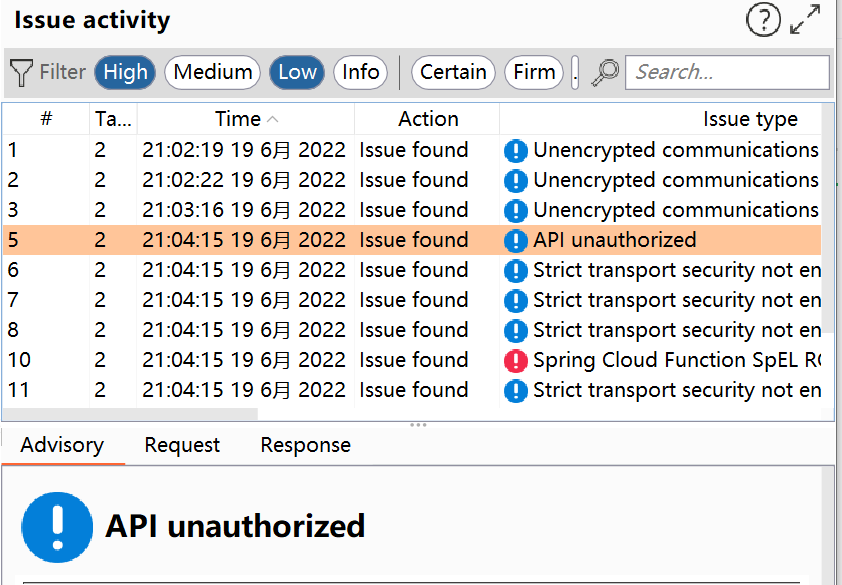 tpt11fb/springvulscan
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
 logisek/huntcyberark
CyberArk Security Audit
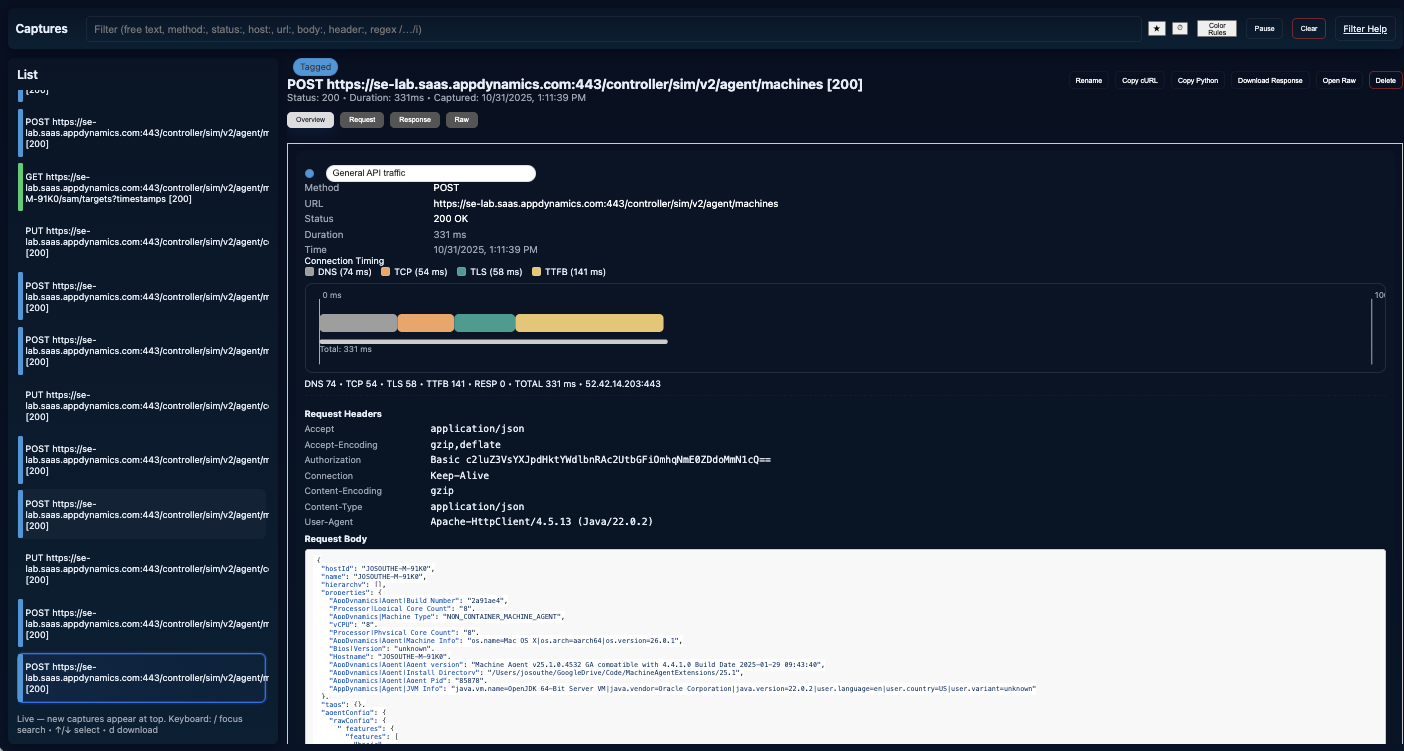 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication