
Burp_Collector
 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
api-security-testinginformation-gatheringpenetration-testing+4
10
sajibuu/burp_collectorA Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 razureink/arisu
Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…
 c1ph3rx13/cve-2023-42442
CVE-2023-42442 JumpServer Session 录像任意下载漏洞
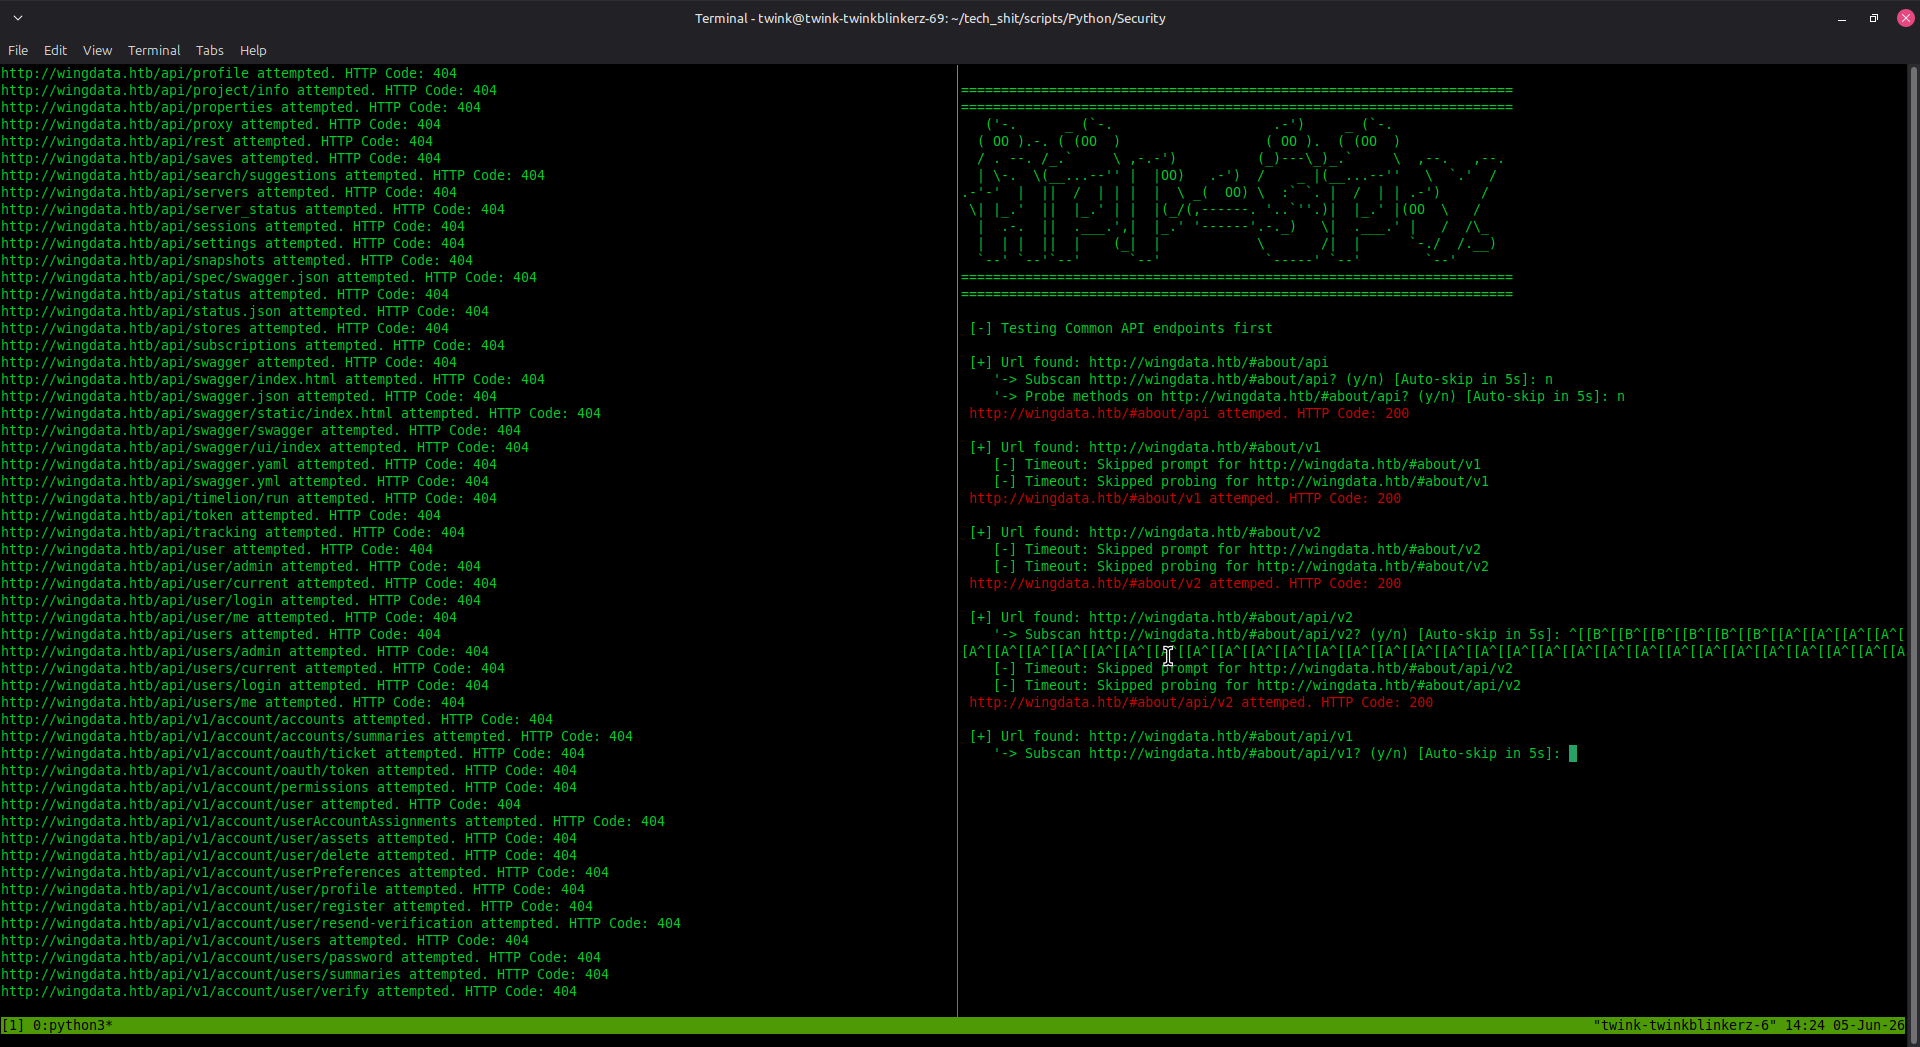 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
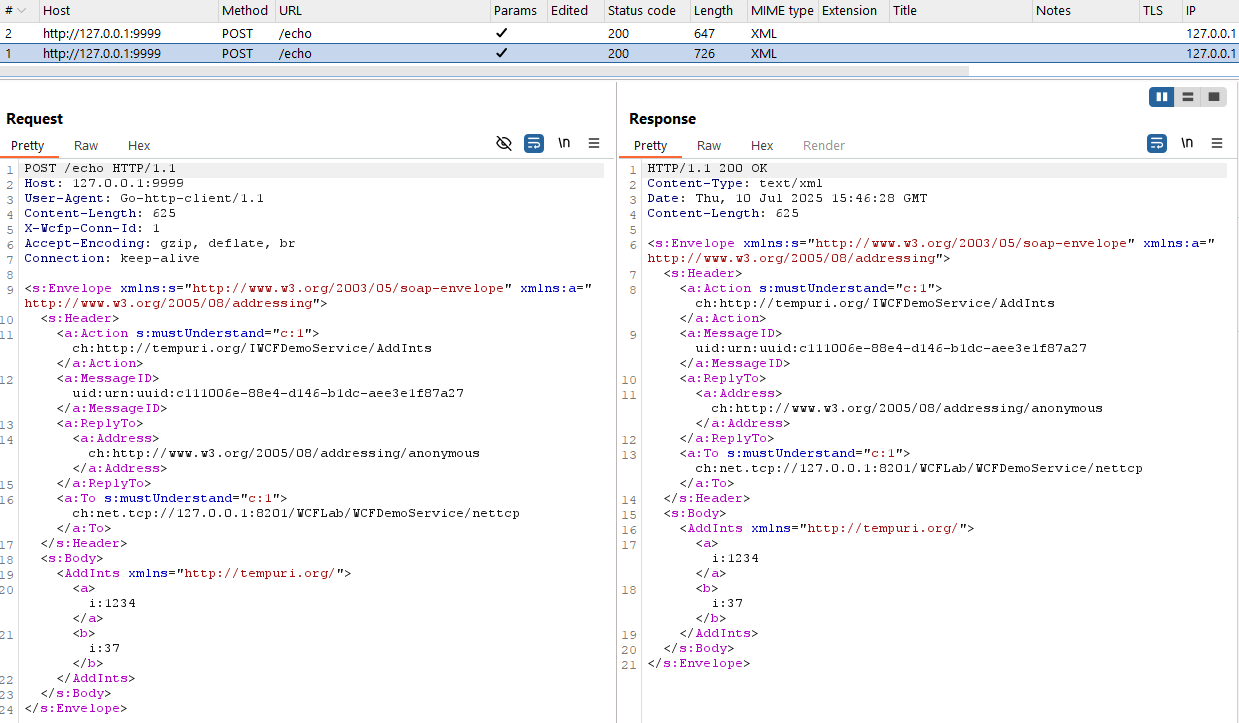 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 t0xodile-swig/http3-adapter
Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…
 ebrasha/abdal-cve-2026-63030
Abdal CVE-2026-63030 is a professional WordPress vulnerability scanner designed to detect exposure to CVE-2026-63030 through version analysis and…
 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…
 null200ok/cve-2026-27944
CVE-2026-27944 - Nginx UI Unauthenticated Backup Download & Decryption
 oscerd/cve-2026-46587
Reproducer for CVE-2026-46587: Apache Camel camel-couchbase CCB_* header injection enabling document disclosure, tampering, and TTL-forced data…
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 nel-droid/cve-2026-71203-poc
PoC: changedetection.io unauthenticated OpenAPI schema disclosure (CVE-2026-71203, Medium 5.3)
 saboor-hakimi/cve-2023-23752
CVE-2023-23752 nuclei template
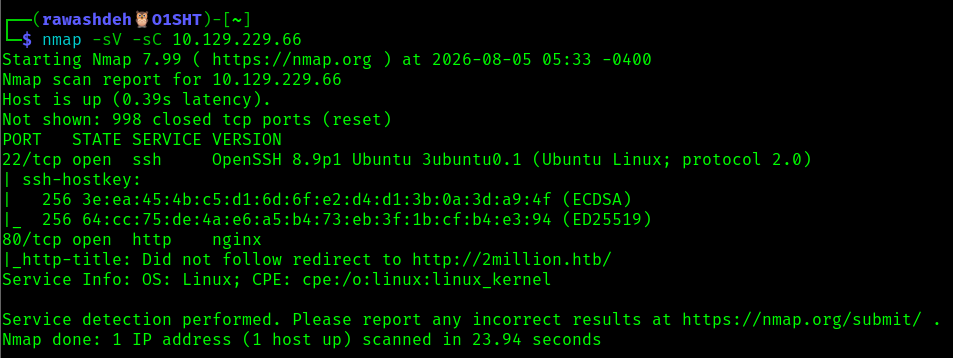 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 fopje/cve-2022-36539
Insecure Permissions WeDayCare