
Pegasus-Pentest-Arsenal
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
api-security-testingctfeducation+9
58
sobri3195/pegasus-pentest-arsenalA comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
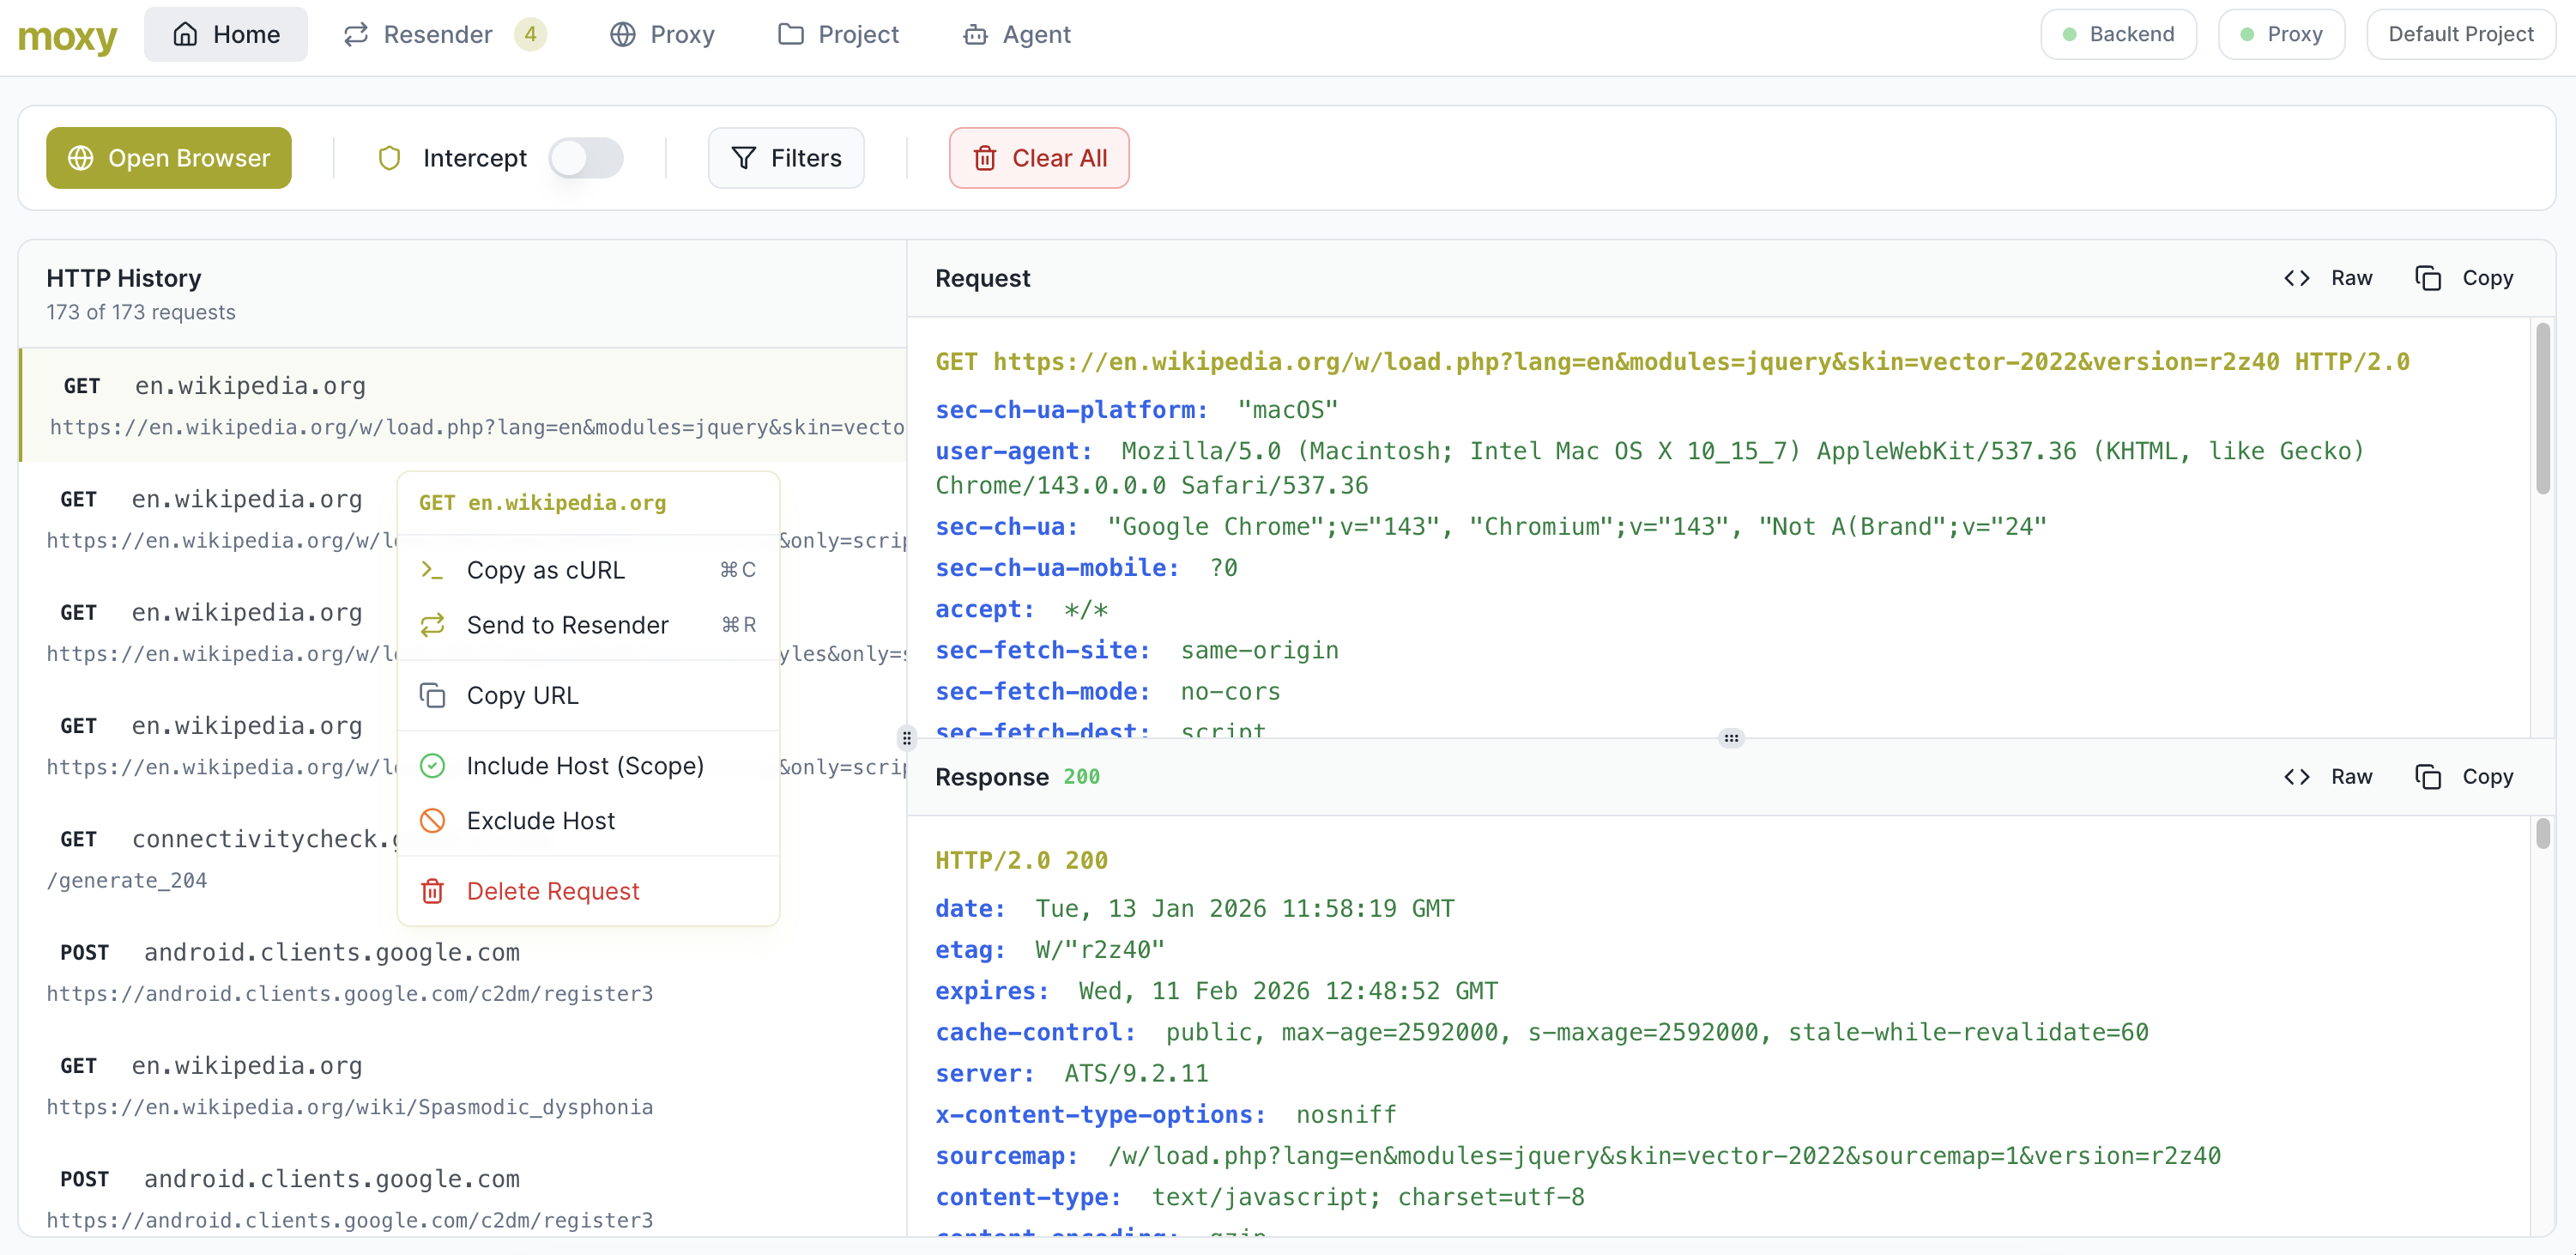 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
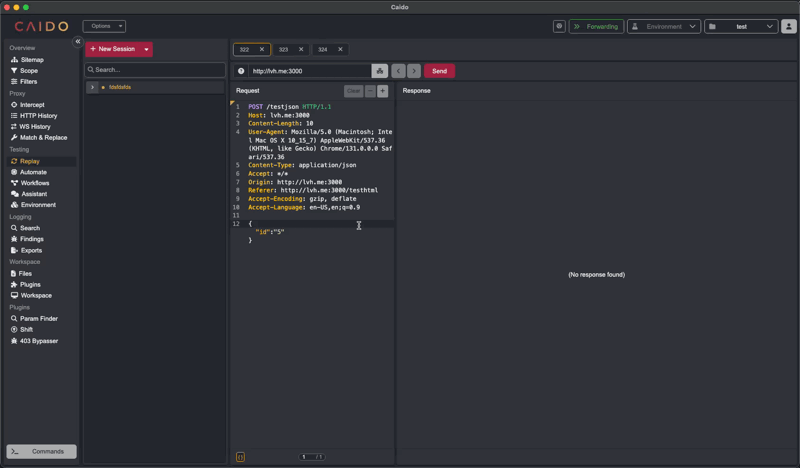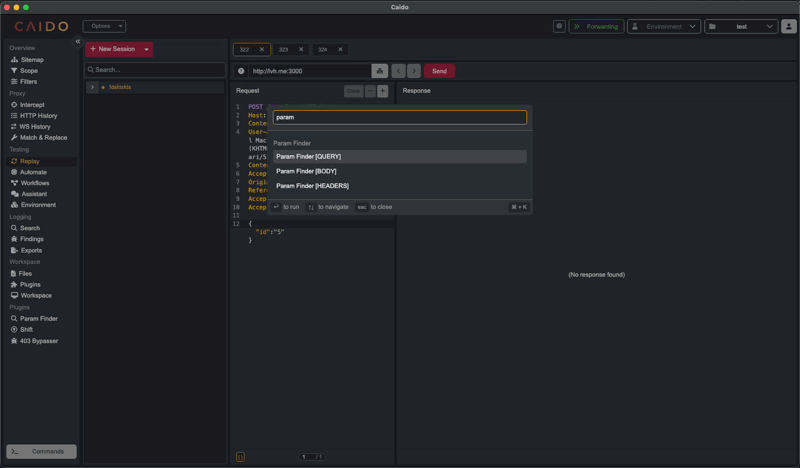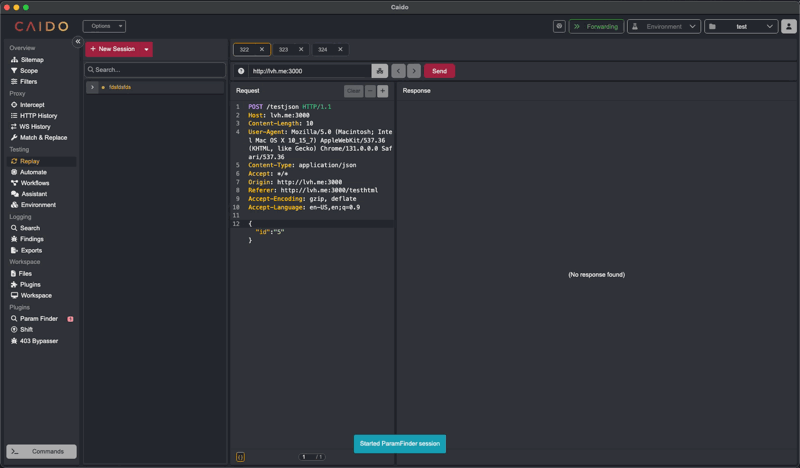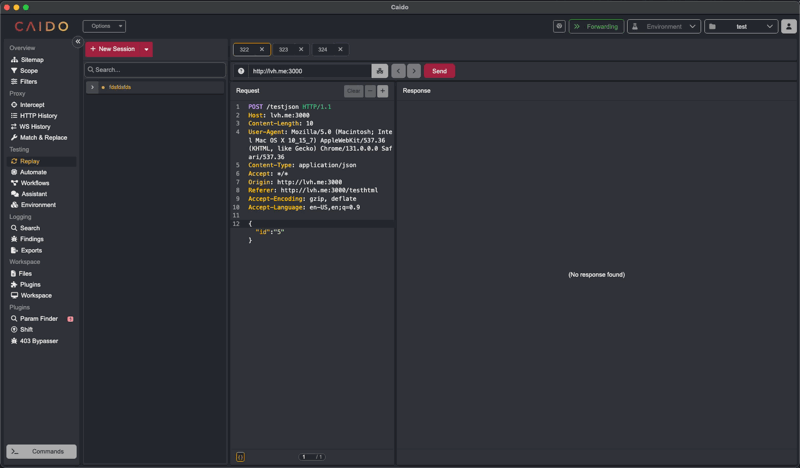 caido-community/paramfinder
Discover hidden parameters in Caido
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
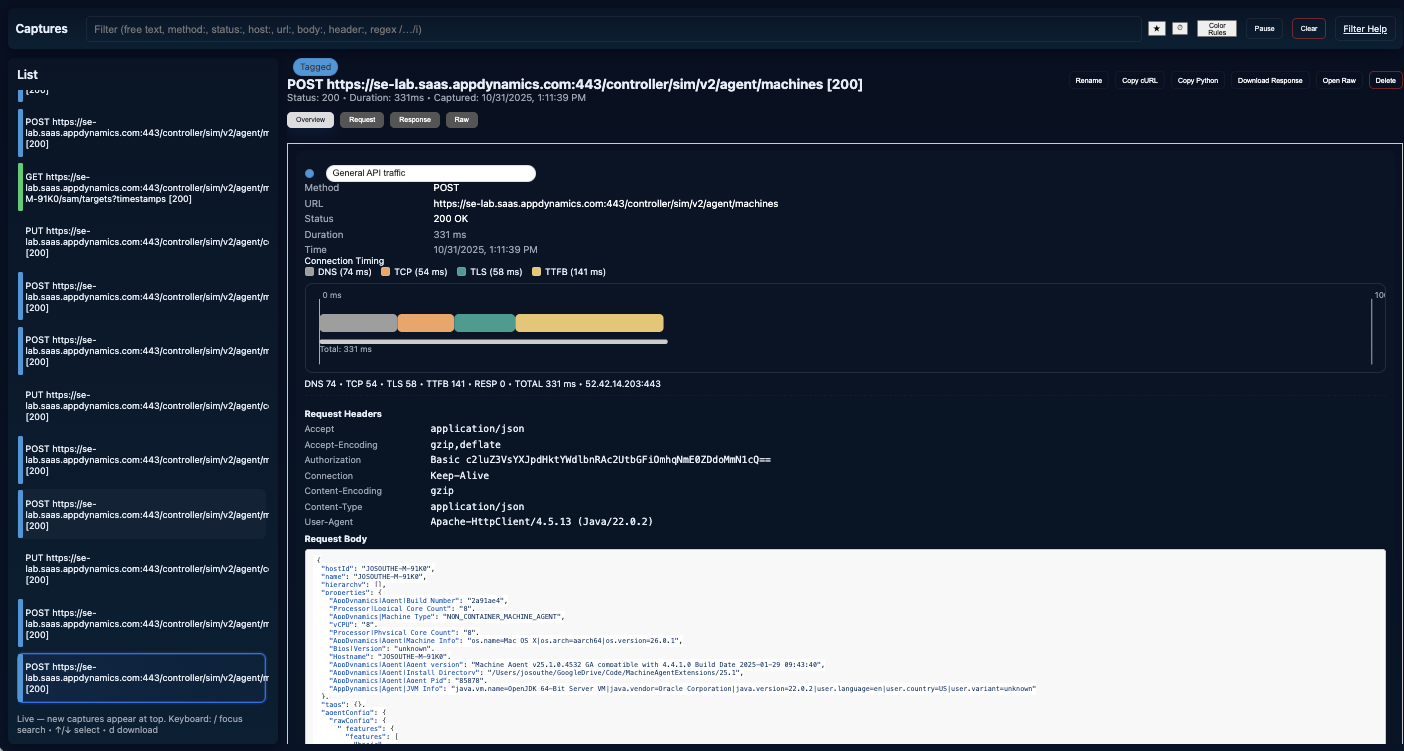 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
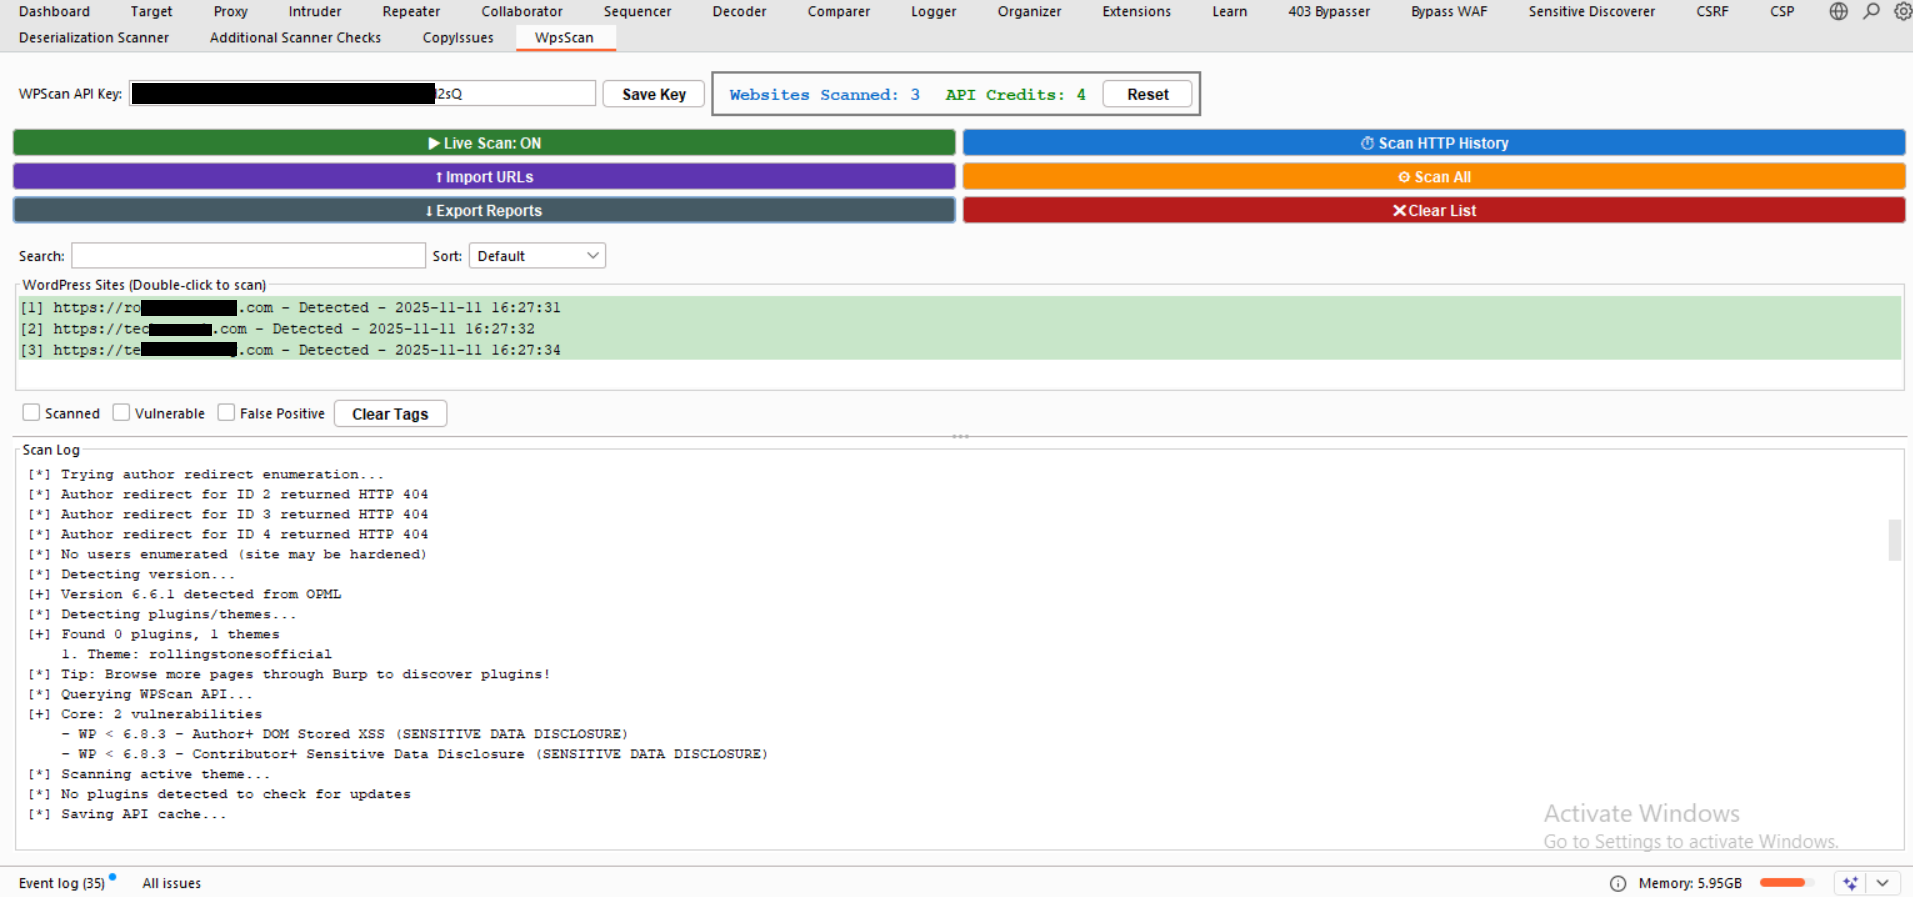 teycir/burpwpsscan
Burp extension for wordpress security scanning
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
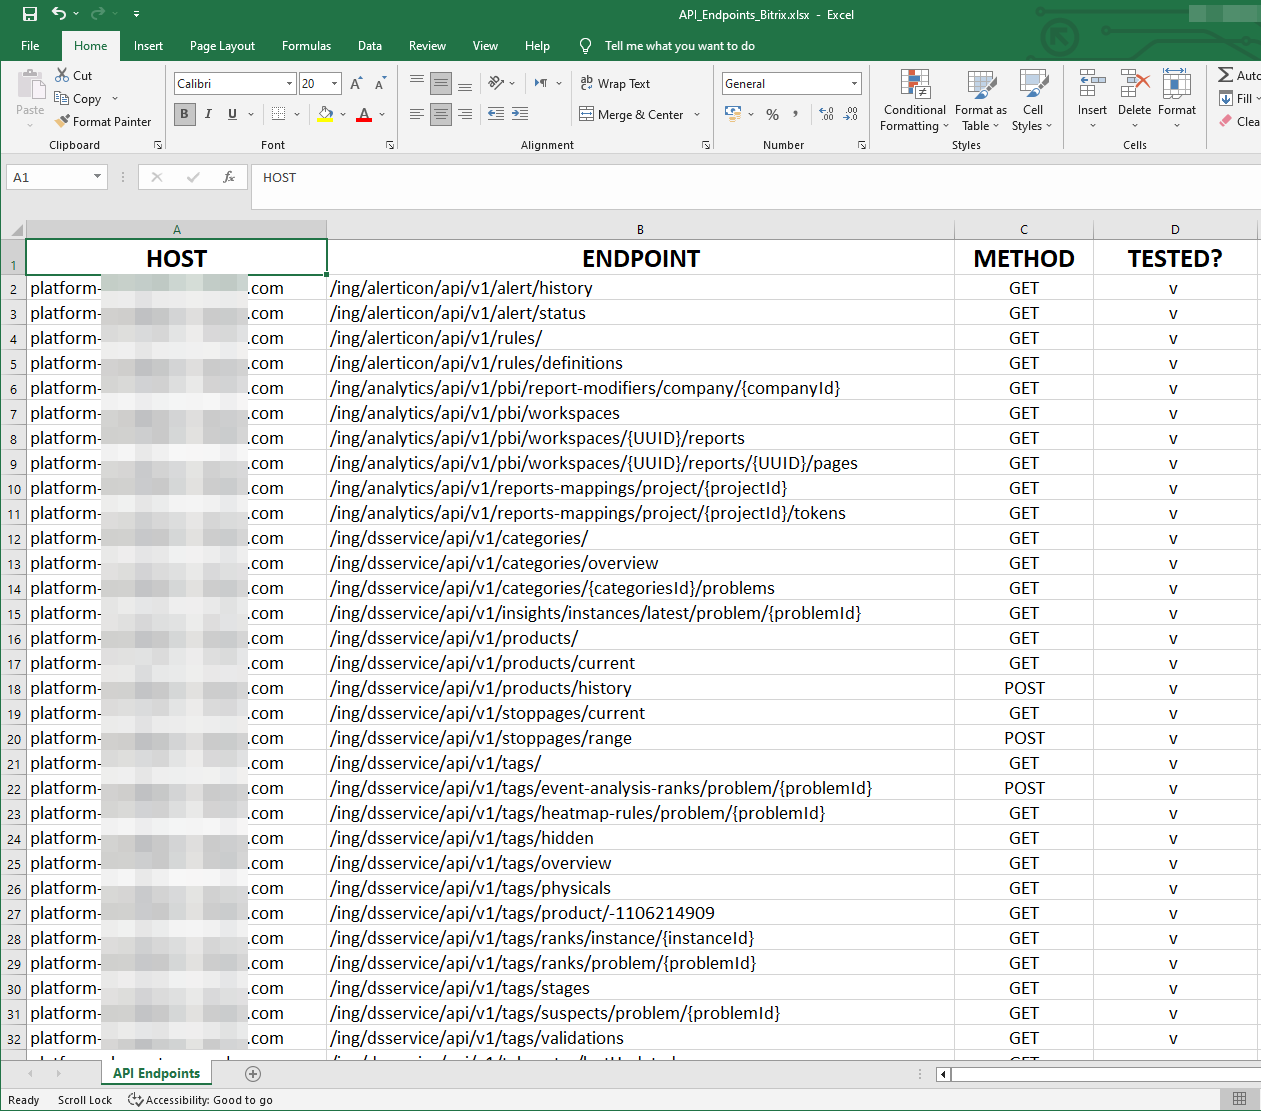 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 hunt-benito/your-bot-my-inbox-cve-2026-68929-fastgpt-unauthenticated-wechat-channel-hijack
Proof-of-concept exploit for CVE-2026-68929, demonstrating unauthenticated cross-tenant takeover of FastGPT WeChat channels via public shareId,…
 c1ph3rx13/cve-2023-42442
CVE-2023-42442 JumpServer Session 录像任意下载漏洞
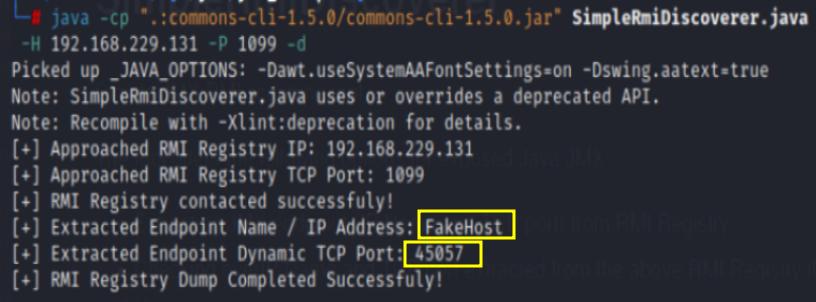 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 null200ok/cve-2026-27944
CVE-2026-27944 - Nginx UI Unauthenticated Backup Download & Decryption
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 nel-droid/cve-2026-71203-poc
PoC: changedetection.io unauthenticated OpenAPI schema disclosure (CVE-2026-71203, Medium 5.3)