
CVE-2026-30944-PoC
Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.

Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…

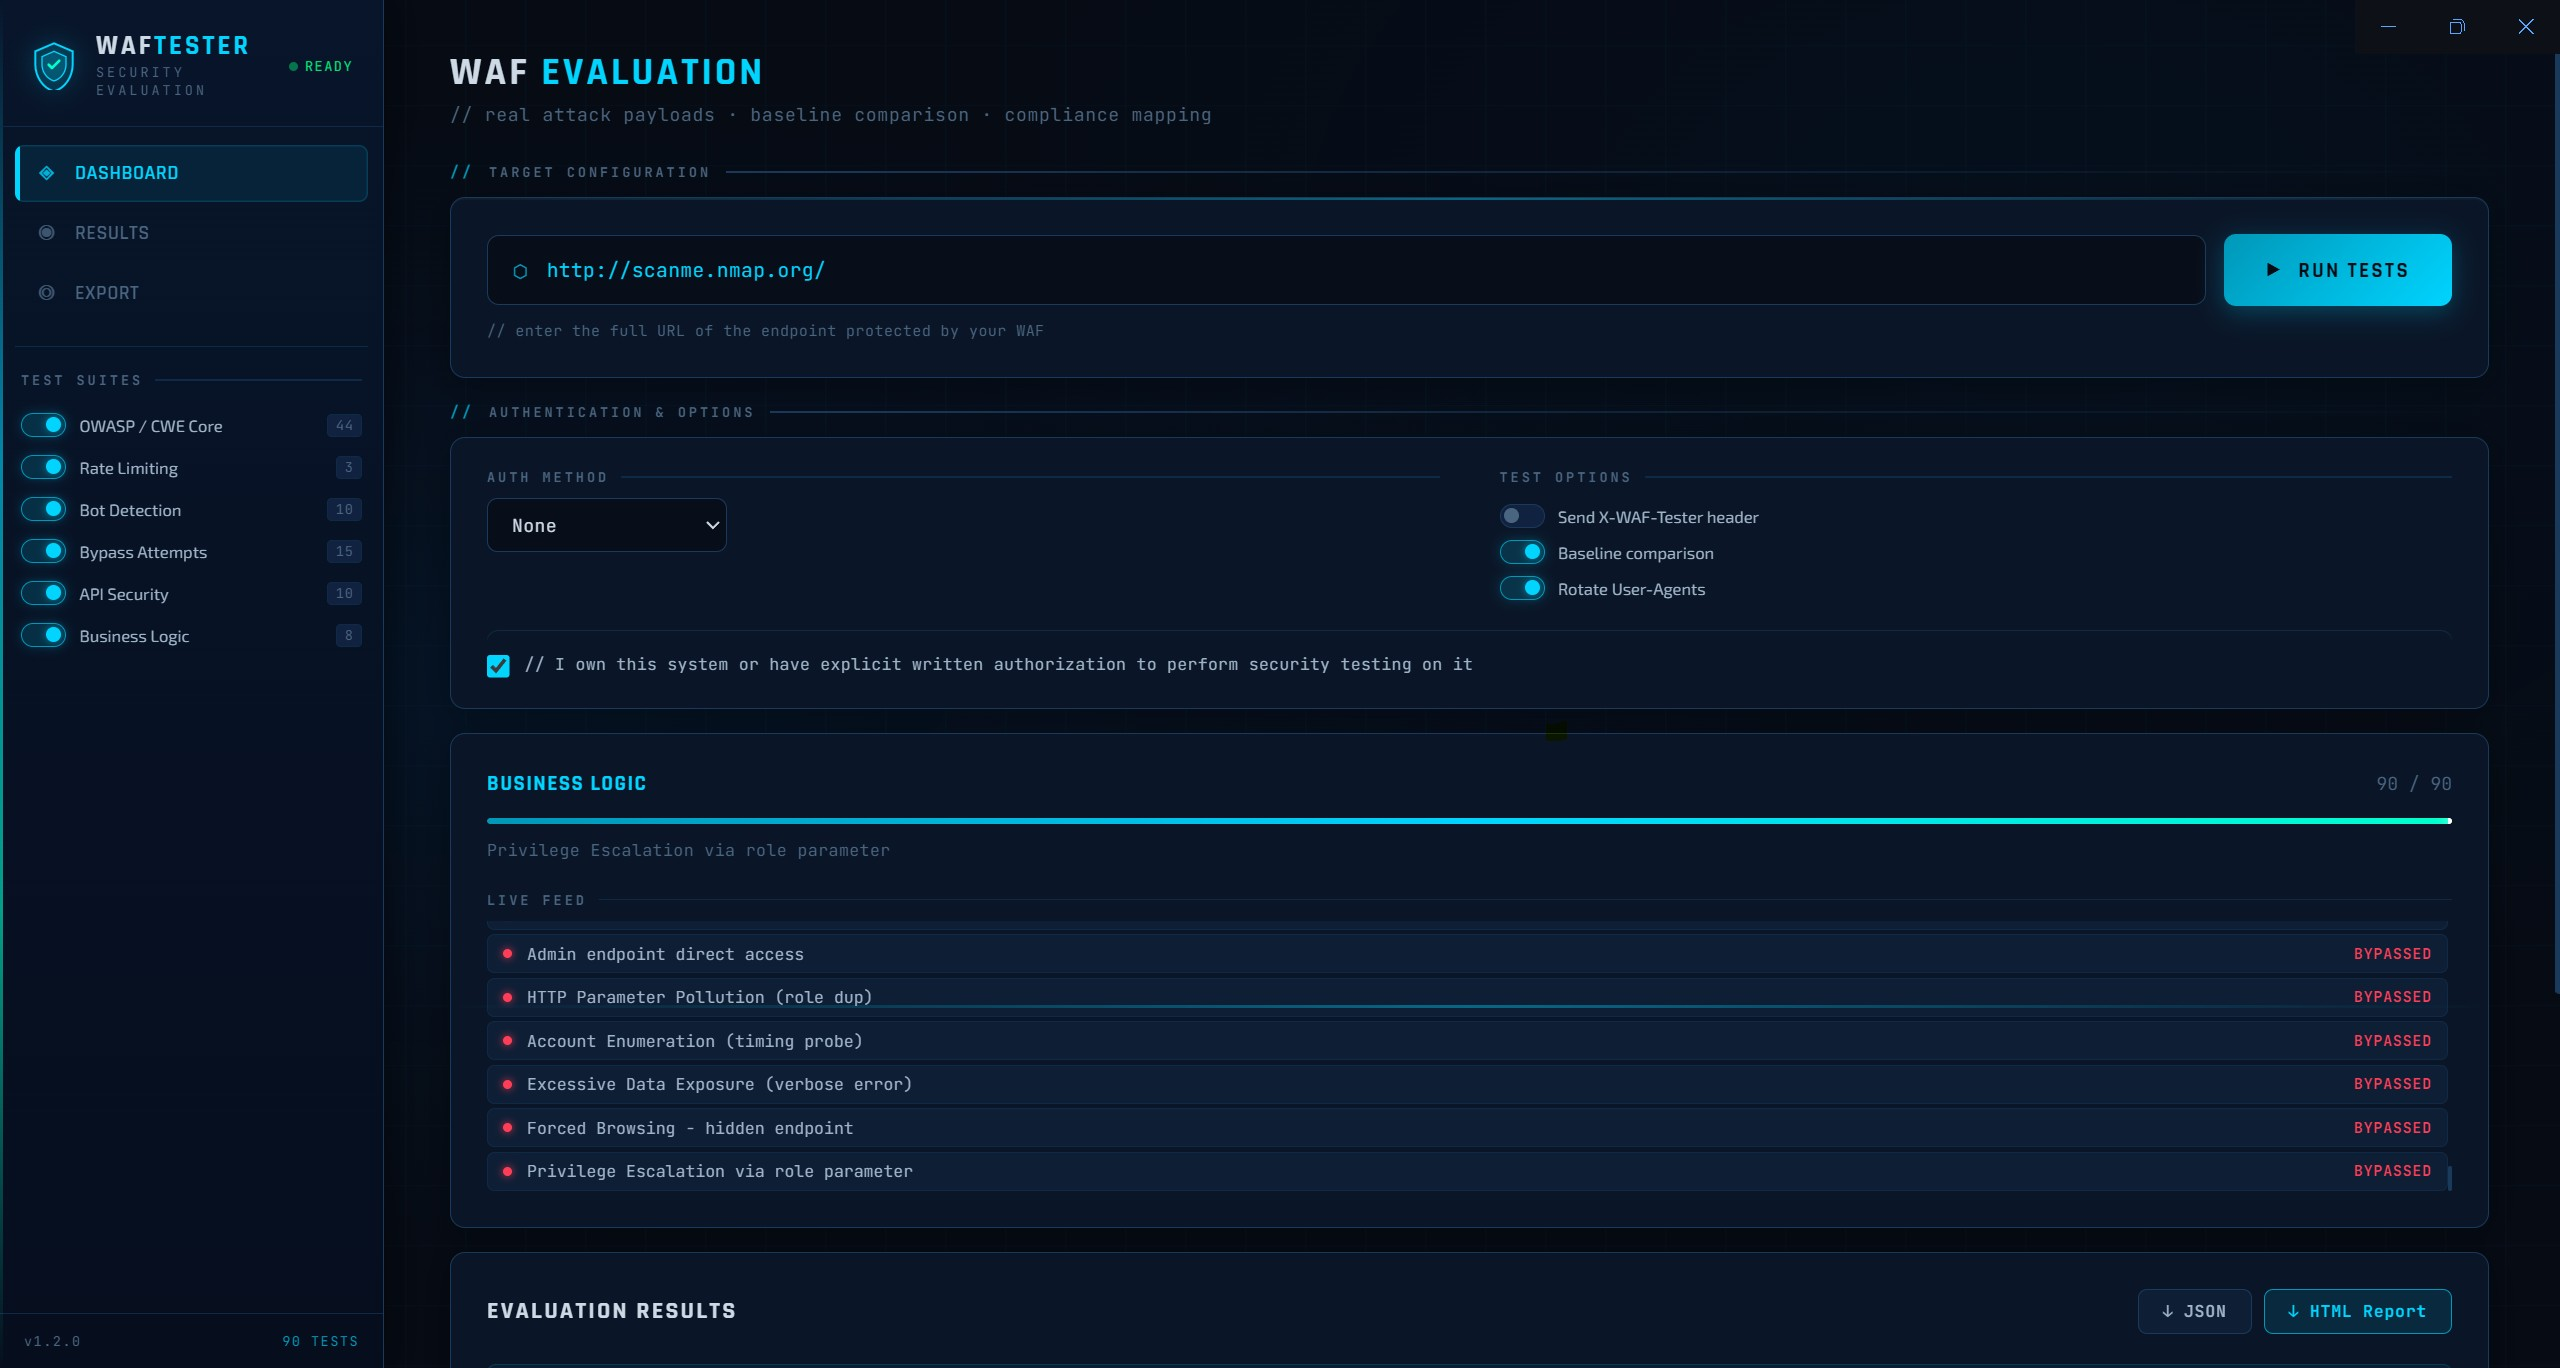
A program for testing WAF functionality

Proof-of-concept exploit for CVE-2023-27532 in Veeam Backup and Replication that abuses an unsecured API endpoint to extract credentials from the…

A Test API for testing the POC against CVE-2022-1388

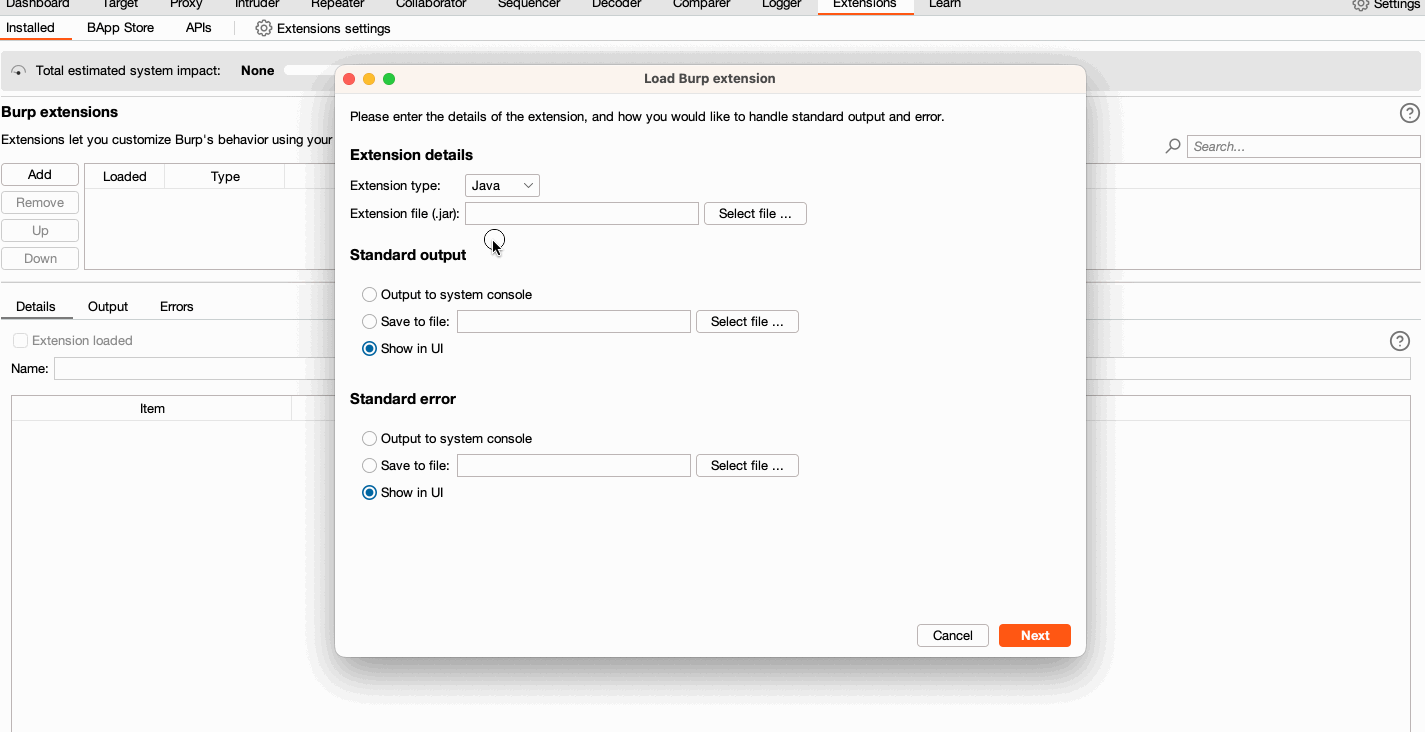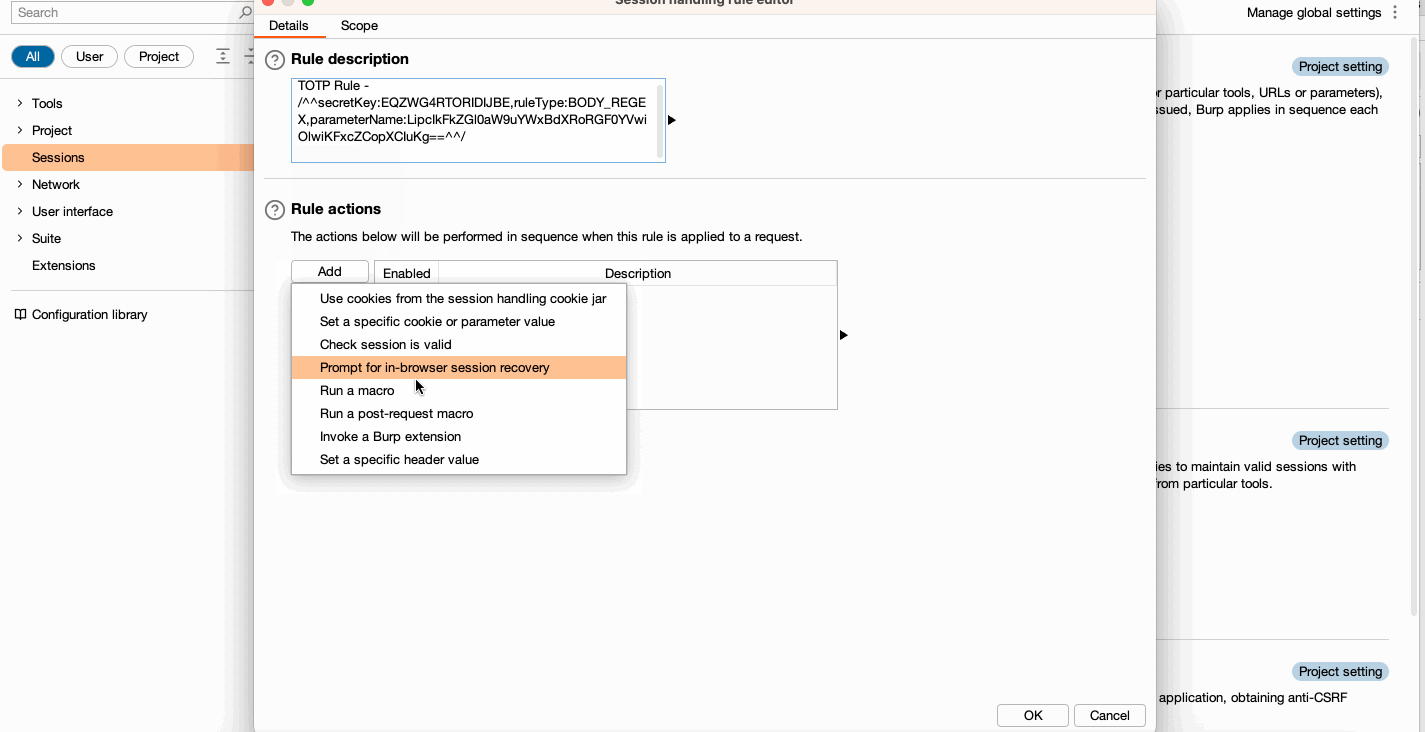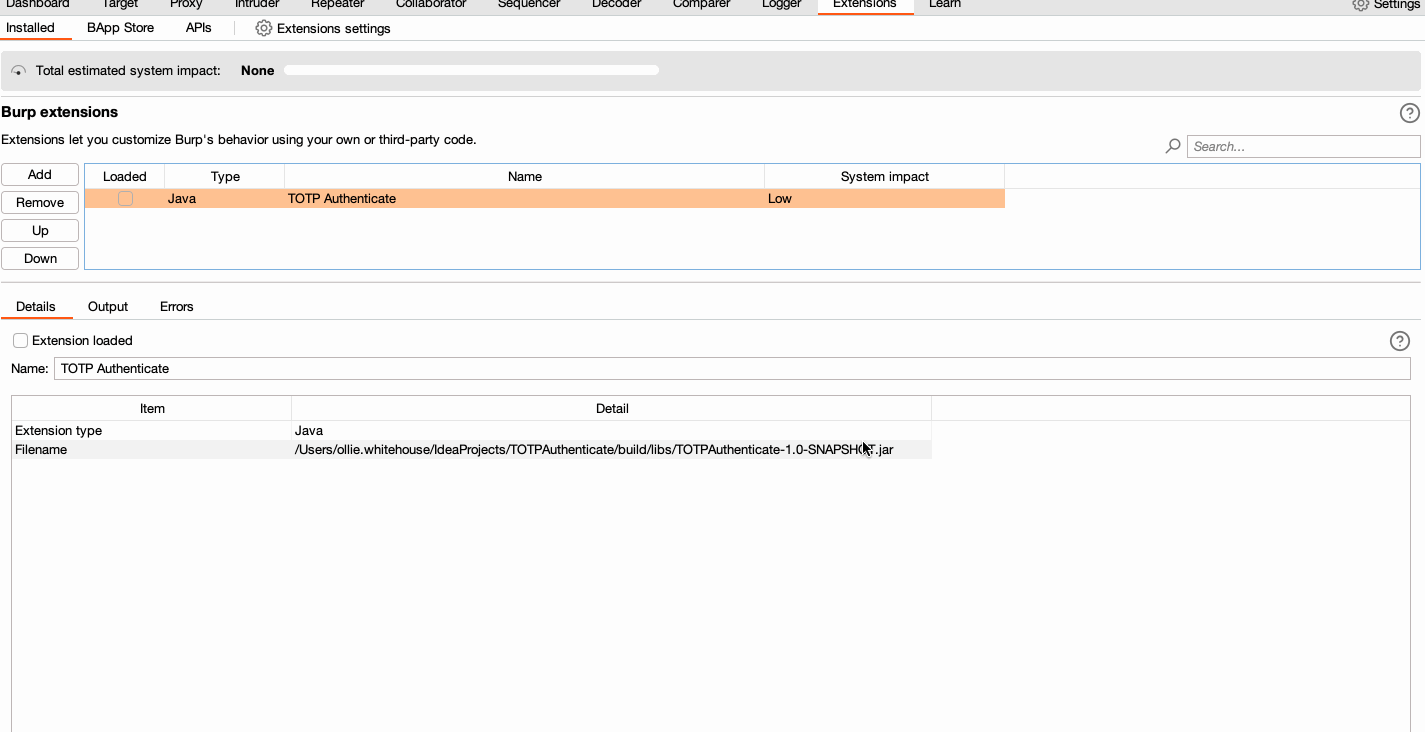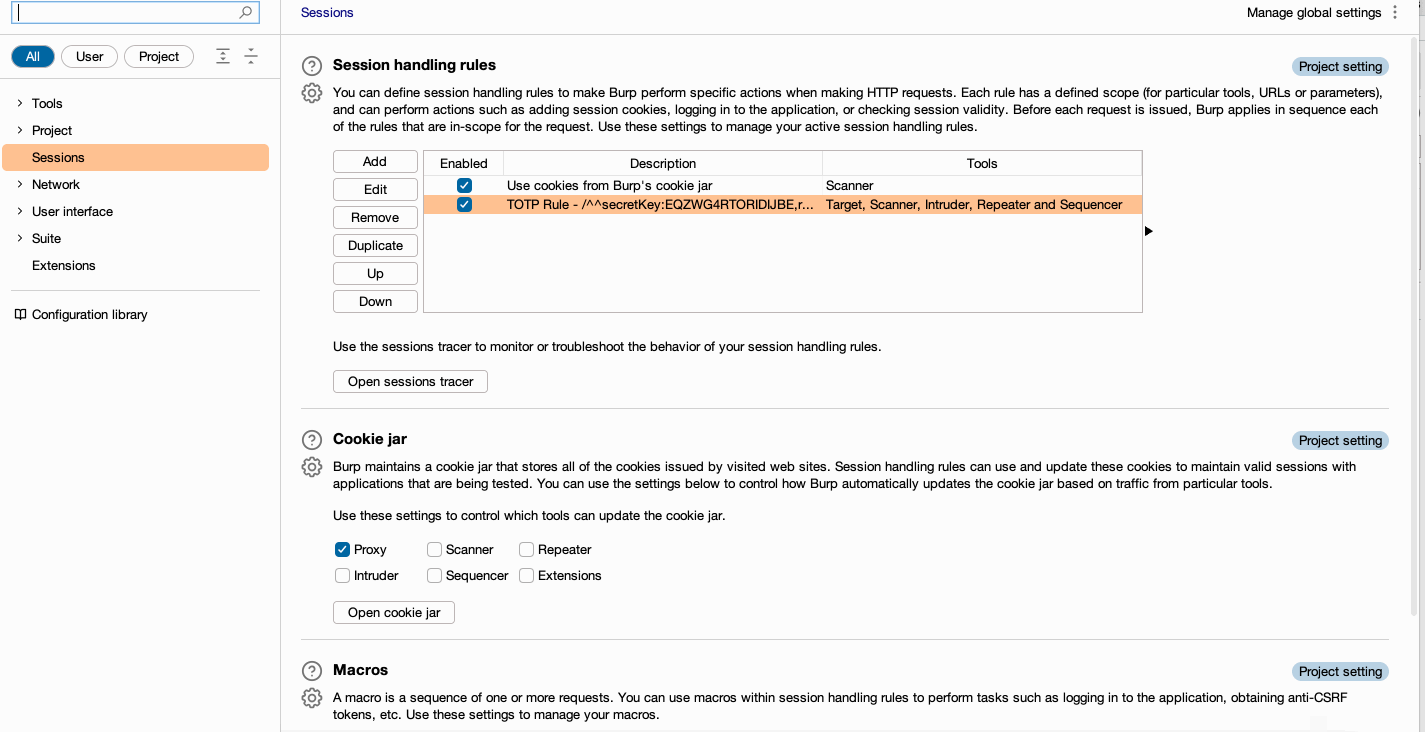
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.

Proof-of-concept exploit for CVE-2026-22014 demonstrating persisted-query ID manipulation in GraphQL APIs to bypass allowlists and execute arbitrary…

Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…

Demonstrates an IDOR vulnerability in TelegAI's chat API allowing unauthorized conversation tampering, leading to phishing and XSS-based account…

Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.

Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.

Automated authorization security scanner for OpenAPI-based APIs. Tests GET endpoints with multiple credential sets to detect privilege escalation and…

Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…

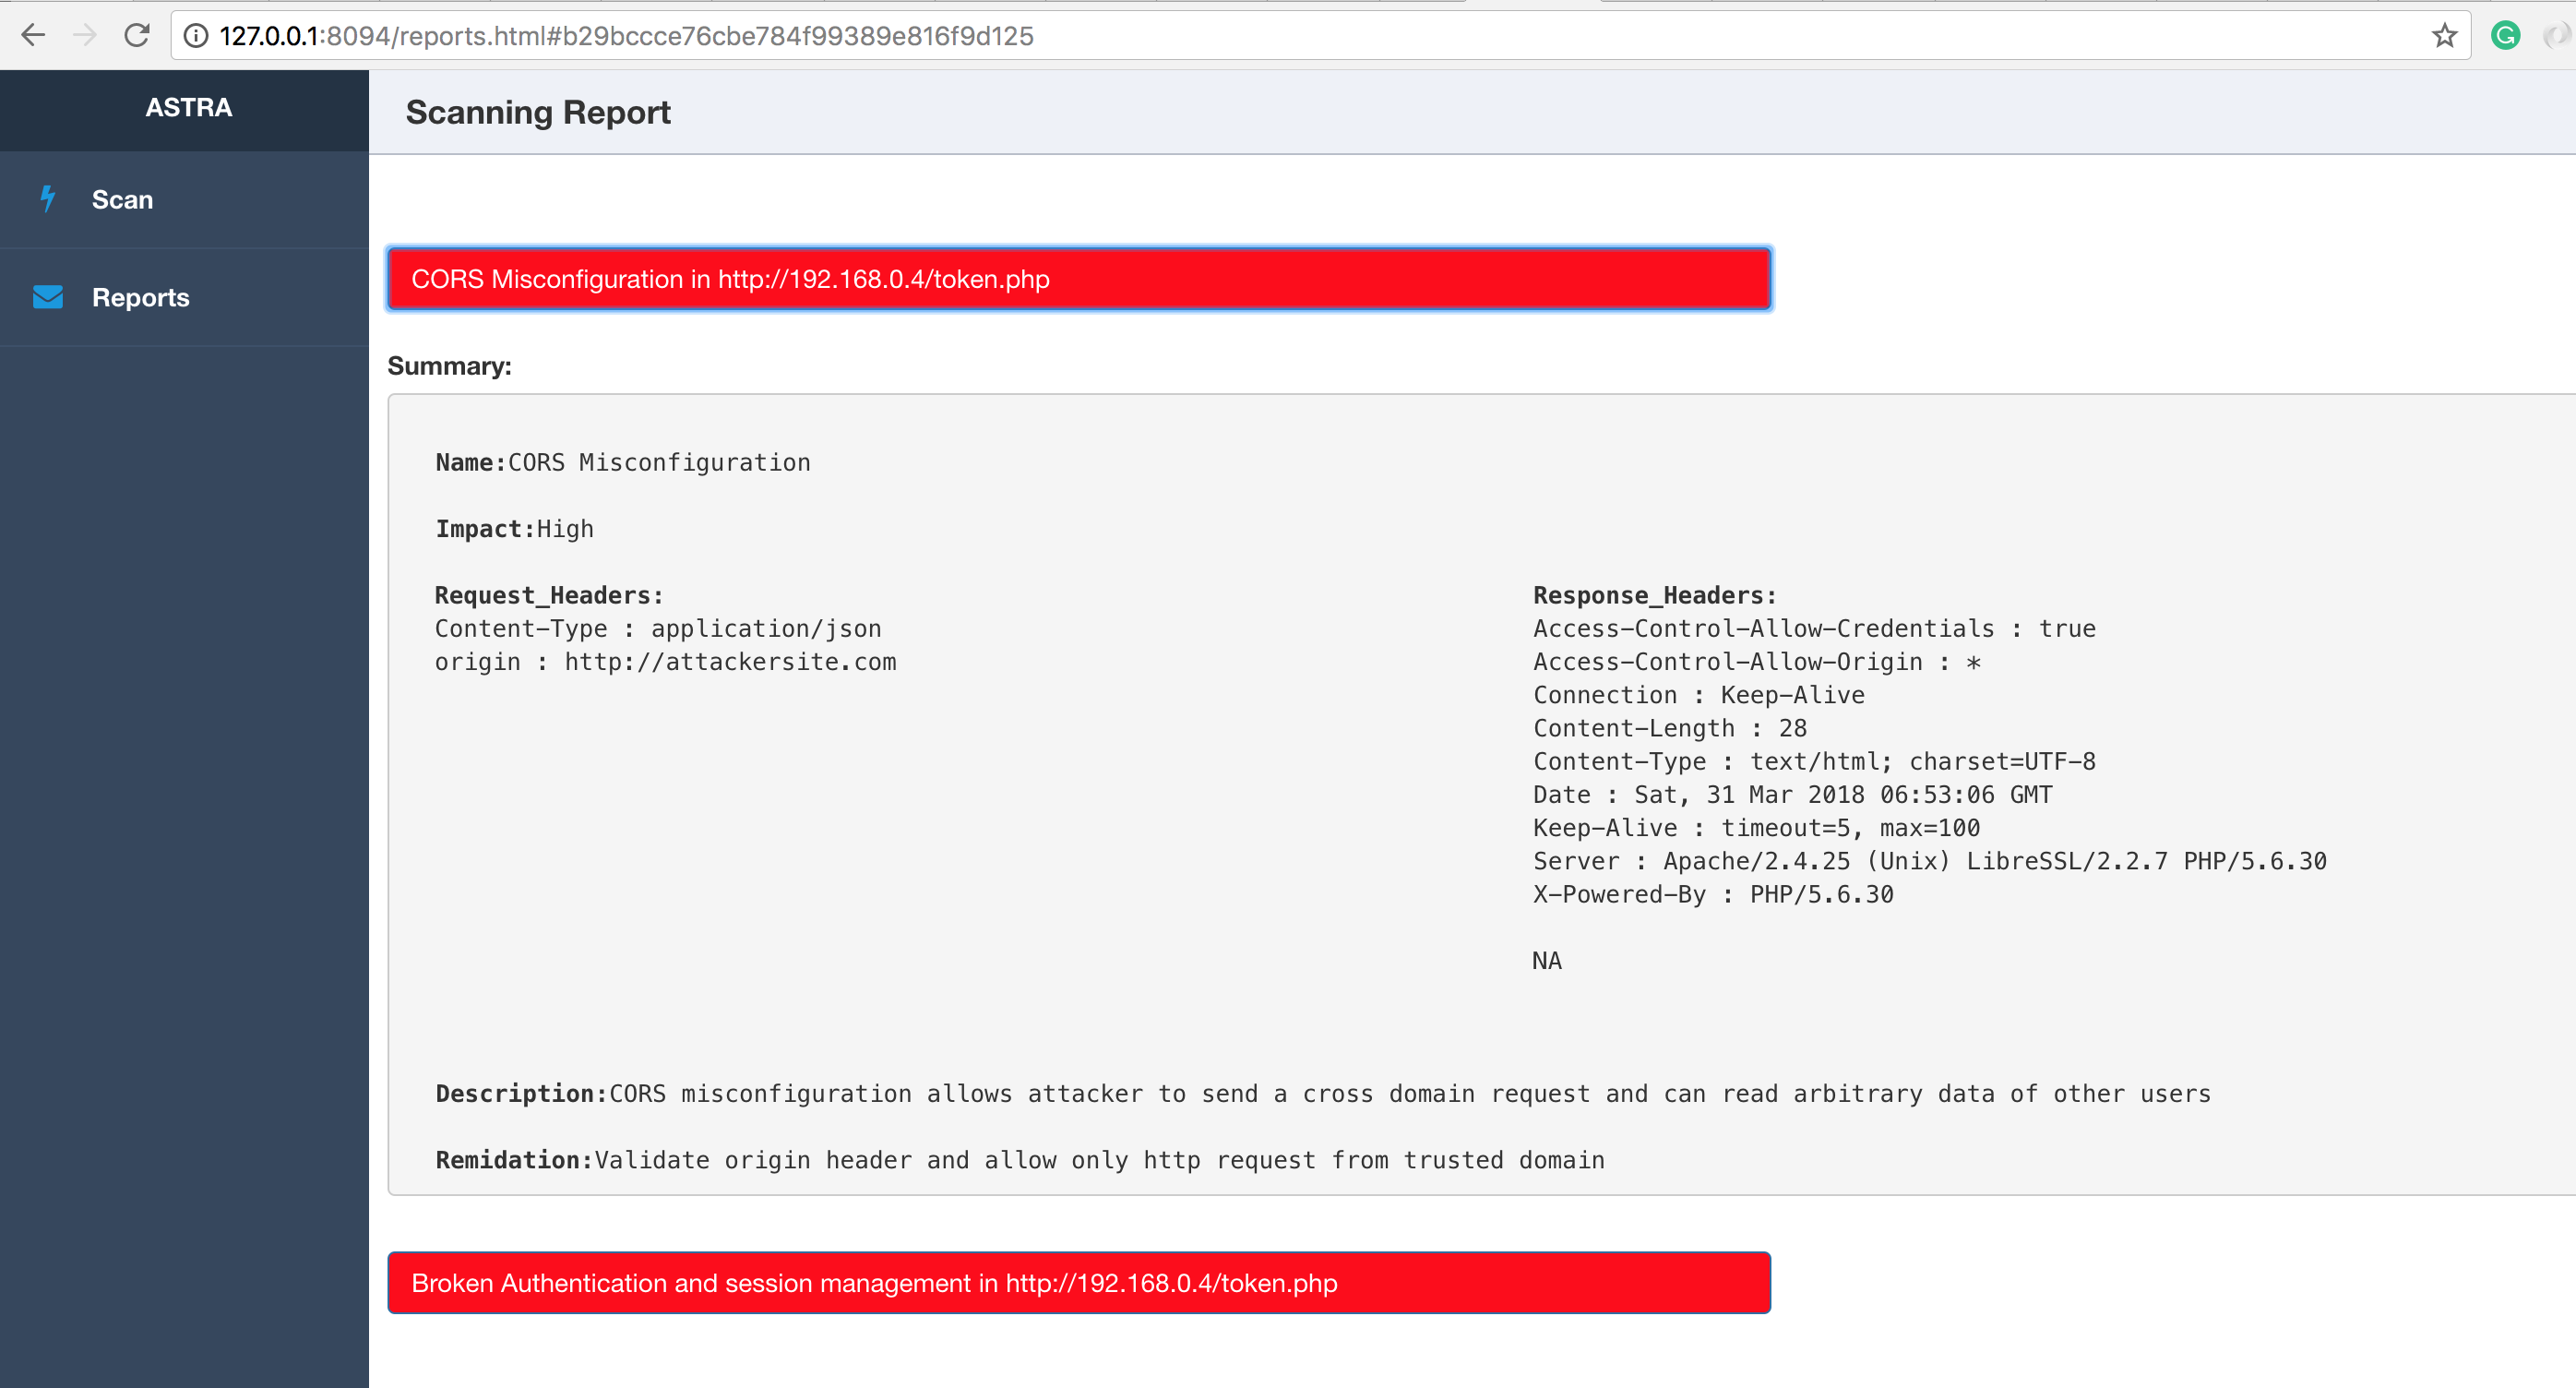
Automated Security Testing For REST API's

SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

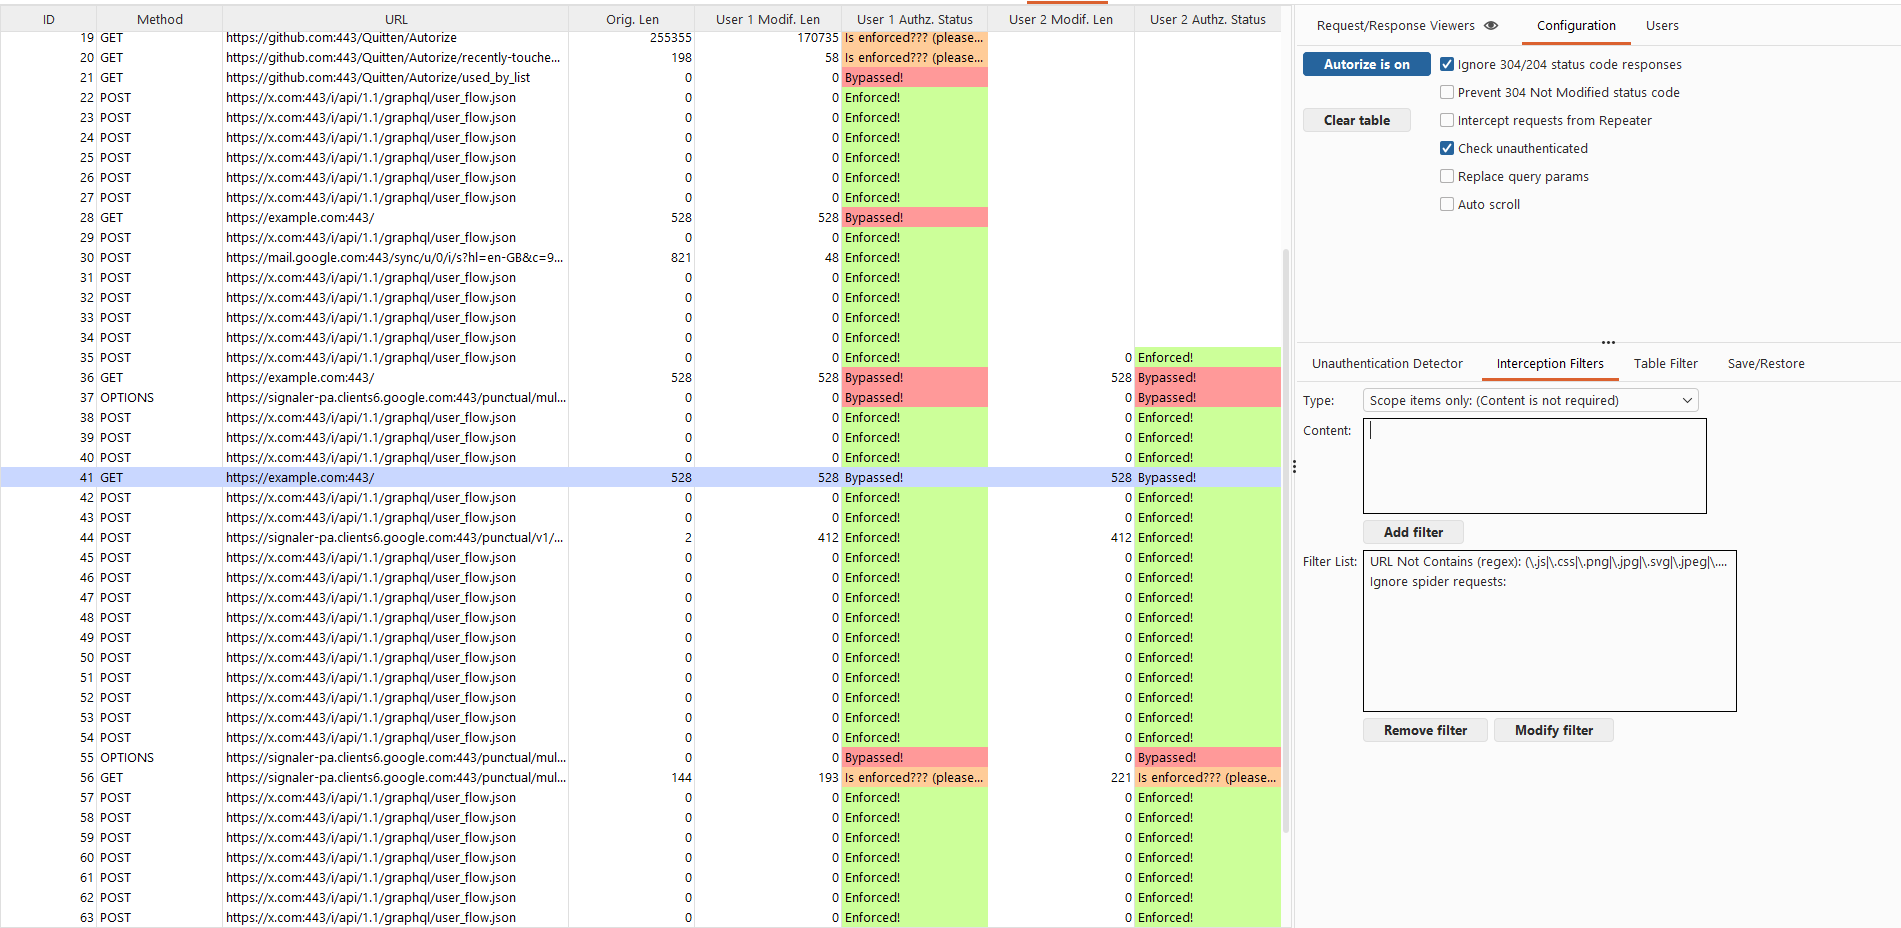
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…

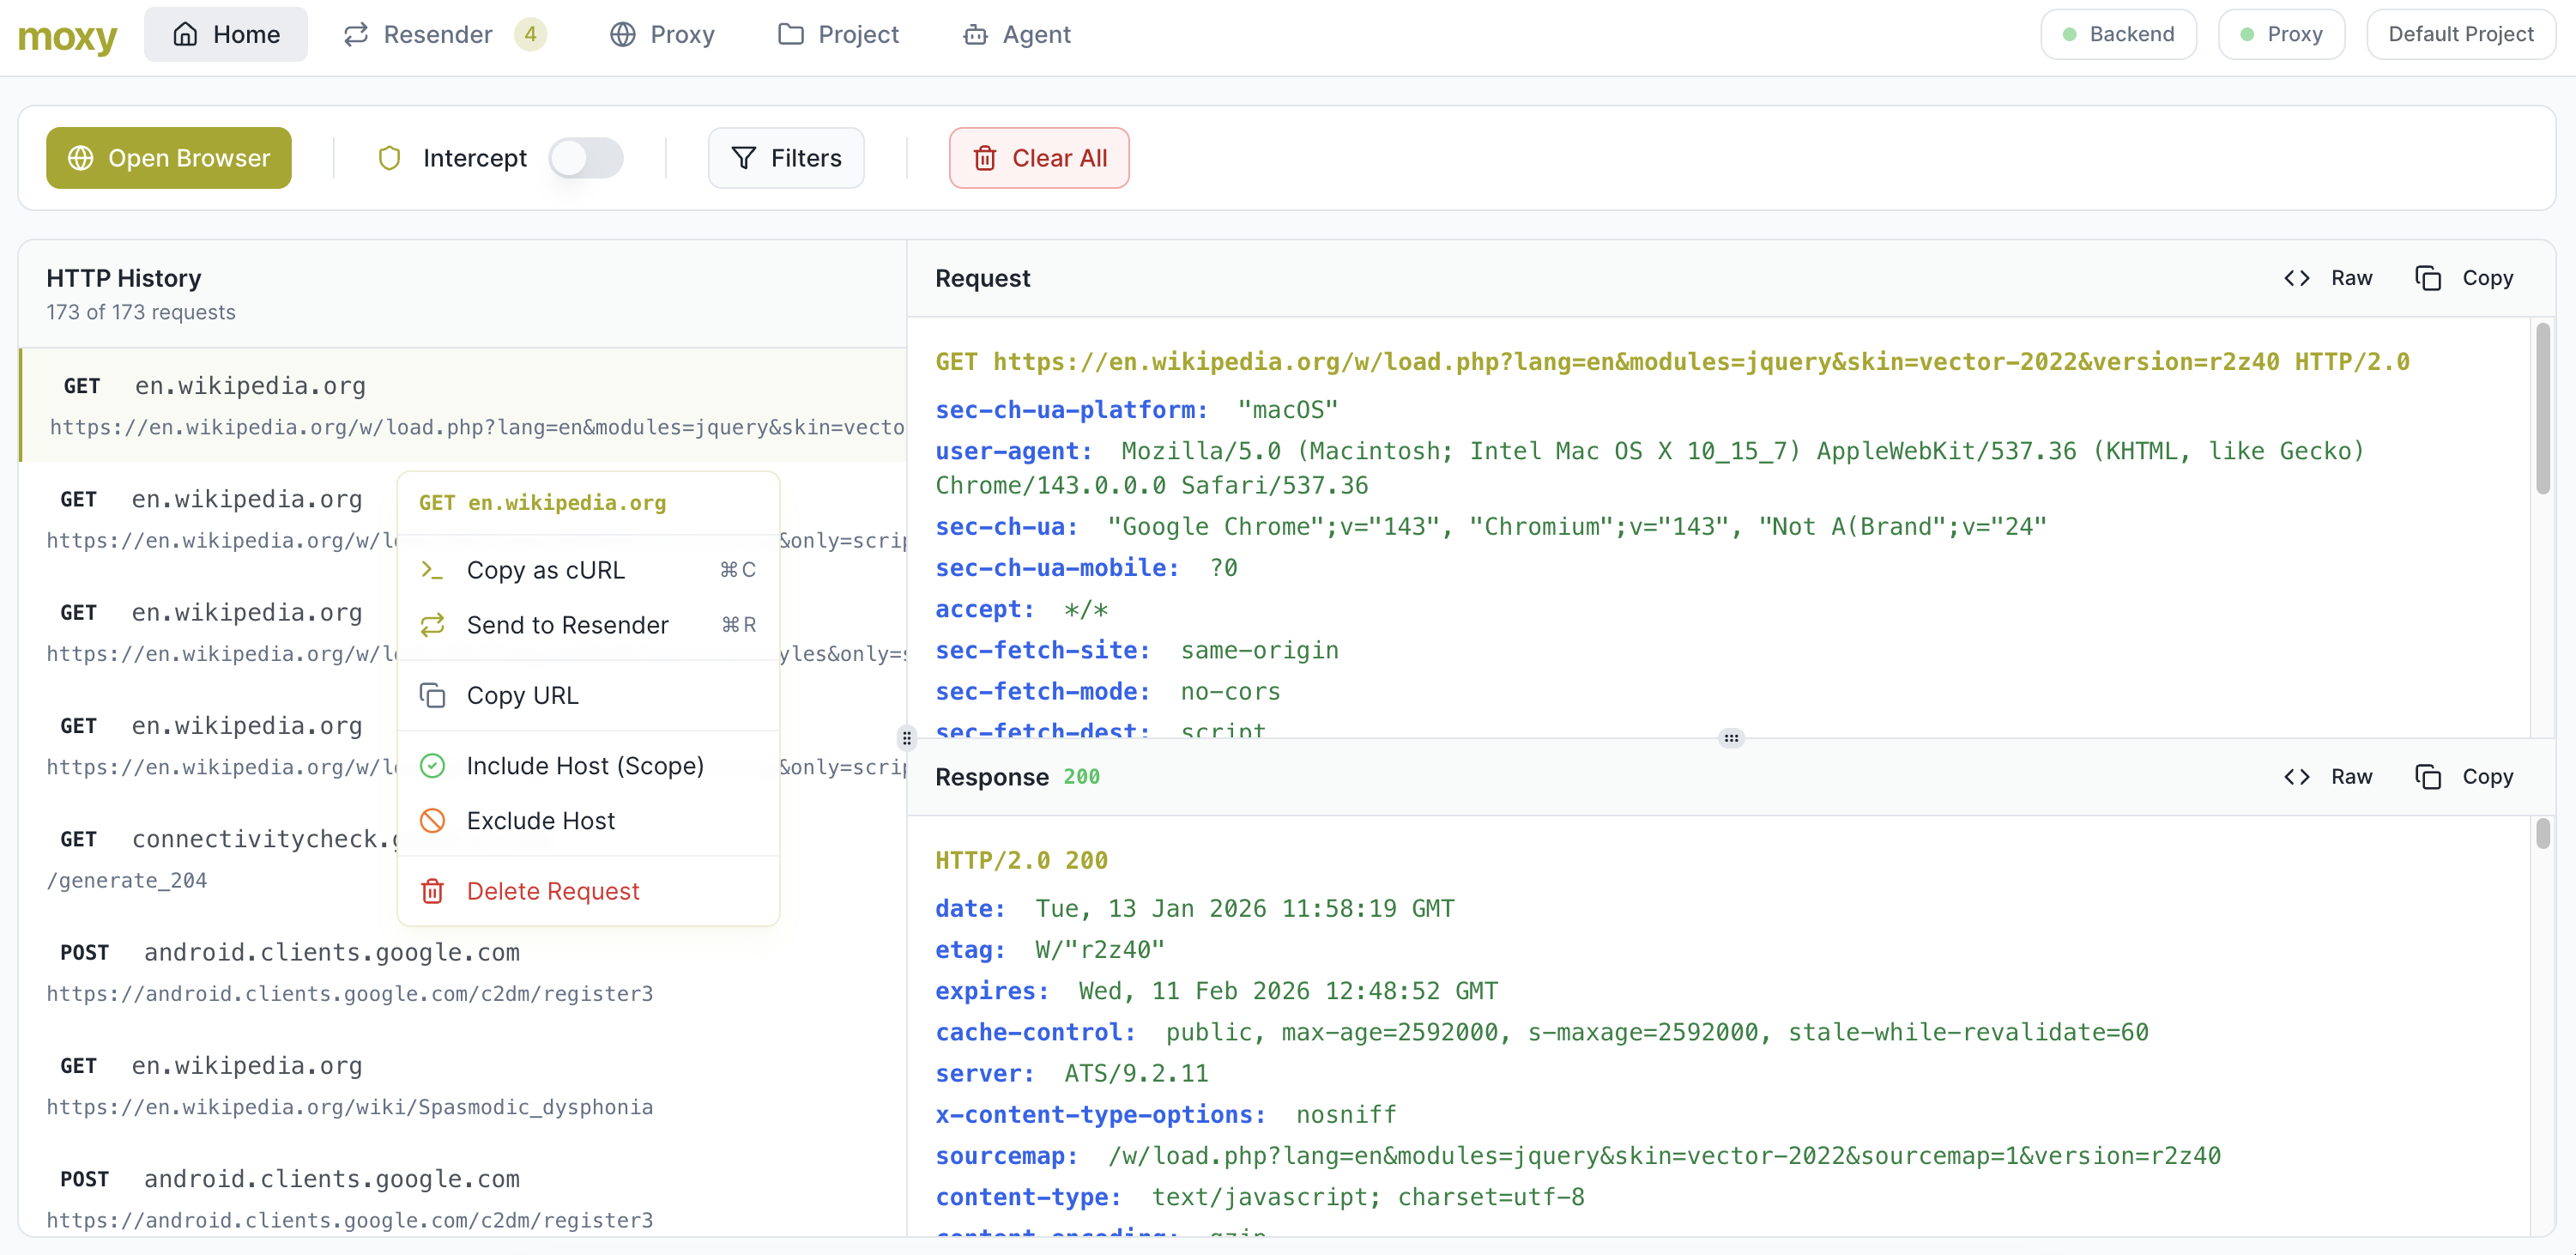
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…