
GraphQLer
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!
api-security-testingfuzzingvulnerability-analysis+1
omar2535/graphqler☸The first ever dependency-aware GraphQL API testing tool!

 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
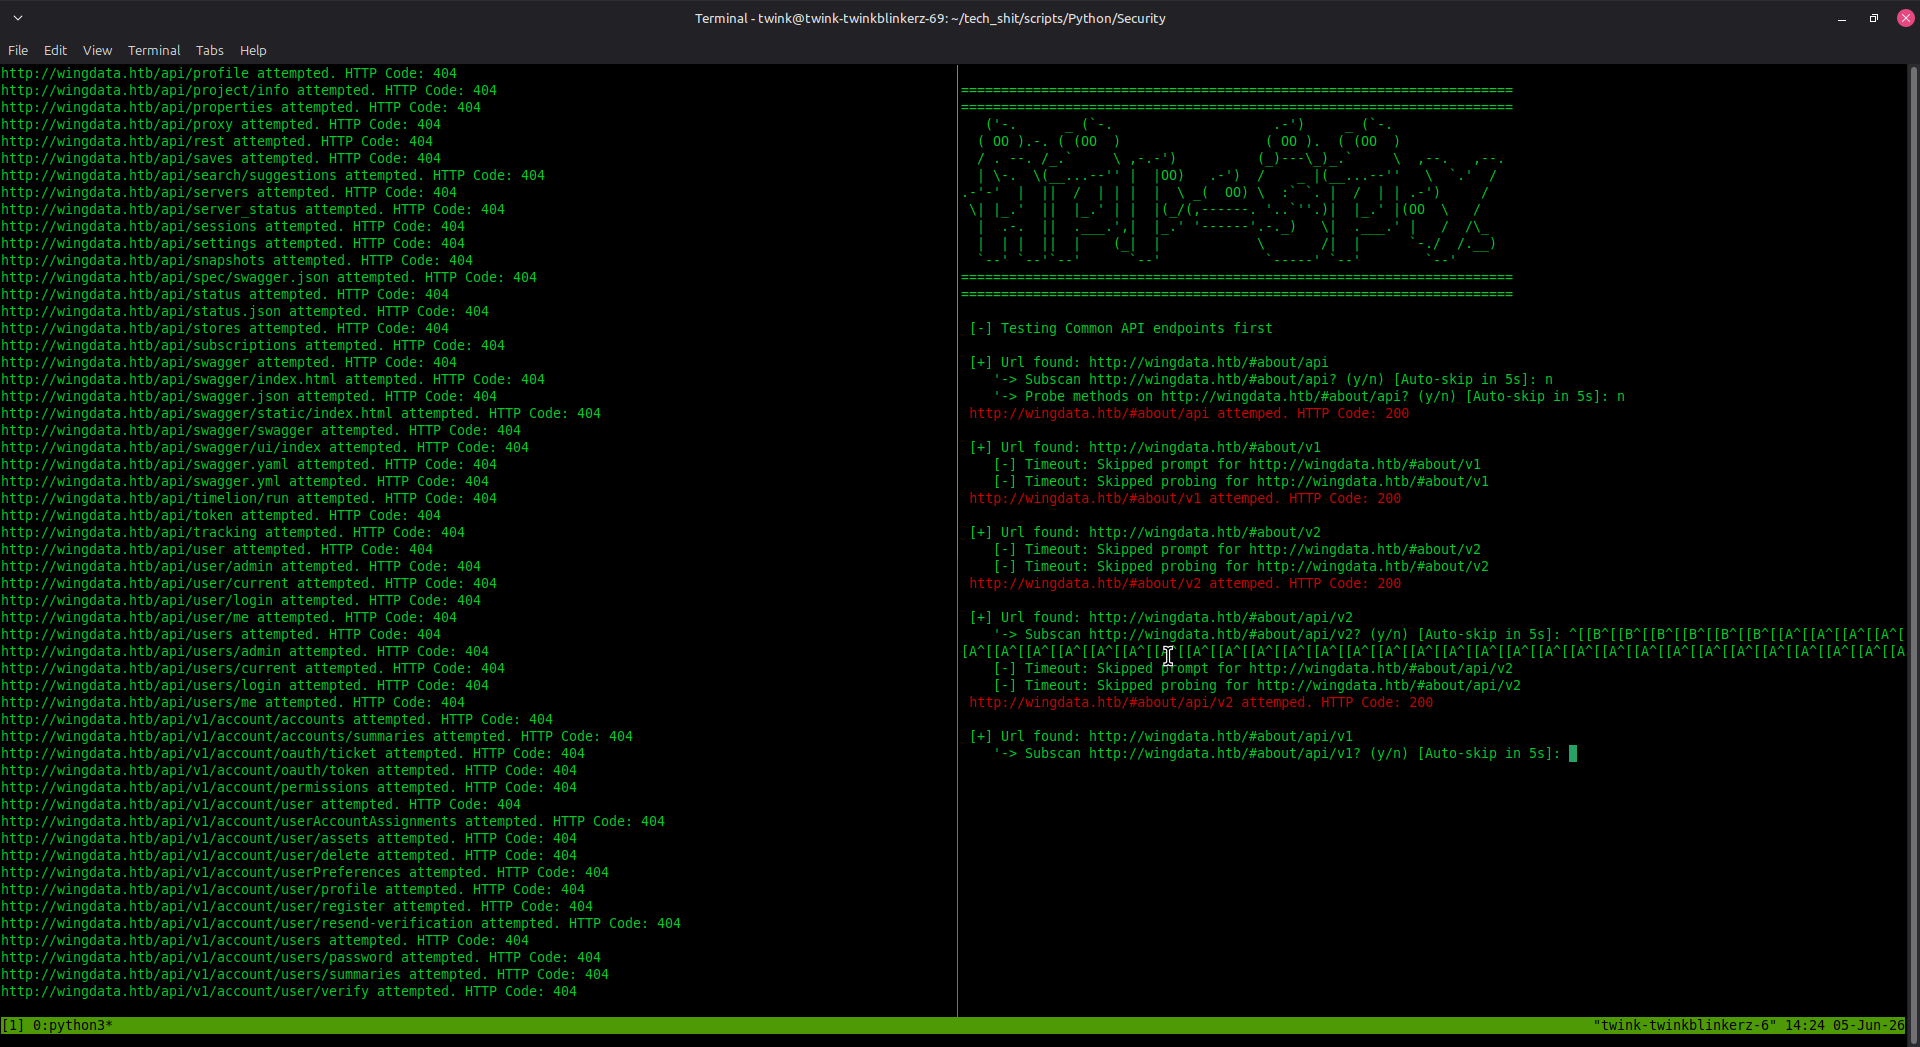 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 ridhinva/litellm-sqli-scanner
Scanner: CVE-2026-42208 LiteLLM SQL Injection — Python scanner for BerriAI LiteLLM proxy instances

 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool

 0xsteph/pentest-ai
Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.
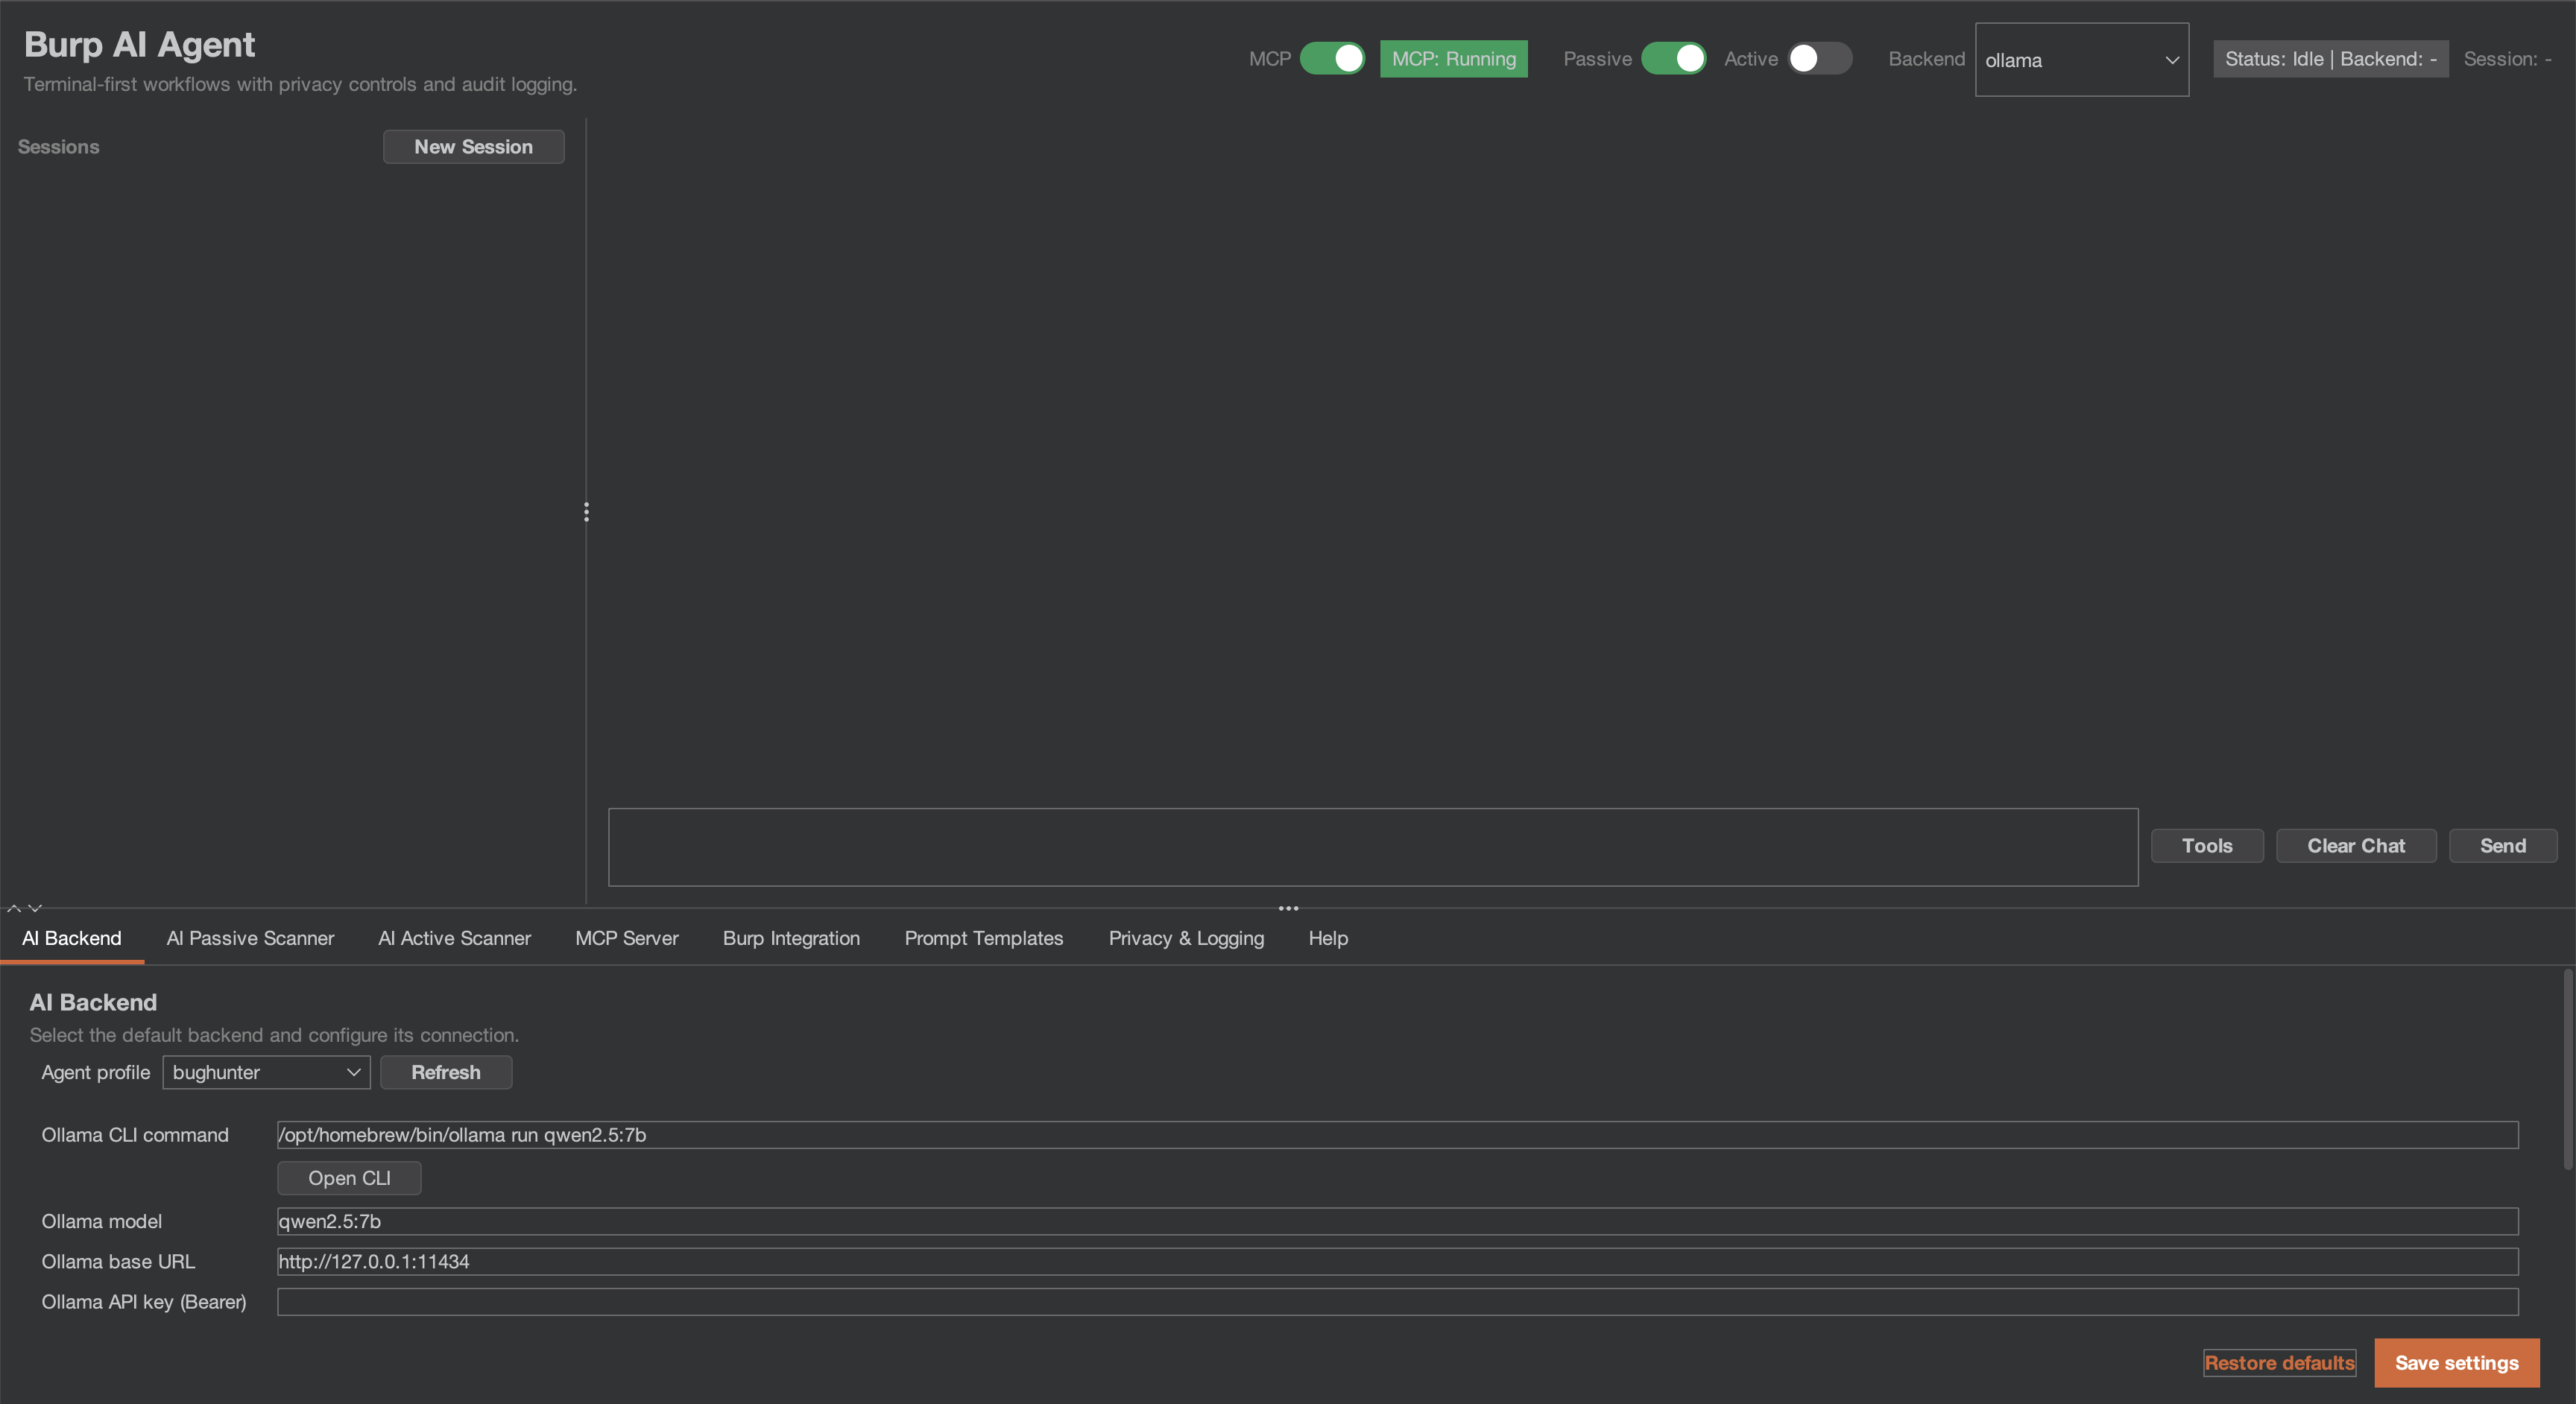 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.