
Mass-Assigner
Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…

Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…

Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…

An on-path blackbox network traffic security testing tool

HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…

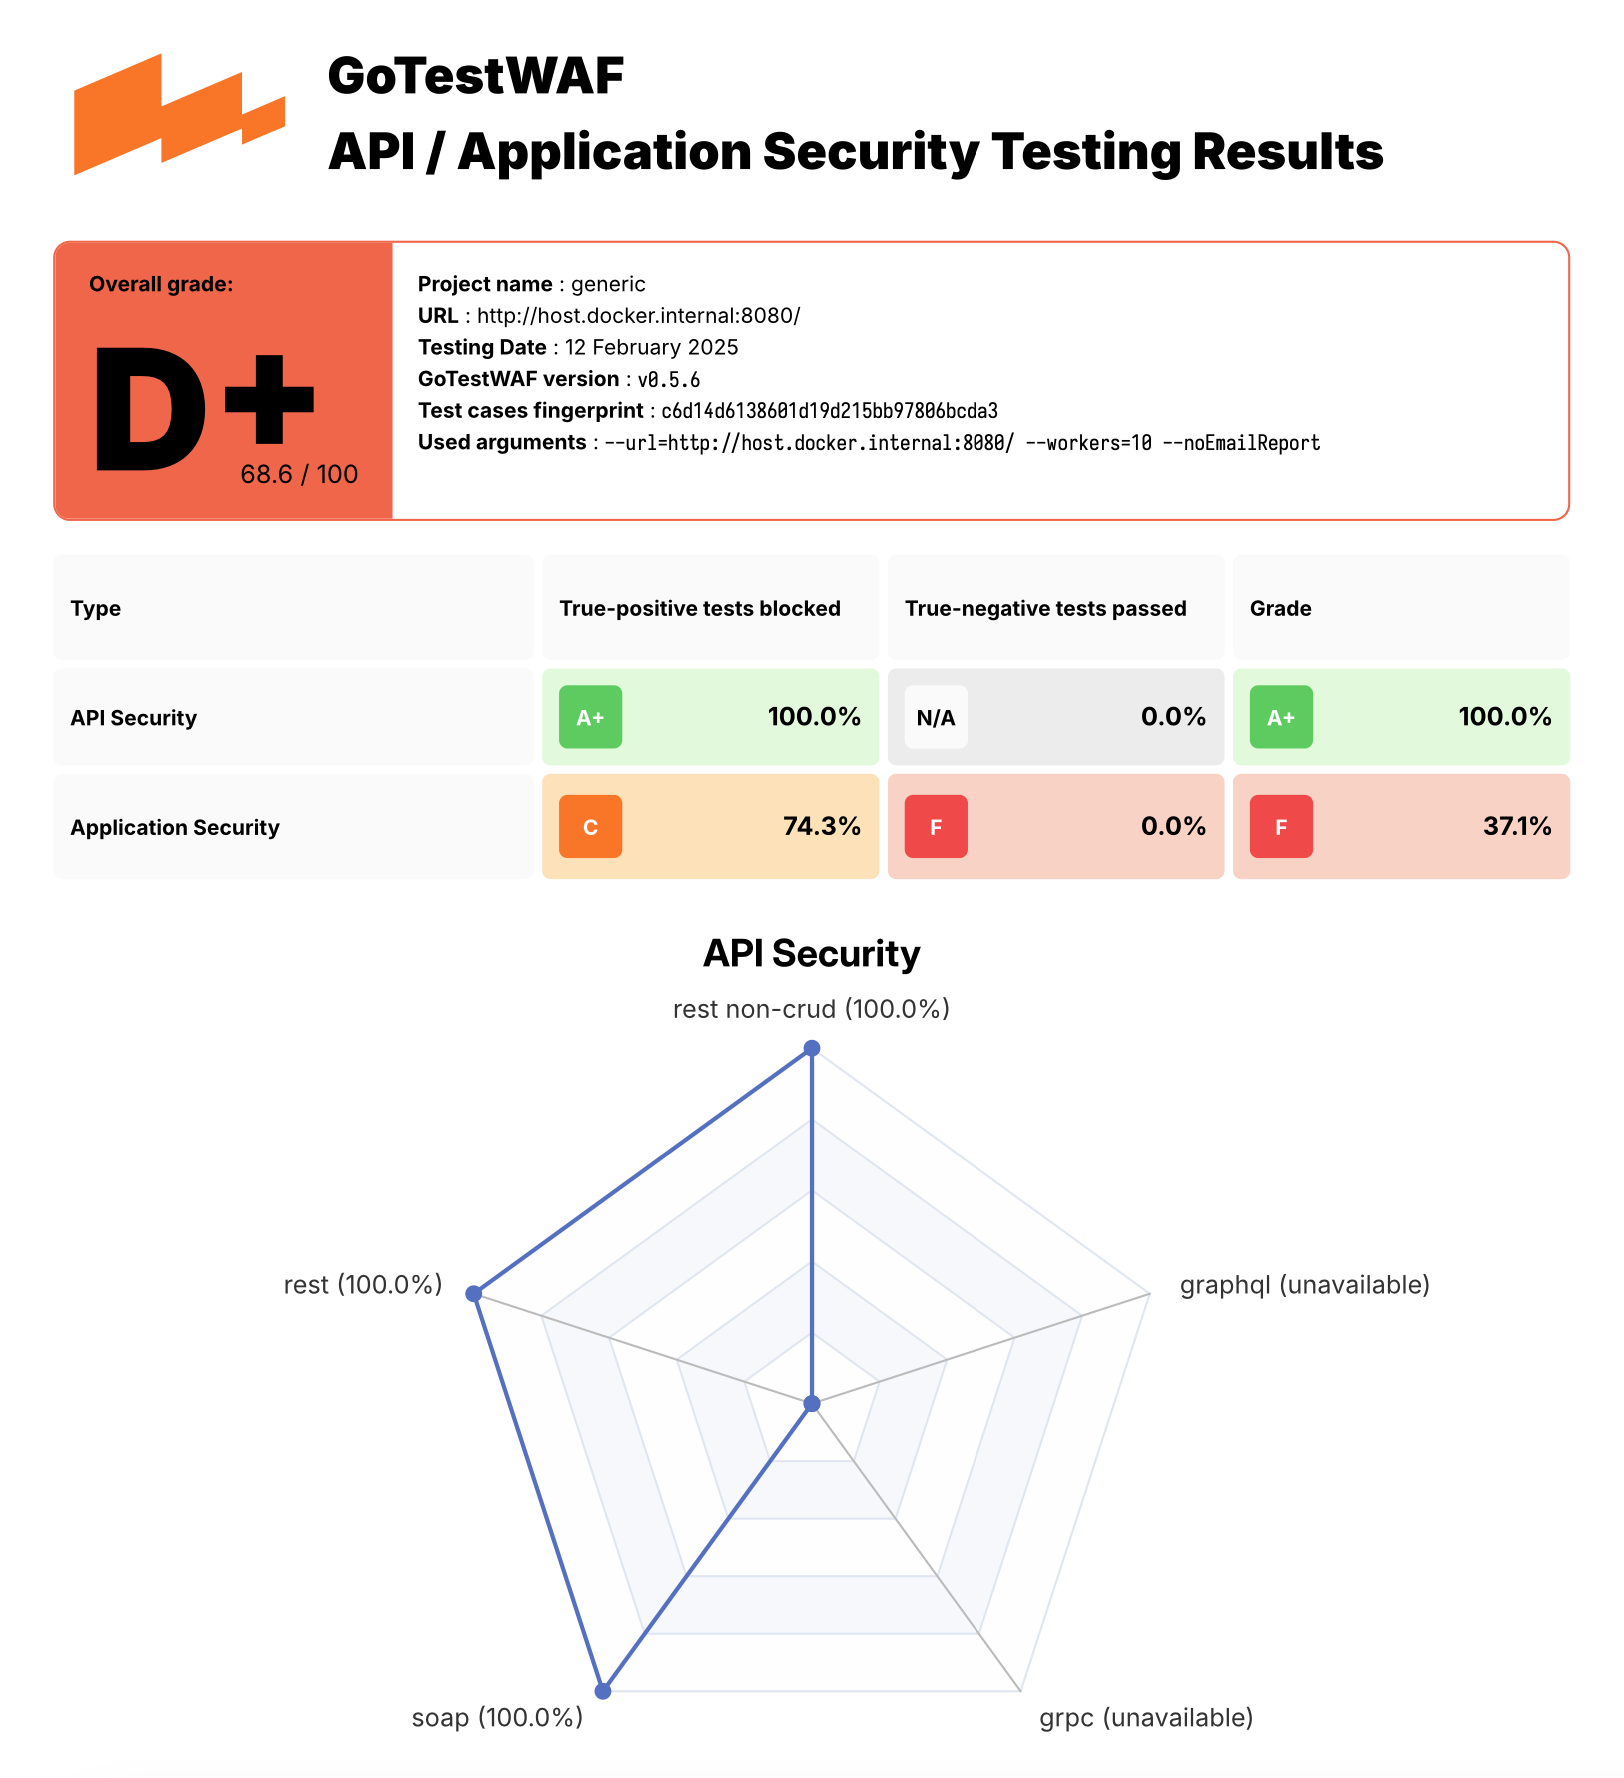
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses

Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…

CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…

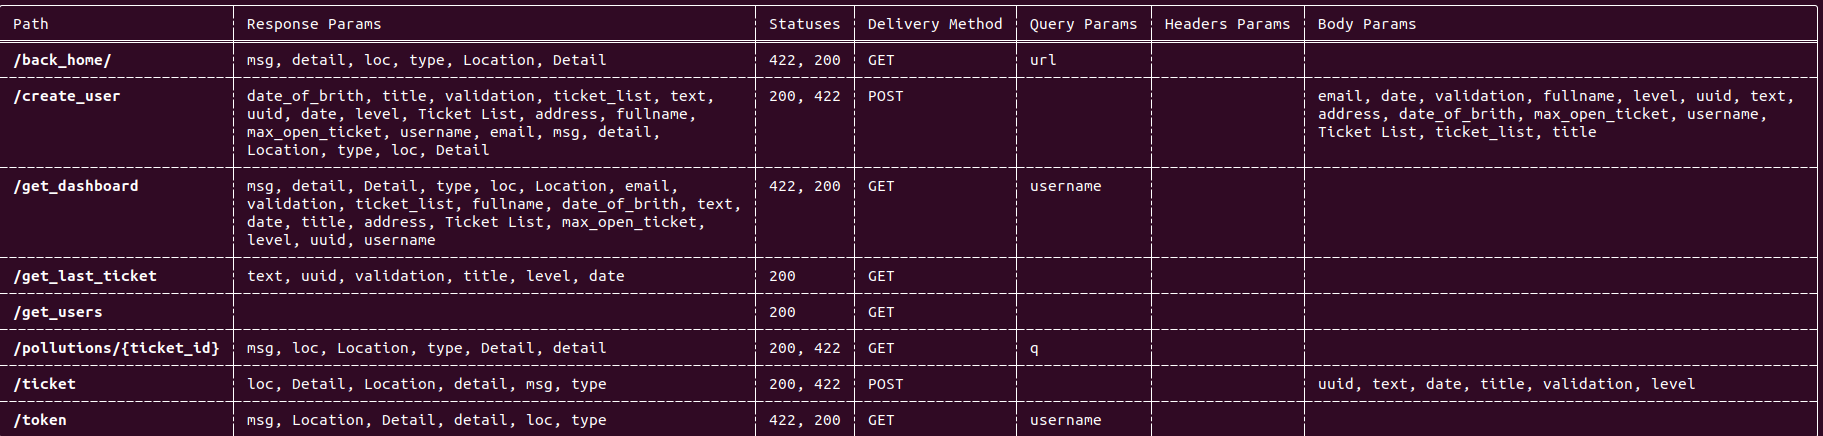
WEB SERVICE SECURITY ASSESSMENT TOOL

GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…

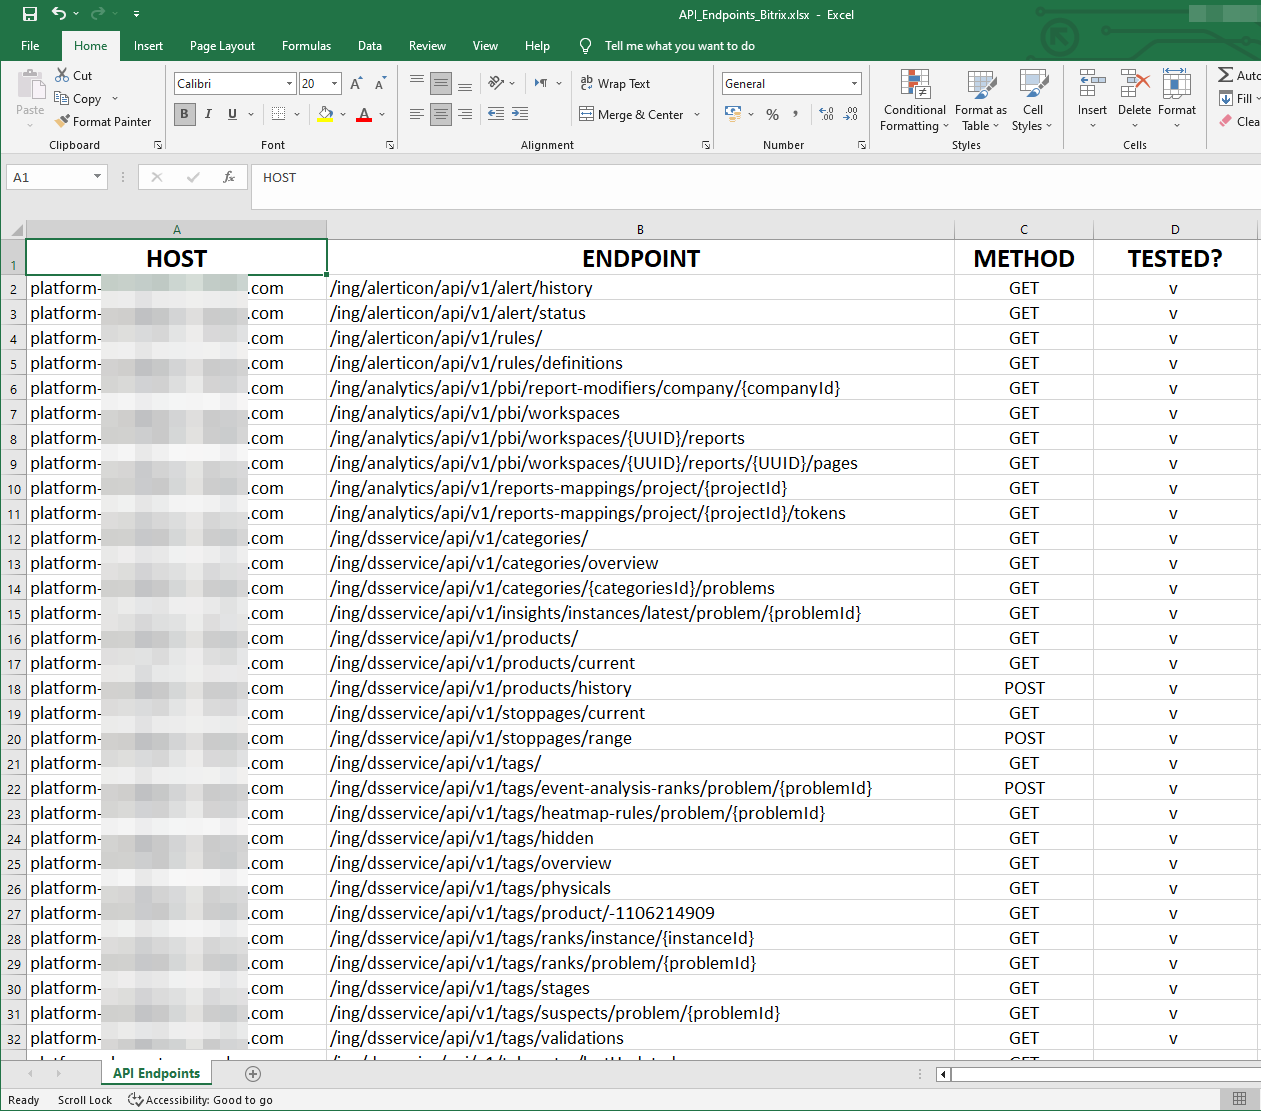
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.

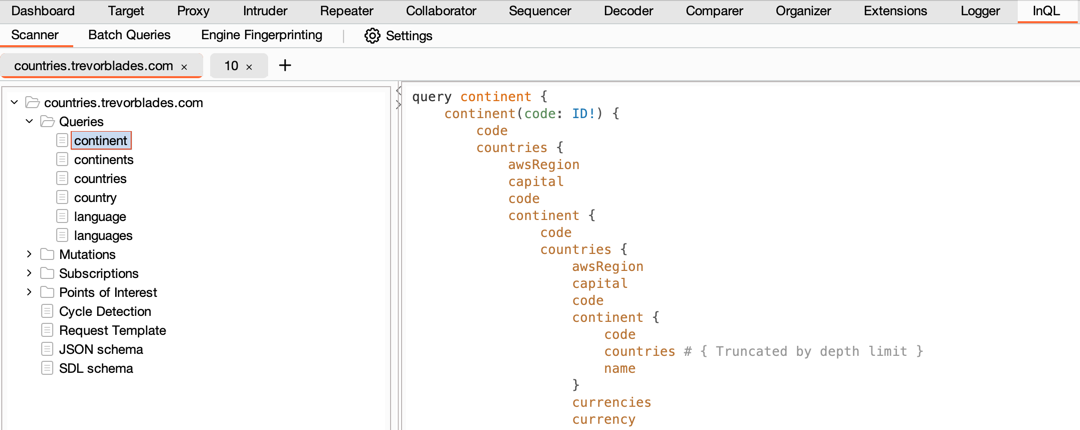
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…

Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.

OAuth Request Crafter

Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324

The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10

The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10

Academic purposes only. Attack against Salesforce lightning with guest privilege.

Automatic SQL injection and database takeover tool