
cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…

CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…

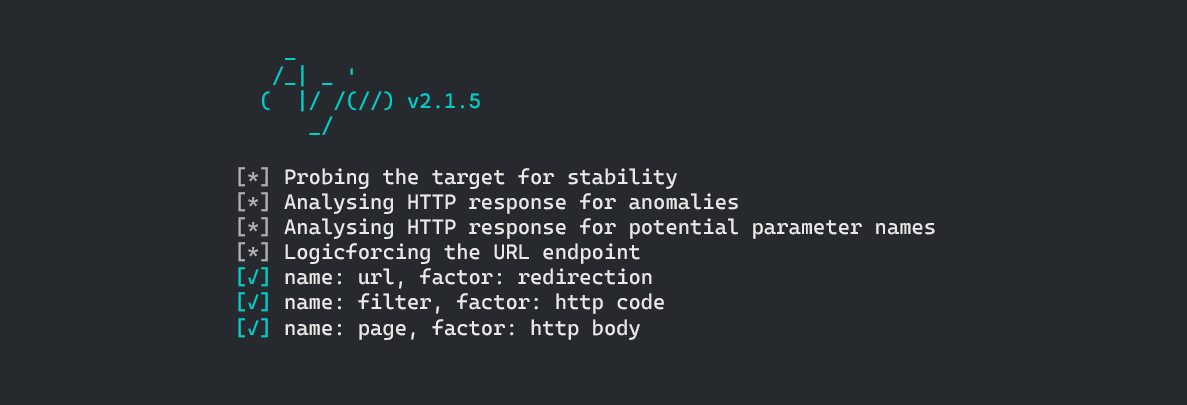
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…

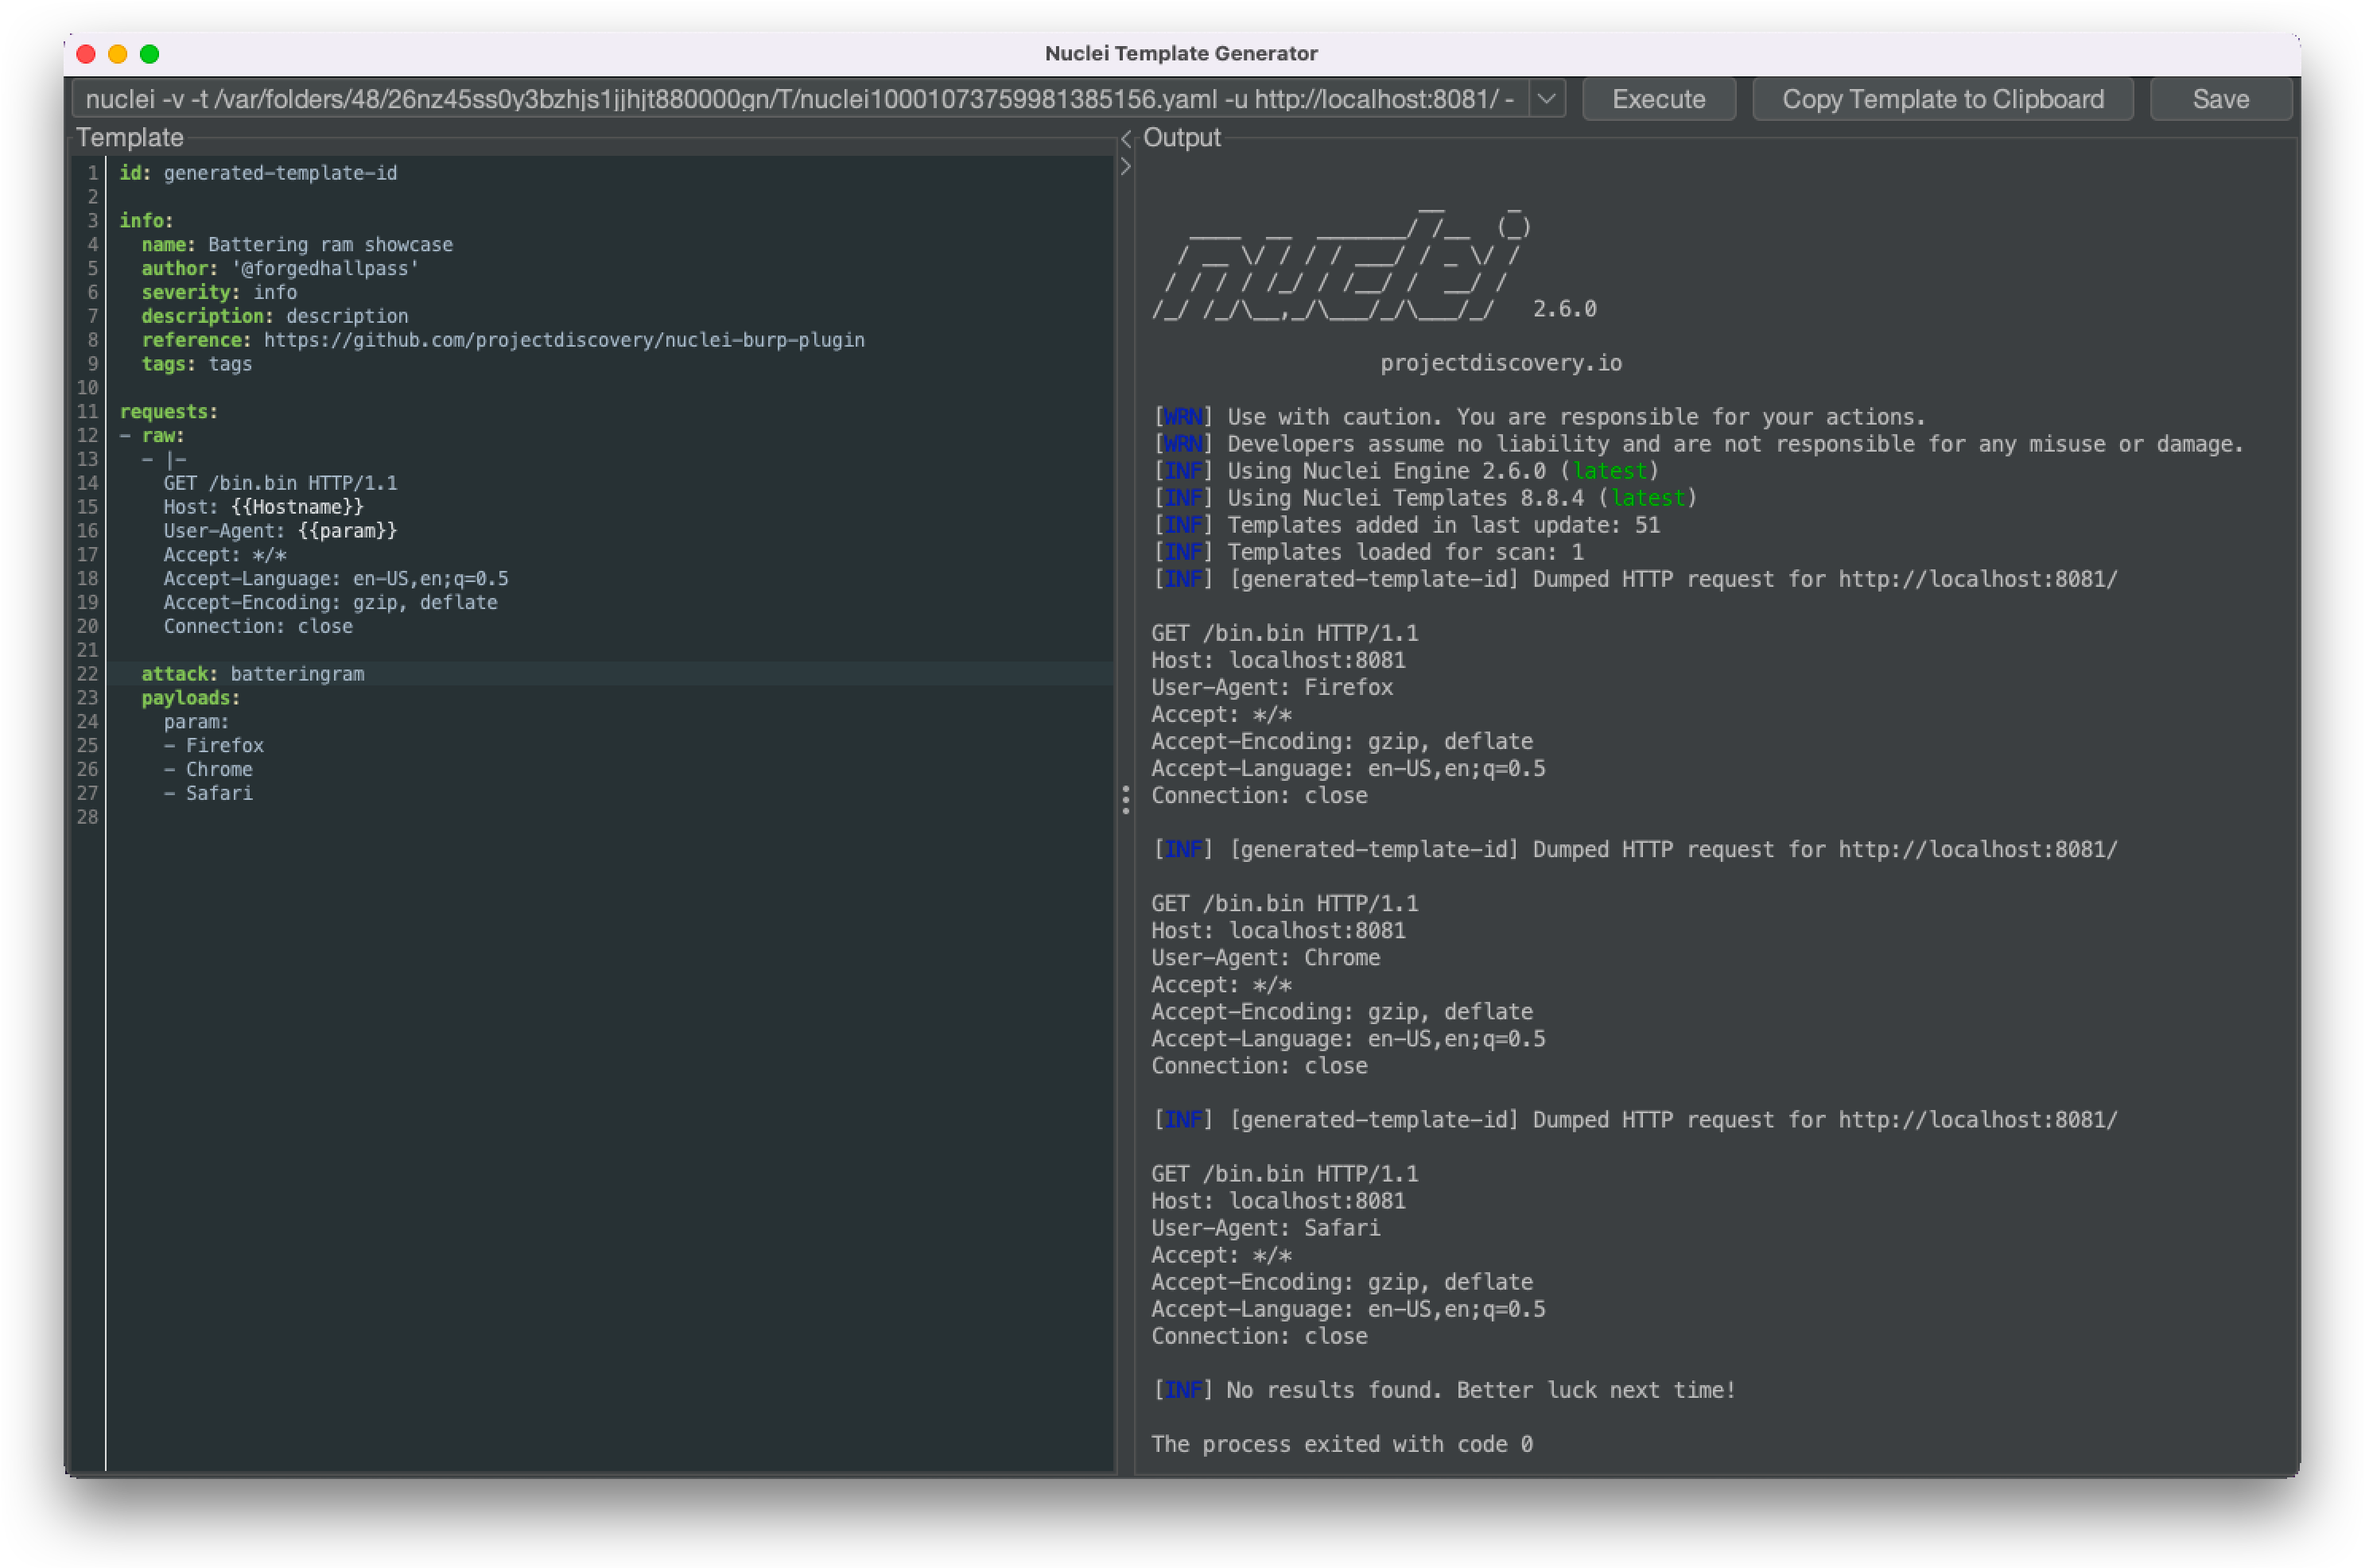
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…

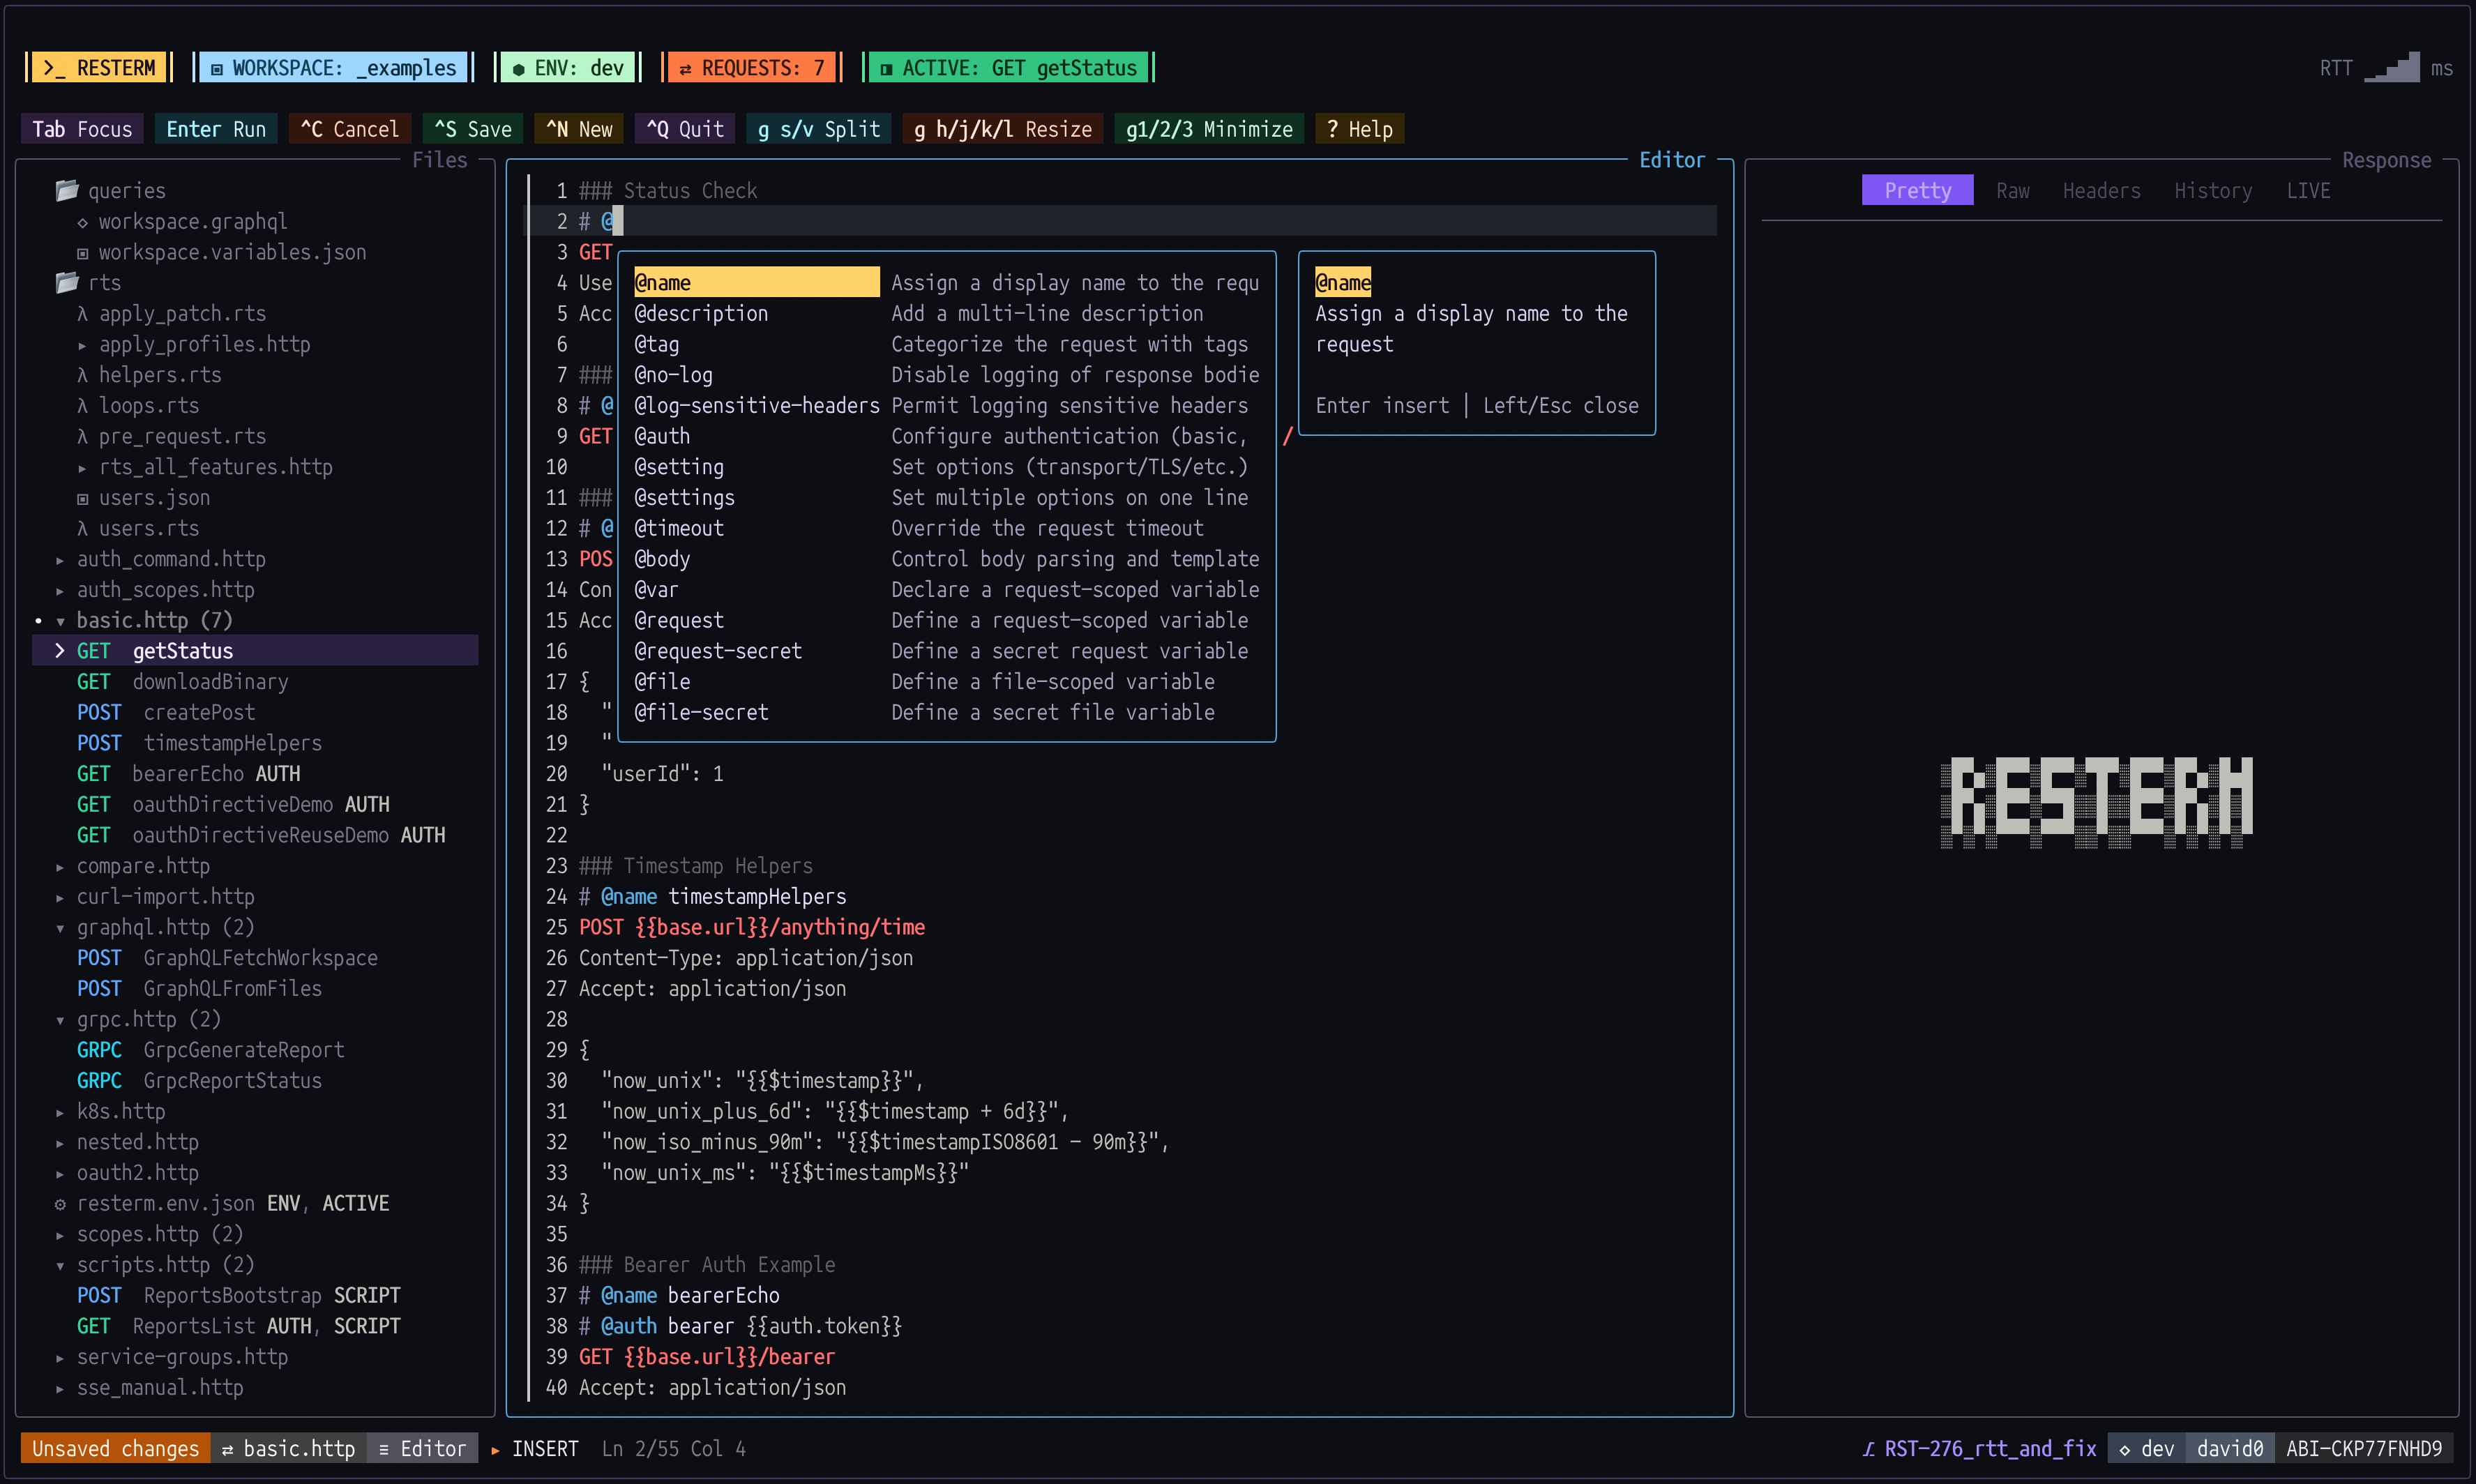
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…

Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…

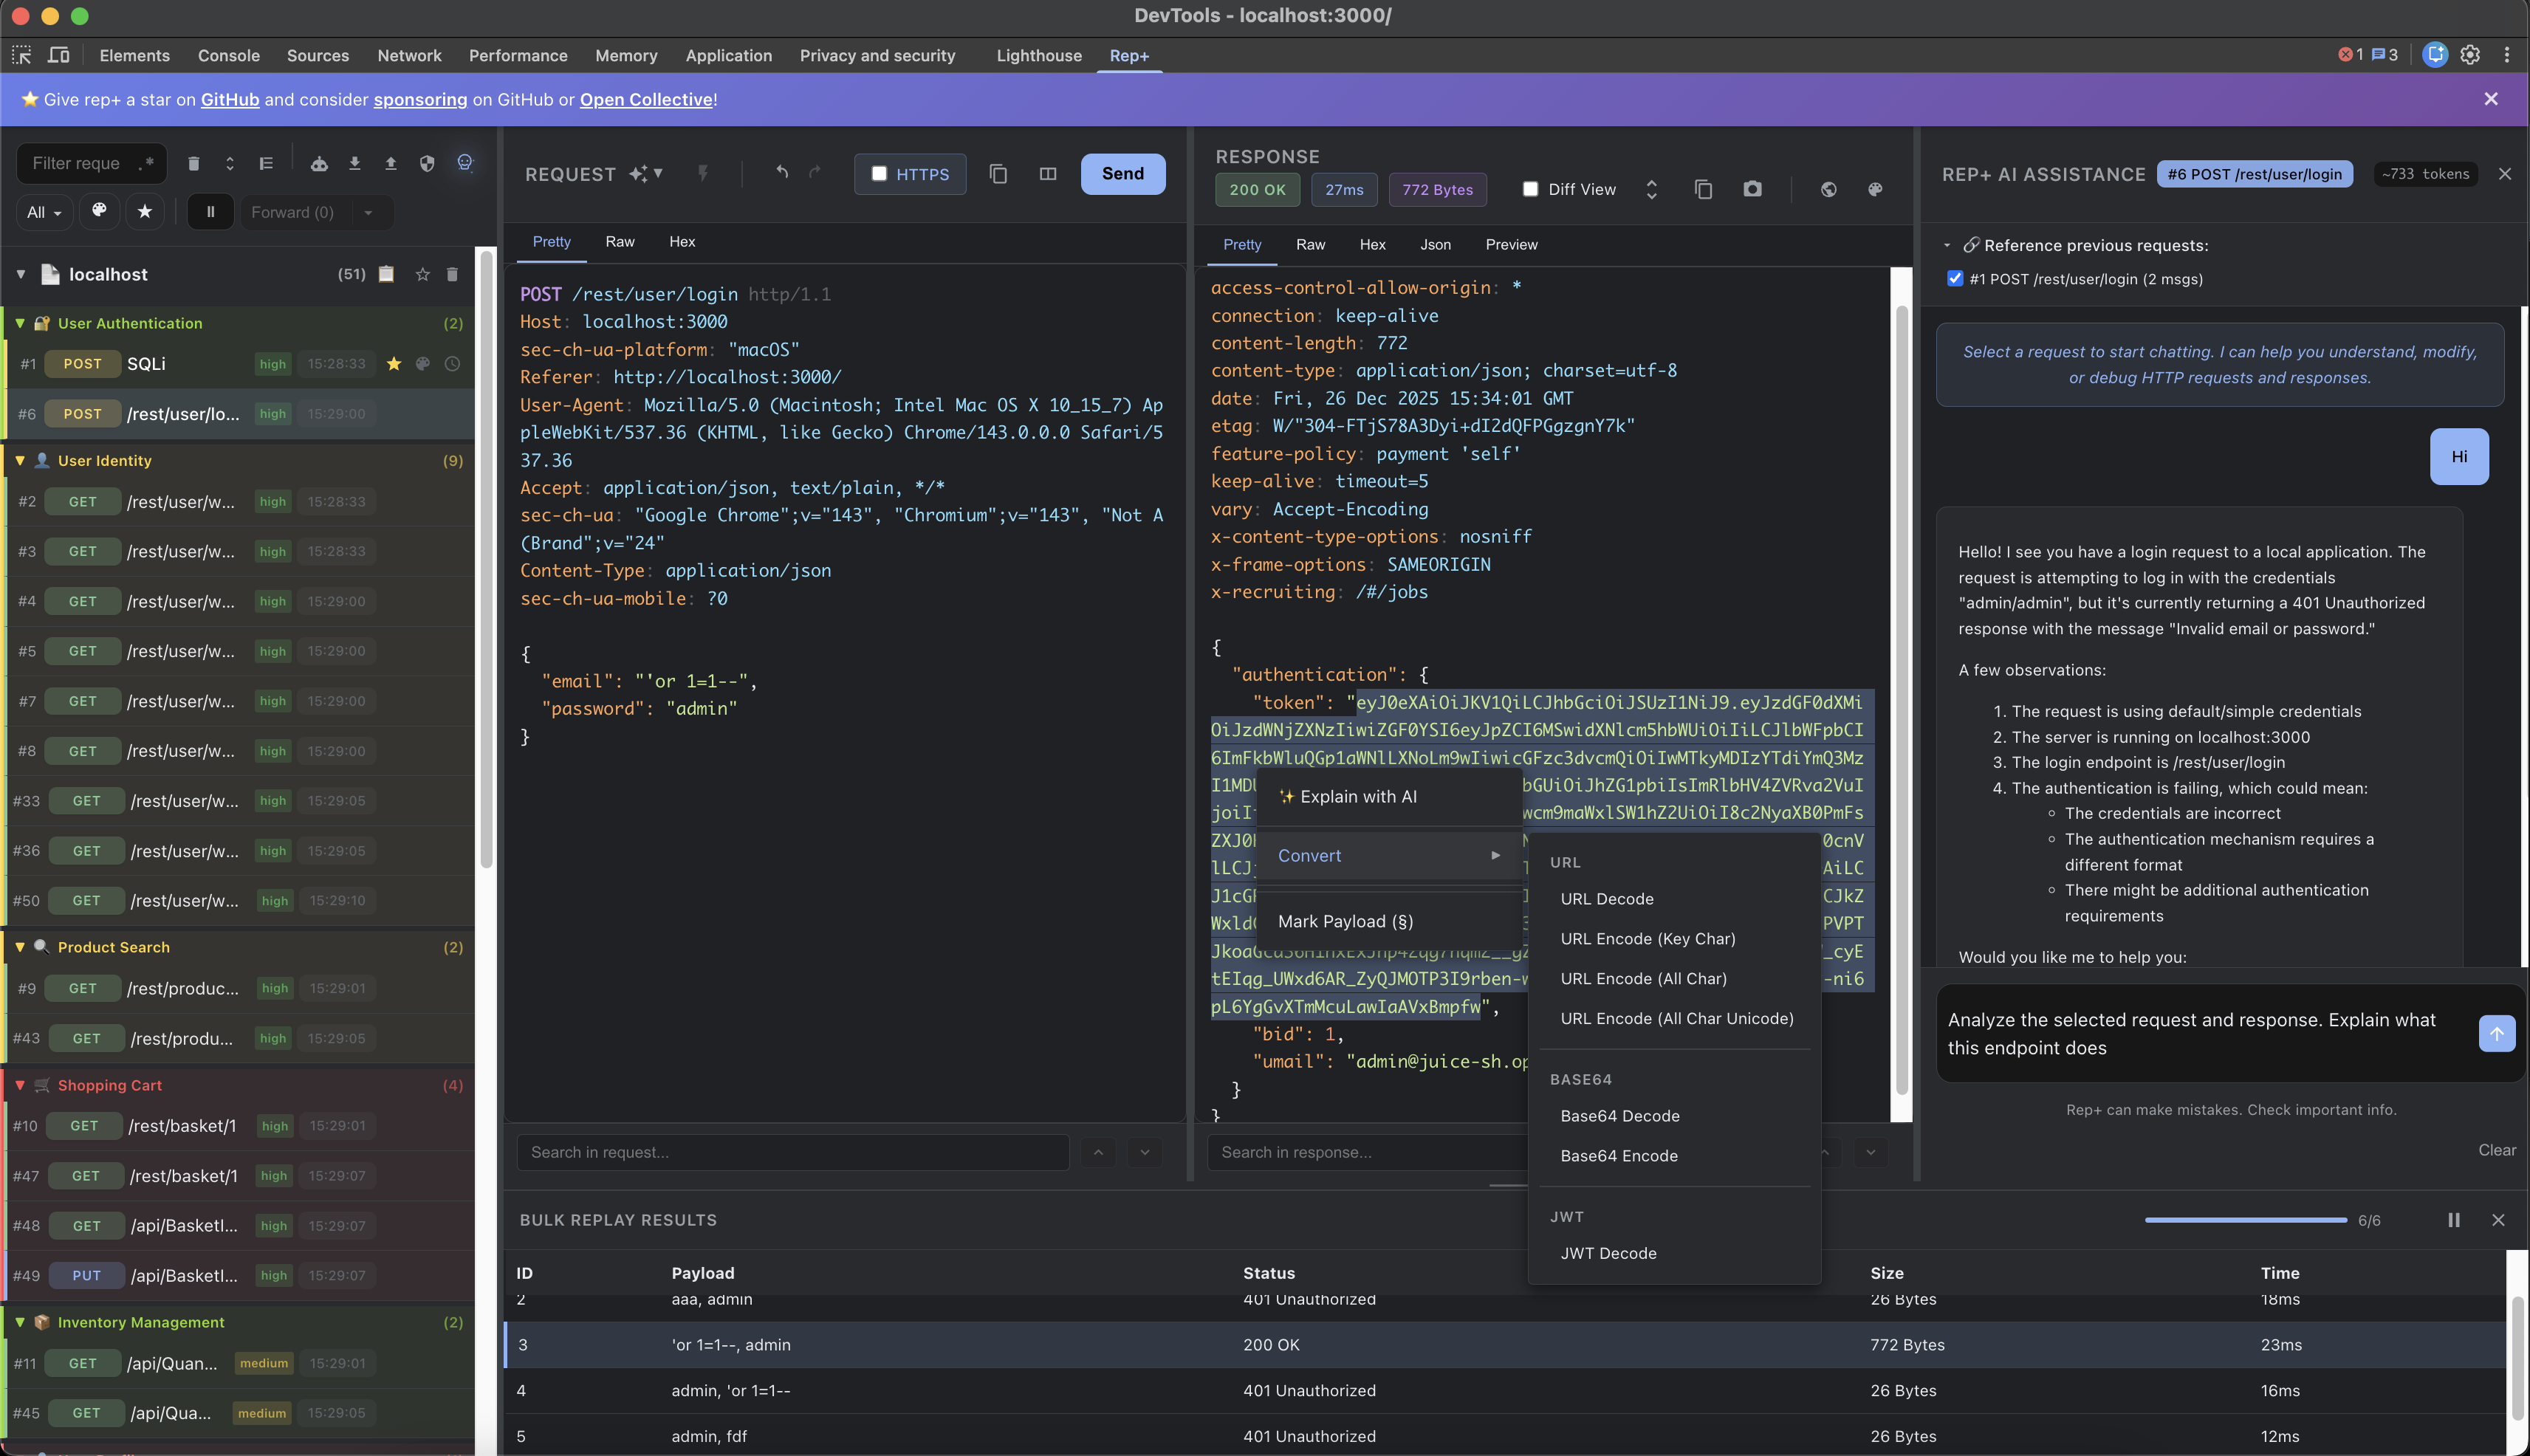
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks

Automated HTTP Request Repeating With Burp Suite

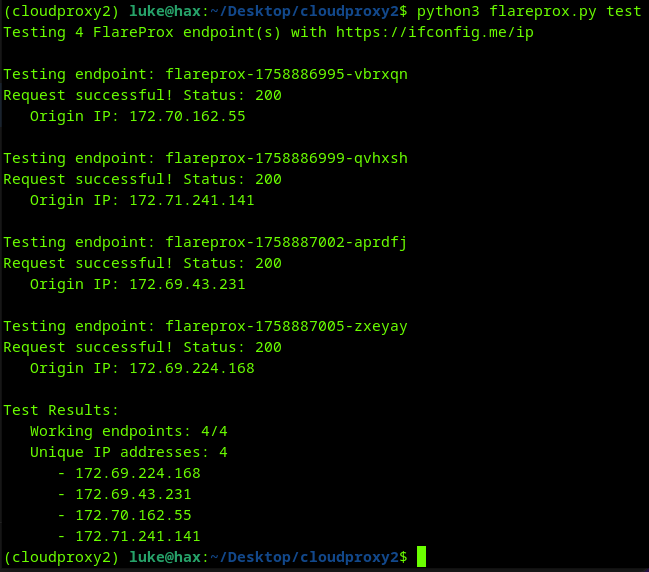
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox

Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).

Rust-powered HTTP Request Smuggling Scanner.

A rapid HTTP downgrade smuggling scanner written in Go.

OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions

Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…

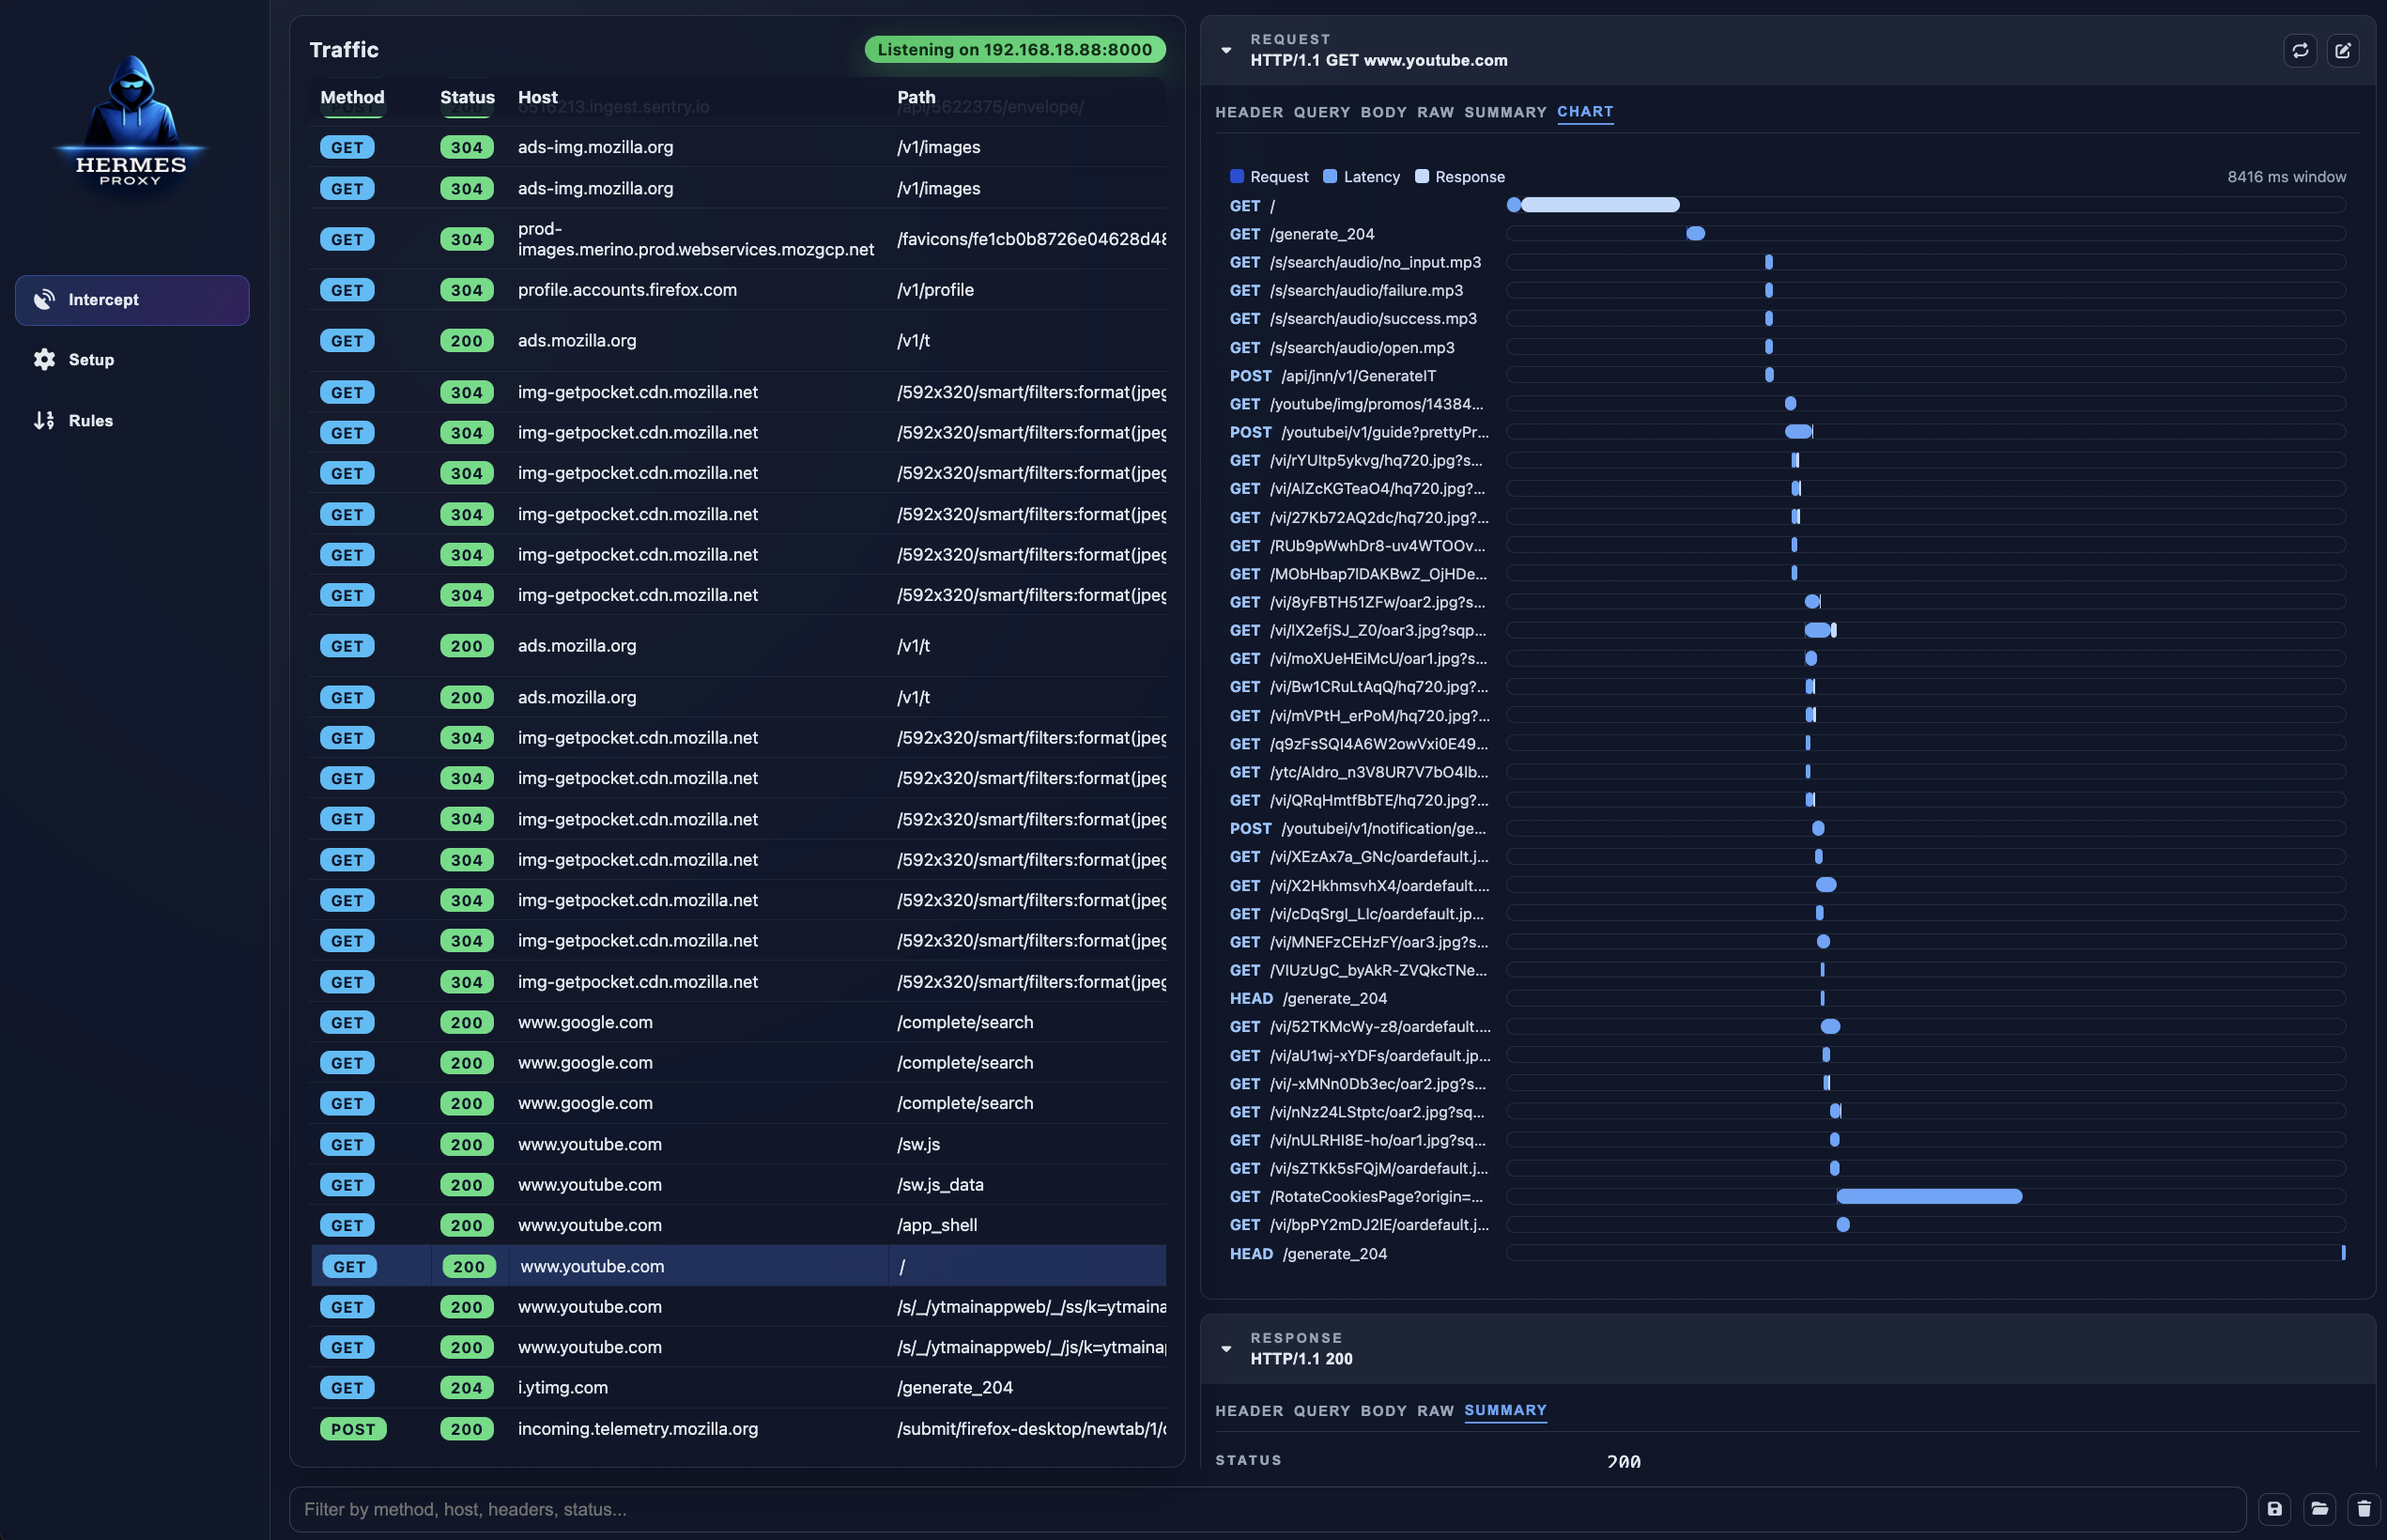
Hermes Proxy - HTTP Traffic Analyzer

This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…

Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…

Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.

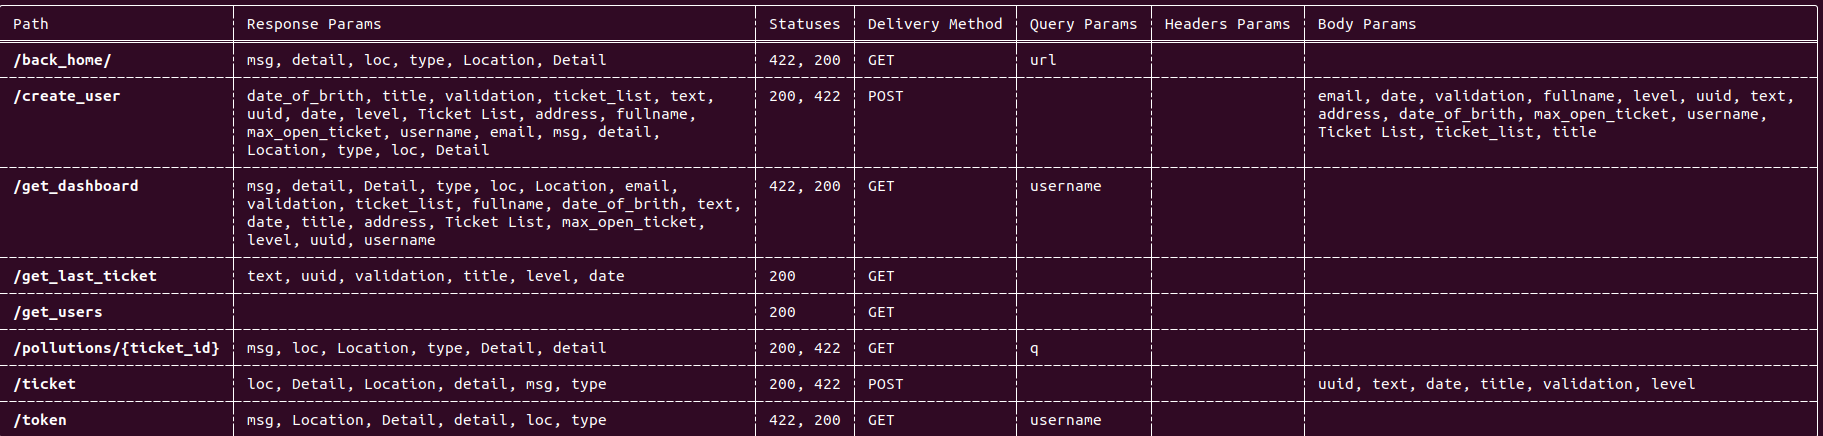
Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…