
SILENTCHAIN
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
ai-securityapi-security-testingcode-analysis+8
silentchainai/silentchainAI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 penteraio/cve-2026-41473-cyberpanel-ai-scanner-unauth
Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…
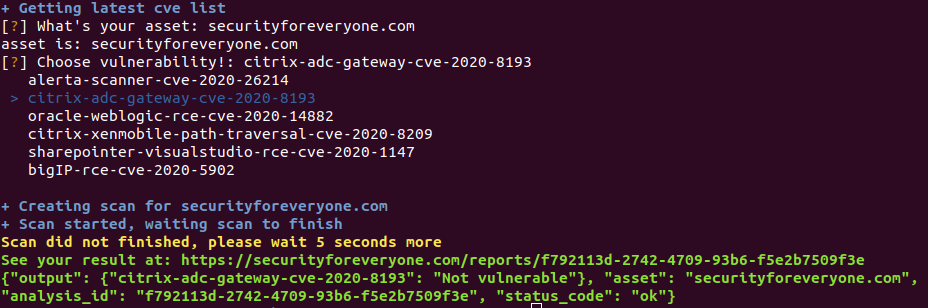 s4e-io-old-labs/s4e-cve-scanner
API-based scanner that retrieves and lists the latest Common Vulnerabilities and Exposures (CVEs) for automated security assessment and vulnerability…

 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 ridhinva/langflow-cors-scanner
Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)
 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.