
Burp_Collector
 sajibuu/burp_collector
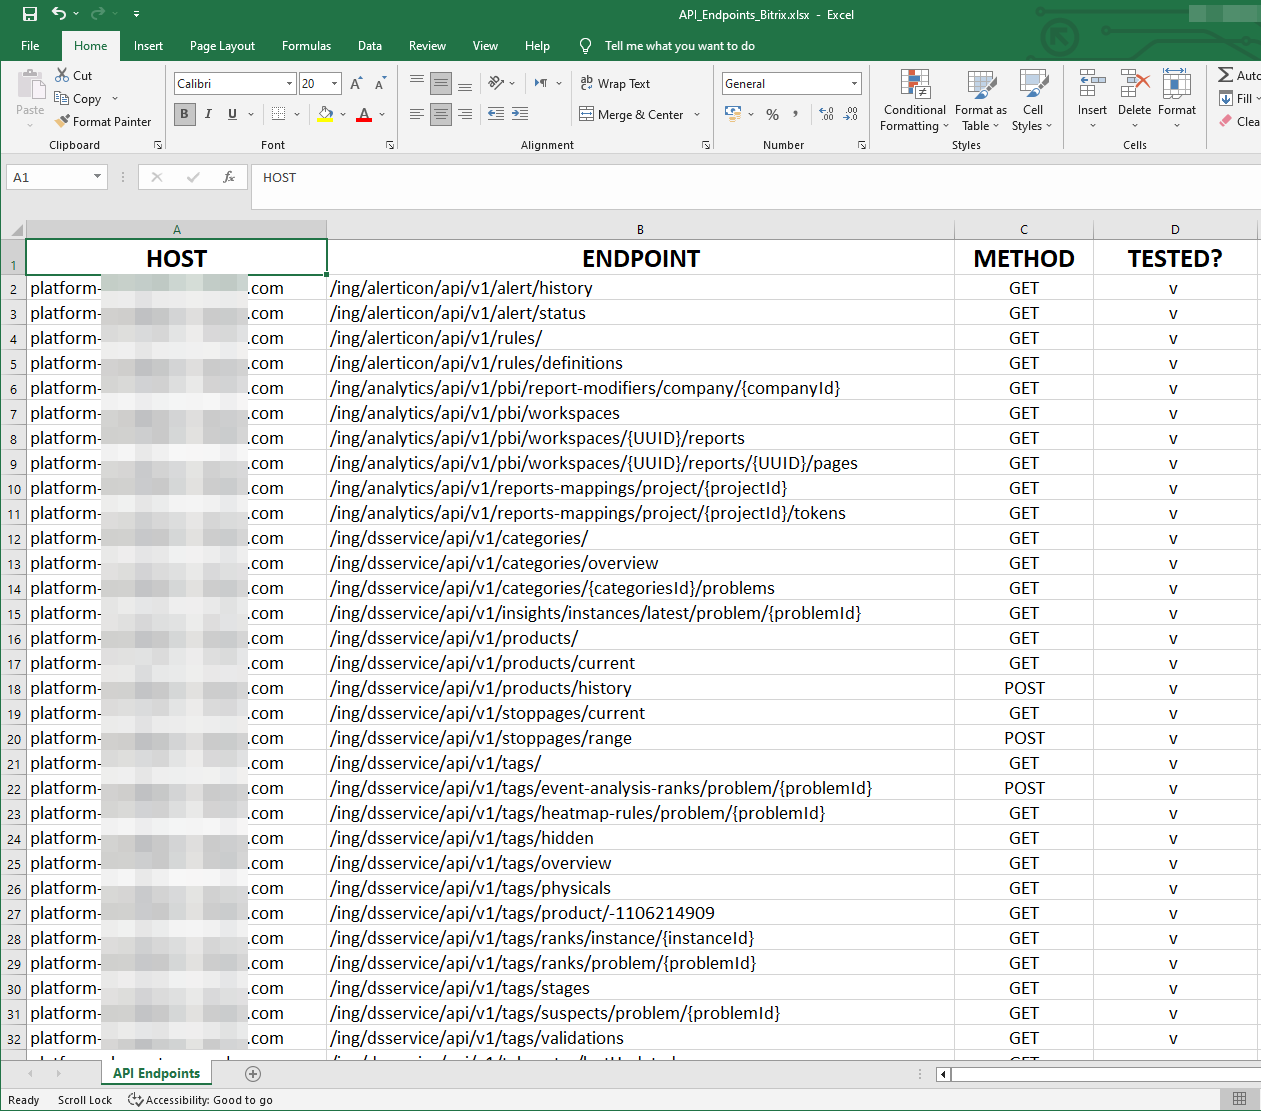
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
api-security-testinginformation-gatheringweb-security+4
10
sajibuu/burp_collectorA Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 marcin-wolak/simplermidiscoverer
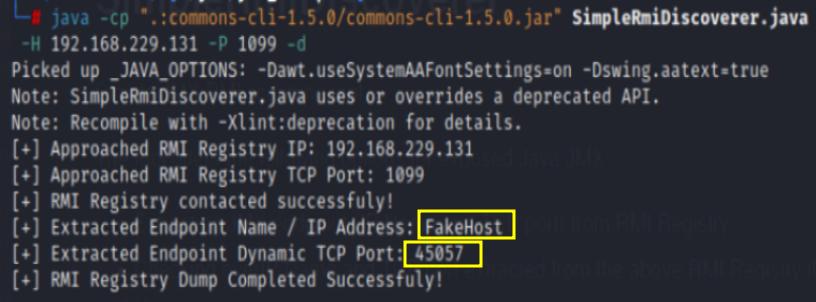
Simple JMX RMI scanning tool
 hannah-portswigger/totpauthenticate
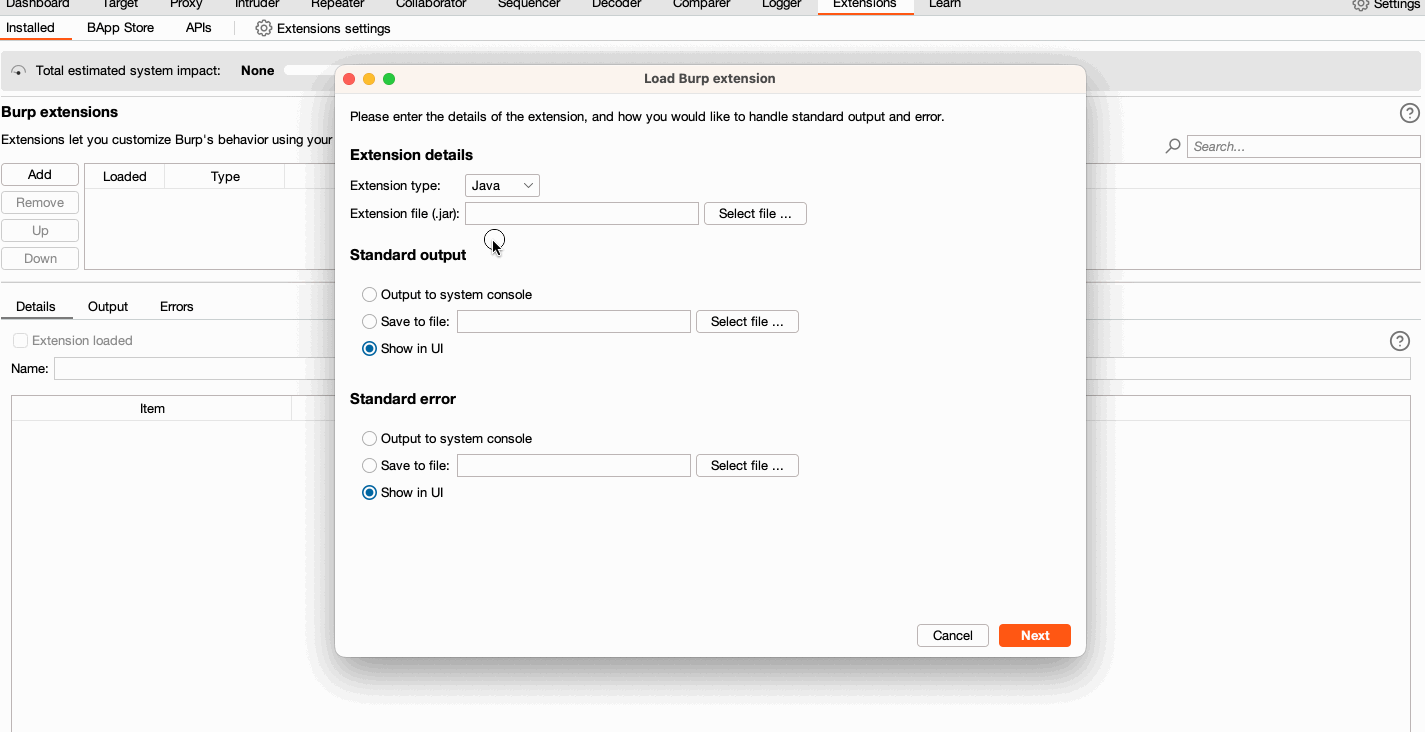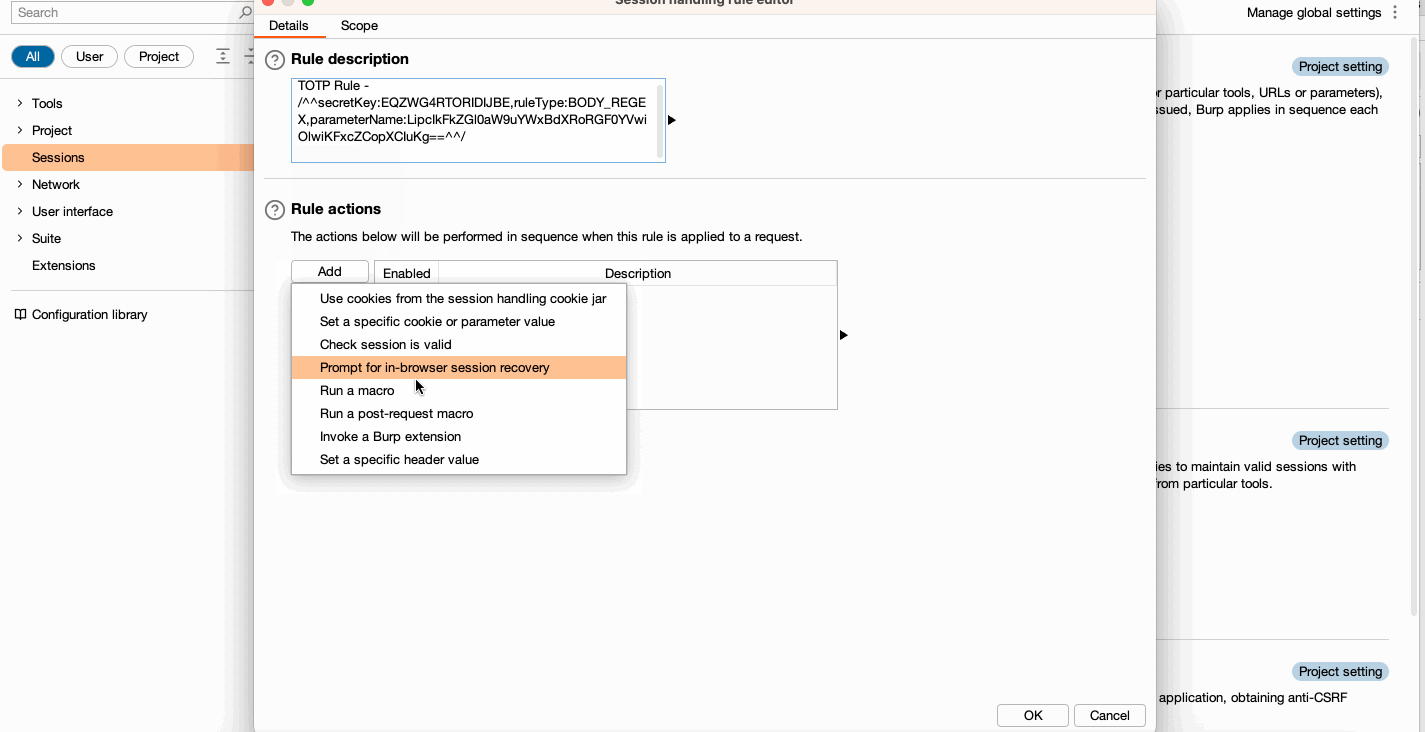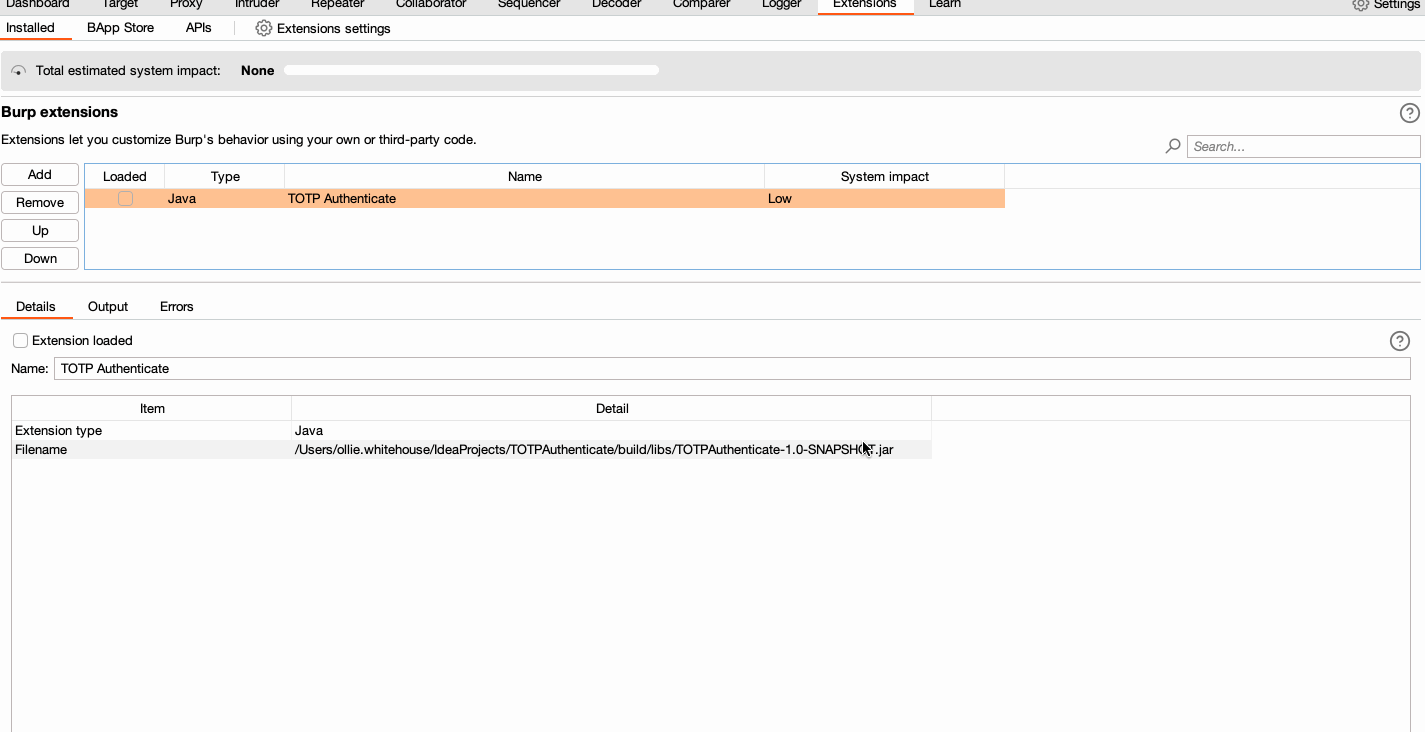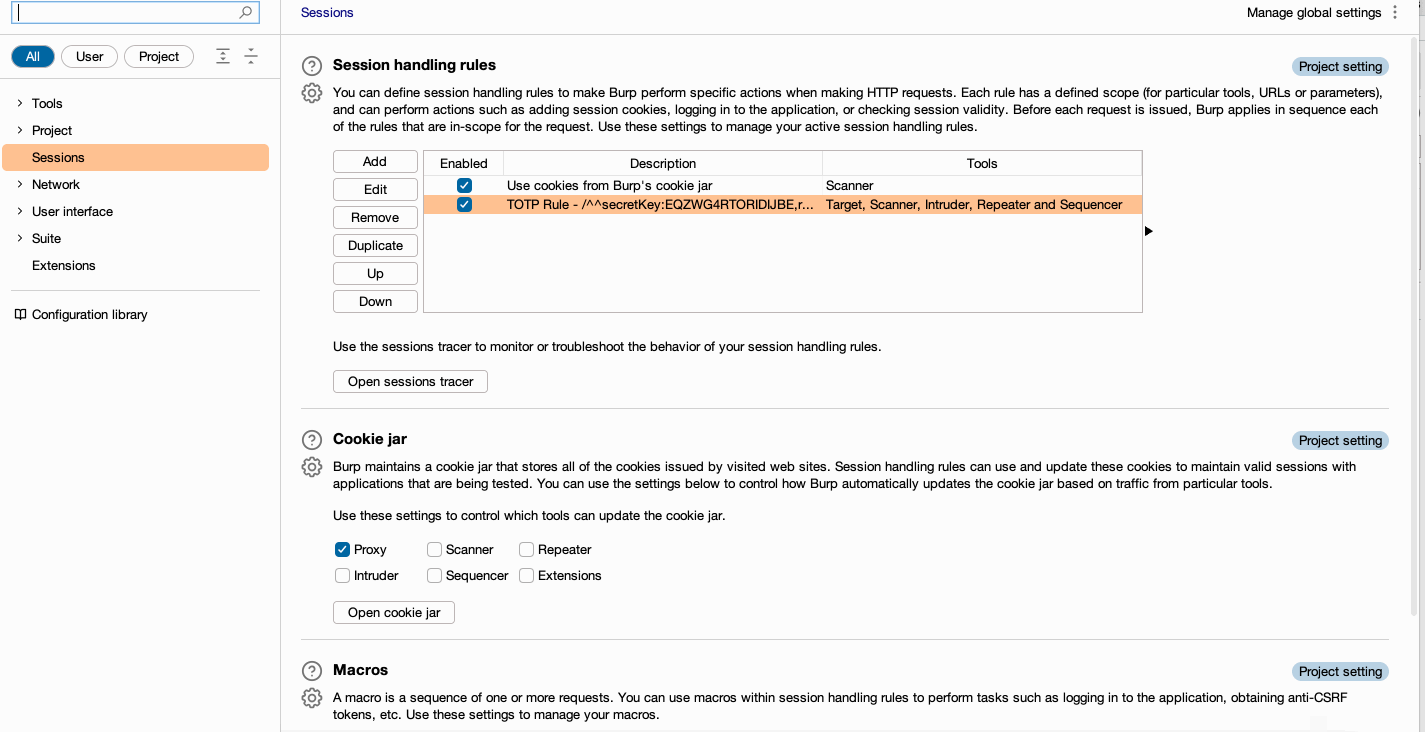
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
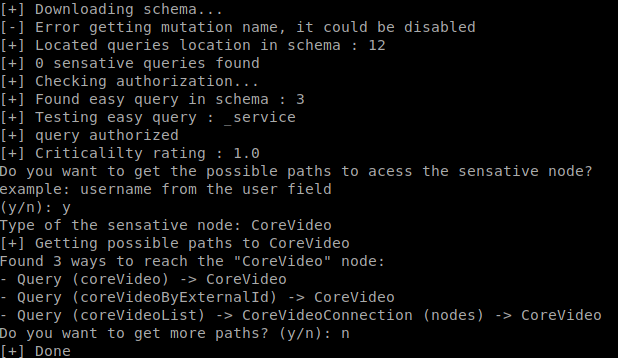 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
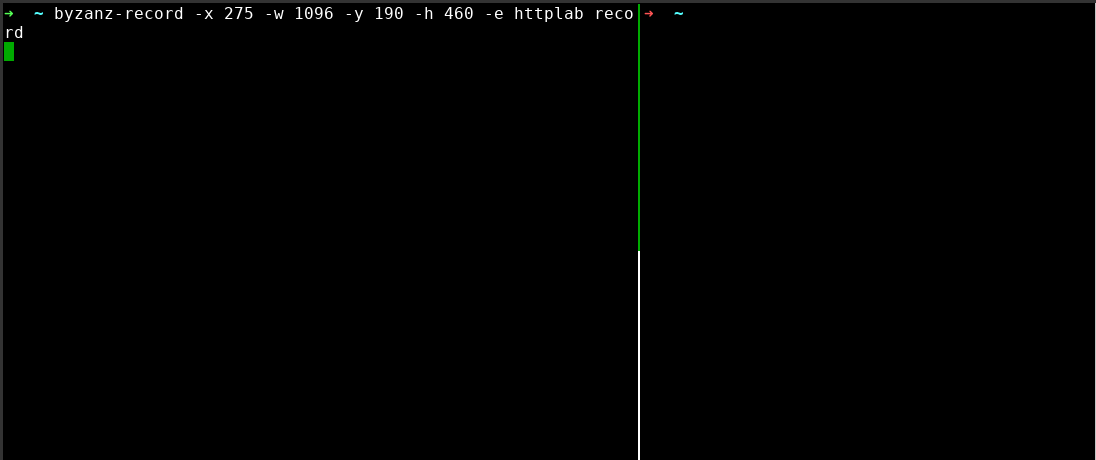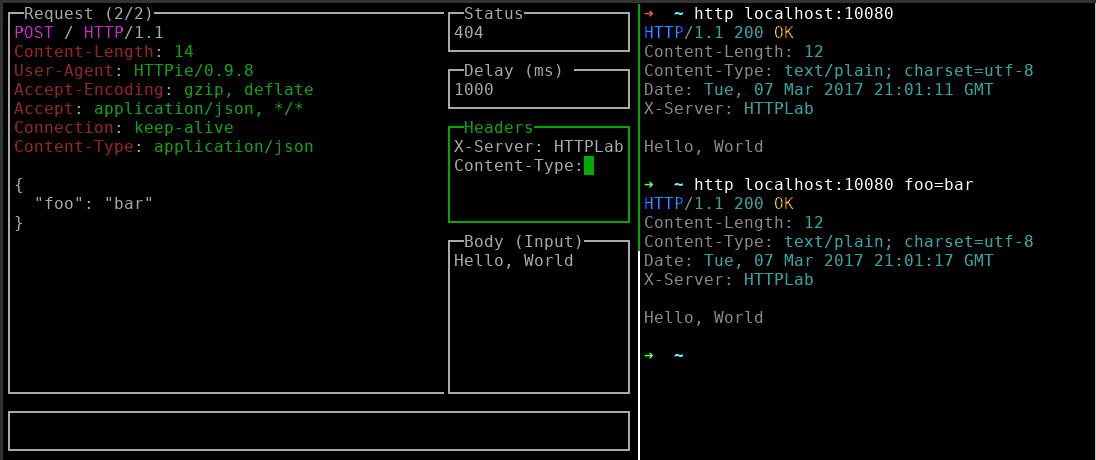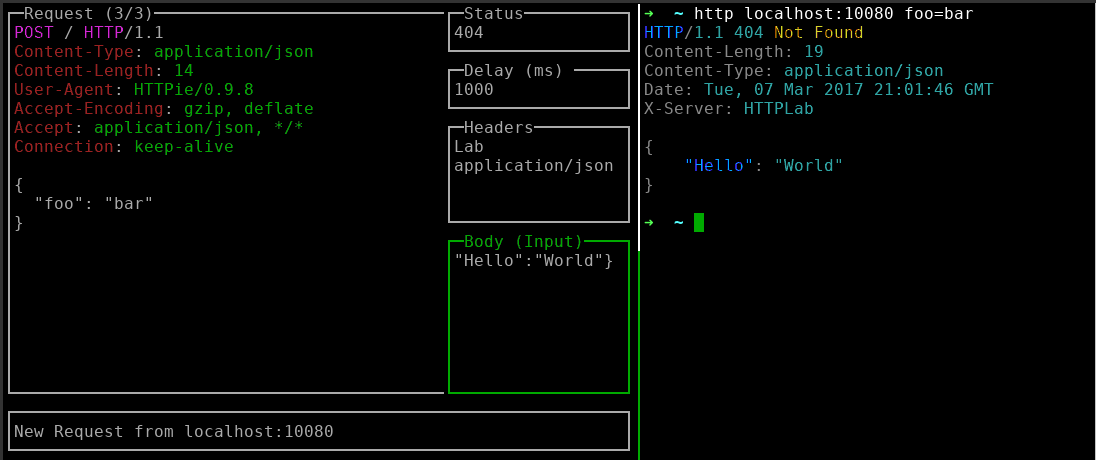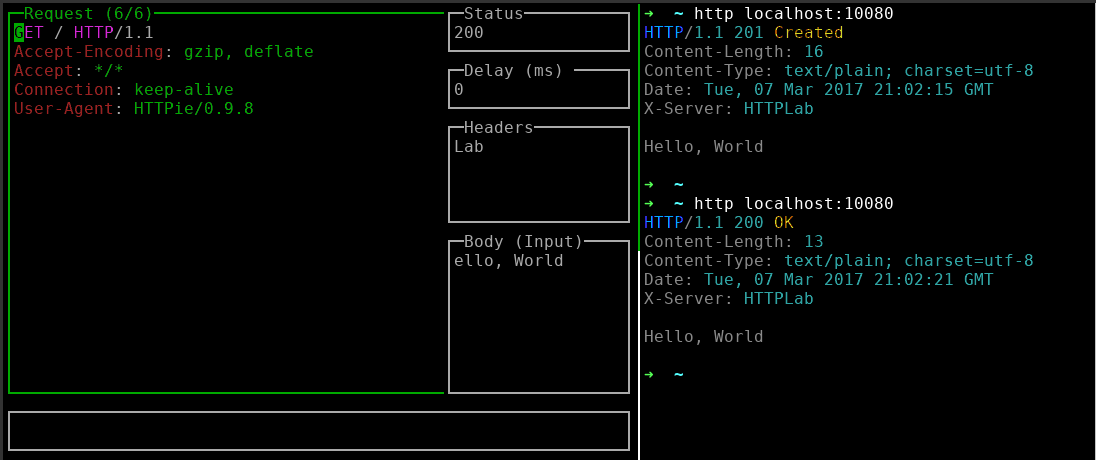 qustavo/httplab
Interactive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing.
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
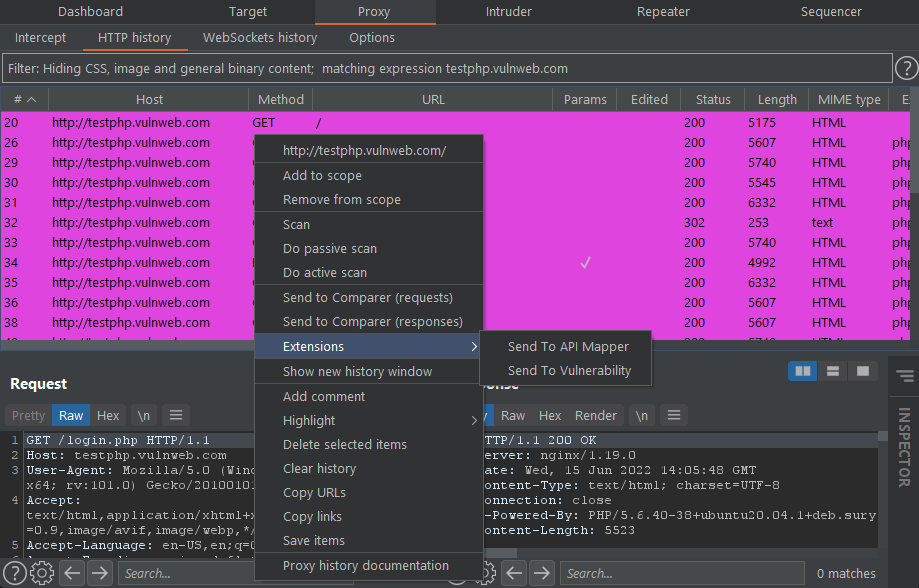 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
 danialhalo/acuautomate
Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.
 owasp/dvsa
a Damn Vulnerable Serverless Application
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer
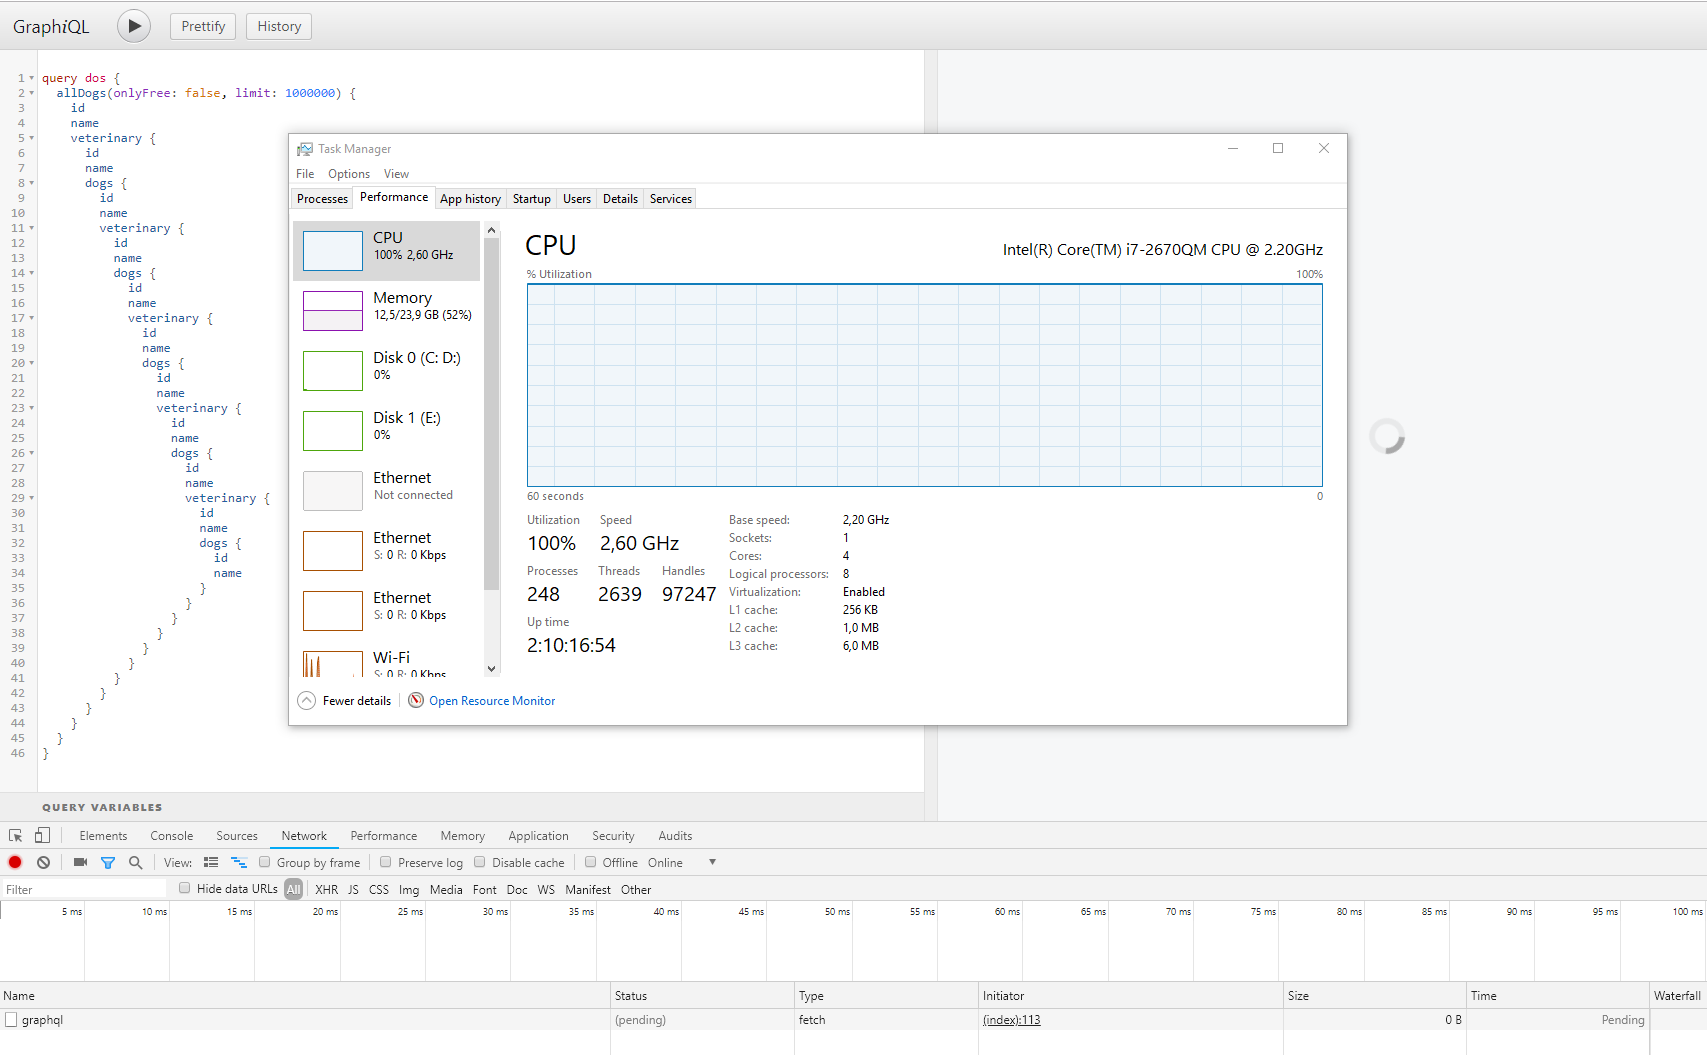 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.
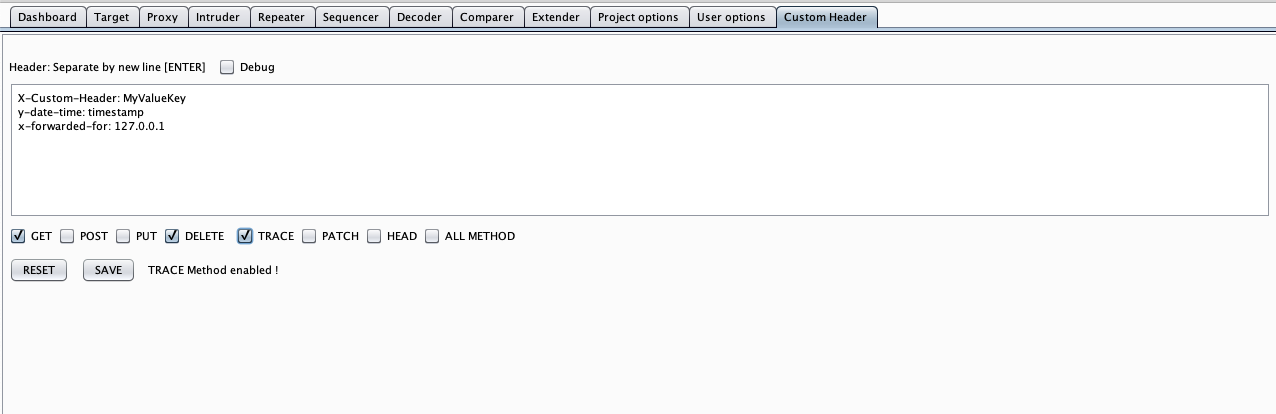 mirfansulaiman/customheader
This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
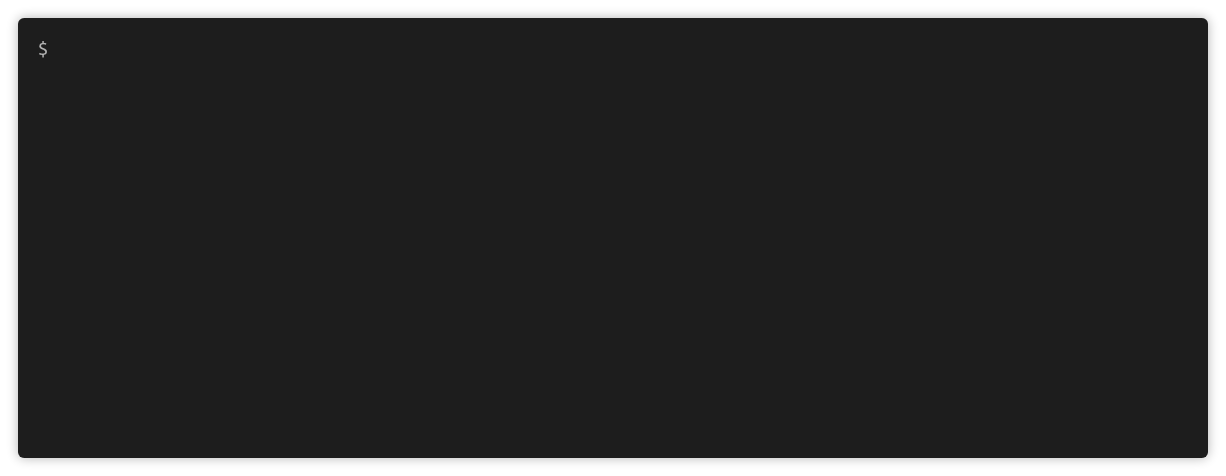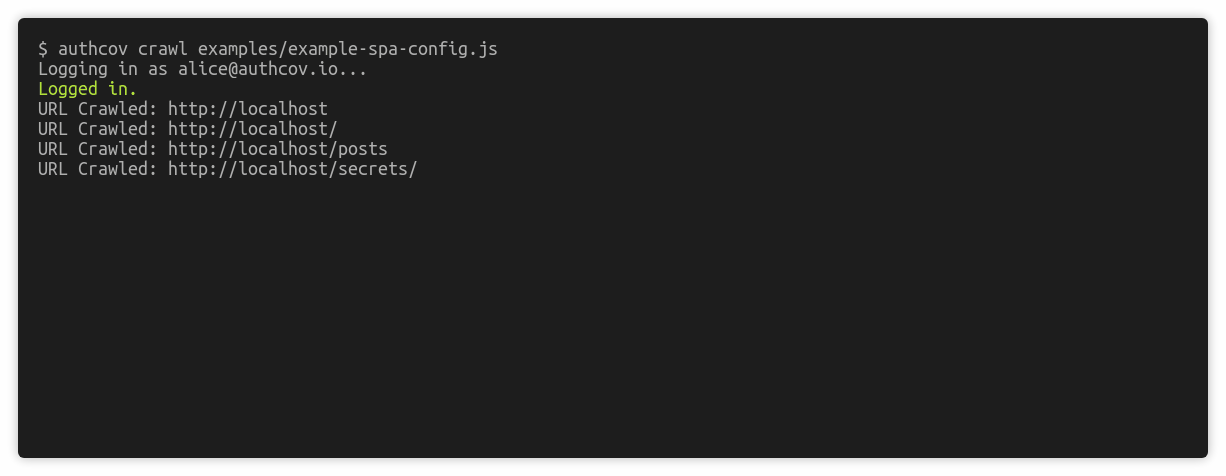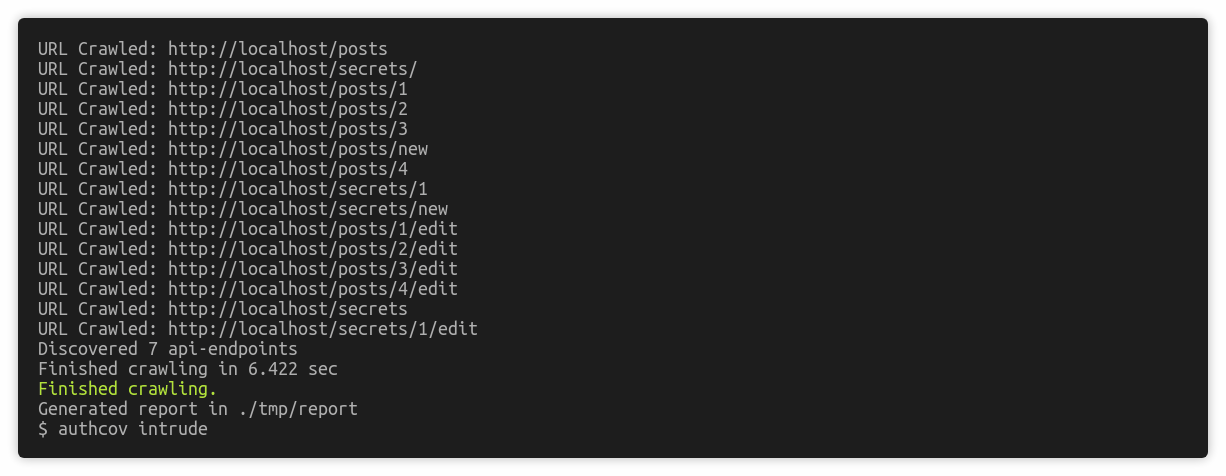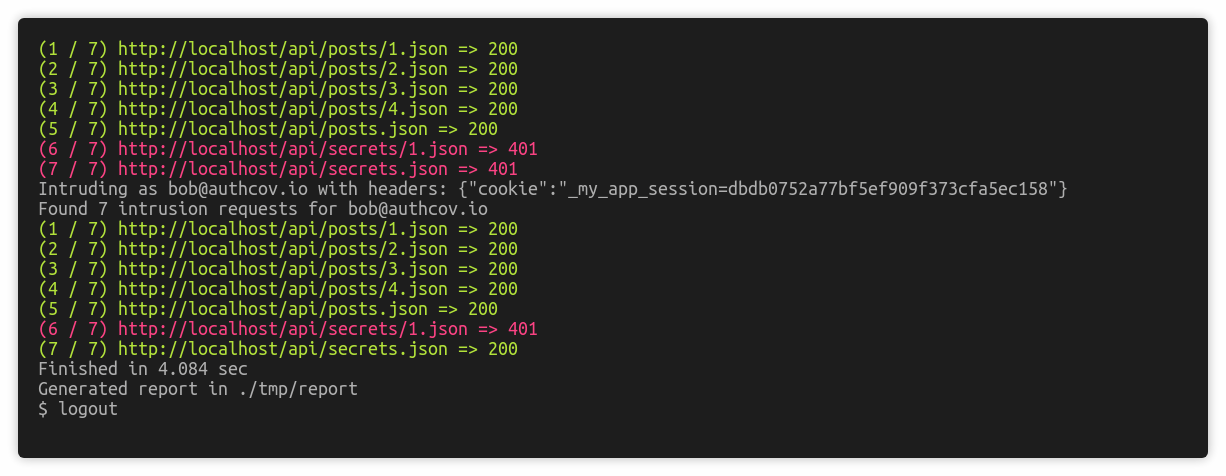 authcov/authcov
Web app authorisation coverage scanning
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions