

-LogicSentry-AI
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
ai-securityapi-security-testingcode-analysis+9
1
vighnesh91/-logicsentry-aiOffline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
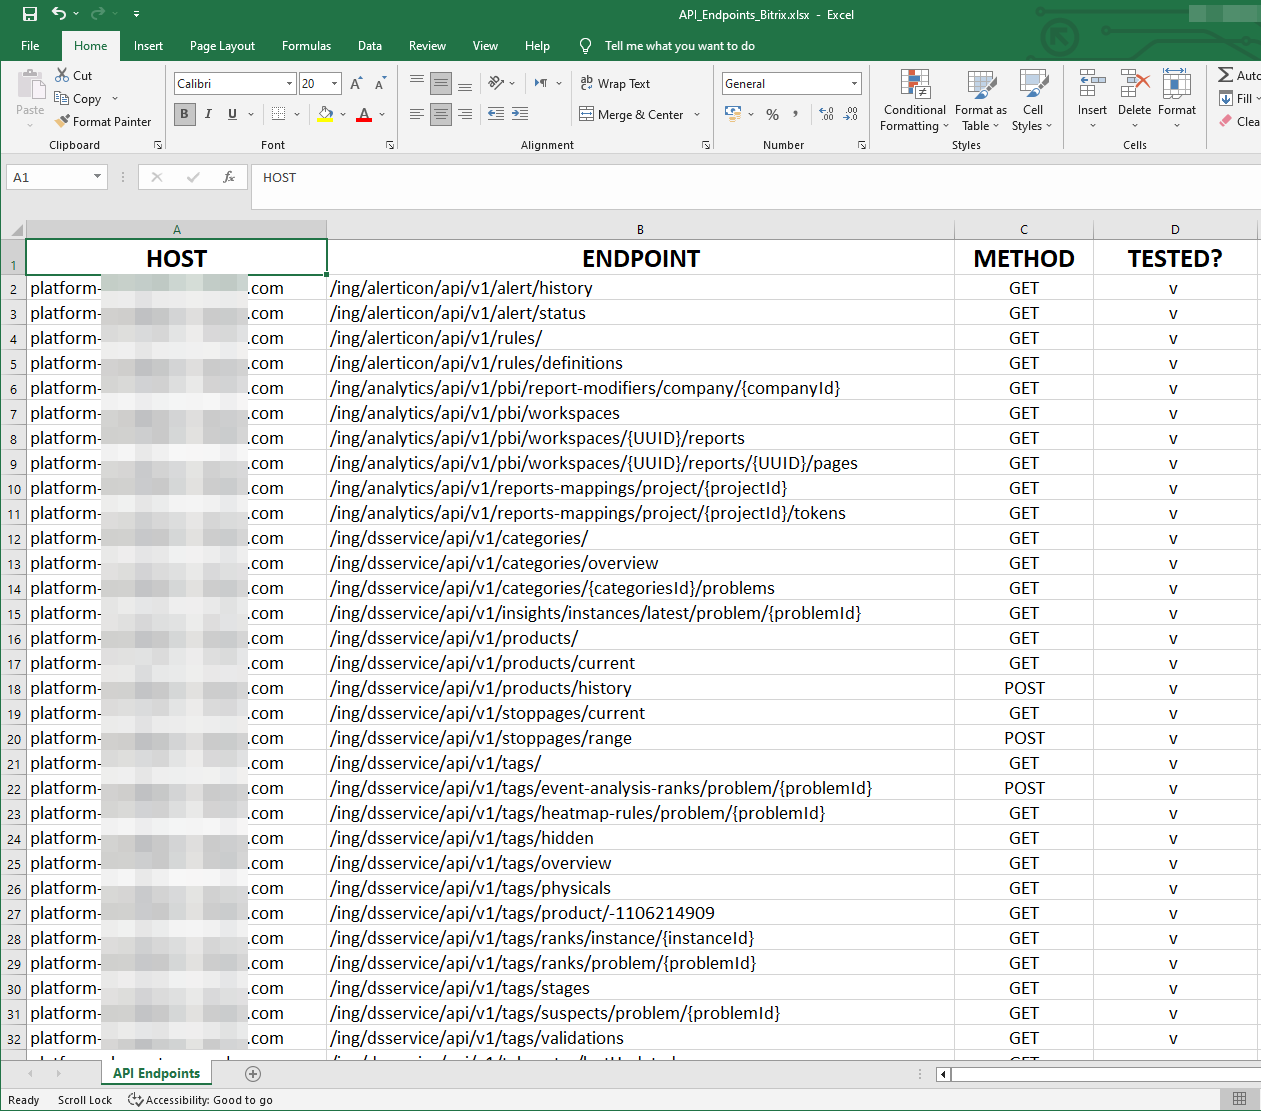 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
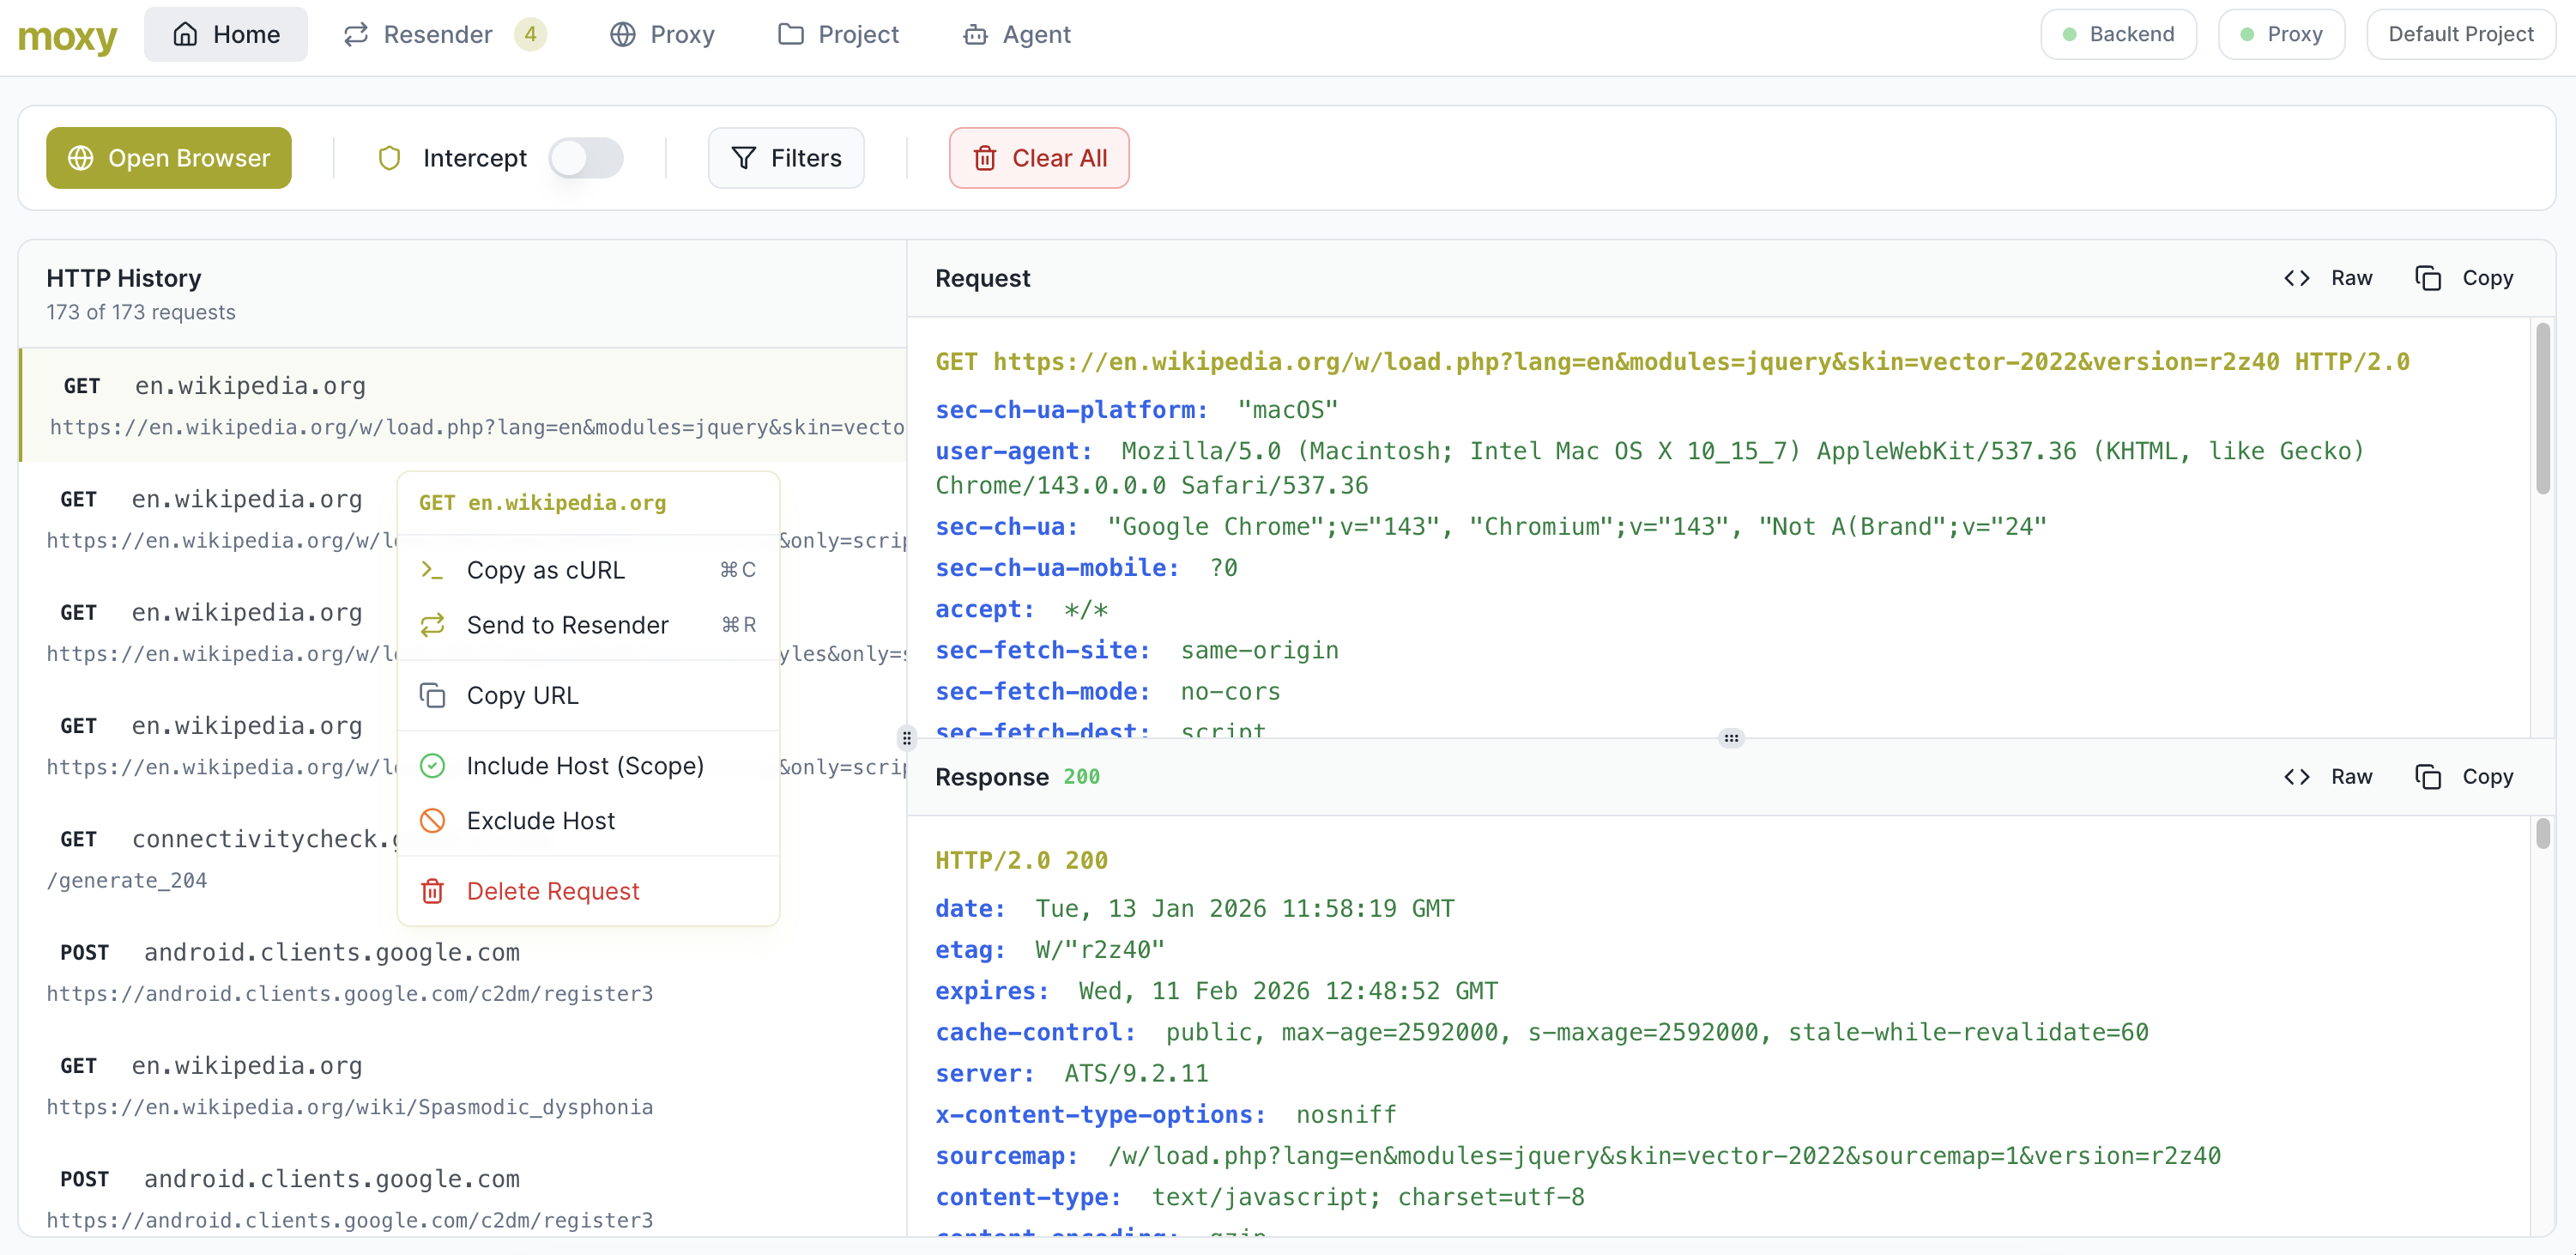 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 sn1r/mass-assigner
Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
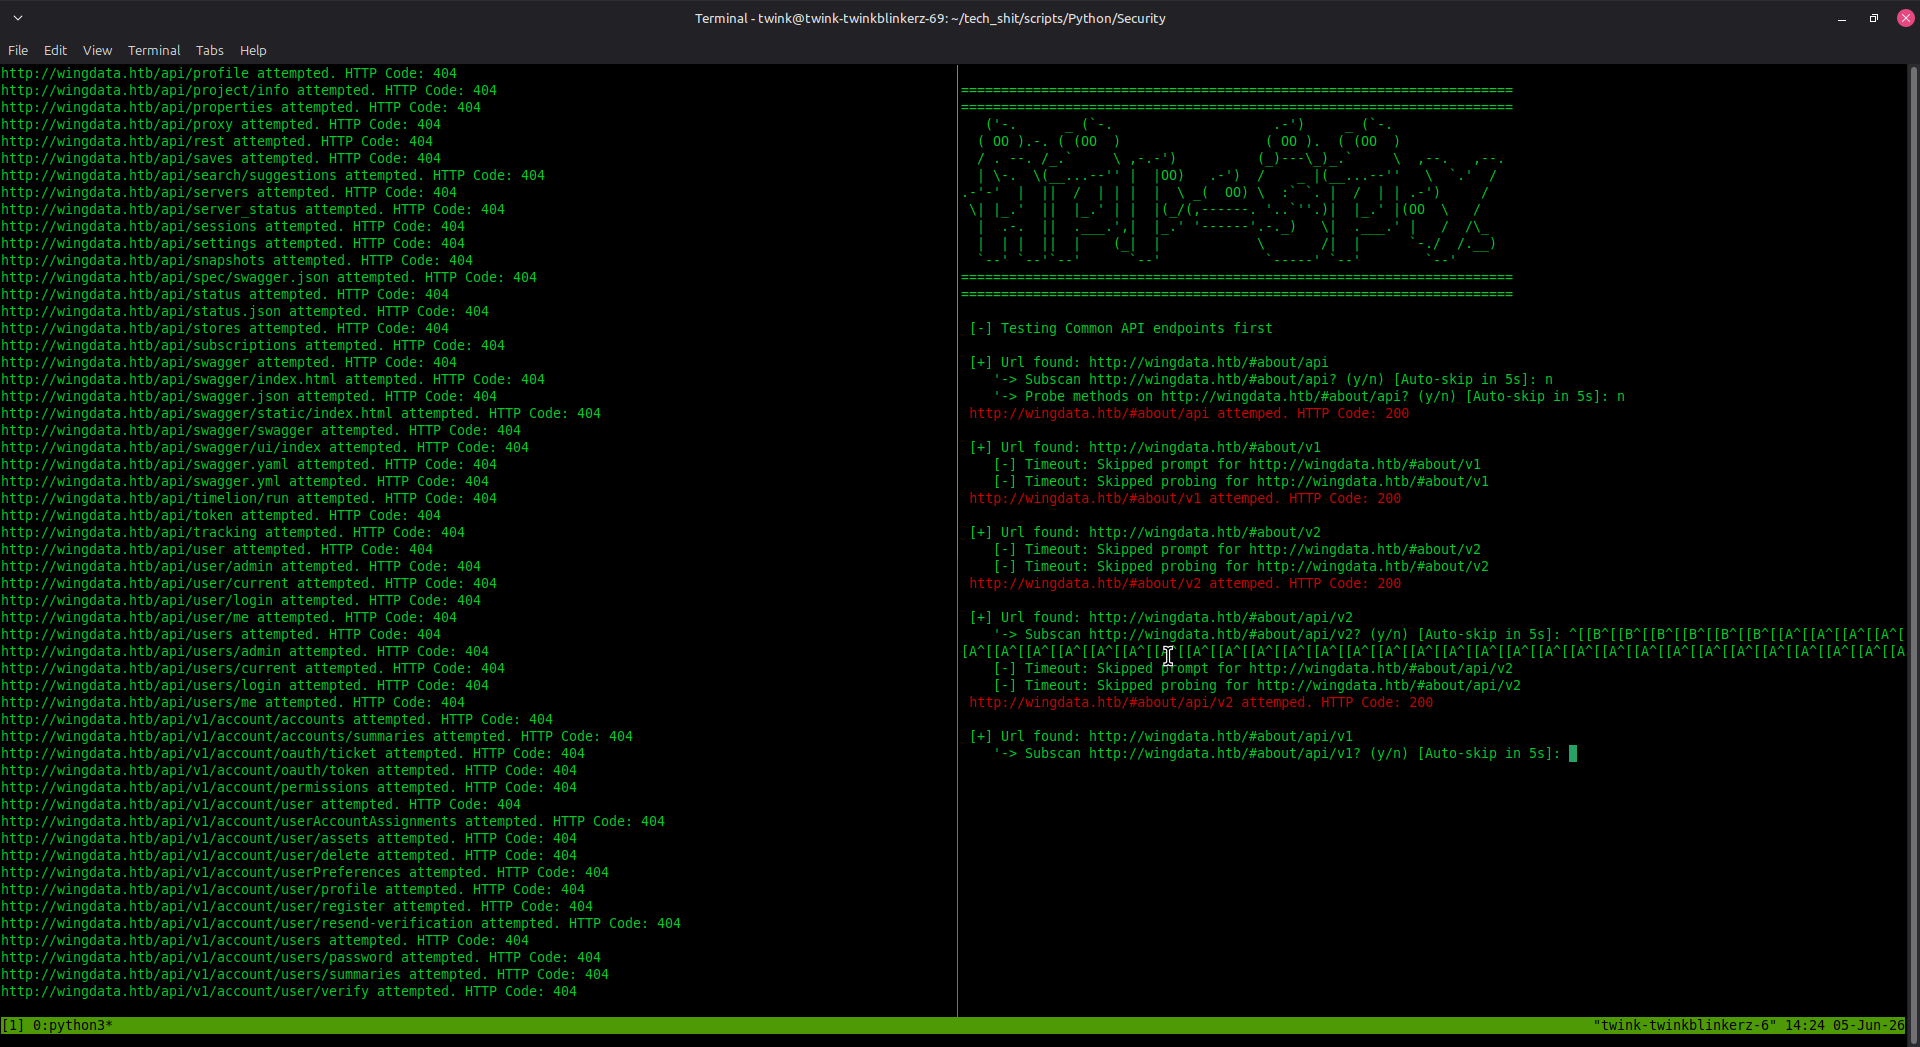 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 blueowl-overlord/burp_cve-2025-31324
Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
 emo-crab/slinger
An HTTP client specifically developed for security researchers
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 google/nogotofail
An on-path blackbox network traffic security testing tool