MappedImagesDetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection

A network packet forensics tool for SSH

Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity

A canary designed to minimize the impact from certain Ransomware actors

Enumerate various traits from Windows processes as an aid to threat hunting

Simulates CVE-2024-38063 TCP/IP remote code execution attack, captures network traffic with TShark, and trains a machine learning model to detect…

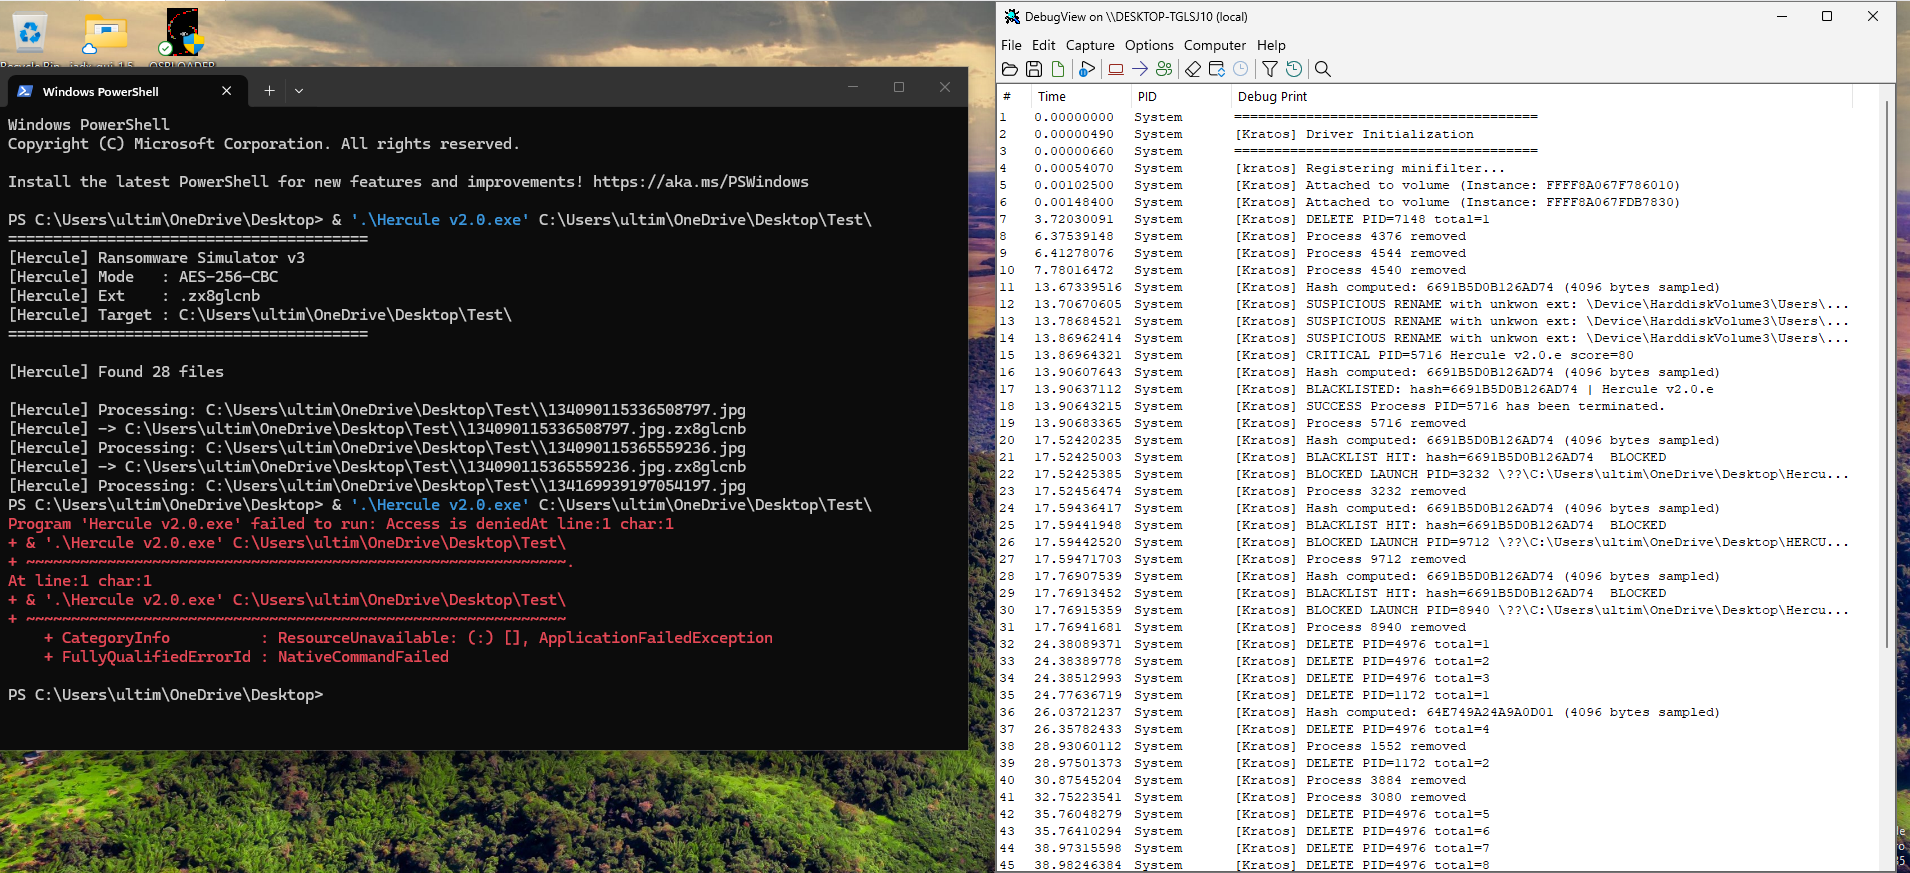
Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize

Zeek plugin to detect and decrypt XOR-encrypted EXEs

This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…

ETW based POC to identify direct and indirect syscalls

Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…

Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…

The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…

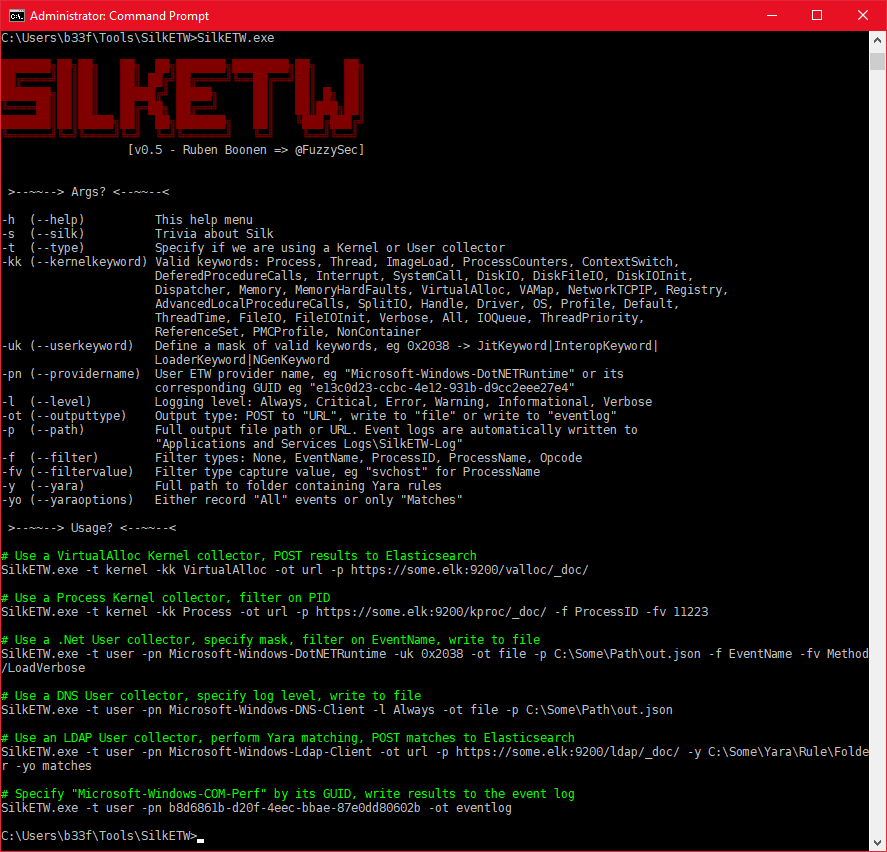
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.