
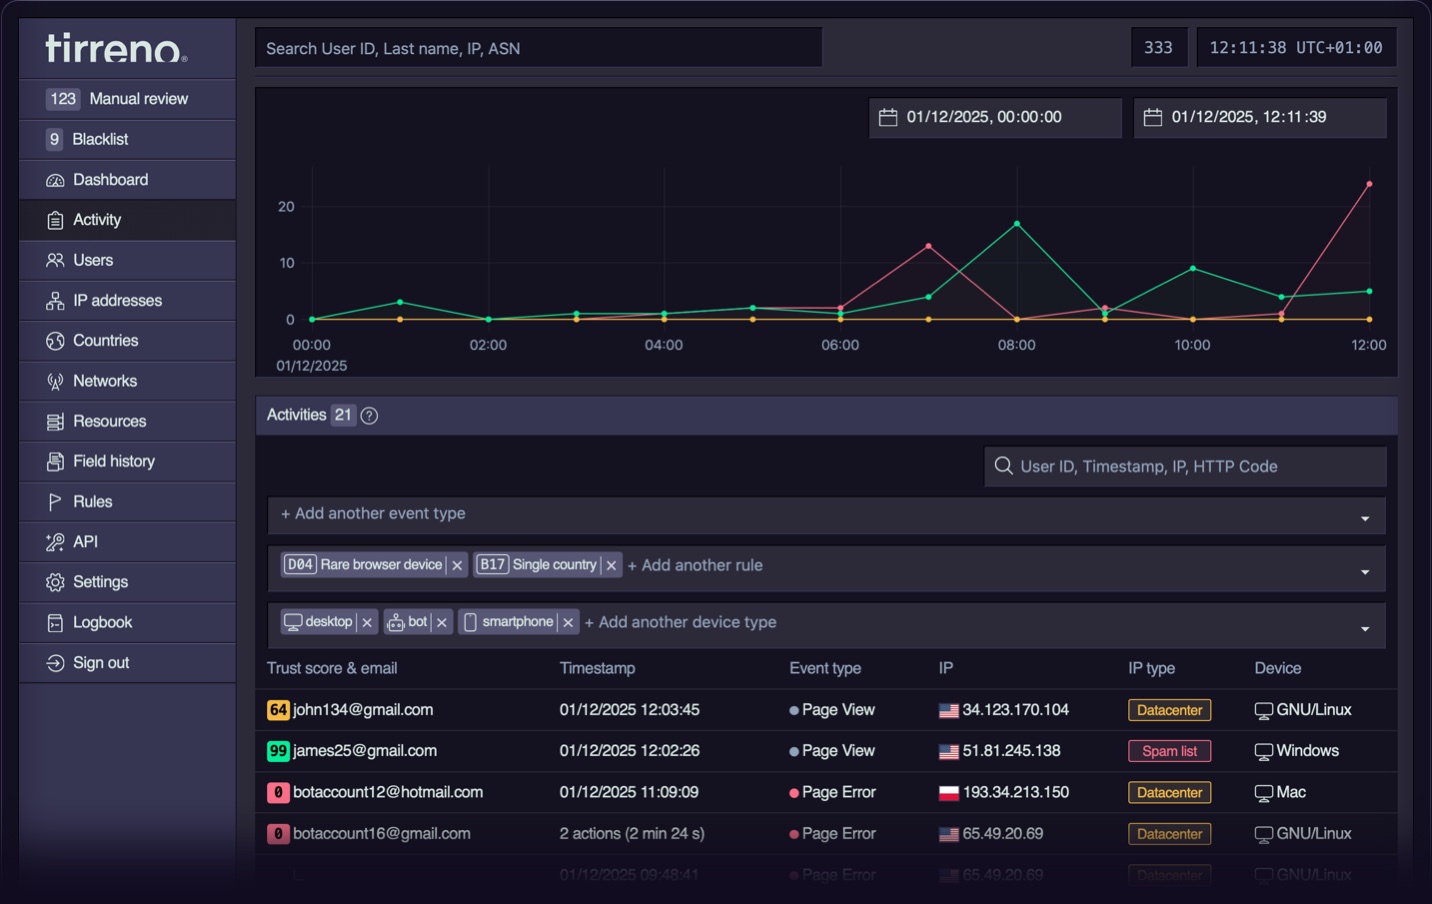
tirreno
 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
anomaly-detectionanti-botapi-security+3
1.6k
tirrenotechnologies/tirrenoOpen-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
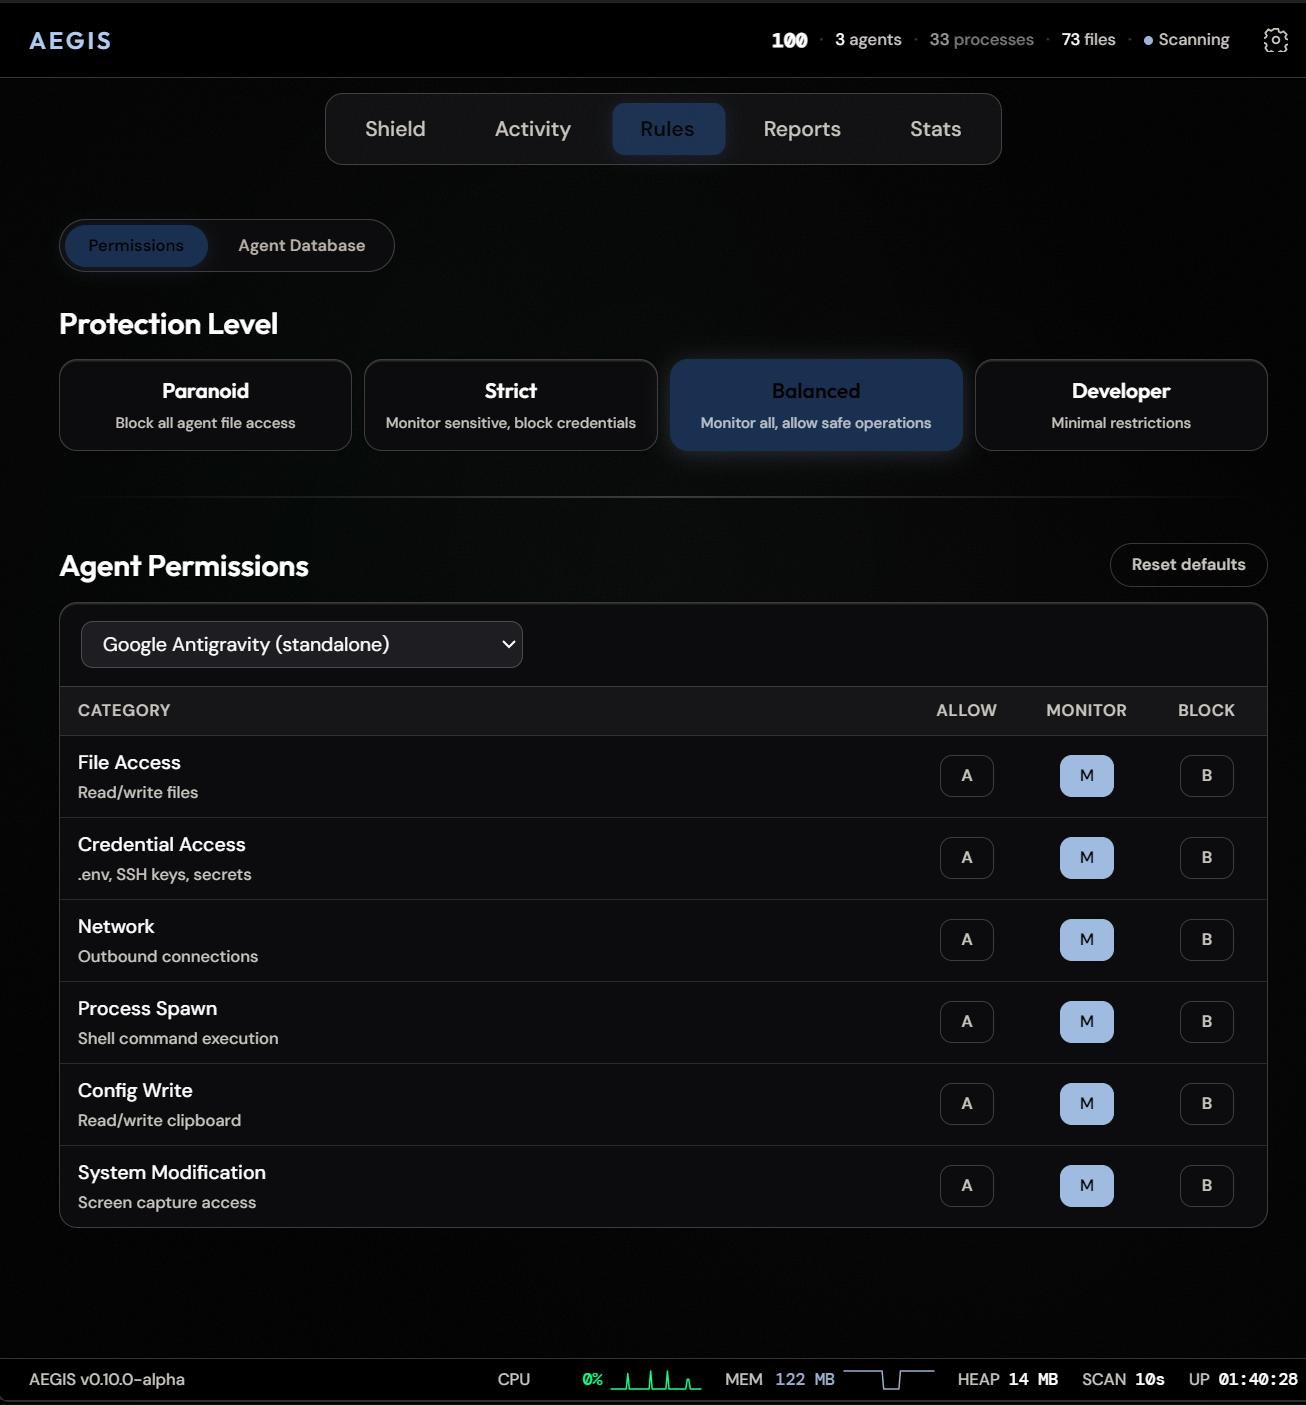 antropos17/aegis
Windows-first desktop oversight for AI agents: live monitoring, local security reviews, token usage, audit reports and opt-in action policies/MCP…
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 thingsboard/thingsboard
All-in-one IoT Platform - Device management, data collection, processing and visualization.
 googlecloudplatform/professional-services
Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
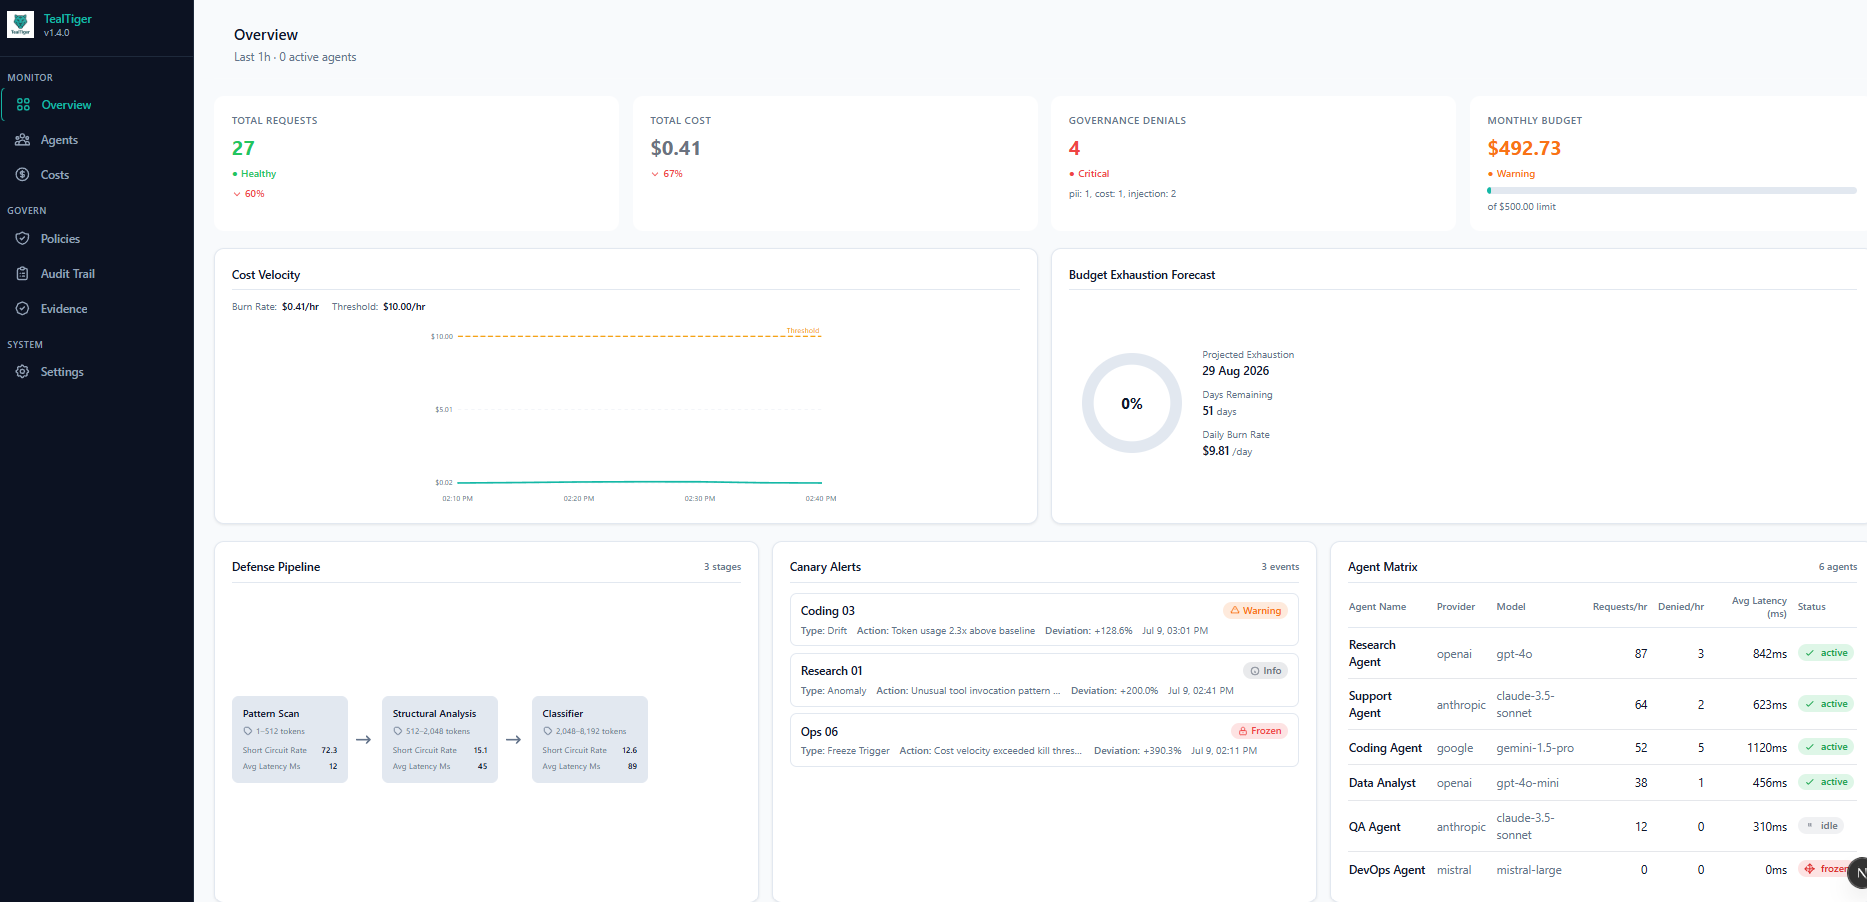 agentguard-ai/tealtiger
Powerful protection for AI agents - Open-source security and cost tracking for AI applications
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
 ziad-hsn/cpra
CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…
 owasp/the-agents-epistemic-baggage
An audit-oriented risk model for how agent-generated inferences can change epistemic status, gain operational authority, and influence later…
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 chainguard-dev/osquery-defense-kit
Production-ready detection & response queries for osquery
 connectedlucy/plague
Default Detections for EDR
 anecdotes-yair/trust-my-agent-ai
Security & Compliance bodyguard for OpenClaw agents
 bplinux/chackd
Daemon to randomize tcp_challenge_ack_limit to prevent side channel attacks CVE-2016-5696
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).